
 Saudi Arabia Cybersecurity Market | 2026-2036
Saudi Arabia Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Saudi Arabia Cybersecurity Market Analytics
Market Context
A capital-intensity divergence between cloud-native specialists and legacy hardware vendors is rotating competitive dynamics in Saudi Arabia. Sirar leverages sovereign data-center certifications to anchor government contracts. Palo Alto Networks sustains premium positioning through AI-driven threat-intelligence platforms. Fast Digital Technology competes on localized managed-security services for mid-market clients.
Technical Definition and Segments
Saudi Arabia cybersecurity encompasses hardware, software, and services that detect, prevent, and respond to unauthorized network intrusions, data exfiltration, and operational technology disruptions, typically operating across on-premises appliances, cloud-native agents, and hybrid orchestration layers. The primary purpose is preserving confidentiality, integrity, and availability of digital assets across critical national infrastructure and commercial enterprises. Cloud-based deployment is outpacing on-premises installations as Saudi organizations migrate workloads to localized hyperscaler regions. Endpoint Security commands disproportionate investment from energy sector buyers protecting distributed operational technology nodes. Managed Services attracts fastest growth among SMEs lacking in-house security operations centers.
Regulatory Environment
Saudi Arabia's National Cybersecurity Authority enforces Essential Cybersecurity Controls mandating baseline protections across all critical infrastructure operators, directly shaping procurement specifications and vendor qualification criteria. SAMR and SDAIA coordinate on data-localization requirements that privilege domestic hosting and sovereign cloud architectures. Stakeholders must monitor evolving NCA amendments and SDAIA artificial-governance standards to anticipate compliance-driven spending shifts.
Market Dynamics
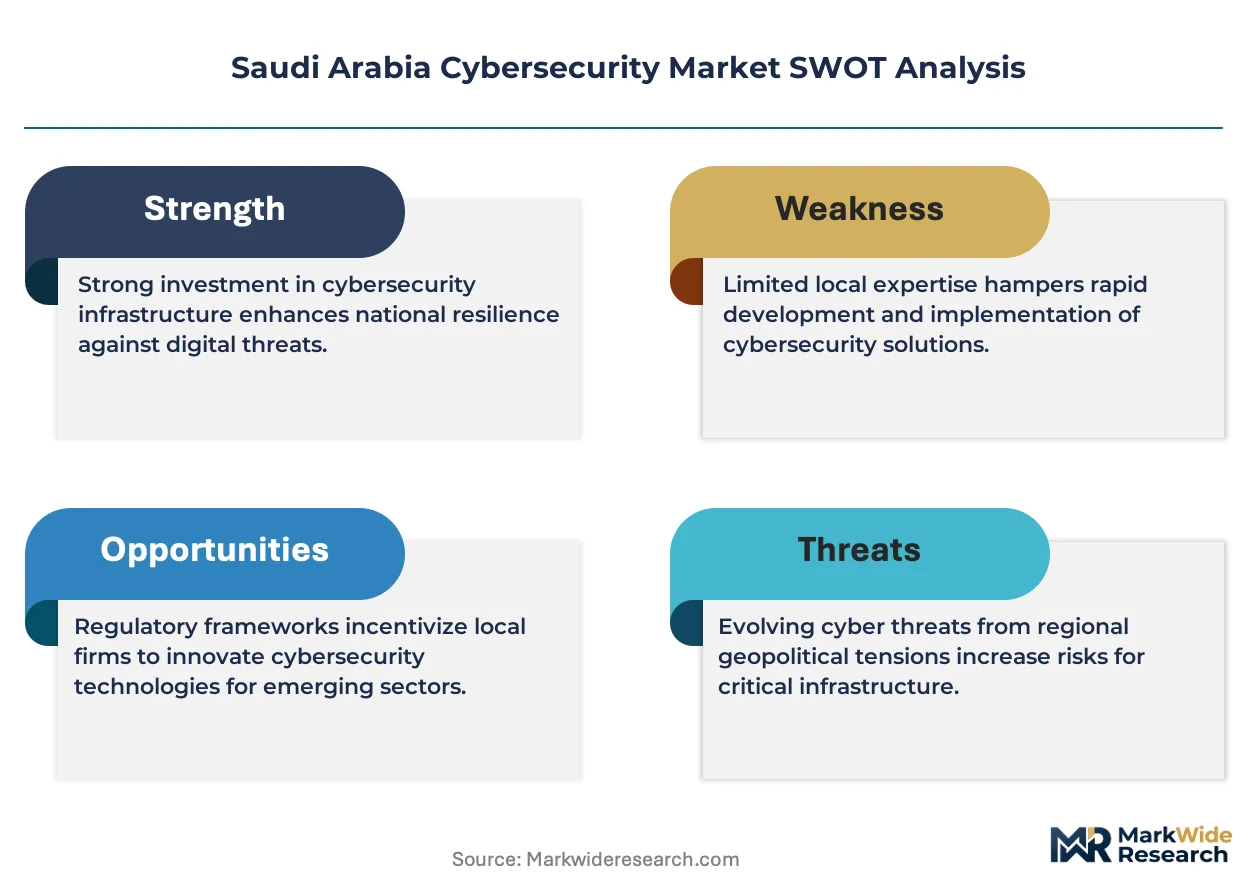
The National Cybersecurity Authority's Essential Cybersecurity Controls framework is mandating baseline protections across all critical infrastructure operators, forcing procurement specifications toward sovereign-certified architectures and reshaping vendor qualification criteria throughout the Kingdom.
Growth Catalysts
- NEOM Smart City Deployments:The giga-project's operational technology nodes require endpoint security at scale, generating concentrated demand for industrial control system protection.
- Essential Cybersecurity Controls:NCA's mandatory compliance framework compels energy and financial sector operators to upgrade security postures on defined timelines.
- Oil and Gas Infrastructure Protection:Operators across the Eastern Province are hardening distributed operational technology networks against targeted intrusions.
Market Restraints
- Specialized Talent Scarcity:Domestic cybersecurity workforce development lags deployment timelines, constraining implementation velocity for complex zero-trust architectures.
- Sovereign Cloud Certification Bottlenecks:Only three domestic data-center operators hold NCA Tier-IV certifications, concentrating supply and extending procurement cycles.
- Legacy System Interoperability:Decades-old SCADA installations in petrochemical facilities resist seamless integration with modern detection-and-response platforms.
Strategic Opportunities
- SDAIA Artificial Intelligence Governance:Pending standards for AI system security will create compliance-driven demand for model-risk management tools.
- Managed Security Services for SMEs:Mid-market enterprises in Jeddah and Dammam lack in-house security operations centers, opening white space for localized service providers.
- Operational Technology Convergence:Integration of IT and OT security stacks presents openings for vendors with cross-domain orchestration capabilities.
Industry Challenges
- Zero-Trust Architecture Deployment Complexity:Organizations struggle to segment legacy networks without disrupting continuous industrial processes.
- Certification Timeline Compression:NCA amendment cycles accelerate faster than vendor product recertification processes can accommodate.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Saudi Arabia Cybersecurity Market |
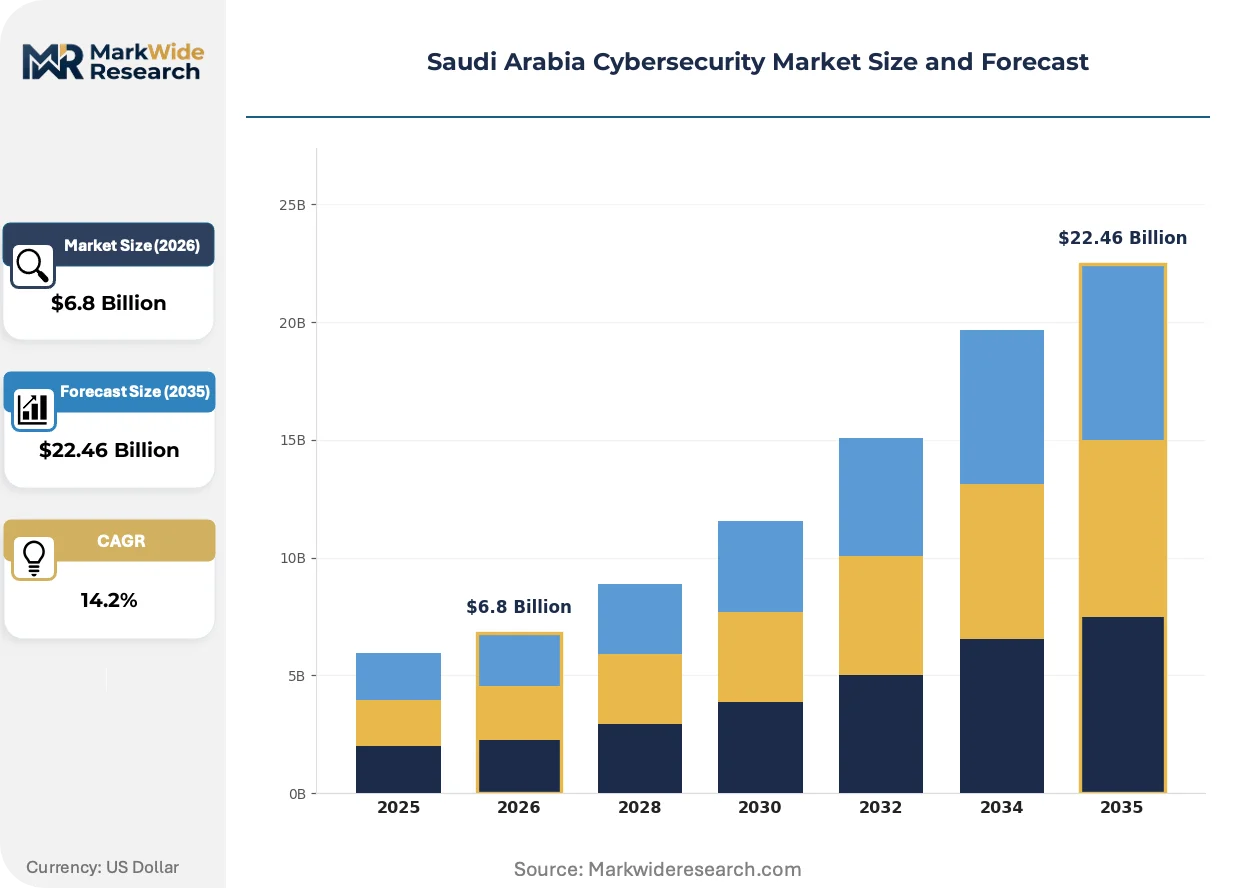
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $22.46 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-premises, Cloud-based, Hybrid, Managed Services Solution Type: Firewall, Intrusion Detection, Antivirus, Endpoint Security Industry Vertical: Financial Services, Healthcare, Government, Energy End User: SMEs, Large Enterprises, Educational Institutions, Non-profits |
| Companies Covered | Sirar, Fast Digital Technology, Palo Alto Networks, Inovasys, Advance Datasec, Taqnia Cyber, Ahlan Cyber, Gateway Infotech, COGNNA, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Saudi Arabia Cybersecurity Market Evolving Landscape
AI-driven threat detection is fragmenting traditional signature-based security paradigms, while regulatory mandates accelerate sovereign infrastructure requirements and buyer procurement patterns shift toward integrated service bundles.
Extended detection and response platforms are fragmenting the endpoint security market by consolidating telemetry across identity, network, and cloud workloads into unified analyst consoles. Saudi Aramco and SABIC affiliates are piloting these architectures at scale, compressing procurement timelines for standalone antivirus contracts. The technology is fragmenting vendor competitive positions by privileging platforms with native SOAR integration over point-product specialists.
NCA amendments to the Essential Cybersecurity Controls framework are tightening data-localization requirements for critical infrastructure operators. Financial institutions in Riyadh must now maintain primary data processing within Kingdom borders, accelerating sovereign cloud migration timelines. SAMR coordination with SDAIA on cross-border data flows is forcing multinational vendors to establish domestic hosting partnerships.
Subscription-based security service bundling is displacing perpetual license purchasing among mid-market enterprises. Local system integrators in the Eastern Province are capturing buyer relationships by wrapping managed detection, incident response, and compliance reporting into single contracts. This pattern concentrates most visibly among healthcare providers and educational institutions lacking dedicated security operations staff.
Saudi Arabia Cybersecurity Market Segmentation
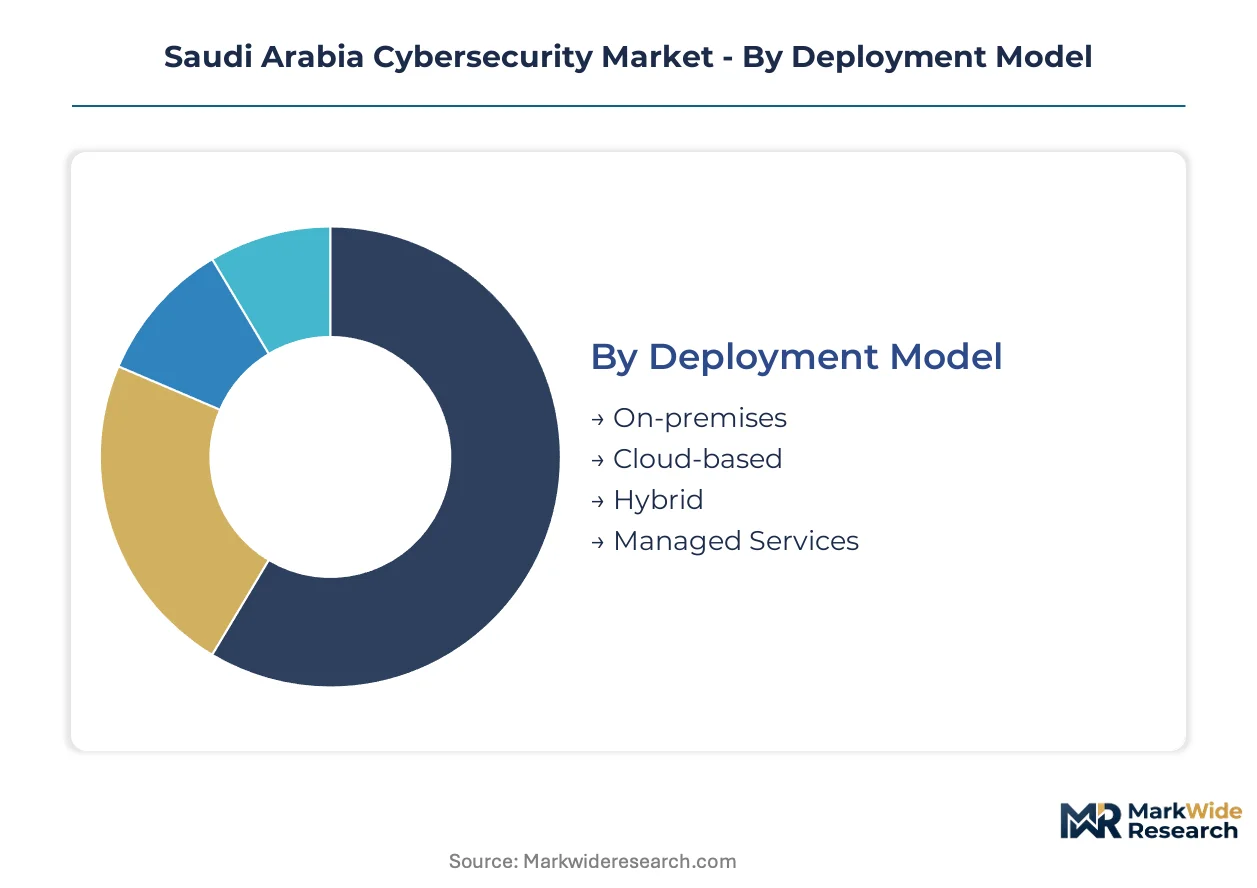
Cybersecurity procurement in Saudi Arabia fragments across deployment preferences, solution architectures, and sector-specific compliance mandates. Understanding these segment boundaries clarifies how NCA certification requirements and sovereign data policies reshape vendor access and pricing power across distinct buyer clusters.
Deployment Model:
Channel mix varies sharply: cloud and managed services flow through hyperscaler partnerships and local system integrators, while on-premises deployments rely on hardware distributors with NCA Tier-IV facility access.
- Cloud-based:Native SaaS architectures hosted within Kingdom borders dominate financial sector procurement in Riyadh. SAMR data-localization rules compel primary processing on sovereign infrastructure, accelerating migration from foreign hyperscaler regions.
- Managed Services:24/7 security operations center capabilities delivered under subscription contracts attract mid-market energy affiliates lacking in-house expertise. Eastern Province petrochemical operators favor this model for OT network monitoring without headcount expansion.
- On-premises:Air-gapped appliances persist in classified government facilities and critical infrastructure control rooms requiring physical isolation from external networks.
- Hybrid:Split workloads across private data centers and sovereign cloud instances accommodate legacy SCADA systems alongside modern analytics pipelines.
By volume, Cloud-based deployments lead. By growth pace, Managed Services is climbing the fastest.
Solution Type:
Cost tier stratification separates enterprise-grade platforms with AI-driven analytics from commoditized signature-based tools serving budget-constrained buyers.
- Endpoint Security:Agent-based protection for servers, workstations, and operational technology nodes commands premium pricing in energy sector deployments. NEOM's smart city infrastructure and Aramco's distributed OT networks drive concentrated demand for industrial-hardened variants.
- Firewall:Next-generation appliances with application-aware inspection anchor perimeter defense for financial institutions in Riyadh's banking district. NCA Essential Cybersecurity Controls mandate baseline gateway protections, forcing refresh cycles at compliance deadlines.
- Intrusion Detection:Network traffic analysis systems with behavioral baselining detect anomalous patterns in hybrid IT-OT environments.
- Antivirus:Signature-based endpoint protection occupies the economy tier, displaced gradually by extended detection platforms in enterprise accounts.
By installed base, Firewall holds the largest footprint. By expansion trajectory, Endpoint Security is gaining share fastest.
Industry Vertical:
Application intensity varies: energy and financial services face mandatory NCA compliance with defined timelines, while healthcare and government operate under staggered implementation schedules.
- Energy:Oil, gas, and petrochemical operators across the Eastern Province deploy layered defenses for geographically distributed operational technology networks. Targeted intrusion campaigns against critical infrastructure drive disproportionate security spending per revenue dollar.
- Financial Services:Banks, insurers, and fintechs in Riyadh's financial district prioritize fraud prevention and real-time transaction monitoring. SDAIA coordination with SAMR on cross-border data flows forces architectural redesigns for multinational institutions.
- Government:Ministries and agencies procure through centralized frameworks emphasizing sovereign certification and domestic vendor preference.
- Healthcare:Hospitals and clinics in Jeddah and Dammam lag in security maturity, presenting white space for managed service providers offering bundled compliance packages.
By current spending, Energy vertical leads. By compliance-driven urgency, Financial Services is expanding most quickly.
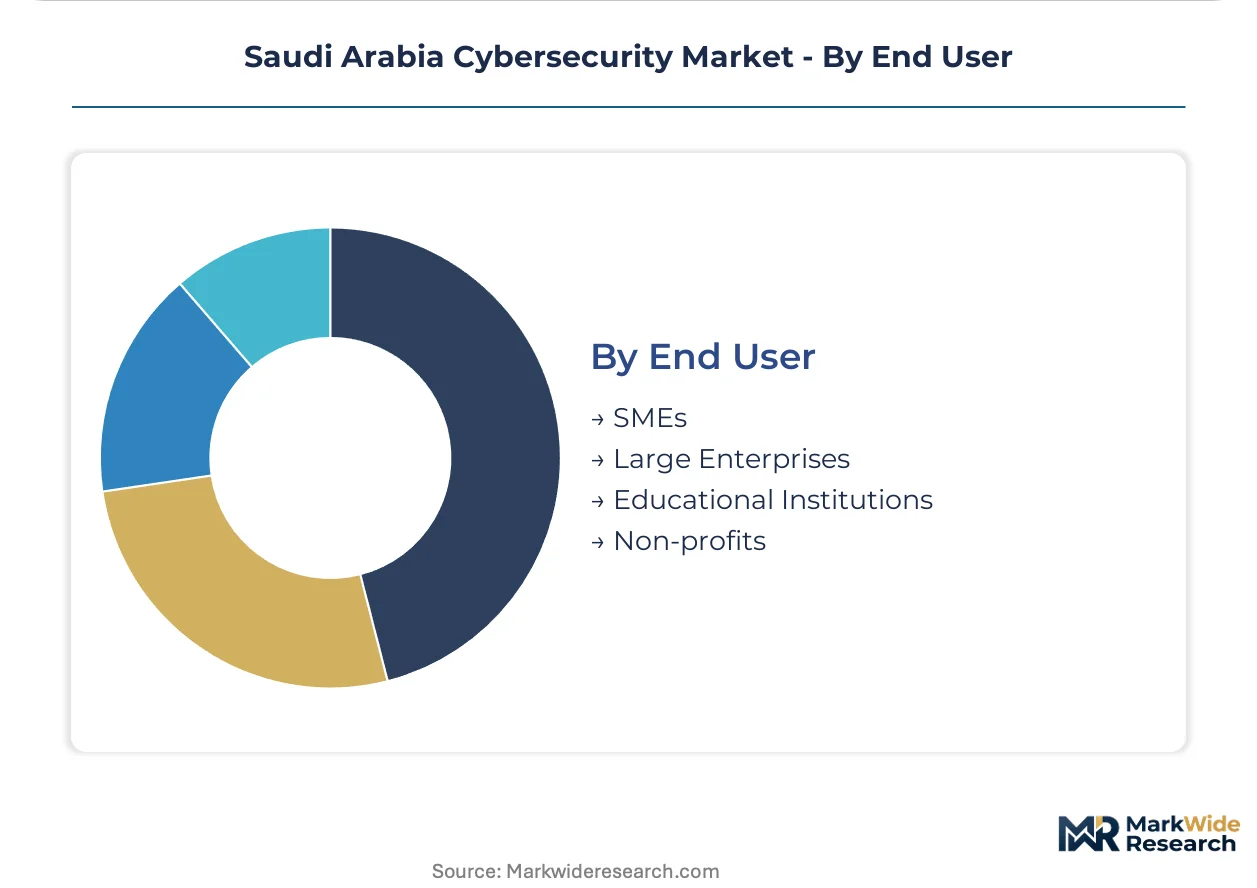
End User:
Customer type determines contract structure: large enterprises negotiate multi-year enterprise licenses, while SMEs and institutions purchase through standardized bundles with implementation support.
- Large Enterprises:Integrated security architectures spanning identity, network, and cloud workloads require dedicated procurement teams and custom professional services. SABIC affiliates and major banking groups operate captive security operations centers with vendor-agnostic tool selection.
- SMEs:Mid-market enterprises in Jeddah and Dammam lack specialized security staff, driving demand for outsourced detection, response, and compliance reporting under single contracts.
- Educational Institutions:Universities and technical colleges face ransomware exposure with limited IT security budgets, favoring subsidized sector-specific frameworks.
- Non-profits:Charitable organizations and cultural foundations represent the smallest addressable pool, typically piggybacking on government-provided security infrastructure.
By contract value, Large Enterprises dominate. By volume growth, SMEs show the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Saudi Arabia's cybersecurity market operates with minimal import dependency for core services, as sovereign certification requirements privilege domestic hosting and local system integrators over foreign hardware vendors. The Kingdom's regulatory framework actively restricts cross-border data flows, redirecting procurement toward NCA-certified domestic operators.
Riyadh
Financial institutions in Riyadh's banking district drive concentrated demand for fraud prevention and real-time transaction monitoring platforms. SAMR data-localization rules compel primary processing on sovereign infrastructure, forcing architectural redesigns for multinational banks. The King Abdullah Financial District anchors compliance-driven security spending with dedicated procurement teams negotiating multi-year enterprise licenses.
Eastern Province
Aramco affiliates and petrochemical operators across Dammam and Jubail Industrial City deploy layered defenses for geographically distributed operational technology networks. Targeted intrusion campaigns against critical infrastructure drive disproportionate security spending per revenue dollar. SABIC's captive security operations centers operate with vendor-agnostic tool selection, compressing procurement timelines for standalone antivirus contracts.
NEOM Northwest
The giga-project's smart city infrastructure generates concentrated demand for industrial control system protection at scale. Endpoint security requirements for operational technology nodes outpace legacy IT deployment models. NCA Essential Cybersecurity Controls mandate baseline protections with defined implementation timelines, accelerating sovereign cloud migration for analytics workloads.
Western Region
Jeddah's healthcare providers and educational institutions lag in security maturity, presenting white space for managed service providers offering bundled compliance packages. Mid-market enterprises in this corridor lack specialized security staff, driving demand for outsourced detection and response under single contracts. Subsidized sector-specific frameworks attract budget-constrained buyers facing ransomware exposure.
Saudi Arabia Cybersecurity Market Competitive Landscape
Concentration sits with sovereign-certified domestic specialists who anchor government contracts through NCA Tier-IV data-center certifications. The vendor base stratifies across three tiers: hyperscaler-aligned platforms with AI-driven analytics, localized managed-security providers serving mid-market verticals, and legacy hardware distributors with established public-sector relationships. M&A activity concentrates on acquiring NCA certification credentials, while strategic partnerships with domestic hosting operators accelerate market access for foreign technology vendors.
Within the sovereign-certified tier, Sirar leverages its domestic data-center infrastructure to anchor government procurement frameworks. Palo Alto Networks sustains premium positioning through AI-native threat-intelligence platforms delivered via localized hosting partnerships. Fast Digital Technology competes on bundled managed-security services for mid-market energy and healthcare clients across the Eastern Province and Western Region.
| Leading Market Players |
|---|
| Sirar |
| Fast Digital Technology |
| Palo Alto Networks |
| Inovasys |
| Advance Datasec |
| Taqnia Cyber |
| Ahlan Cyber |
| Gateway Infotech |
| COGNNA |
| Others |
Value Network & Pricing Analysis
NCA Tier-IV certification gates both vendor qualification and price differentiation simultaneously, concentrating supply among three domestic data-center operators while forcing buyers to pay premiums for sovereign-hosted architectures that satisfy Essential Cybersecurity Controls mandates.
Pricing Analysis
Configured-to-order pricing for customized zero-trust deployments commands premiums of 40-60 percent above standard SaaS tiers. Subscription-based security service bundling now dominates mid-market procurement, displacing perpetual licenses as localized managed-security providers wrap detection, response, and compliance reporting into single contracts. Price differentiation rests on certification grade and after-sales service depth, with NCA-certified vendors capturing margin premiums. Cost compression in the standard SaaS tier intensifies as hyperscaler partnerships proliferate. SMEs in Jeddah and Dammam exhibit highest price sensitivity, while Aramco affiliates and Riyadh financial institutions prioritize sovereign certification over cost.
Supply Chain Analysis
Inventory lead times for NCA-certified hardware appliances extend procurement cycles by 8-12 weeks as only three domestic facilities qualify for Tier-IV sovereign hosting. Supply concentrates in the United States, Israel, and the United Kingdom for advanced threat-intelligence platforms and AI-driven analytics engines. Component dependencies include specialized encryption processors, industrial-hardened endpoint agents, and OT network monitoring sensors. Single-source vulnerability runs through NCA certification bottlenecks, where vendor recertification timelines lag regulatory amendment cycles. Distribution runs through hyperscaler partnerships and local system integrators for cloud deployments, while hardware flows via established distributors with government framework access.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Saudi Arabia's cybersecurity market sits in early-cycle expansion, with NEOM smart city deployments and Essential Cybersecurity Controls compliance deadlines driving penetration well below saturation across mid-market verticals.
For Market Incumbents: Shield government contract anchorage by accelerating NCA amendment response timelines and deepening captive security operations center capabilities. Invest in OT-IT convergence expertise to defend against specialized industrial control system vendors. Prioritize certification investment over price competition in Eastern Province energy corridors. For New Entrants and Emerging Players: Managed security service gaps in Western Region healthcare and education present immediate white-space opportunity. Jeddah's hospital networks and technical colleges lack dedicated security staff, making bundled compliance packages the most penetrable entry point. Pursue partnerships with local system integrators already embedded in SAMR data-localization compliance conversations. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed regional cybersecurity consultancies holding NCA Tier-III certifications and established Eastern Province energy relationships. Long-term viability hinges on sovereign cloud migration tailwinds and SDAIA AI governance standards implementation. Watch NCA amendment acceleration as the critical inflection signal for compliance-driven spending spikes.| Strategic Initiative | Industry Significance |
|---|---|
| NCA Tier-IV Certification Acquisition | Unlocks government framework access and sovereign cloud hosting eligibility for critical infrastructure contracts. |
| OT-IT Security Platform Integration | Addresses Aramco and SABIC demand for unified threat visibility across operational technology networks. |
| Localized Managed Security Service Launch | Captures SME demand in Jeddah and Dammam lacking in-house security operations center capabilities. |
| Hyperscaler Sovereign Cloud Partnership | Satisfies SAMR data-localization requirements for Riyadh financial institutions processing cross-border transactions. |
| AI Governance Compliance Tool Development | Anticipates SDAIA standards for model-risk management in financial sector algorithmic decision systems. |
Research Methodology
Two parallel data streams informed the analysis: structured primary interviews with CISOs at Saudi Aramco affiliates, security procurement leads at Riyadh financial institutions, NCA compliance officers, OT network engineers at SABIC facilities, and managed service provider executives; alongside secondary validation through NCA regulatory filings, SAMR data-localization circulars, SDAIA artificial intelligence governance drafts, hyperscaler sovereign cloud expansion announcements, and SEC disclosures from listed cybersecurity vendors. Bottom-up segment sizing triangulated against top-down macroeconomic indicators.
Across the projection horizon, the analytical framework modeled deployment model transitions, solution type evolution, vertical compliance maturity, and end-user sophistication tiers. CAGRs derived from segment-level growth rate reconciliation and adoption curve positioning. Industry-specific inputs included NCA amendment velocity, NEOM infrastructure build-out schedules, and energy sector OT security budget trajectories.
Underlying assumptions cover regulatory enforcement consistency and sovereign cloud capacity expansion, with deviation risk concentrated in NCA certification timeline compression and specialized talent scarcity constraining implementation velocity. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Smart Grid Cyber Security Market
Cybersecurity
Managed SIEM Service Market
Cybersecurity
Europe Cybersecurity Market
Cybersecurity
Cyber Security Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Cloud Network Security Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Qatar Cybersecurity Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
Hungary Cybersecurity Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Wireless Lan Security Market