
 Cloud Data Loss Prevention Solution Market | 2026-2036
Cloud Data Loss Prevention Solution Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Data Loss Prevention Solution Market Outlook
Capital-intensity divergence between hyperscale platform operators and point-solution vendors is rotating competitive dynamics toward integrated security stacks. Microsoft leverages its Azure-native architecture to embed DLP within broader cloud workloads, while Broadcom sustains enterprise trust through Symantec's established endpoint-to-cloud data protection lineage. Netskope competes by anchoring its offering in zero-trust network access, a capability gap that smaller vendors struggle to close without comparable infrastructure investment.
Cloud Data Loss Prevention solutions encompass policy-driven engines that inspect content in transit, at rest, and in use across distributed cloud environments, employing machine-learning classification, cryptographic tokenization, and contextual access controls to enforce data governance. Their primary commercial purpose is to reduce exfiltration risk and demonstrate compliance to auditors and regulators. Public cloud deployment dominates volume due to SaaS application proliferation, though hybrid cloud configurations capture expanding margin pools as enterprises retain sensitive workloads on-premises while extending controls to multi-tenant infrastructure. Financial services end users drive premium pricing for real-time transaction monitoring integrations, while healthcare organizations represent the fastest-growing adoption segment as telehealth platforms multiply attack surfaces.
FDA 21 CFR Part 11 guidelines for electronic records, HIPAA Security Rule mandates, and the SEC's cybersecurity disclosure rules collectively shape product roadmaps by requiring immutable audit trails and automated incident reporting. The EU AI Act and GDPR cross-border data transfer mechanisms further constrain architecture choices for vendors serving multinational clients. Stakeholders must monitor evolving state-level privacy legislation in the United States, where fragmented regulatory landscapes will determine whether unified policy engines or geography-specific deployments prove more defensible.
Market Dynamics
Machine-learning classification engines are compressing deployment timelines from quarters to weeks, forcing vendors to rearchitect policy engines for real-time SaaS integration rather than batch processing.
Growth Catalysts
- HIPAA Security Rule mandates:Healthcare systems must demonstrate technical safeguards for electronic protected health information, driving automated data discovery and encryption-at-rest requirements.
- Zero-trust architecture adoption:Financial institutions are replacing perimeter-based security with continuous verification models that embed DLP at every data access point.
- Generative AI proliferation:Enterprise deployment of large language models creates novel exfiltration vectors through prompt injection and training data leakage, requiring contextual inspection capabilities.
Market Restraints
- Cloud egress cost volatility:Hyperscale bandwidth pricing unpredictability constrains real-time inspection architectures that require repeated data traversal.
- API rate limiting:SaaS application throttling caps inspection throughput for organizations with high-volume transactional workloads.
- Cross-border data localization:China's data security law and Russia's data localization requirements fragment unified policy enforcement across multinational deployments.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy sectors are extending cloud DLP to industrial IoT data streams, creating demand for protocol-aware inspection of SCADA and Modbus traffic.
- India's Digital Personal Data Protection Act:Cross-border transfer restrictions and consent management mandates are opening deployment opportunities for localized classification engines.
- Confidential computing integration:Hardware-based trusted execution environments are enabling encrypted data processing without decryption exposure, merging with DLP policy enforcement.
Industry Challenges
- Data labeling talent scarcity:Shortage of security engineers capable of tuning machine-learning classifiers for domain-specific sensitive data patterns delays production deployments.
- Legacy mainframe integration:Financial services organizations struggle to extend cloud-native DLP controls to on-premises COBOL-based core banking systems without brittle middleware.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Data Loss Prevention Solution Market |
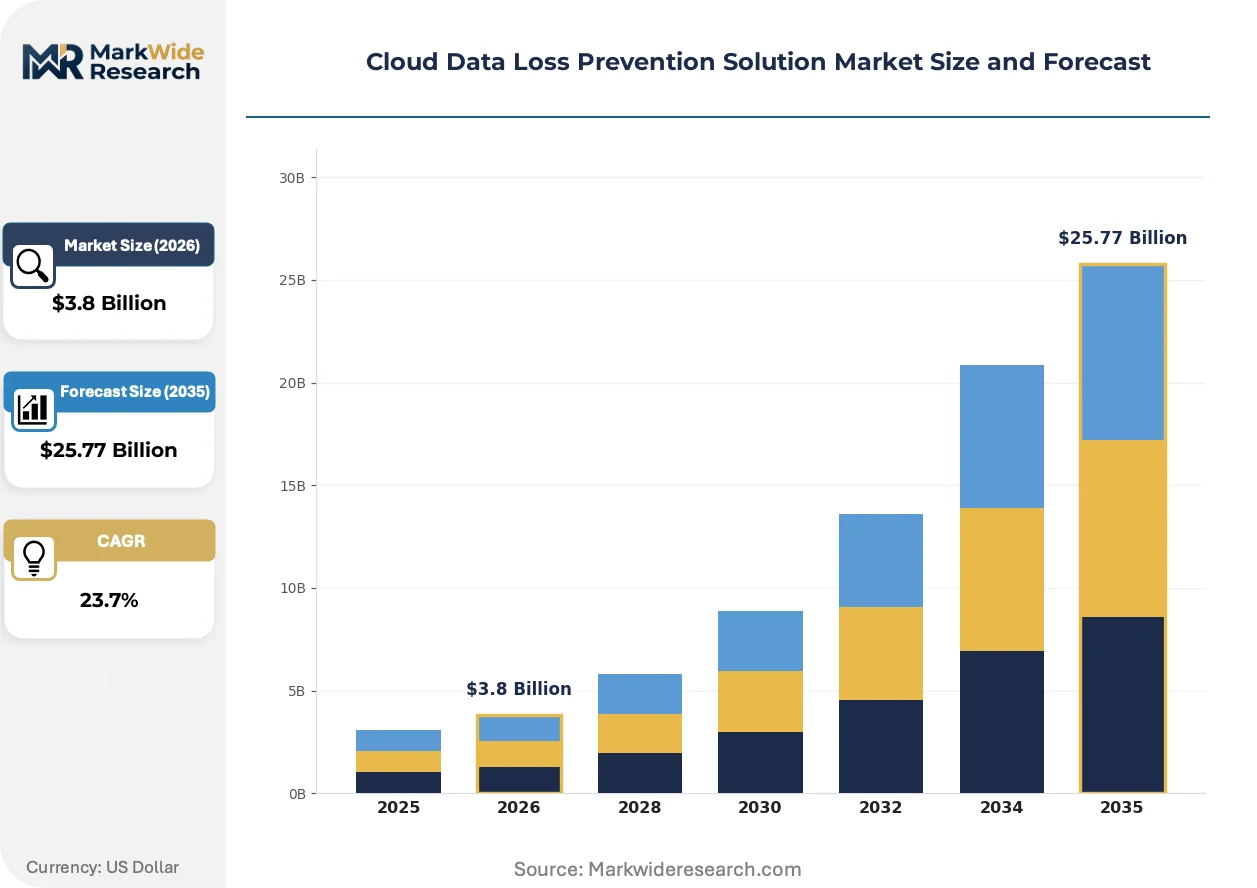
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $25.77 Billion |
| CAGR (2026 – 2036) | 23.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Technology: Content Inspection, User Identity, Data Discovery, Encryption End User: Financial Services, Healthcare, Retail, Government Service Type: Managed Services, Professional Services, Consulting, Training |
| Companies Covered | Microsoft, Broadcom (Symantec), Proofpoint, Forcepoint, Netskope, Varonis, Strac, Cisco Systems, CrowdStrike, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Data Loss Prevention Solution Market Strategic Shifts
Agentless inspection architectures are displacing endpoint-heavy deployments, reshaping how security teams instrument cloud-native applications without code modification or performance degradation.
Natural language processing models trained on regulatory text are miniaturizing compliance mapping from months to days. Healthcare compliance officers at regional hospital networks are deploying these engines to auto-generate HIPAA risk assessments. This compression is eliminating the professional services margin that traditional consultancies captured for manual control framework alignment.
The EU AI Act's risk-based classification system for automated decision-making is mandating algorithmic audit trails for AI systems processing personal data. Financial services firms deploying credit-scoring models must now demonstrate data lineage from training sets through inference outputs. Vendors are responding by embedding immutable logging into MLOps pipelines, with German automotive manufacturers and French insurers representing the most advanced early adopters.
Security procurement committees are consolidating vendor relationships from point-solution portfolios to integrated cloud security platforms. Mid-market enterprises previously buying standalone DLP, CASB, and SWG products now favor unified suites with shared policy engines. This concentration is most pronounced in the United States, where CISOs at technology and professional services firms cite integration cost reduction as the primary selection criterion over best-of-breed functional depth.
Cloud Data Loss Prevention Solution Market Segmentation
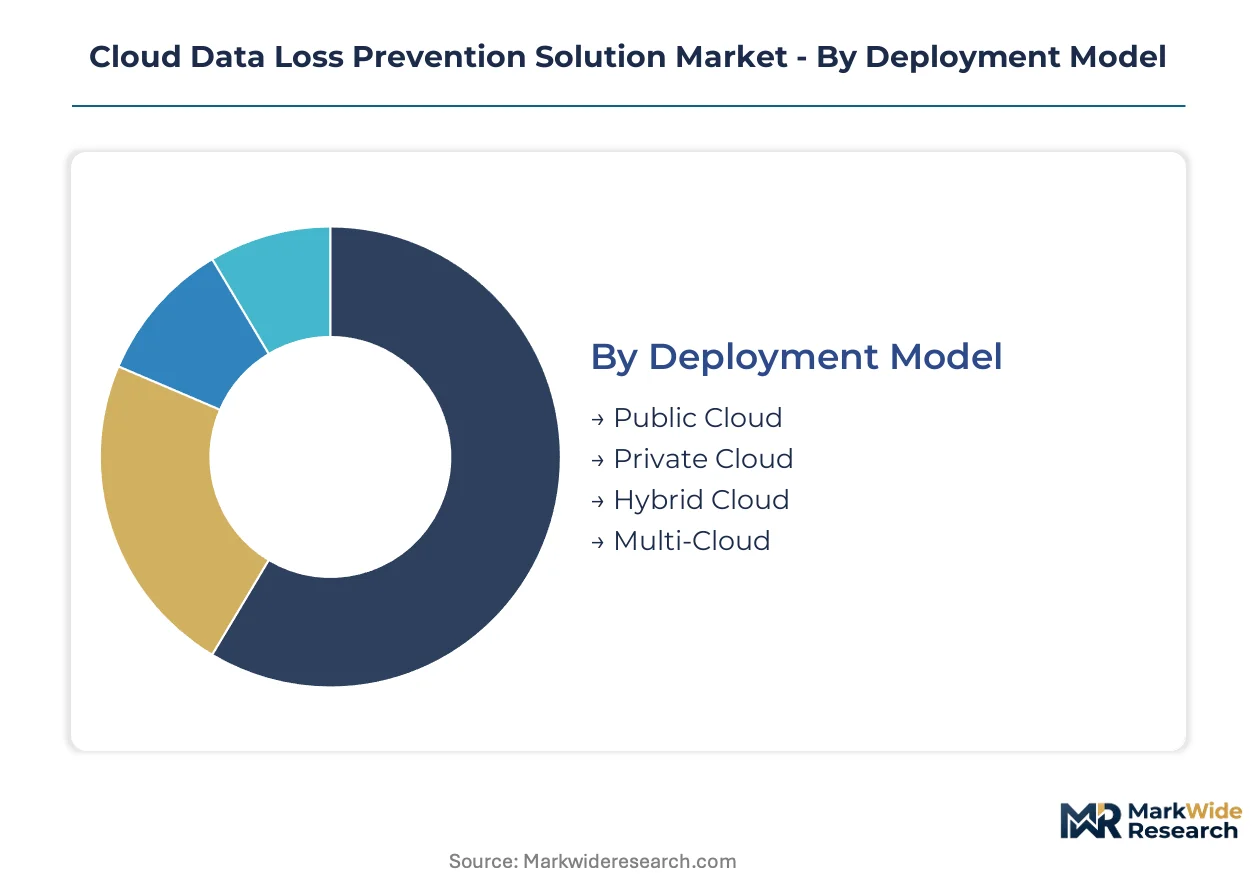
Cloud DLP procurement patterns diverge sharply across deployment architectures and regulatory contexts. Understanding these segment boundaries reveals where vendors must engineer for scale versus customization.
Deployment Model:
Domestic-first segments dominate in regulated industries with data localization mandates, while export-led configurations serve multinational enterprises with distributed footprints.
- Public Cloud:Native SaaS integration enables inspection of Microsoft 365, Salesforce, and Google Workspace traffic without on-premises infrastructure. Healthcare systems in the United States deploy this model for telehealth platforms subject to HIPAA Security Rule technical safeguards, though egress cost volatility constrains real-time inspection at scale.
- Hybrid Cloud:Split architectures retain sensitive workloads on-premises while extending policy enforcement to multi-tenant infrastructure. Financial services institutions in Germany and France favor this approach to satisfy GDPR data residency requirements while maintaining cloud agility for non-sensitive operations.
- Private Cloud:Single-tenant deployments serve defense contractors and intelligence agencies with air-gapped classification engines.
- Multi-Cloud:Unified policy orchestration across AWS, Azure, and Google Cloud addresses vendor lock-in concerns for technology sector enterprises.
Public Cloud holds the largest share; momentum sits with Hybrid Cloud as data sovereignty requirements multiply.
Technology:
Cost-tier stratification separates premium ML-driven engines from baseline pattern-matching tools, with pricing scaling linearly against inspection throughput.
- Content Inspection:Deep packet analysis and natural language processing identify sensitive data in motion across email, web, and API channels. Retailers processing payment card data deploy these engines to satisfy PCI-DSS requirements, with real-time tokenization replacing legacy batch scanning.
- Data Discovery:Automated scanning of object storage, databases, and collaboration platforms maps data lineage for compliance audits. Healthcare organizations expanding telehealth services rely on discovery tools to locate patient records across shadow IT environments before exfiltration occurs.
- User Identity:Behavioral analytics tie data access patterns to individual credentials for insider threat detection.
- Encryption:Key management and tokenization services protect data at rest without compromising searchability.
Content Inspection commands premium pricing; Data Discovery is climbing the fastest as data sprawl outpaces manual inventory efforts.
End User:
Application-specific requirements drive divergent feature priorities, with transaction velocity demands separating financial services from document-centric healthcare workflows.
- Financial Services:Real-time monitoring of SWIFT messages, trading algorithms, and customer payment flows demands sub-millisecond inspection latency. Institutions subject to SEC cybersecurity disclosure rules invest heavily in immutable audit trails that demonstrate data governance to regulators.
- Healthcare:Electronic protected health information protection under HIPAA drives automated classification of unstructured clinical notes and imaging metadata. Regional hospital networks expanding telehealth platforms represent the steepest expansion trajectory as attack surfaces multiply.
- Retail:PCI-DSS compliance for cardholder data environments shapes deployment of point-of-sale integrated DLP.
- Government:FedRAMP authorization requirements and classified information handling protocols constrain vendor selection to cleared providers.
Financial Services contributes the highest revenue per deployment; Healthcare is gaining share fastest.
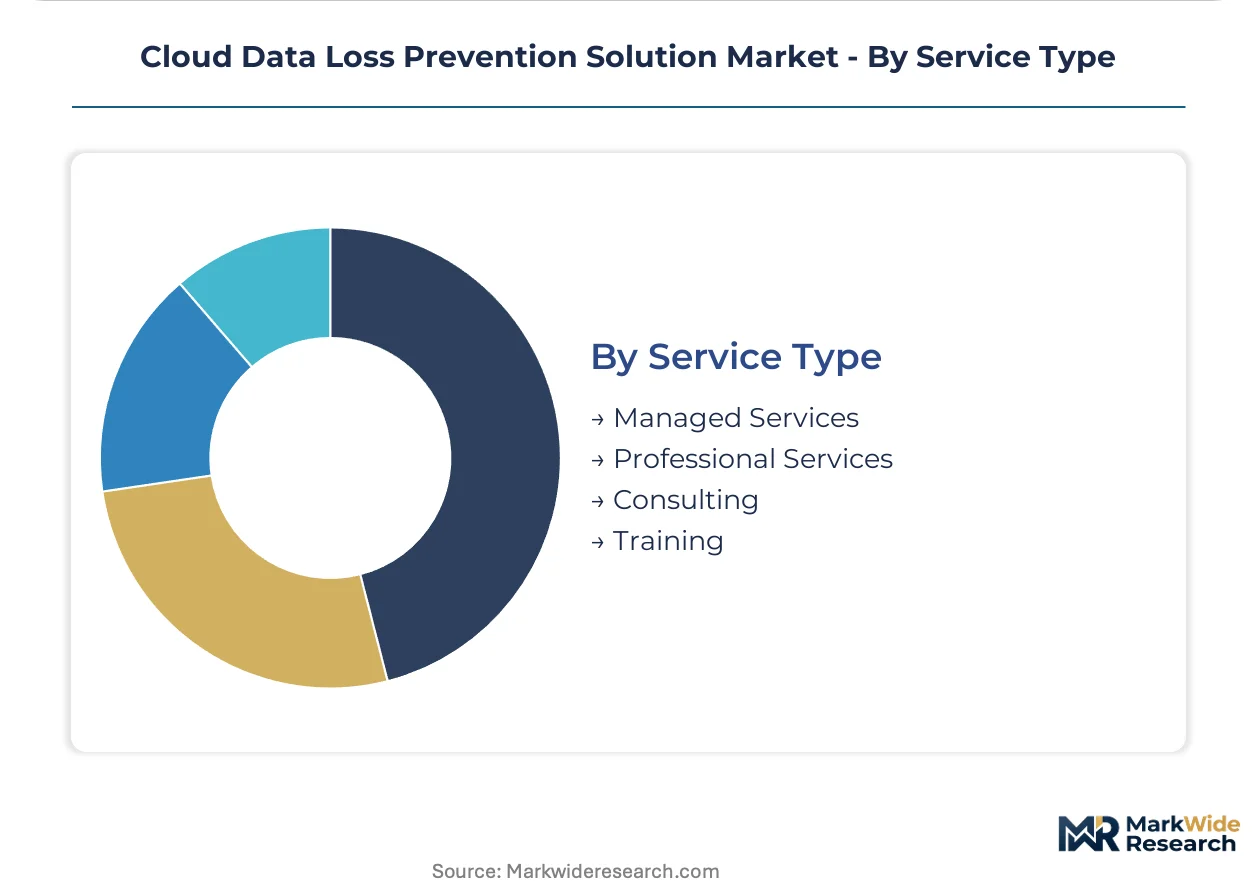
Service Type:
Customer maturity determines services mix, with early-stage buyers requiring consulting-heavy engagements and mature operations shifting to managed detection and response.
- Managed Services:24/7 security operations center monitoring of DLP alerts, false-positive tuning, and incident response execution. Mid-market enterprises lacking internal security engineering capacity outsource policy maintenance to achieve HIPAA and GDPR compliance without headcount expansion.
- Professional Services:Custom policy development, legacy system integration, and compliance framework mapping for complex environments. Financial services organizations modernizing COBOL-based core banking systems require specialized engagement to extend cloud-native controls.
- Consulting:Risk assessment and control framework design preceding technology procurement.
- Training:Security awareness and analyst certification programs for internal SOC teams.
Managed Services holds the largest share; Professional Services sees strongest demand from regulated industries with legacy infrastructure debt.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Buyers in the United States demonstrate the lowest price elasticity for cloud DLP solutions, absorbing premium pricing for integrated security stacks, while procurement committees in India and Southeast Asia prioritize cost-optimized point solutions despite higher integration overhead.
United States
Federal cloud migration mandates and SEC cybersecurity disclosure rules drive sustained enterprise procurement. HIPAA Security Rule enforcement accelerates healthcare system adoption of automated data classification. The Washington D.C.-Northern Virginia corridor concentrates defense contractor and intelligence agency deployments requiring FedRAMP-authorized private cloud configurations.
Germany
GDPR data residency requirements and the EU AI Act's risk-based classification system shape hybrid cloud procurement patterns. German automotive manufacturers in Bavaria lead confidential computing integration for algorithmic audit trails. Frankfurt's financial services cluster demands sub-millisecond inspection latency for real-time transaction monitoring.
United Kingdom
Post-Brexit data transfer mechanisms and Financial Conduct Authority operational resilience rules drive financial services investment. NHS Digital's patient record protection mandates accelerate telehealth platform security spending. London's technology and professional services firms consolidate vendor relationships toward unified cloud security suites.
India
The Digital Personal Data Protection Act's cross-border transfer restrictions open localized classification engine opportunities. Mid-market enterprises lacking internal security engineering capacity outsource policy maintenance to managed service providers. Bangalore's technology sector and Mumbai's financial services cluster represent contrasting deployment maturity profiles.
Japan
METI's cybersecurity framework revisions and financial sector operational continuity requirements sustain premium pricing for integrated platforms. Manufacturing and energy sectors extend cloud DLP to industrial IoT data streams. Tokyo's insurance and automotive headquarters lead MLOps pipeline logging for AI system auditability.
Cloud Data Loss Prevention Solution Market Competitive Environment
Technology leadership and cost leadership are held by different player archetypes, with hyperscale platform operators embedding DLP within broader cloud workloads while point-solution vendors compete on specialized inspection depth. The market exhibits tiered consolidation around integrated security stacks, mid-market suites, and niche compliance specialists. Dominant competitive moves include strategic partnerships with SaaS application providers and portfolio diversification through CASB and zero-trust network access integration.
Within the integrated platform tier, Microsoft and Broadcom exemplify divergent approaches to enterprise trust architecture. Netskope occupies a position anchoring competitive differentiation in zero-trust network access capabilities that smaller vendors struggle to replicate without comparable infrastructure investment. These three represent the primary competitive anchors shaping procurement committee evaluation criteria across regulated industries.
| Leading Market Players |
|---|
| Microsoft |
| Broadcom (Symantec) |
| Proofpoint |
| Forcepoint |
| Netskope |
| Varonis |
| Strac |
| Cisco Systems |
| CrowdStrike |
| Others |
Value Chain & Pricing Dynamics
Agentless inspection architectures replacing endpoint-heavy deployments simultaneously redistribute engineering talent toward India and Eastern Europe while compressing implementation margins that previously sustained professional services revenue. This substitution reshapes vendor cost structures and client procurement economics across deployment models.
Pricing Analysis
Managed service contracts and multi-year subscription renewals drive lifetime value beyond initial SaaS licensing. Three-tier pricing structure across premium, standard, and economy levels segments by inspection throughput volume and ML classification sophistication. Cost compression in the standard tier is intensifying because hyperscale cloud providers bundle baseline DLP with existing enterprise agreements. Mid-market healthcare organizations demonstrate highest price sensitivity, while financial services institutions in Frankfurt and New York absorb premium pricing for sub-millisecond latency guarantees.
Supply Chain Analysis
Container availability fluctuations on Asia-Pacific trade lanes intermittently delay hardware security module deliveries for confidential computing integrations. Engineering talent concentrates in the United States, Israel, and Ireland, with Bangalore and Warsaw emerging as secondary development hubs. The supply chain draws from specialized semiconductor foundries in Taiwan, cryptographic hardware manufacturers in Germany, and cloud infrastructure operators across multiple jurisdictions. Single-source vulnerability in ML training data annotation services threatens deployment timelines. Distribution runs through direct enterprise sales teams supplemented by hyperscaler marketplace listings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The market sits at an inflection where generative AI deployment creates novel exfiltration vectors, accelerating procurement cycles from quarters to weeks.
For Market Incumbents: Secure zero-trust network access integration capabilities to defend against CASB-native competitors eroding standalone DLP margins. Invest in FedRAMP and EU sovereign cloud certifications to maintain eligibility for defense and public sector contracts. Consolidate policy engines across CASB, SWG, and DLP modules to reduce integration costs that drive mid-market churn. For New Entrants and Emerging Players: Lead with confidential computing integration for healthcare and financial services clients requiring algorithmic audit trails under the EU AI Act. Target India's mid-market enterprises outsourcing policy maintenance under the Digital Personal Data Protection Act. Pursue managed service provider partnerships to bypass direct sales infrastructure requirements. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors integrated platform operators over point-solution specialists. Acquisition candidates demonstrating MLOps pipeline logging and immutable data lineage capabilities command strategic premiums. Monitor SEC cybersecurity disclosure enforcement intensity as a signal for accelerated enterprise procurement.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifying DLP, CASB, and SWG modules reduces CISO integration cost concerns in US technology firms. |
| Confidential Computing Partnership | Hardware-based trusted execution environments address EU AI Act audit trail mandates for German automotive manufacturers. |
| Managed Service Expansion | 24/7 SOC monitoring captures mid-market healthcare organizations lacking HIPAA compliance engineering capacity. |
| Zero-Trust Architecture Embedding | Continuous verification models align with NIST guidelines driving US federal cloud migration mandates. |
| Regulatory Certification Investment | FedRAMP and GDPR sovereign cloud authorizations unlock defense contractor and European public sector procurement. |
Study Parameters
A standing panel of CISOs, cloud security architects, compliance officers, and managed service provider executives provided ongoing calibration against deployment realities. Primary fieldwork combined structured interviews with secondary validation through SEC cybersecurity disclosure filings, hyperscaler capex reports, and regulatory enforcement databases. Bottom-up sizing of vendor-reported subscription revenue triangulated against top-down enterprise IT security budget allocations.
Consistency checks against external benchmarks validated projections across deployment models, organization size tiers, vertical industries, integration complexity levels, and regional adoption patterns. CAGRs derived from segmented growth rate analysis applied across the projection horizon. Forecast inputs incorporated HIPAA enforcement intensity, EU AI Act implementation timelines, and cloud egress pricing trajectories from major hyperscalers.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement pressure and hyperscaler pricing stability would require recalibration. Model assumptions reflect current technology adoption curves and compliance mandate implementation schedules. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Software Defined Perimeter (SDP) Market
Security Software
Global Privileged Access Management (PAM) Solutions Market
Security Software
User Provisioning Software Market
Security Software
Battery-Powered Doorbell Camera Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
US Hardware Encryption Market
Security Software
Fraud Detection Software Market
Security Software
Secure Flash Drive Market
Security Software
Secaas Market
Security Software
Global Email Verification Tools Market
Security Software
Global Data Masking Market
Security Software
Global SMS Firewall Market
Security Software
Unified Threat Management (UTM) Market
Security Software
Global Security Software in Telecom Market
Security Software
Software Assurance Market
Security Software
Security Testing Market