
 Devsecops Market | 2026-2036
Devsecops Market Size, Share, and Industry Trends Forecast 2026-2036
Devsecops Market Intelligence
The transition from outsourced security audits to integrated, in-house DevSecOps capabilities is realigning the competitive landscape. Microsoft leverages its Azure platform to offer a deeply integrated toolchain for developers. Synopsys specializes in application security testing solutions that embed directly into CI/CD pipelines. GitLab differentiates by providing a single application for the entire software development lifecycle, including security.
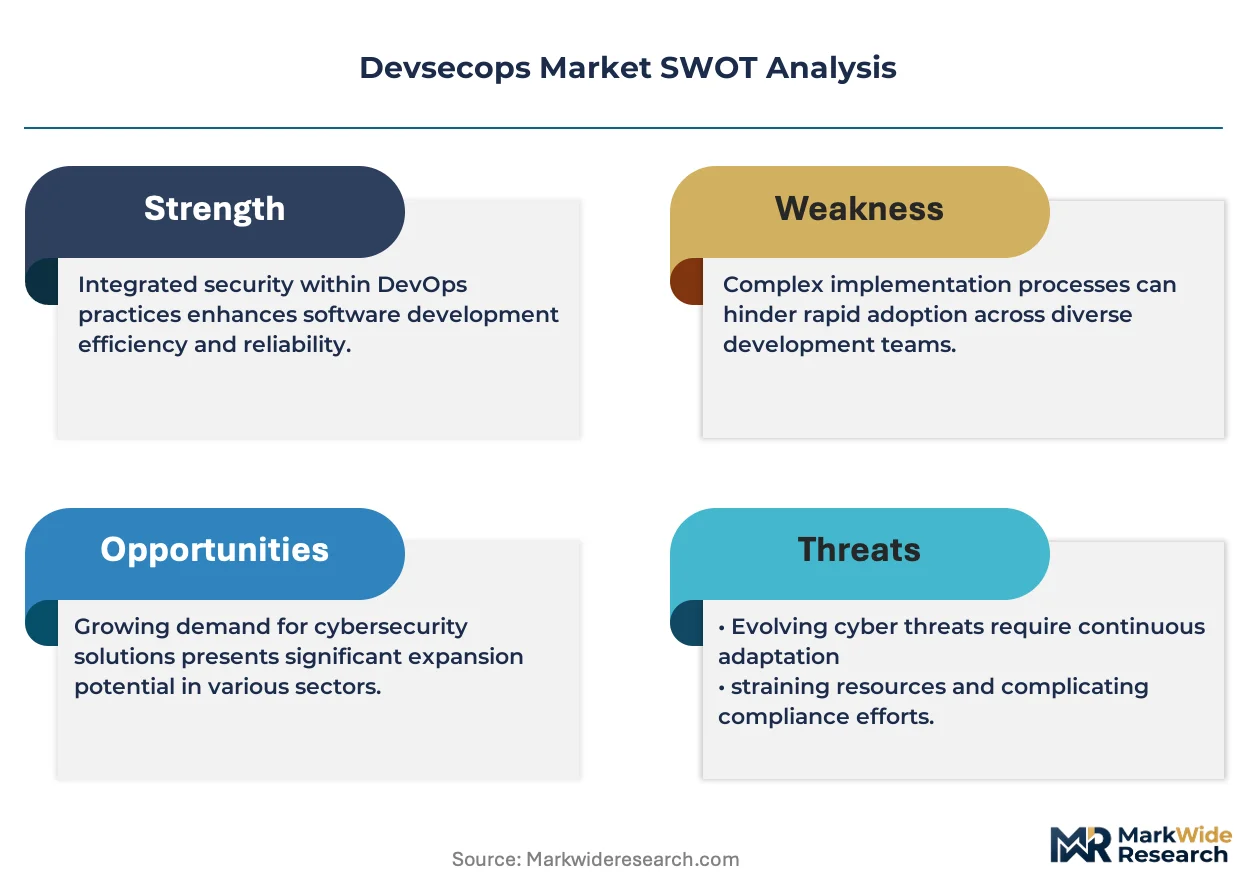
DevSecOps is a methodology that automates the integration of security at every phase of the software development lifecycle. Its primary purpose is to build secure applications by embedding security controls, like static application security testing (SAST), directly into the continuous integration and continuous delivery (CI/CD) pipeline. Among solution offerings, vulnerability management and compliance monitoring tools see high uptake. Financial institutions and government agencies represent the largest end-user segments, driven by stringent data protection requirements.
Compliance with regulations such as the EU's GDPR and the US's HIPAA necessitates a documented, security-by-design approach. These frameworks mandate data protection and privacy controls, directly shaping demand for automated compliance monitoring solutions within development workflows. The critical decision for enterprises now centers on standardizing with a single-vendor platform versus integrating best-of-breed tools for specific security functions.
Market Dynamics
The core structural force shaping the DevSecOps market is the compression of development cycles by CI/CD methodologies. This acceleration makes traditional, post-development security audits untenable, forcing the integration of automated security controls directly into developer workflows and tooling.
Growth Catalysts
- Regulatory Mandates:Frameworks like the EU's GDPR and the US's HIPAA compel organizations to adopt security-by-design principles, directly driving investment in auditable and automated compliance tools within the development lifecycle.
- Financial Sector Transformation:The rapid digitization of banking and fintech services creates a massive attack surface, necessitating the adoption of robust DevSecOps practices to protect sensitive financial data and maintain customer trust.
- CI/CD Pipeline Proliferation:The widespread adoption of continuous integration and continuous delivery pipelines creates a natural integration point for automated security tools, making DevSecOps a logical extension of modern software development practices.
Market Restraints
- Toolchain Complexity:Integrating a diverse set of security tools from multiple vendors into a seamless CI/CD pipeline creates significant technical overhead and interoperability challenges, slowing adoption for some organizations.
- Specialized Talent Scarcity:A persistent shortage of professionals with dual expertise in software development and cybersecurity creates a bottleneck, increasing labor costs and limiting the pace of in-house capability development.
- Legacy System Inertia:Large enterprises with significant investments in monolithic, legacy applications face substantial difficulty and cost in retrofitting them for modern DevSecOps workflows, limiting market penetration in these environments.
Strategic Opportunities
- AI-Powered Security Tools:The convergence of artificial intelligence with security testing offers opportunities for creating predictive threat modeling and autonomous remediation tools that can identify vulnerabilities before they are coded.
- Emerging Geographic Markets:Rapidly digitizing economies in Southeast Asia and Latin America, particularly in their e-commerce and fintech sectors, represent underpenetrated markets for DevSecOps solution providers.
- Securing AI/ML Pipelines:As enterprises increasingly build and deploy machine learning models, a new opportunity emerges for specialized DevSecOps solutions tailored to the unique security needs of MLOps workflows.
Industry Challenges
- Cultural Resistance:Overcoming the traditional divide between development, security, and operations teams remains a primary operational challenge, requiring significant organizational change management to foster a collaborative culture.
- Measuring Security ROI:Quantifying the return on investment for DevSecOps initiatives in concrete financial terms is difficult, making it challenging to secure executive buy-in and budget for non-revenue-generating security functions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Devsecops Market |
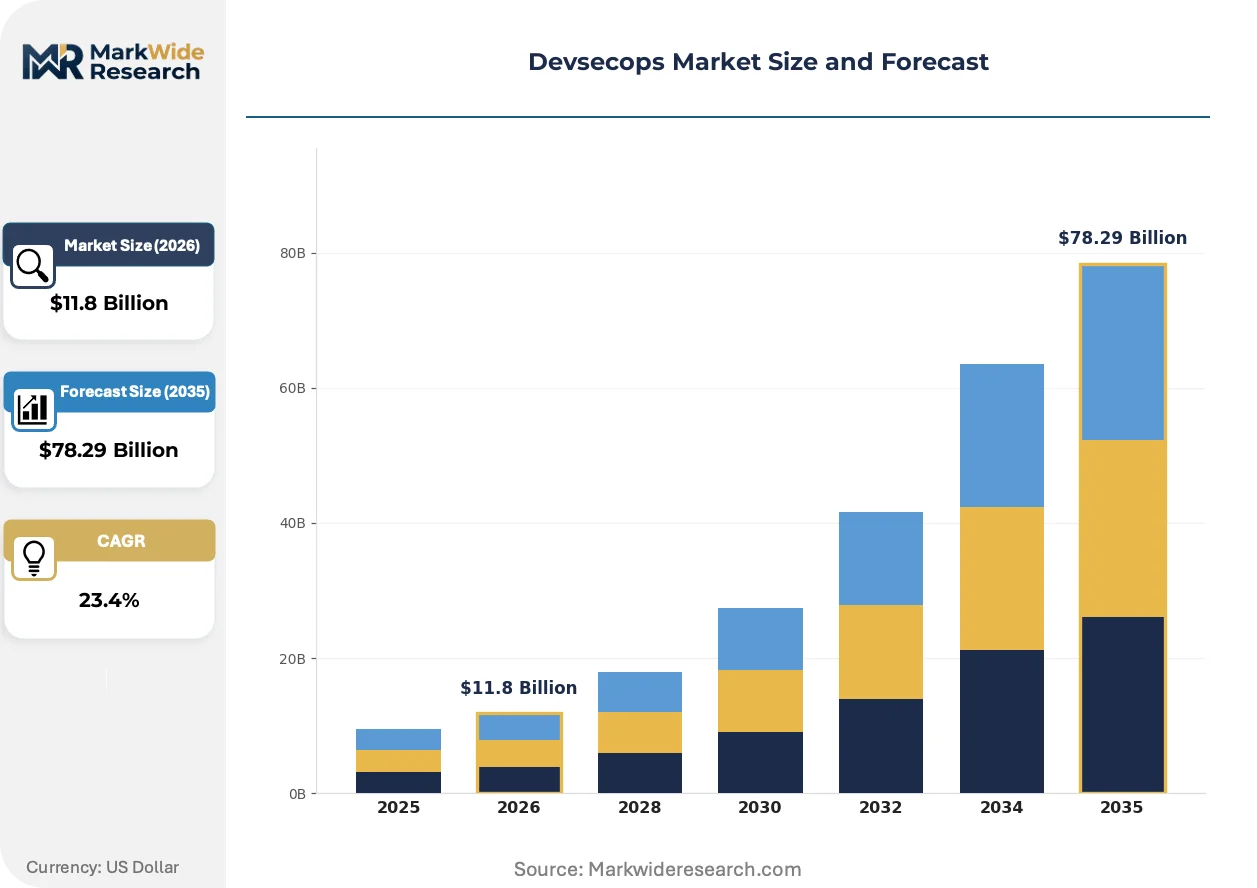
| Market Size in 2026 | $11.8 Billion |
| Market Size in 2035 | $78.29 Billion |
| CAGR (2026 – 2036) | 23.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Type: Cloud-Based, On-Premises, Hybrid Cloud, Edge Computing Solution Offering: Risk Assessment, Vulnerability Management, Compliance Monitoring, Identity & Access Management, Threat Intelligence Application: Continuous Integration, Continuous Delivery, Security Automation, Incident Response, Code Review End User: Financial Institutions, Government Agencies, Technology Providers, Telecommunication Companies, E-commerce Firms |
| Companies Covered | IBM, Microsoft, Google, Palo Alto Networks, Synopsys, Aqua Security, Checkmarx, Snyk, GitLab, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Devsecops Market Strategic Shifts & Innovations
The market's evolution is defined by a push towards greater automation and intelligence to manage the escalating complexity of software supply chains. This shift prioritizes proactive security measures and embedded visibility over reactive, post-deployment fixes, fundamentally altering security team functions.
Software Bill of Materials (SBOM) automation provides a detailed, machine-readable inventory of all components, libraries, and dependencies within a software application. Regulated industries and government bodies are accelerating its adoption to enhance software supply chain transparency. Automated SBOM generation is expanding into dynamic vulnerability management, linking static component lists directly to real-time threat intelligence feeds for continuous risk assessment.
The US Executive Order on Improving the Nation's Cybersecurity establishes new, stringent standards for software sold to federal agencies. This policy directly mandates the use of secure software development practices, including providing SBOMs and evidence of vulnerability testing. Consequently, software vendors targeting the vast US public sector are compelled to integrate and document verifiable DevSecOps processes throughout their development lifecycles.
A clear behavioral change is emerging as mature organizations move from standardized, single-vendor platforms toward a more flexible, integrated toolchain. This trend disrupts the all-in-one suite model, favoring a curated stack of best-of-breed tools for specific functions like static analysis, dynamic analysis, and container scanning. This preference for specialized, API-first tools is most pronounced within large technology firms in the United States and Germany.
Devsecops Market Segmentation
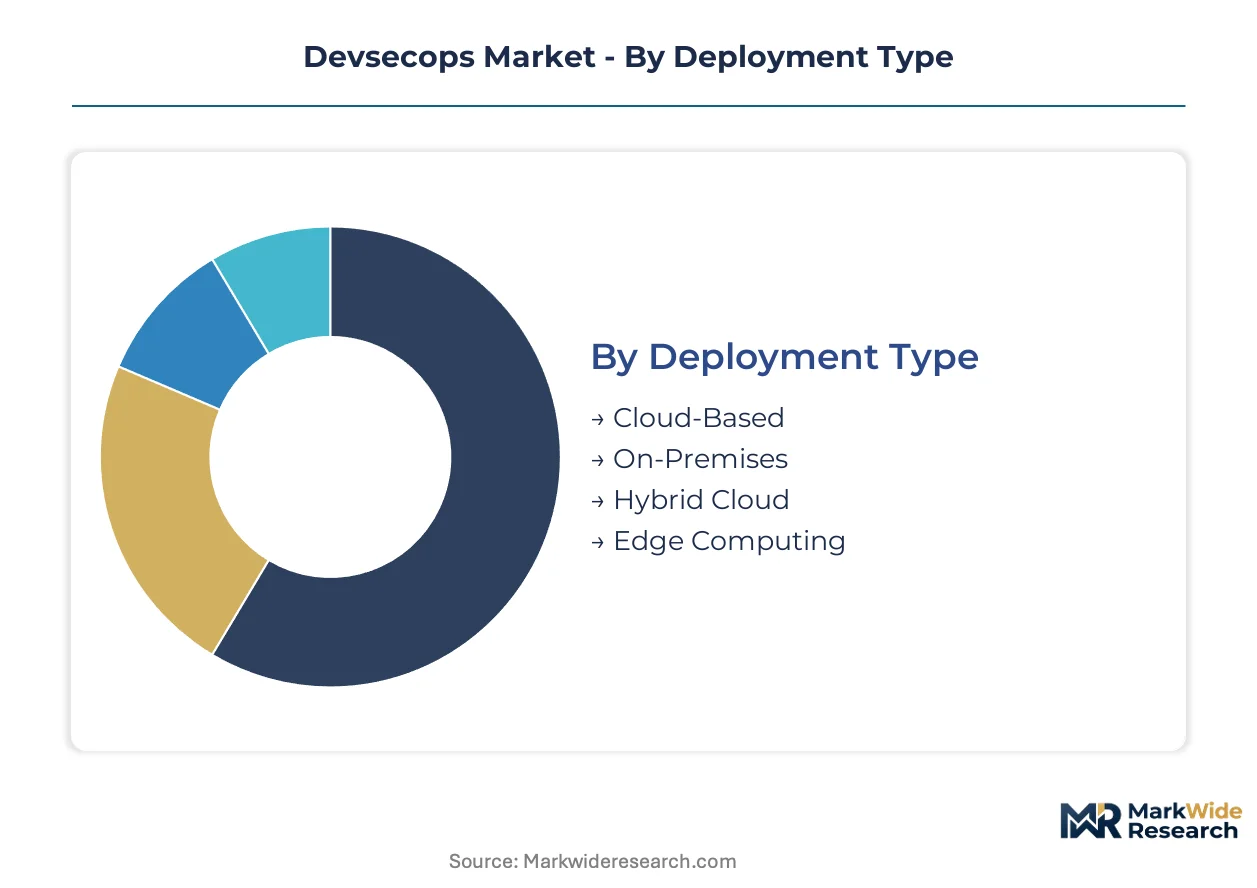
The DevSecOps market segments provide a structured view of how security solutions are delivered and consumed across various operational contexts. Understanding these distinctions is crucial for solution providers to align their offerings with specific enterprise needs and regulatory compliance requirements. Each segment reflects unique technological demands and adoption patterns within the evolving software development landscape.
Deployment Type:
The DevSecOps market categorizes deployment methods based on infrastructure and operational control, influencing data residency and scalability. Enterprises choose deployment models based on their existing IT infrastructure, security policies, and regulatory obligations.
- Cloud-Based:This deployment model leverages public or private cloud infrastructure to host DevSecOps tools and services. It offers scalability, reduced infrastructure overhead, and accessibility, making it attractive for agile development teams and organizations prioritizing rapid deployment.
- On-Premises:On-premises solutions are installed and operated within an organization's own data centers. This option provides maximum control over data and security, often preferred by highly regulated industries like financial institutions and government agencies for stringent data sovereignty requirements.
- Hybrid Cloud:Hybrid cloud deployments combine elements of both on-premises and cloud infrastructure, allowing organizations to manage sensitive workloads locally while leveraging cloud resources for flexibility. This model supports complex enterprise environments that require a balance of control and scalability.
- Edge Computing:Edge computing deployments process data closer to its source, minimizing latency and bandwidth use. This model is gaining traction for DevSecOps in scenarios involving IoT devices or distributed industrial control systems, where real-time security analysis is critical.
Mature deployment sits with On-Premises solutions. Newer deployment is concentrated in Hybrid Cloud environments.
Solution Offering:
Solution offerings address distinct security functions across the development lifecycle, enabling organizations to embed specific security controls. These tools range from proactive vulnerability identification to continuous compliance validation, supporting a holistic security posture.
- Vulnerability Management:These solutions identify, assess, and remediate security weaknesses within applications and infrastructure. They integrate directly into CI/CD pipelines to provide continuous scanning and reporting, crucial for maintaining application integrity against evolving threats.
- Compliance Monitoring:Compliance monitoring tools automate the process of verifying adherence to regulatory standards like GDPR and HIPAA. They provide auditable records and real-time alerts, essential for financial institutions and government agencies navigating complex legal frameworks.
- Risk Assessment:Risk assessment tools evaluate potential security threats and their impact on software projects and organizational assets. They help prioritize remediation efforts by quantifying risk exposure, guiding strategic security investments.
- Identity & Access Management:These solutions manage digital identities and control user access to systems and data throughout the development process. They ensure only authorized personnel and services can interact with sensitive code and environments.
- Threat Intelligence:Threat intelligence platforms collect and analyze data on emerging cyber threats, vulnerabilities, and attack patterns. They provide actionable insights to security teams, enhancing predictive capabilities and proactive defense strategies.
Vulnerability Management solutions currently drive significant market expansion. Threat Intelligence applications are gaining share fastest.
Application:
Application segments define how DevSecOps tools integrate into existing development and operational workflows, ensuring security is an intrinsic part of software delivery. These applications streamline security tasks, making them an inseparable component of modern development practices.
- Security Automation:Security automation involves integrating automated security checks and processes into the CI/CD pipeline, reducing manual effort and accelerating feedback loops. This application is foundational for achieving true DevSecOps, enabling continuous security validation.
- Continuous Integration:DevSecOps tools within continuous integration environments automatically scan code for vulnerabilities as developers commit changes. This early detection mechanism prevents security flaws from propagating further into the development lifecycle.
- Continuous Delivery:In continuous delivery, security checks are automated before applications are released to production, ensuring only secure code reaches end-users. This includes automated penetration testing and configuration audits, verifying deployment integrity.
- Incident Response:Incident response applications within DevSecOps frameworks help teams quickly detect, analyze, and contain security breaches or incidents. They facilitate rapid remediation and post-mortem analysis, minimizing impact.
- Code Review:Automated code review tools analyze source code for potential security vulnerabilities, coding standard violations, and quality issues. These tools support developers in writing more secure and robust applications from the outset.
Security Automation is central to current DevSecOps adoption. Incident Response tools demonstrate a steep expansion trajectory.
End User:
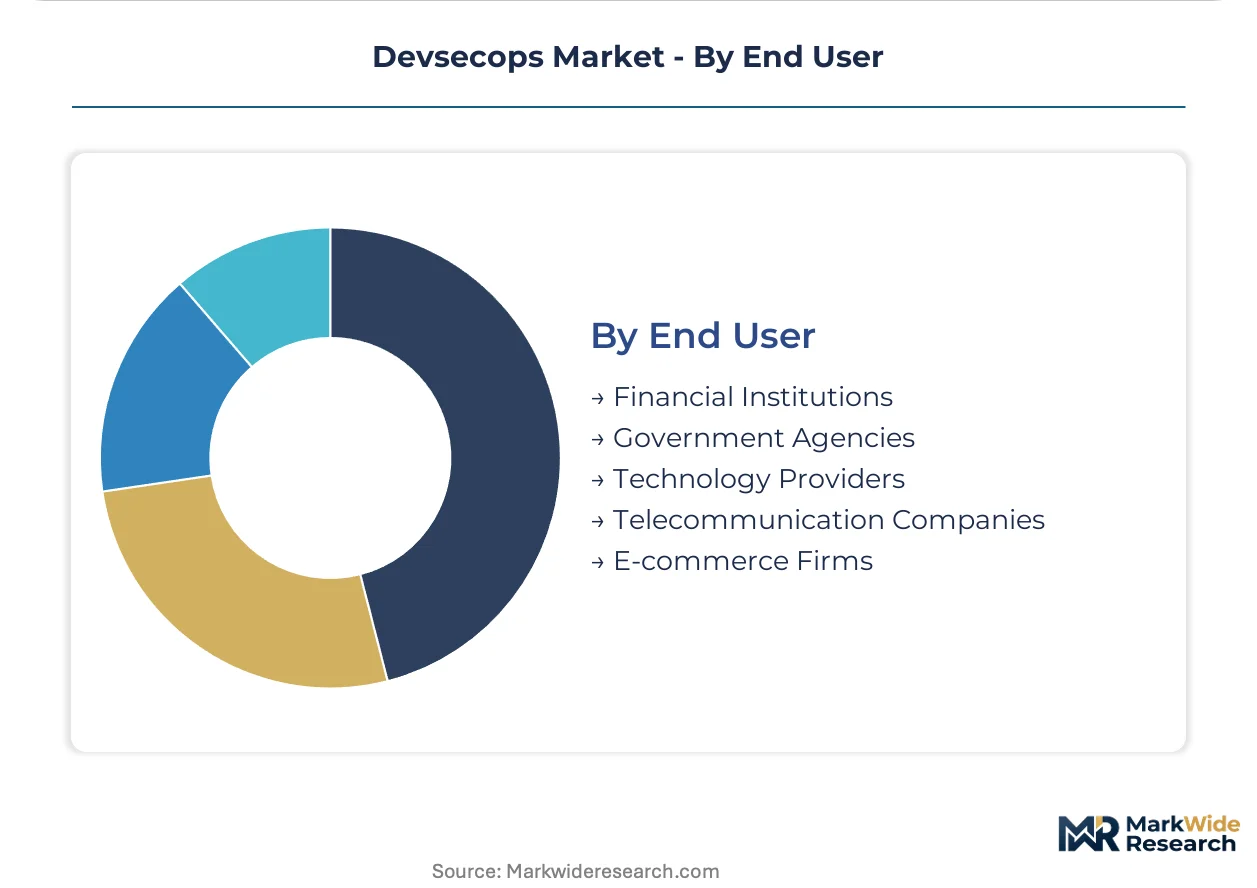
End-user segmentation reflects the varying security demands and regulatory pressures across different industries, influencing the adoption and customization of DevSecOps solutions. Each sector presents unique challenges and priorities for securing its software assets.
- Financial Institutions:Banks, insurance companies, and fintech firms require robust DevSecOps practices to protect sensitive customer data and comply with stringent regulations like GDPR and HIPAA. Their high-value transactions necessitate advanced security controls and continuous monitoring.
- Government Agencies:Public sector entities demand secure software development to safeguard national security data and critical infrastructure. The US Executive Order on Improving the Nation's Cybersecurity directly mandates secure development practices for federal software procurement.
- Technology Providers:Software companies and IT service providers adopt DevSecOps to ensure the security of their own products and services delivered to clients. They often lead in integrating advanced security features into their development pipelines.
- Telecommunication Companies:Telecom firms manage vast networks and sensitive customer communication data, requiring comprehensive DevSecOps to secure their infrastructure and applications. Their complex systems benefit from automated security integration.
- E-commerce Firms:Online retailers handle large volumes of personal and payment information, making them prime targets for cyberattacks. DevSecOps helps these firms build secure shopping platforms and protect customer trust.
Financial Institutions represent the largest end-user segment for DevSecOps. E-commerce Firms are climbing the fastest in adoption.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand for DevSecOps solutions notably concentrates within technology sectors across key global economies. Financial institutions and government agencies represent significant end-user segments, driven by stringent data protection requirements. This regional emphasis underscores the critical need for integrated security practices in software development.
United States
The United States exhibits strong demand for DevSecOps from its expansive technology sectors and government agencies. The US Executive Order on Improving the Nation's Cybersecurity mandates secure development practices for federal software procurement. Silicon Valley and Washington D.C. drive innovation and adoption, integrating advanced security tools.
Germany
Germany's technology sectors and financial institutions show substantial DevSecOps demand, propelled by digitalization initiatives. Compliance with the EU's GDPR and the upcoming EU AI Act necessitates robust data protection. Technology hubs in Munich and Berlin actively embed security automation into CI/CD pipelines for critical enterprise applications.
Japan
Japanese financial services and automotive industries require enhanced DevSecOps capabilities to protect sensitive data and intellectual property. METI guidelines for cybersecurity reinforce the need for secure-by-design approaches. Technology firms in Tokyo and Osaka increasingly adopt automated security testing tools to streamline development processes.
India
India's rapidly expanding fintech and IT services sectors create significant demand for integrated DevSecOps practices. RBI guidelines for financial data protection encourage secure software development. Bangalore and Hyderabad, as major IT hubs, are witnessing a surge in DevSecOps adoption to secure digital transformation projects.
United Kingdom
The United Kingdom's strong financial services and government digital services sectors drive DevSecOps implementation. UK GDPR compliance and NCSC guidelines for secure software supply chains emphasize proactive security measures. London and Manchester tech ecosystems integrate advanced vulnerability management and compliance monitoring solutions.
Devsecops Market Key Industry Players
Strategic partnerships and portfolio diversification dominate the current landscape, as companies seek to offer comprehensive DevSecOps solutions or integrate specialized tools. The market exhibits a fragmented structure with various providers catering to specific security needs across the software development lifecycle. Three strategic archetypes emerge: integrated platform providers, best-of-breed tool specialists, and cloud infrastructure vendors offering native security services. These players focus on expanding their toolchain capabilities and geographic reach.
Within the integrated platform provider archetype, Microsoft, a US-based technology corporation, leverages its Azure platform to offer a deeply integrated toolchain for developers. Synopsys, an American software company, exemplifies best-of-breed application security testing solutions, embedding directly into CI/CD pipelines. GitLab, a US-headquartered single application provider, occupies a unique position by offering a comprehensive platform for the entire software development lifecycle, including security functionalities. These entities demonstrate varied approaches to securing the modern software supply chain.
| Leading Market Players |
|---|
| IBM |
| Microsoft |
| Palo Alto Networks |
| Synopsys |
| Aqua Security |
| Checkmarx |
| Snyk |
| GitLab |
Cost & Logistics Intelligence
Specialized DevSecOps talent scarcity, particularly in tech hubs like Silicon Valley and Munich, drives labor-cost differentials which directly influence solution pricing tiers. This concentration of expertise creates distinct pricing structures for advanced DevSecOps integrations versus basic tooling.
Pricing Analysis
Warranty and service bundling significantly shapes DevSecOps pricing, with comprehensive support packages commanding higher premiums. The dominant pricing model involves SaaS-tiered subscriptions, often supplemented by project-based consulting fees for complex integrations. Price differentiation stems from the level of customization required and the depth of after-sales service provided. Pricing softness stems from the increasing competition among best-of-breed tool providers. Small-to-medium enterprises typically exhibit higher price sensitivity compared to large financial institutions.
Supply Chain Analysis
Direct sales channels and cloud marketplaces represent the primary distribution models for DevSecOps solutions. Geographic supply concentration for core development and talent resides in the United States, Germany, and India. The market relies on open-source software components and underlying cloud infrastructure services. A structural risk involves single-source vulnerability for highly specialized security tools or reliance on a single hyperscale cloud provider. Channel partnerships also extend reach into diverse enterprise segments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
DevSecOps adoption is a cost-of-compliance imperative, with regulations like the EU's GDPR and the US Executive Order on Improving the Nation's Cybersecurity establishing high barriers for non-compliant software vendors.
For Market Incumbents: Anchor existing client relationships by deepening platform integration and offering managed DevSecOps services. Consolidate market share through strategic acquisitions of niche best-of-breed tool specialists. Proliferation of open-source security tools poses a continuous competitive threat. Investment in AI-powered security R&D serves as a critical lever for differentiation.
For New Entrants and Emerging Players: AI-driven predictive threat modeling offers a technology-first wedge into underserved market segments. Target specialized MLOps security solutions and DevSecOps for edge computing environments. Small-to-medium enterprises in rapidly digitizing economies, particularly in Southeast Asia, represent the most penetrable end-user segment. A freemium model for developer adoption provides a scalable go-to-market angle.
For Investors and Strategic Acquirers: Re-rating potential sits with integrated platform providers given the accelerating regulatory pressure for software supply chain security. Long-term viability for DevSecOps solutions remains strong, essential for digital transformation over the next decade. Niche AI/ML security startups or compliance automation specialists represent attractive acquisition targets. Increased regulatory enforcement actions for software supply chain vulnerabilities serve as a key inflection signal to watch.
| Strategic Initiative | Industry Significance |
|---|---|
| Deepen Platform Integration | Seamlessly embeds security into existing developer workflows, reducing friction for large enterprises. |
| Acquire Best-of-Breed Specialists | Expands solution capabilities in critical areas like container security or MLOps security. |
| Invest in AI-Powered Security R&D | Enables predictive threat modeling and autonomous remediation, enhancing proactive defense. |
| Expand into Emerging Geographic Markets | Captures new demand from rapidly digitizing economies in Southeast Asia and Latin America. |
| Develop Specialized MLOps Security Tools | Addresses the unique security needs of machine learning pipelines, a growing enterprise focus. |
Research Approach
Document review covered SEC 10-K filings, industry whitepapers, government cybersecurity reports, and academic journals, complemented by interviews with industry stakeholders. Primary research involved conversations with CTOs, security architects, compliance officers, and DevSecOps engineers across various enterprises. This approach facilitated bottom-up and top-down triangulation of market data and trends.
The quantitative model produced volume and value outputs for the DevSecOps market across the projection horizon. This analytical framework integrated segmentation dimensions including deployment type, solution offering, application, end-user, and regional adoption patterns. Compound Annual Growth Rates were derived through regression analysis, incorporating market growth assumptions and historical data. Software development velocity and regulatory enforcement trends served as key industry-specific forecast inputs.
Several conditions sit outside the modeled scope, including unforeseen geopolitical events or radical technology disruptions. Forecasts reflect documented assumptions regarding market dynamics and technological progression. Periodic stress-testing of base assumptions is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Business Email Compromise (BEC) Market
Security Software
Security Software Market
Security Software
Facial Recognition Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
Wi-Fi Based Home Camera Market
Security Software
Robocall Mitigation Market
Security Software
Secaas Market
Security Software
Personal Data Recovery Software Market
Security Software
Quantum Key Distribution System Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Remote Access Management Market
Security Software
Digital Risk Protection Software Market
Security Software
Global Enterprise Key Management Market
Security Software
Software Defined Perimeter (SDP) Market
Security Software
Global Digital Identity Solutions Market