
 BYOD Security Market | 2026-2036
BYOD Security Market Size, Share, and Industry Trends Forecast 2026-2036
BYOD Security Market Intelligence
North American cloud infrastructure providers is restructuring capacity allocation toward zero-trust architecture delivery. Cisco Systems leverages its networking heritage to anchor enterprise-grade access control deployments across federal accounts. VMware sustains hybrid cloud dominance through workspace virtualization that unifies endpoint policy enforcement. BlackBerry Limited specializes in hardened mobile threat defense for regulated industries with stringent data residency requirements.
BYOD security encompasses endpoint protection systems that enforce encryption, containerization, and continuous authentication across personally owned devices accessing corporate resources. These platforms integrate mobile device management APIs, network access control gateways, and behavioral analytics engines to isolate enterprise data from personal applications. Cloud-based deployment models are capturing fastest expansion as organizations abandon capital-intensive on-premises appliance refresh cycles. Identity management solutions command premium pricing due to biometric and multi-factor authentication integration complexity. Device management retains volume leadership but faces margin compression from platform commoditization.
FDA cybersecurity guidance for connected medical devices, NIST zero-trust architecture mandates, and EU GDPR cross-border data transfer rules are elevating baseline compliance costs for healthcare and financial services adopters. These frameworks force vendors to certify encryption standards, audit logging completeness, and breach notification velocity as table stakes for procurement eligibility. Stakeholders must evaluate whether endpoint detection vendors can demonstrate continuous authorization architecture before committing to multi-year enterprise agreements.
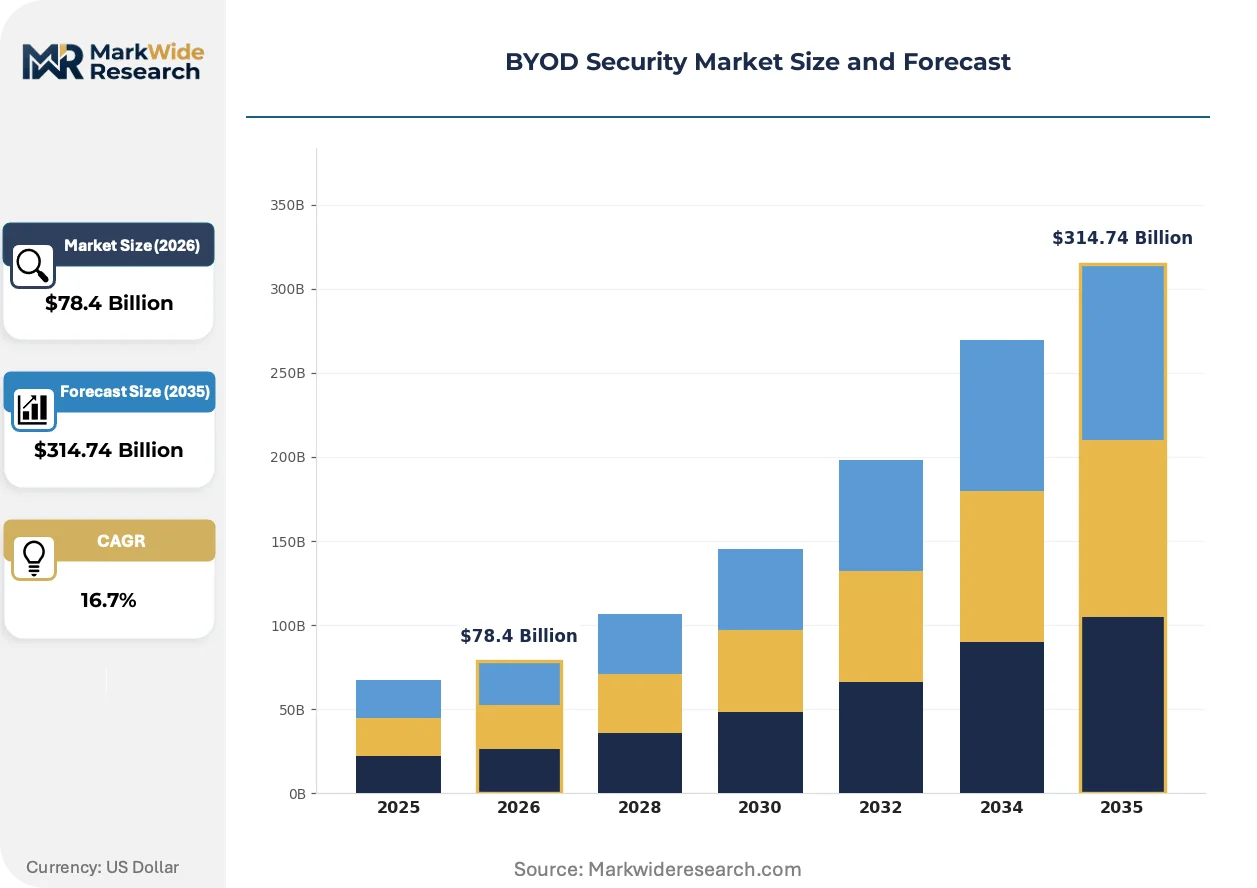
Market Dynamics
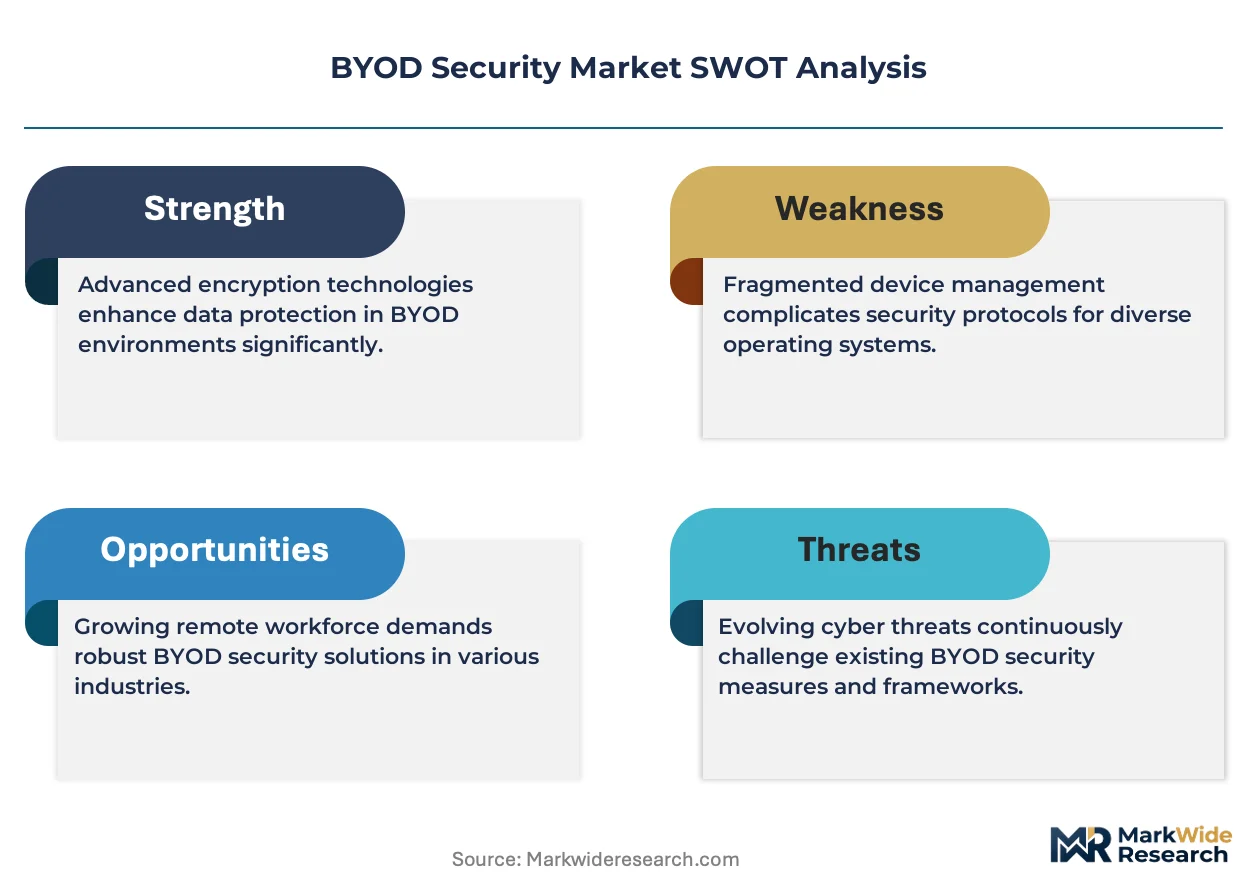
Zero-trust architecture mandates from NIST and FDA cybersecurity guidance for connected medical devices are forcing enterprise procurement teams to requalify vendor stacks around continuous authorization capabilities rather than perimeter-based defenses.
Growth Catalysts
- Healthcare MDM acceleration:Hospitals and health systems are deploying mobile device management platforms at scale to secure clinician-owned tablets and smartphones accessing electronic health records. FDA cybersecurity guidance for connected medical devices elevates baseline encryption requirements.
- NIST zero-trust mandates:Federal agencies and defense contractors must implement continuous authentication architectures. This policy pressure cascades through enterprise supply chains as primes require subcontractor compliance.
- Containerization technology maturation:Work profile and enterprise container solutions now deliver seamless user experience with hardened isolation. Financial services firms in Germany and India are standardizing on these architectures for trader and analyst devices.
Market Restraints
- Certificate authority concentration:Enterprise trust anchor dependence on a limited set of root certificate providers creates systemic vulnerability. A single compromise cascades across millions of managed endpoints.
- Biometric sensor cost volatility:Fingerprint and facial recognition module prices fluctuate with semiconductor foundry capacity allocation. This input cost instability compresses margins on premium identity management tiers.
- Cross-border data transfer friction:EU GDPR restrictions on transatlantic data flows force redundant infrastructure deployment. Vendors must maintain separate European instances, duplicating operational overhead.
Strategic Opportunities
- India SME underpenetration:Small and medium enterprises across manufacturing and services verticals lack dedicated security operations centers. Managed security service providers can capture this whitespace with affordable cloud-delivered endpoint protection.
- AI-powered behavioral analytics convergence:Machine learning anomaly detection fused with mobile threat defense enables predictive compromise identification. Early deployments in German automotive supply chains demonstrate efficacy.
- State-level data sovereignty mandates:Sub-national jurisdictions in the United States are enacting stricter breach notification and encryption standards. Vendors with flexible policy engines gain preferential procurement status.
Industry Challenges
- Zero-trust architecture skill scarcity:Security architects capable of designing continuous authorization frameworks command premium compensation. Enterprise hiring timelines stretch 6-12 months for qualified practitioners.
- Legacy Active Directory integration complexity:Hybrid identity environments require synchronization between cloud-native and on-premises authentication systems. Misconfigurations during migration windows create exploitable gaps.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | BYOD Security Market |
| Market Size in 2026 | $78.4 Billion |
| Market Size in 2035 | $314.74 Billion |
| CAGR (2026 – 2036) | 16.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Device Management, Data Security, Identity Management, Threat Protection Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Enterprise, Educational Institutions, Government Agencies, Healthcare Access Control: Biometric Authentication, Multi-Factor Authentication, Role-Based Access, Zero Trust |
| Companies Covered | Cisco Systems, IBM, VMware, BlackBerry Limited, Check Point Software Technologies, Fortinet, Citrix Systems, Ivanti, Palo Alto Networks, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
BYOD Security Market Strategic Shifts & Innovations
Passwordless authentication architectures and confidential computing enclaves are redrawing the technical boundary between corporate and personal data on shared devices.
Confidential computing using hardware-based trusted execution environments is decentralizing key storage and cryptographic operations from centralized policy servers to individual device secure processors. Healthcare delivery organizations in the United States are piloting these architectures for clinician devices accessing patient records. This shift reduces single points of compromise while complicating forensic investigation workflows.
EU AI Act risk classification rules are forcing security vendors to document algorithmic decision-making in behavioral analytics engines. Biometric authentication systems face heightened scrutiny as high-risk AI applications. German financial institutions are pre-emptively auditing machine learning models for explainability before regulatory deadlines crystallize.
Subscription-based consumption models are displacing perpetual license purchases across endpoint protection categories. Mid-market buyers in India prefer operational expenditure structures that align spending with employee headcount fluctuations. Managed service providers are capturing margin through bundled deployment and policy administration services.
BYOD Security Market Segmentation
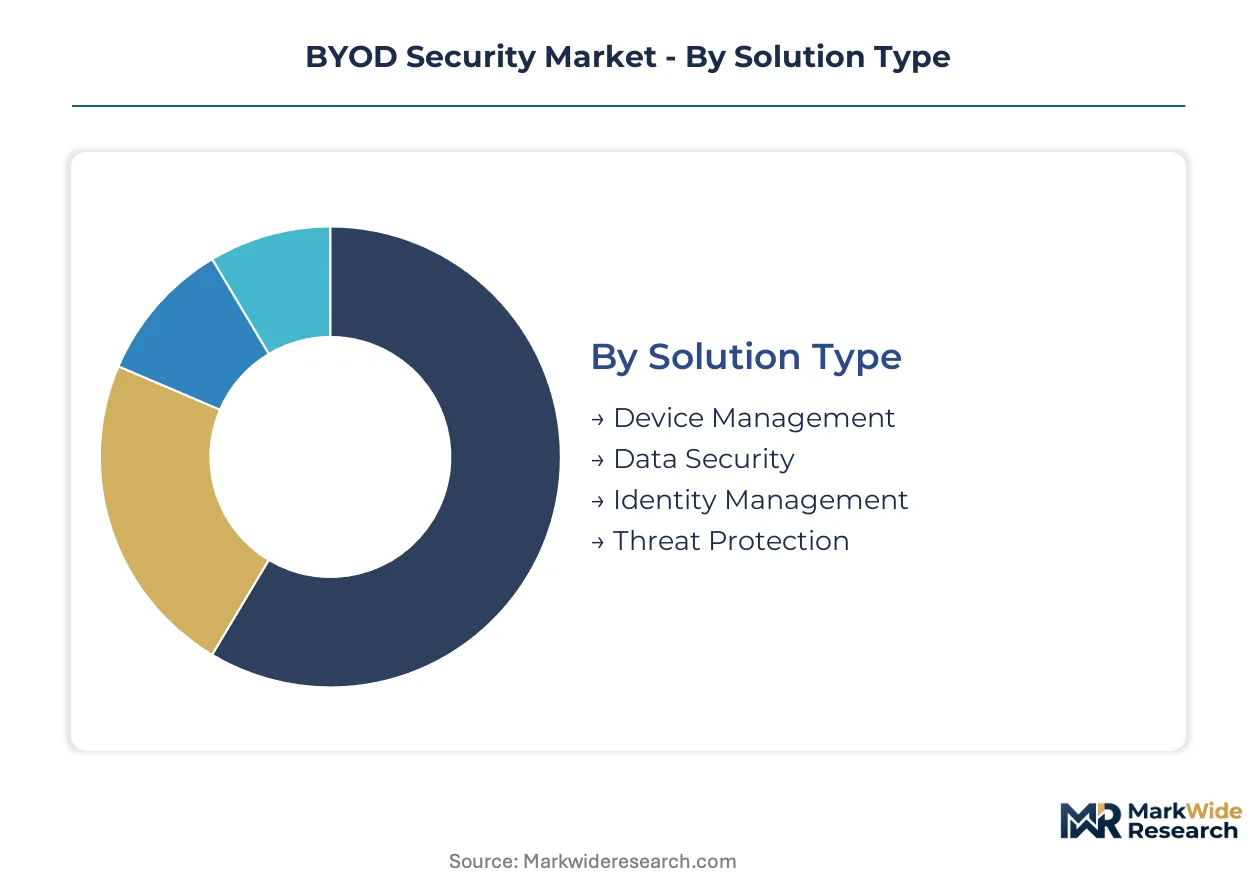
BYOD security architectures fragment across solution layers, deployment topologies, and access control mechanisms. Procurement teams must match organizational risk profiles to specific technology combinations rather than adopting uniform platform stacks.
Solution Type:
Technical capability depth determines vendor selection criteria across the four functional layers.
- Device Management:Mobile device management platforms enforce policy configuration, remote wipe capabilities, and compliance monitoring across heterogeneous endpoint fleets. Healthcare delivery organizations in the United States deploy these systems at scale to secure clinician-owned smartphones accessing electronic health records. FDA cybersecurity guidance elevates encryption and audit logging requirements for hospital procurement decisions.
- Data Security:Containerization and encryption solutions isolate corporate data from personal applications through hardware-backed secure enclaves. Financial services firms in Germany standardize on these architectures for trader devices handling sensitive market data. GDPR cross-border transfer restrictions force redundant European infrastructure deployment.
- Identity Management:Biometric and multi-factor authentication systems command premium pricing due to integration complexity with legacy directories.
- Threat Protection:Behavioral analytics engines detect anomalous access patterns and malware signatures on unmanaged endpoints.
Device Management leads on scale; Data Security leads on momentum.
Deployment Model:
Capital structure preferences and operational maturity drive divergence across delivery mechanisms.
- Cloud-Based:Subscription consumption eliminates capital-intensive appliance refresh cycles and enables rapid policy propagation across distributed workforces. Mid-market enterprises in India prefer operational expenditure alignment with employee headcount fluctuations. Managed service providers capture margin through bundled deployment and administration.
- Hybrid:Split architectures retain sensitive authentication infrastructure on-premises while offloading endpoint telemetry to cloud analytics. Defense contractors implementing NIST zero-trust mandates favor this topology for controlled unclassified information environments.
- On-Premises:Air-gapped deployments persist in classified government facilities with strict data residency requirements.
- Managed Service:Outsourced security operations centers monitor endpoint compliance for organizations lacking internal expertise.
Cloud-Based deployment captures the steepest expansion trajectory; Hybrid retains preference in regulated verticals.
End User:
Industry-specific compliance frameworks reshape functional requirements and procurement velocity.
- Healthcare:Hospitals and health systems accelerate mobile device management adoption to secure clinician-owned tablets accessing patient records. FDA cybersecurity guidance for connected medical devices mandates encryption standards and breach notification velocity as procurement prerequisites.
- Enterprise:Cross-industry corporations implement zero-trust architectures cascading from federal contractor compliance requirements through supply chains.
- Government Agencies:Federal entities and defense contractors implement continuous authentication per NIST mandates.
- Educational Institutions:Universities balance open access cultures with student and faculty device enrollment.
Healthcare leads on procurement urgency; Enterprise leads on absolute volume.
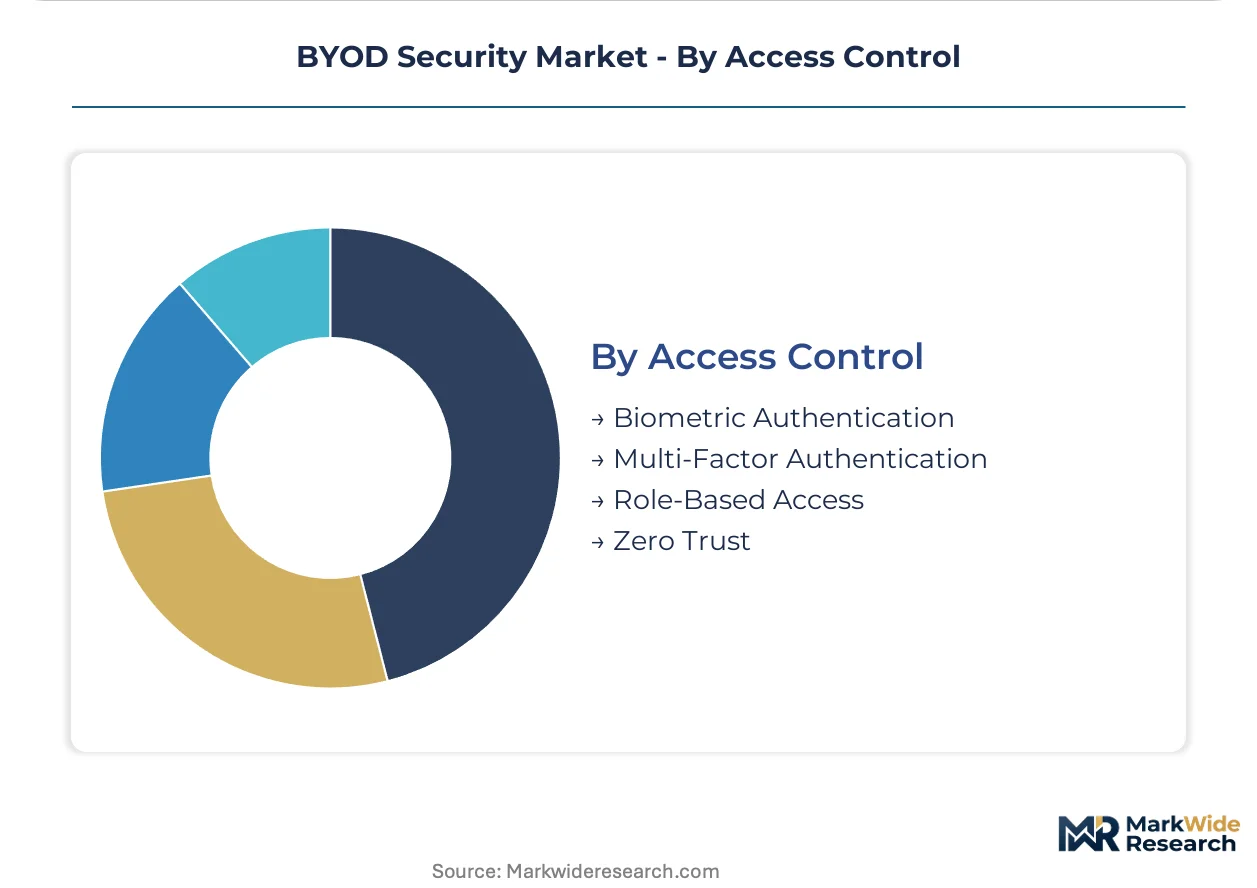
Access Control:
Authentication sophistication tiers separate perimeter-based from continuous authorization paradigms.
- Zero Trust:Continuous verification architectures eliminate implicit trust based on network location, requiring per-session authentication and least-privilege access grants. Federal agencies and their subcontractors implement these frameworks under NIST mandate pressure.
- Multi-Factor Authentication:Layered credential verification combines possession, knowledge, and inherence factors for stepped risk-based access.
- Biometric Authentication:Fingerprint and facial recognition modules face semiconductor foundry cost volatility compressing margins.
- Role-Based Access:Static permission assignments tied to organizational hierarchy persist in legacy environments.
Zero Trust leads on strategic priority; Multi-Factor Authentication leads on installed base.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Germany enforces stricter data sovereignty requirements than India, while the United States drives federal procurement standards through zero-trust mandates. National regulatory frameworks and industrial cluster concentrations reshape deployment priorities across major economies.
United States
Federal agencies and defense contractors anchor demand for continuous authentication architectures under NIST zero-trust mandates. FDA cybersecurity guidance for connected medical devices elevates encryption standards for healthcare procurement. The Washington DC-Baltimore corridor concentrates government contractor activity, with Virginia-based firms securing controlled unclassified information environments.
Germany
Automotive supply chains and financial services firms drive containerization adoption for trader devices handling sensitive market data. EU GDPR cross-border transfer restrictions force redundant European infrastructure deployment. The Frankfurt-Rhine-Main financial cluster standardizes on hardware-backed secure enclaves for mobile endpoint protection.
India
Small and medium enterprises across manufacturing and services verticals lack dedicated security operations centers, creating whitespace for managed security service providers. BIS data localization guidelines pressure vendors to maintain domestic cloud instances. Bangalore and Hyderabad technology corridors attract cloud-delivered endpoint protection deployments for mid-market buyers.
United Kingdom
Enterprise procurement teams requalify vendor stacks around continuous authorization capabilities following NIST-aligned security frameworks. Financial services regulators emphasize audit logging completeness for breach notification velocity. The London-Reading technology belt concentrates fintech and insurance sector mobile device management adoption.
Japan
Manufacturing conglomerates implement hybrid identity architectures synchronizing cloud-native and on-premises authentication systems. METI industrial security guidelines pressure vendors to certify encryption standards for procurement eligibility. The Tokyo-Yokohama corridor anchors enterprise workspace virtualization deployments across automotive and electronics supply chains.
BYOD Security Market Key Industry Players
United States producers anchor one tier; Canadian and Israeli specialists hold differentiated positions in threat intelligence and mobile defense. The vendor base separates into three concentration levels: diversified networking giants with federal account penetration, pure-play endpoint protection vendors, and legacy mobility specialists pivoting toward hardened enclaves. Dominant competitive moves include strategic partnerships with cloud infrastructure providers and portfolio diversification into identity management adjacent categories.
Within the networking-heritage tier, Cisco Systems exemplifies enterprise-grade access control deployment patterns across government accounts. VMware occupies a position bridging hybrid cloud dominance with workspace virtualization unification. BlackBerry Limited represents the legacy-mobility-pivot archetype, specializing in hardened mobile threat defense for regulated industries with stringent data residency requirements.
| Leading Market Players |
|---|
| Cisco Systems |
| IBM |
| VMware |
| BlackBerry Limited |
| Check Point Software Technologies |
| Fortinet |
| Citrix Systems |
| Ivanti |
| Palo Alto Networks |
| Others |
Cost & Logistics Intelligence
Federal defense contractors and healthcare procurement officers concentrate purchasing power around subscription-based SaaS models that align endpoint protection spending with employee headcount fluctuations. This buyer archetype preference forces vendors to abandon perpetual licensing in favor of operational expenditure structures that reduce upfront capital barriers.
Pricing Analysis
Capacity additions in India and Germany are reshaping price floors for cloud-delivered endpoint protection tiers. Three-tier pricing structure across premium, standard, and economy levels separates identity management with biometric integration from basic device management consoles. Cost compression in the standard tier is intensifying because semiconductor foundry allocation volatility squeezes fingerprint sensor margins. Small and medium enterprises in India exhibit the highest price sensitivity, while United States federal accounts tolerate premium pricing for FedRAMP-authorized deployments.
Supply Chain Analysis
India's BIS data localization guidelines and Germany's GDPR enforcement are reshaping sourcing patterns for certificate authority infrastructure and biometric hardware modules. Component supply concentrates in Taiwan for secure processors, South Korea for facial recognition sensors, and the United States for encryption key management systems. Single-source vulnerability pervades the root certificate provider layer, where a compromise cascades across millions of managed endpoints. Distribution runs through hyperscaler marketplaces and managed security service provider channels that bundle deployment with policy administration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
BYOD security functions as a regulatory compounder where NIST zero-trust architecture mandates and FDA cybersecurity guidance for connected medical devices create irreversible procurement tailwinds across federal and healthcare verticals.
For Market Incumbents: Lock in federal account relationships through FedRAMP authorization investments before defense contractor compliance requirements cascade to subcontractor tiers. Acquire specialized behavioral analytics capabilities to counter AI-powered threat detection entrants from Israeli and Canadian cybersecurity clusters. Vertical integration into hardware-backed secure enclave certification reduces dependence on Taiwan-based foundry allocation.
For New Entrants and Emerging Players: The price-point gap between premium identity management suites and economy device management consoles creates whitespace for mid-market cloud-native platforms. Small and medium enterprises across Indian manufacturing corridors lack dedicated security operations centers and represent the most penetrable segment. A managed service provider partnership model with local system integrators accelerates deployment velocity without direct enterprise sales infrastructure.
For Investors and Strategic Acquirers: Cloud infrastructure hyperscalers are the most active acquirer in this space, seeking endpoint protection capabilities to bundle with workspace virtualization offerings. Acquisition targets with zero-trust architecture certification and healthcare compliance expertise command strategic premiums. Watch for FDA enforcement actions against connected medical device manufacturers as an inflection indicator for healthcare MDM procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | FedRAMP authorization unlocks United States federal procurement pipelines under NIST mandate pressure. |
| Healthcare Compliance Specialization | FDA cybersecurity guidance alignment secures hospital system contracts for clinician device management. |
| Confidential Computing Integration | Hardware-based trusted execution environments differentiate platforms for German financial services procurement. |
| Managed Service Provider Partnership | Channel bundling captures Indian SME whitespace without direct sales force expansion. |
| AI-Powered Behavioral Analytics Development | Machine learning anomaly detection meets EU AI Act explainability requirements for biometric authentication. |
Research Approach
Direct dialogue with chief information security officers, healthcare IT procurement managers, federal contractor compliance leads, and managed security service provider executives grounded the qualitative assessment. Secondary validation drew from NIST cybersecurity framework publications, FDA guidance documents for connected medical devices, hyperscaler capex disclosures, and hospital procurement database records. Bottom-up endpoint deployment estimates and top-down security spending allocation models underwent iterative reconciliation.
Segmentation outputs across solution type, deployment model, end user vertical, and access control mechanism informed the analytical framework over the projection horizon. CAGRs derived from policy adoption velocity curves and compliance deadline clustering. Modeled inputs included NIST zero-trust implementation timelines, FDA medical device cybersecurity enforcement patterns, and EU GDPR cross-border transfer restriction evolution.
Caveats apply where semiconductor foundry capacity reallocation or root certificate authority compromise could materially shift the outlook. Forecasts reflect assumptions about regulatory enforcement consistency and healthcare IT budget allocation stability. A small set of named triggers—BIS data localization deadline shifts, EU AI Act behavioral analytics enforcement, and United States federal contractor compliance acceleration—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Keystroke Dynamics Market
Security Software
Global Mobile Security Software Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
Encryption As A Service Market
Security Software
Global Digital Signature Software Market
Security Software
Website Monitoring Software Market
Security Software
ATM Security Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Asia Pacific Anti Money Laundering Solutions Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Global Wireless Intrusion Prevention System Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Global Reputation Protection Software Market
Security Software
Global Email Verification Tools Market
Security Software
Global Optical Encryption Market