
 Endpoint Detection and Response Market | 2026-2036
Endpoint Detection and Response Market Size, Share, and Industry Trends Forecast 2026-2036
Endpoint Detection and Response Market Intelligence
Managed EDR service bundles is hardening as the primary commercial construct, shifting buyer expectations from perpetual licenses to continuous threat-hunting subscriptions. CrowdStrike Holdings Inc. leverages its cloud-native architecture to dominate large-enterprise deployments. Palo Alto Networks Inc. anchors its position through deep integration with firewall and network-security portfolios. Microsoft Corporation extends EDR capabilities through native embedding within operating-system environments.
Endpoint Detection and Response comprises software agents that continuously monitor endpoint devices—workstations, servers, mobile hardware—to detect anomalous behaviors, collect forensic telemetry, and enable automated containment responses against advanced persistent threats. Cloud-based deployment now leads growth trajectories as organizations abandon on-premises infrastructure management for elastic, vendor-operated threat-hunting platforms. Integrated solutions command premium positioning by converging EDR with extended detection and response and security information and event management workflows, while standalone offerings retain share among cost-constrained medium enterprises seeking modular procurement.
The U.S. Cybersecurity and Infrastructure Security Agency enforces binding operational directives mandating federal agency EDR coverage, directly shaping procurement specifications and vendor qualification criteria. The European Union Agency for Cybersecurity operationalizes NIS2 requirements that classify EDR as essential for critical-entity incident-response readiness. ISO/IEC 27001 certification pressures multinational enterprises to demonstrate continuous endpoint monitoring as part of audited information-security management systems. Stakeholders must evaluate whether platform consolidation or best-of-breed specialization delivers superior detection efficacy against ransomware and supply-chain attack vectors.
Market Dynamics
Cloud-native telemetry architectures are compressing deployment timelines from months to days, forcing incumbent vendors to re-engineer agent footprints or cede enterprise accounts to lighter-weight competitors.
Growth Catalysts
- Ransomware frequency:Financial services institutions now mandate continuous behavioral monitoring for trading floor endpoints, expanding agent coverage beyond traditional IT assets.
- NIS2 Directive:The European Union's tightened incident-response obligations classify EDR as essential infrastructure, compelling energy and transport operators to refresh legacy antivirus contracts.
- Zero-trust mandates:Federal procurement specifications from the U.S. Cybersecurity and Infrastructure Security Agency require endpoint visibility as a baseline qualification for vendor selection.
Market Restraints
- Agent performance overhead:Real-time kernel-level monitoring consumes substantial CPU and memory resources, triggering pushback from DevOps teams managing containerized workloads.
- Telemetry storage costs:Cloud-native deployments generate petabyte-scale forensic data, with egress and retention fees accumulating faster than subscription revenue growth.
- Skill scarcity:Managed security service providers face acute shortages of threat-hunting analysts capable of interpreting behavioral indicators of compromise.
Strategic Opportunities
- Operational technology convergence:Manufacturing and energy sectors seek unified visibility across IT and industrial control system endpoints, creating demand for ruggedized EDR agents.
- Small-medium enterprise gap:Cost-constrained organizations below five hundred endpoints remain underserved by premium-tier platforms, opening modular subscription tiers.
- Extended detection integration:Convergence of EDR with network detection and identity threat detection workflows enables platform vendors to displace point solutions.
Industry Challenges
- Alert fatigue management:Security operations centers struggle to triage high volumes of low-fidelity detections without automated correlation engines.
- Multi-cloud agent sprawl:Organizations operating across AWS, Azure, and Google Cloud environments face inconsistent policy enforcement and visibility gaps.
- Attestation timeline pressure:ISO/IEC 27001 certification audits now scrutinize endpoint monitoring coverage, compressing implementation windows for multinational enterprises.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Endpoint Detection and Response Market |
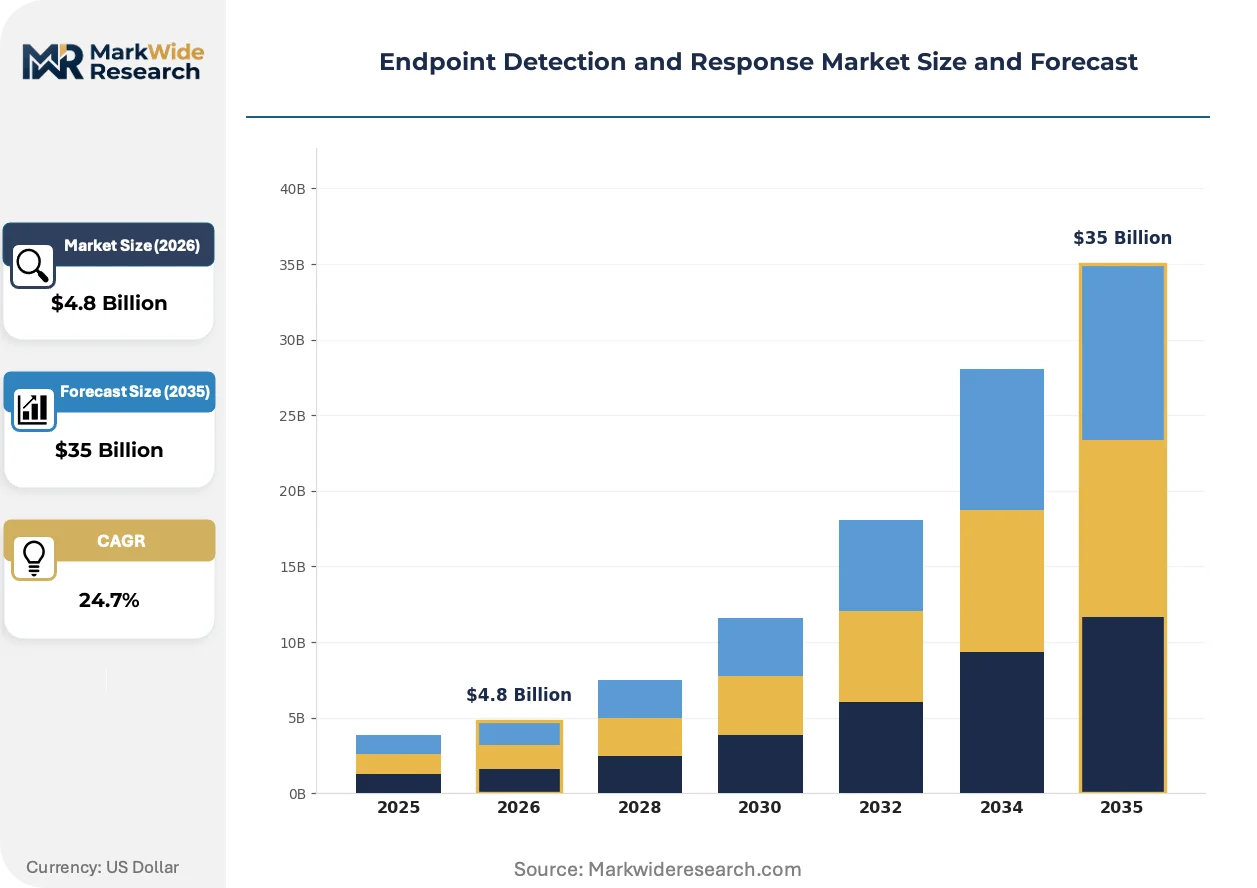
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $35 Billion |
| CAGR (2026 – 2036) | 24.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Solution Type: Network Security, Data Protection, Incident Response, Threat Intelligence Integration Level: Standalone, Integrated, Modular, Platform-Based |
| Companies Covered | Palo Alto Networks Inc., Trend Micro Inc., CrowdStrike Holdings Inc., VMware by Broadcom, Cisco Systems Inc., Microsoft Corporation, Sophos, Acronis, SentinelOne Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Endpoint Detection and Response Market Strategic Shifts & Innovations
Artificial intelligence is compressing detection latency from hours to minutes while reshaping how security teams allocate analyst attention across alert queues.
Extended detection and response platforms are unifying telemetry from endpoints, networks, and identity systems into single-pane workflows. Large enterprises with mature security operations centers are consolidating vendor relationships around these converged stacks. This unification is compressing procurement cycles for standalone EDR point products and elevating platform breadth as a primary selection criterion.
The EU AI Act imposes transparency requirements on automated threat-detection systems deployed within the European Union. Security vendors must now document algorithmic decision logic for high-risk cybersecurity applications. Financial institutions and critical infrastructure operators in Germany, France, and the Netherlands are prioritizing vendors with established conformity assessment procedures.
Security outcome-based contracting is displacing traditional seat-based pricing in managed service engagements. Mid-market enterprises are negotiating contracts tied to mean-time-to-containment metrics rather than agent counts. This shift is most pronounced in the United Kingdom and Nordic markets where CISOs face board-level pressure to demonstrate return on security investment.
Endpoint Detection and Response Market Segmentation
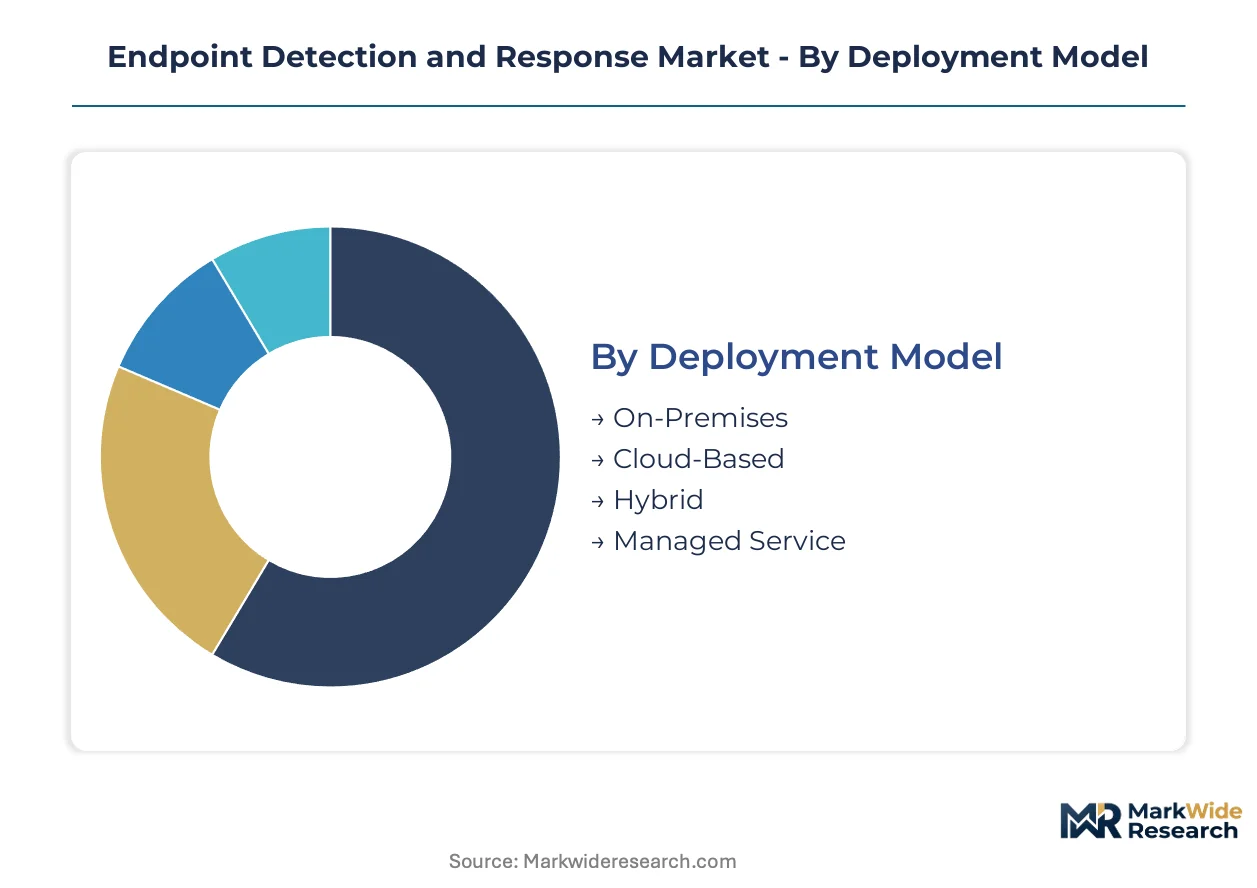
EDR procurement patterns diverge sharply across deployment architectures and organizational scale, with capital requirements and operational maturity dictating segment selection. Buyers trade upfront infrastructure investment against ongoing subscription elasticity, while regulatory pressure compresses decision timelines for government and critical infrastructure accounts.
Deployment Model:
Capital intensity peaks in self-managed infrastructure, while operating expenditure models dominate contemporary procurement.
- Cloud-Based:Vendor-operated telemetry architectures eliminate data center provisioning and reduce time-to-value from quarters to weeks. Demand concentrates among mid-market financial services firms in the United States seeking rapid compliance with federal zero-trust mandates without dedicated security engineering teams.
- Managed Service:Continuous threat-hunting subscriptions transfer operational burden to specialized providers, attracting organizations with acute analyst shortages. European energy operators under NIS2 Directive obligations favor this model to satisfy incident-response readiness requirements without internal SOC buildouts.
- On-Premises:Self-hosted deployments retain relevance for classified government networks and defense contractors with air-gapped operational requirements.
- Hybrid:Split architectures accommodate legacy mainframe endpoints alongside cloud-native workloads in regulated industries with phased migration constraints.
Most installed capacity flows through Cloud-Based deployments. Expansion is steepest in Managed Service.
End User:
Procurement sophistication scales with endpoint count and regulatory exposure, separating commodity buyers from platform consolidators.
- Large Enterprises:Organizations exceeding ten thousand endpoints demand converged XDR platforms unifying telemetry across identity, network, and cloud workloads. North American banking conglomerates drive premium-tier consumption, negotiating outcome-based contracts tied to mean-time-to-containment performance.
- Government:Federal agencies face binding operational directives mandating comprehensive endpoint visibility, with procurement specifications shaped by national cybersecurity authorities. United States civilian and defense departments anchor this segment through multi-year enterprise licensing vehicles.
- Medium Enterprises:Five-hundred to five-thousand endpoint organizations seek modular procurement avoiding premium platform lock-in.
- Small Enterprises:Sub-five-hundred endpoint businesses remain underserved, relying on bundled security suites or managed service provider resale arrangements.
Large Enterprises command the dominant share of vendor R&D attention. Government accounts are climbing the fastest as sovereign cybersecurity budgets expand.
Solution Type:
Functional specialization determines integration complexity and analyst skill requirements across security operations workflows.
- Incident Response:Automated containment playbooks and forensic timeline reconstruction reduce breach dwell time from months to hours. Critical infrastructure operators in Germany and France prioritize these capabilities to satisfy EU AI Act transparency requirements for automated threat-disposition systems.
- Threat Intelligence:Curated indicator feeds and adversary attribution contextualize endpoint alerts within broader campaign patterns. United Kingdom financial institutions leverage these integrations to satisfy board-level demands for demonstrable return on security investment.
- Network Security:East-west traffic visibility complements endpoint telemetry in hybrid cloud environments.
- Data Protection:Endpoint data loss prevention extends monitoring scope to insider threat and exfiltration vectors.
Incident Response capabilities anchor most competitive evaluations. Threat Intelligence is expanding most quickly as information-sharing mandates proliferate.
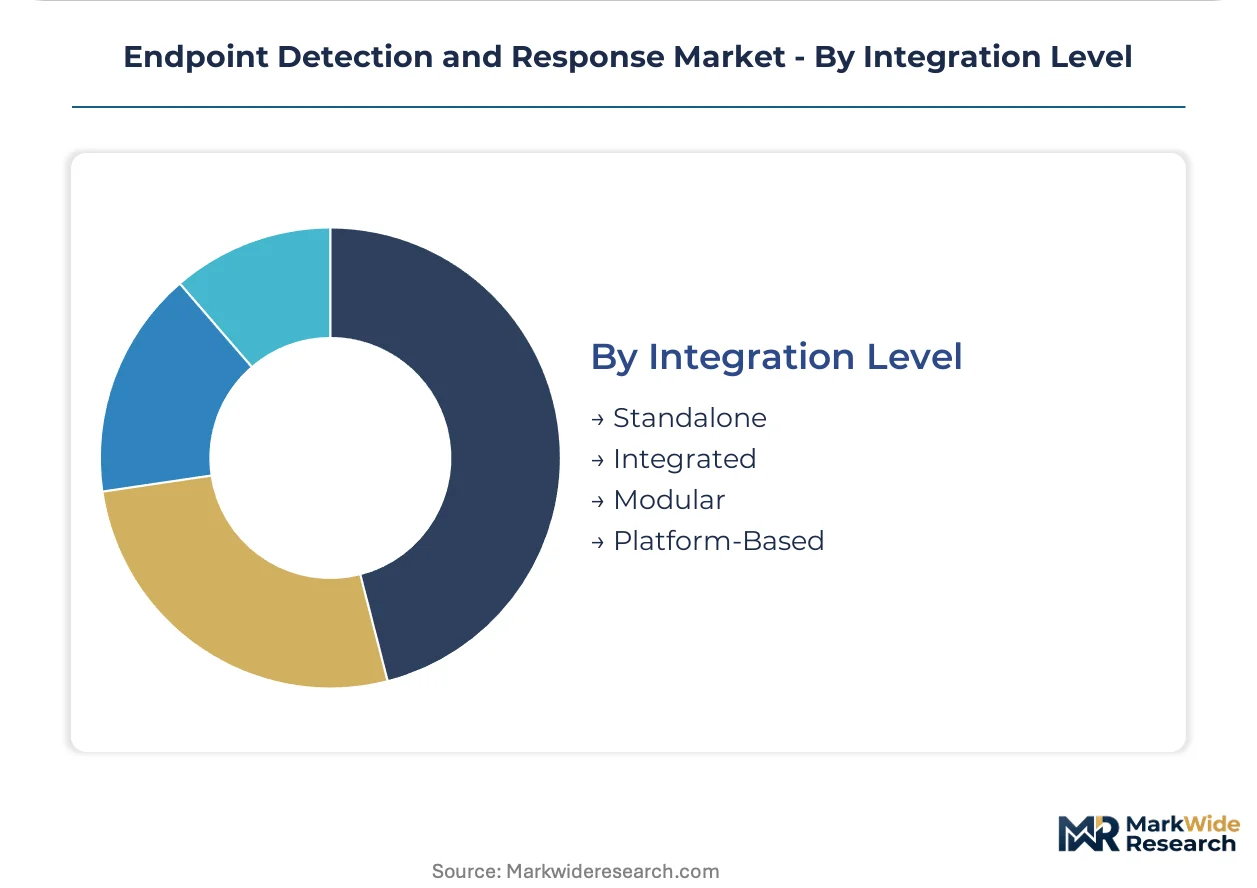
Integration Level:
Architecture decisions determine vendor consolidation potential and total cost of ownership across security tool sprawl.
- Platform-Based:Unified consoles converging EDR, network detection, and identity threat detection displace point solutions through procurement consolidation. Mature security operations centers in Nordic markets drive this segment, seeking to compress vendor relationships and normalize alert correlation across telemetry sources.
- Integrated:Pre-built connectors with adjacent security information and event management and firewall portfolios reduce deployment friction. Palo Alto Networks and CrowdStrike deployments exemplify this approach, anchoring customer retention through workflow embedding.
- Modular:Componentized procurement allows cost-constrained buyers to activate capabilities incrementally.
- Standalone:Best-of-breed specialization persists among organizations with existing security architectures resistant to platform migration.
Platform-Based architectures capture the majority of new enterprise commitments. Integrated solutions are gaining share fastest as mid-market buyers prioritize deployment velocity.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
United States federal agencies deploy EDR at scale under binding operational directives, while Germany's industrial base drives ruggedized agent demand for operational technology convergence. This divergence shapes procurement patterns across both markets.
United States
Financial services institutions mandate continuous behavioral monitoring for trading floor endpoints, expanding coverage beyond traditional IT assets. The Cybersecurity and Infrastructure Security Agency enforces binding operational directives requiring comprehensive endpoint visibility as a baseline vendor qualification. Banking conglomerates in New York and Chicago negotiate outcome-based contracts tied to mean-time-to-containment performance metrics.
Germany
Manufacturing and energy sectors seek unified visibility across IT and industrial control system endpoints, creating demand for ruggedized EDR agents. The EU AI Act imposes transparency requirements on automated threat-detection systems, compelling vendors to document algorithmic decision logic. Industrial clusters in Bavaria and North Rhine-Westphalia prioritize vendors with established conformity assessment procedures for high-risk cybersecurity applications.
United Kingdom
Mid-market enterprises negotiate security outcome-based contracts tied to mean-time-to-containment metrics rather than agent counts. Board-level pressure to demonstrate return on security investment accelerates this shift across London and the Southeast. Financial institutions leverage threat intelligence integrations to satisfy demonstrable security investment requirements.
France
Critical infrastructure operators prioritize automated containment playbooks and forensic timeline reconstruction to reduce breach dwell time. EU AI Act transparency requirements for automated threat-disposition systems shape vendor selection criteria. Energy and transport operators in the Île-de-France region refresh legacy antivirus contracts to satisfy NIS2 Directive incident-response readiness obligations.
Netherlands
Mature security operations centers drive platform-based architectures that compress vendor relationships and normalize alert correlation across telemetry sources. The NIS2 Directive classifies EDR as essential infrastructure for critical entities. Technology clusters in the Randstad region favor converged XDR platforms unifying endpoint, network, and identity telemetry.
Endpoint Detection and Response Market Key Industry Players
Top-tier vendors anchor large-enterprise deployments, while specialized providers occupy modular and mid-market segments. Cloud-native architectures compress deployment timelines from months to days, forcing incumbent vendors to re-engineer agent footprints or cede enterprise accounts. Three archetypes dominate: platform consolidators converging EDR with extended detection and response, cloud-native specialists emphasizing lightweight agent deployment, and integrated security stacks embedding endpoint capabilities within broader firewall and network portfolios. Competitive intensity manifests through strategic partnerships with managed security service providers and portfolio diversification into operational technology security.
Within the platform consolidator tier, CrowdStrike Holdings Inc. and Palo Alto Networks Inc. exemplify divergent architectural approaches to enterprise capture. CrowdStrike Holdings Inc. leverages cloud-native positioning to anchor large-enterprise deployments, while Palo Alto Networks Inc. integrates endpoint capabilities within firewall and network-security portfolios to drive customer retention. Microsoft Corporation extends EDR through native operating-system embedding, representing a third consolidation vector that reduces deployment friction for organizations with existing enterprise agreements.
| Leading Market Players |
|---|
| Palo Alto Networks Inc. |
| Trend Micro Inc. |
| CrowdStrike Holdings Inc. |
| VMware by Broadcom |
| Cisco Systems Inc. |
| Microsoft Corporation |
| Sophos |
| Acronis |
| SentinelOne Inc. |
| Others |
Cost & Logistics Intelligence
The EU AI Act's algorithmic transparency mandates gate qualified supply access and premium-tier pricing for vendors serving critical infrastructure operators in Germany and France. Buyers lacking documented conformity assessment procedures face exclusion from high-margin procurement channels, compressing vendor margins as compliance investments escalate.
Pricing Analysis
Capacity additions in the United States are reshaping price floors for cloud-native EDR platforms as hyperscaler infrastructure expansion reduces telemetry storage costs. Subscription tiers stratify across enterprise, mid-market, and small-business levels, with ISO/IEC 27001 certification and mean-time-to-containment guarantees commanding substantial premiums. Price erosion runs through the mid-market segment as Microsoft and CrowdStrike compete for share with bundled offerings. Government buyers demonstrate lowest price sensitivity due to binding operational directive compliance requirements, while sub-five-hundred endpoint organizations defer purchases entirely.
Supply Chain Analysis
Agent refurbishment and telemetry pipeline optimization programs now govern vendor operational efficiency as cloud-native architectures mature. Core engineering talent concentrates in the United States, Israel, and Ireland, with threat intelligence feeds drawing from Ukraine, Estonia, and Singapore-based research centers. Supply chain vulnerability rests on single-source dependencies for specialized kernel-level monitoring components. Distribution runs through direct enterprise sales, managed security service provider channels, and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Endpoint Detection and Response procurement has shifted toward late-cycle quality differentiation, with buyers prioritizing converged XDR platforms over standalone point solutions as security operations center maturity advances.
For Market Incumbents: Hedge against cloud-native specialist encroachment by embedding EDR capabilities within broader identity and network security portfolios. Palo Alto Networks exemplifies this defensive posture through firewall-anchored workflow integration. Accelerate certification investment for EU AI Act conformity assessment to maintain premium-tier access among German and French critical infrastructure accounts. For New Entrants and Emerging Players: Managed security service providers represent the most accessible channel for modular EDR offerings targeting cost-constrained medium enterprises below five hundred endpoints. White-space opportunity concentrates in operational technology convergence for manufacturing and energy sectors seeking ruggedized agent deployments. Pursue outcome-based contracting structures tied to mean-time-to-containment metrics to differentiate from seat-based incumbents. For Investors and Strategic Acquirers: Roll-up economics work for platform consolidators because security operations center maturity is compressing vendor relationships and elevating breadth as a primary selection criterion. Long-term viability favors vendors with demonstrated XDR integration capabilities and established managed service provider channel density. Monitor NIS2 Directive enforcement intensity across European energy and transport operators as an inflection indicator for infrastructure refresh spending.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Converging EDR with identity and network telemetry displaces point solutions in mature security operations centers. |
| Managed Service Partnership | Channel alliances with MSSPs transfer operational burden and expand reach among analyst-constrained organizations. |
| Operational Technology Expansion | Ruggedized agent development captures manufacturing and energy demand for unified IT-ICS visibility. |
| EU AI Act Certification | Documented conformity assessment procedures unlock premium-tier procurement among German and French operators. |
| Outcome-Based Contracting | Mean-time-to-containment pricing structures align vendor incentives with buyer return-on-investment demands. |
Research Approach
Direct dialogue with chief information security officers, managed security service provider operations directors, federal agency cybersecurity procurement leads, and threat intelligence analysts grounded the qualitative foundation. Secondary validation drew from U.S. Cybersecurity and Infrastructure Security Agency binding operational directives, EU NIS2 implementation guidance, ISO/IEC 27001 audit documentation, and hyperscaler security portfolio disclosures. Bottom-up endpoint deployment estimates triangulated against top-down security software spending benchmarks.
Bottom-up modeling aggregated endpoint counts by organization size, deployment architecture, and vertical regulatory exposure across the projection horizon. Segmentation dimensions spanned cloud-based versus on-premises deployment, enterprise scale tiers, solution type specialization, and integration complexity levels. CAGRs derived from fitted growth curves incorporating ransomware incident frequency trajectories, zero-trust mandate implementation timelines, and analyst labor market constraints.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to EU AI Act enforcement consistency, NIS2 Directive national transposition variations, and hyperscaler pricing aggression. Practitioners should monitor managed security service provider hiring rates and critical infrastructure operator insurance premium movements for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global User Provisioning Market
Security Software
Hardware OTP Token Authentication Market
Security Software
Disk Encryption Software Market
Security Software
Global Optical Encryption Market
Security Software
Parental Control Software Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Global Data Masking Market
Security Software
Encryption As A Service Market
Security Software
Data Loss Prevention Market
Security Software
Global Network Encryption Market
Security Software
Asia-Pacific Smart Doorbell Market
Security Software
Doorbell Camera Market
Security Software
Global Runtime Application Self-Protection Market
Security Software
Antivirus Software Package Market
Security Software
Identity and Access Management (IAM) Market
Security Software
Europe Enterprise Firewall Market