
 Global Insider Threat Management ITM Software Market | 2026-2036
Global Insider Threat Management ITM Software Market Size, Share, and Industry Trends Forecast 2026-2036
Global Insider Threat Management ITM Software Market Foresight
Mid-market enterprises are redrawing the demand map for insider threat management solutions, pulling investment away from legacy government-centric procurement cycles. Forcepoint leverages its federal heritage to compete in commercial sectors with hybrid deployment architectures. Code42 anchors its position through sustained R&D intensity in cloud-native data loss prevention. Teramind specializes in behavioral analytics for regulated industries, occupying a distinct niche between endpoint monitoring and workforce compliance.
Insider Threat Management ITM Software encompasses behavioral monitoring platforms, endpoint telemetry engines, and risk-scoring algorithms that detect anomalous data access, privilege misuse, and exfiltration patterns across enterprise networks. These systems integrate user activity logs, network traffic analysis, and identity governance signals to flag high-risk insider actions before material breaches occur. Cloud-based deployment is expanding fastest as organizations abandon capital-intensive on-premises infrastructure, though hybrid configurations retain strong traction among financial institutions with sovereign data requirements. User Behavior Analytics commands the deepest margin pools due to its dependency on proprietary machine-learning models and specialized data-science talent.
The SEC's cybersecurity disclosure rules, the EU AI Act's risk-classification framework for automated monitoring systems, and Japan's METI guidelines on supply-chain data protection are collectively elevating compliance-driven procurement budgets. These frameworks mandate documented insider risk programs, auditable response protocols, and cross-border data handling transparency. Stakeholders must weigh the trade-off between cloud scalability and jurisdictional data residency as regulatory fragmentation deepens across operational footprints.
Market Dynamics
Zero-trust security mandates are compressing deployment timelines for insider threat platforms, forcing vendors to abandon monolithic architectures in favor of API-first, composable systems that integrate with existing identity stacks.
Growth Catalysts
- EU AI Act risk-classification framework:Automated employee monitoring systems now face mandatory conformity assessments, creating procurement urgency for compliant platforms across German and French financial institutions.
- Cloud-native data loss prevention:Endpoint telemetry engines with real-time exfiltration blocking are displacing legacy DLP appliances in mid-market enterprises seeking reduced operational overhead.
- Japan METI supply-chain guidelines:Data protection mandates for critical infrastructure operators are accelerating behavioral analytics adoption among manufacturing conglomerates with extensive vendor networks.
Market Restraints
- Specialized machine-learning talent scarcity:User behavior analytics development depends on data-science expertise concentrated in Silicon Valley and London, constraining vendor R&D velocity.
- Sovereign data residency requirements:Financial institutions in Germany and Switzerland face jurisdictional fragmentation that complicates cross-border cloud deployments.
- False-positive fatigue:Alert overload from poorly calibrated behavioral models erodes security-team trust and delays incident response protocols.
Strategic Opportunities
- Small and medium enterprise underpenetration:Mid-market organizations in Italy and Spain lack dedicated insider risk programs, presenting greenfield deployment opportunities for managed security service providers.
- Convergence of UEBA and identity governance:Unified platforms combining behavioral analytics with privileged access management are capturing budget from separate tooling purchases.
- India's Digital Personal Data Protection Act:Cross-border data transfer restrictions are creating demand for locally hosted insider threat infrastructure among IT services exporters.
Industry Challenges
- Legacy SIEM integration complexity:Behavioral analytics platforms must normalize disparate log formats from decades-old security information systems, extending implementation timelines.
- Workforce privacy litigation exposure:Employee monitoring transparency requirements under GDPR and emerging US state laws demand legal review of data collection scopes.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Insider Threat Management ITM Software Market |
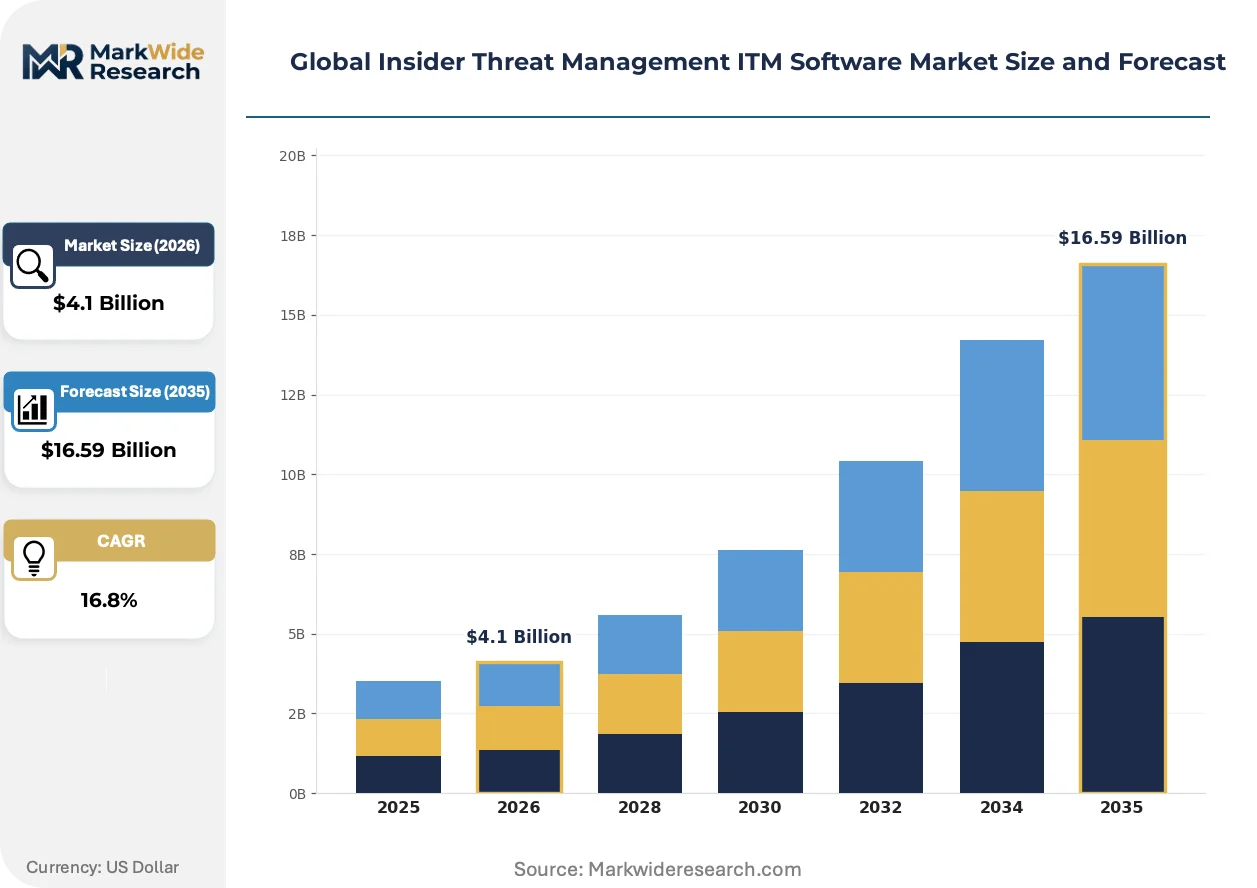
| Market Size in 2026 | $4.1 Billion |
| Market Size in 2035 | $16.59 Billion |
| CAGR (2026 – 2036) | 16.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Virtual Private Cloud Solution Offering: User Behavior Analytics, Data Loss Prevention, Access Management, Incident Response Application: Fraud Detection, Data Exfiltration Prevention, Compliance Monitoring, Risk Assessment End User Type: Financial Institutions, Government Agencies, Technology Firms, Telecommunications Providers |
| Companies Covered | Pathlock, Code42, Teramind, Forcepoint, Veriato, SolarWinds, ActivTrak, Exabeam, Splunk, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Insider Threat Management ITM Software Market Shifts & Advancements
Insider threat management is fragmenting into specialized functional layers, with pure-play behavioral analytics vendors competing against converged security platforms that bundle monitoring with broader zero-trust infrastructure.
Extended detection and response architectures are bifurcating the insider threat market. Endpoint agents with kernel-level visibility now feed telemetry into cloud-native analytics engines that correlate user actions across SaaS applications, on-premises file servers, and collaboration tools. Financial services firms in New York and London are deploying these integrated stacks fastest, compressing standalone UEBA vendor margins as buyers prefer consolidated procurement.
The SEC's cybersecurity disclosure rules are reshaping accountability structures. Public companies must now report material insider breaches within four business days, elevating real-time detection from operational preference to board-level compliance mandate. US-listed technology and healthcare firms are prioritizing platforms with automated incident documentation and forensic timeline reconstruction.
Security procurement is consolidating around outcome-based performance guarantees. Enterprise buyers in Germany and Japan now demand contractual mean-time-to-detect metrics and false-positive rate ceilings, displacing traditional seat-based licensing. Managed detection and response providers are capturing this demand by wrapping insider threat monitoring into broader security operations center subscriptions.
Global Insider Threat Management ITM Software Market Segmentation
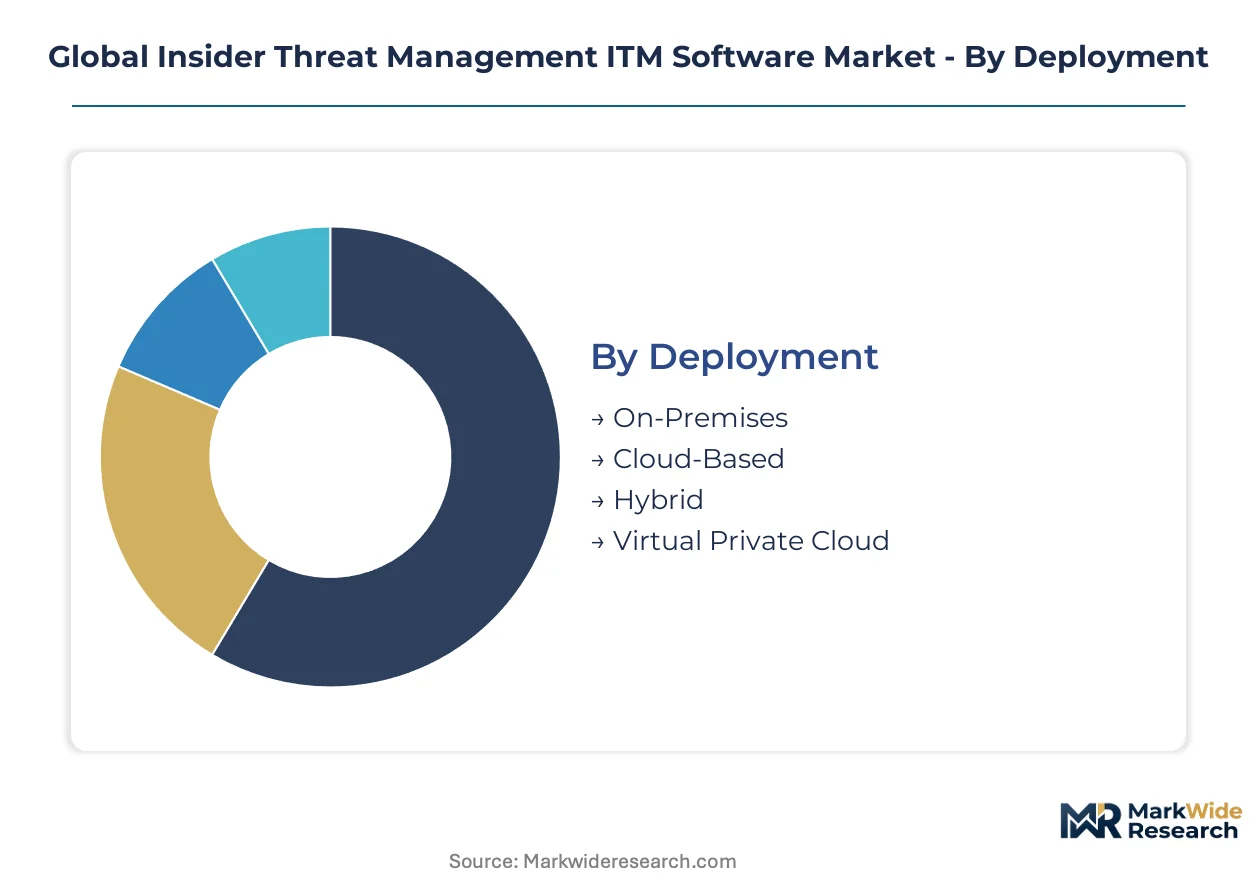
Insider threat management procurement patterns diverge sharply across deployment architectures, solution stacks, and regulatory exposure profiles. Buyers in Germany and Japan prioritize sovereign data controls, while US technology firms favor cloud-native elasticity. Understanding these segment boundaries clarifies where vendor R&D investments concentrate and which compliance frameworks shape purchasing criteria.
Deployment:
Cloud-based configurations dominate export-led demand from US-headquartered multinationals, whereas hybrid and virtual private cloud deployments concentrate in domestic-procurement markets with strict data residency mandates.
- Cloud-Based:Multi-tenant SaaS architectures with auto-scaling compute pools and API-first integration frameworks. Demand concentrates among US technology firms expanding zero-trust footprints across distributed workforces, constrained by EU AI Act conformity assessments for automated monitoring systems.
- Hybrid:Split-stack configurations retaining sensitive telemetry processing on-premises while pushing analytics to cloud substrates. German financial institutions and Swiss pharmaceutical conglomerates favor this model to satisfy GDPR and national banking regulator data localization requirements.
- On-Premises:Air-gapped deployments with dedicated hardware security modules and localized machine-learning training pipelines.
- Virtual Private Cloud:Isolated cloud environments with single-tenant infrastructure and custom encryption key management.
Cloud-Based holds the largest share; momentum sits with Hybrid as jurisdictional fragmentation deepens.
Solution Offering:
Margin pools concentrate in components requiring proprietary data-science talent, while commoditized functions face consolidation pressure from bundled security platforms.
- User Behavior Analytics:Machine-learning models correlating keystroke dynamics, file access patterns, and network traversal anomalies into risk scores. Financial institutions in London and New York deploy these most aggressively, driven by SEC cybersecurity disclosure rules mandating four-day breach reporting windows.
- Data Loss Prevention:Real-time content inspection engines with optical character recognition and structured data fingerprinting. Mid-market enterprises across Italy and Spain are displacing legacy appliances with cloud-native alternatives to reduce operational overhead.
- Access Management:Privileged session monitoring with just-in-time credential elevation and command-level audit trails.
- Incident Response:Automated case management with forensic timeline reconstruction and regulatory notification workflows.
User Behavior Analytics commands premium pricing; Data Loss Prevention is expanding most quickly through managed service provider channels.
Application:
Compliance-driven use cases outpace fraud-focused deployments in procurement velocity, reflecting regulatory penalty structures rather than incident frequency.
- Compliance Monitoring:Continuous audit trails mapping user actions to GDPR, SEC, and Japan METI documentation requirements. German automotive suppliers and US healthcare systems prioritize this application to preempt regulatory enforcement actions.
- Data Exfiltration Prevention:Exfiltration blocking with USB device control, cloud upload interception, and steganography detection. Technology firms in Silicon Valley and Tel Aviv deploy these capabilities to protect intellectual property during employee offboarding cycles.
- Fraud Detection:Anomaly flagging for financial transaction manipulation and procurement collusion schemes.
- Risk Assessment:Quantified insider risk scoring for cyber insurance underwriting and board reporting.
Compliance Monitoring holds the largest share; Data Exfiltration Prevention shows the steepest expansion trajectory as remote work persists.
End User Type:
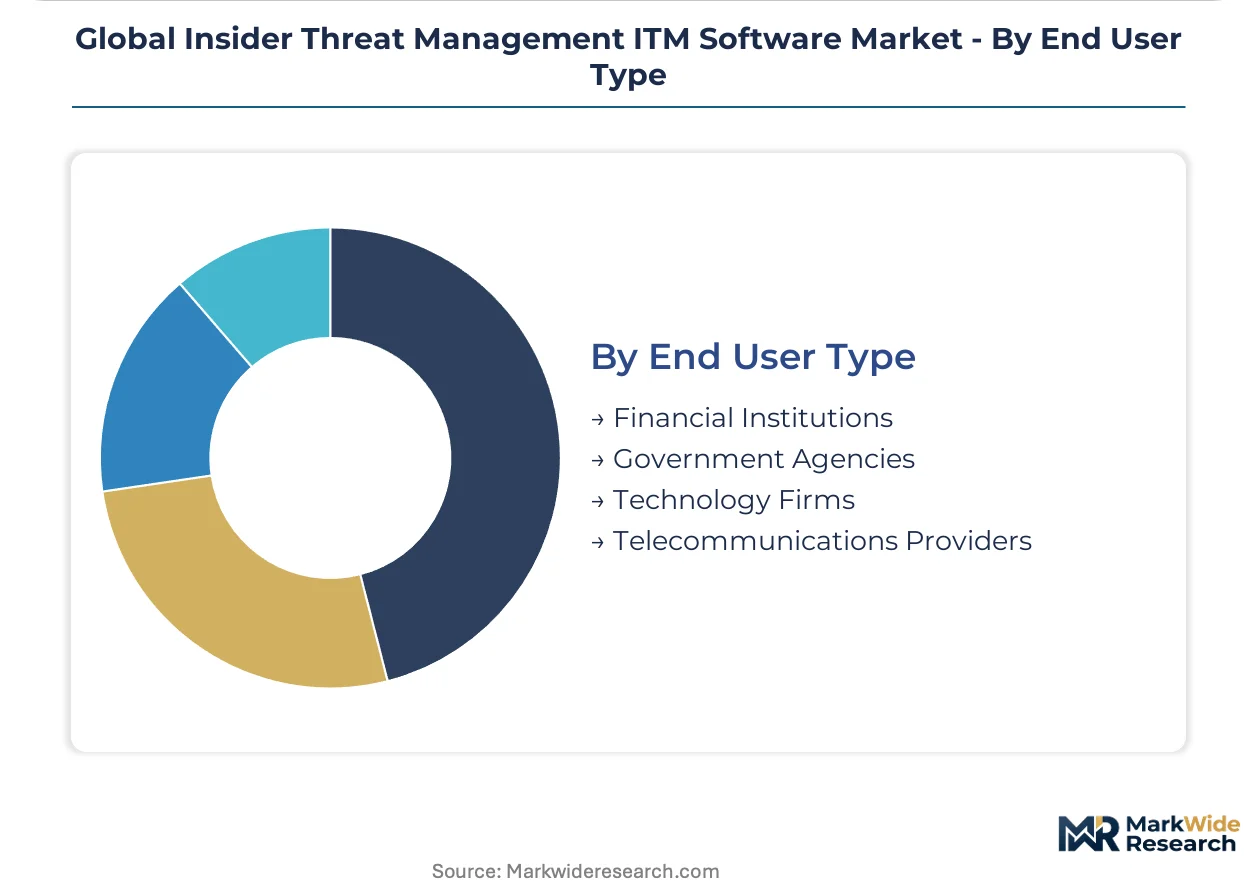
Procurement sophistication varies dramatically, with financial institutions demanding outcome-based performance guarantees and government agencies favoring seat-based licensing with federal security certifications.
- Financial Institutions:Tier-one banks and insurance conglomerates requiring real-time cross-border transaction monitoring. Institutions in Switzerland and Singapore lead adoption, constrained by fragmented sovereign data residency requirements across operational footprints.
- Government Agencies:Defense and intelligence entities with classified network segmentation and insider threat program mandates. US federal procurement cycles dominate this segment, though German and Japanese defense ministries are accelerating parallel investments.
- Technology Firms:Software vendors and cloud service providers protecting source code repositories and customer data environments.
- Telecommunications Providers:Network operators monitoring subscriber data access and lawful intercept compliance.
Financial Institutions hold the largest share; Technology Firms are gaining share fastest as intellectual property theft risks intensify.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Frankfurt-Cyberport fiber corridor underwrites Germany's centrality in European insider threat management procurement, while transatlantic data links position the United States as the primary cloud-native deployment hub.
United States
SEC cybersecurity disclosure rules and zero-trust federal mandates drive procurement velocity among New York financial institutions and Silicon Valley technology firms. The four-day breach reporting window compresses deployment timelines for real-time behavioral analytics. Boston's cybersecurity cluster hosts concentrated vendor R&D operations serving Fortune 500 compliance programs.
Germany
German automotive suppliers and banking conglomerates prioritize hybrid deployment architectures to satisfy GDPR data localization requirements. The EU AI Act's conformity assessments for automated monitoring systems create procurement urgency across Frankfurt and Munich financial centers. Baden-Württemberg's industrial belt leads manufacturing-sector adoption of workforce compliance platforms.
Japan
METI supply-chain data protection guidelines accelerate behavioral analytics adoption among Tokyo and Osaka manufacturing conglomerates with extensive vendor networks. Critical infrastructure operators face mandatory insider risk program documentation. The Nagoya industrial corridor concentrates deployment of endpoint telemetry engines for intellectual property protection.
United Kingdom
London's financial services sector demands outcome-based performance guarantees with contractual mean-time-to-detect metrics. The Information Commissioner's Office enforcement actions elevate audit-ready insider threat documentation. The City and Canary Wharf clusters drive cross-border deployment of cloud-native platforms with EU data residency safeguards.
India
The Digital Personal Data Protection Act's cross-border transfer restrictions create demand for locally hosted insider threat infrastructure among Bangalore and Hyderabad IT services exporters. Managed security service providers capture mid-market opportunities in Mumbai's financial district. Data localization mandates favor domestic deployment over foreign SaaS alternatives.
Global Insider Threat Management ITM Software Market Competitive Landscape
Concentration sits with cloud-native specialists and federal-heritage vendors adapting to commercial procurement cycles. The vendor base spans three strategic tiers: behavioral analytics pure-plays, converged security platforms, and managed detection and response providers. M&A activity targets machine-learning talent acquisition, while geographic expansion focuses on EU AI Act compliance certification and India data center localization.
Within the behavioral analytics tier, Teramind and Code42 exemplify divergent specialization strategies—Teramind anchoring regulated-industry workforce compliance and Code42 occupying cloud-native data loss prevention. Forcepoint represents the federal-commercial crossover archetype, leveraging government security heritage for hybrid enterprise deployments. These three vendors illustrate how vendor origin and architectural choices shape competitive positioning across deployment models and compliance frameworks.
| Leading Market Players |
|---|
| Pathlock |
| Code42 |
| Teramind |
| Forcepoint |
| Veriato |
| SolarWinds |
| ActivTrak |
| Exabeam |
| Splunk |
| Others |
Supply & Pricing Matrix
Cloud-native SaaS architectures achieve 40-60% unit cost advantages over on-premises equivalents at enterprise scale, compressing price floors for behavioral analytics platforms while concentrating supply leverage among hyperscaler-dependent vendors. This scale dynamic forces mid-market buyers toward subscription tiers and pressures on-premises specialists to absorb infrastructure overhead or cede share.
Pricing Analysis
Volume-discount tiering structures separate enterprise deployments above 5,000 seats from mid-market bundles and entry-level SaaS tiers. Pricing stratifies across premium, standard, and economy levels based on machine-learning model sophistication and GDPR compliance certification. Cost compression in the mid-market tier is intensifying because managed security service providers bundle insider threat monitoring into broader SOC subscriptions. Government agencies show least price sensitivity due to federal security certification requirements, while Italian and Spanish mid-market enterprises drive hardest bargain negotiations.
Supply Chain Analysis
Inbound logistics costs from Asia-Pacific cloud regions through the Singapore-Tokyo-Seattle triangle affect latency-sensitive behavioral analytics deployments, though software supply chains remain less physically constrained than hardware-dependent sectors. Development talent concentrates in the United States, United Kingdom, and Israel, with machine-learning engineering pipelines drawing from Stanford, MIT, and Technion graduate pools. Single-source vulnerability sits with NVIDIA GPU supply for model training infrastructure. Distribution runs through direct enterprise sales teams in financial centers and hyperscaler marketplaces for cloud-native deployments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The insider threat management market is recovering from 2022-2023 budget freezes as SEC disclosure deadlines and EU AI Act implementation dates force compliance-driven procurement. This cyclical recovery draws from regulatory penalty structures rather than discretionary security investment.
For Market Incumbents: Consolidate through acquisition of machine-learning specialists in London and Tel Aviv to close talent gaps. Deepen hybrid deployment capabilities for German and Swiss financial institutions facing GDPR localization mandates. Vertical integration into identity governance platforms captures budget from separate UEBA and PAM purchases. Channel control through managed detection and response partnerships defends against cloud-native entrants.
For New Entrants and Emerging Players: Managed service delivery gaps in Italian and Spanish mid-market enterprises offer white-space expansion paths. Target compliance monitoring applications in Indian IT services exporters facing Digital Personal Data Protection Act localization requirements. Partner with domestic data center operators in Bangalore and Hyderabad for sovereign hosting credibility. API-first architectures enable rapid integration with existing SIEM investments.
For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among cloud-native vendors with outcome-based pricing contracts. Long-term viability hinges on EU AI Act conformity assessment completion and India data center localization. Acquisition targets should demonstrate proprietary behavioral models and federal security certifications. Watch for inflection when German automotive suppliers accelerate workforce compliance platform deployment.
| Strategic Initiative | Industry Significance |
|---|---|
| EU AI Act Conformity Certification | Mandatory conformity assessments unlock procurement across Frankfurt and Munich financial centers. |
| India Data Center Localization | Domestic hosting infrastructure satisfies Digital Personal Data Protection Act cross-border restrictions. |
| Machine-Learning Talent Acquisition | Silicon Valley and London data-science expertise constrains vendor R&D velocity. |
| Managed Detection and Response Partnership | SOC subscription bundling captures mid-market buyers seeking reduced operational overhead. |
| Hybrid Deployment Architecture Investment | Split-stack configurations satisfy GDPR and Swiss banking regulator data localization requirements. |
Research Methodology
Findings reconcile primary fieldwork against secondary review of SEC cybersecurity disclosure filings, EU AI Act implementation guidance, and Japan METI supply-chain guidelines. Primary interviews engaged CISOs at tier-one financial institutions, IT procurement officers at German automotive suppliers, and platform engineers at cloud-native security vendors. Secondary validation drew from SEC 10-K cybersecurity risk disclosures, GDPR enforcement action databases, and hyperscaler marketplace transaction data. Bottom-up deployment counts triangulate against top-down addressable market sizing across the analysis window.
Segmentation dimensions modeled include deployment architecture, solution stack composition, end-user industry vertical, and regional regulatory cluster. Value projections incorporate adoption curve assumptions for cloud-native versus hybrid configurations, compliance-driven versus fraud-focused use case prioritization, and outcome-based versus seat-based pricing conversion. CAGRs derive from regression analysis of historical procurement velocity against regulatory deadline proximity. Industry-specific forecast inputs include SEC four-day breach reporting compliance rates and EU AI Act conformity assessment completion timelines.
Forecasts assume regulatory continuity in SEC cybersecurity disclosure rules, EU AI Act risk-classification frameworks, and Japan METI supply-chain guidelines; material policy shifts would require re-modeling. Specific risks that could revise projections include workforce privacy litigation expanding beyond GDPR jurisdictions, sovereign data residency fragmentation deepening across operational footprints, and machine-learning talent scarcity constraining vendor innovation cycles. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Log Management Market
Security Software
Global Consumer Identity and Access Management Market
Security Software
Website Monitoring Software Market
Security Software
Anomaly Detection Market
Security Software
VPN Software Market
Security Software
Battery-Powered Doorbell Camera Market
Security Software
Phone Antivirus Software Market
Security Software
Biometric POS Terminals Market
Security Software
Global Electronic Offender Monitoring Solutions Market
Security Software
Automotive Over-the-Air Cybersecurity Hardening Test Equipment Market
Security Software
Encryption Software Market
Security Software
Global Dynamic Application Security Testing Market
Security Software
US Evidence Management Market
Security Software
Messaging Security Market
Security Software
Cloud Identity and Access Management Software Market
Security Software
Vsaas Market