
 Threat Detection Systems Market | 2026-2036
Threat Detection Systems Market Size, Share, and Industry Trends Forecast 2026-2036
Threat Detection Systems Market Outlook
Cybersecurity talent scarcity is bifurcating the competitive landscape between vendors with captive engineering depth and those dependent on contracted expertise. Smiths Group plc leverages its integrated sensor manufacturing to sustain dominance in physical screening architectures. Teledyne FLIR LLC anchors its position through thermal imaging specialization that extends into perimeter defense applications. Palo Alto Networks, Inc. competes aggressively in network security through AI-native platform consolidation.
Threat detection systems encompass integrated hardware and software architectures designed to identify, classify, and alert operators to anomalous activities across physical and digital domains, typically processing signals at sub-second latency thresholds to enable preemptive response protocols. These systems serve commercial, governmental, and institutional buyers by reducing exposure to operational disruption, data exfiltration, or physical breach incidents. Network security deployments command substantial installed bases due to enterprise cloud migration, while machine learning and artificial intelligence technologies are capturing disproportionate R&D investment as signature-based methods face obsolescence against polymorphic attack vectors. Endpoint protection retains stable replacement demand across regulated industries, though hybrid deployment models are gaining traction where data sovereignty requirements conflict with cloud-native architectures.
FCC guidelines for critical communications infrastructure, EU NIS2 Directive mandates for essential and important entities, and FDA cybersecurity requirements for connected medical devices collectively elevate baseline product standards and compress market access for non-compliant suppliers. The EU AI Act imposes additional conformity obligations on autonomous threat classification systems deployed within member states, creating divergent compliance pathways versus US regulatory frameworks. Stakeholders must monitor evolving cross-border certification reciprocity agreements to anticipate where product standardization investments will yield scalable market entry versus fragmented national approvals.
Market Dynamics
Multi-sensor fusion architectures are restructuring competitive positioning by collapsing the traditional separation between physical screening and network security procurement, forcing vendors to rebuild engineering teams around cross-domain expertise rather than single-modality specialization.
Growth Catalysts
- NATO defense modernization:Member states are consolidating perimeter defense contracts under unified multi-sensor specifications, creating standardized demand pools for integrated thermal-radar-cyber platforms.
- EU AI Act conformity obligations:Autonomous threat classification systems deployed across member states now require documented algorithmic transparency, generating replacement cycles for pre-2024 installed bases.
- Critical infrastructure operator mandates:NIS2 Directive coverage expansion to important entities in energy, transport, and digital infrastructure sectors is mandating detection system upgrades with minimum 24-hour incident reporting capabilities.
Market Restraints
- Semiconductor supply concentration:Advanced sensor processing chips remain concentrated among Taiwanese and South Korean foundries, exposing lead time volatility for multi-sensor platform manufacturers.
- EU-US regulatory divergence:The EU AI Act's risk-classification framework for autonomous systems creates non-trivial redesign costs versus FCC-guided US product architectures, fragmenting R&D allocation.
- Signature-based detection obsolescence:Polymorphic attack vectors have degraded effectiveness of rule-based network security appliances, compressing replacement revenue for vendors without ML-native platform transitions.
Strategic Opportunities
- India critical infrastructure buildout:Smart city and port modernization programs under CEA guidelines are creating first-mover positions for perimeter-cyber integrated system providers.
- Healthcare IoT convergence:FDA cybersecurity requirements for connected medical devices are extending threat detection procurement from IT departments into clinical engineering budgets.
- Edge AI deployment models:On-device inference chips from NVIDIA and Qualcomm are enabling sub-100ms latency threat classification without cloud data egress, unlocking sovereign deployment options for defense and finance end-uses.
Industry Challenges
- Cross-domain engineering scarcity:The intersection of RF sensor physics, machine learning operations, and air-gapped network architecture expertise remains thinly staffed, elongating product development cycles.
- Legacy system integration friction:Decades-old SCADA and building management systems in industrial facilities resist API-based threat feed ingestion, requiring costly protocol translation layers.
- Certification timeline compression:Simultaneous EU AI Act, NIS2, and CE marking processes for autonomous systems are extending time-to-revenue by 8-14 months for new product introductions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Threat Detection Systems Market |
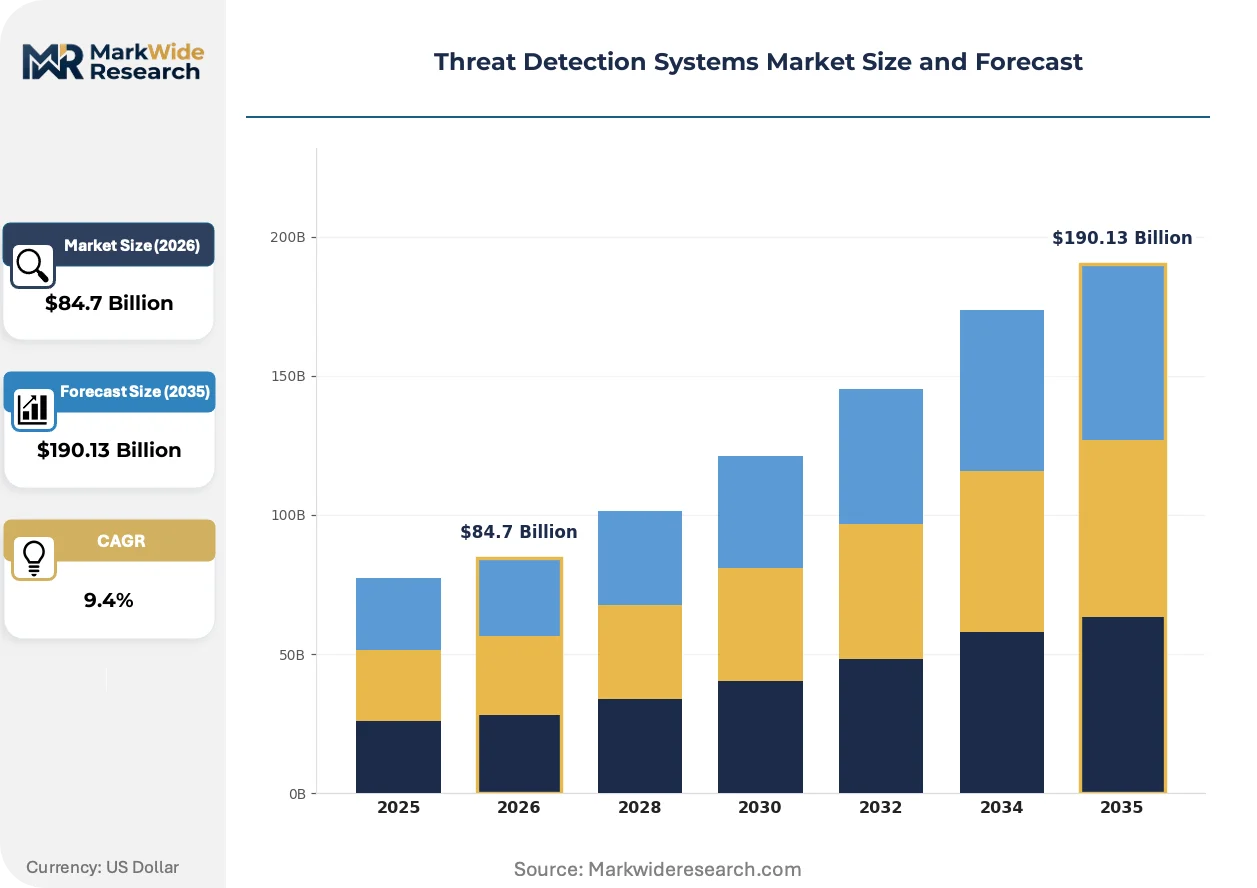
| Market Size in 2026 | $84.7 Billion |
| Market Size in 2035 | $190.13 Billion |
| CAGR (2026 – 2036) | 9.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Intrusion Detection, Network Security, Endpoint Protection, Application Security Technology: Machine Learning, Artificial Intelligence, Behavioral Analysis, Signature-Based Detection Deployment: On-Premises, Cloud-Based, Hybrid, Virtualized End User: Financial Services, Government Agencies, Healthcare, Education |
| Companies Covered | Smiths Group plc, Teledyne FLIR LLC, Thales, Fortinet, Inc., Palo Alto Networks, Inc., Cisco Systems, Inc., Check Point Software Technologies Ltd., Rapiscan Systems, Chemring Group PLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Threat Detection Systems Market Strategic Shifts
Signature-based detection methodologies are losing operational relevance as adversaries automate payload mutation, redirecting vendor investment toward behavioral inference models and sensor fusion architectures that operate without pre-defined threat libraries.
Machine learning inference at the network edge is decomposing the traditional hub-and-spoke security architecture where all traffic funneled to centralized inspection appliances. Financial services firms in Frankfurt and Singapore are deploying GPU-enabled edge nodes for real-time encrypted traffic analysis without decryption. This topology shift is compressing demand for high-throughput centralized firewalls while expanding procurement of distributed inference hardware.
The EU AI Act's risk-based classification system for autonomous threat detection is forcing product architecture redesigns across vendors serving European defense and critical infrastructure sectors. High-risk system categories now require human-in-the-loop override capabilities and algorithmic audit trails, adding 15-25% to firmware development costs. German and French system integrators are responding by segmenting product lines into EU-conforming and export-optimized variants.
Defense agencies are consolidating vendor relationships around multi-year managed detection contracts that bundle hardware refresh cycles with continuous algorithmic update subscriptions. This displaces traditional capital purchase models where agencies owned depreciating equipment outright. The United Kingdom's Ministry of Defence and Australia's Defence Science and Technology Group have both moved to outcome-based contracting structures since 2023.
Threat Detection Systems Market Segmentation
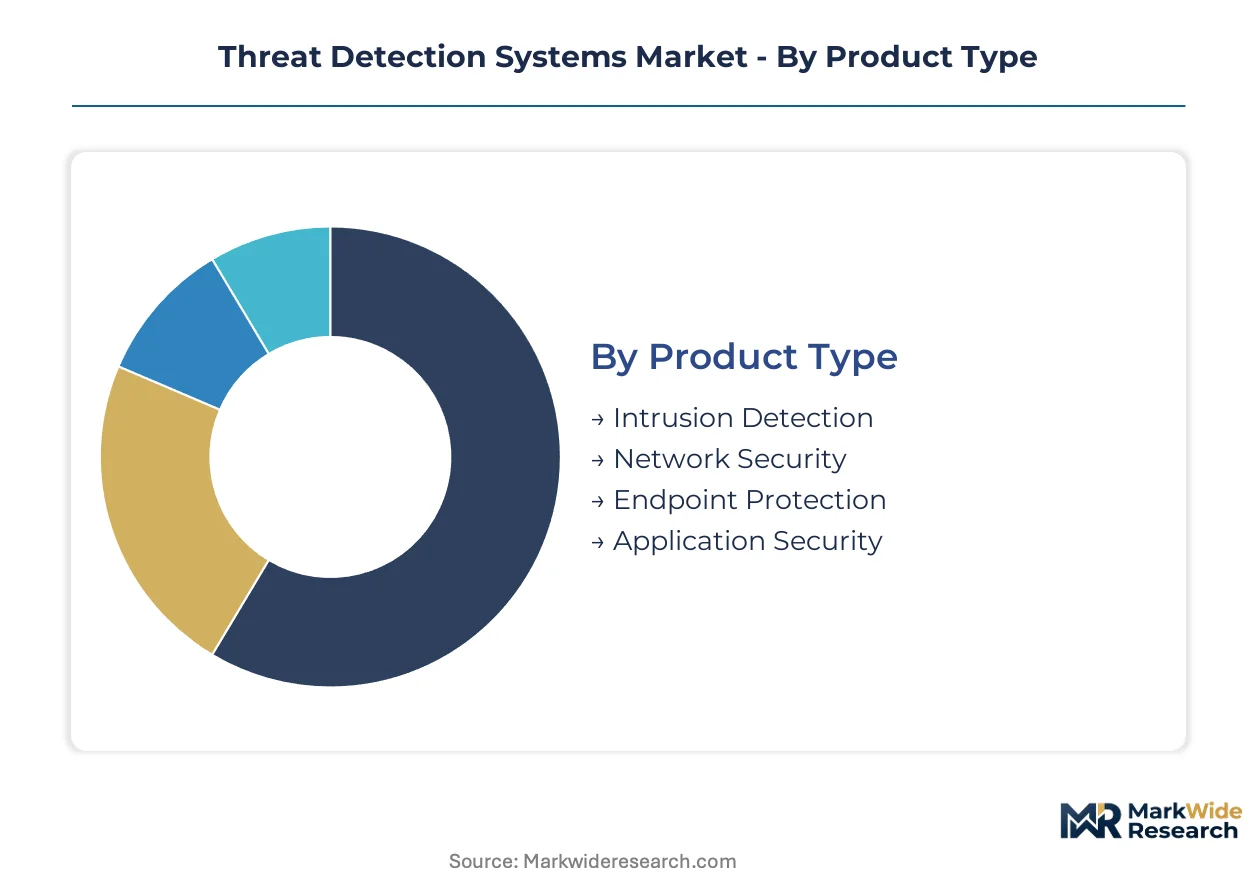
Threat detection procurement patterns diverge sharply across product architectures and deployment topologies. Regulatory mandates from the EU AI Act and NIS2 Directive reshape how buyers evaluate technology categories against compliance thresholds rather than purely technical performance.
Product Type:
FCC guidelines for critical communications infrastructure and EU NIS2 mandates create divergent certification burdens across physical and digital detection modalities.
- Intrusion Detection:Hardware-software systems monitoring network traffic for unauthorized access attempts through packet inspection and anomaly flagging. German energy operators under NIS2 coverage are replacing legacy perimeter sensors with integrated thermal-radar platforms that feed unified SOC dashboards.
- Network Security:Firewalls, secure web gateways, and intrusion prevention systems inspecting data flows at network boundaries. Financial services firms in Frankfurt and Singapore deploy GPU-enabled edge nodes for encrypted traffic analysis without decryption, displacing centralized appliance procurement.
- Endpoint Protection:Agent-based software monitoring device-level activities for malware execution and data exfiltration attempts.
- Application Security:Runtime protection and code vulnerability scanning for web-facing software assets.
Established volume favors Network Security; emerging adoption favors Intrusion Detection.
Technology:
Development cost structures stratify sharply between ML-native architectures and legacy signature libraries.
- Machine Learning:Statistical models trained on behavioral baselines to identify deviations without pre-defined threat signatures. The EU AI Act's high-risk system classification for autonomous detection imposes human-in-the-loop requirements and algorithmic audit trails, adding firmware development overhead.
- Artificial Intelligence:Deep learning architectures processing multi-modal sensor inputs for threat classification. Edge AI deployment using NVIDIA and Qualcomm inference chips enables sub-100ms response latency for defense and sovereign finance applications.
- Behavioral Analysis:Pattern recognition based on user and entity activity baselines rather than known-bad indicators.
- Signature-Based Detection:Rule-matching against databases of known malware hashes and attack indicators.
Procurement momentum concentrates in ML-native platforms; replacement cycles compress for signature-dependent systems.
Deployment:
Data sovereignty requirements and latency thresholds fragment preferred topologies across regulated industries.
- On-Premises:Hardware and software operating within buyer-controlled facilities with no external data egress. Defense agencies and classified government facilities mandate air-gapped architectures under national security protocols.
- Cloud-Based:Vendor-managed infrastructure with elastic scaling and centralized threat intelligence feeds. Mid-market enterprises prioritize operational expenditure models over capital-intensive appliance procurement.
- Hybrid:Split architectures retaining sensitive workloads on-premises while leveraging cloud analytics for non-critical traffic.
- Virtualized:Containerized or VM-based detection functions deployable across distributed infrastructure.
Cloud-Based deployments claim the steepest expansion trajectory; Hybrid models gain traction where sovereignty conflicts with scalability.
End User:
Budget authority and compliance exposure reshape vendor sales motions across institutional buyer types.
- Financial Services:Banks, insurers, and payment processors subject to PCI-DSS and national banking regulator cybersecurity mandates. Frankfurt and Singapore financial centers drive edge AI procurement for real-time transaction monitoring without data residency violations.
- Government Agencies:Defense, intelligence, and civilian departments with classified and unclassified network segments. NATO member states consolidate multi-sensor perimeter contracts under unified thermal-radar-cyber specifications.
- Healthcare:Hospital systems and medical device manufacturers facing FDA cybersecurity requirements for connected equipment.
- Education:Universities and research institutions with dispersed campus networks and open access policies.
Government Agencies anchor capital-intensive procurement; Healthcare represents the fastest-growing vertical as clinical engineering budgets absorb IT security functions.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German defense agencies procure integrated thermal-radar-cyber platforms for NATO perimeter modernization, while Indian port operators under CEA guidelines deploy first-generation multi-sensor systems. This consumption-mix differential separates established European integrated-procurement markets from emerging Asian greenfield installations.
United States
The Department of Defense and civilian agencies drive demand for air-gapped, on-premises architectures under national security protocols. FCC guidelines for critical communications infrastructure mandate minimum cybersecurity baselines for telecom operators. Defense contractors in the Washington DC-Baltimore corridor consolidate multi-year managed detection contracts with algorithmic update subscriptions.
Germany
Energy operators and automotive manufacturers under NIS2 coverage replace legacy perimeter sensors with unified SOC-integrated platforms. The EU AI Act imposes human-in-the-loop requirements and algorithmic audit trails on autonomous threat classification systems. Industrial clusters in Bavaria and Baden-Württemberg anchor procurement for manufacturing facility protection.
United Kingdom
The Ministry of Defence shifted to outcome-based contracting structures for perimeter defense systems in 2023. National cybersecurity mandates for critical infrastructure operators compress replacement cycles for pre-2024 detection architectures. London financial services firms deploy GPU-enabled edge nodes for real-time transaction monitoring without data residency violations.
India
Smart city and port modernization programs under CEA guidelines create first-mover positions for integrated perimeter-cyber system providers. The national critical infrastructure protection framework expands mandatory detection coverage to energy and transport sectors. Mumbai and Chennai port authorities issue tenders for multi-sensor fusion platforms with sub-100ms response latency.
Singapore
Financial services regulators mandate real-time threat detection for payment systems and digital banking infrastructure. The Monetary Authority of Singapore's technology risk management guidelines elevate baseline standards for anomaly detection systems. The city-state's data center cluster drives edge AI procurement for sovereign cloud deployments without cross-border data egress.
Threat Detection Systems Market Competitive Environment
A small set of integrated leaders sits above a broader specialist tier, with engineering depth in sensor fusion and machine learning operations determining competitive position. The upper tier commands multi-year defense contracts and critical infrastructure mandates through captive cross-domain expertise. Three archetypes populate the market: integrated sensor manufacturers with physical screening heritage, network security vendors with AI-native platforms, and defense contractors with classified-systems clearance. Consolidation pressures favor M&A activity around machine learning engineering teams, while product line segmentation into EU-conforming and export-optimized variants addresses regulatory divergence.
Within the integrated sensor tier, Smiths Group plc and Teledyne FLIR LLC exemplify manufacturers leveraging physical screening specialization into perimeter defense applications. Palo Alto Networks, Inc. occupies a position representing network security vendors competing through AI-native platform consolidation. These three entities anchor the competitive structure without exhausting its diversity, as additional specialists in behavioral analytics, endpoint protection, and managed detection services populate adjacent segments.
| Leading Market Players |
|---|
| Smiths Group plc |
| Teledyne FLIR LLC |
| Thales |
| Fortinet, Inc. |
| Palo Alto Networks, Inc. |
| Cisco Systems, Inc. |
| Check Point Software Technologies Ltd. |
| Rapiscan Systems |
| Chemring Group PLC |
| Others |
Value Chain & Pricing Dynamics
EU AI Act conformity obligations gate both supplier qualification and price differentiation simultaneously, as high-risk autonomous threat classification systems require algorithmic audit trails and human-in-the-loop capabilities that only certified vendors can deliver. This regulatory threshold splits procurement into premium EU-conforming tiers and export-optimized alternatives, with defense agencies and critical infrastructure operators absorbing 15-25% firmware development premiums for compliant architectures.
Pricing Analysis
Long-term managed detection contracts with bundled algorithmic update subscriptions now dominate defense and critical infrastructure procurement, displacing traditional capital purchase models where buyers owned depreciating equipment outright. Three-tier pricing structure across premium, standard, and economy levels reflects certification grade differentiation under EU AI Act and NIS2 mandates, with volume scale and after-sales service bundling as secondary drivers. Cost compression in standard-tier network security appliances is intensifying because signature-based detection methods face obsolescence against polymorphic attack vectors. Mid-market enterprises exhibit highest price sensitivity, while classified government facilities demonstrate lowest sensitivity due to national security protocol requirements.
Supply Chain Analysis
Taiwanese and South Korean foundry concentration for advanced sensor processing chips exposes multi-sensor platform manufacturers to lead time volatility and single-source vulnerability. Semiconductor fabrication draws from concentrated geographic supply in Taiwan, South Korea, and the United States, with NVIDIA and Qualcomm inference chips as critical component dependencies. Distribution runs through defense contractor networks in the Washington DC-Baltimore corridor and system integrator channels serving European critical infrastructure operators.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The EU AI Act's risk-classification framework for autonomous systems constitutes a technological and regulatory inflection that will reshape competitive positions across the analysis window. Vendors must architect for algorithmic transparency and human-in-the-loop capabilities or face exclusion from European defense and critical infrastructure procurement.
For Market Incumbents: Shield core defense relationships by accelerating captive machine learning engineering depth before cross-domain talent scarcity worsens product development cycles. Prioritize certification investment for EU AI Act high-risk system compliance to lock out non-conforming rivals from NATO modernization contracts. Consolidate position through backward integration into sensor manufacturing rather than relying on contracted semiconductor supply. For New Entrants and Emerging Players: Managed detection service gaps in healthcare IoT convergence represent the most penetrable white-space, as FDA cybersecurity requirements extend threat detection procurement from IT departments into clinical engineering budgets with less entrenched vendor relationships. Target Indian smart city and port modernization programs under CEA guidelines for first-mover positioning in greenfield multi-sensor fusion deployments. Pursue outcome-based contracting structures that displace capital purchase models in defense agencies. For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across edge AI hardware deployment models as sovereign finance and defense end-uses demand sub-100ms latency without cloud data egress. Acquisition targets should exhibit captive cross-domain engineering expertise spanning RF sensor physics, machine learning operations, and air-gapped network architecture. Watch algorithmic audit trail capabilities as the inflection indicator separating EU-conforming from export-optimized vendor tiers.| Strategic Initiative | Industry Significance |
|---|---|
| EU AI Act Certification Investment | Algorithmic transparency requirements under EU AI Act create defensible moats for compliant vendors in European defense procurement. |
| Edge AI Hardware Deployment | NVIDIA and Qualcomm inference chips enable sovereign deployment options for defense agencies with data residency mandates. |
| Multi-Sensor Fusion Platform Development | NATO unified thermal-radar-cyber specifications consolidate demand pools around integrated perimeter defense architectures. |
| Managed Detection Service Expansion | Outcome-based contracting structures at UK Ministry of Defence displace capital purchase models with recurring revenue streams. |
| Healthcare IoT Security Integration | FDA cybersecurity requirements for connected medical devices extend threat detection into clinical engineering budgets. |
Study Parameters
A standing panel of defense procurement officers, critical infrastructure security directors, machine learning engineering leads, and system integration specialists provided ongoing calibration throughout the research process. Primary interviews combined with secondary validation against SEC filings, EU regulatory databases, NATO procurement disclosures, and hyperscaler capex reports. Bottom-up segment sizing triangulated against top-down macroeconomic indicators to ensure consistency across the analysis window.
Consistency checks validated volume and value outputs against external benchmarks including defense budget appropriations, critical infrastructure protection spending disclosures, and technology vendor revenue segmentations. The analytical framework modeled deployment topology, end-user vertical, technology architecture, and regional regulatory cluster dimensions across the projection horizon. CAGRs derived from segment-level growth trajectory analysis incorporating NATO modernization timelines, NIS2 implementation schedules, and edge AI adoption curves in financial services.
Forecasts assume regulatory continuity in EU AI Act and NIS2 implementation; material policy shifts would require re-modeling across European defense and critical infrastructure segments. Semiconductor supply concentration and cross-border certification reciprocity agreements represent specific risk factors that could revise projections. Practitioners should keep alternative scenarios live as EU-US regulatory divergence and foundry capacity allocation evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Speed Limit Radar Signs Market
Security and Surveillance
Europe Border Security Market
Security and Surveillance
Urban Security Screening Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Security Inspection Market
Security and Surveillance
Global Security Orchestration Market
Security and Surveillance
Global Physical Security Software Market
Security and Surveillance
Mass Transit Security Market
Security and Surveillance
Manned Guarding Services Market
Security and Surveillance
Ballistic Protection Scanners Market
Security and Surveillance
Specialized Threat Analysis and Protection Market
Security and Surveillance
Security Intelligence Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Night Vision Scopes Market
Security and Surveillance
Global Security Advisory Services Market
Security and Surveillance
Baggage Scanner Market