
 Counter Cyberterrorism Market | 2026-2036
Counter Cyberterrorism Market Size, Share, and Industry Trends Forecast 2026-2036
Counter Cyberterrorism Market Outlook
Modular bundling of endpoint detection with threat intelligence feeds is shifting how enterprise buyers evaluate vendor portfolios. Palo Alto Networks leverages its platform consolidation strategy to capture multi-year government contracts. CrowdStrike Holdings sustains its cloud-native architecture as a differentiation point against legacy appliance vendors. Cisco Systems anchors its position through deep integration with existing network infrastructure deployments.
Counter cyberterrorism encompasses the technologies, protocols, and operational frameworks designed to prevent, detect, and neutralize politically motivated cyberattacks against critical systems, typically operating across sub-100 millisecond response windows for automated threat containment. Its primary commercial purpose centers on maintaining continuity for infrastructure operators facing advanced persistent threats from state-affiliated actors. The solution segment clusters around incident response platforms and AI-enhanced intrusion detection, where margin pools deepen as managed detection services displace standalone product sales. Deployment patterns favor hybrid architectures, reflecting regulatory data-sovereignty requirements that resist full cloud migration in defense and intelligence contexts.
The U.S. Cybersecurity and Infrastructure Security Agency, the EU Agency for Cybersecurity, and the UK National Cyber Security Centre collectively shape procurement standards through mandatory incident reporting timelines and certified product evaluation schemes. These frameworks elevate compliance costs for entrants while embedding preferred vendors into national supply chains. Stakeholders must weigh the strategic trade-off between platform consolidation and vendor diversity as supply chain integrity audits tighten across defense-relevant technology tiers.
Market Dynamics
Integrated threat detection platforms are compressing procurement cycles as NATO member states mandate sub-100 millisecond automated response capabilities for critical infrastructure protection.
Growth Catalysts
- EU NIS2 Directive:Mandatory incident reporting timelines and baseline cybersecurity obligations for critical infrastructure operators are accelerating replacement of legacy monitoring stacks across energy and transport sectors.
- Cloud-native architectures:Government agencies are prioritizing elastic compute deployments that unify endpoint detection with real-time threat intelligence feeds, reducing integration overhead.
- Federal cyber defense budgets:United States appropriations for civilian infrastructure protection are creating concentrated demand at the intersection of public procurement and private critical asset ownership.
Market Restraints
- Semiconductor supply concentration:Specialized ASICs for packet inspection and encryption acceleration face single-source dependency on Taiwan-based foundries, exposing hardware refresh timelines to geopolitical disruption.
- Data sovereignty compliance costs:Hybrid deployment mandates from defense and intelligence agencies prevent full cloud migration, forcing redundant infrastructure investment across sovereign jurisdictions.
- Legacy appliance stranded assets:Existing perimeter firewall investments in financial services and manufacturing carry depreciation schedules that delay platform consolidation decisions.
Strategic Opportunities
- Managed detection services:Security operations center outsourcing is displacing standalone product sales as mid-sized infrastructure operators lack in-house threat hunting expertise.
- AI-enhanced forensics convergence:Large language model integration with behavioral analytics is creating new service tiers for post-incident attribution and evidence preservation.
- UK National Cyber Security Centre certification:Product evaluation schemes are embedding preferred vendors into national supply chains with multi-year framework agreements.
Industry Challenges
- Cleared personnel scarcity:Security clearance processing backlogs in defense-relevant technology tiers constrain deployment velocity for classified network protection contracts.
- Supply chain integrity audits:Tiered vendor verification requirements are lengthening procurement cycles as buyers demand hardware provenance documentation through component level.
- Interoperability fragmentation:Proprietary threat intelligence formats impede correlation across multi-vendor environments, forcing costly normalization layer development.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Counter Cyberterrorism Market |
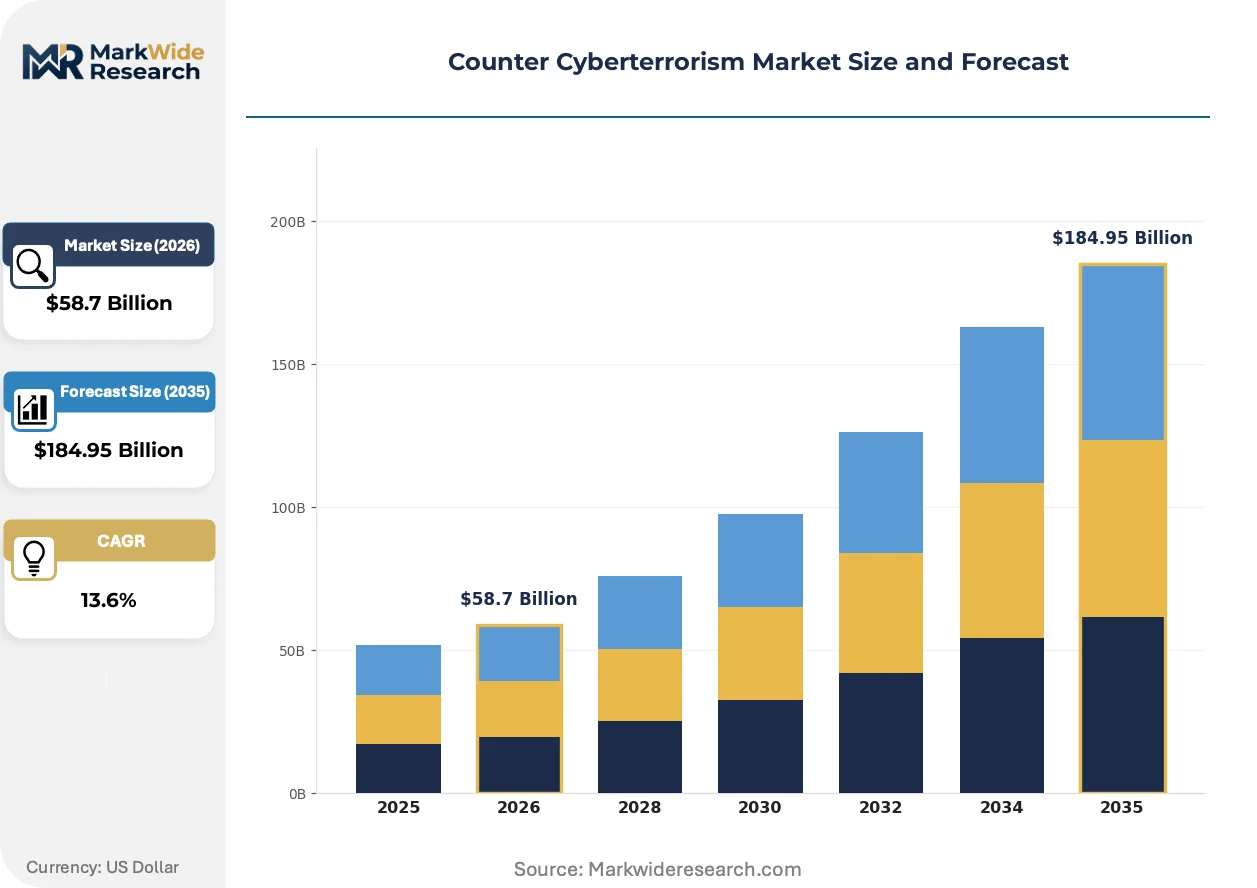
| Market Size in 2026 | $58.7 Billion |
| Market Size in 2035 | $184.95 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
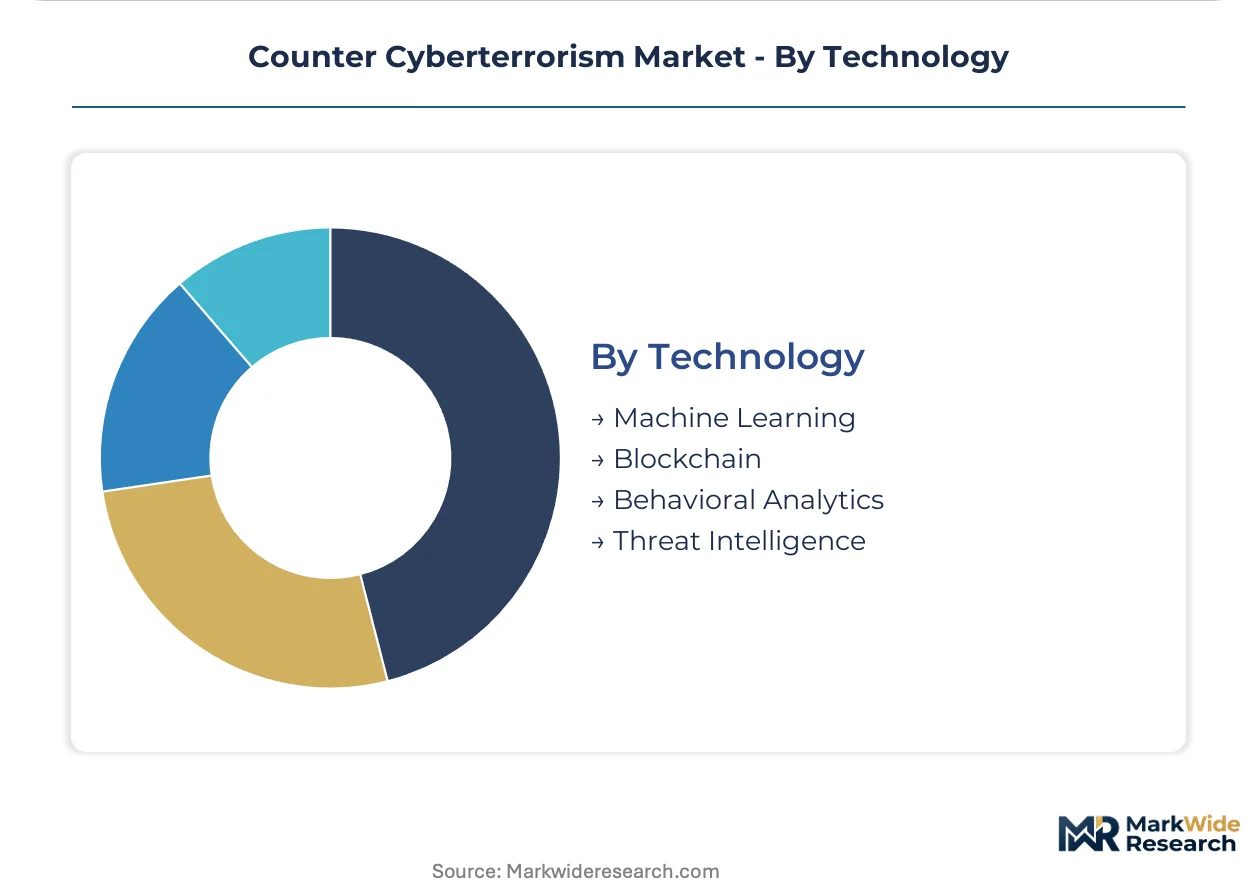
| Segmentation | Solution: Intrusion Detection Systems, Firewalls, Encryption Software, Incident Response Solutions Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government Agencies, Financial Institutions, Telecommunications, Utilities Technology: Machine Learning, Blockchain, Behavioral Analytics, Threat Intelligence |
| Companies Covered | Palo Alto Networks, Cisco Systems, CrowdStrike Holdings, Fortinet, Microsoft Corporation, Lockheed Martin, Raytheon Technologies, IBM Corporation, BAE Systems, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Counter Cyberterrorism Market Strategic Shifts
Zero-trust network architectures are dissolving perimeter-based security models. Artificial intelligence inference at the edge is compressing detection-to-containment intervals. Sovereign cloud requirements are fragmenting vendor consolidation strategies.
Confidential computing is decentralizing sensitive data processing away from centralized cloud regions. Defense agencies in Germany and Australia are deploying hardware-based trusted execution environments for classified workload isolation. This architecture is decentralizing threat analytics across distributed nodes while maintaining cryptographic attestation chains.
The EU AI Act imposes conformity assessments on automated decision systems used for cyber threat response. Critical infrastructure operators must document algorithmic transparency and human oversight protocols before deploying autonomous containment actions. Financial services institutions in France and the Netherlands are front-loading compliance investment to secure early mover accreditation.
Enterprise buyers are unbundling managed detection from incident response retainers. Energy utilities and healthcare systems are negotiating usage-based pricing for forensic investigation hours rather than prepaid annual blocks. This pattern is most visible in United States federal contractor ecosystems where budget flexibility clauses accommodate unpredictable breach response intensity.
Counter Cyberterrorism Market Segmentation

Counter cyberterrorism procurement splits across four dimensions that determine compliance burden and integration complexity. Certification requirements from CISA, ENISA, and NCSC vary sharply by solution type and deployment architecture, reshaping vendor qualification timelines.
Solution:
ENISA certification schemes and CISA's Continuous Diagnostics and Mitigation program impose divergent evaluation criteria across solution categories, with hardware-intensive segments facing longer approval cycles than software-only offerings.
- Intrusion Detection Systems:Network traffic analysis engines with deep packet inspection capabilities process terabit-scale flows in carrier environments. Energy utilities in Germany and transport operators in the United Kingdom are replacing signature-based appliances with AI-enhanced alternatives to meet NIS2-mandated detection timelines.
- Firewalls:Next-generation perimeter controls integrate application-layer inspection with zero-trust policy enforcement. United States federal contractors prioritize FedRAMP-authorized cloud firewall services over on-premises hardware refresh cycles.
- Encryption Software:Quantum-resistant algorithm implementations for data-at-rest and in-transit protection.
- Incident Response Solutions:Digital forensics platforms with chain-of-custody documentation for judicial proceedings.
Leading the category by volume: Intrusion Detection Systems. Growing fastest: Incident Response Solutions.
Deployment:
Cost tier stratification separates sovereign-mandated infrastructure investments from elastic consumption models, with hybrid architectures commanding premium pricing due to dual-environment complexity.
- Hybrid:Split workloads between classified on-premises enclaves and unclassified cloud analytics, requiring cryptographic boundary controls. Defense agencies in Australia and intelligence services in France deploy hardware security modules for cross-domain data transfer, creating specialized integration service demand.
- Managed Services:Outsourced security operations center functions with defined mean-time-to-response contracts. Mid-sized European utilities lacking cleared personnel are contracting MDR providers for 24/7 threat hunting coverage.
- On-Premises:Air-gapped or sovereign-network-only deployments for classified workloads.
- Cloud-Based:Elastic compute for non-sensitive threat intelligence correlation and sandboxing.
Expanding most quickly: Managed Services. Dominating current procurement value: Hybrid.
End User:
Application criticality determines response window mandates, with operators of essential services facing stricter regulatory penalties than commercial sectors for equivalent breach severity.
- Government Agencies:Civilian and defense departments with classified network segmentation requirements. United States CISA and United Kingdom NCSC procurement frameworks are consolidating vendor pools through multi-year enterprise licensing agreements.
- Utilities:Electricity, water, and gas distribution operators designated as critical infrastructure under NIS2 and CISA directives. German transmission system operators are accelerating OT security investment following the 2022 pipeline sabotage investigations.
- Financial Institutions:Banks and payment processors with SWIFT network security obligations.
- Telecommunications:5G core network operators subject to supply chain integrity screening.
Commanding largest budget allocation: Government Agencies. Steepest expansion trajectory: Utilities.
Technology:
Supply concentration in AI training infrastructure and specialized silicon is concentrating vendor partnerships around cloud hyperscalers and defense primes with captive compute access.
- Machine Learning:Supervised and unsupervised models for anomaly detection in network behavior. Behavioral classifiers trained on classified threat data at United States national laboratories are licensed exclusively to cleared contractors.
- Threat Intelligence:Curated indicator feeds with attribution context from government and commercial sources. Financial services institutions in the Netherlands subscribe to sector-specific information sharing and analysis centers for fraud pattern correlation.
- Behavioral Analytics:User and entity behavior analytics for insider threat detection.
- Blockchain:Distributed ledger for immutable audit trails and software supply chain verification.
Highest R&D investment concentration: Machine Learning. Gaining share fastest: Threat Intelligence.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Defense technology parks and cyber innovation hubs concentrate procurement authority across NATO economies. Special economic zones in Tallinn, Tel Aviv, and Maryland create tax-advantaged corridors for classified software development.
United States
Federal cyber defense budgets and CISA procurement frameworks drive concentrated demand from civilian infrastructure operators. The Continuous Diagnostics and Mitigation program mandates FedRAMP-authorized cloud services for federal contractors. Maryland's Fort Meade corridor anchors cleared workforce development for intelligence community vendors.
Germany
Transmission system operators accelerate OT security investment following pipeline sabotage investigations and NIS2 compliance deadlines. The national cybersecurity regulator BSI enforces mandatory incident reporting for critical infrastructure. Bavaria's Munich cluster hosts defense primes developing hardware security modules for cross-domain data transfer.
United Kingdom
NCSC certification schemes embed preferred vendors into national supply chains through multi-year framework agreements. The Cyber Essentials Plus program mandates baseline controls for government suppliers. Cheltenham's GCHQ-adjacent technology park concentrates threat intelligence providers serving Five Eyes partnerships.
France
Intelligence services deploy sovereign cloud architectures with hardware-based trusted execution environments for classified workload isolation. The ANSSI regulator imposes conformity assessments on automated cyber response systems under EU AI Act timelines. Paris-Saclay's research cluster develops quantum-resistant encryption for defense applications.
Australia
Defense agencies mandate hybrid deployments splitting workloads between classified on-premises enclaves and unclassified cloud analytics. The Australian Cyber Security Centre shapes procurement standards for Five Eyes interoperability. Canberra's defense precinct concentrates cleared contractors developing cryptographic boundary controls.
Counter Cyberterrorism Market Competitive Environment
Diversified conglomerates compete with focused pure-play specialists across segmented procurement channels. Platform consolidation strategies dominate federal contracting, while cloud-native architectures capture mid-market managed detection demand. Three archetypes define competitive positioning: integrated platform vendors, threat intelligence specialists, and defense-prime system integrators. M&A activity concentrates around AI-enhanced forensics capabilities, with strategic partnerships securing semiconductor supply for specialized packet inspection hardware.
Among platform consolidation specialists, Palo Alto Networks and CrowdStrike Holdings occupy positions at opposite ends of the deployment spectrum. Cisco Systems anchors the network-integrated tier through deep infrastructure relationships. Defense-prime capabilities reside with Lockheed Martin and BAE Systems, representing cleared-contractor archetypes serving classified network segmentation requirements.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Cisco Systems |
| CrowdStrike Holdings |
| Fortinet |
| Microsoft Corporation |
| Lockheed Martin |
| Raytheon Technologies |
| IBM Corporation |
| BAE Systems |
| Others |
Value Chain & Pricing Dynamics
United States federal contractors operating under CISA's Continuous Diagnostics and Mitigation program anchor procurement volume, compressing vendor margins through multi-year enterprise licensing agreements that favor subscription-based SaaS tiers over perpetual license models.
Pricing Analysis
Short lead-time premiums dominate hardware procurement, with specialized ASICs for packet inspection commanding 15-25% markups over standard delivery windows. Three-tier pricing structure across FedRAMP-authorized premium services, standard commercial cloud tiers, and economy on-premises appliances reflects certification burden differentiation. Pricing pressure stems from semiconductor foundry concentration in Taiwan, forcing buyers into longer contract lock-ins to secure allocation. Mid-sized European utilities lacking cleared security personnel exhibit highest price sensitivity, while defense primes with captive supply chains demonstrate lowest elasticity.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale demand from United States intelligence community vendors, bypassing distribution intermediaries for classified hardware security modules. Manufacturing concentrates in Taiwan for specialized encryption ASICs, the United States for FedRAMP-authorized cloud infrastructure, and Germany for hardware security module assembly. Raw material dependencies include silicon wafers, rare earth elements for magnetics, and cryptographic-grade random number generation components. Single-source vulnerability in Taiwan-based foundries exposes hardware refresh timelines to geopolitical disruption. Distribution runs through cleared-contractor channels with security clearance requirements at component level.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Vertical integration momentum is accelerating as platform vendors pursue captive ASIC design capabilities to reduce Taiwan foundry dependency and secure supply allocation priority.
For Market Incumbents: Acquire specialized semiconductor design teams to internalize encryption acceleration chip development, reducing exposure to Taiwan foundry queue priority. Consolidate threat intelligence data lakes through exclusive licensing agreements with United States national laboratories, creating proprietary training datasets that emerging cloud-native competitors cannot replicate. FedRAMP authorization backlogs present margin compression risk; accelerate compliance investment to maintain federal contractor eligibility. For New Entrants and Emerging Players: Cloud-native managed detection services represent the most penetrable white-space, as mid-sized European utilities under NIS2 deadlines lack in-house security operations center capabilities. Target usage-based forensic investigation pricing models rather than prepaid annual blocks, mirroring United States federal contractor budget flexibility clauses. Partner with existing cleared-contractor infrastructure providers to bypass security clearance processing backlogs that constrain deployment velocity. For Investors and Strategic Acquirers: The window for entry favors AI-enhanced forensics specialists with large language model integration capabilities, ahead of EU AI Act conformity assessment deadlines that will elevate compliance barriers. Long-term viability hinges on embedding into national supply chains through NCSC, CISA, or ENISA certification schemes. Monitor semiconductor supply allocation announcements from Taiwan-based foundries as the critical inflection signal for hardware-dependent vendor valuations.| Strategic Initiative | Industry Significance |
|---|---|
| ASIC Design Acquisition | Captive encryption chip development reduces Taiwan foundry dependency for United States federal contractors. |
| FedRAMP Authorization Acceleration | Early cloud service authorization secures CISA procurement framework eligibility ahead of compliance backlogs. |
| Threat Intelligence Data Licensing | Exclusive national laboratory dataset access creates proprietary machine learning training moats against competitors. |
| Managed Detection Service Launch | Usage-based pricing models capture mid-sized European utilities facing NIS2 compliance deadlines without cleared personnel. |
| Hardware Security Module Partnership | Cross-domain cryptographic boundary controls address Australian and French sovereign cloud deployment mandates. |
Study Parameters
Document review covered CISA procurement frameworks, ENISA certification schemes, and NCSC product evaluation documentation, complemented by interviews with chief information security officers at critical infrastructure operators, federal contracting officers, threat intelligence platform engineers, and semiconductor supply chain managers. Secondary validation drew from SEC 10-K filings of publicly traded cybersecurity vendors, hyperscaler capex disclosures, and customs data on encryption hardware trade flows. Bottom-up demand modeling from end-user procurement patterns was cross-referenced against top-down market sizing from vendor revenue aggregation.
Historical growth trajectories were cross-referenced against panel input from platform engineering directors and government procurement specialists to calibrate projection assumptions. The analytical framework modeled segmentation across solution type, deployment architecture, end-user vertical, and technology layer throughout the forecast period. CAGRs were derived from regression analysis of federal budget appropriations, NIS2 compliance investment patterns, and threat intelligence platform adoption curves. Industry-specific inputs included cleared personnel pipeline constraints, Taiwan foundry capacity allocation trends, and EU AI Act implementation timelines.
The model holds under sustained NATO defense spending and stable Taiwan semiconductor supply; deviation in geopolitical conflict triggers or export control expansion would shift hardware refresh timelines and cloud migration patterns. Forecasts reflect documented assumptions regarding regulatory enforcement intensity and supply chain integrity audit scope. Periodic stress-testing of base assumptions against foundry allocation announcements and federal budget appropriation cycles is recommended.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Critical Infrastructure Protection
Global Airport and Marine Port Security Market
Critical Infrastructure Protection
Global Perimeter Protection Market
Critical Infrastructure Protection
Global Threat Intelligence Platform Market
Critical Infrastructure Protection
Threat Lifecycle Services Market
Critical Infrastructure Protection
Europe Pipeline Security Market
Critical Infrastructure Protection
Middle East and Africa Pipeline Security Market
Critical Infrastructure Protection
Utilities Security Market
Critical Infrastructure Protection
Continuous Threat Exposure Management Market
Critical Infrastructure Protection
Tele Protection Market
Critical Infrastructure Protection
GCC Protective Relay Market
Critical Infrastructure Protection
Latin America Public Infrastructure Safety Market
Critical Infrastructure Protection
Smart Sandbag Market
Critical Infrastructure Protection
Europe Tank Protection Market
Critical Infrastructure Protection
Insider Threat Protection Market
Critical Infrastructure Protection
Asia-Pacific Public Infrastructure Safety Market
Critical Infrastructure Protection
Blast Resistant and Bulletproof Buildings Market