
 Cyber Security in Energy Market | 2026-2036
Cyber Security in Energy Market Size, Share, and Industry Trends Forecast 2026-2036
Cyber Security in Energy Market Outlook
Subscription-based managed detection and response is repositioning how energy operators consume cyber security, shifting capital expenditure to recurring operational contracts. Cisco leverages its industrial networking footprint to embed security directly into utility control system architectures. Darktrace specializes in self-learning AI that maps operational technology environments without predefined threat signatures. Siemens anchors its competitive stance through deep integration between grid automation hardware and native security software stacks.
Cyber security in energy encompasses protective technologies, governance frameworks, and operational procedures engineered to safeguard generation, transmission, and distribution systems from unauthorized access, data exfiltration, or operational disruption. These systems deploy protocol-aware deep packet inspection capable of parsing Modbus, DNP3, and IEC 61850 traffic at sub-millisecond latency to prevent manipulation of breaker commands or setpoint alterations. Managed Services commands the largest revenue share as utilities outsource round-the-clock security operations center staffing rather than building scarce in-house expertise. Cloud-Based deployment represents the fastest-expanding segment, though Hybrid architectures dominate among European operators constrained by GDPR data residency requirements and NIS2 directive localization mandates.
The Federal Energy Regulatory Commission enforces NERC CIP standards with substantial penalties for non-compliance, compelling North American utilities to maintain continuous asset inventory and access logging. EMA and national regulators across Europe implement NIS2 and sector-specific directives that mandate incident reporting timelines and supply chain security assessments for critical energy entities. Stakeholders must weigh the trade-off between cloud-native security agility and the operational resilience requirements of air-gapped or segmented legacy control environments as adversaries refine techniques targeting energy infrastructure specifically.
Market Dynamics
Subscription-based managed detection and response services are compressing capital expenditure cycles into recurring operational contracts across power generation and distribution networks. This structural shift forces incumbent security vendors to reprice perpetual licenses against consumption-based alternatives while utilities defer large-scale infrastructure builds.
Growth Catalysts
- NERC CIP Enforcement:The Federal Energy Regulatory Commission mandates continuous asset inventory and access logging for bulk electric system operators. Penalties for non-compliance compel North American utilities to maintain 24/7 security operations center coverage.
- Legacy Control System Exposure:Operational technology environments running decades-old SCADA and DCS architectures present attack surfaces that adversaries actively probe. Asset owners prioritize protocol-aware monitoring for Modbus and DNP3 traffic.
- Cloud-Native Security Agility:European operators constrained by GDPR data residency requirements adopt hybrid deployment models that segment sensitive control data from cloud analytics. NIS2 directive localization mandates accelerate this architecture.
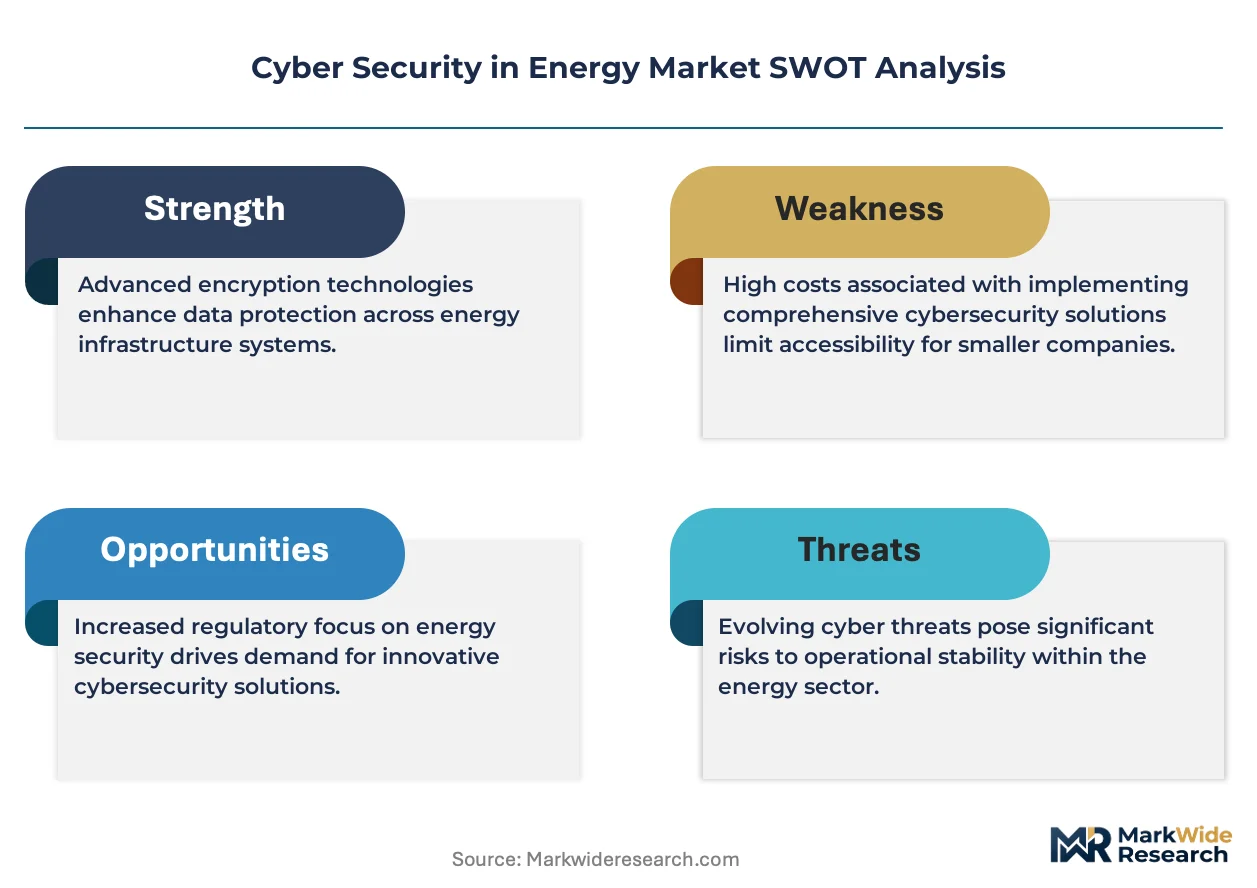
Market Restraints
- Operational Technology Expertise Scarcity:The shallow talent pool for engineers fluent in both industrial control protocols and modern threat detection limits deployment velocity. Utilities compete with technology firms for scarce cybersecurity professionals.
- Air-Gapped Environment Complexity:Segmented legacy networks resist cloud-native security tooling without expensive gateway infrastructure. The cost of bridging operational technology islands to security analytics platforms constrains budget allocation.
- Hardware-Software Integration Lock-In:Grid automation vendors bundle proprietary security modules with switchgear and protection relays. This vertical integration limits third-party solution penetration in brownfield installations.
Strategic Opportunities
- Japan Critical Infrastructure Hardening:METI directives targeting power grid resilience create demand for AI-driven anomaly detection in nuclear and thermal generation facilities. Japanese utilities seek vendors with IEC 61850 expertise.
- Convergence of IT and OT Security Stacks:Unified visibility platforms that correlate enterprise network threats with control system anomalies enable faster incident response. This technology pairing reduces mean-time-to-detection for targeted intrusions.
- Managed Security Service Provider Expansion:German distribution system operators outsource security operations to specialized providers rather than building in-house capabilities. The NIS2 directive's incident reporting timelines accelerate this channel shift.
Industry Challenges
- Industrial Protocol Parsing Latency:Deep packet inspection engines must process Modbus and DNP3 traffic at sub-millisecond speeds to avoid disrupting real-time control loops. Engineering teams struggle to tune detection sensitivity without generating false positives that trigger unnecessary breaker lockouts.
- Cross-Domain Certification Burden:Solutions require simultaneous approval under IEC 62351 for power system communications and NERC CIP for North American asset protection. The sequential validation timeline extends sales cycles by 8-14 months.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cyber Security in Energy Market |
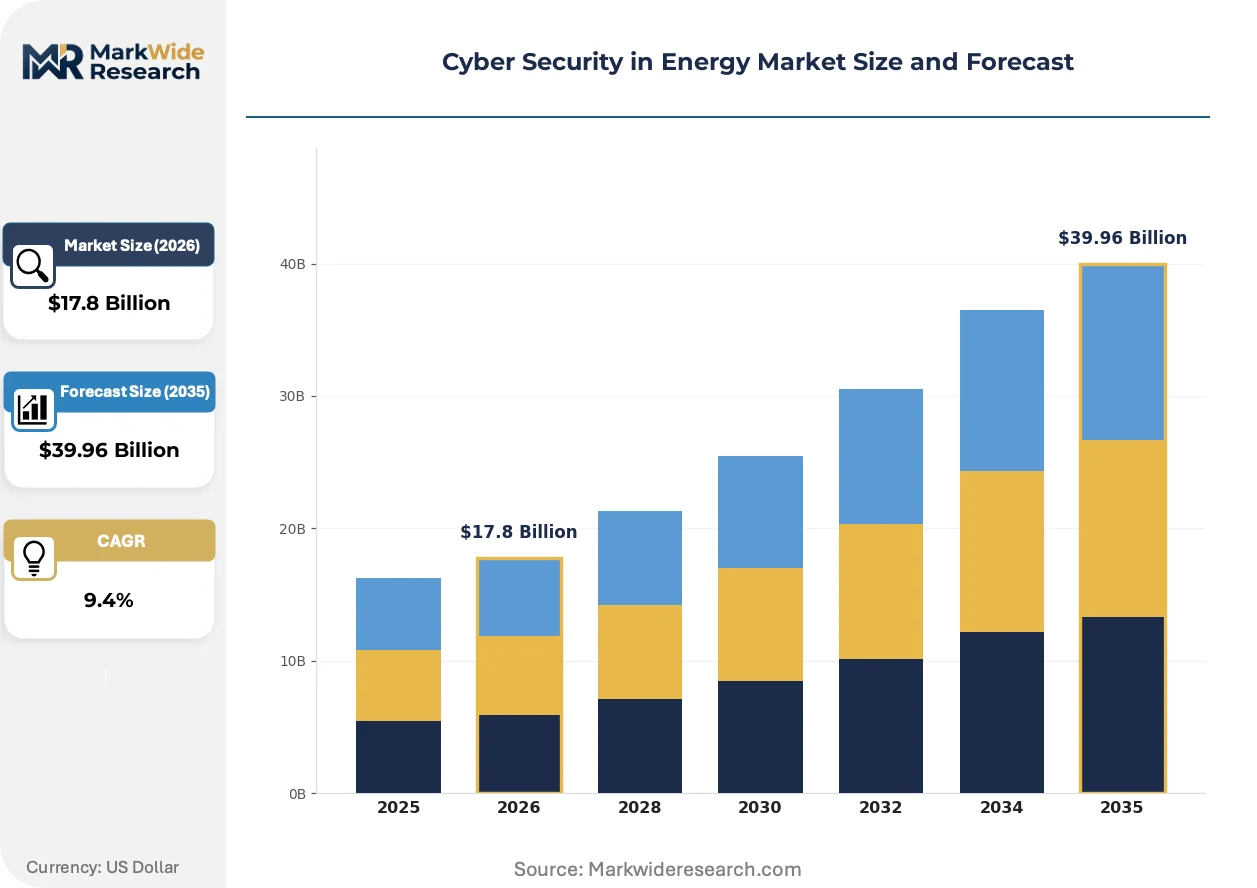
| Market Size in 2026 | $17.8 Billion |
| Market Size in 2035 | $39.96 Billion |
| CAGR (2026 – 2036) | 9.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Services, Consulting, Incident Response, Compliance Audits Deployment: On-Premises, Cloud-Based, Hybrid, Edge Computing End User: Utilities, Renewable Energy Providers, Oil & Gas Companies, Power Generation Firms Technology: Firewall, Intrusion Detection Systems, Antivirus Software, Encryption |
| Companies Covered | Cisco, Trend Micro, Siemens, Darktrace, CrowdStrike, Palo Alto Networks, Check Point Software Technologies, Cloudflare, Fortinet, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cyber Security in Energy Market Strategic Shifts
Self-learning artificial intelligence is displacing signature-based detection in operational technology environments where threat patterns evolve faster than human analysts can codify rules. This capability gap drives procurement decisions toward autonomous systems that map network topology without predefined baselines.
Machine learning models trained on industrial control traffic are overtaking static anomaly detection in substation and generation facility deployments. European transmission system operators pilot these systems to identify novel attack sequences against IEC 61850 GOOSE messaging. The technology is compressing vendor differentiation around historical threat intelligence repositories.
NIS2 directive implementation across European Union member states mandates supply chain security assessments for critical energy entities. The regulation forces utilities to audit vendor software development practices and component provenance before procurement approval. German and French distribution operators now require security attestations as contractual preconditions.
Energy buyers increasingly unbundle security software from hardware procurement cycles. United States power generators negotiate standalone managed detection contracts that renew annually rather than aligning with multi-year capital equipment refreshes. This behavioral shift pressures automation vendors to decouple security licensing from switchgear and protection relay sales.
Cyber Security in Energy Market Segmentation
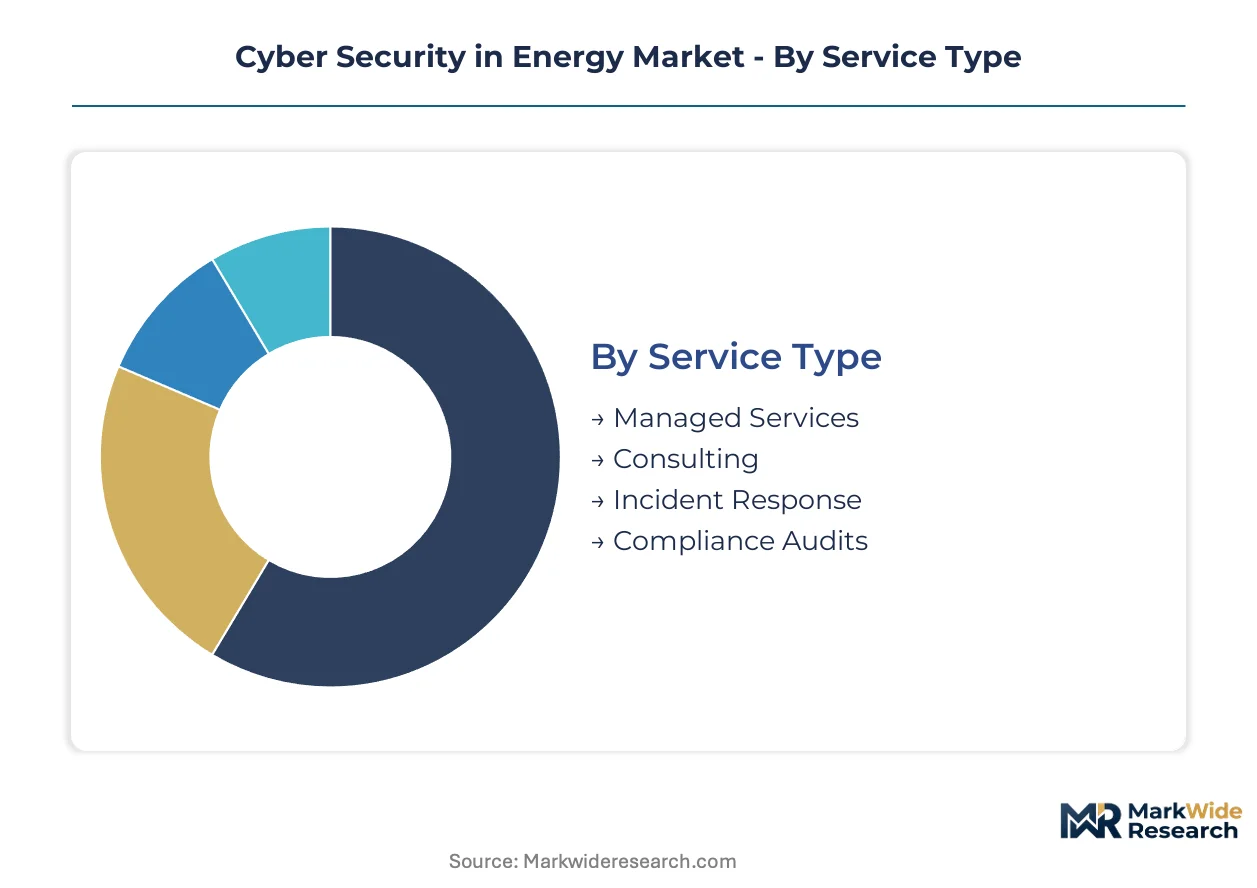
Energy operators segment cyber security procurement around operational constraints rather than enterprise IT preferences. Control system latency requirements, regulatory jurisdiction, and legacy infrastructure age determine solution architecture more than cost optimization alone.
Service Type:
Procurement patterns follow the scarcity of engineers fluent in both industrial protocols and threat intelligence, pushing utilities toward outsourced models.
- Managed Services:Round-the-clock security operations center staffing delivered under recurring contracts. North American utilities facing NERC CIP enforcement outsource continuous monitoring to avoid penalty exposure from compliance gaps. Volume sits with Managed Services; growth tilts toward Incident Response.
- Consulting:Advisory engagements covering control system architecture review and regulatory readiness assessment. German distribution operators engage specialists for NIS2 directive preparation ahead of enforcement deadlines.
- Incident Response:Retained breach containment capabilities with industrial control system expertise. Japanese thermal generation facilities contract specialized providers for targeted intrusion scenarios against SCADA environments.
- Compliance Audits:Systematic verification of asset inventory, access logging, and patch management against regulatory standards. United States bulk electric system operators commission annual assessments to satisfy FERC documentation requirements.
Contract structures favor recurring operational expenditure over perpetual licenses; Incident Response retains fastest expansion trajectory as adversary sophistication escalates.
Deployment:
Architecture selection hinges on data residency obligations and the operational resilience requirements of segmented control networks.
- Hybrid:Segmented deployment preserving sensitive control data on-premises while routing analytics to cloud infrastructure. European operators constrained by GDPR localization mandates and NIS2 directive requirements adopt this architecture most densely.
- Cloud-Based:Fully offloaded security analytics with API integration into operational technology environments. Renewable energy providers with newer digital infrastructure and lighter regulatory burden lead adoption here.
- On-Premises:Air-gapped or physically isolated security stacks within operational technology boundaries. Nuclear generation facilities and critical substations mandate this deployment for breaker command protection.
- Edge Computing:Distributed processing at substation or generation unit level to minimize latency for real-time threat detection. Pilot deployments focus on IEC 61850 GOOSE message inspection in transmission networks.
Hybrid architectures command current procurement volume; Cloud-Based deployment climbs fastest as European operators navigate regulatory clarity on cross-border data flows.
End User:
Threat exposure and regulatory scrutiny intensity vary sharply across energy subsectors, fragmenting solution requirements.
- Utilities:Integrated generation, transmission, and distribution operators managing legacy SCADA and modern AMI infrastructure simultaneously. United States investor-owned utilities balance NERC CIP compliance across geographically dispersed asset bases.
- Power Generation Firms:Merchant generators and independent power producers securing distributed control systems and turbine control platforms. Combined-cycle gas facilities prioritize protocol-aware monitoring for Modbus TCP traffic.
- Renewable Energy Providers:Wind and solar operators with geographically dispersed generation assets connected via wireless and satellite links. Remote monitoring requirements drive demand for lightweight, satellite-tolerant security agents.
- Oil & Gas Companies:Upstream and midstream operators securing pipeline SCADA and terminal automation systems. Midstream compressor stations face targeted intrusion campaigns against flow control systems.
Utilities dominate current expenditure; Renewable Energy Providers expand most quickly as distributed generation capacity accelerates and attack surfaces proliferate across remote sites.
Technology:
Performance requirements for industrial control environments constrain technology selection more than feature breadth.
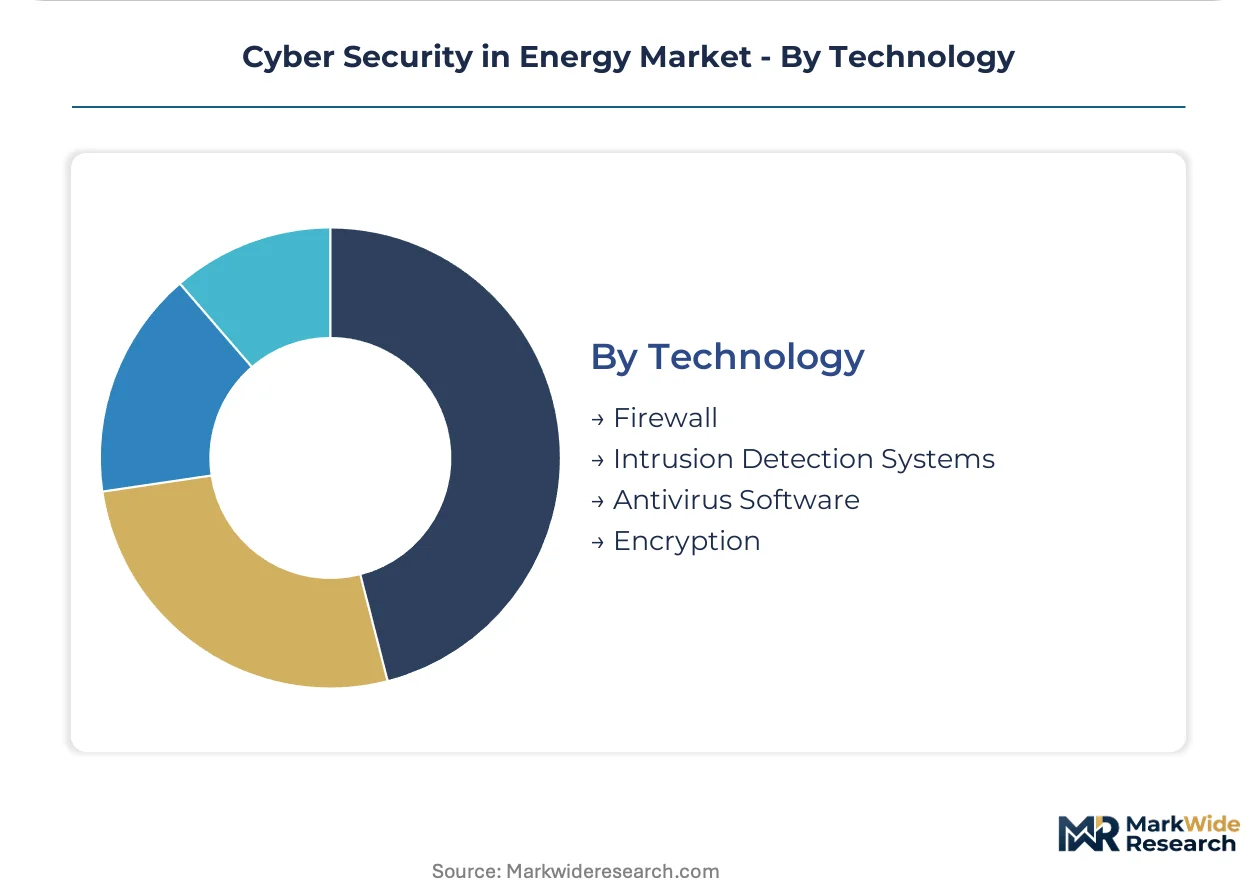
- Intrusion Detection Systems:Protocol-aware deep packet inspection engines parsing Modbus, DNP3, and IEC 61850 at sub-millisecond latency. Transmission substations deploy these for manipulation detection against breaker commands and setpoint alterations.
- Firewall:Industrial-grade network segmentation enforcing whitelist-based communication policies between control system zones. Generation facilities segment safety systems from corporate networks through hardware-enforced boundaries.
- Encryption:Cryptographic protection for data at rest and in transit across operational technology networks. European operators implement IEC 62351-compliant encryption for power system communications per grid code requirements.
- Antivirus Software:Endpoint protection adapted for embedded control system environments with limited processing headroom. Engineering workstations in brownfield installations retain this technology despite signature update challenges.
Intrusion Detection Systems anchor procurement volume; Encryption gains share fastest as NIS2 and similar mandates harden data protection requirements across critical infrastructure.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Cyber security solution production concentrates in technology hubs while consumption patterns follow critical infrastructure density and regulatory enforcement intensity. Demand clusters where bulk electric systems operate aging control systems under strict compliance mandates.
United States
FERC enforces NERC CIP standards with penalty exposure driving continuous monitoring procurement across investor-owned utilities. Texas and California transmission operators lead deployment of protocol-aware detection for SCADA environments. ERCOT grid hardening initiatives in Houston accelerate managed security service adoption.
Germany
NIS2 directive localization mandates and GDPR data residency requirements shape hybrid deployment architecture preferences. Bavarian distribution system operators outsource security operations to specialized providers ahead of enforcement deadlines. Munich industrial clusters prioritize IEC 62351-compliant encryption for power system communications.
Japan
METI directives targeting nuclear and thermal generation resilience create demand for AI-driven anomaly detection platforms. Tokyo Electric and regional utilities seek vendors with IEC 61850 expertise for substation automation protection. Osaka industrial corridors pilot edge computing deployments for real-time GOOSE message inspection.
United Kingdom
Ofgem oversight and critical national infrastructure designation elevate cyber security procurement priority for National Grid and distribution network operators. London financial-technology crossover talent supports OT security specialist growth. Scottish renewable generation assets drive demand for satellite-tolerant remote monitoring solutions.
France
ANSSI guidance on industrial control system protection complements EU NIS2 implementation for RTE and Enedis network operators. Paris-based engineering consultancies advise on supply chain security assessments now required as contractual preconditions. Lyon nuclear automation clusters maintain air-gapped security stacks for breaker command protection.
Cyber Security in Energy Market Competitive Environment
Capital-heavy industrial automation producers compete with asset-light cyber security pure-plays for utility procurement budgets. Market structure tilts toward consolidation as hardware-software bundling limits third-party penetration in brownfield installations. Three archetypes dominate: networking incumbents embedding security into industrial infrastructure, AI-native specialists offering autonomous threat detection, and managed service providers delivering outsourced SOC capabilities. Incumbents defend position through strategic partnerships with grid equipment manufacturers while challengers pursue technology licensing arrangements to bypass certification bottlenecks.
Among networking-centric incumbents, Cisco leverages its industrial switching footprint to integrate security directly into utility control architectures. Darktrace exemplifies the AI-native specialist archetype with self-learning platforms that map OT environments without predefined signatures. Siemens anchors the automation-integrated tier through native security software stacks bundled with grid hardware. These three occupy distinct competitive positions without direct feature-for-feature substitution.
| Leading Market Players |
|---|
| Cisco |
| Trend Micro |
| Siemens |
| Darktrace |
| CrowdStrike |
| Palo Alto Networks |
| Check Point Software Technologies |
| Cloudflare |
| Fortinet |
| Others |
Value Chain & Pricing Dynamics
Subscription-based managed detection and response services are compressing capital expenditure cycles into recurring operational contracts across power generation and distribution networks. This structural shift forces incumbent security vendors to reprice perpetual licenses against consumption-based alternatives while utilities defer large-scale infrastructure builds.
Pricing Analysis
Margin tightening in managed security services reflects the commoditization of baseline SOC capabilities as CrowdStrike and Palo Alto Networks scale industrial verticals. Three-tier pricing structure across premium, standard, and economy levels segments buyers by incident response SLA guarantees and OT protocol coverage breadth. Cost-down pressure on on-premises deployments accelerates because European utilities face NIS2-mandated supply chain audits that inflate vendor qualification overhead. Renewable energy providers exhibit highest price sensitivity due to distributed asset economics; nuclear operators show least sensitivity given breaker command protection requirements.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale buyer demand for embedded security modules bundled with Siemens and Cisco grid automation hardware. Component manufacturing concentrates in the United States, Germany, and Taiwan for industrial-grade network appliances and specialized OT security chipsets. Supply chains draw from scarce FPGA inventories for low-latency packet inspection engines and IEC 62351-certified encryption modules. Single-source vulnerability in semiconductor fabrication for industrial control system processors constrains delivery timelines. Distribution runs through authorized system integrators with NERC CIP certification rather than open channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Self-learning AI platforms are displacing signature-based detection in operational technology environments where threat patterns evolve faster than human analysts can codify rules.
For Market Incumbents: To counter AI-native specialists eroding detection differentiation, Cisco and Siemens should deepen hardware-software integration through native security stacks bundled with switchgear and protection relays. Certification investment in simultaneous IEC 62351 and NERC CIP validation compresses sales cycles by 8-14 months. Channel control through exclusive distribution agreements with NERC-certified system integrators limits third-party solution penetration in brownfield installations. For New Entrants and Emerging Players: A pricing gap between premium AI-native platforms and economy-tier antivirus solutions creates entry opportunity for mid-market managed detection providers. Japanese thermal generation facilities and German distribution system operators represent the most penetrable geographies given METI and NIS2 compliance deadlines. Go-to-market positioning should emphasize IEC 61850 expertise for substation automation protection, a capability scarce among established IT security vendors. For Investors and Strategic Acquirers: Exit pathways concentrate in strategic acquisitions by industrial automation incumbents seeking OT-native threat detection capabilities. Long-term viability favors vendors with demonstrated deployment in air-gapped environments and proven sub-millisecond latency performance. Monitor NERC CIP penalty enforcement intensity and NIS2 implementation timelines across EU member states as demand inflection indicators.| Strategic Initiative | Industry Significance |
|---|---|
| AI-Native Platform Development | Self-learning systems map OT environments without predefined signatures, compressing mean-time-to-detection for novel attack sequences. |
| Hybrid Deployment Architecture | European utilities adopt segmented models preserving control data on-premises while routing analytics to cloud infrastructure per GDPR mandates. |
| Managed Security Service Expansion | German distribution operators outsource SOC operations to specialized providers rather than building scarce in-house OT expertise. |
| IEC 62351 Certification Investment | Encryption vendors accelerate grid code compliance for power system communications across European transmission networks. |
| Edge Computing Pilot Deployment | Osaka industrial corridors test distributed processing for real-time GOOSE message inspection in substation automation. |
Study Parameters
Trade association data, regulatory filings, and customs records anchored secondary inputs for this cyber security in energy market assessment. Primary interviews with utility CISOs, OT security engineers, grid automation procurement leads, and managed security service provider executives combined with FERC enforcement records, NERC CIP audit documentation, EIA infrastructure databases, and EU NIS2 implementation guidance. Bottom-up triangulation across deployment model, service type, and end-user segment validated top-down market sizing.
Granularity-level modeling segmented the market by service type, deployment architecture, end-user subsector, and technology category across the analysis window. CAGRs derived from utility capital expenditure patterns, renewable generation capacity additions, and regulatory enforcement intensity trajectories. Forecast inputs incorporated NERC CIP penalty schedules, NIS2 directive localization timelines, and industrial protocol adoption curves for IEC 61850 and DNP3.
Inputs from FERC, EMA, and METI regulatory databases were available through the study window; gaps in real-time OT incident reporting introduce uncertainty bands around threat detection demand estimates. Forecasts reflect assumptions regarding NERC CIP enforcement continuity, NIS2 implementation uniformity, and semiconductor supply normalization. Practitioners should monitor penalty announcement frequency, EU member state transposition deadlines, and FPGA lead time indicators for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
France Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Belgium Cybersecurity Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Cyber Security Market
Cybersecurity
Post-Quantum Cryptography Market
Cybersecurity
Data-Centric Security Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Global Managed Detection and Response (MDR) Market