
 Cloud Siem Market | 2026-2036
Cloud Siem Market Size, Share, and Industry Trends Forecast 2026-2036
Cloud Siem Market Analysis
Subscription-based consumption and managed security service provider financing is tilting competitive dynamics toward vendors with capital-efficient delivery models. Microsoft Sentinel leverages its Azure infrastructure to anchor enterprise deployments at scale. Splunk Enterprise Security differentiates through deep data lake integration for complex analytics workloads. Securonix specializes in user and entity behavior analytics within cloud-native architectures.
Cloud SIEM denotes a security information and event management platform delivered via cloud infrastructure, ingesting terabyte-scale log volumes from distributed endpoints, networks, and identity systems for real-time correlation and automated response orchestration. Its primary commercial purpose is to compress mean-time-to-detect and mean-time-to-respond metrics for security operations centers. The deployment dimension shows hybrid cloud configurations capturing the strongest momentum as organizations retain sensitive log processing on-premises while pushing analytics to public tiers. Application-wise, threat detection occupies the largest revenue pool while compliance monitoring exhibits the steepest trajectory driven by cross-border data governance mandates.
The US SEC, EU AI Act, and Germany's BSI IT-Grundschutz standards collectively shape product roadmaps by mandating explainable alerting, audit trail integrity, and sovereign data residency. HIPAA and PCI-DSS enforcement in North America further hardens requirements for healthcare and payment sector deployments. Stakeholders must weigh vendor lock-in risks against the operational velocity gains of native platform integration as procurement criteria evolve beyond feature parity toward architectural resilience.
Market Dynamics
Cross-border data sovereignty mandates are compressing vendor selection timelines while forcing architectural splits between analytics engines and log storage jurisdictions.
Growth Catalysts
- EU AI Act explainability requirements:Financial services firms in Frankfurt and Munich must demonstrate auditable AI-driven threat detection logic, accelerating replacement of opaque on-premises rule engines.
- Automotive supplier migration:Continental and Bosch-tier suppliers across Baden-Württemberg are consolidating fragmented SOC tools into unified cloud-native stacks to satisfy BSI IT-Grundschutz certification audits.
- Terabyte-scale telemetry ingestion:Kubernetes-native log shippers and eBPF-based kernel instrumentation are collapsing data pipeline costs for industrial IoT deployments.
Market Restraints
- Cloud egress cost volatility:Multi-terabyte daily log transfers between regions incur unpredictable bandwidth charges that distort three-year TCO models.
- Hyperscaler concentration risk:Three infrastructure providers control the underlying compute substrate for over seventy percent of managed SIEM deployments.
- Quantum-resistant encryption timeline:NIST post-quantum cryptography standards remain incomplete, freezing long-term data retention architecture decisions.
Strategic Opportunities
- Healthcare provider underpenetration:German university hospitals in Berlin and Heidelberg lack dedicated cloud SOC capacity despite HIPAA-equivalent BDSG compliance obligations.
- Federated learning convergence:Privacy-preserving machine learning across siloed tenant data pools enables collective threat intelligence without raw log centralization.
- BSI certification acceleration:Pre-certified managed security service providers can compress six-month procurement cycles to eight weeks for Mittelstand manufacturers.
Industry Challenges
- SOC analyst skill compression:Tier-1 alert triage automation is eliminating entry-level positions while creating unfilled demand for cloud-native detection engineering expertise.
- Mainframe SIEM integration:German insurance conglomerates with decades-old IBM z/OS transaction logs face prohibitive refactoring costs for structured COBOL event streaming.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud Siem Market |
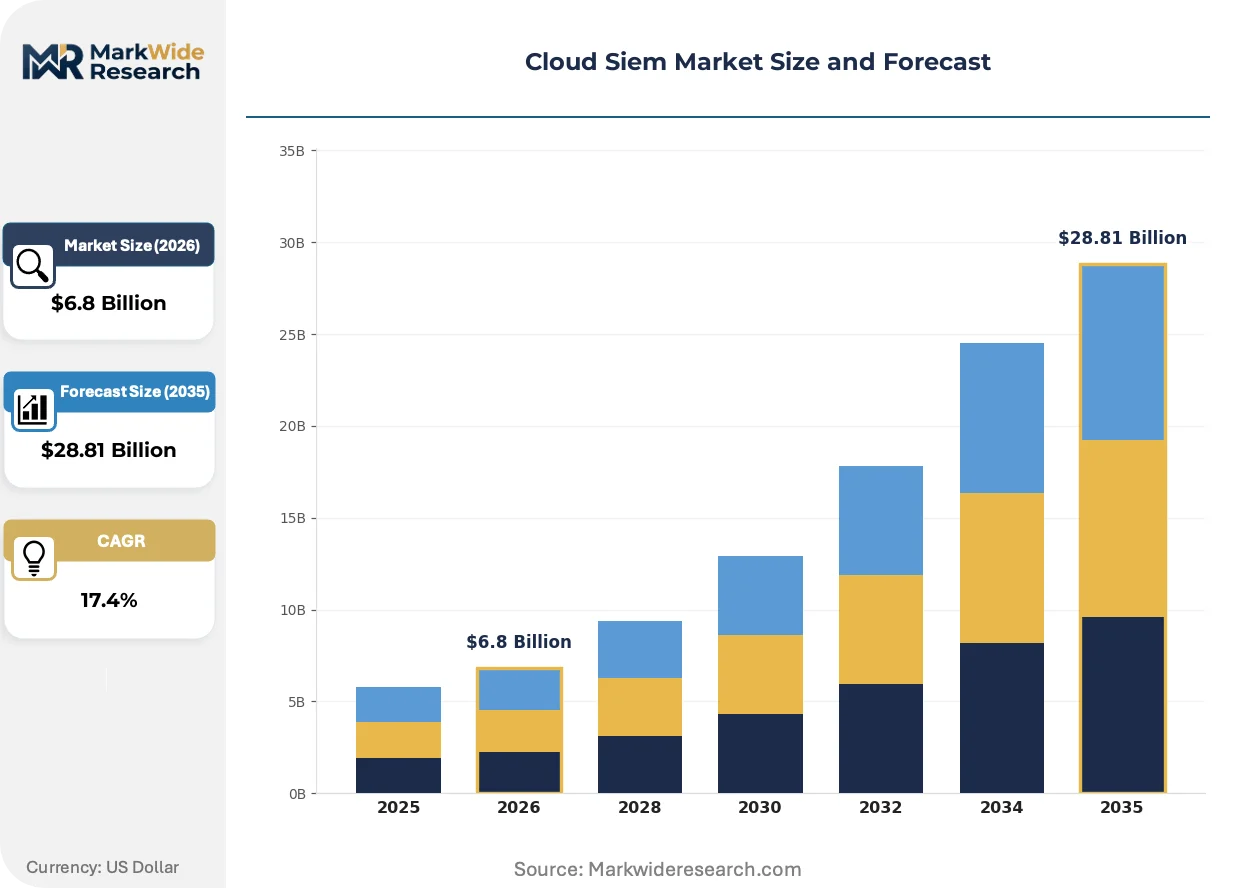
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $28.81 Billion |
| CAGR (2026 – 2036) | 17.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud End User: Enterprises, SMEs, Government Agencies, Educational Institutions Application: Threat Detection, Compliance Monitoring, Incident Response, Data Breach Investigation Service Type: Managed Services, Professional Services, Consulting, Support Services |
| Companies Covered | Microsoft Sentinel, Splunk Enterprise Security, Exabeam Fusion, Securonix, Google Security Operations, Panther, SentinelOne Singularity, Elastic Security, ConnectWise SIEM, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud Siem Market Emerging Trajectories
Detection engineering methodologies are pivoting from signature-based correlation toward behavioral graph analytics that surface lateral movement through identity-layer signals.
Extended detection and response platforms with native SIEM backends are collapsing the standalone security analytics vendor tier. Mid-market enterprises in Bavaria and North Rhine-Westphalia are consolidating endpoint, network, and identity telemetry into single-pane workflows rather than maintaining separate SOC toolchains. This compression is eroding pricing power for point-product vendors lacking adjacent control-plane integration.
Germany's BSI has issued binding guidance requiring sovereign data residency for critical infrastructure operators under the KRITIS framework. Energy utilities and telecommunications providers must now maintain primary log storage within national borders while permitting analytics compute in EU-regional cloud zones. Vendors are responding with partitioned architectures that separate ingestion nodes from processing clusters.
Consumption-based pricing is displacing perpetual licensing as the dominant procurement construct. Large manufacturing groups in Stuttgart and Wolfsburg now negotiate annual commit contracts with burst capacity for quarterly penetration testing windows. This shift transfers infrastructure risk to vendors while compressing customer switching costs.
Cloud Siem Market Segmentation
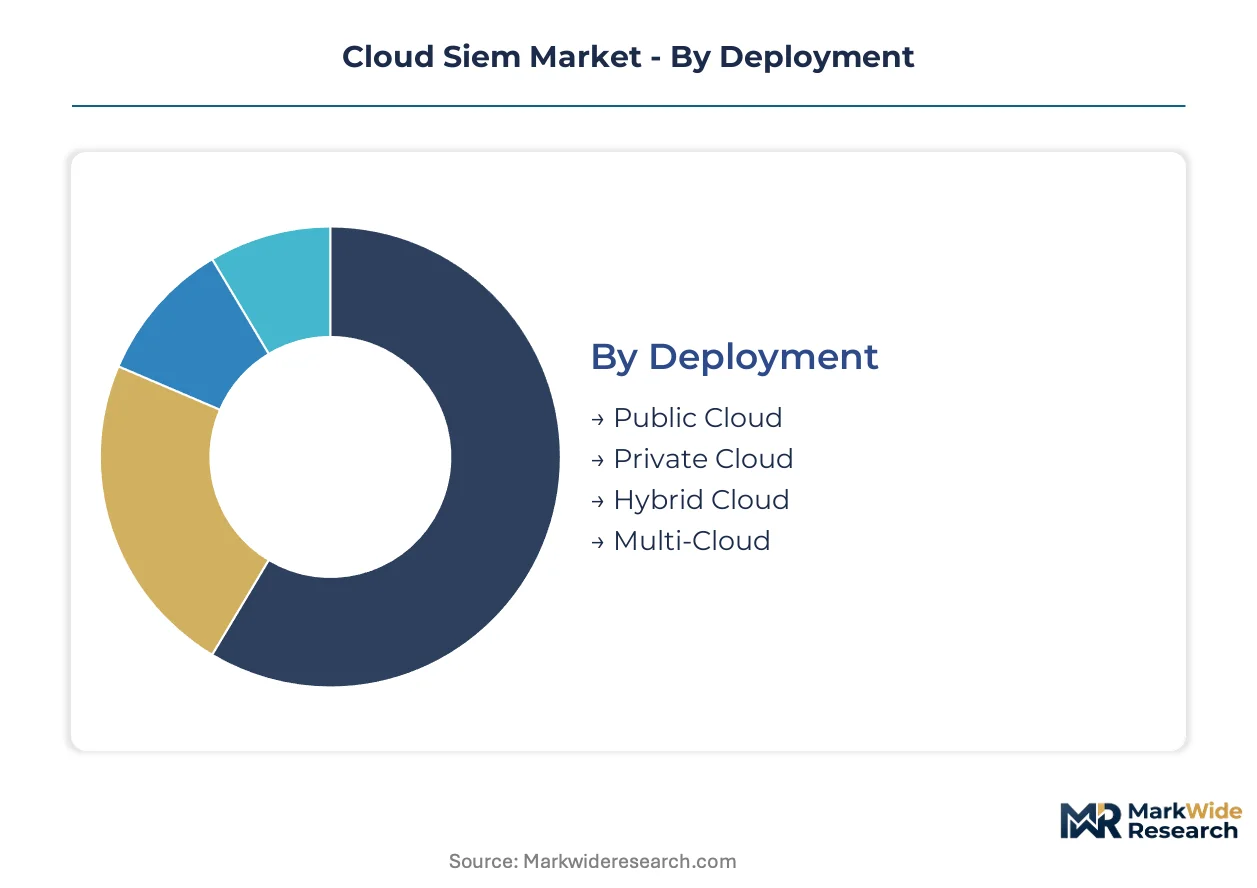
Cloud SIEM procurement patterns diverge sharply across deployment topologies, organizational scale, and service consumption models. Architectural choices directly determine data sovereignty compliance, operational cost structures, and integration complexity for security operations centers.
Deployment:
Cost tier differentiation separates commodity public infrastructure from sovereign-controlled private environments with dedicated compute isolation.
- Hybrid Cloud:Combines on-premises log retention with cloud-based analytics engines, enabling German automotive suppliers to satisfy BSI IT-Grundschutz data residency mandates while accessing elastic processing capacity. Stuttgart-based manufacturers favor this architecture for quarterly penetration testing bursts without permanent infrastructure overprovisioning.
- Public Cloud:Delivers fully managed SIEM through hyperscaler infrastructure with consumption-based metering. North American healthcare systems under HIPAA select public tiers for rapid deployment, though egress bandwidth charges from multi-terabyte daily log transfers create TCO unpredictability.
- Private Cloud:Isolated tenant environments with dedicated hardware stacks for regulated sectors. Frankfurt financial institutions under EU AI Act explainability requirements deploy private nodes for auditable AI-driven threat detection logic.
- Multi-Cloud:Distributed ingestion across AWS, Azure, and GCP regions with unified correlation layers. Mitigates hyperscaler concentration risk but introduces cross-cloud API complexity and fragmented support contracts.
Hybrid Cloud commands the established base. The steepest expansion runs through Multi-Cloud as organizations diversify infrastructure dependencies.
End User:
Customer type stratification reflects divergent security maturity, procurement timelines, and internal SOC staffing levels.
- Enterprises:Global manufacturing conglomerates and financial services groups with dedicated detection engineering teams. German industrial conglomerates in Baden-Württemberg consolidate fragmented SOC tools into unified cloud-native stacks, compressing mean-time-to-detect metrics from hours to minutes.
- Government Agencies:Federal and state entities with classified data handling requirements. US agencies under FISMA and FedRAMP mandates select certified cloud environments with immutable audit trails for forensic investigation retention.
- SMEs:Mid-market manufacturers and professional services firms lacking dedicated security personnel. Bavarian Mittelstand companies increasingly outsource SIEM operations to managed security service providers, trading capital expenditure for predictable operational costs.
- Educational Institutions:University hospitals and research networks with heterogeneous IT estates. Berlin and Heidelberg medical centers face HIPAA-equivalent BDSG compliance obligations without dedicated cloud SOC capacity, creating underpenetrated demand pools.
Enterprises anchor current revenue concentration. Educational Institutions are gaining share fastest as research networks modernize legacy logging infrastructure.
Application:
Functional use case priority determines data pipeline architecture, correlation rule complexity, and retention policy design.
- Threat Detection:Real-time correlation of identity-layer signals, network flows, and endpoint telemetry through behavioral graph analytics. Detects lateral movement patterns that signature-based rule engines miss, driving replacement cycles in Frankfurt banking security operations centers.
- Compliance Monitoring:Automated audit trail generation and cross-border data governance enforcement. Steepest trajectory segment as EU AI Act, SEC cybersecurity disclosure rules, and Germany's KRITIS framework mandate explainable alerting with sovereign data residency.
- Incident Response:Orchestrated containment workflows with automated playbook execution. Reduces mean-time-to-respond through SOAR platform integration, particularly valued by automotive suppliers facing supply chain ransomware exposure.
- Data Breach Investigation:Forensic log reconstruction and timeline analysis for post-incident attribution. Requires immutable storage with quantum-resistant encryption preparation, freezing long-term architecture decisions pending NIST standard finalization.
Threat Detection retains the largest revenue pool. Compliance Monitoring exhibits the most rapid climb as regulatory mandates multiply across jurisdictions.
Service Type:
Margin structure varies dramatically between high-touch professional engagements and scalable managed service contracts.
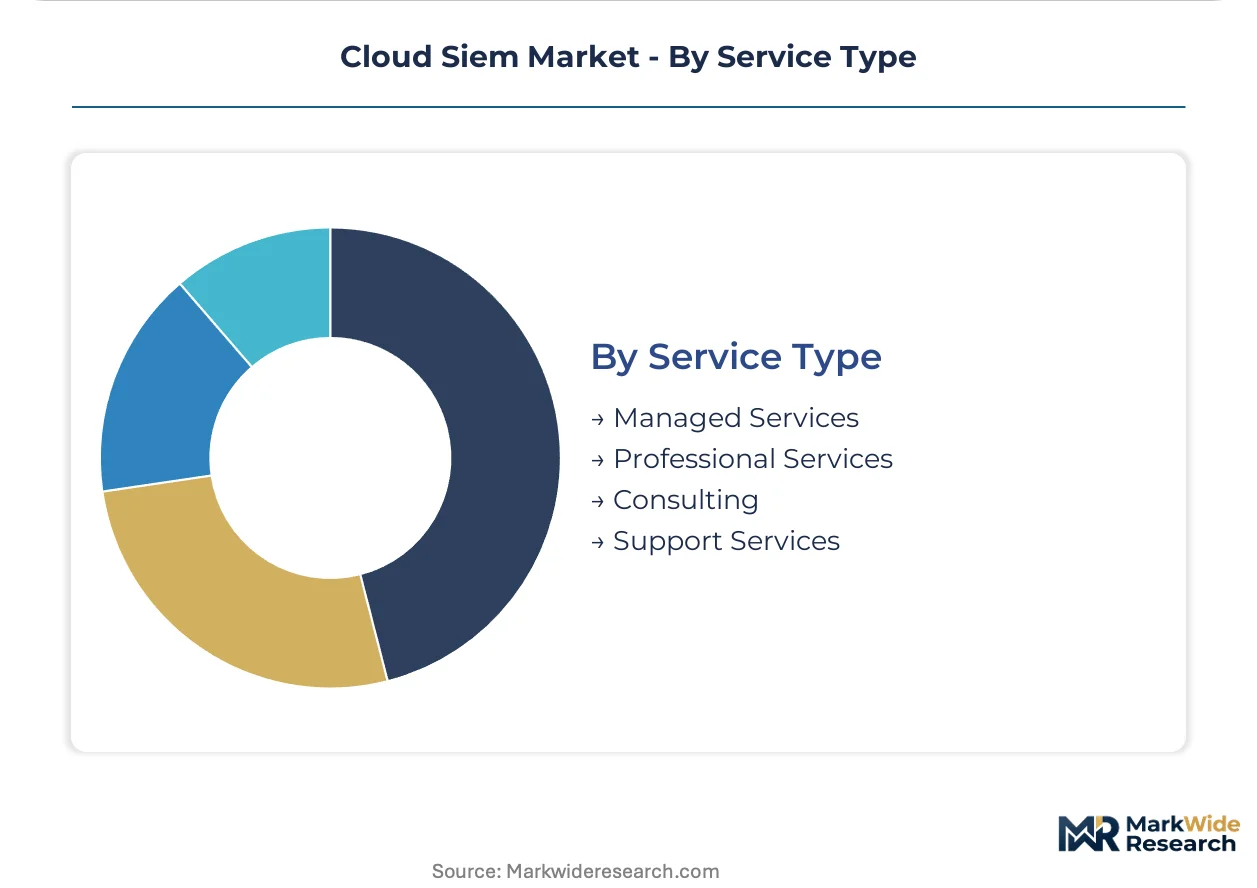
- Managed Services:Fully outsourced SOC operations with 24/7 analyst coverage and guaranteed response SLAs. Transfers infrastructure risk to vendors while compressing customer switching costs through annual commit contracts with burst capacity provisions.
- Professional Services:Custom detection engineering, rule development, and platform migration consulting. High-margin engagements for complex multi-cloud deployments with legacy mainframe SIEM integration challenges.
- Consulting:Security architecture assessment and compliance readiness evaluation. Pre-certified managed security service providers leverage BSI certification to compress six-month procurement cycles to eight weeks for German manufacturers.
- Support Services:Technical assistance, patch management, and feature enablement. Lower-margin foundation tier with renewal-dependent revenue streams.
Managed Services dominates recurring revenue. Professional Services delivers the highest margin expansion as migration complexity intensifies.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Financial services conglomerates and automotive suppliers anchor procurement concentration across industrialized economies. Sovereign data residency mandates and explainable AI requirements compress vendor selection timelines in regulated sectors.
United States
Healthcare systems under HIPAA and financial institutions facing SEC cybersecurity disclosure rules drive hybrid cloud adoption. The SEC mandates immutable audit trails for forensic retention, pushing hospital networks toward consumption-based SIEM contracts. Boston-area biotech clusters consolidate fragmented SOC tools into unified stacks.
Germany
Industrial conglomerates and Mittelstand manufacturers satisfy BSI IT-Grundschutz certification through sovereign cloud deployments. The EU AI Act explainability requirements accelerate replacement of opaque on-premises rule engines in Frankfurt banking centers. Stuttgart automotive suppliers migrate terabyte-scale telemetry to managed cloud-native architectures.
United Kingdom
London financial services firms navigate GDPR cross-border data governance alongside emerging FCA operational resilience mandates. NHS trusts face HIPAA-equivalent data protection obligations without dedicated cloud SOC capacity. The Thames Valley tech corridor experiments with federated learning for privacy-preserving threat intelligence.
Japan
Tokyo-based electronics manufacturers and METI-designated critical infrastructure operators demand quantum-resistant encryption preparation. Financial institutions await NIST post-quantum cryptography standard finalization before committing to long-term retention architectures. Osaka industrial IoT deployments leverage Kubernetes-native log shippers for collapsed data pipeline costs.
India
Bengaluru IT services exporters and Mumbai financial institutions build cloud-native SOCs to serve multinational compliance requirements. RBI cybersecurity guidelines and SEBI disclosure mandates accelerate managed security service provider adoption. Hyderabad pharmaceutical clusters under CDSCO oversight invest in automated audit trail generation.
Cloud Siem Market Vendor Landscape
Channel-controlling players compete with product-specialist players across a tiered vendor landscape. Hyperscaler-backed platforms leverage infrastructure integration for enterprise anchoring, while standalone analytics vendors differentiate through behavioral graph capabilities. Two strategic archetypes dominate: cloud-native SIEM specialists with consumption-based delivery models, and extended detection and response platforms collapsing adjacent security toolchains. Competitive moves concentrate on strategic partnerships for sovereign data residency architectures and portfolio diversification into managed SOC operations.
Within the hyperscaler-anchored tier, Microsoft Sentinel and Google Security Operations occupy positions defined by native cloud infrastructure control. Splunk Enterprise Security exemplifies the data lake integration archetype for complex analytics workloads. Securonix sits within the behavioral analytics specialization vector, representing user and entity behavior analytics capabilities within cloud-native architectures.
| Leading Market Players |
|---|
| Microsoft Sentinel |
| Splunk Enterprise Security |
| Exabeam Fusion |
| Securonix |
| Google Security Operations |
| Panther |
| SentinelOne Singularity |
| Elastic Security |
| ConnectWise SIEM |
| Others |
Supply Flow & Price Mechanics
Hyperscaler compute infrastructure concentration in US West Coast and Irish regions funnels margin pools toward managed security service providers with sovereign data residency architectures. Cloud egress bandwidth charges and quantum-resistant encryption preparation costs are compressing vendor pricing power while elevating procurement negotiation leverage for German automotive conglomerates and Frankfurt financial institutions.
Pricing Analysis
Certification level under BSI IT-Grundschutz and FedRAMP authorization creates the primary spread between premium sovereign-cloud tiers and standard public-cloud offerings. Consumption-based SaaS subscriptions with annual commit contracts and burst capacity provisions dominate procurement structures. Price differentiation hinges on data residency compliance grade and managed SOC analyst coverage SLAs. Pricing pressure stems from Kubernetes-native log shippers collapsing data pipeline costs for industrial IoT deployments. Mid-market manufacturers in Bavaria exhibit highest price sensitivity; Frankfurt banking security operations centers show lowest sensitivity due to EU AI Act explainability mandates.
Supply Chain Analysis
US export controls on advanced AI training hardware and quantum computing components restrict flows to Chinese and Russian entity lists, fragmenting global SIEM infrastructure deployment patterns. Compute substrate supply concentrates in United States, Ireland, and Singapore regions. Raw material dependencies span specialized GPUs, high-bandwidth memory modules, and cryptographically secure enclave processors. Supply chain risk centers on single-source vulnerability for NIST post-quantum cryptography standard-compliant hardware security modules. Distribution runs through hyperscaler marketplaces and certified managed security service provider channels with BSI pre-certification.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud SIEM procurement is fundamentally a service-attach opportunity where managed SOC operations and detection engineering subscriptions expand faster than raw platform licensing. Recurring revenue from 24/7 analyst coverage and automated response orchestration now exceeds perpetual license values in three-year TCO models.
For Market Incumbents: Build switching-cost moats through detection-engineering talent retention and proprietary behavioral graph analytics IP. Consolidate fragmented SOC toolchains into unified XDR backends to neutralize point-product vendor erosion. Defensive moves require backward integration into sovereign data residency node deployment and KRITIS framework pre-certification investment. Threat substitution from Kubernetes-native open-source alternatives demands continuous R&D in eBPF-based kernel instrumentation. For New Entrants and Emerging Players: German university hospitals in Berlin and Heidelberg represent the most penetrable entry point given HIPAA-equivalent BDSG compliance obligations without dedicated cloud SOC capacity. Healthcare provider underpenetration across European research networks offers white-space expansion before incumbent managed service provider consolidation. Go-to-market positioning should emphasize federated learning architectures for privacy-preserving threat intelligence without raw log centralization. For Investors and Strategic Acquirers: Secondary-cycle assets sit with PE-backed managed security service providers holding BSI certification and Mittelstand manufacturing client bases. Long-term viability across a five-to-ten-year window favors vendors with partitioned sovereign-residency architectures separating ingestion nodes from processing clusters. Acquisition target archetype: cloud-native SIEM specialists with consumption-based delivery models and automotive supplier referenceability. Signal to watch: NIST post-quantum cryptography standard finalization unlocking long-term data retention architecture decisions.| Strategic Initiative | Industry Significance |
|---|---|
| Sovereign Cloud Partnership | Enables BSI IT-Grundschutz compliance for Stuttgart automotive suppliers migrating terabyte-scale telemetry. |
| Detection Engineering Talent Acquisition | Addresses SOC analyst skill compression from Tier-1 alert triage automation eliminating entry-level positions. |
| Federated Learning Platform Development | Supports privacy-preserving machine learning across siloed tenant data pools without raw log centralization. |
| Quantum-Resistant Encryption Preparation | Positions vendors for NIST standard finalization and long-term healthcare data retention mandates. |
| Managed SOC Service Expansion | Captures recurring revenue from Bavarian Mittelstand companies trading capital expenditure for operational costs. |
Methodological Framework
Initial hypotheses were tested against primary input from CISOs at German automotive suppliers, detection engineering leads at Frankfurt financial institutions, managed security service provider operations directors, and BSI certification auditors, then refined through secondary validation. Primary fieldwork combined structured interviews with SOC analysts and procurement officers at industrial conglomerates in Baden-Württemberg. Secondary sources encompassed SEC cybersecurity disclosure filings, EU AI Act regulatory texts, BSI IT-Grundschutz certification databases, and hyperscaler infrastructure capex disclosures. Bottom-up telemetry volume modeling and top-down market sizing triangulated demand estimates.
Demand-supply balance dynamics across the analysis window shaped the quantitative framework. Segmentation dimensions modeled include deployment topology, organizational scale, application use case, and service consumption model alongside regional regulatory cluster differentiation. CAGRs derived from installed base growth rates and annual contract value expansion trajectories. Forecast inputs incorporated Kubernetes adoption curves for industrial IoT deployments and EU AI Act implementation timelines for explainable alerting mandates.
Practitioners should monitor quantum-resistant encryption standard finalization, cloud egress cost volatility, and hyperscaler concentration risk for early signals of forecast revision. Forecasts reflect assumptions about sovereign data residency mandate enforcement intensity and managed security service provider certification acceleration. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Data Exfiltration Techniques Market
Cybersecurity
India Cybersecurity Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Deception Technology Market
Cybersecurity
Endpoint Security Market
Cybersecurity
Server Security Market
Cybersecurity
Threat Intelligence Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Nigeria Cybersecurity Market
Cybersecurity
Web Filtering Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market