
 Asia-Pacific Software Defined Perimeter Market | 2026-2036
Asia-Pacific Software Defined Perimeter Market Size, Share, and Industry Trends Forecast 2026-2036
Asia-Pacific Software Defined Perimeter Market Analytics
Enterprise-grade zero-trust certification is rotating through vendor procurement checklists across the Asia-Pacific Software Defined Perimeter landscape. Cisco Systems leverages its integrated security stack to anchor large enterprise deployments in Japan and Australia. Palo Alto Networks competes through cloud-native SDP specialization, while Zscaler sustains dominance in distributed workforce connectivity across Southeast Asian markets.
Asia-Pacific Software Defined Perimeter refers to a security architecture that dynamically creates individualized perimeters around network resources through policy-based access control, typically enforcing microsegmentation with session-specific authentication parameters rather than static perimeter defenses. The framework's primary commercial purpose is to eliminate implicit trust within enterprise networks while enabling secure remote access to cloud and on-premises workloads. Cloud-based deployment models now capture the largest addressable base as organizations retire legacy VPN infrastructure, though hybrid configurations retain the strongest margin pools where compliance mandates require localized data sovereignty. Zero-trust technology foundations lead structural growth, with identity management representing the fastest-expanding capability layer as biometric and behavioral authentication standards harden.
Australia's Cyber Security Centre, Japan's METI, and India's CERT-In collectively shape product certification requirements and procurement eligibility across the region. Australia's Essential Eight maturity model directly mandates network segmentation capabilities that SDP platforms must demonstrate, while India's BIS cybersecurity standards for critical infrastructure operators are tightening vendor qualification protocols. Stakeholders must monitor how divergent national encryption and data-localization rules will fragment platform architectures and inflate compliance engineering costs.
Market Dynamics
Zero-trust architecture mandates from Australia's Cyber Security Centre and Japan's METI are forcing enterprise infrastructure refresh cycles across Asia-Pacific, compressing procurement timelines while elevating vendor certification requirements.
Growth Catalysts
- India's PLI scheme for IT hardware:Domestic manufacturing incentives are reducing equipment costs for SDP deployments while accelerating local compliance certification pathways.
- Biometric identity integration:Behavioral authentication standards are hardening access controls, expanding addressable use cases beyond traditional VPN replacement.
- Australia's Essential Eight maturity model:Federal network segmentation mandates are creating procurement eligibility filters that SDP platforms must satisfy.
Market Restraints
- Data localization engineering costs:Divergent national encryption rules in India, Japan, and Australia are fragmenting platform architectures and inflating R&D overhead.
- Specialized cybersecurity talent scarcity:Zero-trust implementation expertise concentrates in Singapore and Sydney, creating deployment bottlenecks across Southeast Asian markets.
- Legacy VPN sunk-cost inertia:Enterprises with recent infrastructure investments delay full SDP migration despite security gaps.
Strategic Opportunities
- Indonesia's underpenetrated financial sector:Islamic banking digitization and fintech licensing waves are creating first-mover SDP deployment windows.
- 5G network slicing convergence:Telco edge computing partnerships enable SDP microsegmentation at the radio access layer for industrial IoT.
- Vietnam's cybersecurity decree:Critical infrastructure operator mandates are opening compliance-driven procurement channels previously blocked by informal vendor relationships.
Industry Challenges
- Multi-cloud orchestration complexity:Enterprises struggle to maintain consistent policy enforcement across AWS, Azure, and domestic Chinese cloud environments simultaneously.
- Cross-border certification reciprocity gaps:Australia's ACSC, Japan's METI, and India's BIS maintain non-harmonized testing protocols, forcing redundant vendor qualification cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Asia-Pacific Software Defined Perimeter Market |
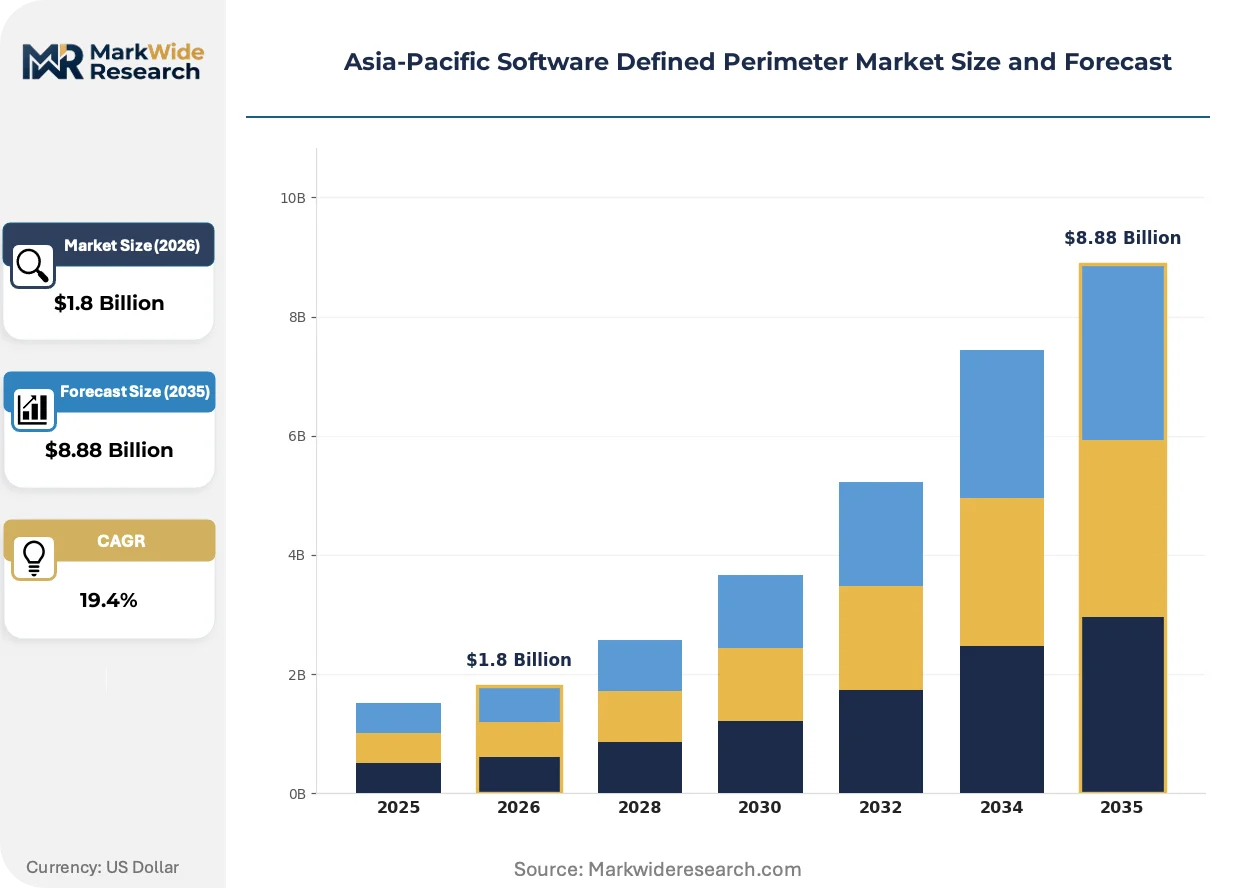
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $8.88 Billion |
| CAGR (2026 – 2036) | 19.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Services End User: SMEs, Large Enterprises, Government, Education Technology: Zero Trust, Multi-Factor Authentication, Identity Management, Network Segmentation Application: Data Protection, Remote Access, Network Security, Compliance Management |
| Companies Covered | Cisco Systems, Inc., Palo Alto Networks, Inc., Check Point Software Technologies Ltd., Fortinet, Inc., Akamai Technologies, Inc., Zscaler, Inc., Broadcom Inc., Juniper Networks, Inc., Intel Corporation, Others |
| Regions Covered | Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Asia-Pacific Software Defined Perimeter Market Evolving Landscape
SDP architecture is converging with identity fabric and edge compute layers, collapsing the traditional perimeter into dynamic policy enforcement points distributed across hybrid infrastructure.
Microsegmentation policy engines are miniaturizing from centralized controllers to lightweight agents embedded directly in Kubernetes sidecars and container runtimes. DevSecOps teams in Australian financial services and Japanese automotive manufacturing are deploying these agents at CI/CD pipeline velocity. This compression is miniaturizing the traditional network security operations center into automated policy-as-code workflows that self-heal without human intervention.
Japan's METI cybersecurity framework revisions now mandate continuous verification architectures for critical infrastructure operators, directly elevating SDP from optional to required procurement category. Industrial control system vendors in the region are accelerating product recertification to satisfy these requirements. Power utilities and transportation operators represent the most affected segments, with procurement committees rewriting technical specifications to exclude static perimeter solutions.
Enterprise buyers are unbundling security software from managed service contracts, demanding standalone SDP licensing with internal operational control. Systems integrators in Singapore and Hong Kong are losing exclusive deployment relationships as direct vendor-to-enterprise sales channels strengthen. This disintermediation is most visible in Australia's federal government sector, where agencies now procure cloud-native security platforms through centralized whole-of-government panels rather than state-level intermediaries.
Asia-Pacific Software Defined Perimeter Market Segmentation
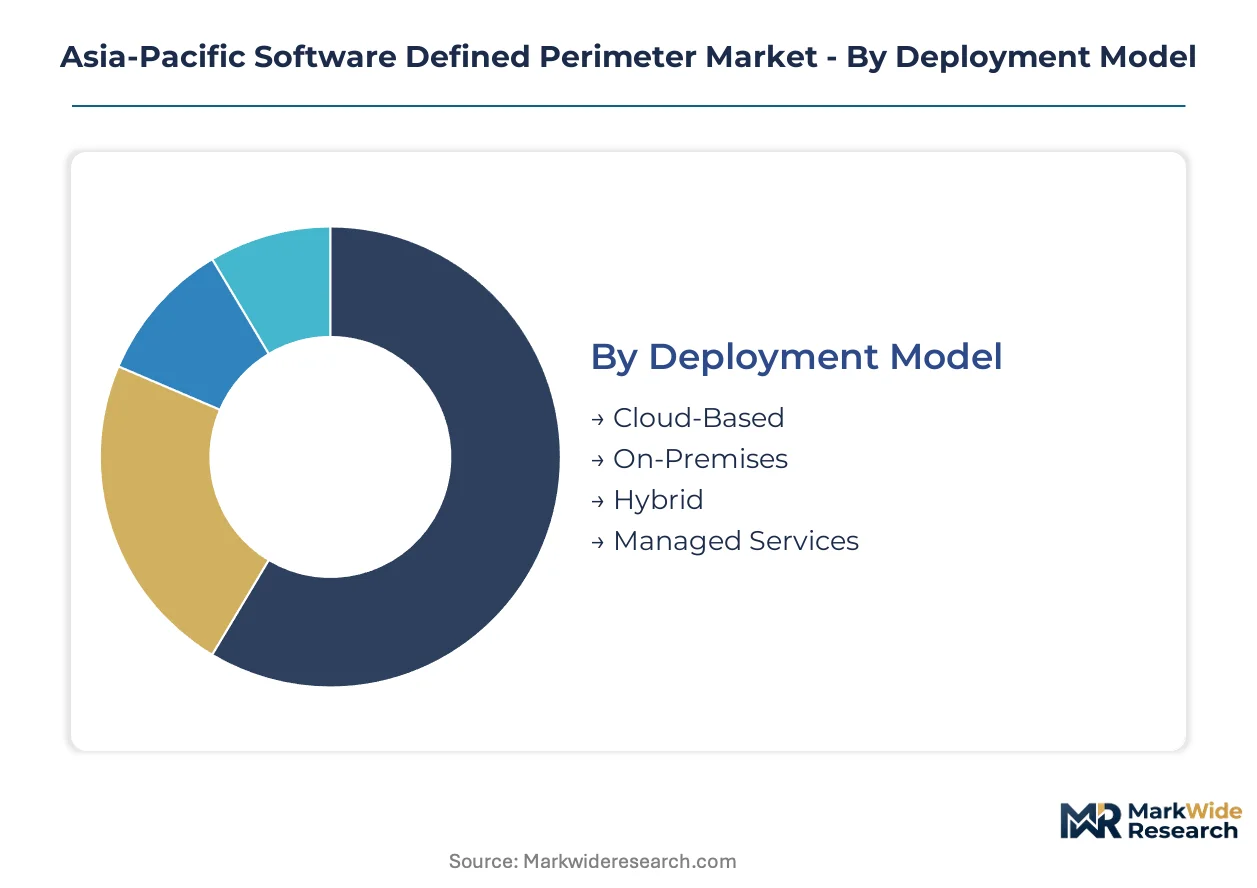
Deployment configurations across Asia-Pacific SDP markets fragment sharply along national data sovereignty requirements. Australia's ACSC mandates, Japan's METI frameworks, and India's BIS standards each impose distinct architectural constraints that vendors must engineer around.
Deployment Model:
Regulatory differentiation across Australia's data localization rules, Japan's critical infrastructure protections, and India's PLI manufacturing incentives shapes procurement eligibility by deployment architecture.
- Cloud-Based:Scalable infrastructure eliminates capital expenditure for Australian fintechs and Singaporean logistics operators retiring legacy VPN gateways. Demand concentrates in Southeast Asian markets where distributed workforces require elastic capacity without sovereign data requirements.
- Hybrid:Split-stack architectures satisfy Japanese METI continuous verification mandates while preserving on-premises control over encryption key management. Power utilities and transportation operators in Tokyo and Osaka prefectures prioritize this configuration for operational technology segmentation.
- On-Premises:Air-gapped deployments serve Indian defense contractors and Australian signals intelligence facilities under strict data residency protocols.
- Managed Services:Outsourced SOC operations appeal to Vietnamese critical infrastructure operators lacking zero-trust implementation expertise domestically.
Established volume favors Cloud-Based; emerging adoption favors Hybrid.
End User:
Customer procurement sophistication determines solution complexity and margin capture across the regional SDP landscape.
- Large Enterprises:Integrated security stacks with identity fabric convergence anchor deployments at Japanese automotive manufacturers and Australian banking consortiums. Procurement committees demand API-native orchestration across AWS, Azure, and domestic cloud environments simultaneously.
- Government:Federal agencies in Canberra and Tokyo mandate zero-trust architectures for critical infrastructure protection, rewriting technical specifications to exclude static perimeter solutions entirely.
- SMEs:Standalone SDP licensing displaces managed service contracts as direct vendor channels strengthen across Hong Kong and Singapore.
- Education:University research networks in Melbourne and Seoul deploy lightweight microsegmentation for multi-tenant laboratory access.
Procurement concentration sits with Large Enterprises; compliance tailwinds accelerate Government fastest.
Technology:
Capability layer maturity determines competitive differentiation and pricing power in vendor positioning.
- Identity Management:Biometric and behavioral authentication standards harden access controls beyond traditional credential verification. Australian financial services deploy these capabilities at CI/CD pipeline velocity through Kubernetes sidecar embeddings.
- Zero Trust:Continuous verification architectures satisfy Japan's METI cybersecurity framework revisions, elevating SDP from optional to required procurement category for critical infrastructure operators.
- Multi-Factor Authentication:Hardware token integration persists in Indian government and defense sectors under BIS procurement protocols.
- Network Segmentation:Microsegmentation policy engines miniaturize to container runtime embeddings for DevSecOps workflows in Sydney and Tokyo.
Technology leadership clusters in Identity Management; regulatory coercion drives Zero Trust expansion.
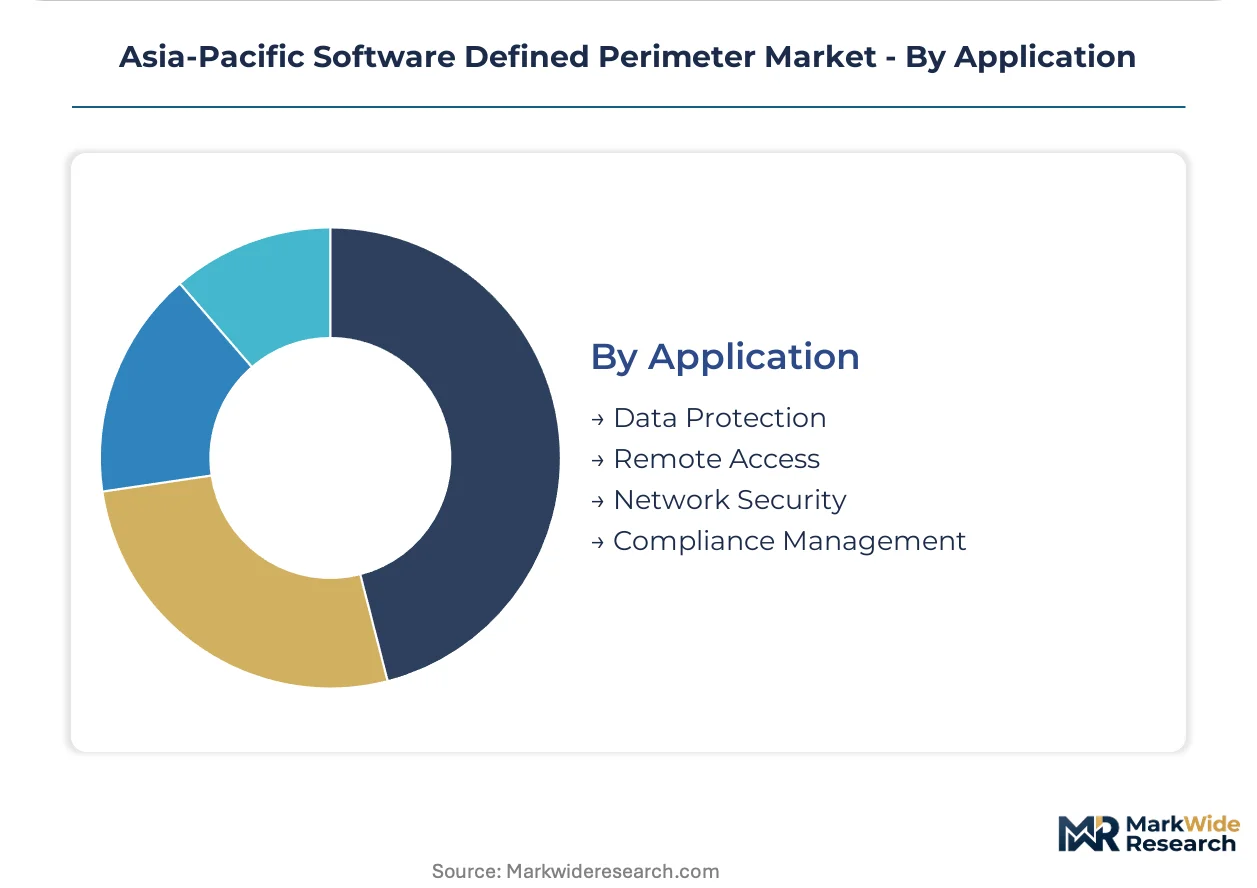
Application:
Use case specificity shapes integration requirements and operational workflow redesign scope.
- Remote Access:VPN replacement dominates initial SDP procurement across Indonesia's underpenetrated Islamic banking sector and Vietnam's fintech licensing waves. Jakarta and Ho Chi Minh City represent first-mover deployment windows.
- Compliance Management:Automated policy-as-code workflows self-heal against Australia's Essential Eight maturity model and India's CERT-In critical infrastructure standards without human SOC intervention.
- Data Protection:Encryption-in-transit requirements fragment across divergent national standards, inflating engineering overhead for cross-border platform architectures.
- Network Security:Industrial control system vendors accelerate recertification to satisfy Japan's METI continuous verification mandates for power utilities.
Volume anchors in Remote Access; compliance complexity elevates Compliance Management fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Vendor engineering teams concentrate in Sydney, Tokyo, and Singapore to address divergent national certification requirements across the Asia-Pacific Software Defined Perimeter landscape. Platform architectures fragment as Australia's ACSC, Japan's METI, and India's BIS each impose distinct data sovereignty and encryption standards.
Australia
Federal agencies and critical infrastructure operators drive procurement volume through Canberra's centralized whole-of-government panels. The Australian Cyber Security Centre's Essential Eight maturity model mandates network segmentation capabilities that disqualify static perimeter solutions. Sydney anchors the region's largest concentration of zero-trust implementation expertise, with financial services and defense contractors clustering in the harbor city.
Japan
Automotive manufacturers and power utilities in Tokyo and Osaka prefectures prioritize hybrid deployment configurations for operational technology segmentation. METI's cybersecurity framework revisions mandate continuous verification architectures, elevating SDP from optional to required procurement category for critical infrastructure operators. Industrial control system vendors accelerate product recertification to satisfy these requirements.
India
Domestic manufacturing incentives under the PLI scheme for IT hardware reduce equipment costs while accelerating local compliance certification pathways. BIS cybersecurity standards for critical infrastructure operators tighten vendor qualification protocols, particularly for defense contractors requiring air-gapped deployments. Bengaluru and Hyderabad host the region's fastest-growing cybersecurity talent pools outside Singapore.
Singapore
Systems integrators face disintermediation as direct vendor-to-enterprise sales channels strengthen, eroding exclusive deployment relationships. The city-state concentrates zero-trust implementation expertise that creates deployment bottlenecks across Southeast Asian markets lacking comparable talent depth. Financial services and logistics operators leverage Singapore's position as regional headquarters for cloud-native security procurement.
Vietnam
Critical infrastructure operator mandates under the country's cybersecurity decree open compliance-driven procurement channels previously blocked by informal vendor relationships. Fintech licensing waves in Ho Chi Minh City create first-mover SDP deployment windows as Islamic banking digitization accelerates across the broader Southeast Asian region. State-owned enterprises lack domestic zero-trust expertise, creating dependency on Singapore-based implementation partners.
Asia-Pacific Software Defined Perimeter Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes across the Asia-Pacific Software Defined Perimeter market. Integrated security stack vendors anchor large enterprise deployments, while cloud-native specialists capture distributed workforce connectivity segments. The competitive structure organizes around three archetypes: full-stack incumbents with certification breadth, cloud-native challengers with API-native orchestration, and regional systems integrators losing ground to direct vendor channels. Dominant competitive moves include strategic partnerships with domestic cloud providers and portfolio diversification into identity fabric convergence.
Among integrated security stack vendors, Cisco Systems, Inc. exemplifies the full-stack incumbent archetype with certification breadth across Australian and Japanese federal procurement channels. Palo Alto Networks, Inc. occupies a position within the cloud-native challenger tier, while Zscaler, Inc. anchors the distributed workforce specialization vector across Southeast Asian markets. These three companies represent distinct competitive positioning strategies rather than overlapping market contests, with each archetype serving different buyer sophistication levels and deployment complexity requirements.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Palo Alto Networks, Inc. |
| Check Point Software Technologies Ltd. |
| Fortinet, Inc. |
| Akamai Technologies, Inc. |
| Zscaler, Inc. |
| Broadcom Inc. |
| Juniper Networks, Inc. |
| Intel Corporation |
| Others |
Value Network & Pricing Analysis
Capacity reservation contracts with Australian federal agencies lock in multi-year supply access while anchoring price visibility for SDP vendors serving Canberra's whole-of-government panels. These arrangements compress procurement cycles for compliant vendors while exposing non-certified competitors to spot-market volatility.
Pricing Analysis
Australia's Essential Eight maturity model dictates the pricing tier structure across Asia-Pacific SDP procurement. Three-tier pricing structure across premium, standard, and economy levels separates ACSC-certified platforms from METI-compliant configurations and uncertified alternatives. Cost compression in the economy tier is intensifying because India's PLI scheme for IT hardware accelerates domestic manufacturing cost advantages. Large enterprises exhibit the lowest price sensitivity due to compliance-driven mandates, while Vietnamese state-owned enterprises demand economy-tier solutions lacking implementation expertise.
Supply Chain Analysis
Extended lead times for zero-trust hardware appliances concentrate inventory pressure on Singapore-based distribution hubs serving Southeast Asian markets. Component sourcing draws from Taiwan for semiconductor-grade encryption modules, South Korea for behavioral authentication sensors, and Japan for industrial-grade edge compute units. Single-source vulnerability in Australian-sourced cryptographic certification creates procurement bottlenecks for vendors seeking ACSC accreditation. Distribution runs through direct vendor-to-enterprise channels that disintermediate traditional systems integrators in Hong Kong and Singapore.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed security services represent the fastest-expanding recurring-revenue layer in Asia-Pacific SDP markets, outpacing hardware licensing growth as Vietnamese and Indonesian operators outsource SOC operations lacking domestic zero-trust expertise.
For Market Incumbents: Compound certification breadth across Australia's ACSC, Japan's METI, and India's BIS frameworks to defend procurement eligibility in federal channels. Deepen upstream control over cryptographic module manufacturing to reduce exposure to Taiwan semiconductor supply constraints. Channel consolidation threatens margin capture as direct sales displace Singapore-based systems integrators. For New Entrants and Emerging Players: Differentiate on cloud-native API orchestration targeting Indonesia's underpenetrated Islamic banking sector where legacy VPN replacement creates first-mover deployment windows. Vietnam's cybersecurity decree opens compliance-driven procurement channels for vendors offering managed service bundles. Prioritize partnerships with domestic cloud providers in Ho Chi Minh City to bypass informal vendor relationship barriers. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among hybrid-deployment specialists serving Japanese power utilities and Australian defense contractors under multi-year operational technology segmentation contracts. Acquisition targets should demonstrate ACSC or METI certification pipelines with demonstrated federal procurement traction. Watch for BIS cybersecurity standard revisions as inflection indicators for Indian critical infrastructure vendor qualification windows.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | API-native orchestration across AWS, Azure, and domestic cloud environments satisfies Australian banking consortium procurement committees. |
| Strategic Partnership | Telco edge computing alliances enable SDP microsegmentation at the 5G radio access layer for Japanese industrial IoT deployments. |
| Geographic Expansion | Local engineering presence in Bengaluru accelerates BIS certification pathways for Indian defense contractor air-gapped deployments. |
| Acquisition of Specialist Firm | Identity fabric convergence capabilities harden biometric authentication standards for Australian financial services CI/CD pipelines. |
| Product Launch | Kubernetes sidecar embeddings miniaturize policy engines for DevSecOps velocity at Tokyo automotive manufacturers. |
Research Methodology
The analysis maps cloud-based, hybrid, on-premises, and managed service deployment configurations, each validated through CTOs at Australian federal agencies, IT procurement officers at Japanese automotive manufacturers, platform engineers at Singaporean financial services firms, and integration specialists across Southeast Asian markets. Primary interview data triangulates against SEC filings from listed security vendors, hyperscaler capex disclosures, Australian Cyber Security Centre procurement databases, and METI framework documentation. Bottom-up deployment volume estimates reconcile with top-down addressable market sizing across the analysis window.
Consistency checks against external benchmarks validate modeled outputs across the projection horizon. Segmentation dimensions include deployment architecture, organization size tier, vertical industry, technology capability layer, and national regulatory cluster. CAGRs derive from fitted growth curves applied to validated baseline estimates. Forecast inputs incorporate India's PLI scheme implementation velocity and Japan's METI continuous verification mandate compliance timelines.
Material uncertainties — regulatory harmonization failures, encryption standard fragmentation, and cybersecurity talent concentration bottlenecks — sit outside the modeled envelope. Forecasts reflect documented assumptions about certification reciprocity development and sovereign data rule stability. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Application Security Market
Cybersecurity
Threat Hunting Market
Cybersecurity
SOC As a Service Market
Cybersecurity
Cognitive Security Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
Austria Cybersecurity Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Netherlands Cybersecurity Market
Cybersecurity
Data Center Security Market
Cybersecurity
Enterprise Network Firewall Market