
 Data-Centric Security Market | 2026-2036
Data-Centric Security Market Size, Share, and Industry Trends Forecast 2026-2036
Data-Centric Security Market Intelligence
The capability gap between cloud-native platforms and legacy on-premises stacks is reorganizing competitive dynamics across the data-centric security landscape. IBM leverages its hybrid cloud infrastructure to anchor enterprise deployments across regulated industries. Varonis Systems specializes in metadata-driven analytics for unstructured data access governance, occupying a distinct niche in insider threat detection.
Data-centric security encompasses cryptographic and access-control methodologies that protect information assets at the data element level rather than perimeter boundaries, employing techniques such as AES-256 encryption, format-preserving tokenization, and dynamic data masking with real-time policy enforcement. Its primary purpose is to ensure persistent protection of sensitive records as they traverse heterogeneous cloud, on-premises, and edge environments. Encryption products dominate current spending as organizations retrofit legacy databases, while cloud-based deployment models represent the fastest-expanding segment driven by multi-tenant SaaS architectures. Machine Learning technology integration is deepening across tokenization and access control layers, concentrating margin pools in automated policy orchestration.
The Federal Trade Commission enforces data breach notification and unfair practice standards that directly shape vendor product roadmaps in the United States, while the European Data Protection Board coordinates GDPR enforcement that mandates privacy-by-design architectures for cross-border data flows. The Securities and Exchange Commission's cybersecurity disclosure rules are compelling publicly traded firms to document data protection controls in regulatory filings. Stakeholders must evaluate whether their current architectures can satisfy converging requirements from financial regulators and data protection authorities without fragmenting into incompatible regional deployments.
Market Dynamics
The convergence of multi-cloud data sprawl and algorithmic enforcement of privacy mandates is compressing deployment timelines for element-level protection architectures. Organizations now face simultaneous pressure from SEC disclosure rules and EU AI Act data governance requirements, forcing architectural decisions that privilege persistent encryption over perimeter hardening.
Growth Catalysts
- GDPR Article 25 mandates:Privacy-by-design requirements in cross-border data flows compel enterprises to embed cryptographic controls at the data element level rather than network boundaries.
- Financial services:Banking and insurance sectors deploy tokenization for PCI-DSS compliance and real-time transaction processing across hybrid infrastructure.
- Machine learning integration:Automated policy orchestration using behavioral analytics reduces manual classification overhead in unstructured data repositories.
Market Restraints
- Specialized talent scarcity:Shortage of cryptographers and data governance architects extends implementation timelines for enterprise deployments.
- Legacy system friction:Retrofitting AES-256 encryption into decades-old database schemas requires expensive middleware development.
- Key management complexity:Distributed key escrow across cloud regions introduces operational risk and compliance audit burden.
Strategic Opportunities
- Edge computing expansion:Manufacturing and healthcare IoT deployments create demand for lightweight format-preserving encryption at sensor nodes.
- Quantum-resistant algorithms:NIST post-quantum cryptographic standards open product roadmaps for long-term data protection against harvest-now-decrypt-later threats.
- API-first architectures:SaaS vendors embed data-centric security through native SDKs, reducing customer implementation friction.
Industry Challenges
- Cross-border data localization:Conflicting sovereignty requirements fragment key management architectures and complicate unified policy enforcement.
- False positive fatigue:Overly sensitive access control policies generate alert volume that overwhelms security operations centers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data-Centric Security Market |
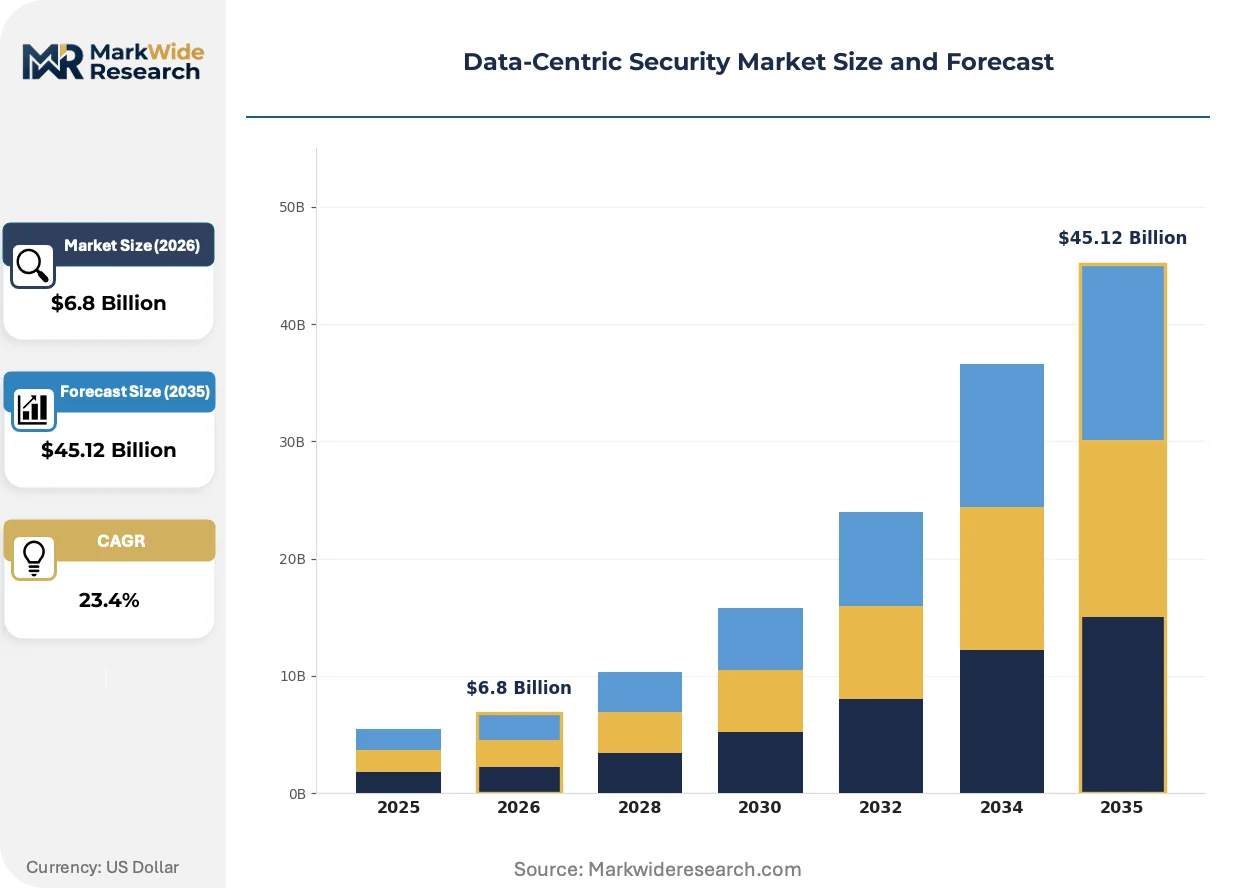
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $45.12 Billion |
| CAGR (2026 – 2036) | 23.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Encryption, Tokenization, Data Masking, Access Control Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Financial Services, Healthcare, Retail, Government Technology: Machine Learning, Blockchain, AI, Big Data Analytics |
| Companies Covered | Informatica, IBM, Broadcom, Micro Focus, Forcepoint, NetApp, Varonis Systems, Orange Cyberdefense, Imperva, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data-Centric Security Market Strategic Shifts & Innovations
Homomorphic encryption and confidential computing are advancing from research prototypes to production workloads, altering how organizations approach sensitive data analytics. These capabilities enable computation on encrypted data without decryption, collapsing traditional trade-offs between utility and protection.
Confidential computing using hardware-based trusted execution environments is miniaturizing the attack surface for cloud-based analytics. Healthcare and financial services firms pilot these enclaves for multi-party computation on sensitive records. The technology is compressing compliance costs by eliminating data movement for processing.
The EU AI Act's risk-based classification system mandates automated logging and auditability for high-risk AI systems processing personal data. Vendors must demonstrate technical documentation of data lineage and protection controls. Healthcare AI developers in Germany and France face the steepest compliance ramps.
Enterprise buyers now demand consumption-based pricing for data protection services rather than perpetual licenses. Security vendors respond with metered tokenization and encryption APIs. This shift is most pronounced among fintech startups in Singapore and digital health firms in Israel seeking operational flexibility.
Data-Centric Security Market Segmentation
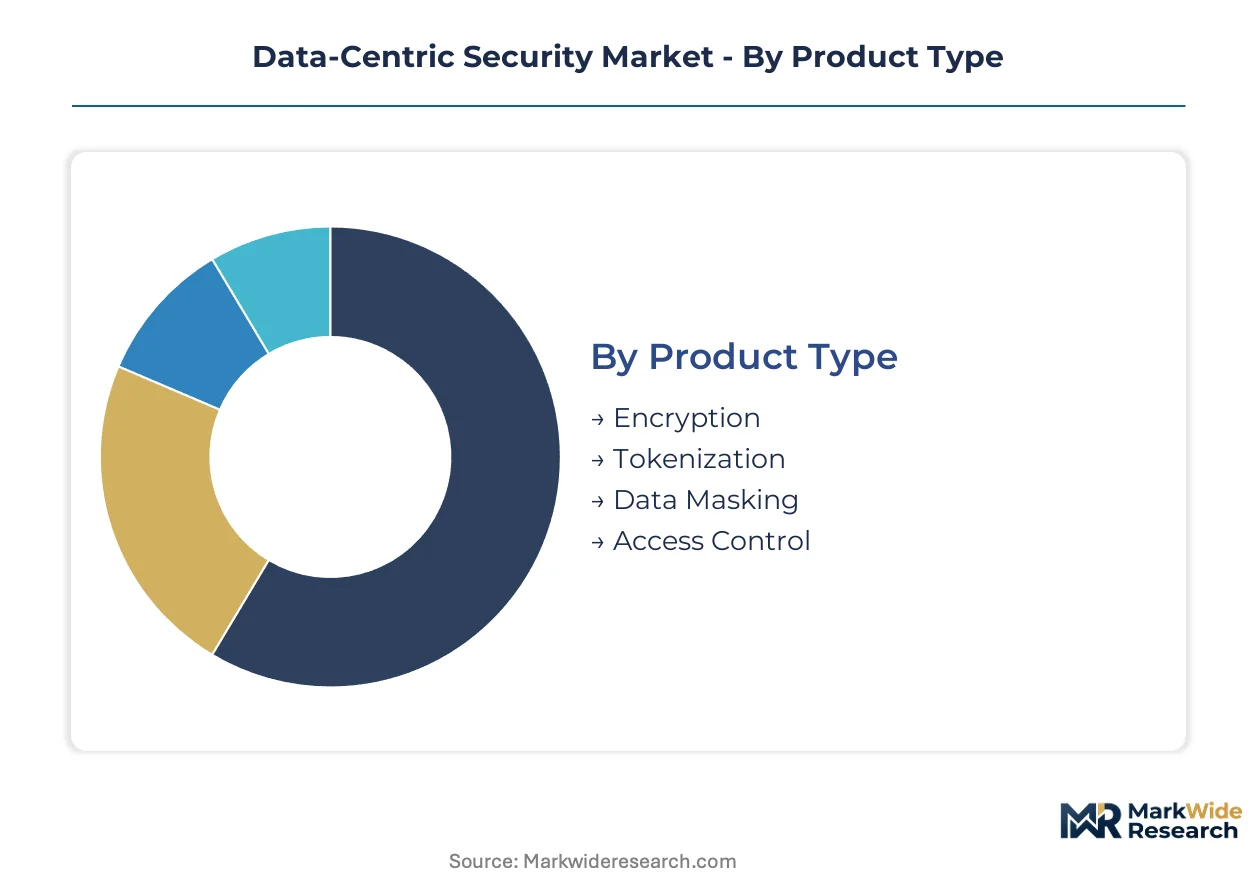
Data-centric security architectures fragment across four critical dimensions that determine both procurement patterns and architectural complexity. Vendors must align product roadmaps with deployment preferences, regulatory exposure, and technology maturity curves that vary sharply across buyer segments.
Product Type:
Substitution pressure concentrates most intensely in data masking, where static approaches face displacement by dynamic, policy-driven alternatives that preserve analytical utility.
- Encryption:AES-256 and format-preserving algorithms protect data elements at rest and in transit across heterogeneous infrastructure. Banking networks in the United States and Germany deploy persistent encryption for PCI-DSS compliance, though key management complexity extends implementation timelines.
- Tokenization:Format-preserving substitution replaces sensitive values with non-sensitive equivalents that retain referential integrity for transaction processing. Retail payment processors and insurance claims systems favor this approach for its minimal application refactoring requirements.
- Data Masking:Static and dynamic obfuscation techniques shield non-production environments from exposure. Manufacturing firms apply masking for ERP testing while healthcare providers use it for clinical analytics sandboxes.
- Access Control:Attribute-based and policy-driven authorization governs data element visibility at query time. Metadata-driven implementations from specialized vendors address insider threat detection in unstructured repositories.
Encryption retains volume leadership; tokenization holds the steepest expansion curve.
Deployment Model:
Cost tier differentiation separates enterprise buyers seeking capital expenditure predictability from mid-market adopters prioritizing operational flexibility.
- On-Premises:Hardware security modules and dedicated key management infrastructure serve defense contractors and national healthcare systems with stringent data sovereignty mandates. German automotive suppliers and French aerospace firms maintain these deployments for intellectual property protection.
- Cloud-Based:Multi-tenant SaaS architectures with consumption-based metering reduce upfront investment for fintech startups and digital health ventures. Singaporean payment platforms and Israeli medical device companies favor this model for rapid scaling.
- Hybrid:Split workloads between cloud analytics and on-premises transactional systems address regulatory fragmentation. Japanese banking consortia deploy hybrid models to satisfy FSA guidance while leveraging AWS and Azure for compute-intensive workloads.
- Managed Services:Outsourced key lifecycle and policy administration relieves talent-constrained organizations of operational burden. Australian superannuation funds and Canadian provincial health authorities contract managed encryption for compliance coverage without internal cryptographer hires.
Cloud-based deployment is climbing the fastest; on-premises maintains revenue concentration among regulated incumbents.
End User:
Application-specific risk profiles drive divergent technology preferences, with financial services demanding real-time performance and healthcare prioritizing audit granularity.
- Financial Services:Real-time transaction tokenization and algorithmic trade surveillance dominate investment. Swiss private banks and Dutch clearinghouses deploy element-level protection across Swift messaging and blockchain settlement layers.
- Healthcare:HIPAA compliance and clinical data interoperability requirements shape purchasing. Mayo Clinic and Karolinska Institutet pilot confidential computing for multi-party genomics research without centralizing raw patient records.
- Retail:PCI-DSS scope reduction and loyalty program analytics drive demand. Nordic omnichannel merchants implement format-preserving encryption to preserve customer behavior tracking while de-scoping payment data.
- Government:Classified information handling and citizen identity systems require certified implementations. UK Cabinet Office and Australian Signals Directorate specify evaluated products for protective marking schemes.
Financial services retains procurement volume leadership; healthcare is gaining share fastest through AI Act compliance investment.
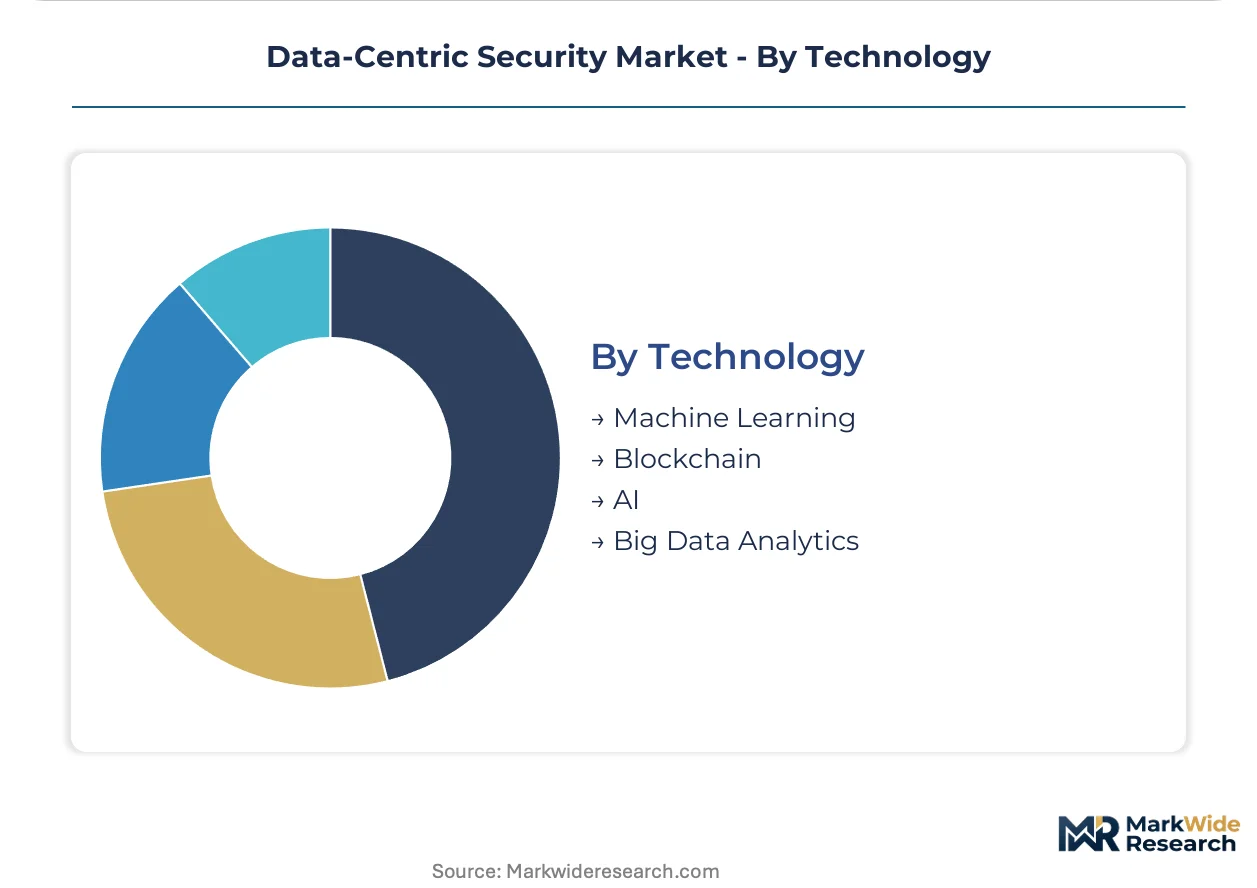
Technology:
Customer type segmentation separates buyers seeking autonomous policy engines from those requiring deterministic, auditable logic chains.
- Machine Learning:Behavioral analytics automate data classification and anomalous access detection. Varonis Systems and competitors deploy ML for insider threat identification in unstructured file shares.
- Blockchain:Distributed ledger anchoring provides immutable audit trails for data lineage verification. Estonian e-government infrastructure and Dubai trade finance platforms employ blockchain for cross-border attestation.
- AI:Natural language processing extracts and classifies sensitive entities from document repositories. French legal tech vendors and German compliance software firms integrate AI for GDPR Article 30 record-keeping automation.
- Big Data Analytics:Homomorphic encryption and secure multi-party computation enable analytics on encrypted datasets. Healthcare AI developers in Israel and quantitative hedge funds in Connecticut pilot these capabilities for privacy-preserving model training.
Machine learning retains deployment prevalence; confidential computing and homomorphic methods represent the steepest technology trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Price sensitivity in data-centric security procurement varies sharply by regulatory maturity, with United States buyers prioritizing speed-to-deployment over cost optimization while German and Japanese purchasers demand extensive compliance documentation regardless of premium pricing.
United States
Financial services firms and cloud-native enterprises drive fastest adoption curves for tokenization and encryption APIs. The SEC's cybersecurity disclosure rules and FTC data breach enforcement compel publicly traded companies to document protection controls in regulatory filings. New York and California clusters concentrate vendor headquarters and enterprise security operations centers where hybrid cloud deployments dominate procurement patterns.
Germany
Automotive suppliers and industrial machinery manufacturers anchor demand for on-premises hardware security modules and sovereign key management. GDPR Article 25 privacy-by-design mandates and BSI technical guidelines enforce cryptographic controls at data element levels for cross-border flows. Bavaria and Baden-Württemberg host dense concentrations of Mittelstand engineering firms retrofitting AES-256 encryption into legacy ERP systems.
Japan
Banking consortia and electronics manufacturers prioritize managed encryption services to offset domestic cryptographer shortages. FSA guidance on cloud outsourcing and METI data governance frameworks shape architectural decisions privileging hybrid deployments. Tokyo and Osaka financial districts pilot confidential computing for multi-party analytics while maintaining on-premises transaction processing.
Singapore
Fintech startups and digital health ventures favor consumption-based SaaS security models for operational flexibility. Monetary Authority of Singapore technology risk management guidelines and PDPA data protection requirements accelerate cloud-native tokenization adoption. The city-state's payments hub concentrates real-time transaction protection deployments across Southeast Asian corridor banks.
Israel
Cybersecurity research laboratories and medical device manufacturers pioneer homomorphic encryption for privacy-preserving AI training. Israel National Cyber Directorate certification requirements and health ministry data localization rules shape product development roadmaps. Tel Aviv's security technology cluster generates specialized vendors targeting healthcare AI compliance under converging GDPR and EU AI Act extraterritorial pressures.
Data-Centric Security Market Key Industry Players
A small set of integrated leaders sits above a broader specialist tier, with full-stack platform vendors competing against point-solution providers for enterprise architecture decisions. The market structure reflects consolidation pressure from cloud hyperscalers embedding native encryption while standalone vendors defend differentiation through metadata analytics and automated policy orchestration. Two strategic archetypes dominate: hybrid cloud infrastructure anchors and unstructured data governance specialists. Competitive moves concentrate on strategic partnerships with SaaS platforms and technology licensing for API-first security embedding.
Within the infrastructure-anchored tier, IBM represents integrated platform breadth across regulated industries, while NetApp exemplifies storage-centric protection architectures. Varonis Systems occupies a distinct position among metadata-driven specialists targeting insider threat detection in unstructured repositories. These three companies illustrate the competitive tension between horizontal consolidation and vertical depth that shapes vendor positioning across financial services and healthcare procurement cycles.
| Leading Market Players |
|---|
| Informatica |
| IBM |
| Broadcom |
| Micro Focus |
| Forcepoint |
| NetApp |
| Varonis Systems |
| Orange Cyberdefense |
| Imperva |
| Others |
Cost & Logistics Intelligence
Capacity utilization at cryptographic hardware manufacturing facilities in Taiwan and Germany sets minimum viable price floors for enterprise encryption deployments, concentrating supply-side leverage among semiconductor foundries with certified security module production lines while compressing margins for software-only vendors competing against integrated platform providers.
Pricing Analysis
Annual maintenance and key-escrow service contracts generate lifetime value multiples exceeding initial license fees by factors of three to five in enterprise deployments. Consumption-based SaaS metering dominates cloud-native segments while perpetual licensing persists in defense and national healthcare systems. Price differentiation stems from FIPS 140-2 certification tier and geographic data residency guarantees. Cost compression in mid-market tokenization reflects hyperscaler native encryption embedding. Fintech startups exhibit highest price sensitivity; sovereign wealth funds and central banks demonstrate lowest.
Supply Chain Analysis
Just-in-time component sourcing governs hardware security module production, with strategic stockpiling of quantum-resistant cryptographic processors emerging among defense contractors anticipating NIST standardization. Manufacturing concentrates in Taiwan, Germany, and the United States for specialized secure enclave chips. Supply chains draw from rare earth element processors in China, silicon wafer fabricators in Japan, and precision assembly facilities in Israel. Single-source vulnerability in post-quantum algorithm licensing creates concentration risk. Distribution runs through systems integrators and direct enterprise sales with managed service overlays.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Data-centric security sits in early-cycle expansion as GDPR Article 25 enforcement and SEC cybersecurity disclosure rules simultaneously mandate element-level protection architectures across Fortune 500 deployments.
For Market Incumbents: Secure hybrid cloud infrastructure anchoring through exclusive partnerships with AWS, Azure, and GCP marketplace integrations before hyperscalers fully native their encryption stacks. Deepen metadata analytics R&D to defend against point-solution disintermediation in unstructured data governance. Prioritize FIPS 140-3 Level 4 certification investment to maintain premium pricing in federal and financial verticals. For New Entrants and Emerging Players: FedRAMP and StateRAMP fast-tracks open federal agency procurement channels currently underserved by legacy vendors. Target healthcare AI developers in Germany and Israel facing steepest EU AI Act compliance ramps with API-first tokenization bundles. Pursue channel partnerships with existing GRC platforms to bypass direct enterprise sales cycle friction. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among managed encryption service providers with multi-year government contracts and healthcare system key-administration agreements. Long-term viability favors vendors with quantum-resistant algorithm roadmaps and confidential computing hardware partnerships. Watch NIST post-quantum standardization finalization as inflection signal for harvest-now-decrypt-later threat response spending.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | Hardware enclave integration with Intel SGX and AMD SEV compresses healthcare multi-party analytics compliance costs. |
| API-First Security Embedding | Native SDK distribution through Salesforce and ServiceNow marketplaces reduces fintech implementation friction. |
| Quantum-Resistant Algorithm Roadmap | NIST CRYSTALS-Kyber and Dilithium early adoption defends against harvest-now-decrypt-later nation-state threats. |
| Managed Key Lifecycle Service | Outsourced HSM administration relieves talent-constrained Australian superannuation funds of cryptographer hiring burden. |
| Cross-Border Data Localization Architecture | Split key escrow across Frankfurt, Singapore, and Virginia satisfies conflicting sovereignty mandates without policy fragmentation. |
Research Approach
Desk research of regulatory filing databases, hyperscaler security product documentation, and cryptographic standards body publications preceded structured interviews with CISOs at financial services firms, data protection officers at German automotive suppliers, cloud security architects at Israeli medical device companies, and procurement leads at Japanese banking consortia. Primary intelligence combined with secondary validation from SEC 10-K cybersecurity disclosures, EU Data Protection Board enforcement trackers, and NIST cryptographic standardization drafts. Bottom-up deployment sizing and top-down market reconstruction were triangulated against vendor revenue segment reporting.
Variance decomposition across product type, deployment model, end-user vertical, and technology integration depth shaped the analytical framework over the projection horizon. CAGRs derived from segment-level adoption curves weighted by regulatory enforcement intensity and cloud migration velocity. Quantum-resistant algorithm readiness and confidential computing hardware availability served as technology-specific forecast inputs alongside cross-border data flow restriction indices.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement pressure and hyperscaler native encryption embedding timelines would require recalibration. Forecasts reflect assumptions regarding GDPR and SEC rule implementation consistency without anticipating fundamental cryptographic standard disruptions. Revision becomes warranted when post-quantum algorithm standardization accelerates or major cloud providers vertically integrate element-level protection natively at no incremental cost.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Global Zero-Trust Security Market
Cybersecurity
Enterprise Network Firewall Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Global Patch Management Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Threat Intelligence Market
Cybersecurity
South Korea Ransomware Protection Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
Global Network Security Policy Management Market