
 France Cybersecurity Market | 2026-2036
France Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
France Cybersecurity Market Analysis
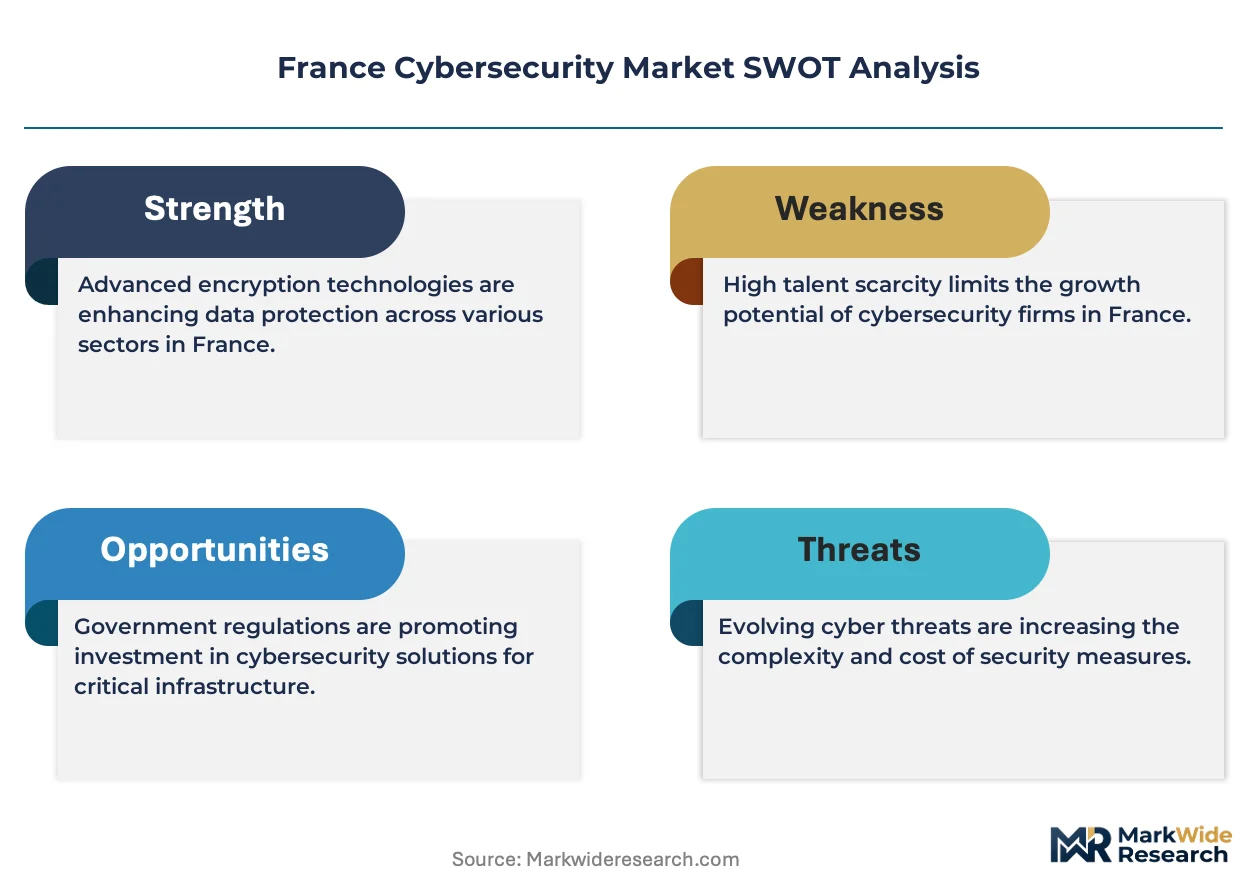
NIS2 is expanding the compliance burden for mid-market enterprises that previously operated below regulatory thresholds. Atos SE leverages its sovereign cloud credentials to anchor large public-sector contracts. Thales Group competes through embedded cryptography in defense and aerospace systems. Orange Cyberdefense dominates managed security services for French multinational corporations.
France cybersecurity encompasses hardware, software, and services designed to protect digital assets from unauthorized access, disruption, or exfiltration, with next-generation firewalls inspecting encrypted traffic at line speeds exceeding 100 Gbps. The primary purpose spans safeguarding national critical infrastructure, enterprise intellectual property, and citizen data across interconnected operational technology environments. Managed Security Services leads service type revenue due to persistent talent shortages pushing organizations toward outsourced security operations centers. Cloud deployment models are gaining share fastest as French regulators clarify data localization requirements under GDPR and the forthcoming SecNumCloud certification revisions. Network Security anchors application type spending because industrial control system vulnerabilities in energy and manufacturing verticals command premium remediation budgets.
ANSSI sets technical standards for security certification while CNIL enforces data protection penalties that reshape breach disclosure economics for French enterprises. The EU Cyber Resilience Act, once transposed, will impose mandatory security update obligations on connected device manufacturers selling into France. Stakeholders must monitor how quantum-safe cryptography migration timelines intersect with existing PKI infrastructure refresh cycles.
Market Dynamics
The France Cybersecurity Market is undergoing structural compression as NIS2 transposition forces mid-market enterprises into compliance regimes previously reserved for critical infrastructure operators. This regulatory cascade is redrawing competitive boundaries between sovereign cloud providers and international platform vendors.
Growth Catalysts
- NIS2 Transposition:France's implementation of the EU directive mandates 24-hour incident reporting for energy and transport operators, expanding addressable market for managed detection and response services.
- Quantum Cryptography R&D:Paris-Saclay cluster investment in post-quantum algorithms is accelerating migration timelines for defense and financial PKI infrastructure.
- SecNumCloud Certification:Revised sovereign cloud standards are disqualifying non-compliant vendors from public-sector procurement, creating protected demand pools for accredited providers.
Market Restraints
- Specialized Talent Scarcity:ANSSI-certified security architects command compensation premiums that inflate SOC operational costs beyond mid-market absorption thresholds.
- Legacy OT Integration Friction:Industrial control systems in French manufacturing verticals lack native API connectivity, forcing expensive gateway deployments for zero-trust overlay.
- Cross-Border Data Localization:GDPR-Schrems II compliance complexity restricts French enterprises from leveraging lower-cost security operations centers in non-adequacy jurisdictions.
Strategic Opportunities
- Regional MSS Expansion:Grand Est and Occitanie manufacturing bases remain underserved by managed security services relative to Paris-Île-de-France concentration.
- EU Cyber Resilience Act Preparation:Connected device manufacturers require pre-market conformity assessment partnerships ahead of mandatory security update obligations.
- AI-Augmented Threat Detection:Convergence of large language models with SIEM platforms enables natural language query interfaces for tier-1 analyst augmentation.
Industry Challenges
- Certification Backlog:ANSSI's Common Criteria evaluation queue extends delivery timelines for defense contractors bidding NATO-aligned programs.
- Multi-Cloud Policy Orchestration:French enterprises operating across AWS, Azure, and OVHcloud environments struggle with consistent identity governance enforcement.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | France Cybersecurity Market |
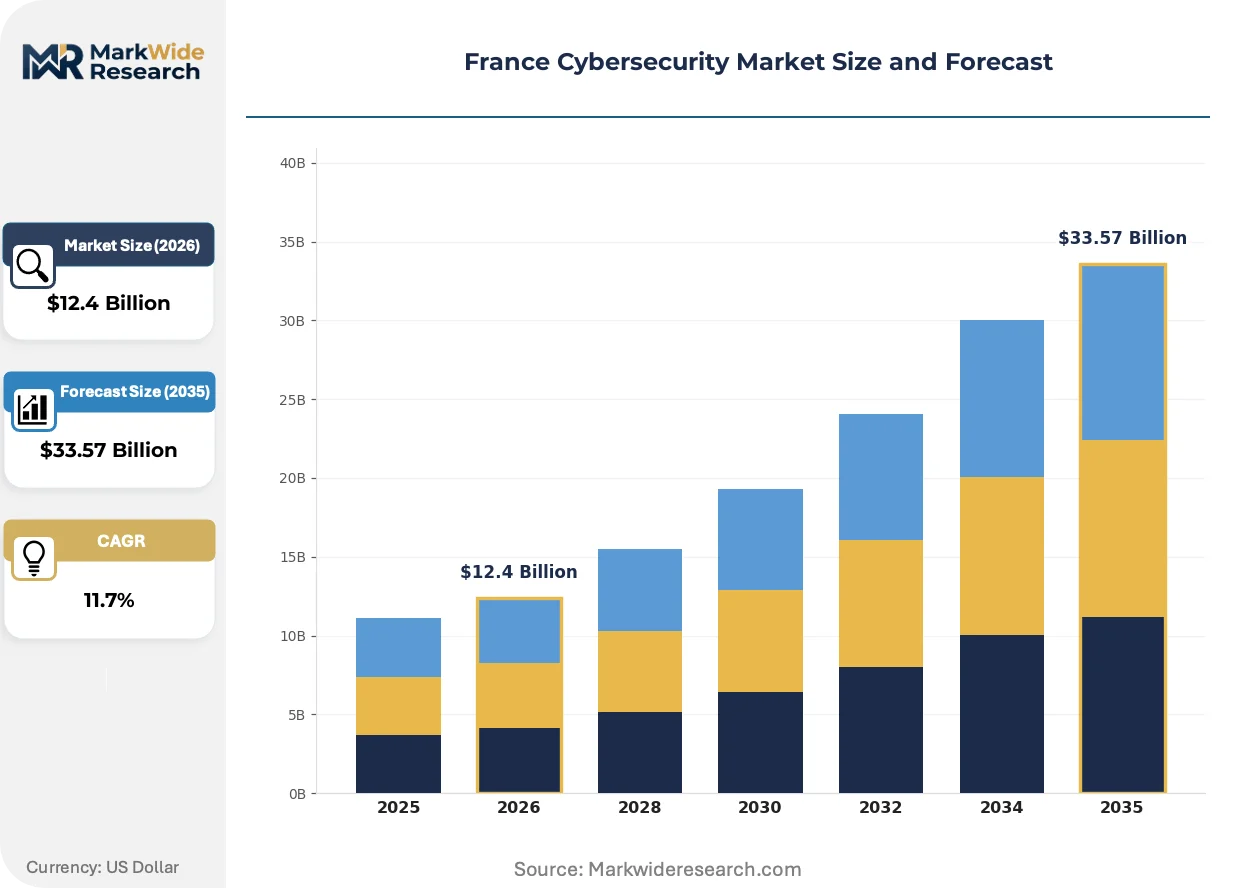
| Market Size in 2026 | $12.4 Billion |
| Market Size in 2035 | $33.57 Billion |
| CAGR (2026 – 2036) | 11.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Managed Security Services, Incident Response, Threat Intelligence, Compliance Management Deployment Model: On-Premises, Cloud, Hybrid, Virtual Application Type: Network Security, Data Security, Endpoint Security, Application Security End User: Government, BFSI, Healthcare, Retail |
| Companies Covered | Atos SE, Sopra Steria Group, Factosecure, Wallix Group, Airbus Defence & Space CyberSecurity, Orange Cyberdefense, Capgemini SE, Stormshield, Thales Group, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
France Cybersecurity Market Emerging Trajectories
Security architecture in France is pivoting from perimeter defense to identity-centric verification models. This transformation is compressing procurement cycles for hardware firewalls while expanding software-defined security service contracts.
Confidential computing is rewriting data protection economics for French healthcare and finance sectors. Hospices and mutual insurers are piloting encrypted memory processing for patient record analytics. The technology is compressing traditional database encryption overhead while enabling multi-party computation across competing institutions.
France's transposition of the EU Cyber Resilience Act imposes mandatory vulnerability disclosure timelines on IoT manufacturers. Industrial gateway producers must maintain 10-year security update commitments for energy sector deployments. Medical device vendors are restructuring quality management systems to integrate IEC 62443 security development lifecycle requirements ahead of notified body audits.
French enterprise procurement of cybersecurity services is consolidating under single MSSP relationships with outcome-based SLA structures. Manufacturing groups in Hauts-de-France are replacing multi-vendor point solutions with integrated detection-response-recovery contracts. This consolidation is visible most acutely in CAC 40 industrial conglomerates seeking unified telemetry across OT and IT environments.
France Cybersecurity Market Segmentation
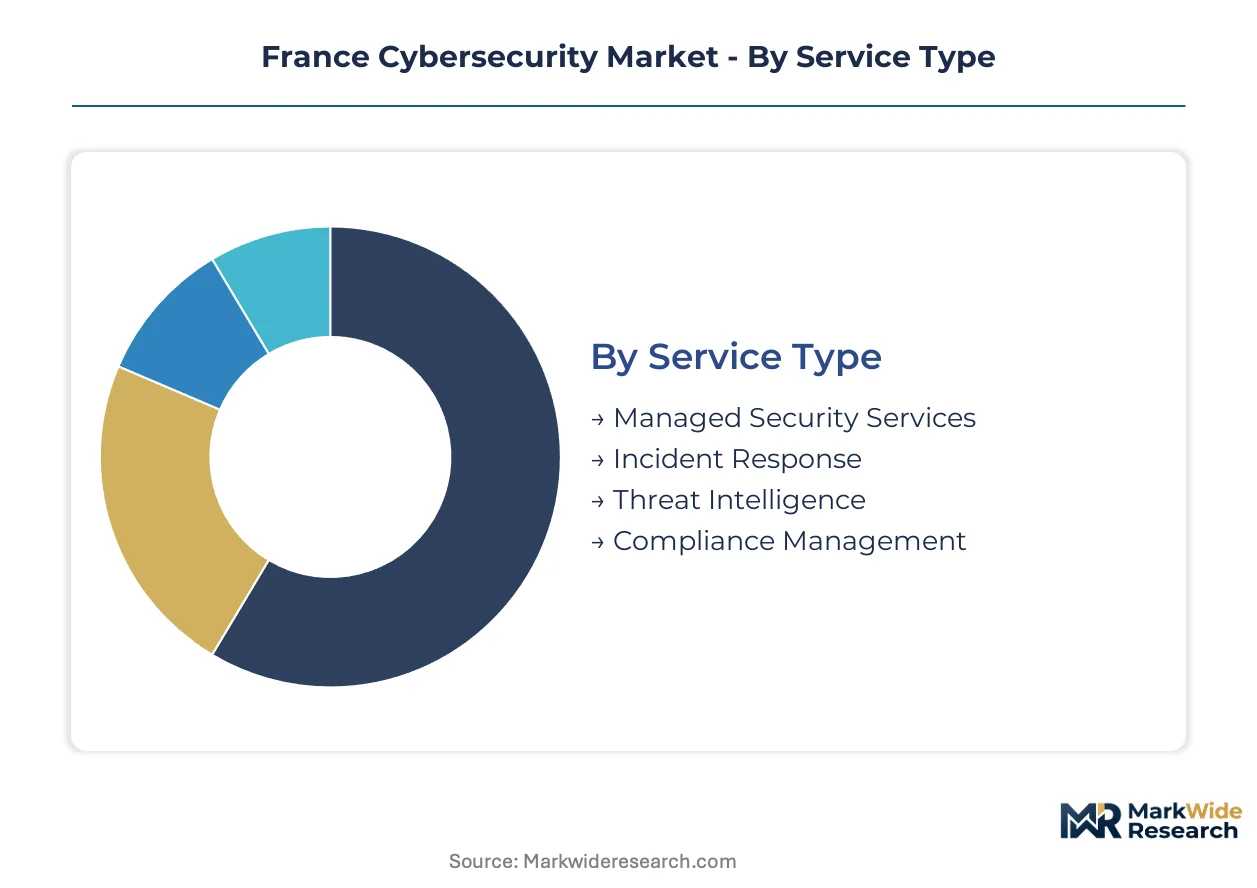
Segmentation in the France cybersecurity market reveals how procurement priorities diverge between sovereign compliance mandates and operational technology protection requirements. Buyers select service tiers based on ANSSI certification status and SecNumCloud eligibility rather than feature comparisons alone.
Service Type:
Procurement teams weight service selection against internal SOC staffing gaps and regulatory reporting obligations under NIS2.
- Managed Security Services:Outsourced security operations centers deliver 24/7 threat monitoring with ANSSI-certified analysts. French energy operators and CAC 40 manufacturers concentrate demand here due to mandatory incident response timelines and persistent talent scarcity in Ile-de-France.
- Incident Response:Retainer-based emergency containment and forensic investigation services activate within four-hour SLAs for critical infrastructure. Regional hospital networks in Grand Est and Occitanie are expanding retainer coverage following ransomware disruptions to patient care systems.
- Threat Intelligence:Sector-specific IOC feeds and actor attribution reports tailored to French aerospace and defense supply chains.
- Compliance Management:Automated evidence collection and CNIL breach notification workflows for GDPR and forthcoming Cyber Resilience Act obligations.
Managed Security Services leads on scale; Incident Response leads on momentum.
Deployment Model:
Deployment architecture decisions hinge on data localization requirements and legacy OT system connectivity constraints.
- Cloud:SecNumCloud-certified sovereign platforms with encryption key escrow under French jurisdiction. Public-sector procurement and defense contractors in Paris-Saclay cluster are migrating fastest to meet revised certification standards disqualifying non-compliant vendors.
- Hybrid:Split architectures keeping sensitive PKI and quantum cryptography workloads on-premises while pushing telemetry analytics to accredited cloud tiers. BFSI institutions in La Défense district favor this model for customer transaction data.
- On-Premises:Air-gapped security stacks for classified defense networks and nuclear facility operational technology.
- Virtual:Containerized security functions deployed across multi-cloud environments with policy orchestration layers.
Cloud deployment gains share fastest; Hybrid retains the largest installed base among regulated enterprises.
Application Type:
Application-layer spending tracks vulnerability exposure in interconnected industrial control systems and encrypted data flows.
- Network Security:Next-generation firewalls and zero-trust network access inspecting TLS 1.3 traffic at 100+ Gbps. French energy transmission operators and manufacturing verticals command premium budgets for industrial control system gateway protection.
- Data Security:Confidential computing enclaves and quantum-safe encryption for healthcare analytics and mutual insurer record processing.
- Endpoint Security:Extended detection and response agents with kernel-level visibility across remote workforces and OT engineering stations.
- Application Security:DevSecOps pipeline integration and software composition analysis for connected device manufacturers preparing EU Cyber Resilience Act conformity assessments.
Network Security anchors current spending; Data Security climbs the fastest on confidential computing pilots.
End User:
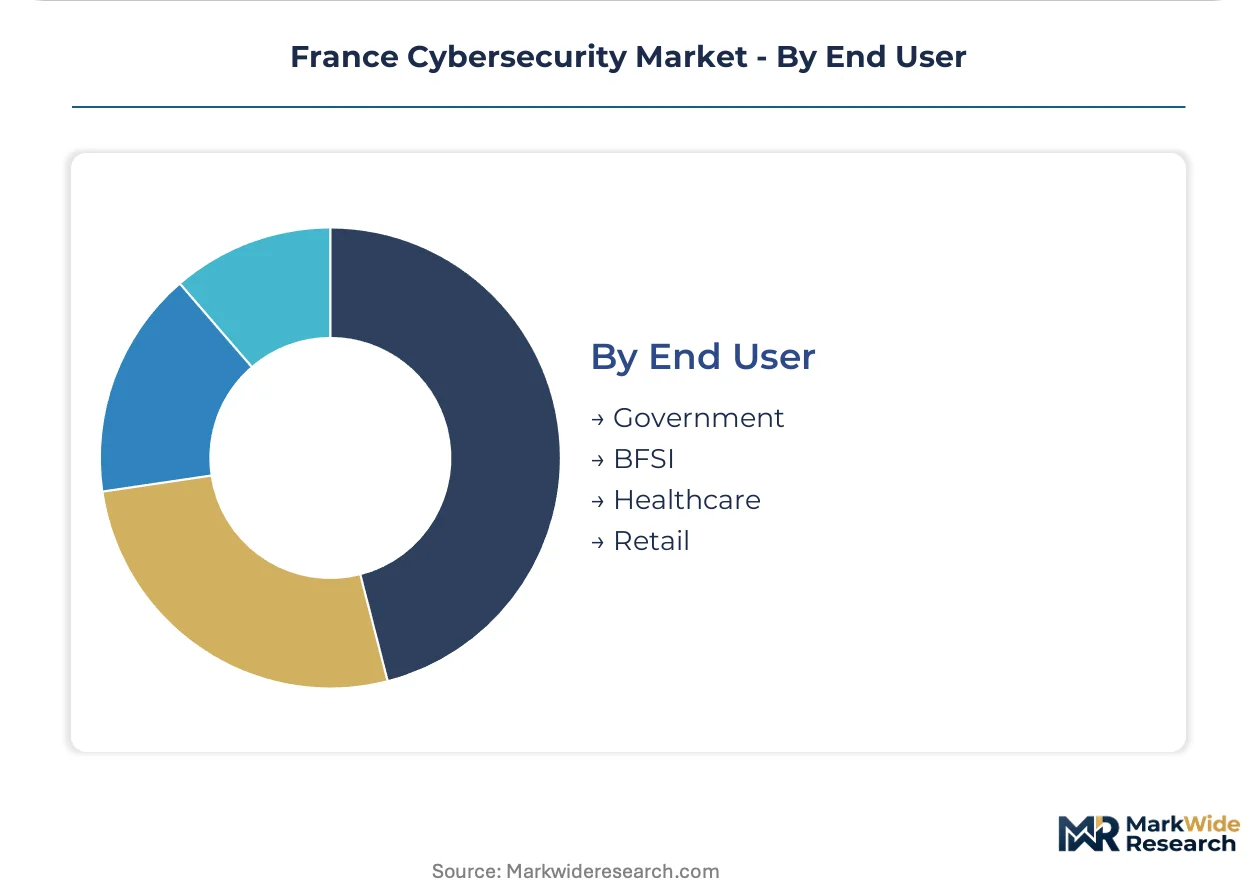
End-user demand concentrates where regulatory enforcement carries criminal liability for security failures.
- Government:ANSSI-directed procurement of sovereign cloud and classified network protection spanning ministries, agencies, and military commands. Defense contractors in Brittany and Provence-Alpes-Côte d'Azur aerospace clusters drive embedded cryptography demand.
- BFSI:Payment infrastructure protection and quantum-resistant PKI migration for systemic banks under European Central Bank oversight. Paris-based investment firms and mutual insurers are piloting multi-party computation for cross-institutional fraud detection.
- Healthcare:Medical device security and patient record confidentiality for hospital groups and regional health agencies.
- Retail:POS terminal protection and e-commerce fraud prevention for national chains and logistics operators.
Government leads on contract value; BFSI shows the steepest expansion trajectory on quantum cryptography mandates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Paris-Saclay's concentration of ANSSI-certified security architects anchors national capacity, with Île-de-France hosting over half of France's cybersecurity workforce. Regional demand clusters follow defense procurement geography and critical infrastructure density.
Île-de-France
La Défense financial district and Paris-Saclay research cluster drive sovereign cloud migration and quantum cryptography R&D. CNIL enforcement actions against data breaches reshape procurement priorities for systemic banks. Defense contractors in the Saclay plateau accelerate zero-trust architecture deployment across NATO-aligned supply chains.
Provence-Alpes-Côte d'Azur
Aerospace and naval defense concentration in Toulon and Marseille sustains embedded cryptography demand for military platforms. Thales Group facilities anchor specialized supply chains for secure communications. Regional hospital networks expand incident response retainers following ransomware disruptions to patient care systems.
Hauts-de-France
Manufacturing conglomerates in Lille and Dunkirk consolidate multi-vendor security contracts under integrated MSSP relationships. Industrial control system vulnerabilities in energy transmission command premium remediation budgets. Regional authorities promote cybersecurity apprenticeship pipelines to address ANSSI-certified talent scarcity.
Auvergne-Rhône-Alpes
Grenoble's semiconductor ecosystem intersects with hardware security module development for financial PKI infrastructure. BFSI institutions pilot confidential computing for cross-institutional fraud detection. The region's medical device manufacturers restructure quality systems for EU Cyber Resilience Act conformity assessments.
Occitanie
Space industry concentration in Toulouse drives secure satellite communications procurement. Regional manufacturing bases remain underserved by managed security services relative to Paris-Île-de-France concentration. Local authorities leverage EU structural funds to attract MSSP delivery centers.
France Cybersecurity Market Vendor Landscape
Diversified conglomerates compete with focused pure-play specialists across contract tiers. The vendor base stratifies between sovereign cloud providers holding SecNumCloud accreditation and international platform vendors pursuing certification. Three archetypes dominate: defense-anchored systems integrators, telecom-born MSSP platforms, and boutique cryptography specialists. Consolidation pressure intensifies as NIS2 compliance mandates expand addressable market for integrated detection-response-recovery contracts.
Among defense-anchored conglomerates, Thales Group and Airbus Defence & Space CyberSecurity exemplify embedded security architecture for aerospace and military applications. Orange Cyberdefense occupies a position within the telecom-born MSSP tier, leveraging pan-European network infrastructure for managed detection services. Atos SE anchors the sovereign cloud specialist archetype through public-sector accreditation and ANSSI-directed procurement relationships.
| Leading Market Players |
|---|
| Atos SE |
| Sopra Steria Group |
| Factosecure |
| Wallix Group |
| Airbus Defence & Space CyberSecurity |
| Orange Cyberdefense |
| Capgemini SE |
| Stormshield |
| Thales Group |
| Others |
Supply Flow & Price Mechanics
Captive integration of ANSSI-certified security architects within sovereign cloud providers anchors both supply security and premium pricing power for accredited vendors serving French public-sector procurement. Defense contractors and critical infrastructure operators pay compliance premiums that non-certified competitors cannot access, compressing margins for unaccredited international platforms while protecting domestic specialist margins.
Pricing Analysis
Bundled managed detection-and-response contracts dominate enterprise procurement, while unbundled point solutions face commoditization pressure. Three-tier pricing structure across premium, standard, and economy levels separates SecNumCloud-accredited sovereign platforms from hybrid deployments and generic cloud-native alternatives. Pricing pressure stems from mid-market enterprises absorbing NIS2 compliance costs without proportional budget expansion. CAC 40 manufacturers show least price sensitivity due to criminal liability exposure for security failures.
Supply Chain Analysis
Dual-sourcing requirements for cryptographic hardware modules mandate multi-supplier qualification across French defense procurement, forcing vendors to maintain parallel certification tracks. Supply concentrates in France for sovereign cloud infrastructure, Germany for hardware security modules, and Taiwan for semiconductor components underlying encryption accelerators. Gallium nitride substrates and quantum-grade optical components anchor raw material dependencies. Single-source vulnerability in post-quantum algorithm intellectual property creates concentration risk. Distribution runs through ANSSI-accredited systems integrators with direct ministry relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The France cybersecurity market functions as a stable compounder where regulatory mandate expansion under NIS2 and the EU Cyber Resilience Act generates recurring compliance-driven demand with limited cyclical exposure.
For Market Incumbents: Lock in SecNumCloud accreditation renewals ahead of revised certification standards disqualifying current holders. Deepen vertical integration into quantum cryptography R&D through Paris-Saclay cluster partnerships to capture defense PKI refresh cycles. The threat of hyperscaler platform vendors achieving accreditation requires preemptive channel control in Grand Est and Occitanie manufacturing bases.
For New Entrants and Emerging Players: Cloud-native SIEM platforms with natural language query interfaces offer the most penetrable wedge for tier-1 analyst augmentation in mid-market enterprises. Target regional hospital networks in Provence-Alpes-Côte d'Azur and Occitanie expanding incident response retainers post-ransomware disruptions. Partner with established MSSPs for ANSSI certification sponsorship rather than pursuing independent accreditation.
For Investors and Strategic Acquirers: Roll-up economics work for boutique cryptography specialists because ANSSI certification backlogs create scarcity premiums for accredited engineering teams. Five-to-ten-year viability hinges on quantum-safe migration service capabilities intersecting with defense and BFSI PKI refresh cycles. Watch ANSSI Common Criteria evaluation queue lengths as the inflection signal for certification-constrained supply bottlenecks.
| Strategic Initiative | Industry Significance |
|---|---|
| SecNumCloud Accreditation Renewal | Revised sovereign cloud standards under ANSSI direction protect incumbent pricing power in public-sector procurement. |
| Quantum Cryptography R&D Partnership | Paris-Saclay cluster collaboration accelerates post-quantum algorithm deployment for defense PKI infrastructure. |
| Regional MSSP Delivery Center | EU structural funds in Occitanie subsidize expansion into underserved manufacturing bases outside Île-de-France. |
| AI-Augmented SIEM Platform Launch | Large language model integration addresses ANSSI-certified analyst scarcity through tier-1 workflow automation. |
| EU Cyber Resilience Act Conformity Service | Pre-market assessment partnerships capture connected device manufacturer demand ahead of mandatory security obligations. |
Methodological Framework
Coverage spans France, Germany, and the United Kingdom, with primary inputs from each jurisdiction triangulated against secondary validation. Interviews with CISOs at CAC 40 manufacturers, ANSSI certification officers, procurement leads at regional hospital networks, and sovereign cloud platform engineers informed demand-side assessments. Secondary sources include ANSSI technical standard publications, CNIL enforcement action databases, EU Cyber Resilience Act draft impact assessments, and SecNumCloud certification registries. Bottom-up service-type demand modeling and top-down regulatory mandate sizing were reconciled through iterative triangulation.
Granularity-level modeling deployed service type, deployment model, application type, and end-user vertical as primary segmentation dimensions, with quantum cryptography readiness status as an industry-specific overlay. CAGRs across the projection horizon derived from regulatory mandate timing, certification queue dynamics, and technology refresh cycle assumptions. Forecast inputs incorporated NIS2 transposition implementation schedules, EU Cyber Resilience Act conformity assessment timelines, and post-quantum algorithm standardization progress from NIST and ANSSI.
Regulatory delay, certification backlog extension, and quantum computing advancement timeline acceleration are the dominant revision risks to modeled assumptions. Deviation in ANSSI certification processing capacity would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Europe Web Application Firewall Market
Cybersecurity
Data Protection Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Endpoint Security Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Europe Mobile Security Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
UK Cybersecurity Market
Cybersecurity
DNS Security Market
Cybersecurity
Global Patch Management Market