
 China Ransomware Protection Market | 2026-2036
China Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
China Ransomware Protection Market Insights
China's eastern seaboard technology corridor is reconfiguring ransomware defense procurement patterns. Huawei leverages integrated silicon-to-software stacks to dominate domestic infrastructure bids. Qihoo 360 sustains consumer brand recognition while extending enterprise endpoint coverage. Sangfor Technologies specializes in converged security appliances for mid-market provincial deployments.
Ransomware protection encompasses endpoint detection, network segmentation, cloud workload defense, and immutable backup architectures engineered to intercept encryption payloads before data exfiltration completes. Endpoint Protection and Cloud Security segments lead current procurement volumes as state-owned enterprises modernize hybrid infrastructure. Behavioral Analytics and Threat Intelligence technologies attract fastest-growing investment as CISOs prioritize autonomous response over signature-dependent detection. Managed Services deployment shows emerging margin concentration among operators with cleared personnel access to sensitive government systems.
MIIT's multi-level protection scheme and SAMR's critical information infrastructure regulations mandate certified domestic encryption and incident reporting protocols. GB standards for cybersecurity等级保护 (classified protection) shape product certification requirements and foreign vendor market access limitations. Stakeholders must monitor regulatory alignment between commercial product roadmaps and evolving state secret compliance tiers.
Market Dynamics
MIIT's multi-level protection scheme upgrades are compelling state-owned enterprises to replace legacy signature-based defenses with behavioral analytics platforms. Provincial financial institutions now face mandatory incident reporting timelines that accelerate procurement cycles.
Growth Catalysts
- Critical Information Infrastructure Mandates:SAMR's regulations designate finance, energy, and transportation as protected tiers. Operators in these sectors must deploy certified domestic encryption and maintain immutable backup architectures.
- State-Owned Bank Modernization:China's policy banks and provincial commercial lenders are consolidating cybersecurity budgets. These institutions prioritize converged security appliances over point solutions.
- Cloud Workload Expansion:Hybrid infrastructure adoption across eastern seaboard technology corridors creates demand for cloud-native ransomware detection. Beijing and Shanghai data centers drive early deployment.
Market Restraints
- Certified Component Concentration:Domestic silicon and encryption module suppliers cluster in Shenzhen and Hefei. Supply bottlenecks for certified hardware extend deployment timelines.
- Foreign Vendor Access Limitations:GB standards for cybersecurity等级保护 restrict procurement of non-domestic endpoint platforms. Multinational vendors face product localization requirements.
- Skilled Analyst Scarcity:Shortage of SOC personnel cleared for sensitive government systems limits managed services scaling. Training pipelines lag behind deployment needs.
Strategic Opportunities
- Western Province Penetration:Sichuan and Shaanxi industrial bases remain underpenetrated relative to coastal corridors. Provincial SOEs in these regions are beginning multi-level protection compliance programs.
- AI-Augmented Response Convergence:Integration of large language models with endpoint detection enables autonomous containment. Early adopters in Shenzhen's fintech cluster validate these architectures.
- Cleared Personnel Services:Operators with MIIT security clearance access can deliver managed detection and response to defense-adjacent enterprises. This channel commands premium positioning.
Industry Challenges
- Legacy System Integration Friction:Provincial banks operate heterogeneous core banking platforms. Ransomware protection deployment requires custom middleware development.
- Certification Timeline Compression:GB standard updates accelerate faster than vendor product recertification cycles. Roadmap misalignment risks procurement disqualification.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | China Ransomware Protection Market |
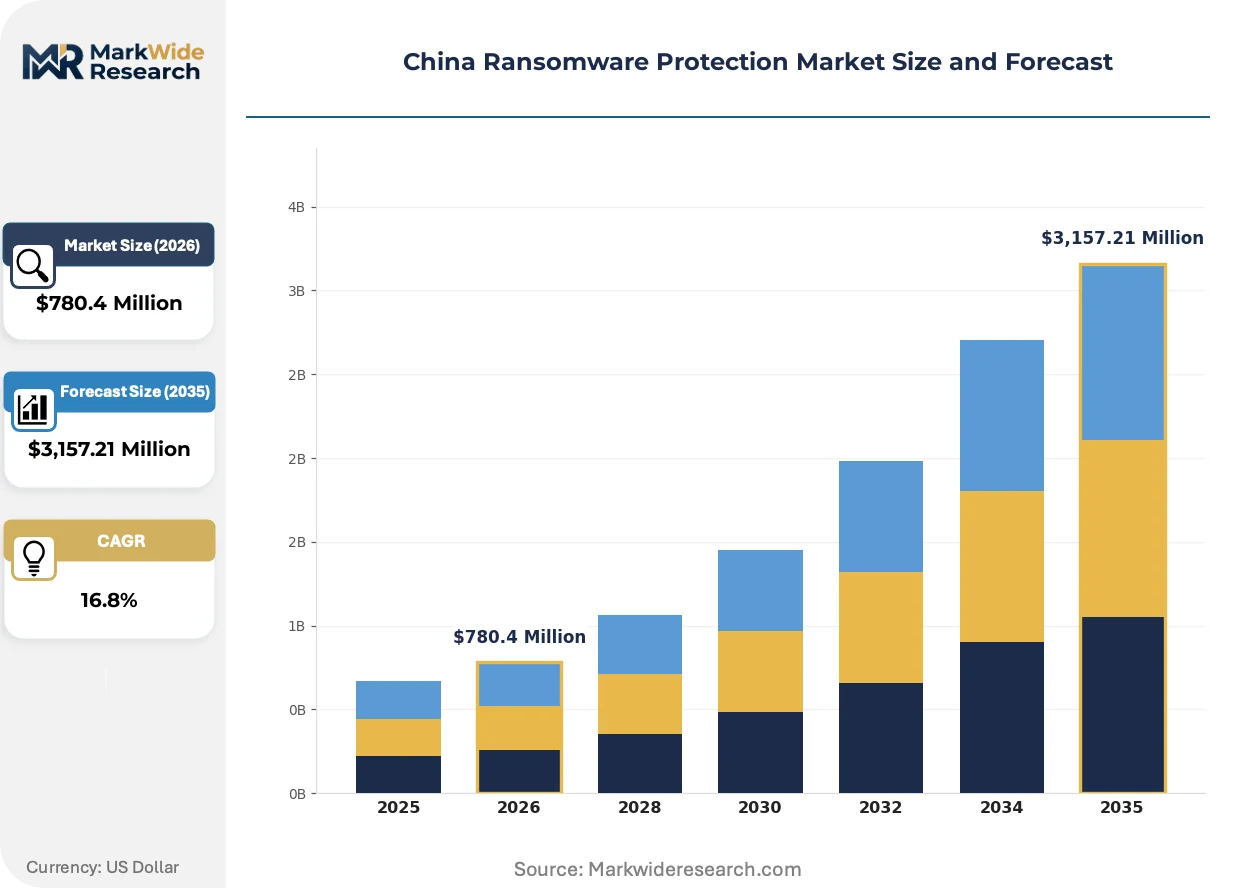
| Market Size in 2026 | $780.4 Million |
| Market Size in 2035 | $3,157.21 Million |
| CAGR (2026 – 2036) | 16.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Protection, Network Security, Cloud Security, Data Backup Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Healthcare, Finance, Retail, Education Technology: Artificial Intelligence, Machine Learning, Behavioral Analytics, Threat Intelligence |
| Companies Covered | Alibaba, NSFOCUS, Qihoo 360, Baidu, Venustech, Tencent Security, Sangfor Technologies, EFW, Huawei, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
China Ransomware Protection Market Trends and Innovations
Behavioral analytics platforms are displacing signature-dependent detection across China's financial sector. CISOs now prioritize autonomous response capabilities that intercept encryption payloads before exfiltration completes.
Extended detection and response architectures are virtualizing security operations center functions. State-owned enterprises in Beijing and Shanghai are consolidating point solutions into unified platforms. This convergence compresses vendor count while elevating platform stickiness.
MIIT's data security governance rules mandate real-time incident reporting for designated critical infrastructure. Provincial operators must deploy certified domestic systems with automated telemetry. Financial institutions in the Yangtze River Delta corridor are fastest to comply.
Subscription-based managed detection services are displacing perpetual license procurement among mid-market provincial enterprises. Systems integrators with cleared personnel access capture margin concentration. This pattern is most visible in Guangdong's manufacturing technology clusters.
China Ransomware Protection Market Segmentation
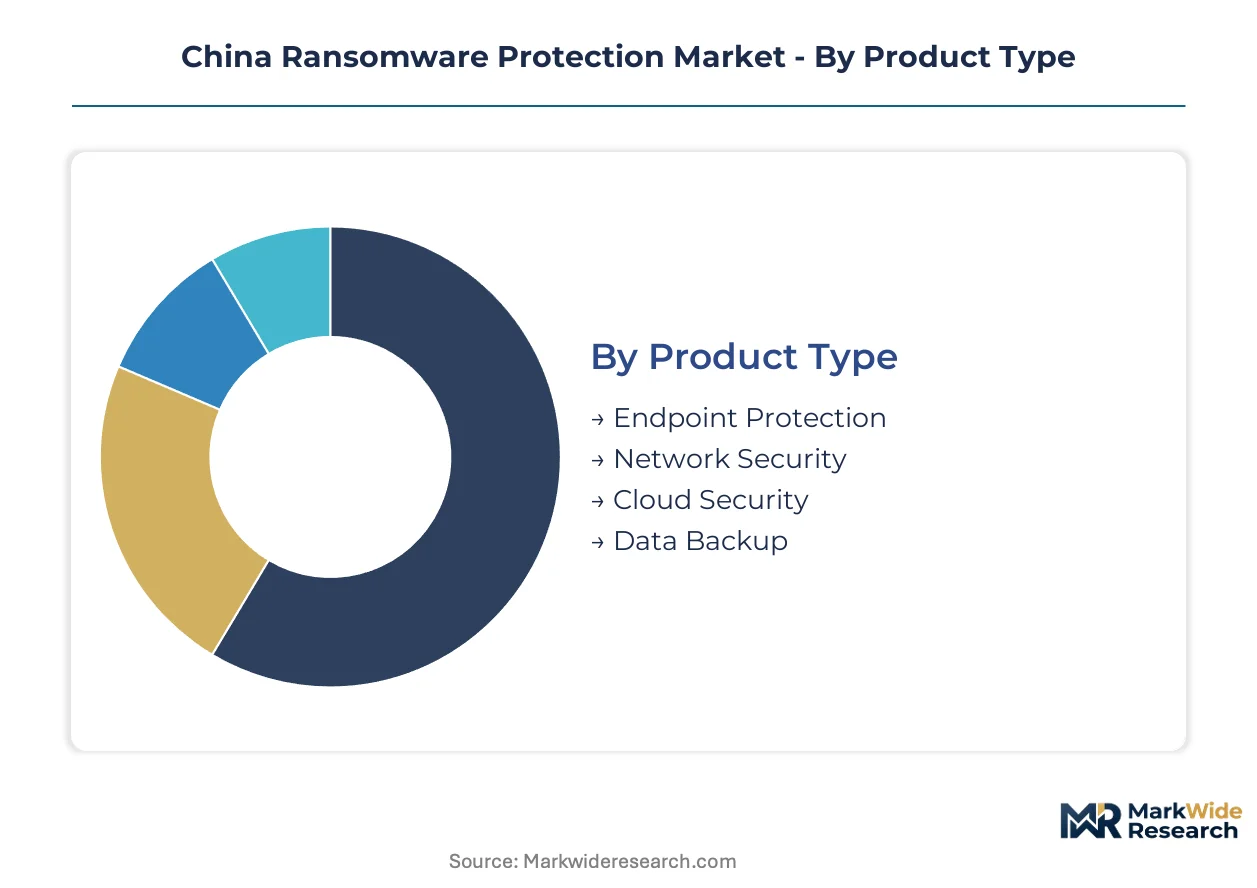
Procurement patterns across China's ransomware protection market diverge sharply by infrastructure maturity and regulatory exposure. State-owned enterprises prioritize certified domestic platforms, while provincial mid-market buyers seek converged appliances that compress deployment complexity.
Product Type:
Use cases span from endpoint encryption interception to immutable backup architectures for core banking systems.
- Endpoint Protection:Behavioral detection engines intercept encryption payloads before file system compromise completes. Beijing's state-owned banks and Shanghai's provincial financial institutions drive procurement as MIIT's multi-level protection scheme mandates endpoint telemetry.
- Cloud Security:Cloud-native workload defense monitors containerized applications and serverless functions for anomalous encryption activity. Yangtze River Delta data centers lead deployment, with Shenzhen's fintech clusters validating autonomous response architectures.
- Network Security:Segmentation appliances isolate lateral movement paths between critical infrastructure tiers. Demand concentrates in energy and transportation operators designated under SAMR's protected tiers.
- Data Backup:Immutable snapshot systems maintain air-gapped recovery points outside ransomware reach. Provincial SOEs in Sichuan and Shaanxi are beginning compliance-driven procurement cycles.
The dominant share belongs to Endpoint Protection, while Cloud Security is closing the gap fastest.
Deployment:
Cost tiers separate cleared-personnel managed services from self-operated on-premises platforms.
- Managed Services:Operators with MIIT security clearance deliver 24/7 detection and response to defense-adjacent enterprises. Premium positioning reflects cleared analyst scarcity and automated telemetry mandates under data security governance rules.
- Hybrid:Split architectures maintain sensitive workloads on-premises while bursting analytics to certified domestic clouds. Guangdong's manufacturing technology clusters show emerging subscription displacement of perpetual licenses.
- On-Premises:Air-gapped deployments satisfy state secret compliance tiers for critical information infrastructure. Certification bottlenecks for domestic silicon extend deployment timelines.
- Cloud-Based:Fully virtualized protection suits mid-market provincial enterprises without dedicated SOC staffing. Beijing and Shanghai technology corridors drive early adoption.
Managed Services commands the steepest margin premium, though Hybrid architectures are expanding most quickly among compliance-driven buyers.
End User:
Application criticality determines procurement urgency and certification stringency.
- Finance:Policy banks and provincial commercial lenders consolidate cybersecurity budgets around converged appliances. Mandatory incident reporting timelines accelerate replacement of legacy signature-based defenses.
- Healthcare:Patient data protection drives investment in behavioral analytics platforms that detect encryption anomalies. GB standards for cybersecurity等级保护 shape product certification requirements.
- Retail:Point-of-sale and e-commerce infrastructure face ransomware targeting payment card data. Eastern seaboard technology corridors show fastest compliance adoption.
- Education:Research institutions with sensitive government funding require cleared-personnel access for managed services. Procurement lags finance and healthcare due to budget fragmentation.
Finance holds the largest committed spend, with Healthcare gaining share fastest as patient data regulations tighten.
Technology:
Maturity curves separate production-deployed AI from emerging autonomous response capabilities.
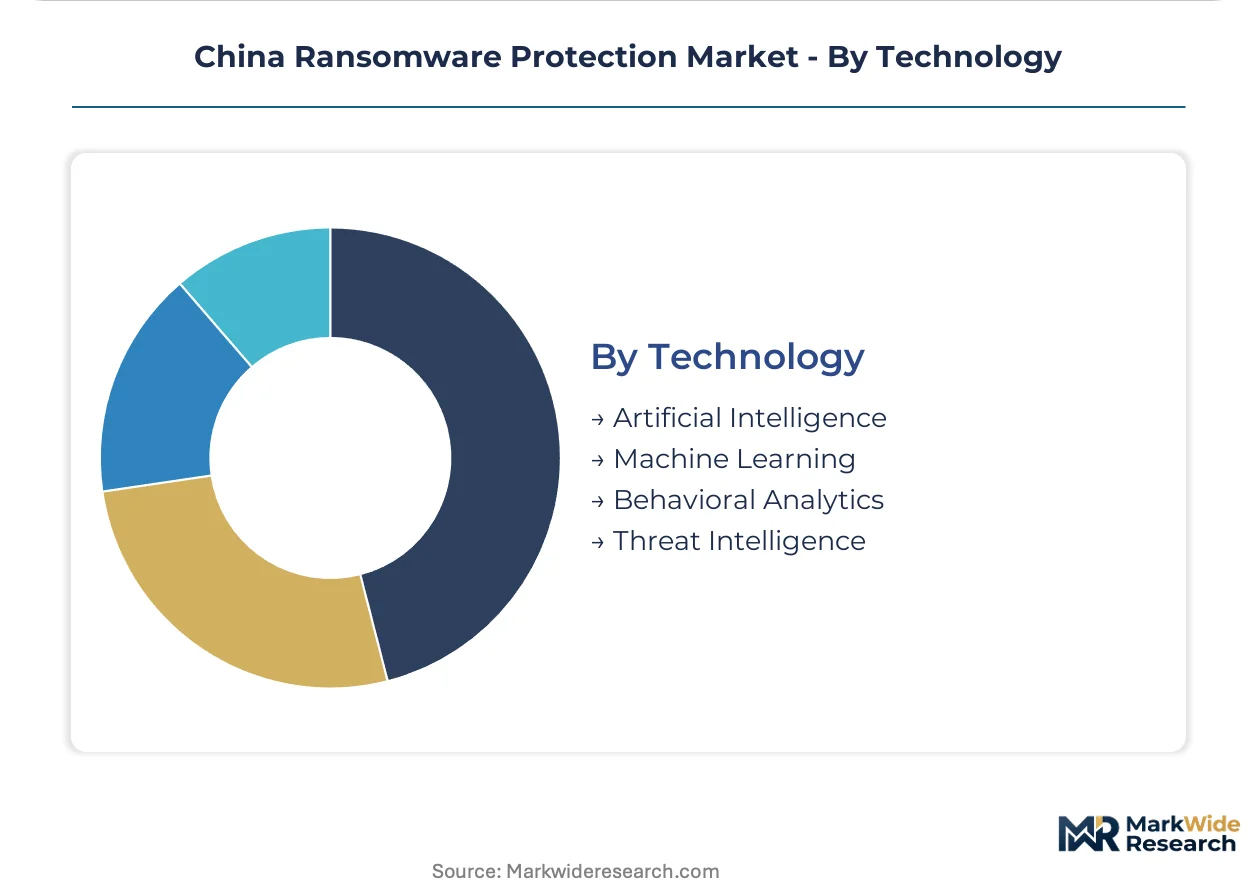
- Behavioral Analytics:Pattern recognition engines identify encryption payloads without signature dependency. CISOs prioritize autonomous containment over detection-only systems.
- Threat Intelligence:Real-time feed integration correlates local telemetry with national attack campaigns. MIIT's incident reporting mandates automate telemetry sharing for designated critical infrastructure.
- Artificial Intelligence:Large language model integration enables natural language query of security events. Shenzhen's fintech cluster validates early architectures.
- Machine Learning:Supervised models refine detection thresholds based on labeled enterprise traffic. Training data scarcity limits provincial deployment outside Beijing and Shanghai.
Behavioral Analytics anchors current procurement, while Threat Intelligence is climbing the fastest as real-time mandates take effect.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Domestic silicon and encryption module suppliers cluster in Shenzhen and Hefei, creating supply bottlenecks that extend deployment timelines for certified hardware. Provincial SOEs in western industrial bases are beginning compliance-driven procurement cycles as MIIT mandates accelerate.
Yangtze River Delta
Shanghai's provincial financial institutions and Jiangsu manufacturing technology clusters drive hybrid infrastructure adoption. SAMR's critical information infrastructure regulations mandate certified domestic encryption for finance sector operators. Nanjing and Hangzhou data centers validate cloud-native ransomware detection architectures.
Pearl River Delta
Shenzhen's fintech cluster leads autonomous response validation for AI-augmented endpoint detection. MIIT's data security governance rules compel real-time incident reporting from designated critical infrastructure. Guangdong manufacturing enterprises show fastest subscription displacement of perpetual licenses.
Beijing-Tianjin-Hebei
State-owned banks in Beijing consolidate cybersecurity budgets around converged security appliances. GB standards for cybersecurity等级保护 shape product certification requirements and restrict foreign vendor access. Tianjin's industrial technology corridors deploy behavioral analytics platforms for mandatory telemetry.
Sichuan-Chongqing
Provincial SOEs in Chengdu and Chongqing industrial bases are beginning multi-level protection compliance programs. Certified component concentration from eastern suppliers creates deployment timeline friction. Local financial institutions face compressed procurement cycles under mandatory incident reporting timelines.
Shandong Peninsula
Qingdao and Jinan manufacturing enterprises adopt immutable backup architectures for core system protection. SAMR regulations designate energy and transportation operators as protected tiers requiring air-gapped recovery points. Regional procurement lags coastal corridors due to SOC personnel scarcity.
China Ransomware Protection Market Competitive Landscape
Platform integrators command the system tier; component specialists sit upstream in encryption modules and silicon. The vendor landscape stratifies between converged appliance providers and point-solution specialists. Three archetypes dominate: integrated infrastructure vendors, endpoint detection platforms, and managed security service operators. Competitive positioning hinges on MIIT security clearance access and certification velocity under evolving GB standards.
Within the integrated infrastructure tier, Huawei leverages silicon-to-software stacks for domestic bid dominance. Qihoo 360 occupies a position bridging consumer brand recognition with enterprise endpoint expansion. Sangfor Technologies exemplifies the converged appliance archetype for mid-market provincial deployments. These three anchors represent distinct competitive vectors: vertical integration breadth, brand-to-enterprise migration capability, and mid-market deployment efficiency.
| Leading Market Players |
|---|
| Alibaba |
| NSFOCUS |
| Qihoo 360 |
| Baidu |
| Venustech |
| Tencent Security |
| Sangfor Technologies |
| EFW |
| Huawei |
| Others |
Pricing and Supply Chain Analysis
Shenzhen's encryption module fabrication clusters anchor domestic supply capacity for certified ransomware protection hardware, concentrating component sourcing power among vendors with MIIT security clearance access. This geographic concentration translates directly into pricing leverage for converged appliance providers serving state-owned bank procurement cycles.
Pricing Analysis
MIIT's multi-level protection scheme dictates the pricing tier structure across China's ransomware protection market. Three-tier pricing structure across premium, standard, and economy levels separates cleared-personnel managed services from self-operated platforms and cloud-native deployments. Certification grade and volume scale drive price differentiation, with provincial SOEs facing compressed margins due to mandatory domestic component sourcing. Cost compression in mid-market tiers is intensifying because certification bottlenecks extend deployment timelines and elevate vendor switching costs.
Supply Chain Analysis
Export-control restrictions on advanced encryption silicon limit technology flows into China's domestic ransomware protection supply chain. Component sourcing draws from Shenzhen, Hefei, and Shanghai fabrication clusters for certified encryption modules and behavioral analytics processors. Raw material dependencies include domestic-grade silicon wafers, cryptographic co-processors, and air-gapped storage substrates. Single-source vulnerability concentrates in cleared-personnel certification pipelines for managed services delivery. Distribution runs through state-owned systems integrators with MIIT security clearance access.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
China's ransomware protection market represents a high-growth disruption as MIIT's data security governance rules mandate real-time incident reporting and automated telemetry across critical information infrastructure.
For Market Incumbents: Harden certification velocity under evolving GB standards to defend procurement positioning against emerging cloud-native entrants. Prioritize backward integration into domestic encryption module supply to mitigate Shenzhen-Hefei component bottlenecks. Expand cleared-personnel training pipelines to capture managed services margin concentration before SOC analyst scarcity worsens. For New Entrants and Emerging Players: Sichuan and Shaanxi industrial bases offer underpenetrated provincial SOE segments beginning multi-level protection compliance programs. Target converged appliance deployments for mid-market financial institutions facing compressed procurement timelines under mandatory incident reporting rules. Partner with regional systems integrators possessing existing MIIT clearance relationships to accelerate market access. For Investors and Strategic Acquirers: Carve-out targets emerge from state-owned technology conglomerates spinning off cybersecurity divisions to meet SAMR's critical information infrastructure mandates. Long-term viability hinges on certification maintenance velocity and cleared-personnel access depth. Monitor MIIT security clearance approval timelines as the primary inflection signal for managed services scalability.| Strategic Initiative | Industry Significance |
|---|---|
| Certification Velocity Investment | Accelerated GB standard recertification prevents procurement disqualification under MIIT's evolving mandates. |
| Cleared-Personnel Pipeline Expansion | MIIT security clearance access enables premium positioning in managed detection and response services. |
| Converged Appliance Development | Unified platforms displace point solutions among provincial banks consolidating cybersecurity budgets. |
| Western Province Partnership | Sichuan and Shaanxi SOE relationships capture compliance-driven procurement before coastal saturation. |
| AI-Augmented Response Integration | Large language model deployment validates autonomous containment architectures in Shenzhen's fintech cluster. |
Research Methodology
Initial hypotheses were tested against primary input from CISOs at state-owned banks, MIIT compliance officers, provincial systems integrators, and endpoint platform engineers and refined through secondary validation. Primary fieldwork combined structured interviews with cybersecurity procurement leads at financial institutions and technology vendors with documentary analysis of GB standard filings, SAMR regulatory releases, and MIIT policy circulars. Bottom-up deployment forecasts triangulated against top-down infrastructure spending projections from eastern seaboard technology corridors.
Demand-supply balance modeling anchored the analytical framework across the analysis window. Segmentation dimensions included product type, deployment model, end-user vertical, and regional adoption pattern reflecting infrastructure maturity gradients between coastal and western provinces. CAGRs derived from deployment velocity curves calibrated against regulatory mandate implementation timelines. Forecast inputs incorporated MIIT multi-level protection scheme upgrade schedules and provincial SOE modernization budget cycles.
Practitioners should monitor GB standard revision cadence and MIIT clearance approval backlogs for early signals of forecast deviation. Forecasts reflect assumptions about regulatory enforcement consistency and domestic component supply stability. Material shifts in export-control regime stringency or state-owned bank consolidation patterns would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
SD-WAN Security Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Global Managed Detection and Response (MDR) Market
Cybersecurity
Digital Security Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Cybersecurity in Gaming Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Anti-Malware Market
Cybersecurity
Server Security Market
Cybersecurity
Global Ddos Protection Market
Cybersecurity
Europe Cloud DLP Market
Cybersecurity
Global Network Forensics Market
Cybersecurity
Data Security Market