
 Advanced Malware Detection (AMD) Market | 2026-2036
Advanced Malware Detection (AMD) Market Size, Share, and Industry Trends Forecast 2026-2036
Advanced Malware Detection (AMD) Market Outlook
Israel is reshaping competitive dynamics in advanced malware detection through sustained investment in military-derived cybersecurity R&D and active government-backed venture programs. CrowdStrike leverages cloud-native architecture to dominate endpoint protection across North American enterprise accounts. Palo Alto Networks anchors its position through in-house production of inline threat-prevention hardware. Fortinet controls mid-market expansion with integrated firewall-detection bundles that reduce procurement complexity.
Advanced malware detection encompasses systems that identify, analyze, and neutralize malicious software through multi-layered inspection of code behavior, network traffic anomalies, and file execution patterns in isolated sandbox environments. These platforms typically process payloads at throughput rates exceeding 10 Gbps while maintaining sub-millisecond latency for real-time blocking decisions, serving critical infrastructure and data-intensive industries where breach containment windows have compressed to minutes. Cloud-based deployment now captures the fastest expansion trajectory as organizations abandon capital-intensive appliance refresh cycles for elastic consumption models. Behavior-based technology leads innovation investment, displacing signature-dependent approaches that fail against polymorphic and zero-day threats. Large enterprises represent the deepest margin pool, though government agencies are emerging as high-loyalty accounts with multi-year procurement frameworks.
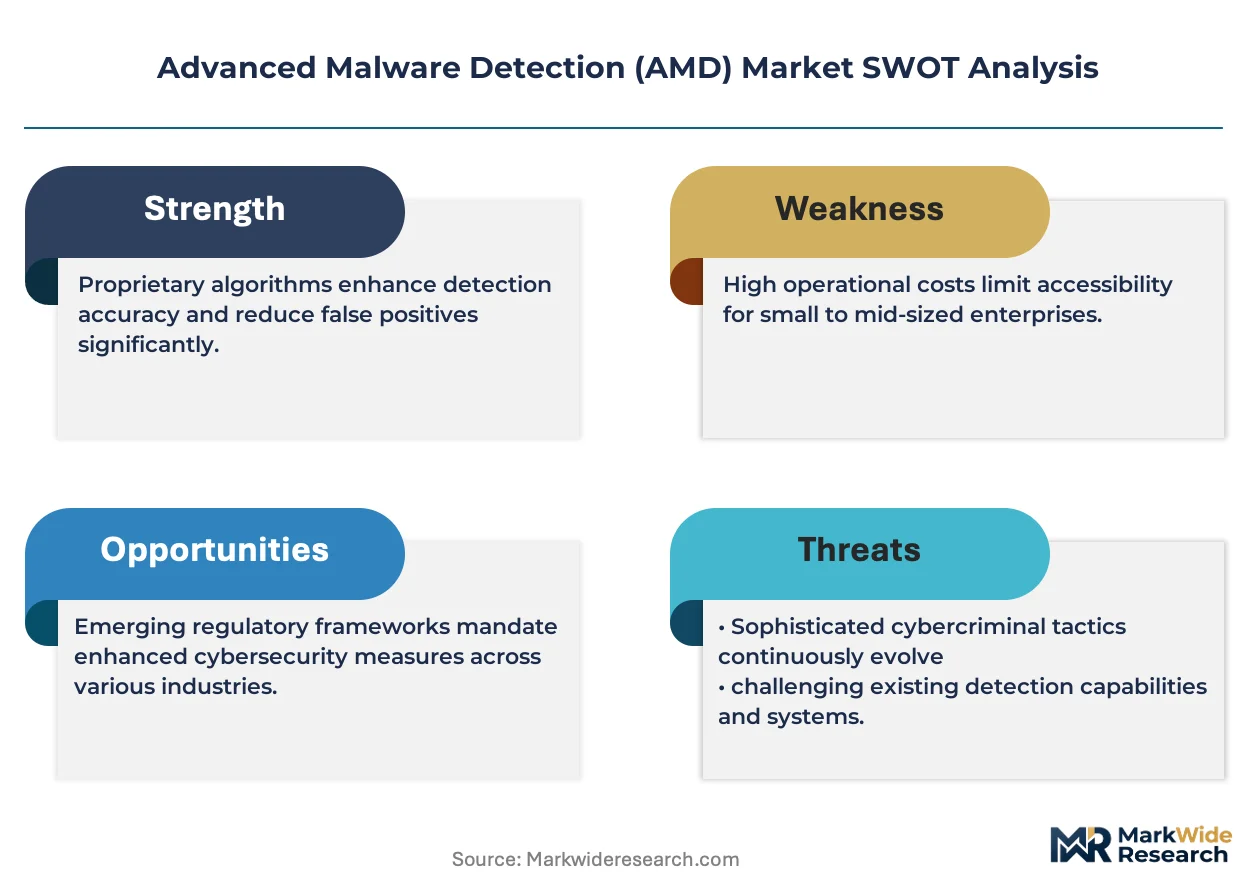
The U.S. SEC enforces disclosure mandates for material cybersecurity incidents, compelling publicly traded firms to invest in auditable detection infrastructure. The EU NIS2 Directive expands incident-reporting obligations to critical sectors including energy, transport, and digital infrastructure, directly stimulating procurement across member states. ISO 27001 certification requirements now explicitly reference automated threat-detection capabilities as a control objective. Stakeholders must weigh build-versus-buy decisions for AI-powered detection engines as regulatory pressure intensifies and adversarial AI renders static defenses obsolete.
Market Dynamics
Behavior-based detection architectures are compressing containment windows from hours to minutes, forcing infrastructure operators to abandon signature-dependent systems that cannot track polymorphic threats. This technological inflection is redistributing procurement budgets toward cloud-native platforms with sub-millisecond response latency.
Growth Catalysts
- EU NIS2 Directive:Mandatory incident-reporting obligations across energy, transport, and digital infrastructure sectors are compelling critical operators to deploy automated detection infrastructure with auditable response capabilities.
- Financial services:Banks and payment processors are accelerating replacement of static antivirus layers with sandboxed behavioral analysis to meet SEC disclosure mandates for material cybersecurity events.
- Industrial control systems:German manufacturing clusters are driving fastest regional spending as operational technology networks converge with IT infrastructure, expanding attack surfaces requiring real-time payload inspection.
Market Restraints
- Specialized talent scarcity:Shortage of malware reverse engineers and threat-hunting analysts with adversarial AI expertise is inflating personnel costs and extending deployment timelines.
- Compute intensity:Deep packet inspection and sandbox emulation at 10+ Gbps throughput demands specialized hardware accelerators, elevating total cost of ownership versus software-only alternatives.
- Alert fatigue:High false-positive rates from behavioral heuristics strain security operations centers, causing analyst burnout and delayed response to genuine intrusions.
Strategic Opportunities
- Managed detection services:Mid-market enterprises lacking in-house security operations are adopting outsourced threat-hunting subscriptions, opening recurring revenue streams for platform vendors.
- Edge convergence:Integration of malware detection with 5G network slicing and IoT gateways creates new deployment points for lightweight behavioral agents in distributed environments.
- EU AI Act compliance:Automated threat-response systems classified as high-risk AI will require conformity assessments, positioning certified vendors for preferred procurement status in member states.
Industry Challenges
- Adversarial ML sophistication:Attackers are weaponizing generative models to craft polymorphic payloads that evade trained classifiers, forcing continuous retraining cycles and model drift management.
- Legacy system integration:Air-gapped industrial environments running decades-old operating systems cannot host modern endpoint agents, requiring network-tap architectures that increase complexity.
- Cross-border data residency:Sandboxed file analysis in cloud platforms conflicts with data-sovereignty requirements in regulated jurisdictions, fragmenting deployment architectures.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Advanced Malware Detection (AMD) Market |
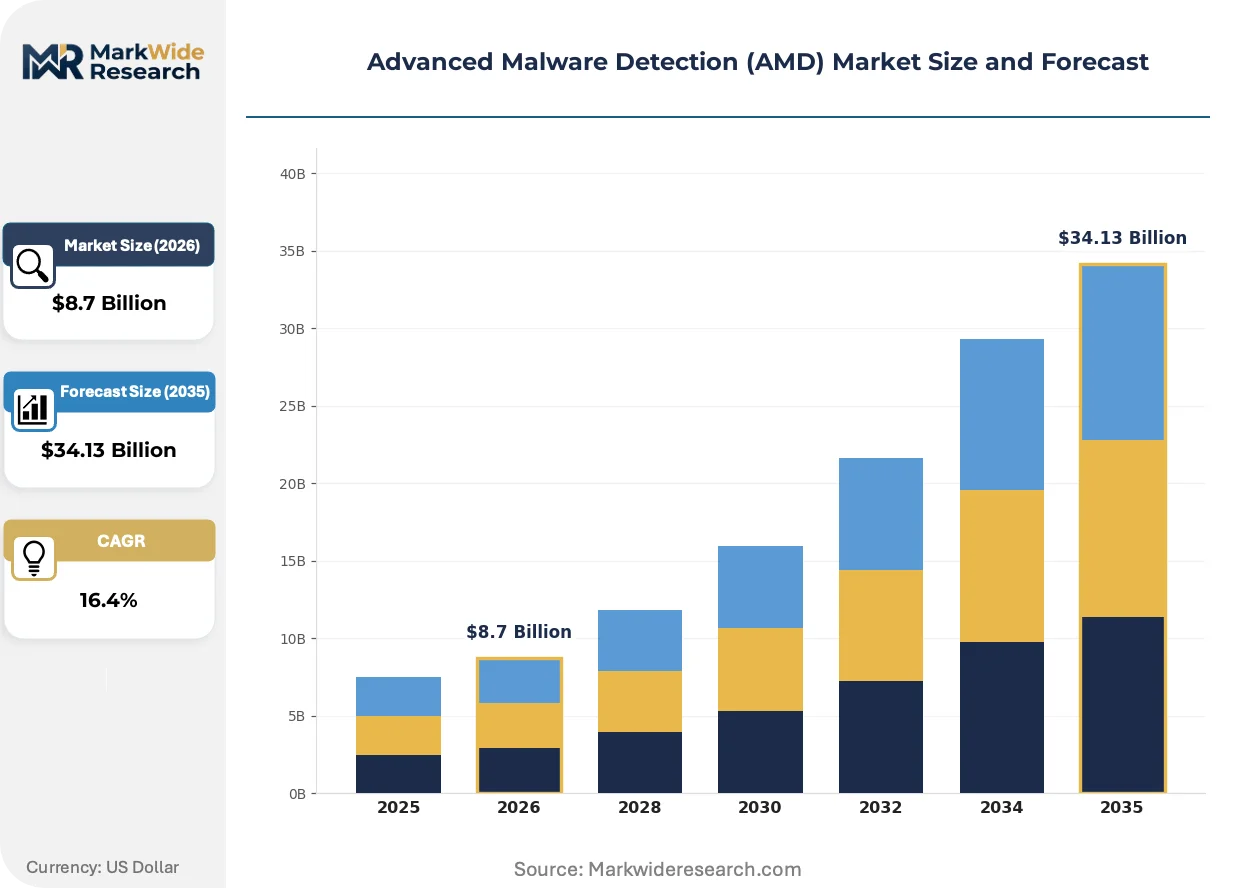
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $34.13 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Service Technology: Signature-Based, Behavior-Based, Heuristic Analysis, Sandbox Analysis End User: Small Enterprises, Medium Enterprises, Large Enterprises, Government Agencies Application: Banking, Retail, Healthcare, IT Services |
| Companies Covered | Fortinet, IBM Security, CrowdStrike, Trend Micro, Check Point, Palo Alto Networks, Microsoft Security, McAfee, SentinelOne, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Advanced Malware Detection (AMD) Market Strategic Shifts
Automated threat neutralization is displacing human-in-the-loop response models as machine-speed attacks outpace analyst reaction times. Three developments are compressing the innovation cycle and redrawing competitive boundaries.
Memory-safe runtime protection using hardware-assisted isolation is rendering obsolete traditional signature-scanning engines that require prior threat intelligence. Critical infrastructure operators in energy and water utilities are piloting these architectures at scale, eliminating the exposure window between zero-day emergence and signature distribution. The structural consequence is collapsing R&D investment into static detection databases.
The EU AI Act's risk-classification framework for automated decision systems is forcing security vendors to document training-data provenance and model explainability. Industrial cybersecurity procurement in Germany and France now favors platforms with third-party conformity assessments, compressing vendor qualification timelines. Energy sector buyers are delaying commitments until certification pathways clarify, creating temporary demand pauses.
Consumption-based licensing for detection capacity is displacing perpetual appliance purchases across North American enterprise accounts. Financial services and healthcare providers are consolidating vendor relationships around elastic platforms that scale with transaction volumes rather than fixed infrastructure. This pattern is most pronounced in cloud-first organizations undergoing datacenter consolidation, where capital avoidance outweighs long-term operational expenditure considerations.
Advanced Malware Detection (AMD) Market Segmentation
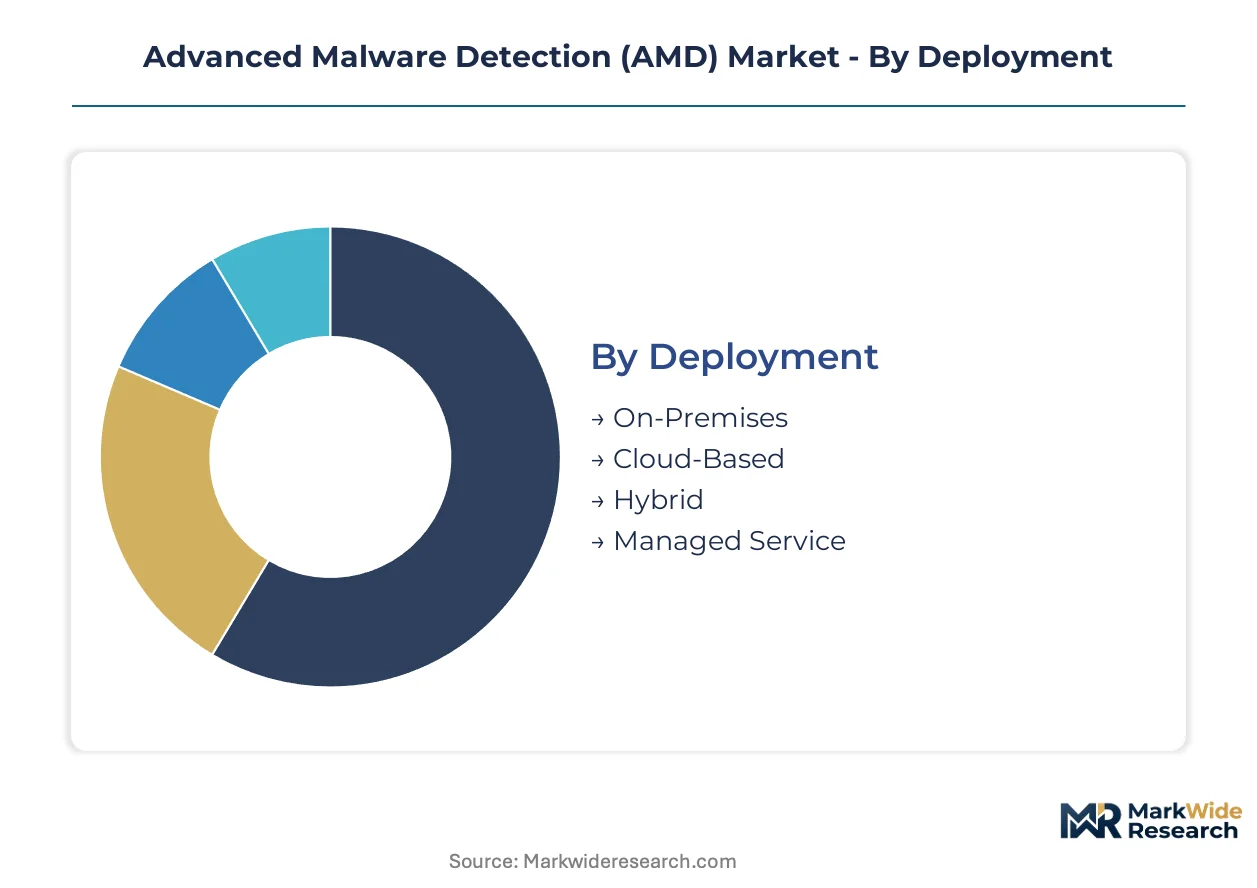
Deployment architecture, detection methodology, and customer scale define procurement patterns in advanced malware detection. Each segmentation axis reveals distinct margin structures and technology requirements that shape vendor positioning.
Deployment:
Organizations select deployment models based on data sovereignty constraints, capital availability, and internal security operations maturity.
- Cloud-Based:Elastic consumption models eliminate appliance refresh cycles and scale detection capacity with transaction volumes. Financial services firms in the United States and healthcare providers undergoing datacenter consolidation are abandoning perpetual licenses for metered throughput pricing.
- Managed Service:Outsourced threat-hunting subscriptions address talent scarcity in mid-market enterprises lacking dedicated security operations centers. German industrial clusters and North American municipal governments are adopting these arrangements to compress response latency without building internal teams.
- On-Premises:Air-gapped environments in critical infrastructure and classified government networks require hardware appliances with localized sandboxing.
- Hybrid:Split architectures route high-volume traffic to cloud inspection while retaining sensitive payload analysis on-site.
Established volume favors On-Premises; emerging adoption favors Cloud-Based.
Technology:
Detection methodology determines efficacy against polymorphic threats and computational infrastructure requirements.
- Behavior-Based:Dynamic analysis of code execution patterns in isolated sandbox environments identifies zero-day threats without prior signatures. Energy utilities and water treatment facilities are piloting hardware-assisted runtime isolation that eliminates exposure windows between threat emergence and signature distribution.
- Sandbox Analysis:Deep payload emulation at throughput rates exceeding 10 Gbps enables real-time blocking decisions for high-frequency trading platforms and payment processors. ISO 27001 certification requirements now explicitly reference these capabilities as control objectives.
- Signature-Based:Static pattern matching against threat intelligence databases remains cost-effective for commodity malware families.
- Heuristic Analysis:Rule-based anomaly detection supplements behavioral layers with lower computational overhead.
Behavior-Based platforms are gaining share fastest as signature-dependent systems fail against adversarial AI.
End User:
Customer scale dictates pricing architecture, support intensity, and compliance complexity.
- Large Enterprises:Multi-year procurement frameworks with dedicated threat-hunting teams and custom integration requirements. These accounts generate the deepest margin pools and demand sub-millisecond response latency for distributed global operations.
- Government Agencies:High-loyalty accounts with classified security requirements and sovereign data residency mandates. EU member states are expanding procurement under NIS2 Directive obligations for automated incident reporting.
- Medium Enterprises:Consolidated vendor relationships favoring integrated firewall-detection bundles that reduce procurement complexity.
- Small Enterprises:Price-sensitive segment relying on managed services or bundled endpoint protection.
Large Enterprises dominate current revenue; Government Agencies are climbing the fastest under regulatory compulsion.
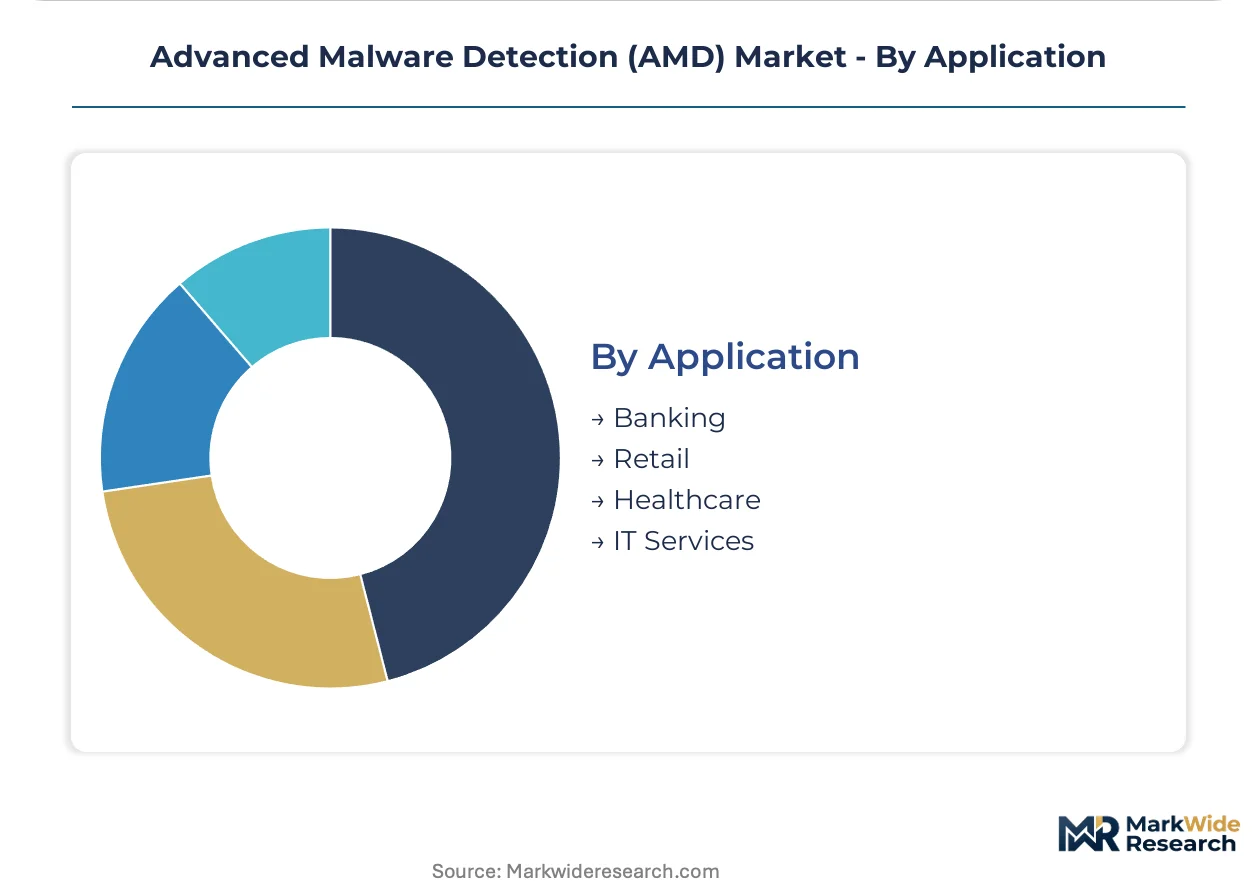
Application:
Industry-specific breach containment windows and regulatory exposure shape technology selection.
- Banking:SEC disclosure mandates for material cybersecurity incidents compel investment in auditable detection infrastructure with documented response timelines. Sandboxed behavioral analysis is displacing static antivirus layers across payment processors and investment banks.
- Healthcare:HIPAA requirements and patient data sensitivity drive demand for encrypted payload inspection with audit trails. Cloud deployment faces friction from data residency requirements in regulated jurisdictions.
- IT Services:Managed security providers aggregate detection capacity across client portfolios, favoring elastic licensing models.
- Retail:Point-of-sale protection and e-commerce transaction security prioritize throughput over deep inspection depth.
Banking commands premium pricing; Healthcare represents the steepest expansion trajectory as breach costs escalate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Frankfurt-Cologne rail corridor and Rhine River industrial belt anchor Germany's concentration of operational technology security investment, while the Los Angeles-Long Beach port complex and Texas power grid interconnect define North American critical infrastructure exposure. Japan's Tokyo-Osaka Shinkansen corridor and South Korea's Seoul-Busan logistics spine concentrate East Asian financial and manufacturing demand. The UAE's Jebel Ali port and Saudi Arabia's Red Sea pipeline network shape Middle Eastern procurement patterns around energy sector protection.
United States
Financial services firms along Manhattan's fintech corridor and defense contractors clustered around Washington D.C. and Northern Virginia drive premium-tier demand for sub-millisecond detection latency. The SEC enforces disclosure mandates for material cybersecurity incidents, compelling publicly traded firms to invest in auditable detection infrastructure. California's Silicon Valley and Seattle's cloud computing hub concentrate enterprise adoption of elastic, consumption-based licensing models.
Germany
Industrial manufacturing clusters in Bavaria and Baden-Württemberg are accelerating replacement of air-gapped operational technology networks with converged IT-OT infrastructure requiring real-time payload inspection. The EU NIS2 Directive expands incident-reporting obligations to energy, transport, and digital infrastructure sectors, directly stimulating procurement across federal states. The Ruhr industrial region and Hamburg port authority are piloting hardware-assisted runtime isolation for water treatment and logistics systems.
Japan
Tokyo's financial district and Osaka's manufacturing belt prioritize sandboxed behavioral analysis for high-frequency trading platforms and automotive supply chain protection. METI guidelines emphasize supply chain cybersecurity for critical industries, aligning procurement with international certification standards. The Nagoya industrial corridor and Fukuoka semiconductor clusters are deploying managed detection services to address talent scarcity in threat-hunting operations.
United Kingdom
London's investment banking center and Edinburgh's fintech hub demand documented response timelines for regulatory compliance with overlapping EU and domestic frameworks. The Financial Conduct Authority maintains stringent operational resilience requirements for payment systems and trading infrastructure. Manchester's media and technology corridor and Cambridge's cybersecurity research cluster are emerging as secondary demand centers for cloud-native detection platforms.
Israel
Military-derived cybersecurity R&D concentrated in Tel Aviv and Haifa feeds commercial spin-offs specializing in adversarial AI countermeasures and behavioral detection engines. Government-backed venture programs sustain early-stage innovation in autonomous threat-response systems. The Beersheba CyberSpark complex and Jerusalem technology corridor are integrating domestic capabilities into export-oriented platform development for European and North American markets.
Advanced Malware Detection (AMD) Market Competitive Environment
Platform integrators command the system tier; component specialists sit upstream supplying detection engines and sandbox emulation modules to larger vendors. The vendor base stratifies across three functional layers: cloud-native endpoint protection platforms, inline threat-prevention hardware manufacturers, and managed security service providers. Consolidation pressure intensifies as customers demand unified consoles spanning network, endpoint, and cloud workloads. Dominant competitive moves include strategic partnerships between firewall vendors and behavioral analysis engine providers, plus geographic expansion through regional system integrator channels.
Within the cloud-native platform tier, CrowdStrike and SentinelOne exemplify architecture-first positioning built on elastic consumption models. Palo Alto Networks anchors the inline hardware segment through in-house production of threat-prevention appliances. Fortinet occupies a position in the mid-market expansion vector with integrated bundles that reduce procurement complexity for resource-constrained security operations.
| Leading Market Players |
|---|
| Fortinet |
| IBM Security |
| CrowdStrike |
| Trend Micro |
| Check Point |
| Palo Alto Networks |
| Microsoft Security |
| McAfee |
| SentinelOne |
| Others |
Value Chain & Pricing Dynamics
Regulatory chokepoint exposure through the EU AI Act's high-risk system classification determines both tier spreads in detection platform pricing and supply chain regionalization strategies for sandbox hardware components.
Pricing Analysis
Volume-discount tiering structures dominate procurement, with three-tier pricing separating enterprise-grade behavioral engines with sub-millisecond latency guarantees from mid-market integrated bundles and economy-tier signature-based alternatives. Price differentiation rests on certification level under ISO 27001 and EU AI Act conformity assessment status, plus throughput capacity scaling. Pricing pressure stems from cloud-native consumption models displacing perpetual appliance licenses, compressing upfront revenue recognition. Small enterprises exhibit highest price sensitivity, while government agencies with multi-year frameworks demonstrate lowest elasticity.
Supply Chain Analysis
Supplier-financing arrangements through extended payment terms are becoming standard for specialized hardware accelerators and FPGA-based deep packet inspection components. Component manufacturing concentrates in Taiwan, the United States, and Israel, with sandbox emulation modules drawing from Israeli military-derived R&D clusters and Taiwanese semiconductor fabrication. Supply chain risk centers on single-source vulnerability for hardware-assisted runtime isolation chipsets. Distribution runs through regional system integrators serving critical infrastructure operators, with direct vendor relationships reserved for tier-one financial services and government accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Capital expenditure cycles in financial services and energy infrastructure are driving a cyclical recovery as post-pandemic compliance deadlines compress procurement timelines.
For Market Incumbents: Pre-empt adversarial AI disruption by accelerating in-house behavioral engine development and securing exclusive distribution partnerships with German industrial system integrators. Vertical integration into hardware-assisted runtime isolation chipsets defends margin position against cloud-native entrants. Certification investment under EU AI Act conformity assessment pathways locks in preferred procurement status. For New Entrants and Emerging Players: Establish a beachhead in managed detection services for mid-market healthcare providers lacking internal security operations centers. White-space targets include municipal government networks in North American secondary metros and Japanese manufacturing supply chain protection. Go-to-market execution should emphasize consumption-based licensing with rapid deployment guarantees. For Investors and Strategic Acquirers: The EU AI Act's high-risk system classification reshapes the acquisition landscape toward vendors with documented training-data provenance and third-party conformity assessments. Long-term viability favors platforms with elastic cloud architectures and recurring revenue concentration. Acquisition target archetypes include Israeli behavioral engine specialists and German OT-security integrators. The signal to watch is NIS2 Directive procurement acceleration across energy and transport sectors.| Strategic Initiative | Industry Significance |
|---|---|
| EU AI Act Certification Investment | Third-party conformity assessments unlock preferred procurement status in German and French industrial cybersecurity tenders. |
| Cloud-Native Platform Migration | Elastic consumption models displace perpetual licenses across North American financial services consolidation waves. |
| Hardware-Assisted Runtime Isolation | FPGA-based deep packet inspection eliminates exposure windows for energy utility zero-day containment. |
| Managed Detection Service Expansion | Outsourced threat-hunting subscriptions address talent scarcity in Japanese automotive supply chain security. |
| OT-IT Convergence Integration | Converged infrastructure protection captures fastest-growing German manufacturing cybersecurity spending. |
Study Parameters
Two parallel data streams informed the analysis: structured primary interviews with CISOs, SOC directors, threat-hunting analysts, and industrial control system engineers; and secondary validation against SEC cybersecurity disclosure filings, EU NIS2 Directive implementation guidance, ISO 27001 certification databases, and hyperscaler security capex disclosures. Bottom-up triangulation across deployment architecture adoption curves and top-down reconciliation against regulatory compliance spending estimates anchored volume projections.
Forecast inputs considered deployment model migration patterns, detection methodology substitution rates, and end-user compliance urgency across the analysis window. Segmentation dimensions modeled include cloud-native versus on-premises architecture, behavior-based versus signature-dependent technology, and enterprise scale tiering. CAGRs were derived from elasticity-adjusted adoption curves and regulatory deadline clustering. Industry-specific inputs encompassed adversarial AI development velocity and hardware accelerator cost decline trajectories.
Stress conditions across EU AI Act implementation delays, semiconductor supply disruption, and adversarial ML sophistication acceleration were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions about compliance deadline adherence and cloud migration pace. Macroeconomic contraction, regulatory scope expansion, or breakthrough quantum-resistant encryption would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
Network Detection and Response Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Operational Technology Security Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Application-Level Encryption Market