
 Cybersecurity in Gaming Market | 2026-2036
Cybersecurity in Gaming Market Size, Share, and Industry Trends Forecast 2026-2036
Cybersecurity in Gaming Market Insights
ISO 27001 certification is rotating as the primary qualification gating vendor selection among AAA game publishers and platform holders. Fortinet, Inc. leverages its integrated security fabric to anchor enterprise-grade deployments across multiplayer backend infrastructure. Palo Alto Networks, Inc. competes through specialized threat intelligence for real-time cheat detection and anti-tamper systems. Kaspersky Lab sustains its position in Eastern European and Asian markets through localized gaming-focused malware research.
Cybersecurity in gaming encompasses the protection of game software, player data, live service infrastructure, and financial transaction systems from unauthorized access, exploitation, or disruption through layered defensive architectures including encryption protocols, behavioral analytics, and runtime application self-protection. The discipline serves to preserve revenue continuity, player trust, and competitive integrity across an industry where single breaches can terminate live service economies. DDoS mitigation and anti-cheat systems dominate current spending as threat volume escalates against tournament broadcasts and ranked multiplayer servers. Cloud-based deployment represents the fastest-expanding segment as hybrid architectures allow studios to distribute security workloads across edge nodes and centralized data centers. Managed services capture disproportionate margin pools by bundling 24/7 security operations center oversight with incident response retainers.
FCC oversight of broadband infrastructure resilience intersects with state-level data privacy statutes to shape how gaming firms architect cross-border player data flows. PCI DSS compliance mandates directly constrain how publishers design in-game purchase systems and virtual currency wallets. GDPR extraterritorial reach forces even non-European studios to implement data localization and erasure capabilities for EU players. Stakeholders must monitor the divergence between regional breach notification timelines and emerging AI-generated social engineering tactics to calibrate defensive investment priorities.
Market Dynamics
Live service monetization architectures are forcing studios to reclassify cybersecurity from cost center to revenue protection infrastructure, with real-time transaction integrity now treated as critical path for virtual economy stability.
Growth Catalysts
- GDPR extraterritorial enforcement:EU data localization mandates compel non-European publishers to deploy regional security infrastructure, expanding addressable market for compliance-native vendors.
- Esports tournament integrity requirements:Prize pools exceeding eight figures drive anti-cheat and broadcast protection spending across competitive gaming circuits.
- Cloud edge node proliferation:Distributed compute architectures multiply attack surface area, generating recurring demand for hybrid security orchestration platforms.
Market Restraints
- Specialized talent scarcity:Shortage of professionals combining game engine expertise with threat intelligence analysis inflates security operations center staffing costs.
- California-Washington supplier concentration:Publisher and cloud provider clustering in two US states creates geographic single-point-of-failure risk for vendor revenue concentration.
- Legacy console certification friction:Platform holder security review timelines delay patch deployment for zero-day vulnerabilities in cross-platform titles.
Strategic Opportunities
- Southeast Asia mobile gaming expansion:Underpenetrated markets with high smartphone penetration present greenfield demand for lightweight anti-cheat SDKs.
- AI-generated content moderation:Convergence of large language models with behavioral analytics enables real-time toxicity detection at scale.
- India's data protection bill implementation:Emerging localization requirements create first-mover advantage for domestic security operations center partnerships.
Industry Challenges
- ISO 27001 certification timeline compression:Publisher vendor qualification cycles now demand six-month evidence windows that strain documentation capacity.
- Cross-platform engine fragmentation:Proprietary anti-cheat implementations for console, PC, and mobile codebases multiply integration testing overhead.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cybersecurity in Gaming Market |
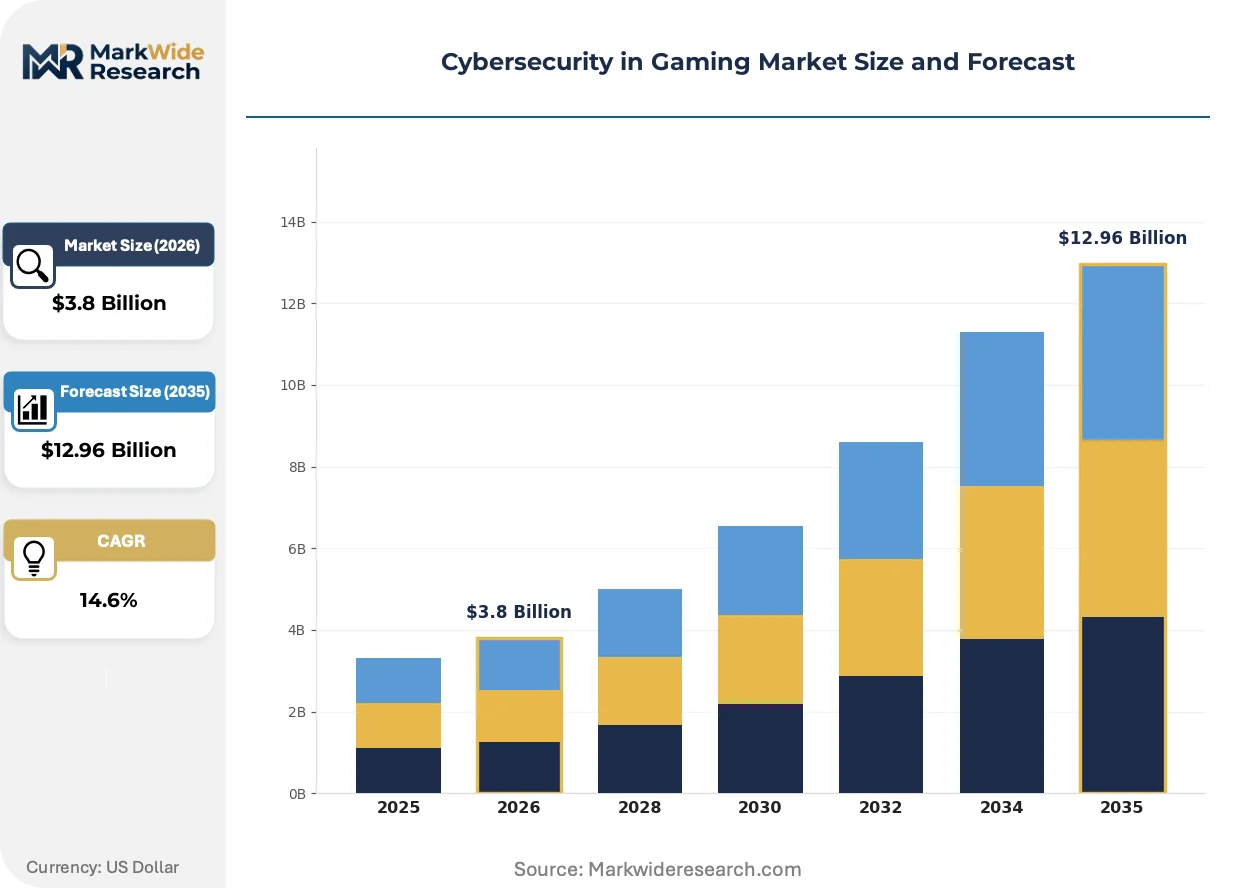
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $12.96 Billion |
| CAGR (2026 – 2036) | 14.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Threat Type: Malware, Phishing, DDoS, Ransomware Deployment Model: On-premises, Cloud-based, Hybrid, Managed Services End User: Game Developers, Publishers, Esports Organizations, Players Compliance Standard: GDPR, PCI DSS, ISO 27001, HIPAA |
| Companies Covered | Fortinet, Inc., McAfee LLC, Trend Micro Incorporated, Symantec Corporation, Cisco Systems, Cloudflare, Inc., Akamai Technologies, Inc., Kaspersky Lab, Palo Alto Networks, Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cybersecurity in Gaming Market Trends and Innovations
Runtime application self-protection is migrating from experimental deployment to standard architecture, with behavioral heuristics replacing signature-based detection as the dominant defensive paradigm across multiplayer backends.
Behavioral biometrics for player authentication is bifurcating the identity verification market. Mid-tier studios are adopting keystroke dynamics and mouse movement patterning as drop-in SDK replacements for hardware-backed two-factor systems. The technology is bifurcating vendor tiers between premium hardware security module integrators and lightweight software-only alternatives.
EU AI Act risk classification rules are reshaping how publishers deploy automated moderation systems. High-risk categorization for real-time player behavior analysis triggers conformity assessment obligations that delay deployment timelines. French CNIL guidance on automated decision-making is prompting studios to implement human-in-the-loop override architectures for ban appeals.
Security procurement through managed detection and response retainers is displacing perpetual license models among independent studios. Monthly subscription structures align vendor incentives with continuous threat coverage rather than upfront tool deployment. This shift concentrates most visibly in the Nordic indie development cluster, where capital efficiency priorities favor operational expenditure treatment of security spend.
Cybersecurity in Gaming Market Segmentation
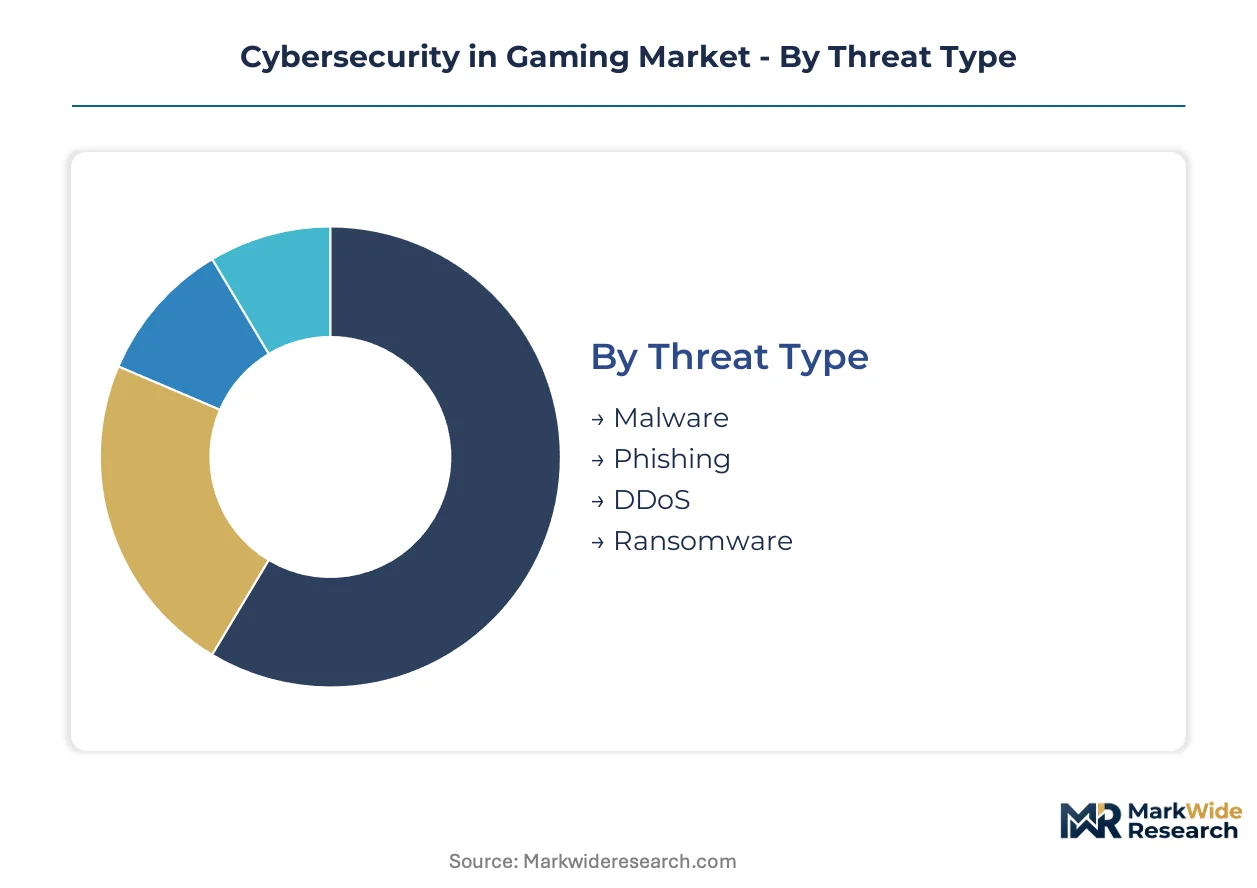
Gaming cybersecurity vendors face divergent technical requirements across threat vectors, infrastructure architectures, and stakeholder risk profiles. Segment-level substitution pressures intensify as studios consolidate vendor relationships and platform holders mandate unified compliance frameworks.
Threat Type:
Signature-based detection tools face acute substitution pressure from behavioral analytics and runtime self-protection platforms, compressing legacy endpoint security margins.
- Malware:File-based threats targeting game executables and modding tools demand continuous signature updates and sandbox analysis. Demand clusters among PC game publishers distributing through third-party storefronts, constrained by platform holder certification delays that extend vulnerability windows.
- DDoS:Volume-based and protocol attacks against matchmaking servers and tournament broadcasts require always-on mitigation with sub-second response. Esports organizations in the United States drive premium spending as prize pool integrity becomes non-negotiable.
- Phishing:Credential harvesting via fake login portals and social engineering against support staff. Mobile-first studios in Southeast Asia prioritize lightweight SDK integration over enterprise-grade email gateways.
- Ransomware:Encryption attacks against source code repositories and live service databases. Mid-tier developers with limited backup infrastructure represent concentrated vulnerability.
DDoS retains volume leadership; ransomware holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates capital-constrained indie studios from AAA publishers with dedicated security operations centers.
- Cloud-based:Distributed security workloads across edge nodes and centralized data centers enable elastic scaling during launch windows and live events. Studios migrating from on-premises server farms in California and Washington state prioritize API-native orchestration platforms.
- Managed Services:Bundled 24/7 security operations center oversight with incident response retainers transfers operational burden to specialized providers. Nordic indie developers favor subscription structures that align vendor incentives with continuous threat coverage.
- Hybrid:Split architectures preserving sensitive matchmaking logic on-premises while offloading DDoS mitigation to cloud scrubbing centers. Cross-platform publishers navigating console certification friction adopt this model to maintain patch autonomy.
- On-premises:Dedicated hardware appliances for latency-sensitive anti-cheat verification and hardware security module key management. Esports tournament operators with broadcast integrity mandates sustain residual demand.
Cloud-based deployments command the largest addressable base; managed services are climbing the fastest as procurement shifts from perpetual licenses.
End User:
Application complexity varies sharply across the value chain, with upstream infrastructure protection commanding technical sophistication downstream consumer tools cannot match.
- Game Developers:Source code protection, build pipeline integrity, and pre-release leak prevention. Independent studios with limited security headcount drive demand for integrated development environment plugins and automated vulnerability scanning.
- Publishers:Multi-title security governance, vendor qualification, and cross-platform compliance coordination. GDPR extraterritorial enforcement compels regional infrastructure deployment for EU player data.
- Esports Organizations:Tournament integrity systems, broadcast protection, and player device hardening. Prize pools exceeding eight figures justify dedicated anti-cheat operations centers.
- Players:Account takeover prevention, credential stuffing detection, and client-side anti-cheat agents. Keystroke dynamics and mouse movement patterning emerge as lightweight alternatives to hardware-backed two-factor systems.
Publishers retain volume leadership; esports organizations post the steepest budget expansion as competitive integrity spending accelerates.
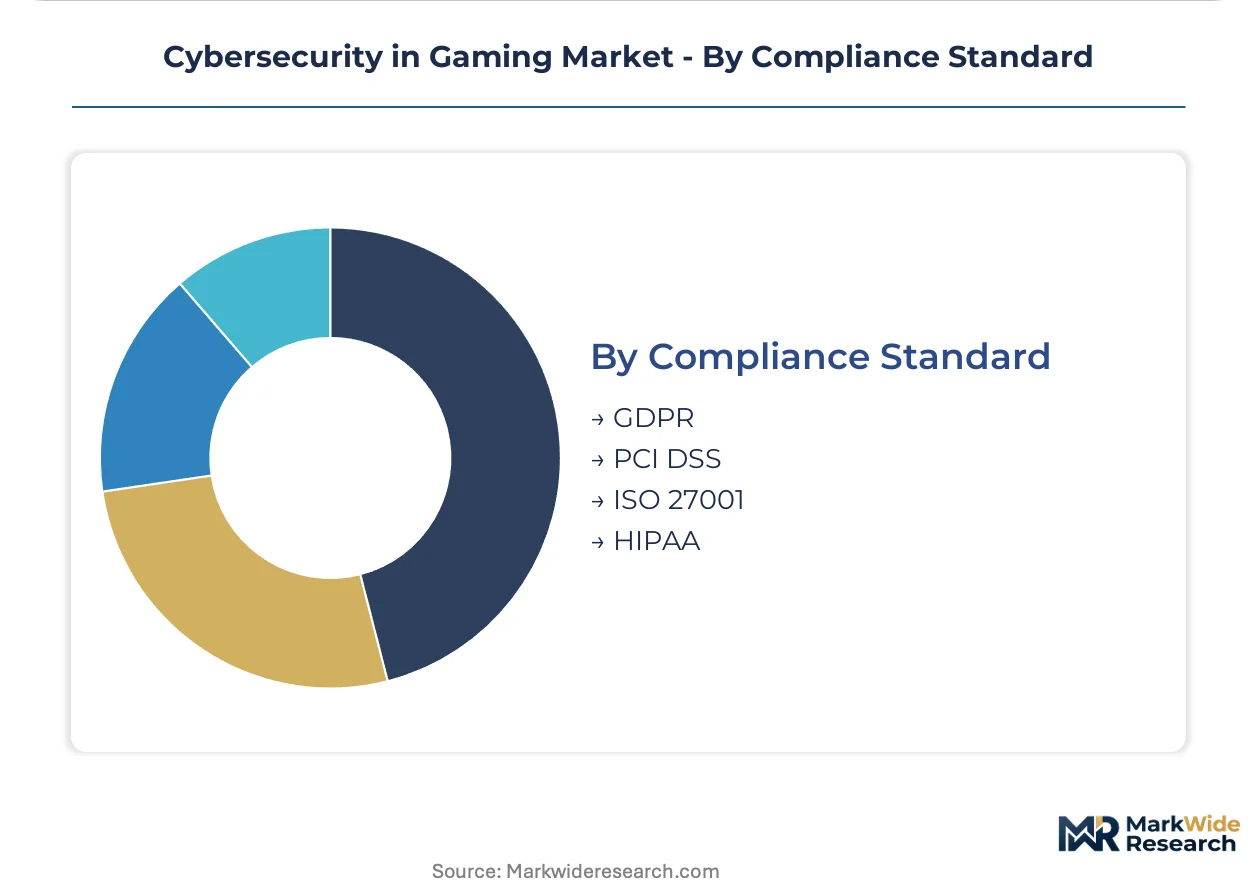
Compliance Standard:
Maturity differentiation separates baseline regulatory adherence from premium certification that gates vendor selection at major platform holders.
- ISO 27001:Information security management system certification now rotates as primary qualification gating vendor selection among AAA game publishers. Six-month evidence windows strain documentation capacity for mid-tier security vendors.
- GDPR:EU data localization and erasure capabilities force even non-European studios to implement regional infrastructure. French CNIL guidance on automated decision-making prompts human-in-the-loop override architectures for ban appeals.
- PCI DSS:Payment card industry standards directly constrain in-game purchase system design and virtual currency wallet architecture. Compliance mandates shape backend infrastructure decisions for free-to-play monetization.
- HIPAA:Health information protection applies narrowly to fitness gaming applications and medical rehabilitation platforms with biometric data collection. Specialized vertical with limited crossover to mainstream gaming security.
ISO 27001 retains vendor selection dominance; GDPR drives the steepest infrastructure investment as extraterritorial enforcement expands.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The submarine cable landing stations at Hillsboro, Oregon and Los Angeles anchor trans-Pacific data flows that underpin gaming infrastructure investment patterns across major economies.
United States
Publisher concentration in California and Washington state drives demand for enterprise-grade DDoS mitigation and real-time cheat detection systems. FCC oversight of broadband resilience intersects with CCPA enforcement to shape cross-border player data architecture. The San Francisco Bay Area and Seattle metropolitan clusters host the majority of AAA studio security operations centers.
Germany
GDPR extraterritorial enforcement compels regional data localization for EU player bases, expanding compliance-native vendor opportunities. The BSI federal cybersecurity authority mandates baseline standards for critical infrastructure protection that extend to esports tournament operators. Frankfurt's internet exchange anchors central European gaming traffic scrubbing capacity.
China
Domestic cloud provider ecosystems and gaming license requirements create parallel security procurement channels distinct from Western vendors. MIIT cybersecurity review procedures for online games mandate pre-launch security assessments. The Yangtze River Delta concentration of game studios drives localized anti-cheat research and development investment.
South Korea
Esports tournament integrity standards and professional gaming league regulations sustain premium spending on broadcast protection and player device hardening. The Korea Internet and Security Agency operates dedicated gaming sector threat intelligence sharing programs. Seoul's Pangyo Techno Valley hosts concentrated security vendor R&D facilities serving domestic publishers.
United Kingdom
Post-Brexit data adequacy negotiations with the EU reshape how UK-based publishers architect player data flows and regional infrastructure placement. The National Cyber Security Centre issues sector-specific guidance for online gaming platform operators. London's financial technology corridor generates crossover demand for virtual currency wallet protection and transaction integrity systems.
Cybersecurity in Gaming Market Competitive Landscape
Listed leaders compete with private specialists across threat intelligence integration and managed detection response bundling. The vendor base stratifies between integrated platform providers and point-solution specialists, with procurement consolidation favoring multi-vector coverage. Three archetypes dominate: network security fabric vendors, cloud-native edge protection specialists, and managed security service operators with gaming sector expertise. Competitive positioning hardens through ISO 27001 certification acceleration and geographic data center expansion to satisfy localization mandates.
Within the integrated platform tier, Fortinet, Inc. and Palo Alto Networks, Inc. represent the dominant architectural approaches for multiplayer backend protection, while Kaspersky Lab occupies a distinct position in Eastern European and Asian market coverage through localized threat research capabilities.
| Leading Market Players |
|---|
| Fortinet, Inc. |
| McAfee LLC |
| Trend Micro Incorporated |
| Symantec Corporation |
| Cisco Systems |
| Cloudflare, Inc. |
| Akamai Technologies, Inc. |
| Kaspersky Lab |
| Palo Alto Networks, Inc. |
| Others |
Pricing and Supply Chain Analysis
Behavioral analytics substitution for signature-based detection tools is redrawing procurement geography and compressing margin structures across vendor tiers. Studios migrating from perpetual licenses to managed detection and response retainers are simultaneously dispersing supplier relationships across Nordic indie clusters and California-Washington enterprise hubs while flattening price premiums for legacy endpoint security.
Pricing Analysis
Volume-discount tiering structures separate capital-constrained indie developers from AAA publishers with dedicated security operations centers. Three-tier pricing structure across premium, standard, and economy levels aligns with ISO 27001 certification maturity, with human-in-the-loop override architectures and hardware security module integration commanding top-tier positioning. Pricing pressure stems from procurement consolidation favoring multi-vector coverage bundles over point-solution stacking. Indie developers exhibit highest price sensitivity, prioritizing operational expenditure treatment through monthly subscription structures, while esports organizations with eight-figure prize pool exposure demonstrate lowest sensitivity to premium tiering for broadcast integrity systems.
Supply Chain Analysis
The United States and Germany anchor enterprise-grade security fabric development, while South Korea and China sustain specialized anti-cheat research and localized threat intelligence capabilities. Supply chains draw from silicon fabrication in Taiwan for hardware security modules, proprietary behavioral heuristic engines developed in California and Washington state, and cloud edge node infrastructure distributed across Frankfurt and Seoul internet exchanges. Single-source vulnerability concentrates in platform holder certification review timelines that delay patch deployment for zero-day vulnerabilities. Distribution runs through direct vendor relationships with AAA publishers, managed security service operator intermediation for mid-tier studios, and lightweight SDK marketplaces serving Southeast Asia mobile developers.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Fragmentation across threat vectors, deployment models, and compliance tiers creates multiple white-space entry points. Cloud edge node proliferation and AI-generated social engineering tactics are splintering demand into specialized niches that favor focused specialists over integrated platform providers.
For Market Incumbents: Secure ISO 27001 certification acceleration to maintain vendor selection gating at AAA publishers facing six-month evidence window compression. Fortify regional data center expansion in Germany and India to satisfy GDPR and emerging data protection bill localization mandates, insulating revenue concentration risk from California-Washington supplier clustering. For New Entrants and Emerging Players: Lead with lightweight anti-cheat SDKs targeting Southeast Asia mobile gaming expansion, where smartphone penetration outpaces security infrastructure deployment. Bundle behavioral biometrics for player authentication as drop-in replacements for hardware-backed two-factor systems, capturing mid-tier studios capital-constrained from premium hardware security module integrators. For Investors and Strategic Acquirers: Capital is best deployed toward managed detection and response operators with gaming sector expertise and established Nordic indie developer subscription relationships. Long-term viability hinges on recurring revenue retention through continuous threat coverage alignment rather than upfront tool deployment. Monitor divergence between regional breach notification timelines and AI-generated social engineering tactic sophistication as inflection indicator for defensive investment priority shifts.| Strategic Initiative | Industry Significance |
|---|---|
| ISO 27001 Certification Acceleration | Gates vendor selection at AAA publishers facing compressed six-month evidence windows. |
| Regional Data Center Expansion | Satisfies GDPR extraterritorial enforcement and India's emerging localization requirements. |
| Managed Detection and Response Retainer Model | Aligns vendor incentives with continuous threat coverage for Nordic indie developer clusters. |
| Behavioral Biometrics SDK Development | Captures mid-tier studios seeking lightweight alternatives to hardware-backed two-factor systems. |
| AI-Generated Content Moderation Integration | Addresses EU AI Act high-risk categorization for real-time player behavior analysis systems. |
Research Methodology
A standing panel of chief information security officers at AAA publishers, managed security service operator technical directors, esports tournament operations leads, and platform holder compliance officers provided ongoing calibration. Primary interviews combined with secondary validation against SEC filings, FCC broadband resilience disclosures, GDPR enforcement actions by French CNIL, and cloud provider capex statements. Bottom-up sizing across threat type, deployment model, end user, and compliance standard segments triangulated with top-down macroeconomic anchors.
Consistency checks validated volume and value outputs against hyperscaler infrastructure investment disclosures and esports prize pool growth trajectories across the analysis window. Segmentation dimensions modeled encompass threat vector substitution dynamics, cloud-native versus hybrid architecture adoption patterns, and regional regulatory cluster divergence. CAGRs derived from elasticity-adjusted demand curves incorporating live service monetization architecture proliferation and AI-generated social engineering tactic volume escalation.
The analysis sits within stated boundaries; outcomes outside sustained cloud migration momentum, stable GDPR enforcement intensity, or continued esports prize pool expansion would require recalibration. Forecasts reflect documented assumptions regarding behavioral analytics substitution velocity and platform holder certification timeline evolution. Recalibration cycles align with material shifts in FCC broadband oversight, EU AI Act conformity assessment obligations, and state-level data privacy statute divergence.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Sweden Cybersecurity Market
Cybersecurity
North America IoT Security Market
Cybersecurity
M2M Network Security Market
Cybersecurity
Digital Security Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
5G Security Market
Cybersecurity
Saudi Arabia Cybersecurity Market
Cybersecurity
Latin America Cybersecurity Market
Cybersecurity
Global IoT Digital Forensics Market
Cybersecurity
United Arab Emirates Cybersecurity Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Mobile Encryption Market