
 Dark Web Intelligence Market | 2026-2036
Dark Web Intelligence Market Size, Share, and Industry Trends Forecast 2026-2036
Dark Web Intelligence Market Analysis
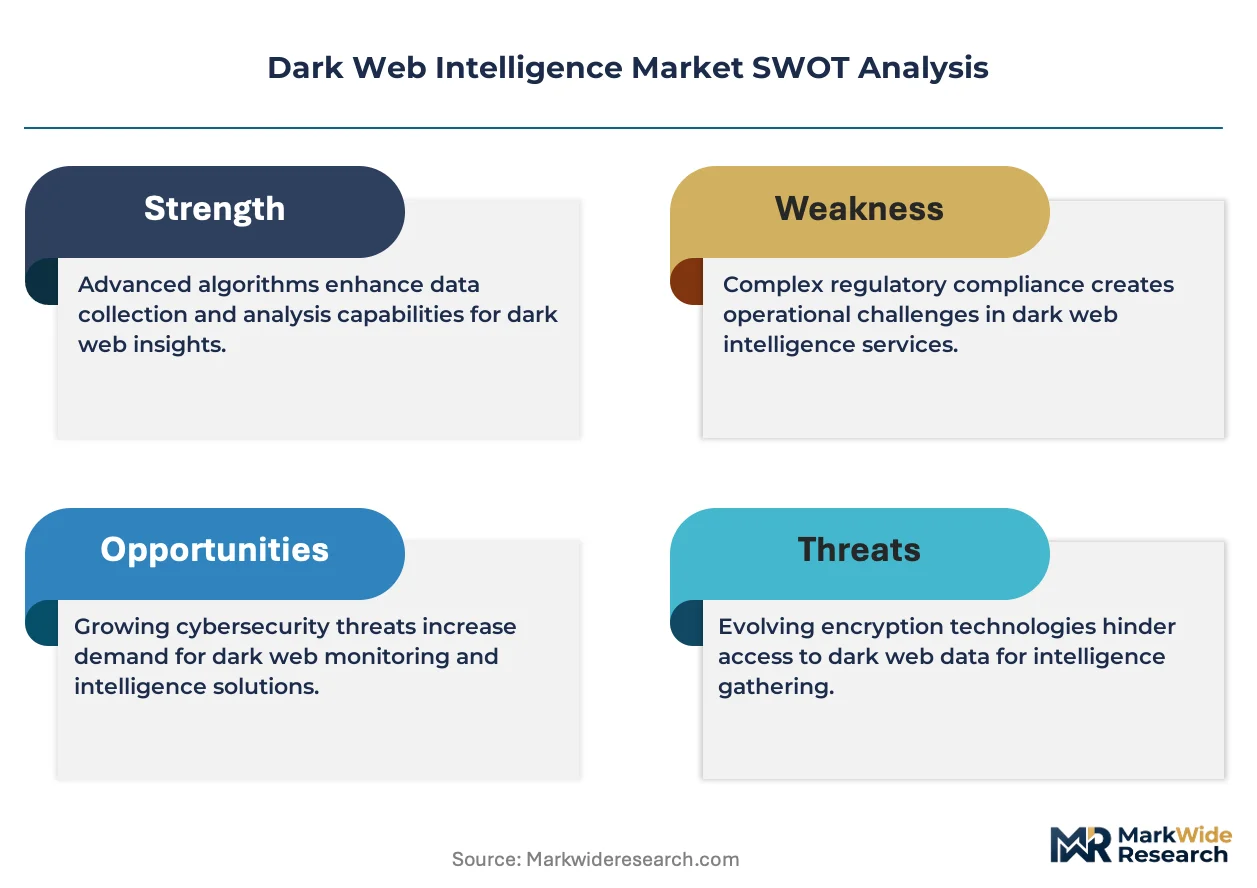
Threat actor profiling revenue is reshaping margin distribution across the Dark Web Intelligence landscape. Recorded Future leverages automated reconnaissance pipelines to dominate technical intelligence collection. Flashpoint anchors human-source intelligence networks that penetrate closed criminal forums. Terbium Labs specializes in data-fingerprinting algorithms that trace stolen credentials across illicit marketplaces.
Dark web intelligence encompasses the systematic collection, analysis, and operationalization of data from anonymized networks including Tor, I2P, and Freenet, typically requiring specialized crawlers, natural language processing for slang decryption, and cryptocurrency transaction tracing to map criminal supply chains. Its primary purpose is preemptive threat mitigation—enabling organizations to detect leaked credentials, impending attacks, or stolen assets before exploitation occurs. Threat intelligence solutions now capture the largest margin pool as enterprises prioritize actionable indicators over raw data feeds, while cloud-based deployment architectures expand fastest among mid-market buyers seeking elastic infrastructure without capital commitment. Law enforcement end users sustain premium pricing for investigative platforms with chain-of-custody documentation and courtroom-ready evidence packaging.
The Federal Bureau of Investigation and Europol coordinate cross-border takedowns that temporarily disrupt data availability yet simultaneously stimulate demand for resilient monitoring infrastructure. NIST cybersecurity frameworks and the EU Cyber Resilience Act mandate external threat visibility assessments that directly incorporate dark web reconnaissance into compliance checklists. Stakeholders must weigh build-versus-buy decisions for onion-routing infrastructure against vendor platforms as criminal forums migrate to decentralized protocols faster than enterprise procurement cycles adapt.
Market Dynamics
The migration of criminal forums to decentralized protocols and peer-to-peer architectures is compressing data visibility windows for traditional crawling infrastructure. Enterprises now face procurement cycles that lag six to eighteen months behind adversary platform shifts, forcing vendor consolidation around hybrid human-machine collection stacks.
Growth Catalysts
- GDPR Article 32 mandates:European enterprises must implement technical measures ensuring security of processing, explicitly covering external threat visibility including dark web reconnaissance for credential exposure detection.
- Financial services:Payment card networks and retail banks deploy continuous monitoring to preempt account takeover campaigns before credential dumps reach exploitation phase.
- Federal cybersecurity directives:United States critical infrastructure operators face mandatory continuous dark web reconnaissance under CISA guidance for sixteen designated sectors.
Market Restraints
- Specialized linguist scarcity:Human-source intelligence networks require analysts fluent in Russian, Mandarin, and Arabic cybercriminal argot, constraining collection scale.
- Cryptocurrency tracing infrastructure:Blockchain analytics platforms demand sustained capital commitment for wallet clustering algorithms and exchange partnership negotiations.
- Forum access decay:Closed criminal communities implement rigorous vetting procedures and invite-only membership, degrading automated crawler penetration rates.
Strategic Opportunities
- Mid-market cloud deployment:Elastic infrastructure models enable organizations below ten thousand employees to access tier-one intelligence feeds without capital expenditure commitment.
- Law enforcement evidence packaging:Investigative platforms with embedded chain-of-custody documentation command premium pricing from national security agencies and cybercrime units.
- Natural language processing convergence:Slang decryption algorithms combined with behavioral biometrics enable automated threat actor attribution at scale previously requiring human analyst teams.
Industry Challenges
- Onion-routing infrastructure build-versus-buy decisions:Enterprise security teams lack internal expertise to maintain Tor exit node farms and I2P peer discovery systems.
- Integration friction with SIEM platforms:Dark web intelligence feeds require custom API development to correlate with internal security event data streams.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Dark Web Intelligence Market |
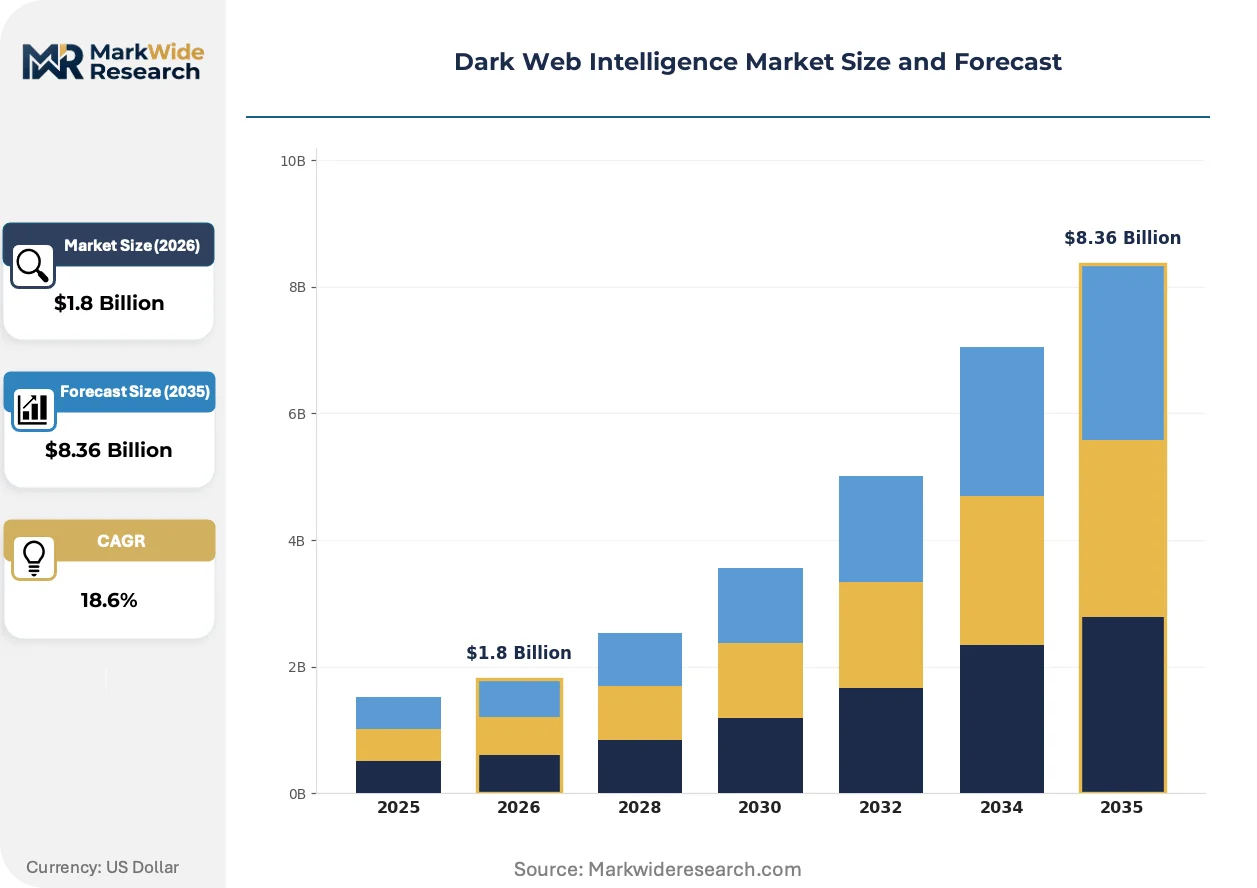
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $8.36 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Threat Intelligence, Monitoring Tools, Data Analytics, Investigative Platforms End User: Government Agencies, Financial Institutions, Cybersecurity Firms, Law Enforcement Deployment: On-Premise, Cloud-Based, Hybrid Solutions, Managed Services Service Type: Consulting, Managed Security, Incident Response, Training |
| Companies Covered | Terbium Labs, Digital Shadows, Recorded Future, Cybint, SenseCy, Flashpoint, IntSights, Bitsight, DarkOwl, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Dark Web Intelligence Market Emerging Trajectories
Automated reconnaissance pipelines are compressing analyst-to-alert ratios while regulatory mandates harden external threat visibility into audit-ready compliance artifacts. The competitive frontier shifts toward attribution confidence and evidence admissibility rather than raw data volume.
Natural language processing systems trained on cybercriminal forum corpora are collapsing the latency between threat actor planning chatter and defensive alert generation. Financial institutions and critical infrastructure operators deploy these engines to process Russian-language market discussions without human linguist bottlenecks. The technology is collapsing incident response preparation windows from weeks to hours for credential exposure events.
The EU AI Act's risk-based classification framework imposes documentation obligations on automated threat detection systems processing personal data from illicit sources. Security vendors must now maintain algorithmic audit trails and human oversight protocols for machine-generated intelligence products. European enterprise buyers increasingly require vendor compliance attestations before procurement authorization.
Mid-market buyers now reject annual subscription contracts in favor of consumption-based pricing tied to alert volume or investigated indicators. Managed security service providers bundle dark web monitoring into broader threat intelligence packages, displacing direct vendor relationships for organizations below five hundred employees. This pattern concentrates most visibly in United States healthcare and professional services verticals where CISO resources remain constrained.
Dark Web Intelligence Market Segmentation
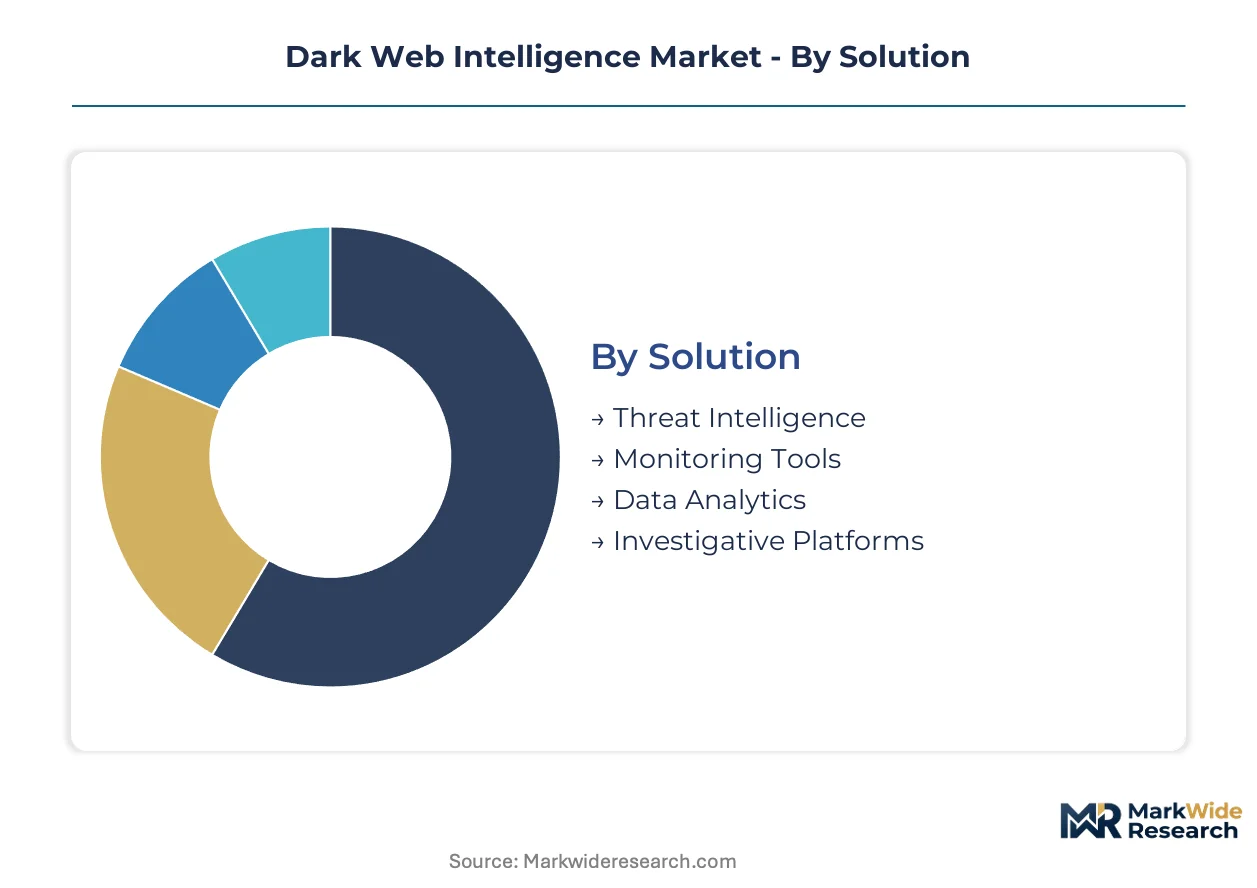
Dark web intelligence procurement patterns diverge sharply across organizational maturity, regulatory exposure, and technical sophistication. Solution architecture, deployment models, and service relationships each reshape vendor selection criteria and contract structures in distinct ways.
Solution:
Use-case spectrum spans raw data ingestion through courtroom-ready evidence generation, with capability depth determining price tier and integration complexity.
- Threat Intelligence:Aggregated indicator feeds combining credential dumps, exploit chatter, and actor attribution scores. Financial institutions in the United States prioritize these feeds for preemptive account takeover blocking, driven by CISA sector-specific guidance.
- Monitoring Tools:Continuous crawler infrastructure tracking Tor hidden services, I2P eepsites, and Telegram channels for brand exposure and executive targeting. European enterprises under GDPR Article 32 mandate deploy these for automated credential leak detection.
- Data Analytics:Cryptocurrency transaction clustering and wallet attribution engines.
- Investigative Platforms:Chain-of-custody documentation systems for law enforcement evidence packaging.
Established volume favors Threat Intelligence; emerging adoption favors Investigative Platforms.
End User:
Customer type determines procurement authority, budget scale, and compliance documentation requirements.
- Government Agencies:National security and defense intelligence units requiring cleared-analyst access and classified infrastructure integration. United States federal demand concentrates here under continuous reconnaissance mandates for critical infrastructure protection.
- Financial Institutions:Retail banks, payment processors, and investment firms deploying real-time credential exposure monitoring. European banking supervisors now explicitly incorporate dark web visibility into operational risk assessments.
- Cybersecurity Firms:MSSPs and boutique consultancies reselling intelligence feeds to downstream clients.
- Law Enforcement:Cybercrime units and federal investigators requiring admissible evidence trails.
Margin concentration sits with Financial Institutions; steepest expansion trajectory belongs to Law Enforcement.
Deployment:
Cost tier structures separate capital-intensive infrastructure from elastic operational expenditure models.
- On-Premise:Dedicated Tor exit node farms and air-gapped analysis environments for classified or sovereignty-sensitive operations. Government agencies in the United States and European defense ministries sustain this segment despite high fixed costs.
- Cloud-Based:API-accessible intelligence feeds with consumption-based pricing and zero infrastructure commitment. Mid-market enterprises below ten thousand employees across United States healthcare and professional services verticals are gaining share fastest here.
- Hybrid Solutions:Split architectures keeping sensitive collection on-premise while leveraging cloud analytics.
- Managed Services:Fully outsourced monitoring with analyst augmentation and incident response integration.
Cloud-Based deployment is climbing the fastest; On-Premise retains the premium pricing tier.
Service Type:
Supply concentration clusters around high-touch advisory relationships versus automated product delivery.
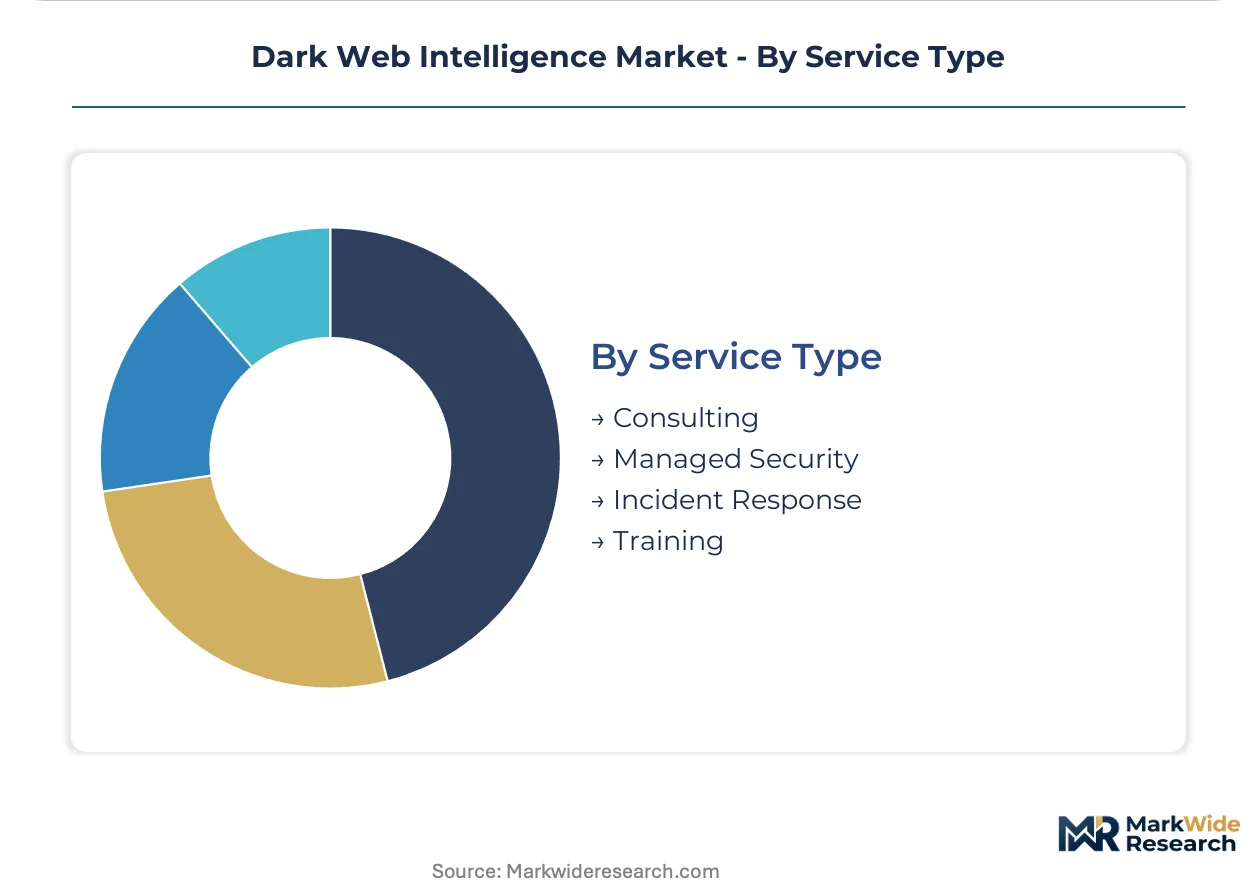
- Consulting:Strategic assessments of external threat exposure, dark web reconnaissance program design, and compliance gap analysis. European enterprises navigating EU AI Act documentation obligations drive specialized demand here.
- Managed Security:Continuous monitoring operations with SLA-backed alert generation and analyst investigation. United States critical infrastructure operators under federal directive mandate this service category for sixteen designated sectors.
- Incident Response:Post-breach dark web investigation for credential validation and actor identification.
- Training:Analyst certification in forum infiltration, cryptocurrency tracing, and slang decryption.
Managed Security captures the largest contract values; Training shows the narrowest addressable market.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Consumption patterns for dark web intelligence diverge sharply across geographies. United States buyers prioritize preemptive threat blocking for critical infrastructure protection. European procurement emphasizes GDPR compliance documentation and algorithmic audit trails. Asia-Pacific demand concentrates on multilingual analyst capabilities and regional cryptocurrency tracing infrastructure.
United States
CISA mandates continuous dark web reconnaissance across sixteen critical infrastructure sectors including energy, finance, and healthcare. Federal cybersecurity directives issued under the National Cybersecurity Strategy compel operators to maintain external threat visibility as a condition of sector participation. Washington DC and Northern Virginia host the densest concentration of threat intelligence vendors serving federal agencies and defense contractors.
Germany
Industrial conglomerates and automotive manufacturers deploy dark web monitoring to protect intellectual property and supply chain credentials. The EU Cyber Resilience Act and GDPR Article 32 impose mandatory technical measures for external threat detection, with German regulators enforcing stringent documentation standards. Frankfurt's financial services cluster drives specialized demand for real-time credential exposure alerts among Bundesbank-supervised institutions.
United Kingdom
London-based investment banks and insurance underwriters prioritize automated reconnaissance for executive protection and market-moving threat detection. The National Cyber Security Centre's guidance on supply chain resilience explicitly incorporates dark web intelligence into baseline security practices. The Thames Valley cybersecurity corridor concentrates vendor operations serving both commercial and Government Communications Headquarters-adjacent requirements.
France
Luxury goods houses and aerospace-defense primes deploy monitoring tools to counter counterfeiting networks and credential harvesting campaigns targeting design IP. CNIL oversight of automated processing systems shapes vendor selection criteria, with French buyers demanding explicit human oversight protocols for machine-generated intelligence. Paris-Saclay's research cluster hosts emerging NLP specialists focused on slang decryption for Francophone criminal forums.
Israel
Defense technology exporters and cybersecurity unicorns integrate dark web intelligence into nation-state threat attribution workflows. Military unit alumni networks supply human-source intelligence expertise that penetrates closed Arabic and Persian-language criminal communities. Tel Aviv's cybersecurity district concentrates boutique consultancies serving both domestic intelligence requirements and export markets across Europe and North America.
Dark Web Intelligence Market Vendor Landscape
Capability concentration sits with specialized reconnaissance providers; scale advantage sits with integrated threat intelligence platforms. The vendor base separates into three functional tiers: automated crawling infrastructure operators, human-source intelligence networks, and hybrid platforms combining machine collection with analyst augmentation. Consolidation pressure intensifies as criminal forum migration to decentralized protocols outpaces standalone technical collection capabilities. Dominant competitive moves include strategic partnerships with blockchain analytics providers and vertical integration into incident response services.
Within the automated reconnaissance tier, Recorded Future exemplifies platform-scale operations, while Flashpoint anchors human-source intelligence capabilities. Terbium Labs occupies a specialized position in data-fingerprinting and credential tracing across illicit marketplaces. These three entities represent distinct archetypes—machine-scale collection, human-network penetration, and algorithmic data attribution—that collectively define the competitive frontier for external threat visibility.
| Leading Market Players |
|---|
| Terbium Labs |
| Digital Shadows |
| Recorded Future |
| Cybint |
| SenseCy |
| Flashpoint |
| IntSights |
| Bitsight |
| DarkOwl |
| Others |
Supply Flow & Price Mechanics
Transatlantic fiber corridors carry the bulk of dark web intelligence platform traffic between European data centers and United States cloud regions, with latency-sensitive crawler infrastructure commanding premium colocation costs that concentrate pricing power among hyperscale-adjacent vendors while forcing mid-tier providers toward consumption-based SaaS models.
Pricing Analysis
Long-term enterprise offtake agreements dominate procurement for critical infrastructure operators under CISA mandates, while mid-market buyers gravitate toward consumption-based SaaS tiers pegged to alert volume. Pricing stratifies across premium, standard, and economy tiers based on attribution confidence scores and evidence admissibility documentation. Cost compression in standard-tier feeds is intensifying because Flashpoint and Recorded Future have automated core collection workflows. Government agencies show least price sensitivity due to chain-of-custody requirements; professional services firms below five hundred employees exhibit highest elasticity.
Supply Chain Analysis
United States export-control regimes under EAR Category 5 restrict specialized onion-routing hardware and cryptographic analysis tools to allied intelligence partnerships, constraining supply concentration in Israel, United Kingdom, and domestic United States vendors. Raw material dependencies center on GPU clusters for NLP training, Tor exit node bandwidth, and blockchain node infrastructure. Single-source vulnerability runs through cloud hyperscalers for elastic compute. Distribution feeds through managed security service providers who bundle monitoring into broader threat intelligence packages.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Dark web intelligence is approaching a platform-economics inflection where API interoperability between reconnaissance engines and SIEM ecosystems determines vendor survival, with the STIX/TAXII standardization push enabling modular substitution that rewards open-architecture players.
For Market Incumbents: Build switching-cost moats through embedded workflow integration with Splunk and Microsoft Sentinel deployments. Acquire boutique linguist networks in Tel Aviv and Eastern Europe to counter automated NLP commoditization. CISA procurement centralization poses consolidation pressure; secure FedRAMP authorization to maintain federal access.
For New Entrants and Emerging Players: French aerospace-defense supply chains show underpenetration for credential exposure monitoring despite CNIL documentation requirements. Target mid-market German automotive suppliers facing EU Cyber Resilience Act compliance deadlines with hybrid cloud-on-premise deployment models. Partner with regional MSSPs rather than direct enterprise sales to bypass Flashpoint's human-source network advantages.
For Investors and Strategic Acquirers: Boutique consultancies with cleared-analyst pools and Arabic/Persian forum penetration capabilities represent priority acquisition targets. Long-term viability hinges on attribution automation reducing human linguist dependency. Watch for European banking supervisor guidance explicitly mandating dark web visibility as operational risk capital trigger.
| Strategic Initiative | Industry Significance |
|---|---|
| Hybrid Collection Architecture Development | Combines automated Tor crawling with human-source networks to penetrate invite-only criminal forums. |
| Blockchain Analytics Partnership | Wallet clustering capabilities from Chainalysis or Elliptic integration enable cryptocurrency tracing revenue streams. |
| FedRAMP Authorization Pursuit | Cloud-based vendors require this certification to serve United States federal agencies under CISA mandates. |
| NLP Slang Decryption Investment | Automated Russian and Mandarin cybercriminal argot processing collapses analyst-to-alert ratios for financial clients. |
| Incident Response Vertical Integration | Post-breach investigation services capture higher margins than raw intelligence feed subscriptions. |
Methodological Framework
Two parallel data streams informed the analysis: structured interviews with threat intelligence directors, CISOs at financial institutions, federal procurement officers, and dark web analyst team leads; and secondary validation against CISA directive texts, EU AI Act documentation requirements, SEC cybersecurity disclosure filings, and vendor contract structure databases. Bottom-up sizing of deployment models and end-user segments was triangulated against top-down market value estimates from technology expenditure surveys.
Forecast inputs considered solution type, deployment architecture, organization size tier, and regional regulatory intensity across the projection horizon. CAGR derivation incorporated technology adoption S-curves for NLP automation, compliance mandate phase-in schedules, and criminal forum migration patterns toward decentralized protocols. Cryptocurrency tracing infrastructure buildout rates and linguist analyst supply constraints shaped segment-specific growth differentials.
The forecast holds incumbent behavior within observed patterns; aggressive platform consolidation moves by Recorded Future or Flashpoint would shift outcomes beyond modeled ranges. Material shifts in criminal adoption of fully peer-to-peer architectures without crawlable surfaces, or European banking regulator enforcement intensity, would require updated calibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
Big Data Security Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Cloud Security Gateway Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Network Detection and Response Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Banking Cyber Security Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Global Cyber Threat Intelligence Market