
 Cloud-Based Email Security Market | 2026-2036
Cloud-Based Email Security Market Size, Share, and Industry Trends Forecast 2026-2036
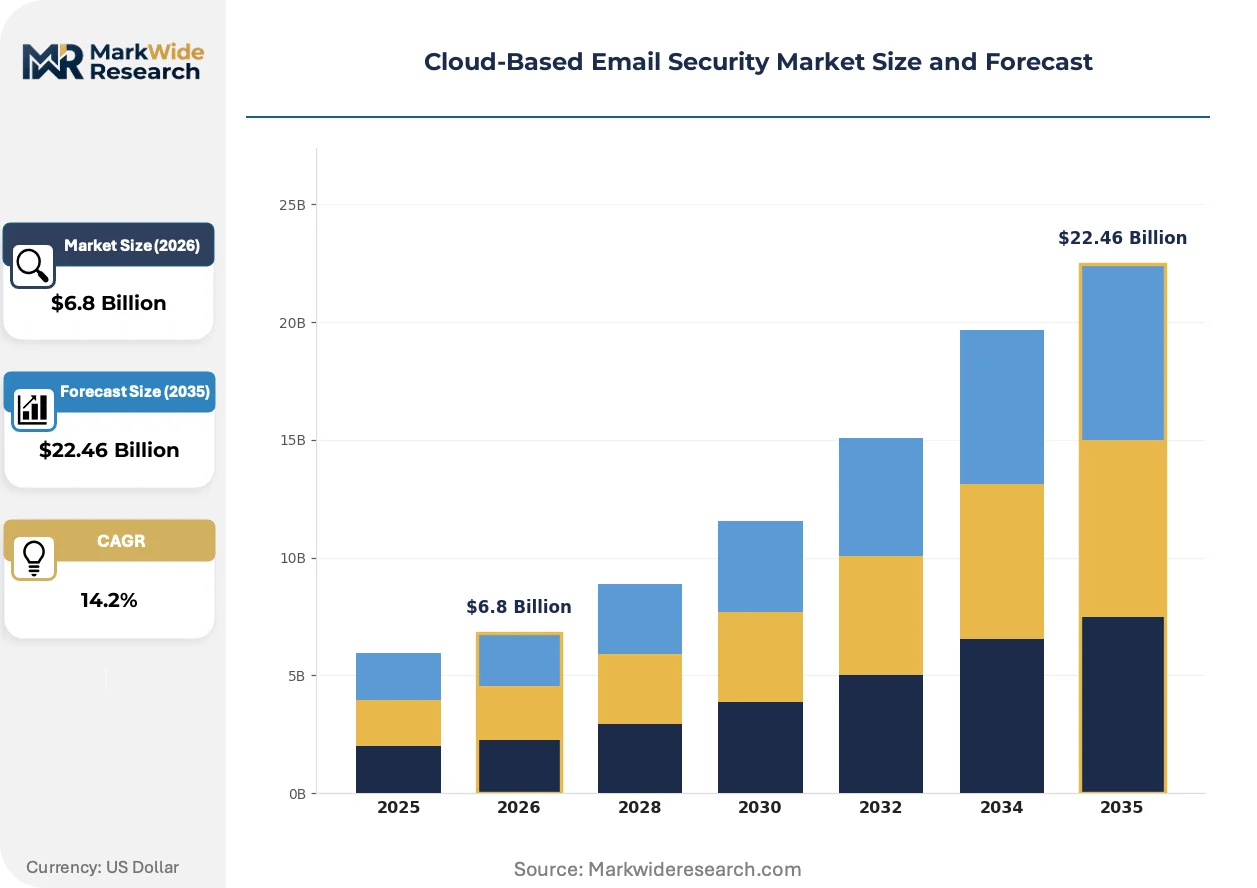
Cloud-Based Email Security Market Outlook
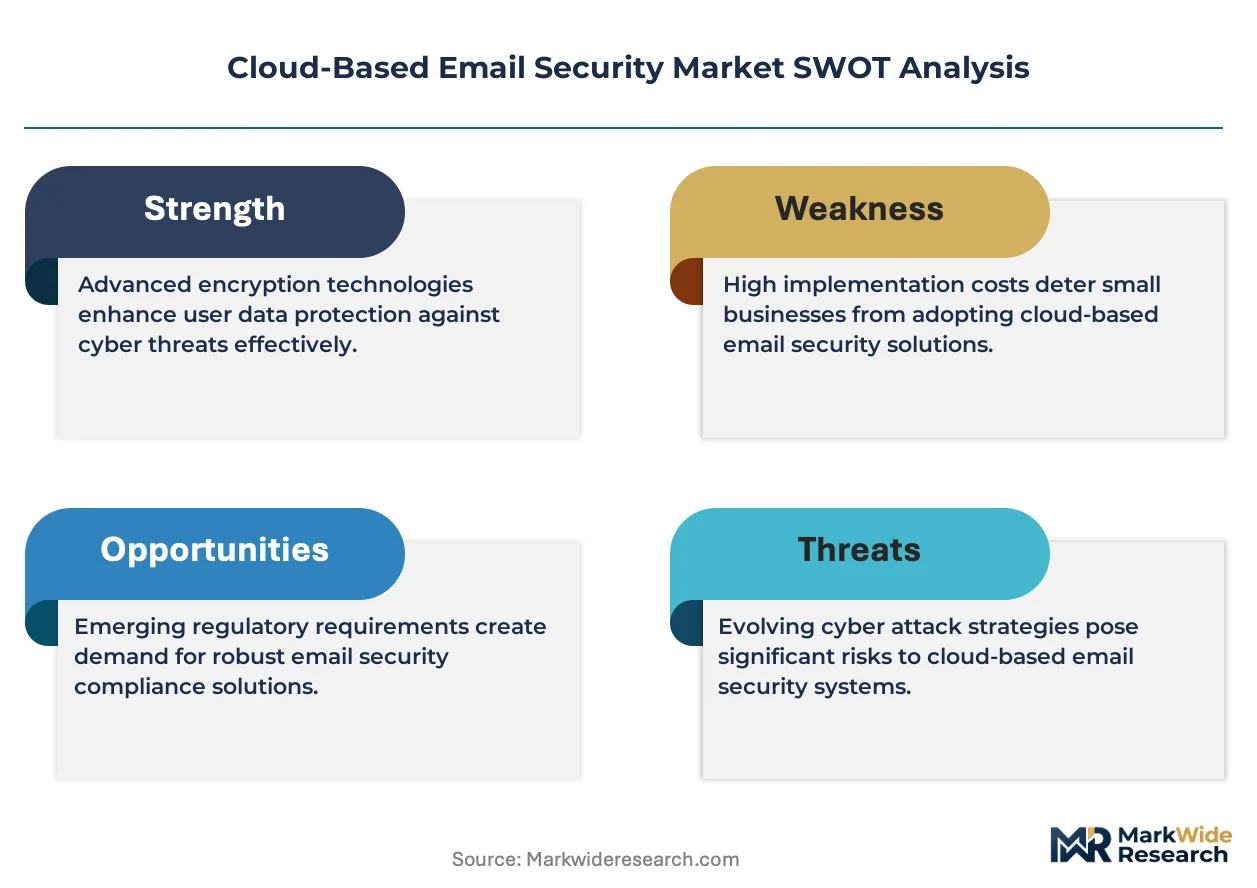
Platform licensing revenue is reconfiguring margin pools away from perpetual on-premises deployments toward recurring cloud subscriptions. Proofpoint leverages API-native architecture to sustain differentiation in the mid-market segment. Cisco Secure Email anchors its position through deep integration with enterprise networking infrastructure. Mimecast competes by extending archiving and continuity services alongside core threat protection.
Cloud-based email security encompasses SaaS-delivered systems that inspect SMTP traffic, detect phishing payloads, and enforce data loss prevention policies using machine learning classifiers and sandbox detonation chambers. These platforms serve commercial and governmental organizations by intercepting business email compromise attempts and malware distribution before messages reach user inboxes. Threat detection capabilities represent the fastest-expanding service type as adversaries deploy generative AI for social engineering. Large corporations dominate end-user demand due to complex supply chain email flows and regulatory audit requirements. Hybrid cloud deployments are gaining traction among organizations maintaining legacy on-premises exchange infrastructure while migrating selective workloads.
The EU AI Act, HIPAA, and ISO 27001 collectively shape product development roadmaps by mandating explainability in automated filtering decisions and documented encryption key management. The FCC and SEC in the United States impose additional disclosure obligations for publicly traded firms experiencing email-borne data breaches. Stakeholders must evaluate how emerging quantum-resistant encryption standards will alter certificate infrastructure investments and interoperability testing protocols.
Market Dynamics
Generative AI-powered phishing campaigns are forcing enterprises to abandon signature-based detection in favor of behavioral analysis and natural language processing models that inspect email intent rather than payload hashes.
Growth Catalysts
- EU AI Act compliance mandates:Financial services firms across Germany, France, and Italy must deploy explainable automated filtering systems by 2026, accelerating replacement of opaque legacy rule engines.
- Business email compromise volume:Manufacturing supply chains generate dense email flows between procurement teams and offshore vendors, creating concentrated demand for sender authentication and domain fraud detection.
- API-native architecture:Cloud-delivered platforms integrate directly with Microsoft 365 and Google Workspace via REST APIs, eliminating gateway latency and reducing deployment friction for mid-market IT teams.
Market Restraints
- Certificate infrastructure concentration:TLS and S/MIME certificate issuance depends on a narrow base of root certificate authorities, creating systemic vulnerability if any major provider experiences compromise or distrust event.
- Sandbox detonation costs:Real-time payload analysis in isolated virtual environments consumes substantial compute resources, pressuring gross margins for vendors serving high-volume enterprise inboxes.
- Data residency fragmentation:Divergent national encryption key storage requirements between the United States, Germany, and Japan force vendors to maintain redundant regional infrastructure, elevating operational complexity.
Strategic Opportunities
- Quantum-resistant certificate migration:NIST post-quantum cryptography standards will compel certificate authority re-issuance cycles, creating replacement demand for email encryption infrastructure across regulated industries.
- Continuity service bundling:Email archiving and disaster recovery capabilities address SEC and FINRA retention requirements, allowing vendors to expand average contract value within existing financial services accounts.
- Managed detection and response integration:Convergence of email security with broader SOC workflows enables vendors to capture security operations center budgets previously allocated to separate endpoint and network monitoring tools.
Industry Challenges
- Machine learning model explainability:SOC analysts require transparent reasoning for automated quarantine decisions to satisfy internal audit and external regulator scrutiny, complicating black-box neural network deployment.
- Legacy Exchange coexistence:Hybrid cloud architectures force vendors to maintain parallel filtering paths for on-premises and cloud-hosted mailboxes, doubling integration testing and support overhead.
- Threat intelligence signal fatigue:High-volume indicator feeds generate excessive false positives when applied to diverse enterprise email patterns, degrading analyst trust and platform utilization rates.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Cloud-Based Email Security Market |
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $22.46 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Filter Services, Threat Detection, Encryption Solutions, Backup Services Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud End User: Small Enterprises, Mid-Sized Companies, Large Corporations, Government Agencies Compliance Standard: GDPR, HIPAA, ISO 27001, PCI DSS |
| Companies Covered | Check Point Avanan, Cisco Secure Email, Proofpoint, Microsoft Defender for Office 365, IRONSCALES, Mimecast, Barracuda Email Protection, Cloudflare Email Security, Abnormal AI, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Cloud-Based Email Security Market Strategic Shifts
Natural language understanding models are collapsing the distinction between legitimate business correspondence and socially engineered deception, forcing platform architectures toward continuous retraining pipelines and federated learning approaches.
Large language model-based detection engines inspect semantic patterns and sender behavioral biometrics rather than static attachment signatures. Financial services and professional services firms are deploying these systems within six-month procurement cycles, abandoning three-year appliance refresh schedules. This compression is collapsing the traditional enterprise sales motion toward proof-of-concept trials with immediate production cutover.
The EU AI Act's risk classification framework mandates human oversight for automated decisions affecting fundamental rights, including email filtering that blocks employment or financial communications. Vendors must engineer audit trails and override workflows into product roadmaps. German and French banking regulators are already inspecting these capabilities during licensing examinations, creating competitive differentiation for compliant architectures.
Security procurement teams are consolidating vendor relationships and demanding unified platforms that span email, collaboration tools, and cloud file sharing. Mid-market enterprises previously buying point solutions now issue RFPs for integrated communication security suites. This concentration is most visible in United States healthcare and legal sectors, where HIPAA and state bar compliance officers prefer single-vendor accountability for data protection attestations.
Cloud-Based Email Security Market Segmentation
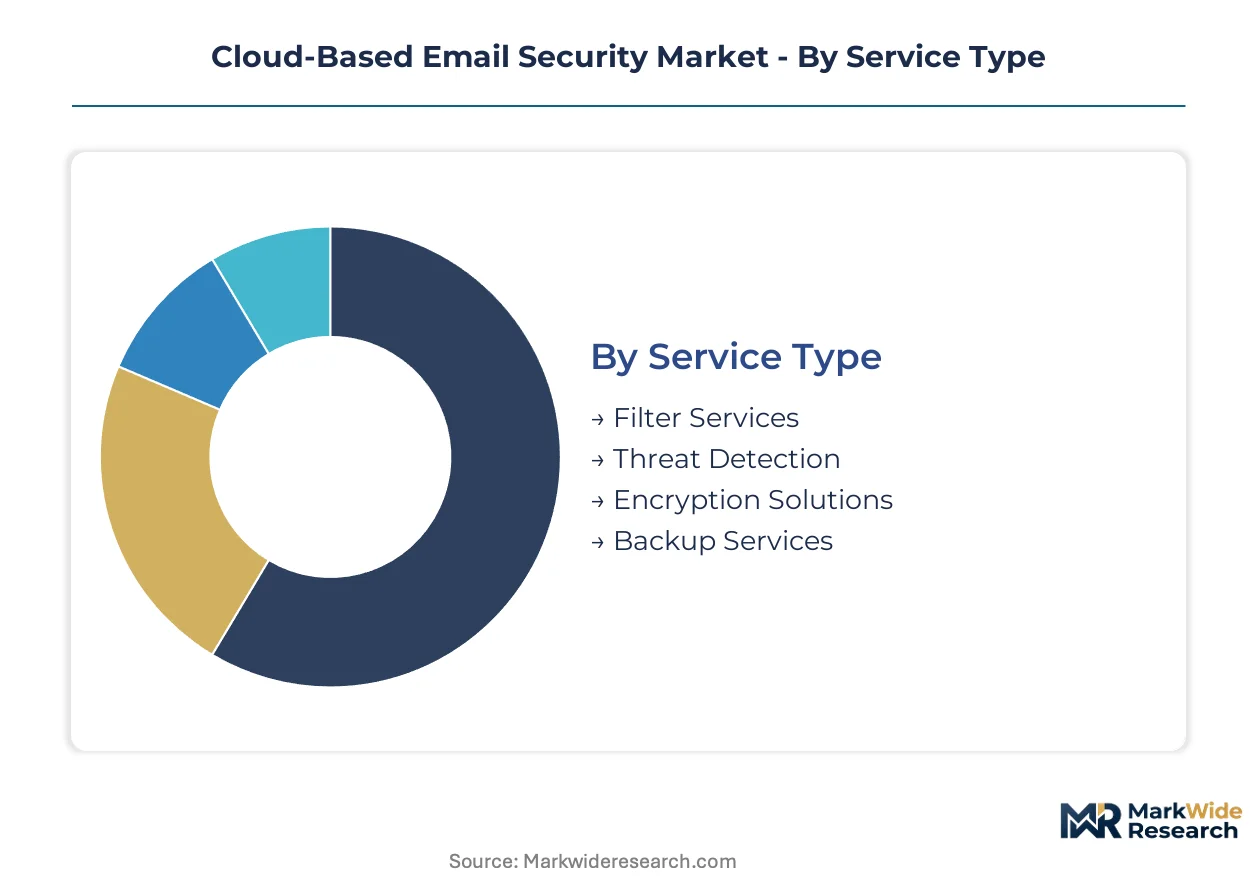
Cloud-based email security procurement patterns diverge sharply across organizational scale, regulatory exposure, and infrastructure maturity. Segment-level analysis reveals where platform vendors concentrate engineering resources and which customer profiles command premium pricing power.
Service Type:
Cost tier determines feature bundling and margin structure across the four service categories.
- Threat Detection:Machine learning classifiers inspect SMTP traffic for phishing payloads, business email compromise indicators, and generative AI-generated social engineering content. Financial services institutions in Germany and the United States concentrate procurement here due to SEC and BaFin disclosure obligations for email-borne breaches. This segment is climbing the fastest as adversaries automate attack personalization.
- Encryption Solutions:TLS and S/MIME certificate management plus end-to-end message encryption enforce data loss prevention policies. Healthcare systems under HIPAA and European enterprises facing GDPR Article 32 technical requirements drive concentrated demand for quantum-resistant certificate migration paths.
- Filter Services:Rule-based and reputation filtering blocks spam and known malware signatures at the gateway level. Mid-sized companies with limited SOC staffing rely on these baseline protections.
- Backup Services:Archiving and continuity capabilities address regulatory retention mandates and disaster recovery scenarios. SEC 17a-4 and FINRA compliance requirements in the United States sustain this segment.
Threat Detection holds installed capacity. Encryption Solutions is rotating up the share rankings.
Deployment Model:
Customer infrastructure maturity and data sovereignty requirements shape deployment architecture selection.
- Public Cloud:SaaS-native platforms integrate via REST APIs with Microsoft 365 and Google Workspace, eliminating gateway latency. Small enterprises and mid-sized companies across the United States and Japan favor this model for rapid deployment and minimal capital expenditure.
- Hybrid Cloud:Parallel filtering paths serve on-premises Exchange infrastructure alongside cloud-hosted mailboxes during migration transitions. Manufacturing supply chains in Germany maintain this architecture to preserve legacy procurement system integrations while adopting cloud analytics.
- Private Cloud:Dedicated tenant instances satisfy national encryption key storage requirements and air-gapped security demands. Government agencies in Japan and defense contractors select this model.
- Multi-Cloud:Orchestrated security policies span heterogeneous cloud environments to prevent vendor lock-in. Large corporations with distributed global operations deploy these configurations.
Public Cloud commands volume leadership. Hybrid Cloud is gaining preference among regulated enterprises with legacy dependencies.
End User:
Organizational scale dictates complexity tolerance, integration requirements, and procurement authority structures.
- Large Corporations:Dense supply chain email flows between procurement teams and offshore vendors create concentrated risk surfaces. Complex Active Directory integrations and SIEM correlation requirements characterize this segment. United States-based multinationals with SEC disclosure obligations represent the core revenue base.
- Government Agencies:Classified communications and citizen service portals demand FedRAMP or equivalent national certification. Stringent audit trails and human oversight workflows for automated filtering decisions distinguish procurement specifications.
- Mid-Sized Companies:Limited internal security operations center staffing drives preference for managed detection and response bundling. API-native platforms reduce deployment friction for IT teams without dedicated email security specialists.
- Small Enterprises:Cost-sensitive buyers prioritize out-of-box Microsoft 365 or Google Workspace native protections, with limited appetite for third-party augmentation.
Large Corporations anchor vendor revenue concentration. Government Agencies is expanding fastest among regulated sectors.
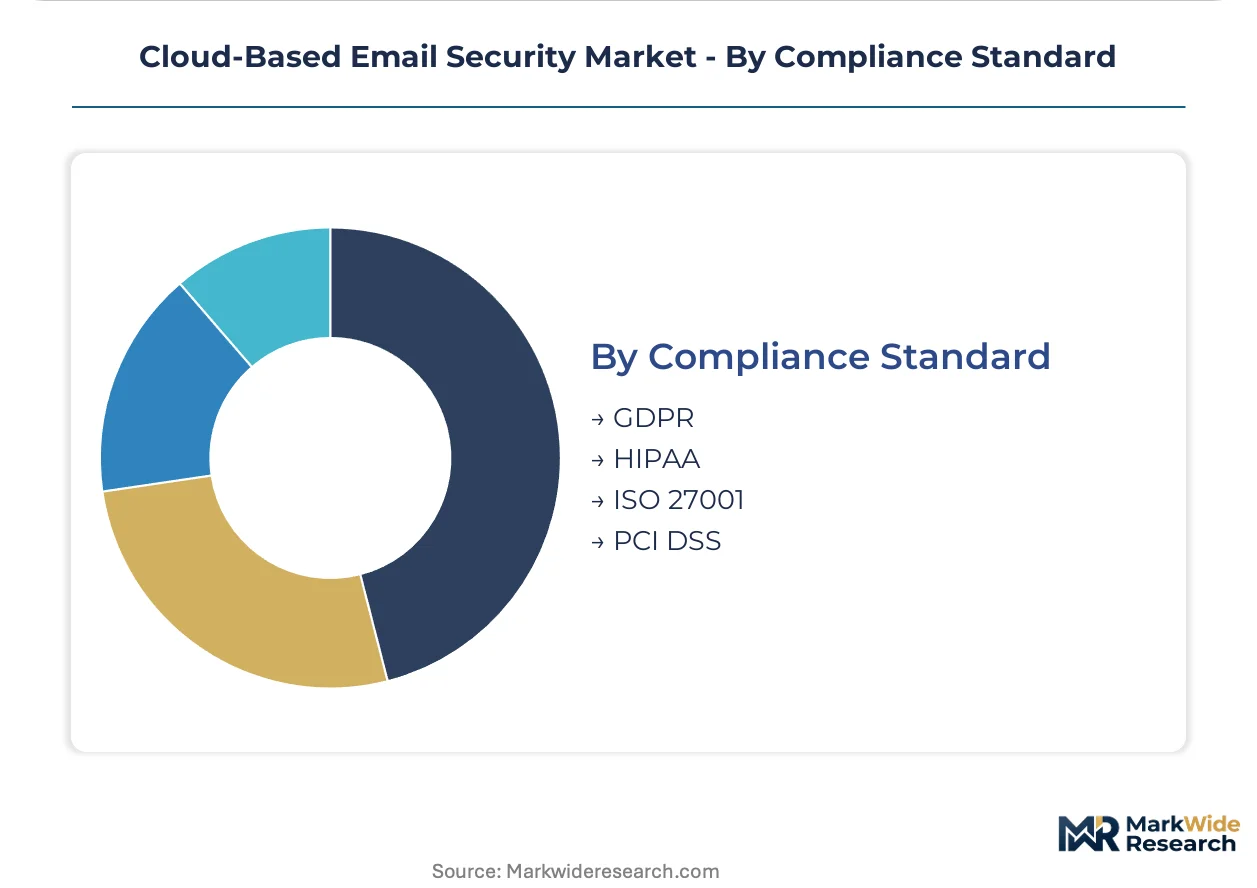
Compliance Standard:
Regulatory jurisdiction determines technical control requirements and vendor qualification barriers.
- GDPR:Article 32 mandates encryption and breach notification capabilities for controllers processing EU resident data. French and Italian banking regulators inspect automated decision explainability during licensing examinations.
- HIPAA:Security Rule technical safeguards require access controls, audit controls, and transmission security for protected health information. United States healthcare systems and business associates drive procurement with specific Business Associate Agreement requirements.
- PCI DSS:Requirement 4 mandates encryption of cardholder data transmitted across open networks. Retail and payment processors concentrate demand here.
- ISO 27001:Annex A controls for communications security provide framework-agnostic certification valued by professional services firms and multinational corporates seeking transferable audit evidence.
GDPR compliance requirements hold broadest geographic coverage. HIPAA is tightening procurement specifications fastest among United States healthcare consolidators.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Price sensitivity varies sharply across geographies. Small enterprises in Japan and mid-sized companies in Germany resist premium tiers, while United States financial institutions absorb higher costs for compliance-grade capabilities.
United States
SEC disclosure obligations for email-borne data breaches drive procurement among publicly traded firms. The FCC imposes additional notification requirements on telecommunications providers handling business communications. New York and Boston financial centers concentrate demand for sender authentication and domain fraud detection systems.
Germany
BaFin licensing examinations now inspect automated decision explainability for email filtering systems. The EU AI Act mandates human oversight workflows for communications affecting employment or financial access. Manufacturing supply chains in Bavaria and North Rhine-Westphalia maintain hybrid cloud architectures to preserve legacy procurement integrations.
Japan
METI guidelines on critical infrastructure protection elevate security requirements for government agencies and defense contractors. National encryption key storage requirements force vendors to maintain dedicated regional infrastructure. Tokyo and Osaka corporate headquarters anchor demand for private cloud deployments with air-gapped security specifications.
France
CNIL enforcement actions under GDPR Article 32 accelerate replacement of legacy rule engines with explainable filtering systems. The EU AI Act risk classification framework applies directly to automated employment communication screening. Paris banking clusters and Lyon manufacturing hubs concentrate mid-market procurement for API-native platforms.
United Kingdom
Financial Conduct Authority operational resilience rules mandate business continuity capabilities for email-dependent trading operations. Post-Brexit data sovereignty requirements complicate cross-border encryption key management. London financial services firms and Manchester legal sector clusters drive demand for integrated archiving and threat protection bundles.
Cloud-Based Email Security Market Competitive Environment
Capability concentration sits with specialized threat detection vendors; scale advantage sits with platform conglomerates. The vendor base organizes into three tiers: API-native specialists, infrastructure-integrated incumbents, and AI-first challengers. Dominant competitive moves include strategic partnerships with cloud productivity suites and portfolio diversification into adjacent communication security domains.
Within the infrastructure-integrated tier, Cisco Secure Email and Microsoft Defender for Office 365 occupy positions leveraging deep enterprise networking and productivity platform relationships respectively. Proofpoint represents the API-native specialist archetype with mid-market penetration. These three exemplify how architectural differentiation—network integration versus cloud-native APIs—shapes competitive positioning without requiring homogeneous customer targeting.
| Leading Market Players |
|---|
| Check Point Avanan |
| Cisco Secure Email |
| Proofpoint |
| Microsoft Defender for Office 365 |
| IRONSCALES |
| Mimecast |
| Barracuda Email Protection |
| Cloudflare Email Security |
| Abnormal AI |
| Others |
Value Chain & Pricing Dynamics
Trans-Pacific fiber routes connecting Tokyo and Los Angeles shape cost structures for cloud security vendors maintaining redundant regional infrastructure, concentrating margin pressure on providers serving Japanese government agencies while enabling tiered subscription pricing across compliance-grade and standard service tiers.
Pricing Analysis
Extended service contracts and continuity service bundling drive lifetime value beyond initial platform licensing. Pricing stratifies across premium, standard, and economy tiers based on certification grade—FedRAMP-authorized deployments command substantial premiums over SOC 2-aligned alternatives—and customization level for SIEM integration complexity. Cost compression in the standard tier is intensifying because Microsoft Defender native bundling reduces standalone vendor pricing power. Small enterprises exhibit highest price sensitivity, while United States financial institutions under SEC disclosure obligations absorb premium tiers without procurement friction.
Supply Chain Analysis
Certificate infrastructure concentration between the United States and Germany dominates supply chain risk profiles for encryption-dependent deployments. TLS and S/MIME certificate issuance draws from a narrow base of root certificate authorities anchored in American and German trust frameworks, with quantum-resistant algorithm migration creating transitional dependency on NIST-standardized providers. Single-source vulnerability in root CA compromise scenarios threatens systemic trust erosion. Distribution runs through direct enterprise sales motions for large corporations, supplemented by channel partners and managed security service providers serving mid-market accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud-based email security sits in early-cycle expansion as generative AI-powered phishing campaigns force accelerated replacement of signature-based detection systems, compressing procurement cycles from three-year appliance refreshes to six-month proof-of-concept trials.
For Market Incumbents: Harden API-native architecture differentiation against Microsoft Defender native bundling by deepening integration complexity with legacy SIEM and SOAR platforms that entrench switching costs. Prioritize FedRAMP and EU AI Act compliance investments to capture government agency expansion and German banking procurement specifications. Consolidate channel partner programs to control distribution economics against emerging AI-first challengers. For New Entrants and Emerging Players: Establish a beachhead in mid-sized manufacturing supply chains across Bavaria and North Rhine-Westphalia, where hybrid cloud architectures create parallel filtering complexity that incumbents serve reluctantly. Target managed detection and response bundling for IT-constrained buyers seeking unified communication security suites. Lead with natural language understanding demonstrations that collapse procurement evaluation timelines against rule-based legacy alternatives. For Investors and Strategic Acquirers: API-native specialists with established Microsoft 365 and Google Workspace integration libraries represent the highest-conviction acquisition archetype for platform conglomerates seeking architectural differentiation. Long-term viability hinges on convergence with broader SOC workflows capturing budgets from separate endpoint and network monitoring tools. Watch for quantum-resistant certificate migration mandates as inflection indicators for encryption infrastructure replacement demand.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Deep Microsoft 365 and Google Workspace API integration eliminates gateway latency for mid-market IT teams. |
| Regulatory Compliance Investment | FedRAMP authorization and EU AI Act explainability engineering open government and German banking procurement channels. |
| Managed Detection and Response Bundling | Convergence with SOC workflows captures security operations budgets from separate endpoint monitoring tools. |
| Quantum-Resistant Certificate Migration | NIST post-quantum cryptography standards compel replacement cycles across regulated healthcare and financial services accounts. |
| Continuity Service Expansion | Archiving and disaster recovery capabilities address SEC 17a-4 and FINRA retention requirements within existing accounts. |
Study Parameters
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs, IT procurement officers, platform engineers, and managed security service provider executives. Secondary validation drew from SEC 10-K filings, FedRAMP authorization databases, EU AI Act implementation guidance, and hyperscaler security capex disclosures. Bottom-up deployment counts and top-down addressable market sizing were triangulated to constrain estimation variance.
Calibration against historical adoption curves and regulatory enforcement timelines anchored projection parameters across the analysis window. Segmentation dimensions modeled include service type, deployment architecture, organizational scale, and compliance jurisdiction. CAGRs were derived from fitted growth trajectories incorporating threat volume elasticity and procurement cycle compression effects. Quantum-resistant cryptography transition schedules and NIS2 Directive implementation pacing served as industry-specific forecast inputs.
Sensitivities concentrate around regulatory enforcement intensity, adversarial AI advancement pace, and certificate authority trust events that could compress or extend replacement cycles. Forecasts reflect documented assumptions about migration timelines and compliance interpretation consistency. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Next-Gen Firewall Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Global Serverless Security Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Penetration Testing Market
Cybersecurity
Data Diode Solution Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Retail Cybersecurity Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Cloud Siem Market