
 Application-Level Encryption Market | 2026-2036
Application-Level Encryption Market Size, Share, and Industry Trends Forecast 2026-2036
Application-Level Encryption Market Analysis
Modular bundling of encryption with cloud workload protection is expanding buyer choice across enterprise procurement cycles. Microsoft Corporation leverages its Azure ecosystem to anchor application-level encryption within broader security suites. Thales e-Security specializes in hardware security module integration for high-assurance deployments. Amazon Web Services controls the largest cloud-native encryption deployment base, competing on seamless key management automation.
Application-level encryption refers to cryptographic protection applied directly within software applications rather than at the network or storage tier, typically employing AES-256 or RSA-4096 algorithms with key rotation intervals under ninety days to safeguard data in use, in transit, and at rest. Its primary commercial purpose is to ensure that even infrastructure compromises expose no readable plaintext to attackers. Encryption software and cloud security segments lead current revenue generation, while tokenization and secure messaging represent the fastest-growing sub-areas as enterprises shift from perimeter defense to data-centric security models. On-premises deployment retains dominance in regulated financial services and government verticals, though cloud-based and hybrid configurations capture expanding share among mid-market healthcare and retail adopters seeking operational flexibility without sacrificing compliance posture.
The EU GDPR and the EU AI Act impose strict data protection and algorithmic transparency requirements that directly elevate application-level encryption to a mandatory control. In the United States, HIPAA and SEC cybersecurity disclosure rules compel healthcare and financial entities to demonstrate encryption at the application layer within incident response protocols. Stakeholders must monitor how emerging quantum-resistant algorithms from NIST reshape product roadmaps and procurement specifications across these regulatory frameworks.
Market Dynamics
Zero-trust security architectures now mandate cryptographic protection at the application layer, compelling enterprises to abandon perimeter-based models in favor of data-centric encryption embedded directly within software workflows.
Growth Catalysts
- Federal Zero-Trust Mandates:United States government agencies now require application-level encryption as a non-negotiable procurement specification, driving vendor certification cycles and enterprise adoption benchmarks.
- Healthcare Data Breach Exposure:HIPAA enforcement actions against major hospital networks have elevated encryption from optional safeguard to board-level risk management priority.
- Quantum-Resistant Algorithm Development:NIST's post-quantum cryptography standards are forcing early-mover financial institutions to upgrade legacy encryption infrastructure before regulatory deadlines crystallize.
Market Restraints
- Hardware Security Module Costs:High-assurance deployments require Thales and Entrust HSM integration, adding six-figure capital expenditure per data center.
- Key Management Complexity:Cryptographic key lifecycle management demands specialized personnel that mid-market enterprises struggle to recruit and retain.
- Performance Latency Trade-offs:AES-256 encryption at volume introduces computational overhead that latency-sensitive trading platforms find operationally prohibitive.
Strategic Opportunities
- Mid-Market Healthcare SaaS:Cloud-native encryption bundles targeting regional hospital networks remain undersupplied relative to enterprise-tier solutions.
- EU AI Act Compliance Services:Algorithmic transparency requirements create adjacent revenue streams for encryption vendors offering audit-ready key escrow.
- Confidential Computing Convergence:Integration of application-level encryption with AMD SEV and Intel TDX trusted execution environments opens new workload categories.
Industry Challenges
- Cryptographic Engineering Talent Scarcity:FIPS 140-3 validation requires specialized expertise that vendors compete aggressively to secure.
- Legacy System Integration Friction:Mainframe and AS/400 environments in financial services resist standard API-based encryption deployment patterns.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Application-Level Encryption Market |
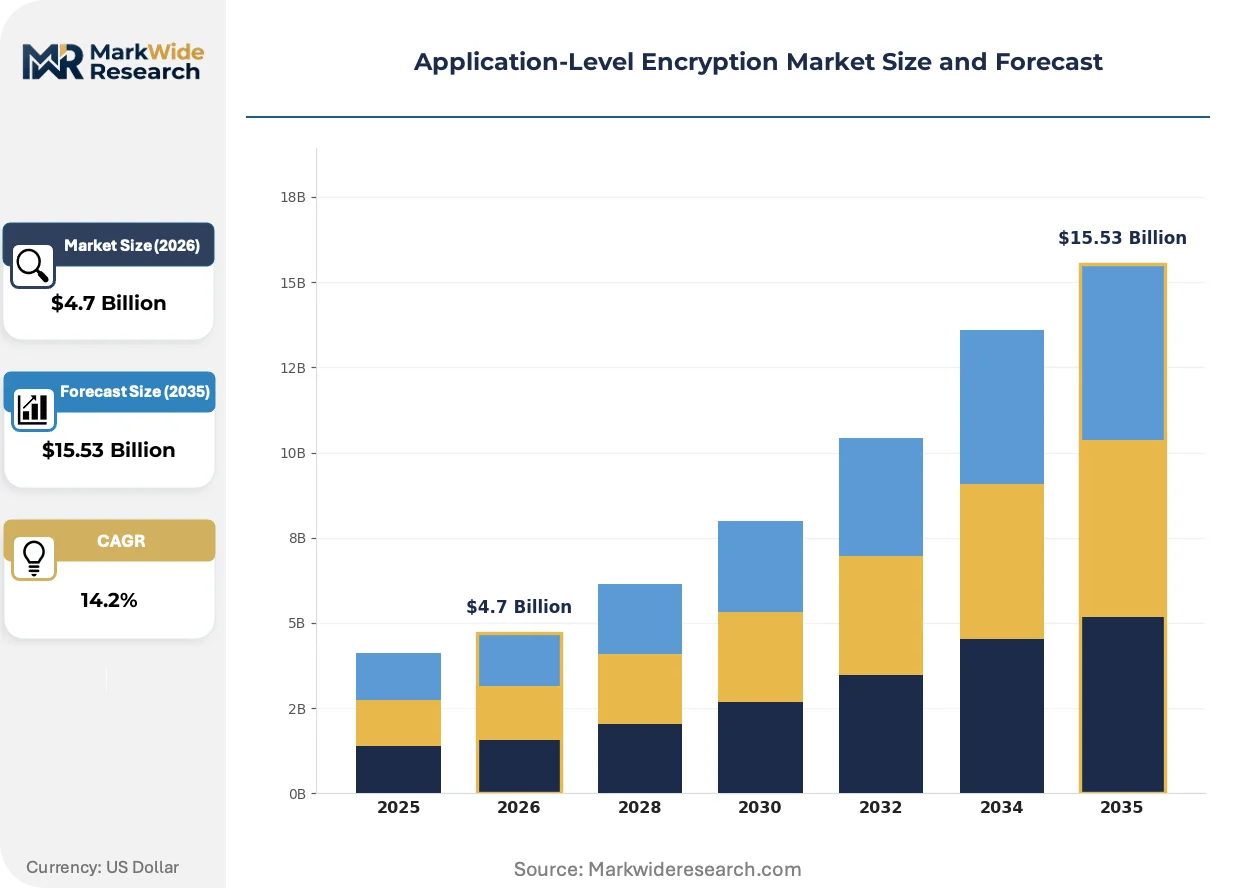
| Market Size in 2026 | $4.7 Billion |
| Market Size in 2035 | $15.53 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
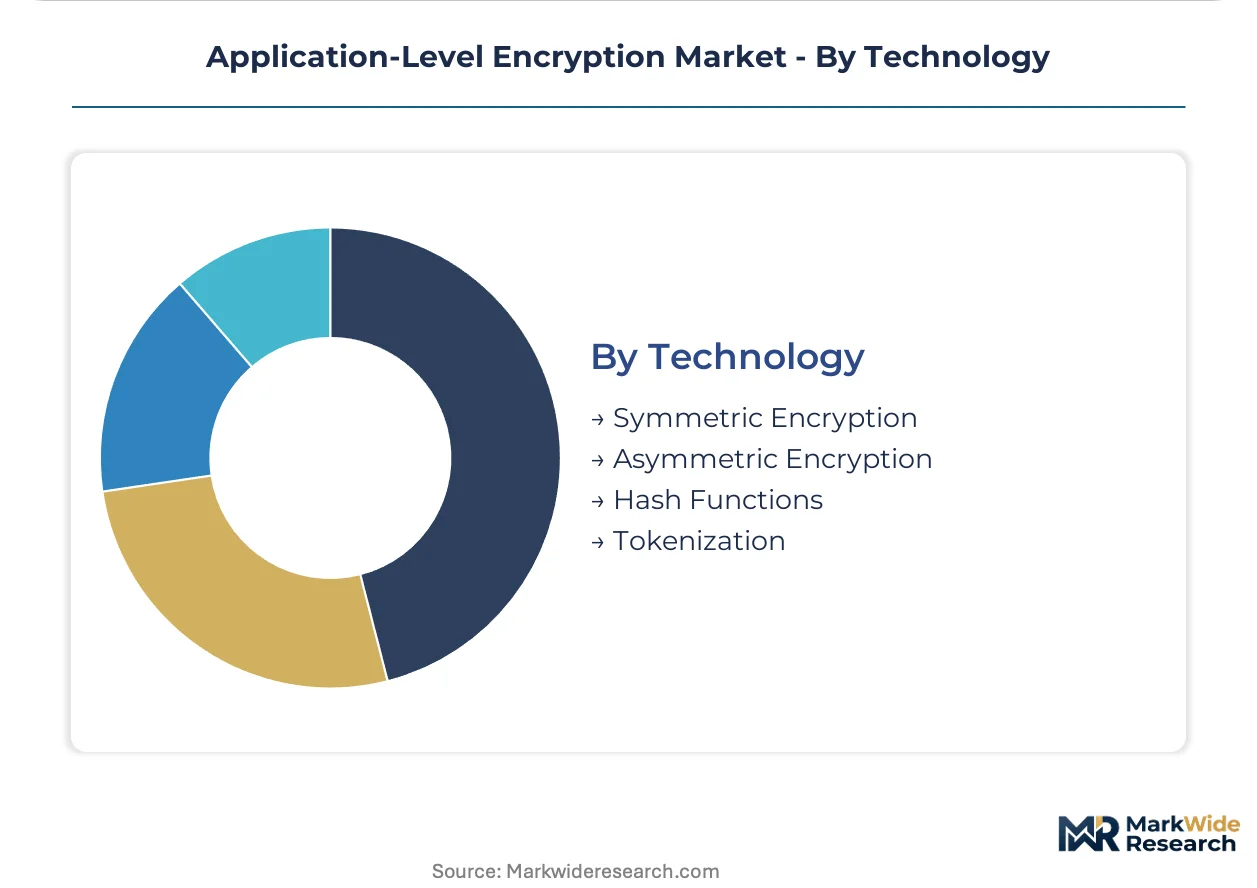
| Segmentation | Product Type: Encryption Software, Data Loss Prevention, Cloud Security, Secure Messaging Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Financial Services, Healthcare, Retail, Government Technology: Symmetric Encryption, Asymmetric Encryption, Hash Functions, Tokenization |
| Companies Covered | Amazon Web Services, Microsoft Corporation, Google LLC, IBM Corporation, Oracle Corporation, Thales e-Security, Symantec Corporation, McAfee, Sophos, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Application-Level Encryption Market Emerging Trajectories
Homomorphic encryption capabilities are migrating from research environments into production financial analytics, enabling computation on encrypted data without decryption exposure.
Format-preserving encryption is integrating tokenization logic directly into payment processing workflows, allowing Visa and Mastercard networks to maintain data utility while stripping sensitive fields. Retail banking adopters in Germany and France are deploying these schemes ahead of PSD3 implementation. The technology is integrating PCI-DSS compliance into real-time transaction authorization without separate token vault infrastructure.
The EU AI Act's risk classification framework is compelling machine learning pipeline operators to encrypt training datasets and model weights as high-risk system requirements take effect. Automotive manufacturers deploying autonomous vehicle algorithms face particular scrutiny from Germany's KBA and France's CNIL. Tier-1 suppliers are responding by embedding encryption into edge inference units before vehicle platform integration.
Enterprise buyers now demand encryption functionality as a standard component of cloud workload protection platforms rather than standalone procurement. Healthcare systems in Texas and California are consolidating vendor relationships around Microsoft and AWS bundles that merge key management with identity governance. This preference compression disadvantages point-solution specialists lacking hyperscaler distribution partnerships.
Application-Level Encryption Market Segmentation

Application-level encryption vendors must navigate divergent certification requirements across product architectures, with FIPS 140-3 validation timelines and HIPAA attestation burdens reshaping portfolio prioritization. Procurement committees now weight segment-specific compliance overhead alongside functional capability during enterprise security stack decisions.
Product Type:
FIPS 140-3 Level 2 certification burdens encryption software and cloud security modules most heavily, while secure messaging solutions face lighter validation cycles under Common Criteria.
- Encryption Software:Deploys AES-256 and RSA-4096 algorithms with key rotation under ninety days, embedded directly into application codebases. Demand concentrates among United States federal contractors responding to zero-trust mandates, where Thales and Entrust HSM integration adds six-figure procurement overhead per deployment.
- Cloud Security:Bundles key management automation with workload protection platforms, competing on seamless Azure and AWS ecosystem integration. Mid-market healthcare systems in Texas and California consolidate vendor relationships around these bundles, merging encryption with identity governance in single procurement cycles.
- Data Loss Prevention:Monitors data exfiltration channels with policy-driven encryption triggers for sensitive field detection.
- Secure Messaging:Protects communications in transit with end-to-end encryption protocols for regulated industry workflows.
Encryption software sits at the top of the volume ranking, with cloud security climbing the fastest.
Deployment Model:
Capital expenditure profiles diverge sharply across deployment architectures, with on-premises installations demanding hardware security module investments that cloud-native alternatives eliminate.
- On-Premises:Retains dominance in regulated financial services and government verticals requiring physical key custody and air-gapped infrastructure. United States federal agencies mandate this architecture for classified systems under zero-trust procurement specifications.
- Cloud-Based:Captures expanding share among mid-market healthcare and retail adopters seeking operational flexibility without sacrificing HIPAA or PCI-DSS compliance posture. AWS controls the largest deployment base, competing on automated key lifecycle management.
- Hybrid:Balances sensitive workload isolation with burst capacity elasticity across on-premises and cloud infrastructure.
- Managed Service:Outsources cryptographic operations to specialized providers, addressing key management talent scarcity in regional hospital networks.
On-premises deployments retain the highest revenue concentration, though cloud-based configurations gain share fastest among new adopters.
End User:
Regulatory enforcement intensity varies dramatically across verticals, with SEC cybersecurity disclosure rules and HIPAA penalty structures elevating encryption to board-level priority in financial and healthcare sectors.
- Financial Services:Institutions embed encryption into transaction workflows as standard procurement requirement, with quantum-resistant algorithm upgrades driven by NIST post-quantum cryptography standards. Major banks face operational latency trade-offs when AES-256 encryption processes high-frequency trading volumes.
- Healthcare:HIPAA enforcement actions against major hospital networks have elevated encryption from optional safeguard to mandatory control. Regional networks in Texas and California now demand cloud-native encryption bundles that merge key management with identity governance.
- Retail:Payment processors deploy format-preserving encryption for PCI-DSS compliance in real-time transaction authorization.
- Government:United States federal zero-trust mandates require application-level encryption as non-negotiable procurement specification.
Financial services command the largest current revenue pool, with healthcare demonstrating the steepest expansion trajectory.
Technology:
Algorithm selection determines performance characteristics and regulatory acceptance, with NIST standardization processes governing enterprise procurement specifications.
- Symmetric Encryption:AES-256 dominates production deployments for data-at-rest protection, offering computational efficiency for high-volume workloads. Financial services institutions standardize on ninety-day key rotation intervals to satisfy internal risk frameworks.
- Tokenization:Integrates format-preserving logic directly into payment processing workflows, allowing Visa and Mastercard networks to maintain data utility while stripping sensitive fields. Retail banking adopters in Germany and France deploy these schemes ahead of PSD3 implementation.
- Asymmetric Encryption:RSA-4096 secures key exchange and digital signature operations across distributed application architectures.
- Hash Functions:Provides data integrity verification without reversible encryption for audit trail and checksum applications.
Symmetric encryption maintains dominant deployment scale, with tokenization expanding most quickly in payment processing modernization.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Application-level encryption emerged from United States defense contractor requirements in the 1990s, spreading through Silicon Valley cloud infrastructure providers before reaching European financial centers and Asian manufacturing hubs. The technology's geographic diffusion now follows regulatory enforcement intensity rather than pure market size.
United States
Federal zero-trust mandates and HIPAA enforcement actions against Texas and California hospital networks drive procurement specifications. SEC cybersecurity disclosure rules compel financial entities to demonstrate encryption within incident response protocols. The Austin-San Antonio corridor hosts expanding cloud security engineering clusters serving mid-market healthcare adopters.
Germany
Automotive manufacturers deploying autonomous vehicle algorithms face scrutiny from KBA regulators demanding encrypted training datasets. The EU AI Act's high-risk system requirements accelerate adoption among Tier-1 suppliers. Bavaria's Munich-Stuttgart industrial corridor embeds encryption into edge inference units before vehicle platform integration.
United Kingdom
Financial services institutions in the City of London embed encryption into transaction workflows as standard procurement requirements. Post-quantum cryptography upgrades follow NIST standards implementation timelines. The Thames Valley technology cluster attracts specialized cryptographic engineering talent for FIPS 140-3 validation work.
France
CNIL enforcement of GDPR data protection obligations elevates application-level encryption to mandatory control status. Retail banking networks deploy format-preserving encryption ahead of PSD3 implementation. The Paris-Saclay research cluster advances homomorphic encryption capabilities for production financial analytics.
Japan
METI guidance on critical infrastructure protection drives encryption adoption among financial and telecommunications operators. Manufacturing supply chain security concerns accelerate deployment in automotive and electronics sectors. The Tokyo-Osaka corridor concentrates cloud-native encryption engineering for hybrid deployment architectures.
Application-Level Encryption Market Vendor Landscape
Premium-margin players sit above commodity-margin players across certification depth and hardware security module integration capabilities. The vendor base stratifies between hyperscale cloud platforms with automated key management and specialized hardware security providers serving high-assurance deployments. Three archetypes dominate: ecosystem-anchored platforms, hardware security specialists, and point-solution encryption vendors. Consolidation pressure favors M&A activity targeting mid-market healthcare SaaS capabilities, while strategic partnerships with confidential computing hardware providers reshape competitive positioning.
Within the ecosystem-anchored tier, Microsoft Corporation and Amazon Web Services represent the dominant cloud-native deployment architectures, with Thales e-Security occupying a position among hardware security module specialists serving regulated financial and government verticals requiring physical key custody.
| Leading Market Players |
|---|
| Amazon Web Services |
| Microsoft Corporation |
| Google LLC |
| IBM Corporation |
| Oracle Corporation |
| Thales e-Security |
| Symantec Corporation |
| McAfee |
| Sophos |
| Others |
Supply Flow & Price Mechanics
FIPS 140-3 validation costs cascade through three pricing tiers, with Level 3 certification adding six-figure overhead per deployment that hyperscalers absorb through volume while point-solution vendors pass through directly. Hardware security module procurement from Thales and Entrust anchors premium tier economics, compressing margins for mid-market entrants lacking cloud-native automation.
Pricing Analysis
Three-tier pricing structure across premium, standard, and economy levels segments buyers by compliance burden and deployment scale. Premium tiers bundle Thales HSM integration with dedicated key custody, while standard tiers compete on Azure and AWS ecosystem anchoring. Cost compression in the economy tier intensifies because mid-market healthcare adopters demand cloud-native bundles without standalone procurement overhead. Regional hospital networks exhibit highest price sensitivity; federal contractors show lowest sensitivity due to mandated zero-trust specifications.
Supply Chain Analysis
FIPS 140-3 validation gates upstream component sourcing, with semiconductor fabrication for cryptographic processors concentrating in Taiwan, South Korea, and the United States. Hardware security module assembly draws from German precision manufacturing and Chinese PCB fabrication. Single-source vulnerability runs through Taiwan's advanced node capacity for secure enclave chips. Distribution runs through hyperscaler marketplaces and specialized cybersecurity channel partners serving regulated verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Application-level encryption functions as a geographic-arbitrage play between United States federal procurement premiums and European regulatory compliance deadlines, with EU AI Act enforcement creating 18-24 month cost advantages for early movers.
For Market Incumbents: Acquire mid-market healthcare SaaS capabilities to defend against hyperscaler bundle compression. Federal zero-trust mandate saturation threatens point-solution margins; vertical integration into confidential computing hardware partnerships with AMD and Intel secures workload category expansion. For New Entrants and Emerging Players: Post-quantum cryptography readiness offers entry into financial services upgrade cycles ahead of NIST standardization crystallization. Mid-market healthcare SaaS in Texas and California remains most penetrable, with algorithmic transparency audit services as the specific go-to-market angle for EU AI Act compliance. For Investors and Strategic Acquirers: Consolidation pressure builds where FIPS 140-3 validation talent scarcity intersects with hyperscaler distribution exclusion. Long-term viability favors vendors with confidential computing hardware partnerships and healthcare SaaS integration depth. The signal to watch is NIST post-quantum cryptography standard finalization triggering enterprise refresh cycles.| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Partnership | AMD SEV and Intel TDX integration opens edge inference workload categories for automotive Tier-1 suppliers. |
| Mid-Market Healthcare SaaS Acquisition | Regional hospital network consolidation demands cloud-native encryption bundles with embedded identity governance. |
| Post-Quantum Cryptography Roadmap | NIST algorithm standardization forces financial services infrastructure upgrades before regulatory deadlines. |
| EU AI Act Compliance Service Launch | Algorithmic transparency requirements from CNIL and KBA create adjacent revenue streams for audit-ready key escrow. |
| Hyperscaler Marketplace Distribution | AWS and Azure ecosystem anchoring compresses procurement cycles for mid-market healthcare and retail adopters. |
Methodological Framework
Direct dialogue with CISOs at financial institutions, healthcare IT directors, federal procurement officers, and cryptographic engineering leads grounded qualitative findings. Secondary validation drew from SEC cybersecurity disclosure filings, HIPAA enforcement action databases, NIST post-quantum cryptography standard drafts, and hyperscaler capex disclosures. Bottom-up deployment modeling and top-down regulatory mandate sizing were triangulated against vendor certification timelines.
Bottom-up segment analysis tracked encryption software, cloud security, tokenization, and secure messaging deployments across on-premises, cloud-based, hybrid, and managed service architectures. Modeled dimensions included deployment model, end-user vertical, technology type, and geographic regulatory cluster. CAGRs were derived from procurement cycle velocity and compliance deadline clustering. Forecast inputs incorporated federal zero-trust mandate implementation pacing and EU AI Act risk classification enforcement sequencing.
The model holds under stable regulatory enforcement intensity; deviation in NIST standardization timelines or HIPAA penalty structure changes would shift enterprise upgrade pacing. Forecasts reflect assumptions about hyperscaler bundle adoption rates and hardware security module cost trajectories. A model refresh is warranted upon material change in federal procurement specification updates or quantum-resistant algorithm deprecation schedules.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Data Center Security Market
Cybersecurity
Internet of Things (IoT) Security Market
Cybersecurity
Content Delivery Network (CDN) Security Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Cloud-Based Database Security Market
Cybersecurity
Global Virtualization Security Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Big Data Security Market
Cybersecurity
Global Information Security Consulting Market
Cybersecurity
Industrial Cybersecurity Market
Cybersecurity
Global Deep Packet Inspection (DPI) Market
Cybersecurity
Managed SIEM Service Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
Australia Cybersecurity Market