
 United States Cybersecurity Market | 2026-2036
United States Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
United States Cybersecurity Market Analytics
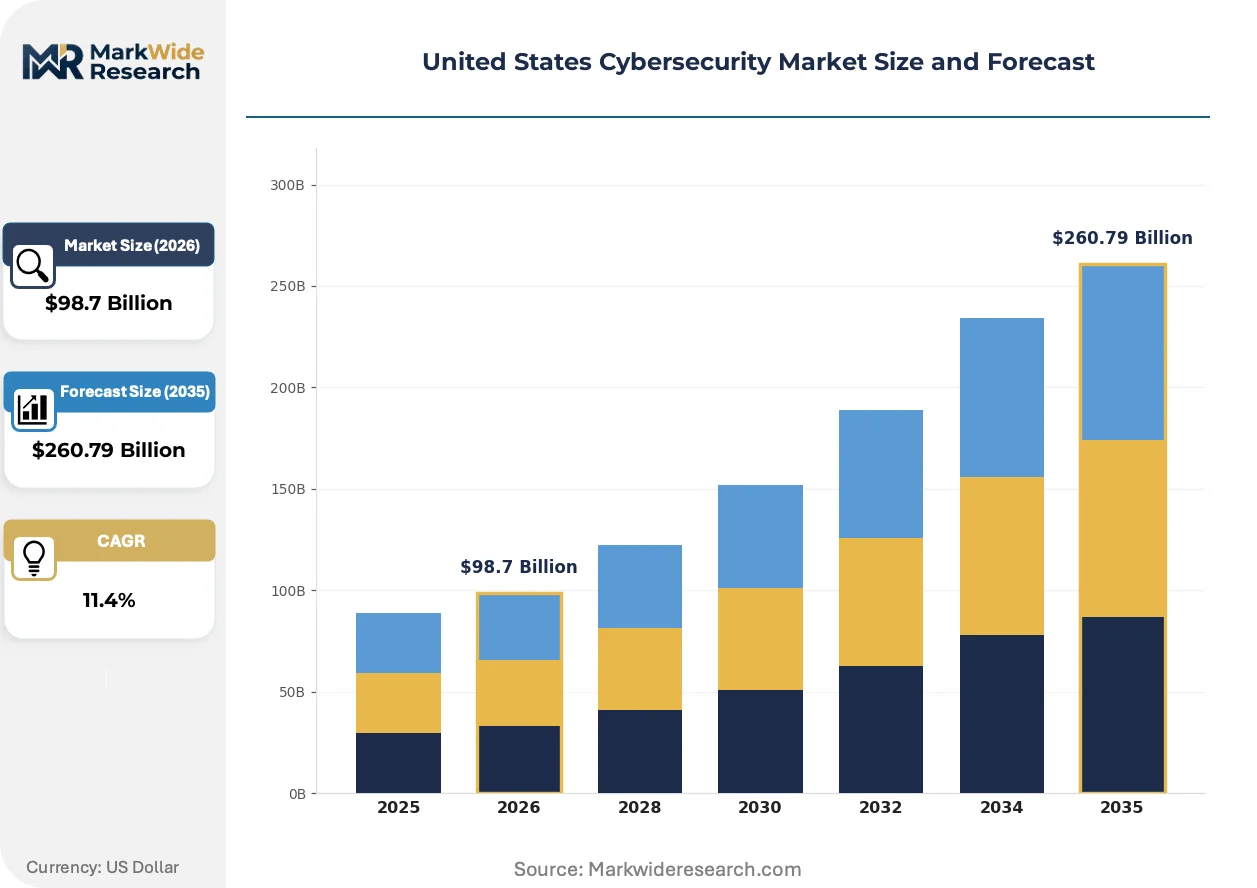
Multi-source procurement of security tools is shifting toward consolidated platform contracts as enterprises reduce vendor sprawl. Palo Alto Networks leverages its integrated Cortex platform to anchor large-scale federal deployments. CrowdStrike Holdings Inc. differentiates through cloud-native endpoint detection with native threat intelligence. Microsoft Corporation dominates identity and access management through Entra and Azure security bundles.
United States cybersecurity encompasses hardware, software, and services designed to protect digital infrastructure from unauthorized access, data exfiltration, and operational disruption, with modern platforms processing telemetry at millisecond granularity to enable real-time threat containment. Cloud Security leads product-type expansion as hybrid work persists, while Managed Services captures margin pools from skills-constrained mid-market buyers. Artificial Intelligence within the technology dimension is maturing fastest, shifting from anomaly detection to autonomous response orchestration.
Federal demand is shaped by NIST, CISA binding operational directives, and SEC cybersecurity disclosure rules that mandate incident reporting and board-level accountability. The Department of Defense CMMC program is tightening supply-chain certification requirements for contractors. Stakeholders must monitor how AI-enabled offensive capabilities reshape defensive architecture requirements and procurement timelines.
Market Dynamics
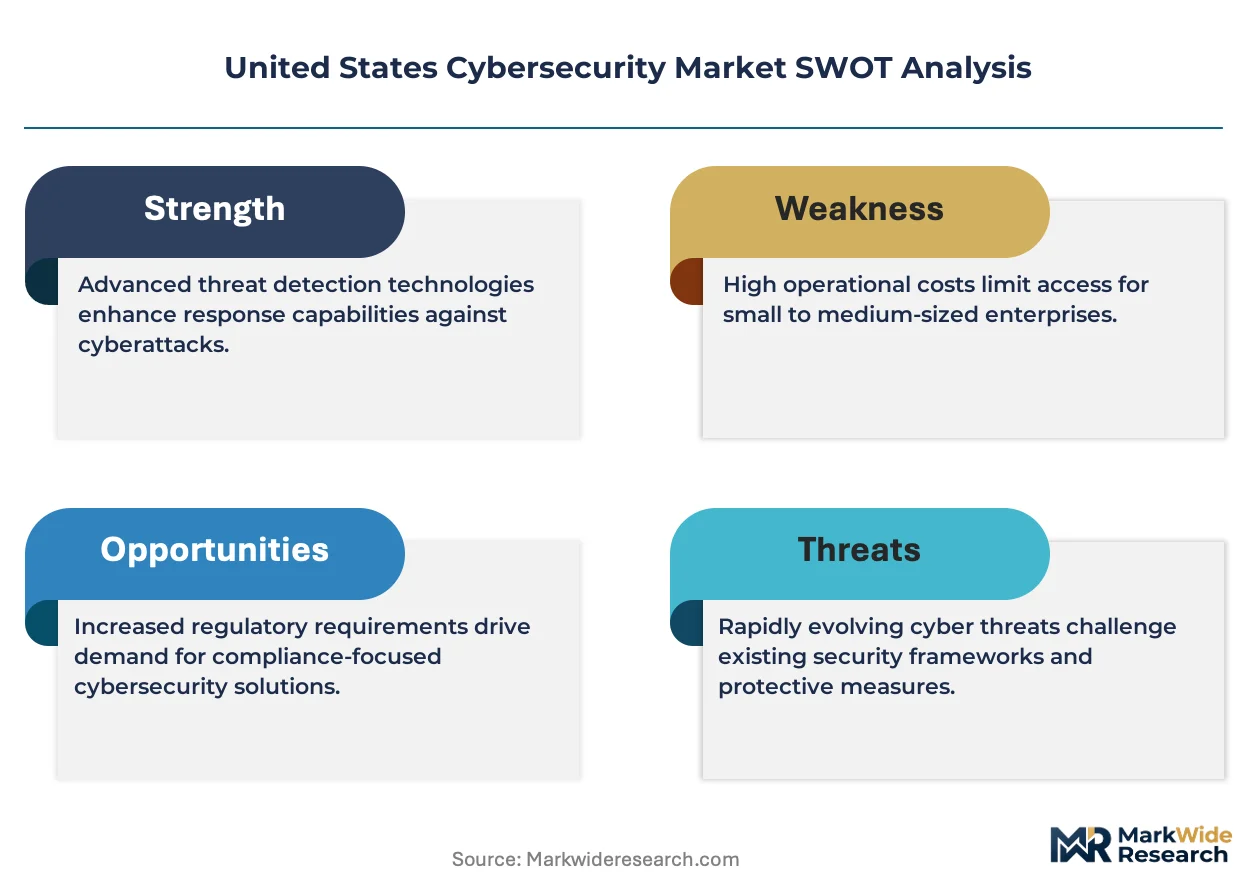
Zero-trust architecture mandates from federal agencies are compressing procurement cycles and forcing vendors to bundle endpoint, cloud, and identity tools into unified platforms rather than point solutions.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Public companies must report material incidents within four business days and disclose board-level oversight structures, accelerating enterprise security spending.
- Critical Infrastructure Operators:Energy utilities and water treatment facilities face CISA binding operational directives requiring segmented network architectures and continuous monitoring.
- AI-Powered Threat Detection:Machine learning models trained on adversarial behavior patterns now process security telemetry at speeds impossible for human analysts alone.
Market Restraints
- Specialized Talent Scarcity:Certified security architects and incident responders command premium compensation that mid-market enterprises cannot match, constraining in-house program maturity.
- Legacy System Interoperability:Decades-old operational technology in manufacturing and energy sectors lacks API connectivity, forcing expensive gateway deployments or risky rip-and-replace decisions.
- Supply Chain Certification Burden:Defense contractors must achieve CMMC Level 2 or 3 certification across their entire subcontractor network, creating administrative bottlenecks.
Strategic Opportunities
- Managed Detection and Response:Skills-constrained organizations in the Midwest manufacturing belt and Southeast healthcare corridor outsource 24/7 security operations to specialized providers.
- Post-Quantum Cryptography:NIST's finalized encryption standards create replacement demand across federal agencies and financial services before cryptographically relevant quantum computers emerge.
- Converged Platform Consolidation:Vendors integrating endpoint detection, cloud security posture management, and identity governance capture larger contract values than standalone tool vendors.
Industry Challenges
- Alert Fatigue and False Positives:Security operations centers drown in thousands of daily alerts, causing analyst burnout and missed genuine intrusions.
- Fragmented Tool Sprawl:Enterprises average dozens of disconnected security products, creating visibility gaps and redundant licensing costs that procurement teams struggle to rationalize.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | United States Cybersecurity Market |
| Market Size in 2026 | $98.7 Billion |
| Market Size in 2035 | $260.79 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Healthcare, Financial Services, Government, Education Technology: Artificial Intelligence, Blockchain, Machine Learning, IoT Security |
| Companies Covered | Palo Alto Networks Inc., Fortinet Inc., Cisco Systems Inc., CrowdStrike Holdings Inc., Microsoft Corporation, IBM Corporation, Broadcom Inc., Check Point Software Technologies Ltd., Zscaler Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
United States Cybersecurity Market Evolving Landscape
Autonomous security response capabilities are moving from experimental to production deployment, compressing the window between threat detection and containment from hours to seconds.
Extended detection and response platforms are electrifying how security teams correlate telemetry across endpoints, networks, and cloud workloads. Large federal contractors and Fortune 500 enterprises are standardizing on these platforms for their 2025-2027 refresh cycles. The technology is electrifying vendor consolidation as point-solution providers face displacement or forced acquisition.
CISA's Secure by Design pledge and binding operational directives now require federal agencies to remove default passwords, provide CVEs within 90 days, and maintain software bills of material. These mandates cascade through defense industrial base contractors who must demonstrate compliance to maintain eligibility. Critical infrastructure operators in the energy and water sectors face the steepest compliance ramps.
Enterprise buyers now demand consumption-based pricing aligned to actual protected assets rather than per-seat licensing. Mid-market healthcare systems and municipal governments lead this shift, pressuring vendors to unbundle professional services from software subscriptions. This model is most visible in California's tech-forward enterprises and Texas's rapidly scaling energy sector.
United States Cybersecurity Market Segmentation
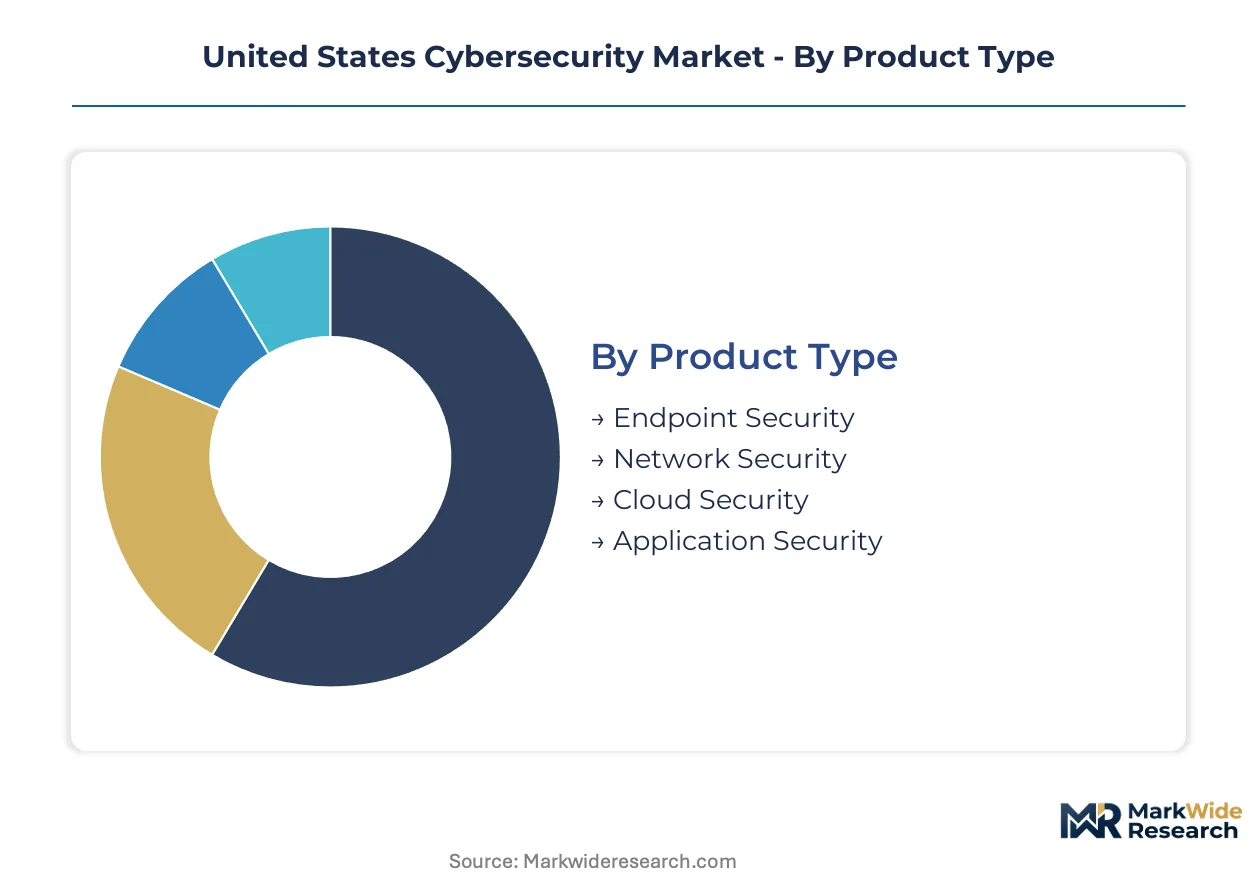
Segmentation reveals how procurement priorities diverge across the United States cybersecurity landscape. Federal mandates, cloud migration velocity, and skills availability reshape which product types and deployment models capture budget allocation in distinct end-use verticals.
Product Type:
Enterprise buyers prioritize integration depth over point-solution functionality when evaluating security investments.
- Endpoint Security:Agent-based protection for laptops, servers, and mobile devices processes behavioral telemetry to block malware execution. Defense contractors in Virginia's Dulles corridor and Maryland's Fort Meade cluster drive demand as CMMC compliance deadlines tighten.
- Cloud Security:Posture management and workload protection for multi-cloud environments scans configurations against CIS benchmarks. California's SaaS vendors and Texas energy firms expanding cloud infrastructure represent the steepest expansion trajectory.
- Network Security:Firewalls and intrusion prevention systems inspect traffic at perimeter and east-west boundaries.
- Application Security:Static and dynamic testing tools identify vulnerabilities in custom code before production deployment.
Endpoint Security leads on scale; Cloud Security leads on momentum.
Deployment Model:
Skills scarcity and compliance complexity determine whether enterprises build internal capabilities or outsource operations.
- Managed Services:Third-party security operations centers deliver 24/7 monitoring, threat hunting, and incident response under SLA-defined metrics. Midwest manufacturing belt buyers in Ohio and Michigan outsource to bridge certified analyst gaps without competing for Silicon Valley compensation levels.
- Cloud-Based:SaaS-delivered security tools scale protection elastically without hardware procurement cycles. Healthcare systems in Florida and Georgia accelerate adoption as HIPAA audit pressures intensify.
- Hybrid:Split architectures maintain sensitive data on-premises while leveraging cloud analytics.
- On-Premises:Air-gapped or self-hosted deployments satisfy classified environment requirements.
Cloud-Based deployments gain share fastest; Managed Services commands premium pricing.
End User:
Regulatory enforcement intensity and asset criticality shape security spending intensity across verticals.
- Government:Federal agencies and state entities operate under binding CISA operational directives mandating zero-trust architecture and continuous monitoring. Washington DC's contracting ecosystem and state capitols in Sacramento, Austin, and Albany concentrate procurement volume.
- Financial Services:Banks, insurers, and payment processors face SEC disclosure rules and FFIEC examination standards. New York's Manhattan financial district and Charlotte's banking hub anchor demand for real-time fraud detection.
- Healthcare:Hospitals and payers balance HIPAA security rule compliance with clinical workflow continuity.
- Education:Universities and K-12 districts protect research IP and student records with constrained IT budgets.
Government leads on compliance-driven spending; Financial Services leads on threat sophistication.
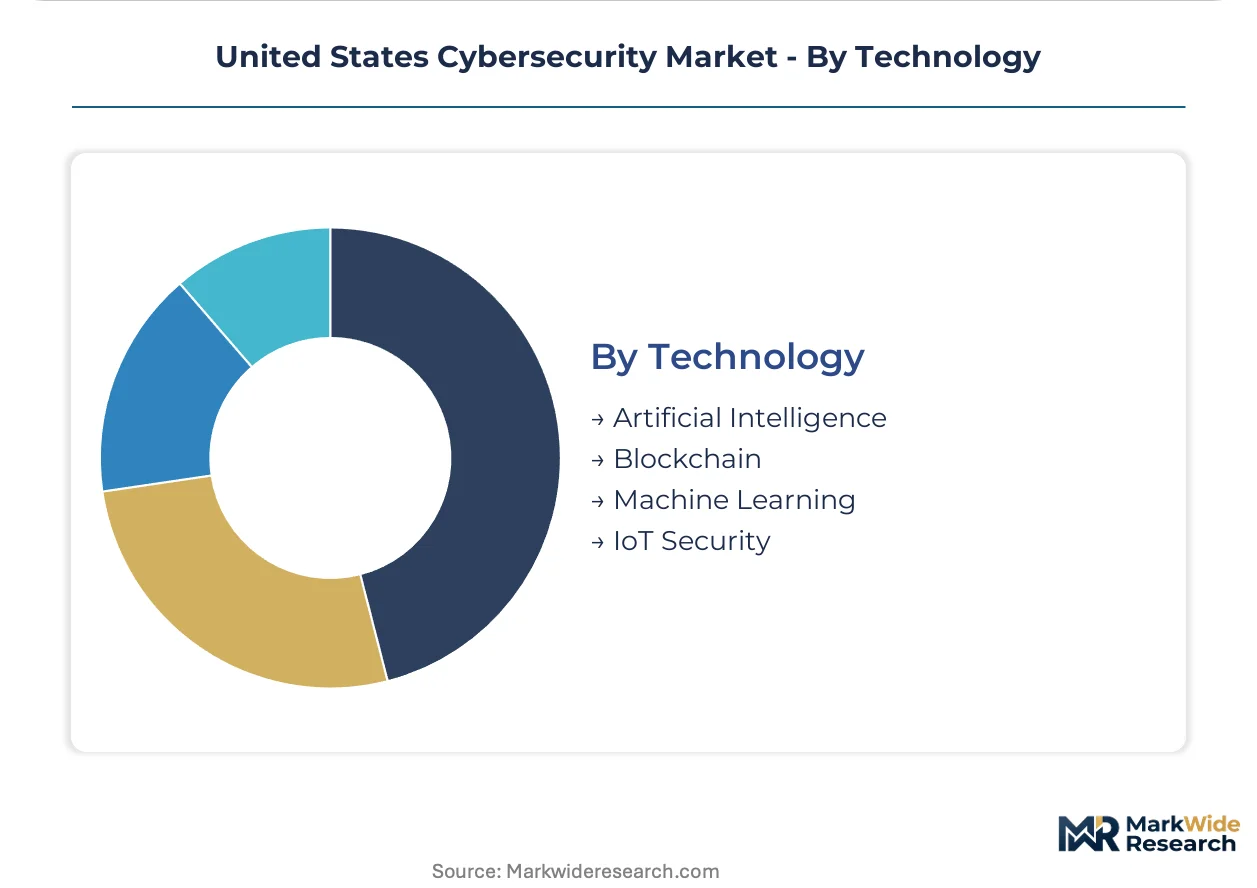
Technology:
Automation maturity separates experimental pilots from production-scale security operations.
- Artificial Intelligence:Autonomous response systems execute containment actions without human approval, compressing dwell time from hours to seconds. Federal R&D contracts through DARPA and In-Q-Tel accelerate vendor development timelines.
- Machine Learning:Behavioral models trained on adversarial patterns prioritize alerts and reduce false positive rates. Large enterprises in Seattle and Boston deploy these tools to address analyst burnout in overloaded security operations centers.
- IoT Security:Agentless discovery and segmentation protects connected devices lacking traditional endpoint protection.
- Blockchain:Distributed ledger applications for identity verification and audit logging remain niche.
Machine Learning leads on current deployment scale; Artificial Intelligence leads on capability advancement.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's tech corridor anchors the nation's cybersecurity demand, with Washington DC's federal contracting hub and Texas's energy sector forming complementary concentration zones across distinct regulatory environments.
California
Cloud-native enterprises and SaaS vendors drive platform consolidation across San Francisco Bay Area and San Jose metro clusters. CISA binding operational directives cascade through state agencies headquartered in Sacramento, accelerating zero-trust procurement cycles. Los Angeles healthcare systems and San Diego defense contractors represent the steepest managed services adoption trajectory.
Virginia and Maryland
Dulles corridor defense contractors and Fort Meade intelligence community facilities demand CMMC Level 2/3 compliant endpoint protection at scale. Department of Defense supply-chain certification mandates compress vendor selection timelines for subcontractors throughout Northern Virginia. Baltimore-Washington corridor cybersecurity operations centers capture federal outsourcing contracts requiring cleared personnel.
Texas
Energy sector operators in Houston and Dallas-Fort Worth face CISA critical infrastructure directives mandating segmented industrial control architectures. State-level data privacy legislation adds compliance layers atop federal requirements for financial services firms expanding in Austin. San Antonio's military intelligence presence anchors specialized threat intelligence demand.
New York
Manhattan financial institutions confront SEC cybersecurity disclosure rules requiring four-day incident reporting and documented board oversight structures. FFIEC examination standards drive real-time fraud detection procurement across Charlotte-competing banking operations in Buffalo and Syracuse. State Department of Financial Services regulations mandate encryption standards exceeding federal baselines.
Massachusetts
Greater Boston's healthcare and biotechnology clusters balance HIPAA security rule compliance with research IP protection across Cambridge and Worcester. Academic medical centers deploy AI-enabled threat detection to address analyst capacity constraints. Route 128 technology corridor vendors serve as regional managed security services providers to Midwest manufacturing clients.
United States Cybersecurity Market Competitive Landscape
Global majors compete with regional champions across platform breadth versus specialization depth, creating a tiered structure where consolidated vendors capture federal contracts while niche players retain mid-market footholds. Network security incumbents, cloud-native challengers, and identity-centric platform builders represent three dominant strategic archetypes. Competitive dynamics center on M&A-driven portfolio expansion and strategic partnerships to bridge capability gaps without organic development timelines.
Within the integrated platform tier, Palo Alto Networks and CrowdStrike Holdings Inc. exemplify converged endpoint-cloud-identity positioning that federal agencies now mandate. Microsoft Corporation anchors the identity-centric vector through Entra and Azure security bundles. These three vendors occupy positions where procurement consolidation favors vendors reducing vendor sprawl over point-solution specialists.
| Leading Market Players |
|---|
| Palo Alto Networks Inc. |
| Fortinet Inc. |
| Cisco Systems Inc. |
| CrowdStrike Holdings Inc. |
| Microsoft Corporation |
| IBM Corporation |
| Broadcom Inc. |
| Check Point Software Technologies Ltd. |
| Zscaler Inc. |
| Others |
Value Network & Pricing Analysis
Horizontal integration across cloud infrastructure providers anchors both supply positioning and pricing power in the United States cybersecurity market, as hyperscaler partnerships determine platform delivery economics and federal procurement eligibility. Bundled subscription models compress standalone vendor margins while rewarding consolidated platform players with multi-year contract visibility.
Pricing Analysis
Input-cost pass-through from certified security analyst labor and cloud compute infrastructure shapes vendor pricing structures across the United States cybersecurity landscape. Three-tier pricing structure across premium, standard, and economy levels separates federal-compliant deployments from mid-market SaaS bundles and basic endpoint protection. Pricing pressure stems from procurement consolidation mandates that favor platform breadth over point-solution depth. Mid-market healthcare systems and municipal governments exhibit highest price sensitivity, while defense contractors prioritize CMMC certification over cost minimization.
Supply Chain Analysis
Threat intelligence feed supply rests on specialized data brokers concentrated in the United States, Israel, and the United Kingdom, with adversarial signature databases and dark web monitoring services as critical inputs. Cloud infrastructure dependencies center on AWS, Azure, and Google Cloud compute capacity for security operations center platforms. Single-source vulnerability in cleared personnel pipelines for federal contracts creates bottlenecks for vendors serving intelligence community facilities. Distribution runs through value-added resellers holding federal procurement certifications and direct enterprise sales teams for Fortune 500 accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The United States cybersecurity market functions as a stable compounder, with regulatory compliance mandates from CISA and SEC disclosure rules generating recurring procurement cycles that outpace discretionary IT spending volatility.
For Market Incumbents: Anchor federal contract eligibility through accelerated CMMC certification investments across subcontractor networks, countering emerging cloud-native challengers that lack cleared personnel infrastructure. Deepen platform integration between endpoint detection, cloud security posture management, and identity governance to capture procurement consolidation mandates that displace standalone tool vendors.
For New Entrants and Emerging Players: Launch via consumption-based pricing models targeting Midwest manufacturing belt buyers constrained by Silicon Valley compensation benchmarks for in-house security operations. Penetrate managed detection and response services for municipal governments and regional healthcare systems, leveraging channel partnerships with existing IT managed service providers rather than building direct sales infrastructure.
For Investors and Strategic Acquirers: Roll-up economics work for specialized threat intelligence and identity governance vendors because federal zero-trust mandates create forced-replacement demand for legacy authentication systems. Five-to-ten year viability hinges on AI-enabled autonomous response capabilities that compress detection-to-containment windows. Monitor CISA binding operational directive expansion into additional critical infrastructure verticals as inflection indicator for sector-wide procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified endpoint-cloud-identity bundles capture federal zero-trust procurement mandates displacing point solutions. |
| CMMC Certification Investment | Level 2/3 compliance unlocks Department of Defense supply-chain contracts requiring cleared personnel infrastructure. |
| Consumption-Based Pricing Launch | Asset-aligned subscriptions attract mid-market healthcare and municipal buyers avoiding per-seat licensing complexity. |
| Strategic Partnership | Hyperscaler alliances with AWS and Azure accelerate federal deployment timelines through pre-authorized environments. |
| Acquisition of Specialist Firm | Threat intelligence and identity governance targets fill portfolio gaps without organic development delays. |
Research Methodology
Direct dialogue with CISOs at Fortune 500 enterprises, federal procurement officers, managed security services executives, and cloud infrastructure architects grounded qualitative findings in operational reality. Secondary validation drew from SEC cybersecurity disclosure filings, CISA binding operational directives, CMMC program documentation, and hyperscaler security service revenue disclosures. Bottom-up and top-down triangulation reconciled vendor-reported bookings with federal contract award databases and enterprise IT spending surveys.
Bottom-up modeling aggregated segment-level demand across endpoint security, cloud security posture management, identity governance, and managed detection and response services, then cross-checked against top-down macroeconomic and regulatory spend assumptions across the projection horizon. Deployment model, organization size, vertical regulatory intensity, and integration complexity shaped segmentation boundaries. CAGRs derived from historical procurement cycle analysis and mandated compliance deadline schedules, with AI-enabled capability maturation curves as industry-specific forecast inputs.
Forecast precision tightens around the base case; tail outcomes carry wider variance under accelerated quantum computing timelines or expanded CISA critical infrastructure designations. Forecasts reflect assumptions about regulatory enforcement consistency and federal budget continuity. Material deviation in CMMC implementation pace or SEC disclosure rule litigation warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
India Cybersecurity Market
Cybersecurity
Cyber Security As a Service Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
5G Security Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Corporate Web Security Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
China Cybersecurity Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Application-Level Encryption Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
New Zealand Cybersecurity Market
Cybersecurity
Digital Security Market