
 Denmark Cybersecurity Market | 2026-2036
Denmark Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Denmark Cybersecurity Market Outlook
A capital-intensity divergence between managed security service providers and product-centric vendors is redrawing competitive boundaries in Danish cybersecurity. Netic A/S leverages its domestic data center footprint to anchor high-assurance contracts with public-sector clients. Fortinet competes through integrated hardware-software stacks that reduce operational overhead for mid-market enterprises. CSIS Security Group specializes in threat intelligence services that command premium pricing from financial institutions.
Cybersecurity encompasses technologies, processes, and controls designed to protect systems, networks, and data from digital attacks, with specifications including AES-256 encryption standards, zero-trust architecture protocols, and real-time SIEM (Security Information and Event Management) processing latencies under 100 milliseconds. Its primary commercial purpose is to ensure confidentiality, integrity, and availability of information assets across enterprise and government operations. Network security solutions occupy the largest installed base among Danish enterprises due to legacy infrastructure dependencies, while cloud security demonstrates the fastest expansion as organizations migrate workloads to Microsoft Azure and AWS regions serving Northern Europe. Managed services capture disproportionate margin pools because Danish buyers prioritize operational transfer of risk over capital-intensive in-house security operations centers.
The Danish Business Authority enforces NIS2 transposition requirements that mandate incident reporting within 24 hours for essential and important entities, directly expanding addressable demand for managed detection and response capabilities. The Danish Data Protection Agency applies GDPR penalties that have reached substantial levels, compelling retail and healthcare end users to invest in data-loss prevention and encryption solutions. ISO 27001 certification serves as a de facto market access credential for vendors serving critical national infrastructure operators. Stakeholders must weigh whether to build sovereign cloud security capabilities or partner with Nordic-focused hyperscale providers as regulatory fragmentation between EU frameworks and national implementation deepens.
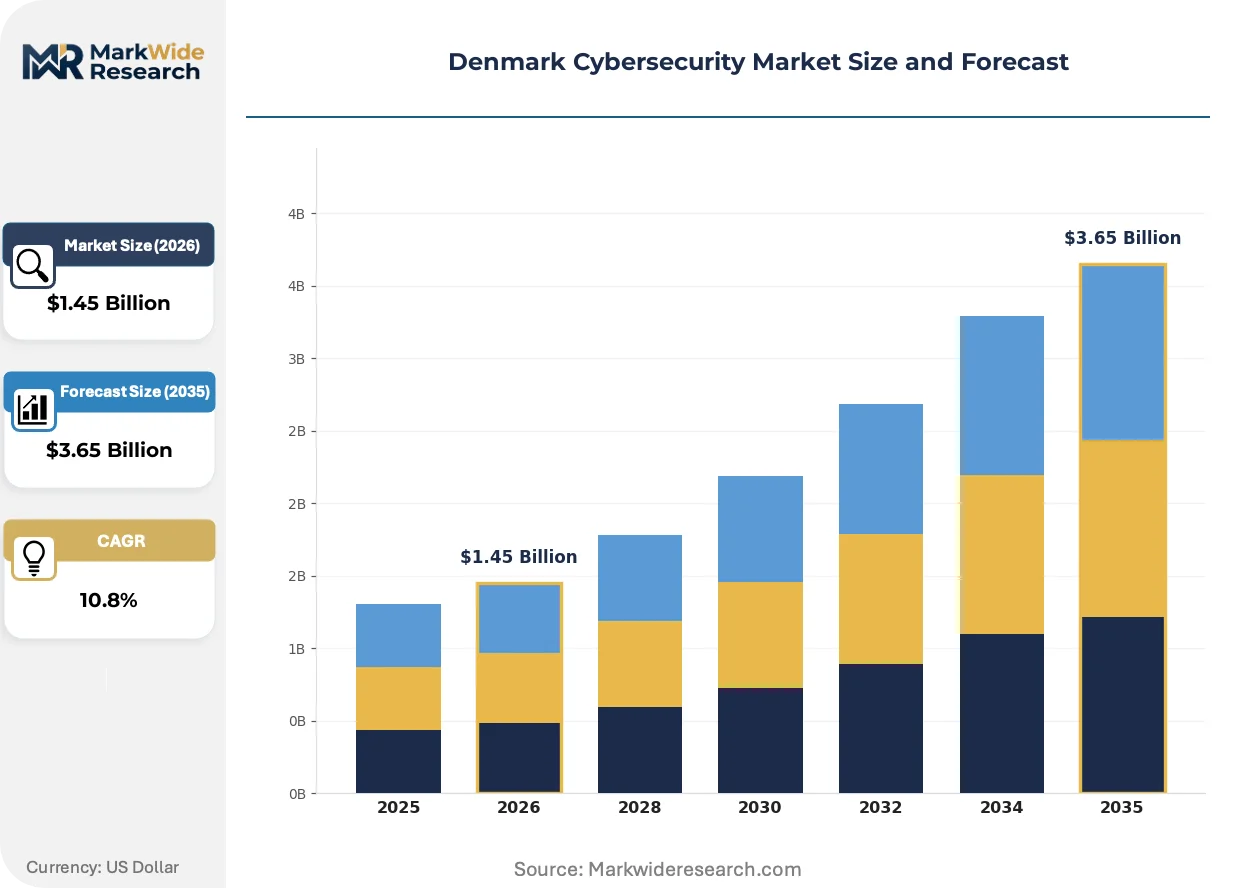
Market Dynamics
The EU NIS2 Directive's transposition into Danish national law is compressing procurement cycles for managed detection and response services while mandating 24-hour incident reporting windows that legacy security operations cannot satisfy.
Growth Catalysts
- NIS2 Compliance Mandates:The Danish Business Authority enforces stricter operational resilience requirements for essential and important entities, directly expanding contract volumes for incident response retainers.
- Financial Services Modernization:Copenhagen's fintech cluster is migrating core workloads to Microsoft Azure and AWS Northern Europe regions, generating concentrated demand for cloud-native security architectures.
- GDPR Penalty Exposure:The Danish Data Protection Agency's enforcement actions have elevated data-loss prevention and encryption to board-level priorities across retail and healthcare verticals.
Market Restraints
- Specialized Talent Scarcity:Domestic supply of certified security architects and SOC analysts trails demand by a structural margin, inflating personnel costs for managed service providers.
- Hyperscale Dependency:Critical cloud security capabilities rely on Azure and AWS infrastructure concentrated in Ireland and Sweden, creating jurisdictional risk for sovereign data requirements.
- Legacy Network Inertia:Deep installed bases of perimeter-based firewalls and on-premise SIEM deployments slow zero-trust architecture rollouts in established enterprises.
Strategic Opportunities
- Critical Infrastructure Vertical:Energy and transport operators face NIS2 designation thresholds that expand addressable demand for OT security and industrial control system monitoring.
- AI-Augmented Threat Detection:Convergence of machine learning inference with SIEM platforms enables predictive response capabilities that command premium pricing from financial institutions.
- Sovereign Cloud Partnerships:Regulatory fragmentation between EU frameworks and Danish national implementation creates white space for Nordic-focused data center operators to anchor high-assurance contracts.
Industry Challenges
- ISO 27001 Certification Timelines:Vendors serving critical national infrastructure operators face extended audit cycles that delay market entry and compress bid windows.
- Multi-Cloud Integration Complexity:Enterprises operating across Azure, AWS, and private cloud environments struggle with unified policy enforcement and identity federation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Denmark Cybersecurity Market |
| Market Size in 2026 | $1.45 Billion |
| Market Size in 2035 | $3.65 Billion |
| CAGR (2026 – 2036) | 10.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Security, Network Security, Cloud Security, Application Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, Healthcare, Financial Services, Retail Service Type: Consulting, Implementation, Managed, Training |
| Companies Covered | Netic A/S, Fortinet, Factosecure, Cisco Systems, IBM Corporation, CSIS Security Group, Check Point Software Technologies, NNIT A/S, Logpoint, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Denmark Cybersecurity Market Strategic Shifts
Security service delivery models are splitting between high-touch managed detection and automated platform offerings, with buyer sophistication determining which path dominates procurement decisions.
Extended detection and response platforms consolidate endpoint, network, and cloud telemetry into unified attack surface visibility. Danish mid-market enterprises are adopting these solutions faster than large-cap peers due to leaner internal security teams. The technology is bifurcating vendor strategies between pure-play software vendors and managed service wrappers that bundle human analysts with platform licenses.
The EU AI Act's risk classification framework imposes documentation and transparency obligations on automated threat detection systems deployed in critical infrastructure. Danish cybersecurity vendors must now maintain algorithmic audit trails and human oversight protocols for machine learning models used in SOC workflows. Financial services institutions are responding by demanding contractual indemnification for AI-driven false positives that trigger incident response costs.
Danish buyers are consolidating vendor relationships and prioritizing operational transfer of risk over capital-intensive in-house security operations center builds. Managed security service providers are displacing point product vendors in multi-year contracts that bundle detection, response, and recovery obligations. This concentration is most visible in Copenhagen's fintech cluster, where venture-backed firms favor subscription-based security consumption to preserve balance sheet flexibility.
Denmark Cybersecurity Market Segmentation
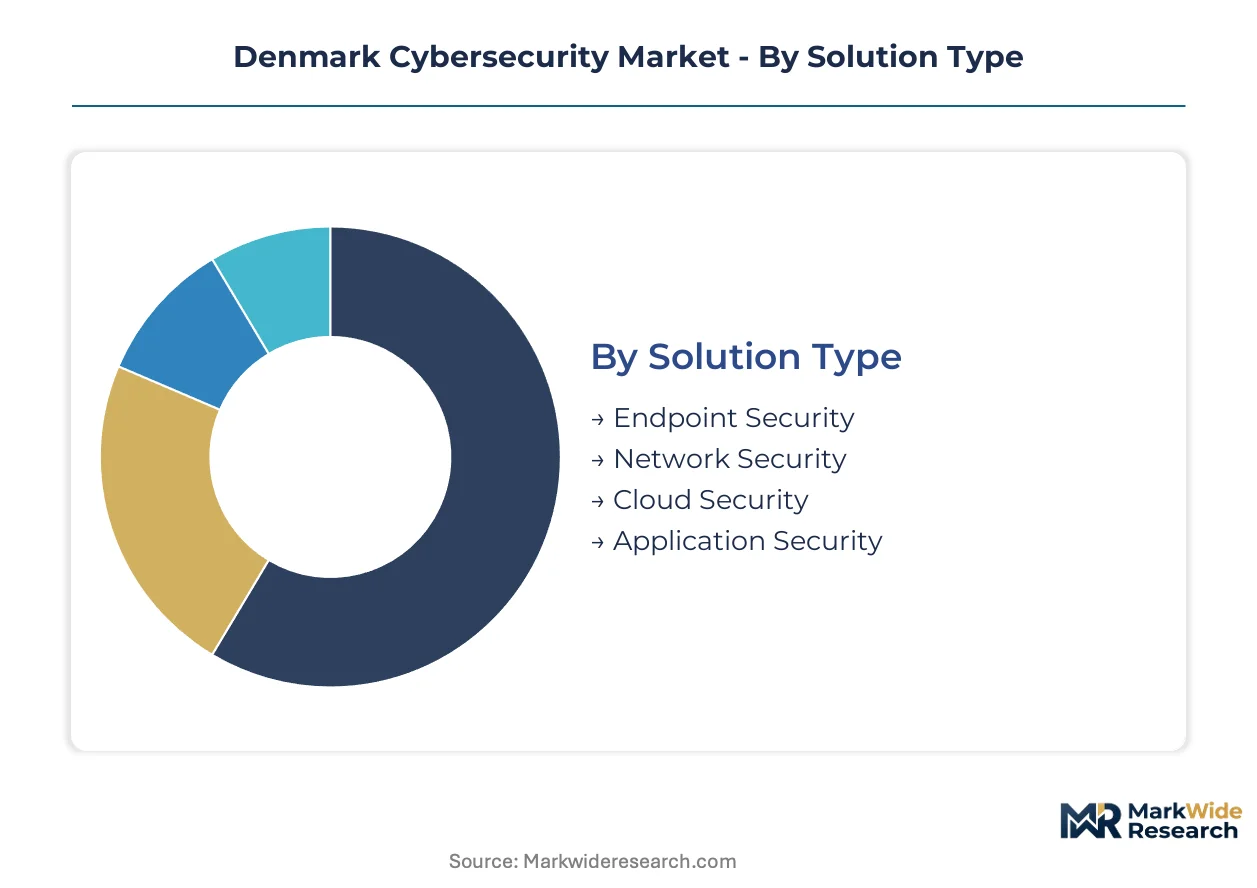
Segmentation in the Danish cybersecurity market reveals how NIS2 compliance pressures and cloud migration patterns reshape procurement priorities across solution architectures and service delivery models. Buyers concentrate spending where regulatory mandates intersect with operational risk transfer preferences.
Solution Type:
Domestic demand clusters around legacy-compatible platforms while export-oriented vendors push cloud-native architectures. Copenhagen's fintech cluster drives differential adoption patterns.
- Endpoint Security:Agent-based protection for laptops, servers, and mobile devices with EDR capabilities. Danish healthcare networks concentrate procurement here due to dispersed clinical workstations and BYOD policies. GDPR penalty exposure elevates encryption and data-loss prevention modules to mandatory status.
- Network Security:Firewalls, intrusion detection systems, and secure access service edge platforms. Financial services institutions in Copenhagen maintain the largest installed base, though perimeter-centric designs create friction with zero-trust mandates. Legacy refresh cycles compress as NIS2 deadlines approach.
- Cloud Security:Workload protection, CASB, and cloud-native application protection platforms. Danish enterprises migrating to Azure and AWS Northern Europe regions generate concentrated demand for shared-responsibility alignment.
- Application Security:Static and dynamic testing tools, software composition analysis, and runtime protection. DevSecOps adoption in Copenhagen's venture-backed fintech firms outpaces established enterprises.
Network Security commands the established base. The steepest expansion runs through Cloud Security.
Deployment Model:
Cost tier differentiation separates capital-intensive builds from operational expenditure models, with mid-market buyers favoring subscription structures.
- On-Premises:Hardware appliances and perpetual-license software deployed within customer data centers. Critical national infrastructure operators in energy and transport sectors mandate this model for sovereign control. Extended procurement cycles and skilled maintenance requirements constrain adoption.
- Cloud-Based:SaaS-delivered security platforms with elastic scaling. Copenhagen fintech startups prefer this model for balance sheet flexibility and rapid provisioning. Shared-tenant architectures raise data residency questions under Danish Data Protection Agency guidance.
- Hybrid:Orchestrated policies across on-premise and cloud workloads. Enterprises with legacy SIEM investments use this bridge architecture during multi-year migration programs. Complexity in unified policy enforcement creates implementation bottlenecks.
- Managed Services:Outsourced SOC operations with contractual response obligations. Danish buyers prioritize operational risk transfer over in-house capability builds. Netic A/S and domestic MSSPs capture public-sector contracts through sovereign data center footprints.
Managed Services is gaining share fastest as procurement shifts from capital to operational expenditure models.
End User:
Application-specific requirements drive divergent technology priorities, with regulated verticals commanding premium pricing.
- Government:Central and municipal agencies with critical infrastructure designations. The Danish Business Authority's NIS2 enforcement mandates 24-hour incident reporting windows that legacy operations cannot satisfy. Sovereign cloud requirements favor domestic data center operators.
- Healthcare:Hospitals, clinics, and digital health platforms. GDPR penalties from the Danish Data Protection Agency have elevated encryption and access control to board-level priorities. Interoperability requirements with regional health networks complicate security architecture decisions.
- Financial Services:Banks, insurers, and Copenhagen's venture-backed fintech cluster. Basel operational resilience guidelines intersect with NIS2 mandates to demand predictive threat detection capabilities. AI-augmented SIEM platforms command premium pricing here.
- Retail:E-commerce platforms and physical store networks with omnichannel data flows. Payment card industry compliance overlaps with GDPR to drive point-of-sale encryption and customer data platform security investments.
Financial Services commands the established base. Healthcare shows the steepest expansion trajectory as GDPR enforcement intensifies.
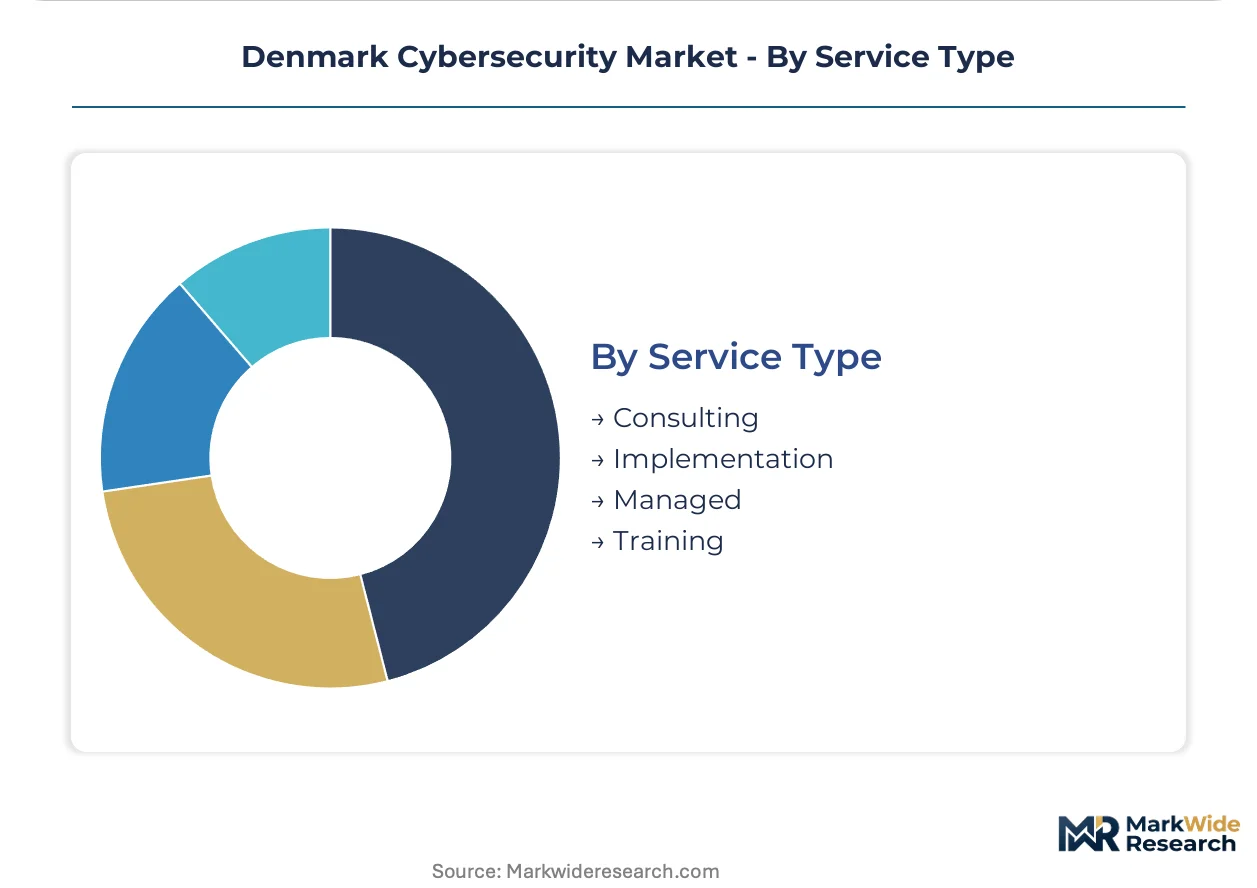
Service Type:
Customer maturity determines whether buyers seek advisory engagement or full operational takeover, with Danish preferences shifting toward the latter.
- Consulting:Risk assessments, architecture design, and compliance readiness programs. ISO 27001 certification preparation for critical infrastructure vendors generates sustained demand. Audit timelines extend market entry delays for new service providers.
- Implementation:Deployment, integration, and migration services. Multi-cloud environments across Azure, AWS, and private infrastructure create complexity premiums. Danish enterprises with lean IT teams outsource integration to avoid project failure risk.
- Managed:Ongoing monitoring, detection, and response operations. The Danish Business Authority's NIS2 reporting mandates expand contract volumes for MDR retainers. Domestic MSSPs differentiate through 24/7 Danish-language SOC analysts.
- Training:Security awareness programs and certification preparation. Specialized talent scarcity elevates internal capability building as a complementary spend to technology procurement.
Implementation services anchor the established base. Managed services climb the fastest as operational risk transfer preferences harden.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Danish cybersecurity procurement shows sharp demand-elasticity contrasts. Copenhagen's venture-backed fintech cluster absorbs premium pricing for cloud-native architectures, while municipal governments in peripheral regions prioritize cost-efficient managed service bundles.
Capital Region
Copenhagen anchors Denmark's cybersecurity demand through its dense fintech and pharmaceutical headquarters concentration. The Danish Business Authority's NIS2 enforcement mandates compress procurement cycles for incident response retainers. Microsoft Azure and AWS Northern Europe regions serve workloads from Ørestad's data center cluster, generating concentrated cloud security contract volumes.
Central Denmark Region
Aarhus drives healthcare cybersecurity spending through its university hospital network and digital health startup ecosystem. GDPR penalties from the Danish Data Protection Agency have elevated encryption procurement to mandatory status for patient data platforms. The city's robotics and automation industrial base creates specialized OT security demand for manufacturing control systems.
North Denmark Region
Aalborg's energy sector concentration exposes critical infrastructure operators to NIS2 designation thresholds. The Danish Energy Agency coordinates sector-specific resilience requirements that expand addressable demand for industrial control system monitoring. Offshore wind farm digitalization projects in the Kattegat generate marine-telemetry security contracts.
Southern Denmark Region
Odense's manufacturing base and port logistics operations sustain mid-market enterprise security spending. Lean IT teams across industrial SMEs favor subscription-based managed detection services over capital-intensive SOC builds. The Great Belt strait's maritime traffic control systems require sovereign data center hosting for regulatory compliance.
Zealand Region
Roskilde and Køge municipal governments consolidate procurement through shared service agreements that favor domestic MSSPs with Danish-language support capabilities. Educational institutions across the region drive endpoint security volumes through dispersed student and faculty device populations. ISO 27001 certification requirements for public-sector vendors extend sales cycles for new market entrants.
Denmark Cybersecurity Market Competitive Environment
A small set of integrated leaders sits above a broader specialist tier that captures margin pools through vertical-specific expertise. The Danish market structures around three archetypes: domestic MSSPs leveraging sovereign data center footprints, multinational platform vendors with hardware-software integration, and boutique threat intelligence specialists commanding premium pricing from financial institutions. Competitive moves concentrate on multi-year managed service contract consolidation and NIS2 compliance certification acceleration.
Among Denmark-based operators, Netic A/S anchors the domestic MSSP archetype through public-sector relationships requiring sovereign data residency. Fortinet occupies the integrated platform tier with hardware-software stacks that reduce operational overhead for mid-market enterprises. CSIS Security Group exemplifies the specialist vector through threat intelligence services that command premium retention from Copenhagen's financial institutions.
| Leading Market Players |
|---|
| Netic A/S |
| Fortinet |
| Factosecure |
| Cisco Systems |
| IBM Corporation |
| CSIS Security Group |
| Check Point Software Technologies |
| NNIT A/S |
| Logpoint |
| Others |
Value Chain & Pricing Dynamics
Hyperscale infrastructure utilization in Ireland and Sweden anchors cost structures for Danish cloud security providers, concentrating supply-side leverage among Nordic data center operators while compressing price floors for mid-market SaaS offerings. This scale dynamic feeds directly into procurement patterns where Copenhagen's fintech cluster absorbs premium pricing for sovereign-hosted alternatives.
Pricing Analysis
Managed detection and response retainers drive lifetime value through multi-year contractual obligations that bundle human analyst coverage with platform licensing. Subscription tiers stratify across premium SOC-as-a-service, standard co-managed detection, and economy alert-only monitoring levels, with NIS2 compliance certification commanding material premiums. Price compression runs through standard-tier offerings as domestic MSSPs expand capacity. Municipal governments in peripheral Zealand regions exhibit highest price sensitivity; financial institutions in Copenhagen's Ørestad cluster demonstrate lowest.
Supply Chain Analysis
Just-in-time provisioning dominates cloud security delivery, though critical infrastructure operators maintain strategic stockpiles of on-premise hardware for sovereign control requirements. Core platform development concentrates in the United States, Israel, and Ireland, with threat intelligence feeds sourcing from Estonia and the United Kingdom. Danish vendors depend on Azure and AWS Northern Europe regions for elastic compute, creating single-source vulnerability to hyperscale pricing adjustments. Distribution runs through direct enterprise sales for large accounts and domestic MSSP channel partnerships for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating among Copenhagen's venture-backed fintech cluster as procurement consolidates around multi-year managed service contracts, fragmenting point-product vendor influence.
For Market Incumbents: Consolidate around NIS2 compliance certification acceleration to anchor public-sector relationships before the Danish Business Authority hardens enforcement thresholds. Absorb specialist threat intelligence capabilities through targeted capability acquisition rather than organic build, as boutique providers like CSIS Security Group command irreplaceable financial services retention. Sovereign data center capacity expansion in Denmark proper—not Nordic outsourcing—represents the priority defensive lever. For New Entrants and Emerging Players: Lead with OT security specialization targeting Aalborg's energy sector and North Denmark offshore wind operators, where NIS2 designation thresholds expand addressable demand faster than saturated IT security verticals. The critical infrastructure segment remains penetrable due to extended ISO 27001 certification timelines delaying established vendor entry. A go-to-market angle anchored in Danish-language 24/7 SOC operations with marine-telemetry expertise bypasses hyperscale provider limitations. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among domestic MSSPs with sovereign data center footprints and public-sector contract backbones, offering visibility across a 5-10 year regulatory enforcement horizon. Acquisition targets should display vertical integration into Danish-language analyst pools rather than pure platform licensing. The signal to watch is Danish Business Authority staffing levels for NIS2 audit capacity, which dictates compliance service demand inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Managed Detection and Response Platform Launch | Captures NIS2-mandated 24-hour incident reporting contracts from Danish Business Authority-designated entities. |
| Sovereign Cloud Partnership | Secures high-assurance positioning against Azure and AWS jurisdictional risk for critical infrastructure operators. |
| Acquisition of OT Security Specialist | Addresses Aalborg energy sector demand for industrial control system monitoring under NIS2 thresholds. |
| ISO 27001 Certification Acceleration | Compresses market entry timelines for vendors serving Danish critical national infrastructure operators. |
| AI-Augmented SIEM Integration | Commands premium pricing from Copenhagen fintech institutions facing Basel operational resilience guidelines. |
Study Parameters
A standing panel of CISOs at Danish financial institutions, public-sector procurement officers, MSSP operations directors, and Danish Data Protection Agency enforcement leads provided ongoing calibration across primary interview cycles. Secondary validation drew from Danish Business Authority regulatory filings, EU NIS2 implementation guidance documents, Azure and AWS Northern Europe region capex disclosures, and ISO 27001 certification registry data. Bottom-up contract value aggregation and top-down market sizing triangulated volume estimates.
Consistency checks against external benchmarks validated output plausibility across the projection horizon. The analytical framework modeled segmentation across solution architecture, deployment model, end-user vertical, and service delivery type, with regional adoption patterns and regulatory enforcement intensity as cross-cutting dimensions. CAGRs derived from fitted growth curves anchored to disclosed contract values and procurement cycle compression rates observed under NIS2 transposition timelines.
The analysis sits within stated boundaries; outcomes outside sustained Danish Business Authority enforcement staffing or hyperscale infrastructure pricing stability would require recalibration. Forecasts reflect documented assumptions regarding NIS2 designation thresholds and GDPR penalty trajectory. Practitioners should keep alternative scenarios live as EU AI Act implementation guidance for automated threat detection systems evolves.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Database Security Market
Cybersecurity
Cybersecure Vehicle Control Unit Gateway Systems Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Global Digital Forensic Laboratory As a Service Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
North America IoT Security Market
Cybersecurity
Mexico Cybersecurity Market
Cybersecurity
Data Protection Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Application Security Market
Cybersecurity
Cloud Access Security Broker Market