
 China Cybersecurity Market | 2026-2036
China Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
China Cybersecurity Market Analysis
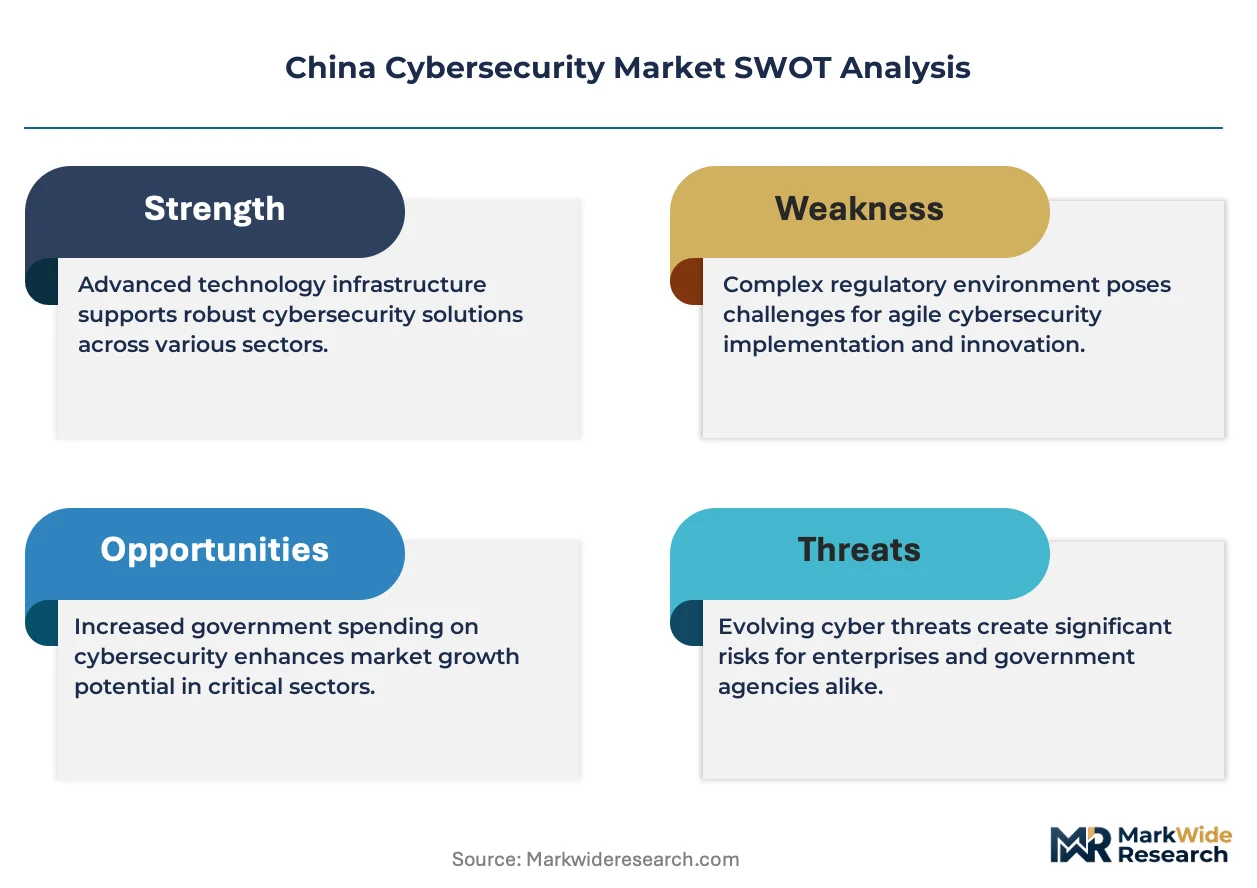
Domestic semiconductor foundry capacity in Shanghai and Shenzhen is decoupling from foreign chip dependencies for security hardware fabrication. QI-ANXIN Technology Group Inc. leverages government certification pathways to anchor its position in critical infrastructure protection. Huawei Technologies Co., Ltd. sustains integrated secure-cloud offerings through captive silicon design. Sangfor Technologies Inc. dominates the mid-enterprise firewall segment with localized threat intelligence.
China cybersecurity encompasses hardware, software, and services engineered to protect digital assets against unauthorized access, data exfiltration, and operational disruption across classified and commercial systems. The field employs cryptographic modules meeting GB/T standards, behavioral analytics engines, and air-gapped deployment architectures for defense-grade environments. Network Security captures the largest revenue pool among product types due to state-mandated perimeter hardening at tier-one institutions. Cloud Security represents the fastest-expanding category as state-owned enterprises migrate core workloads to government-certified sovereign cloud platforms. Endpoint Security maintains mature margins in regulated sectors where MLPS Level 3 compliance requires persistent device monitoring.
SAMR enforces data localization and cross-border transfer rules that shape product architecture decisions for foreign and domestic vendors alike. MIIT's certification regime for commercial cryptographic products controls market access at the component level. NMPA-aligned healthcare data protection rules extend compliance obligations to medical IoT supply chains. Stakeholders must monitor how draft AI security regulations reshape vulnerability disclosure timelines and red-team testing mandates.
Market Dynamics
China's cybersecurity market operates under state-directed procurement mandates that fuse compliance architecture with sovereign technology development, compressing vendor selection around government-certified supply chains.
Growth Catalysts
- MLPS 2.0 mandates:The multi-level protection scheme requires tiered audits for critical infrastructure operators, creating recurring compliance expenditure cycles across energy, finance, and telecommunications sectors.
- Sovereign cloud migration:State-owned enterprises are relocating core workloads to government-certified cloud platforms, expanding demand for cloud-native security stacks.
- Beijing Zhongguancun corridor:Concentrated R&D investment in this technology cluster accelerates domestic threat intelligence development and hardware-software integration.
Market Restraints
- Semiconductor supply concentration:Domestic foundry capacity in Shanghai and Shenzhen remains insufficient for advanced security chip fabrication, creating dependency bottlenecks for cryptographic modules.
- MIIT certification timelines:Commercial cryptographic product approval processes extend market entry durations for component vendors.
- Foreign technology substitution costs:Decoupling from established international security architectures requires complete stack rebuilds for tier-one institutions.
Strategic Opportunities
- Healthcare IoT expansion:NMPA-aligned data protection rules extend compliance obligations to medical device supply chains, creating new endpoint security demand.
- AI security regulation:Draft frameworks governing vulnerability disclosure and red-team testing will reshape service delivery models for algorithmic systems.
- Zero-trust architecture:State-owned banks are expanding procurement of perimeter-less security models, opening deployment opportunities across financial infrastructure.
Industry Challenges
- GB/T cryptographic expertise scarcity:Qualified engineers capable of implementing national cryptographic standards remain concentrated in Beijing and Shenzhen, constraining nationwide deployment velocity.
- Air-gapped system integration:Defense-grade environments require physical network isolation that complicates cloud-native security tool deployment and update cycles.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | China Cybersecurity Market |
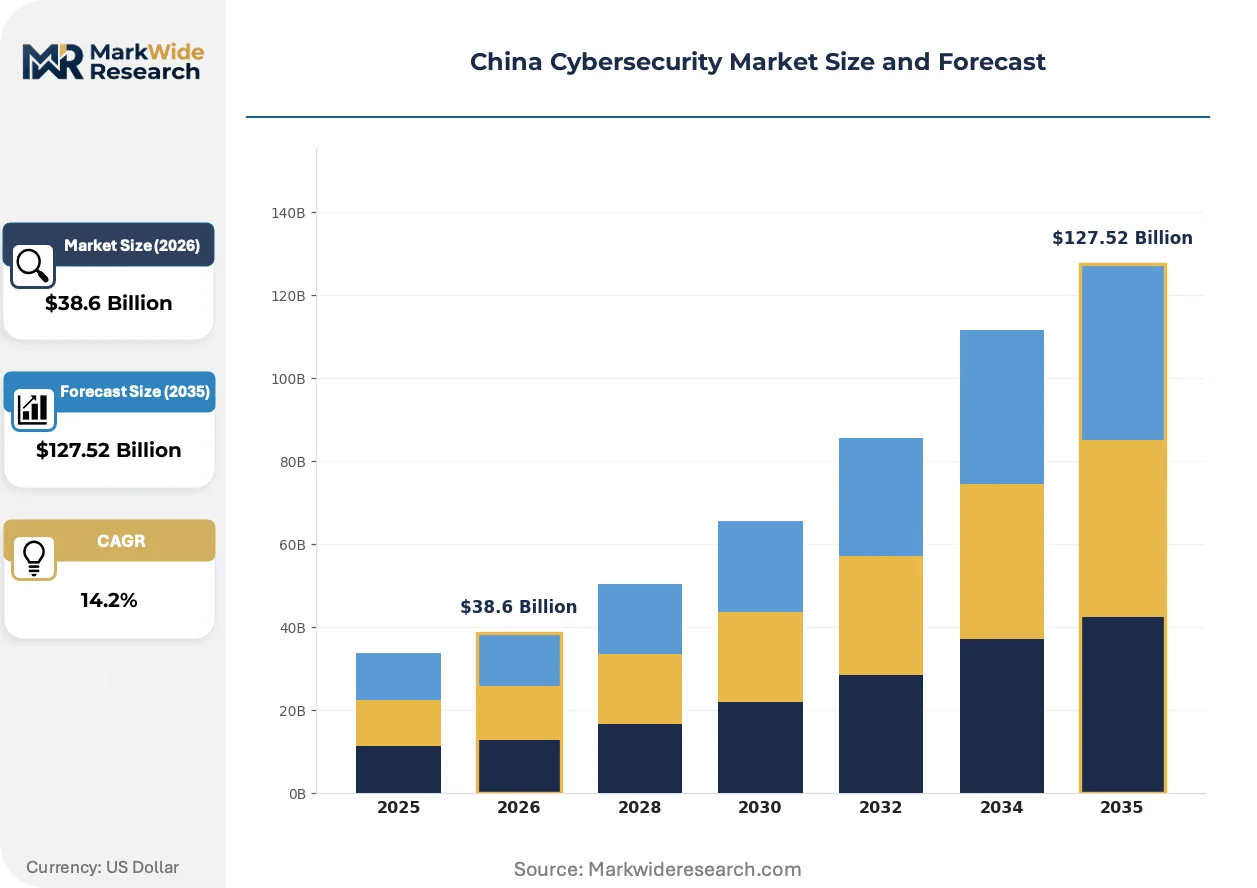
| Market Size in 2026 | $38.6 Billion |
| Market Size in 2035 | $127.52 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Endpoint Security, Network Security, Cloud Security, Application Security End User: Government, BFSI, Healthcare, Telecom Deployment Model: On-Premise, Cloud-Based, Hybrid, Managed Service Service Type: Consulting, Implementation, Training, Support |
| Companies Covered | Sangfor Technologies Inc., Beijing Chaitin Future Technology Co.,Ltd, 360 Security Technology, Qihoo 360, Beijing TopSec Network Security Technology Co., QI-ANXIN Technology Group Inc., ThreatBook, H3C Technologies, Huawei Technologies Co., Ltd., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
China Cybersecurity Market Emerging Trajectories
Domestic technology substitution is compressing vendor ecosystems around state-certified platforms while regulatory granularity accelerates specialization in compliance automation tools.
Hardware security modules built on domestic semiconductor designs are consolidating control over cryptographic key management in critical infrastructure deployments. State-owned banks and energy utilities are adopting these modules at accelerated procurement cycles. This consolidation is compressing foreign component presence in tier-one security stacks.
SAMR data localization enforcement is mandating architectural redesigns for cross-border data flows. Product engineering teams must embed territorial data residency controls at the infrastructure layer. Cloud security vendors targeting multinational operations face the most extensive reconfiguration requirements.
Security service unbundling is fragmenting traditional bundled offerings into discrete compliance, monitoring, and incident response contracts. Mid-enterprise buyers in manufacturing and logistics verticals are driving this decomposition. Guangdong province exhibits the most pronounced shift toward modular procurement structures.
China Cybersecurity Market Segmentation
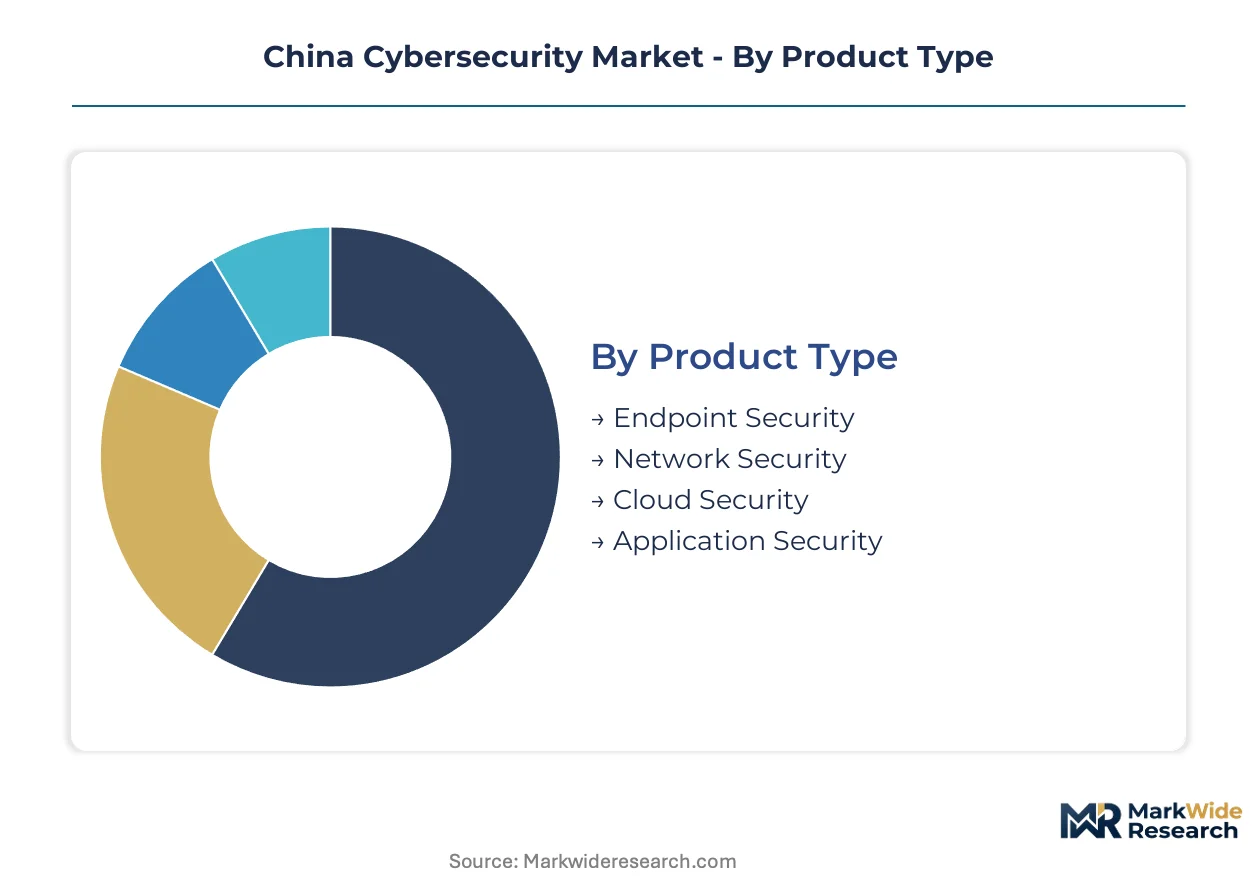
China's cybersecurity market fragments along four distinct axes that reflect state procurement priorities, compliance mandates, and infrastructure modernization cycles. Product type segmentation captures the largest revenue pools, while deployment model choices increasingly hinge on sovereign cloud certification requirements.
Product Type:
Network Security commands premium pricing due to MLPS-mandated perimeter hardening, while Cloud Security volumes accelerate fastest as state-owned enterprises migrate core workloads.
- Endpoint Security:Persistent device monitoring agents enforce MLPS Level 3 compliance across regulated sectors. Demand concentrates in Beijing's Zhongguancun corridor where government and defense contractors require air-gapped deployment architectures.
- Network Security:Perimeter hardening appliances and next-generation firewalls dominate procurement at tier-one institutions. State-owned banks and energy utilities drive recurring expenditure cycles under mandatory audit schedules.
- Cloud Security:Native security stacks for government-certified sovereign cloud platforms are gaining share fastest as SOE workload migration accelerates.
- Application Security:Code scanning and runtime protection tools address DevSecOps pipelines in fintech and e-commerce verticals.
Today's leader: Network Security. Tomorrow's challenger: Cloud Security.
End User:
Government buyers anchor procurement volume through centralized tenders, while healthcare compliance obligations are expanding fastest under NMPA-aligned data protection rules.
- Government:Central and provincial agencies mandate domestic vendor certification through MIIT-controlled procurement frameworks. Beijing and Shenzhen concentrate the highest security expenditure per capita.
- BFSI:State-owned banks are expanding zero-trust architecture procurement as perimeter-less security models replace legacy network segmentation. The sector faces the most stringent MLPS audit frequencies.
- Healthcare:Medical IoT supply chains now fall under NMPA data protection obligations, creating new endpoint security demand in hospital networks and device manufacturing.
- Telecom:Critical infrastructure operators face tiered compliance audits with mandatory cryptographic module deployment across 5G core networks.
Volume concentration: Government. Fastest policy expansion: Healthcare.
Deployment Model:
On-Premise retains margin dominance in defense-grade environments, while Cloud-Based deployment climbs fastest where sovereign certification enables SOE adoption.
- On-Premise:Air-gapped hardware security modules and physical network isolation remain mandatory for classified systems. Defense and government intelligence sectors sustain this model despite higher operational overhead.
- Cloud-Based:Government-certified sovereign cloud platforms are capturing mid-enterprise manufacturing and logistics workloads previously locked in private data centers.
- Hybrid:Split architectures allow sensitive data residency on-premise while leveraging cloud analytics for threat intelligence processing.
- Managed Service:Modular procurement structures in Guangdong province are driving unbundled security operations center contracts.
Maturity anchor: On-Premise. Growth engine: Cloud-Based.
Service Type:
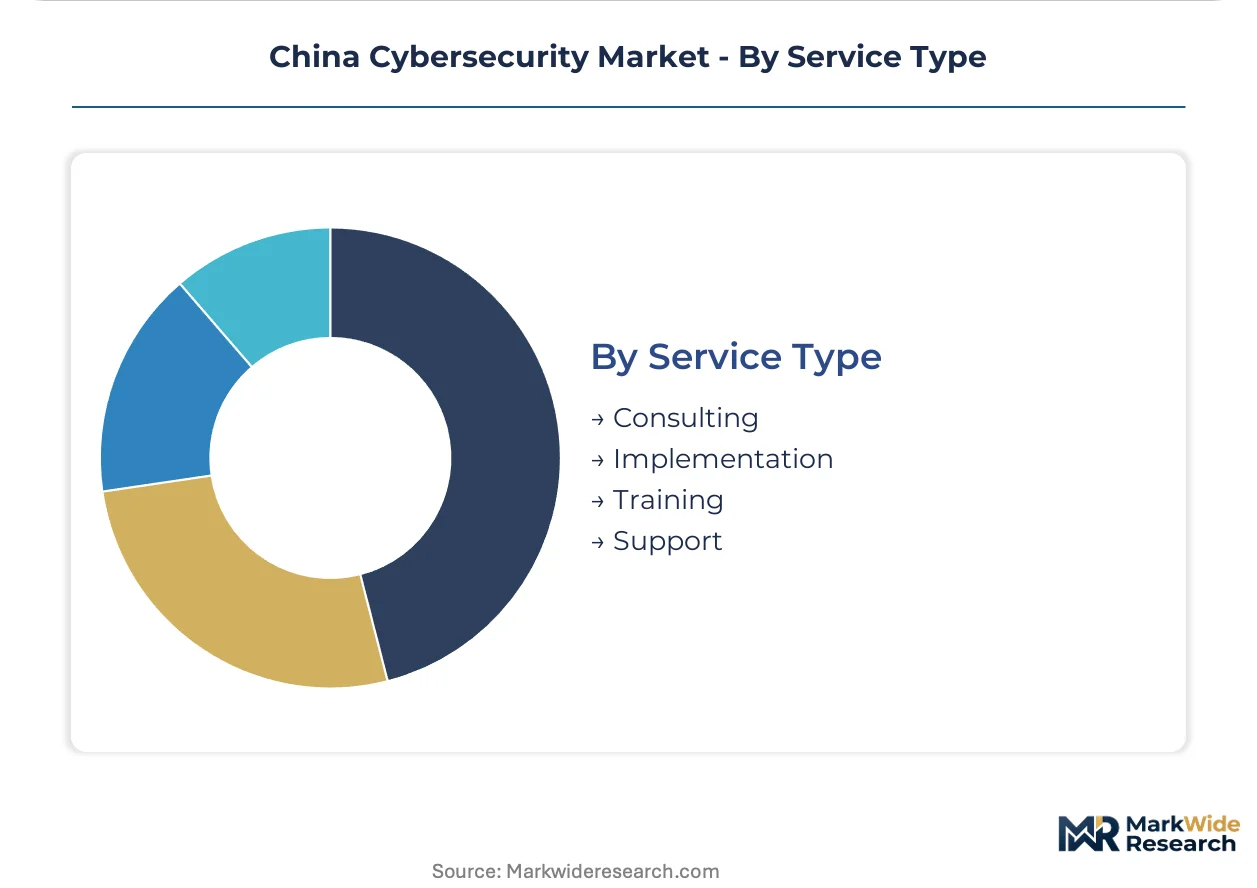
Implementation services capture the largest project value, while Training demand is expanding fastest due to acute GB/T cryptographic expertise scarcity.
- Consulting:MLPS compliance gap assessments and audit preparation dominate engagement types. Tier-one institutions require complete stack rebuilds for foreign technology substitution.
- Implementation:System integration for hardware security modules and zero-trust architectures generates the highest per-project revenue. State-owned banks and energy utilities drive concentrated demand.
- Training:Certification programs for GB/T cryptographic standards are proliferating as qualified engineers remain scarce outside Beijing and Shenzhen.
- Support:Recurring maintenance contracts for air-gapped systems require specialized update cycles that complicate cloud-native tool deployment.
Revenue concentration: Implementation. Fastest capacity build: Training.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory-arbitrage dynamics are reshaping cybersecurity procurement as cost-of-compliance gaps between sub-regional enforcement intensities redirect vendor investment toward Beijing-Tianjin-Hebei and Yangtze River Delta corridors.
Beijing-Tianjin-Hebei
Central government agencies and defense contractors anchor demand through MIIT-controlled procurement frameworks. SAMR data localization mandates concentrate cloud security vendor headquarters in Zhongguancun. Air-gapped system deployment for classified networks sustains premium pricing for hardware security modules.
Yangtze River Delta
Shanghai's financial sector drives zero-trust architecture adoption among state-owned banks. Domestic semiconductor foundry expansion in Pudong reduces cryptographic module import dependency. MLPS Level 3 compliance audits generate recurring service revenue across Jiangsu and Zhejiang manufacturing hubs.
Pearl River Delta
Shenzhen's electronics supply chain demands endpoint security for medical IoT device manufacturing under NMPA-aligned rules. Guangdong province leads modular security procurement unbundling. Cross-border data flow restrictions between Shenzhen and Hong Kong reshape cloud architecture decisions for multinational operations.
Sichuan-Chongqing
Western infrastructure digitization creates demand for sovereign cloud security stacks in Chengdu's telecommunications sector. GB/T cryptographic expertise scarcity constrains deployment velocity outside coastal corridors. Chongqing's automotive manufacturing verticals adopt air-gapped monitoring for industrial control systems.
Shandong Peninsula
Qingdao and Jinan energy utilities face tiered MLPS audits with mandatory cryptographic module deployment. State-owned enterprise workload migration to government-certified platforms accelerates cloud-native security procurement. Localized threat intelligence development lags Beijing and Shenzhen concentrations.
China Cybersecurity Market Vendor Landscape
Beijing-based vendors anchor the premium tier; Shenzhen and Hangzhou specialists hold mid-market positions through hardware-software integration advantages. Market structure concentrates around state-certified supply chains with MIIT approval serving as the primary gating mechanism. Three archetypes dominate: integrated technology conglomerates with captive silicon design, pure-play cybersecurity vendors with government certification pathways, and telecommunications equipment providers extending into security services. Competitive moves center on foreign technology substitution contracts and sovereign cloud platform partnerships.
Within the government-certified vendor tier, QI-ANXIN Technology Group Inc. and Sangfor Technologies Inc. exemplify divergent strategic positions. QI-ANXIN occupies a position anchored in critical infrastructure protection through certification pathways, while Sangfor represents mid-enterprise firewall specialization with localized threat intelligence capabilities. Huawei Technologies Co., Ltd. sits within the integrated technology conglomerate archetype, leveraging captive silicon design for secure-cloud offerings. These three companies illustrate how vendor selection compresses around state-directed procurement mandates that fuse compliance architecture with domestic technology development priorities.
| Leading Market Players |
|---|
| Sangfor Technologies Inc. |
| Beijing Chaitin Future Technology Co.,Ltd |
| 360 Security Technology |
| Qihoo 360 |
| Beijing TopSec Network Security Technology Co. |
| QI-ANXIN Technology Group Inc. |
| ThreatBook |
| H3C Technologies |
| Huawei Technologies Co., Ltd. |
| Others |
Supply Flow & Price Mechanics
Domestic semiconductor foundry expansion in Shanghai and Shenzhen is compressing import dependency for cryptographic modules while simultaneously reshaping cost economics across hardware security tiers. This production-method transition concentrates procurement leverage among MIIT-certified vendors who control captive silicon supply.
Pricing Analysis
Distributor margins on commercial cryptographic products compress as direct-to-OEM channels expand under state procurement mandates. Three-tier pricing structure across premium, standard, and economy levels separates defense-grade hardware security modules from mid-enterprise firewalls and commodity endpoint agents. Pricing pressure stems from foreign technology substitution mandates requiring complete stack rebuilds. State-owned banks exhibit lowest price sensitivity due to compliance-driven procurement, while Guangdong manufacturing verticals drive hardest bargain on modular security services.
Supply Chain Analysis
Advanced lithography equipment supply rests on Dutch, Japanese, and US specialty producers, constraining domestic foundry capacity for security chip fabrication. Raw material dependencies span silicon wafers, photoresist chemicals, and rare earth elements for magnetic components. Single-source vulnerability concentrates in extreme ultraviolet lithography systems held by ASML. Distribution runs through MIIT-certified vendor networks with direct state procurement frameworks bypassing traditional channel structures.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
China's cybersecurity market functions as a regulatory compounder where MLPS 2.0 audit mandates generate recurring compliance expenditure cycles across critical infrastructure sectors.
For Market Incumbents: Acquire GB/T cryptographic engineering talent pools to anchor implementation service capacity. Consolidate control over sovereign cloud platform partnerships before foreign technology substitution contracts finalize. Threat of emerging pure-play vendors with localized threat intelligence capabilities intensifies margin pressure in mid-enterprise firewall segments. For New Entrants and Emerging Players: Begin with NMPA-aligned healthcare IoT endpoint security where compliance obligations are expanding fastest under medical data protection rules. Target Sichuan-Chongqing western infrastructure digitization where GB/T expertise scarcity constrains incumbent deployment velocity. Go-to-market angle centers on modular procurement structures unbundling traditional bundled security operations. For Investors and Strategic Acquirers: Valuations sit cheapest among mid-market hardware-software integration specialists with MIIT certification pathways but limited geographic footprint. Long-term viability hinges on sustained state-directed procurement momentum and sovereign cloud migration acceleration. Acquisition target archetype: pure-play vendors with government certification assets and underpenetrated regional presence. Watch sovereign cloud platform partnership announcements as inflection indicator for tier-one contract access.| Strategic Initiative | Industry Significance |
|---|---|
| MIIT Certification Investment | Unlocks procurement access to state-owned bank and energy utility tenders under MLPS mandates. |
| Domestic Semiconductor Foundry Partnership | Reduces cryptographic module import dependency while securing supply priority under state technology substitution policies. |
| Sovereign Cloud Platform Integration | Captures workload migration demand from state-owned enterprises relocating core systems to government-certified infrastructure. |
| GB/T Cryptographic Training Program | Addresses acute engineering scarcity outside Beijing-Shenzhen corridors while building implementation service revenue. |
| Healthcare IoT Endpoint Security Launch | Targets NMPA-aligned compliance obligations extending to medical device supply chains and hospital networks. |
Methodological Framework
Direct dialogue with cybersecurity procurement officers at state-owned banks, MIIT certification auditors, sovereign cloud platform engineers, and hardware security module integration specialists grounded qualitative findings. Secondary validation drew from MIIT commercial cryptographic product registries, SAMR data localization enforcement notices, MLPS audit disclosure filings, and state-owned enterprise IT expenditure reports. Bottom-up vendor revenue triangulation against top-down compliance expenditure modeling anchored market sizing.
Segmentation outputs across product type, end user, deployment model, and service type dimensions combined with geographic procurement cluster analysis throughout the forecast period. CAGRs derived from compliance audit frequency projections, sovereign cloud migration timelines, and foreign technology substitution contract awards. Industry-specific inputs included MIIT certification queue lengths and domestic foundry capacity expansion schedules.
Caveats apply where MIIT regulatory timeline acceleration or semiconductor equipment export restriction shifts could materially shift the outlook. Forecasts embed assumptions around sustained state-directed procurement intensity and sovereign cloud platform certification velocity. A small set of triggers—draft AI security regulation finalization, advanced lithography equipment access changes, and cross-border data flow rule tightening—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Asia Pacific Digital Forensics Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
E-Mail Security Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
New Zealand Cybersecurity Market
Cybersecurity
Information Security Products and Services Market
Cybersecurity
Domain Name System (DNS) Firewall Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Russia Cybersecurity Market
Cybersecurity
Big Data Security Market