
 Corporate Web Security Market | 2026-2036
Corporate Web Security Market Size, Share, and Industry Trends Forecast 2026-2036
Corporate Web Security Market Analysis
ISO/IEC 27001 certification cycles are redrawing competitive boundaries for enterprise web security procurement. Cisco Systems leverages its integrated networking-security stack to dominate hardware-centric deployments. Zscaler anchors cloud-native Secure Access Service Edge positioning with zero-trust architecture specialization. Palo Alto Networks competes through platform consolidation spanning firewall, DNS security, and threat intelligence layers.
Corporate web security encompasses hardware, software, and cloud-delivered solutions that inspect, filter, and block malicious HTTP/HTTPS traffic at network perimeters and endpoints, operating across proxy-based inspection depths of 2,048 to 8,192 bytes for TLS 1.3 encrypted sessions. Its primary purpose is preventing data exfiltration, credential theft, and malware delivery while preserving workforce productivity. Cloud-based deployment captures the fastest expansion as distributed workforces abandon legacy hub-and-spoke architectures. Web filtering solutions within the solution segment generate disproportionate margin pools due to recurring threat-intelligence subscription attach rates. Managed services for small and medium enterprises remain structurally underpenetrated relative to large corporations with in-house security operations centers.
The U.S. SEC cybersecurity disclosure rules and HIPAA security requirements mandate incident reporting and access controls that directly expand web security budgets for regulated entities. Europe's GDPR and NIS2 Directive impose cross-border data-flow monitoring obligations that European enterprises address through hybrid deployment models combining on-premises inspection with cloud policy enforcement. Stakeholders must evaluate whether their current vendor relationships deliver sufficient API interoperability to avoid lock-in as artificial intelligence-powered threat detection becomes table stakes for enterprise renewals.
Market Dynamics
Cloud migration by financial services firms is compressing procurement cycles for perimeter security solutions as distributed architectures abandon centralized data inspection models.
Growth Catalysts
- EU AI Act compliance mandates:European enterprises must deploy automated threat detection for high-risk AI systems, expanding web security budgets for classification and monitoring infrastructure.
- TLS 1.3 encryption proliferation:Deep packet inspection requirements at 8,192-byte depths drive hardware refresh cycles for proxy appliances unable to handle modern cipher suites.
- Japan's financial sector:Tokyo-based institutions accelerating zero-trust adoption to meet METI cybersecurity framework revisions for critical infrastructure protection.
Market Restraints
- Semiconductor supply concentration:Custom ASIC production for high-throughput inspection appliances depends on Taiwan-based foundry capacity, creating 18-24 month procurement lead times.
- GDPR cross-border friction:Data localization requirements complicate cloud-delivered security policy enforcement for multinational enterprises with distributed workforces.
- Legacy hub-and-spoke substitution:Existing MPLS and private circuit investments create switching costs that delay SASE migration for mid-market enterprises.
Strategic Opportunities
- German Mittelstand segment:Small and medium enterprises with underpenetrated managed security services represent white space for outsourced SOC-as-a-service offerings.
- NIS2 Directive tailwind:Expanded entity coverage and incident reporting obligations create compliance-driven replacement cycles for basic web filtering solutions.
- Browser isolation convergence:Integration of remote browser isolation with zero-trust network access is opening new architectural procurement categories.
Industry Challenges
- Zero-trust architecture skill scarcity:Enterprise security teams lack personnel capable of designing microsegmentation policies for hybrid cloud environments.
- ISO/IEC 27001 certification timelines:12-18 month audit cycles delay vendor qualification for regulated procurement, compressing competitive windows.
- API interoperability complexity:Vendor-specific policy languages create integration friction when enterprises attempt multi-vendor security stack orchestration.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Corporate Web Security Market |
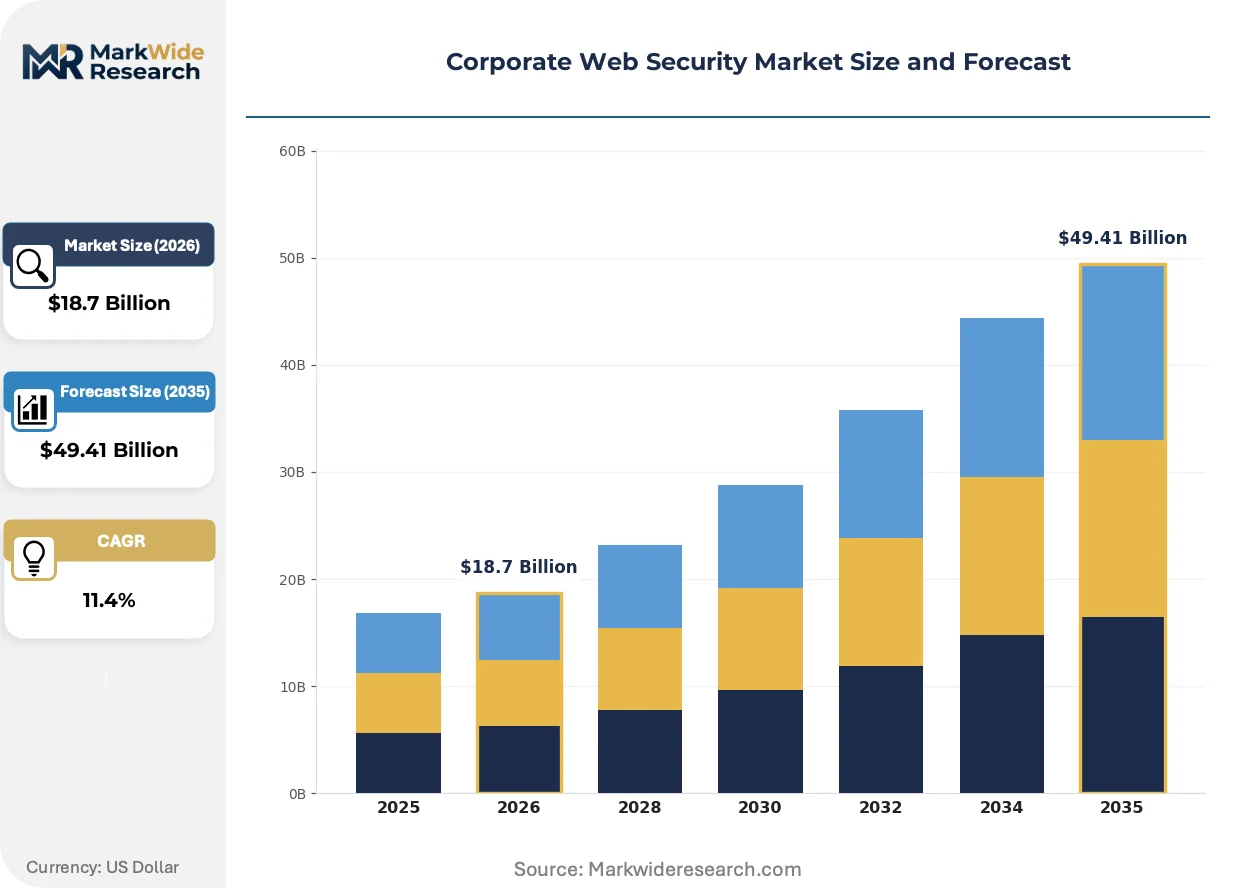
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $49.41 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Firewall, VPN, Intrusion Detection, Web Filtering Deployment: On-premises, Cloud-based, Hybrid, Managed Services End User: Small Enterprises, Medium Enterprises, Large Corporations, Public Sector Service Type: Consulting, Implementation, Support, Training |
| Companies Covered | Cisco Systems, Zscaler, Barracuda Networks, Trend Micro, Sophos, McAfee, Fortinet, Palo Alto Networks, Trustwave Holdings, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Corporate Web Security Market Emerging Trajectories
Artificial intelligence is embedding into inspection engines at every layer of the web security stack, from TLS fingerprinting to behavioral anomaly detection in encrypted sessions.
Secure Access Service Edge architecture is fragmenting traditional market boundaries between network security and WAN optimization. Financial services buyers in Frankfurt and Singapore are deploying converged stacks that collapse five discrete appliance categories into cloud-native policy enforcement points. This compression is eroding standalone proxy and VPN vendor margins while expanding platform attach rates for threat intelligence subscriptions.
The EU AI Act's risk classification system is mandating automated logging and human oversight mechanisms for AI systems processing personal data. German automotive manufacturers and French healthcare providers must now document web traffic inspection decisions that feed into automated access controls. Hybrid deployment models combining on-premises logging with cloud policy engines are emerging as the dominant architectural response.
Security procurement is consolidating under centralized IT governance functions as CISOs gain direct budget authority previously held by network operations teams. Large enterprises in the United States and Japan are unbundling hardware acquisition from managed service contracts, creating separate competitive arenas for appliance vendors and SOC operators. This bifurcation is most visible in healthcare verticals where HIPAA security rule compliance requires distinct accountability for infrastructure and monitoring service levels.
Corporate Web Security Market Segmentation
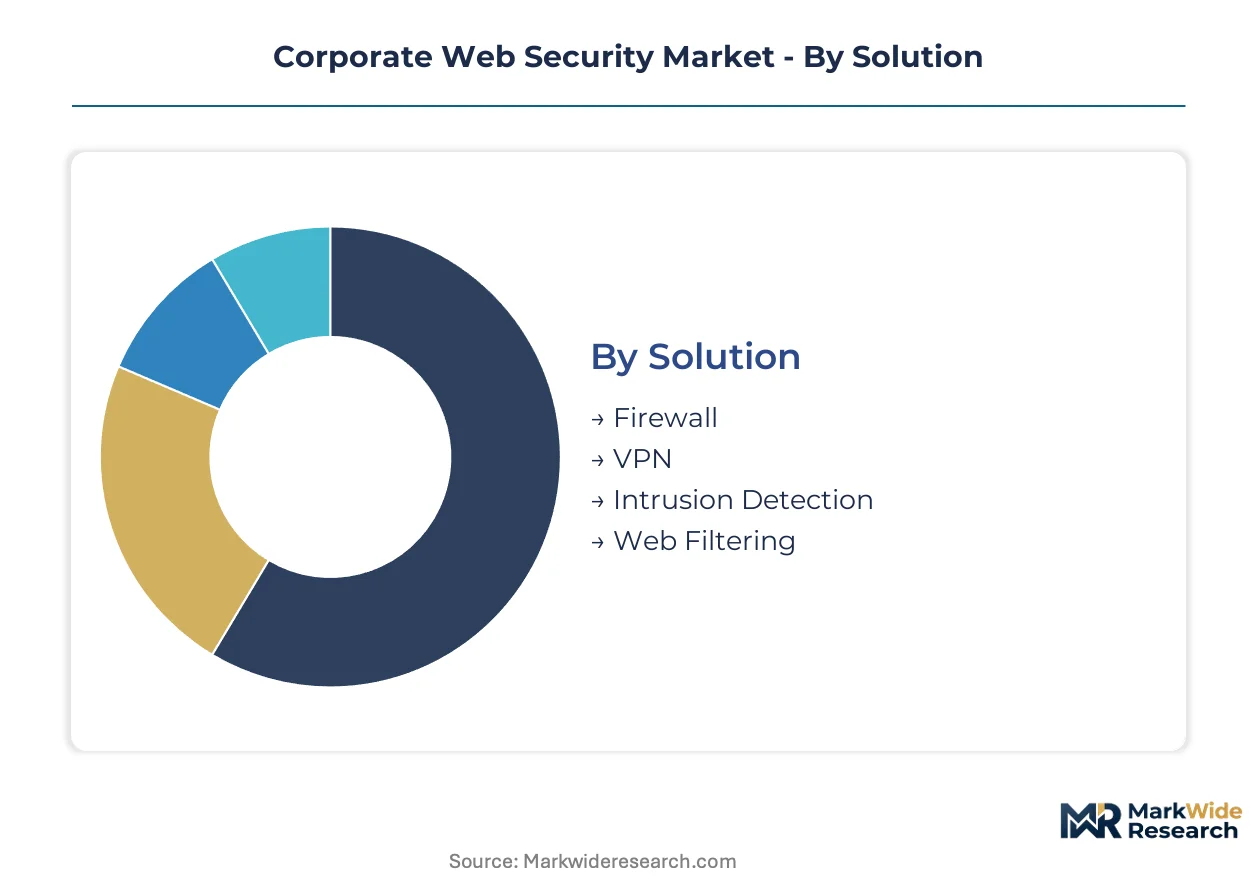
Corporate web security procurement diverges sharply across organizational scale and technical architecture, with cloud migration and zero-trust mandates fragmenting traditional buying patterns. Segment boundaries are blurring as platform vendors bundle firewall, VPN, and web filtering into unified stacks, forcing standalone vendors into niche positioning.
Solution:
Firewall solutions face the most acute substitution pressure from cloud-native SASE platforms that collapse network and security functions into single policy engines.
- Firewall:Hardware and virtualized appliances inspect stateful traffic at network perimeters, with next-generation variants integrating application-layer visibility and intrusion prevention. Financial services firms in Frankfurt and Singapore drive demand for high-throughput appliances handling TLS 1.3 at 8,192-byte inspection depths.
- VPN:Remote access tunnels encrypt workforce connections to corporate resources, though zero-trust network access architectures are displacing traditional client-based models in large enterprise renewals.
- Intrusion Detection:Signature and behavioral engines monitor traffic anomalies, with managed detection services gaining traction among mid-market buyers lacking in-house SOC capabilities.
- Web Filtering:URL categorization and content inspection block malicious destinations, generating recurring revenue through threat-intelligence subscription attach rates.
Firewall retains volume leadership; web filtering holds the steepest expansion curve.
Deployment:
Cost tier stratification separates enterprise buyers willing to absorb capital expenditure from mid-market adopters prioritizing operational flexibility.
- On-premises:Physical appliances deployed in data centers and branch offices maintain inspection control for regulated industries with data localization requirements. German automotive manufacturers and Japanese financial institutions favor this model for GDPR and METI compliance documentation.
- Cloud-based:Distributed policy enforcement points replace hub-and-spoke architectures, with financial services firms in London and New York compressing procurement cycles for perimeter replacement.
- Hybrid:Combined on-premises logging with cloud policy engines addresses EU AI Act audit trail mandates for high-risk AI systems processing personal data.
- Managed Services:Outsourced SOC operations and policy management target the German Mittelstand and similar SME segments with underpenetrated security staffing.
Cloud-based deployment is climbing the fastest; hybrid architectures gain share in European regulated verticals.
End User:
Customer type determines procurement authority structure, with CISO budget centralization reshaping vendor engagement models across organizational scale.
- Small Enterprises:Organizations under 100 employees rely heavily on managed services and bundled ISP security offerings due to zero dedicated security personnel.
- Medium Enterprises:Mid-market buyers with 100-999 employees represent white space for SOC-as-a-service offerings, particularly in Germany's industrial belt.
- Large Corporations:Fortune 500 and equivalent entities unbundle hardware acquisition from managed service contracts, creating separate competitive arenas for appliance vendors and monitoring operators.
- Public Sector:Government and healthcare entities face distinct compliance timelines, with HIPAA security rule enforcement expanding web security budgets in US hospital systems.
Large corporations dominate absolute spending; medium enterprises show the steepest adoption acceleration.
Service Type:
Margin concentration varies sharply across the implementation lifecycle, with post-deployment services generating recurring revenue streams that hardware sales cannot match.
- Consulting:Architecture design and zero-trust transformation planning command premium pricing, though skill scarcity limits vendor capacity to serve demand.
- Implementation:Deployment and integration services face margin compression as cloud-native platforms reduce customization requirements.
- Support:Tiered maintenance contracts with SLA guarantees represent the most predictable revenue stream across all customer segments.
- Training:Certification programs for ISO/IEC 27001 compliance and vendor-specific platforms address personnel gaps in enterprise security teams.
Support services retain volume leadership; consulting holds the steepest pricing escalation.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The EU AI Act and NIS2 Directive are redirecting European enterprise security budgets toward automated compliance infrastructure. Financial services regulators in Tokyo, Washington, and Frankfurt are compressing procurement timelines for zero-trust architectures. Cloud migration patterns concentrate demand in metropolitan technology corridors with dense enterprise presence.
United States
SEC cybersecurity disclosure rules mandate incident reporting within four business days, expanding web security procurement for publicly traded firms. HIPAA security requirements enforce access controls and audit trails that drive hospital system investments in perimeter inspection. New York and San Francisco financial institutions are unbundling hardware acquisition from managed service contracts.
Germany
The NIS2 Directive expands entity coverage to critical infrastructure operators, triggering compliance-driven replacement cycles for basic web filtering. GDPR cross-border data-flow monitoring obligations favor hybrid deployment models combining on-premises logging with cloud enforcement. Frankfurt financial centers and Stuttgart automotive clusters are deploying TLS 1.3 inspection at 8,192-byte depths.
Japan
METI cybersecurity framework revisions for critical infrastructure protection accelerate zero-trust adoption among Tokyo-based financial institutions. Custom ASIC procurement lead times of 18-24 months create bottlenecks for high-throughput inspection appliances. Osaka manufacturing conglomerates and Nagoya industrial zones are consolidating security procurement under centralized CISO budget authority.
United Kingdom
Post-Brexit data protection alignment with GDPR maintains cross-border monitoring obligations for multinational enterprises. London financial services firms compress perimeter replacement cycles as distributed architectures abandon hub-and-spoke models. Manchester and Birmingham mid-market enterprises represent white space for SOC-as-a-service offerings.
Singapore
The Monetary Authority of Singapore's technology risk management guidelines enforce robust access controls for financial institutions. Cloud-native SASE deployment is fragmenting traditional boundaries between network security and WAN optimization. Singapore-based regional headquarters for multinational corporations are deploying converged stacks collapsing multiple appliance categories.
Corporate Web Security Market Vendor Landscape
Listed leaders compete with private specialists across cloud-native and hardware-centric deployment vectors, producing a tiered market structure. Cisco Systems and Palo Alto Networks anchor the consolidated platform tier through integrated networking-security stacks. Zscaler occupies the cloud-native specialist position with zero-trust architecture specialization. Strategic moves concentrate on API interoperability expansion and managed service portfolio diversification to capture mid-market SOC outsourcing demand.
Within the platform consolidation tier, Cisco Systems exemplifies hardware-centric dominance through integrated networking-security stacks. Zscaler anchors cloud-native positioning with zero-trust architecture specialization. Palo Alto Networks occupies the multi-layer platform position spanning firewall, DNS security, and threat intelligence layers.
| Leading Market Players |
|---|
| Cisco Systems |
| Zscaler |
| Barracuda Networks |
| Trend Micro |
| Sophos |
| McAfee |
| Fortinet |
| Palo Alto Networks |
| Trustwave Holdings |
| Others |
Supply Flow & Price Mechanics
Eighteen-to-twenty-four month lead times for custom ASIC production at Taiwan-based foundries concentrate hardware procurement power among enterprises with capital reserves to pre-commit inventory, compressing margin flexibility for mid-market buyers unable to absorb working capital lock-up. This supply constraint amplifies pricing power for cloud-native vendors whose subscription models bypass silicon bottlenecks entirely.
Pricing Analysis
Certification level creates the primary spread between enterprise tiers, with ISO/IEC 27001-compliant solutions commanding premium positioning against uncertified alternatives. The dominant structure runs subscription-tiered SaaS pricing with annual commitments, though hardware appliances retain project-based capital expenditure models for regulated verticals. Price differentiation hinges on threat-intelligence feed quality and managed SOC bundling, with cost compression in mid-market cloud tiers intensifying due to platform vendor consolidation. Financial services buyers in Frankfurt and New York show least price sensitivity; German Mittelstand manufacturers exhibit highest elasticity.
Supply Chain Analysis
Taiwan and South Korea anchor custom semiconductor fabrication for high-throughput inspection appliances, while China and Vietnam concentrate printed circuit board assembly and chassis manufacturing. The supply chain draws from advanced node wafers, specialized networking silicon, and precision thermal management components. Single-source vulnerability at Taiwan-based foundries creates structural exposure for hardware-centric vendors. Distribution runs through authorized channel partners for enterprise accounts, with direct-to-customer cloud provisioning bypassing traditional logistics entirely.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating as Fortune 500 CISOs centralize procurement authority previously fragmented across network operations and security teams, compressing vendor negotiation leverage. This consolidation demands differentiated positioning strategies across stakeholder archetypes.
For Market Incumbents: Fortify platform attach rates by embedding threat-intelligence subscriptions into core licensing, neutralizing standalone feed vendors. Cisco Systems and Palo Alto Networks should deepen backward integration into custom silicon design to bypass Taiwan foundry queue bottlenecks. ISO/IEC 27001 certification maintenance serves as the priority defensive moat against cloud-native challengers.
For New Entrants and Emerging Players: ISO/IEC 27001 fast-track certification unlocks regulated procurement pipelines in German automotive and French healthcare verticals where audit timelines currently exclude unqualified vendors. The German Mittelstand segment offers penetrable white space with 100-999 employee enterprises lacking dedicated security operations centers. SOC-as-a-service bundling with transparent per-seat pricing addresses this gap without demanding capital-intensive hardware development.
For Investors and Strategic Acquirers: Long-term, this sits as a compliance-infrastructure play because regulatory mandates across the EU AI Act, NIS2 Directive, and SEC disclosure rules create durable replacement cycles independent of economic cycles. Acquisition targets should display cloud-native architecture with API interoperability layers enabling multi-vendor orchestration. The signal to watch is CISO budget authority consolidation velocity in mid-market enterprises.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidated SASE stacks displace standalone proxy and VPN vendors in financial services procurement. |
| Managed Service Diversification | SOC-as-a-service offerings capture German Mittelstand demand with underpenetrated security staffing. |
| Certification Investment | ISO/IEC 27001 compliance unlocks regulated vertical procurement pipelines with 12-18 month audit cycles. |
| API Interoperability Expansion | Open policy languages reduce integration friction for multi-vendor security stack orchestration. |
| Geographic Expansion | Tokyo and Singapore financial centers compress zero-trust procurement timelines for cloud-native entrants. |
Methodological Framework
The analysis maps firewall, VPN, intrusion detection, and web filtering sub-sectors, each validated through CISOs, IT procurement officers, platform engineers, and channel partners across primary interviews. Secondary sources include SEC cybersecurity disclosure filings, EU NIS2 implementation guidance, METI framework revisions, and hyperscaler security capex disclosures. Bottom-up deployment model sizing triangulates against top-down enterprise security budget benchmarks.
Consistency checks against external benchmarks validated volume and value outputs across the projection horizon. The analytical framework models segmentation by solution type, deployment architecture, organizational scale, and service delivery model, with CAGRs derived from elasticity-adjusted adoption curves. Forecast inputs incorporate TLS 1.3 migration velocity and zero-trust architecture penetration rates by vertical.
Underlying assumptions cover regulatory enforcement timelines, foundry capacity allocation, and enterprise cloud migration velocity, with deviation risk concentrated in semiconductor supply disruption and GDPR cross-border enforcement variance. Recalibration cycles align with material shifts in EU AI Act implementation guidance and SEC disclosure rule amendments.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Global Quantum Cryptography Solutions Market
Cybersecurity
Web Application Firewall Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Cloud Authentication Market
Cybersecurity
Container-based Firewall Market
Cybersecurity
Bahrain Cybersecurity Market
Cybersecurity
North America Data Exfiltration Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Switzerland Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Digital Immune System Market
Cybersecurity
Global Ddos Protection Market