
 Container-based Firewall Market | 2026-2036
Container-based Firewall Market Size, Share, and Industry Trends Forecast 2026-2036
Container-based Firewall Market Insights
Market Context
North America is tilting toward cloud-native security capacity as enterprises containerize legacy applications at scale. Palo Alto Networks leverages deep packet inspection integration to sustain technology leadership in hybrid deployment architectures. Fortinet anchors its position through extensive channel control and competitive pricing for managed services segments. Aqua Security specializes in runtime protection for Kubernetes clusters, occupying a distinct niche against broader platform vendors.
Technical Definition and Segment Structure
A container-based firewall is a network security appliance or software agent designed to filter, inspect, and control traffic between microservices running in containerized environments such as Docker and Kubernetes, typically enforcing policies at Layer 3-7 with granularity down to individual pod identities. Its primary commercial purpose is to replace perimeter-centric security models with zero-trust microsegmentation that follows workloads across multi-cloud and on-premises infrastructure. Cloud-native deployment leads in new customer acquisition velocity while hybrid architectures capture the largest margin pools from enterprises in extended migration phases. Behavioral analysis and machine learning technologies are outpacing signature-based detection in growth terms, though deep packet inspection retains structural importance in regulated verticals requiring content-level visibility.
Regulatory Framework and Outlook
The EU AI Act, NIS2 Directive, and GDPR collectively shape product certification requirements and liability frameworks for cybersecurity vendors serving European critical infrastructure operators. In the United States, NIST SP 800-204 and FedRAMP authorization pathways determine market access for government agency procurement, while SEC disclosure rules on material cybersecurity incidents are expanding enterprise accountability. Stakeholders must monitor whether emerging sovereign cloud mandates fragment product roadmaps or create standardization opportunities across jurisdictions.
Market Dynamics
Zero-trust microsegmentation is displacing perimeter-centric security architectures as enterprises containerize legacy workloads, forcing vendors to integrate identity-aware policy engines directly into Kubernetes control planes.
Growth Catalysts
- NIS2 Directive compliance mandates:European critical infrastructure operators must implement granular network segmentation, accelerating procurement of container-native enforcement tools.
- Kubernetes cluster proliferation:Financial services firms are deploying service mesh architectures that require pod-level traffic inspection for payment processing environments.
- Behavioral analysis engines:Machine learning-based threat detection is outpacing signature-based methods in runtime protection deployments across cloud-native workloads.
Market Restraints
- Specialized talent scarcity:Certified Kubernetes security architects command premium compensation, constraining enterprise implementation velocity.
- Hybrid complexity premiums:Organizations maintaining on-premises OpenShift alongside AWS EKS face integration cost multipliers for unified policy management.
- Deep packet inspection latency:Content-level inspection introduces measurable throughput degradation in high-frequency trading environments.
Strategic Opportunities
- Automotive edge deployments:German manufacturers are extending Kubernetes to factory floor systems, creating demand for low-latency container firewalls.
- FedRAMP authorization pathways:US federal cloud procurement requirements favor vendors with pre-authorized container security platforms.
- Service mesh convergence:Integration of firewall policies with Istio and Linkerd data planes eliminates redundant control layers.
Industry Challenges
- Legacy mainframe integration:Financial institutions struggle to map COBOL-based transaction flows to microservice identity models for policy enforcement.
- Certification timeline compression:EU AI Act conformity assessments for automated threat response systems extend vendor time-to-market by 8-14 months.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Container-based Firewall Market |
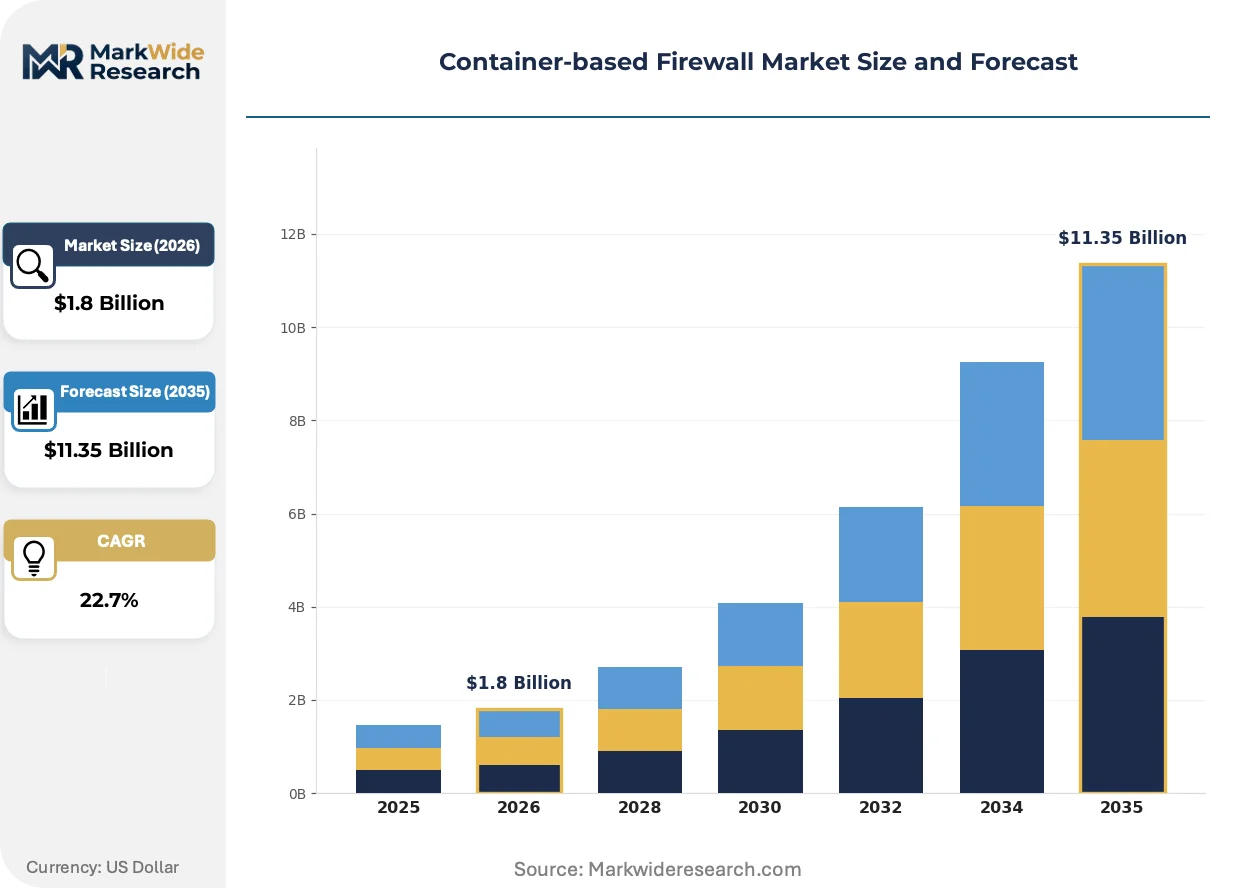
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $11.35 Billion |
| CAGR (2026 – 2036) | 22.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Type: On-Premises, Cloud-Native, Hybrid, Managed Services Technology: Signature-Based, Behavioral Analysis, Machine Learning, Deep Packet Inspection Application: Data Center Security, Microsegmentation, Compliance Monitoring, Threat Prevention End User: Telecommunication Providers, Financial Institutions, Software Developers, Government Agencies |
| Companies Covered | Palo Alto Networks, Fortinet, Juniper Networks, Alibaba Cloud, Huawei Cloud, Tigera, Aqua Security, Qualys, Microsoft, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Container-based Firewall Market Trends and Innovations
Container firewall architectures are converging with service mesh and runtime security layers, collapsing previously distinct product categories into unified cloud-native protection fabrics.
eBPF-based packet filtering is virtualizing kernel-level network enforcement without sidecar proxies. Cloud-native payment processors at scale are adopting this approach to eliminate latency from traditional iptables chains. The technology is virtualizing the boundary between host and container networking, enabling single-root policy trees that follow workloads across clusters.
EU AI Act risk classification requirements are mandating algorithmic transparency for automated threat response systems. Vendors serving European critical infrastructure must document machine learning model decision pathways for regulatory audit. Automotive and energy sector buyers in Germany are prioritizing vendors with pre-certified explainable AI components.
Consumption-based licensing is replacing perpetual seat models as primary revenue structure. Managed security service providers are negotiating outcome-aligned contracts tied to detected breach attempts rather than protected node counts. This shift is most pronounced in North American financial services procurement, where CISOs demand variable cost structures aligned to actual workload density.
Container-based Firewall Market Segmentation
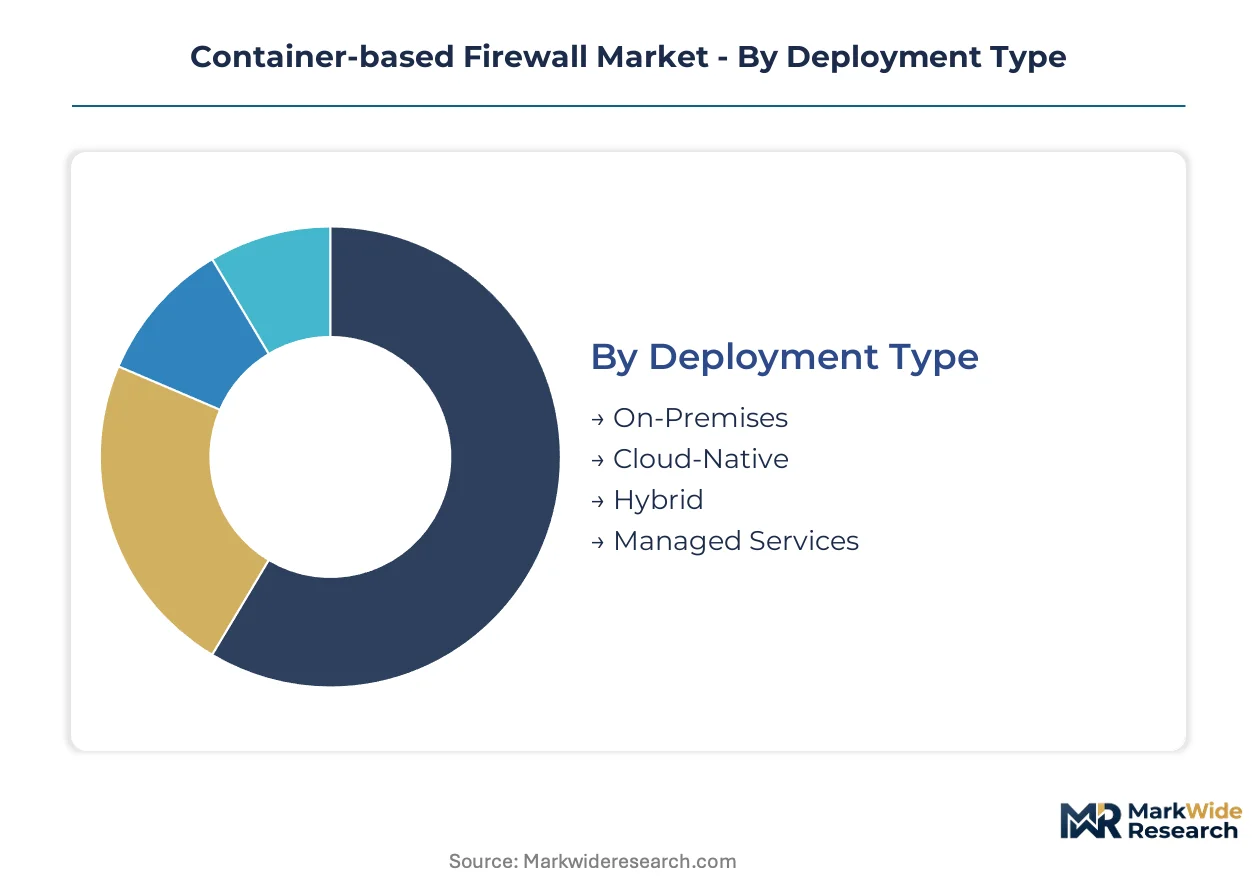
Container-based firewall procurement patterns diverge sharply across deployment contexts and enforcement mechanisms. Understanding these fault lines reveals where vendor R&D investments concentrate and which customer segments command premium pricing.
Deployment Type:
After-sales service intensity varies dramatically by deployment model, with managed services requiring continuous policy tuning while on-premises installations demand episodic architectural consulting.
- On-Premises:Hardware appliances or software agents deployed within enterprise data centers enforce container traffic policies at the host kernel level. Financial institutions in Frankfurt and Stuttgart retain these configurations for payment processing environments where data sovereignty requirements prohibit cloud egress.
- Cloud-Native:Serverless enforcement agents integrate directly with AWS VPC CNI, Azure CNI, and GCP GKE network fabrics. German automotive manufacturers migrating factory floor systems to Kubernetes clusters are standardizing on this model for elastic scaling across development and production pipelines.
- Hybrid:Unified policy orchestration spans on-premises OpenShift and public cloud EKS/AKS clusters simultaneously. This architecture captures the largest professional services attach rates as enterprises navigate extended migration phases.
- Managed Services:Third-party security operations centers assume full policy lifecycle management. Telecommunication providers in Berlin are outsourcing container firewall operations to specialized MSSPs under outcome-aligned contracts.
By volume, Cloud-Native leads. By growth pace, Managed Services is expanding most quickly.
Technology:
Cost tier stratification separates signature-based offerings from premium behavioral and ML-enabled platforms, with deep packet inspection commanding the highest price points in regulated verticals.
- Signature-Based:Pattern-matching engines detect known threat indicators against curated vulnerability databases. These solutions dominate budget-constrained segments but face displacement as zero-day attack volumes rise.
- Behavioral Analysis:Baseline deviation detection identifies anomalous container network flows without prior threat intelligence. EU AI Act transparency requirements are accelerating certification investments for these engines serving critical infrastructure operators.
- Machine Learning:Adaptive models trained on container-specific traffic patterns predict and preempt lateral movement attempts. Software developers in Munich are prioritizing vendors with pre-certified explainable AI components to satisfy emerging audit requirements.
- Deep Packet Inspection:Content-level protocol analysis inspects encrypted TLS sessions via certificate pinning and memory introspection. Government agencies require this capability for classified workload protection, accepting throughput penalties.
By maturity, Signature-Based leads installed base. By revenue trajectory, Machine Learning is gaining share fastest.
Application:
Customer type segmentation separates enterprise infrastructure teams seeking broad platform coverage from specialized buyers demanding point-solution depth.
- Data Center Security:Perimeter-hardening deployments protect east-west traffic within consolidated container fleets. Traditional enterprises containerizing legacy applications drive procurement here.
- Microsegmentation:Pod-identity-aware policies enforce zero-trust boundaries between individual microservices. Financial institutions deploying service mesh architectures for payment processing require this granularity.
- Compliance Monitoring:Continuous audit trails and policy drift detection satisfy NIS2 Directive and FedRAMP evidence requirements. Government agencies mandate these capabilities for authorization maintenance.
- Threat Prevention:Runtime exploit blocking and automated containment respond to detected intrusions without human intervention. Automotive manufacturers extending Kubernetes to operational technology networks prioritize this function.
By deployment frequency, Data Center Security leads. By strategic priority, Microsegmentation is climbing the fastest.
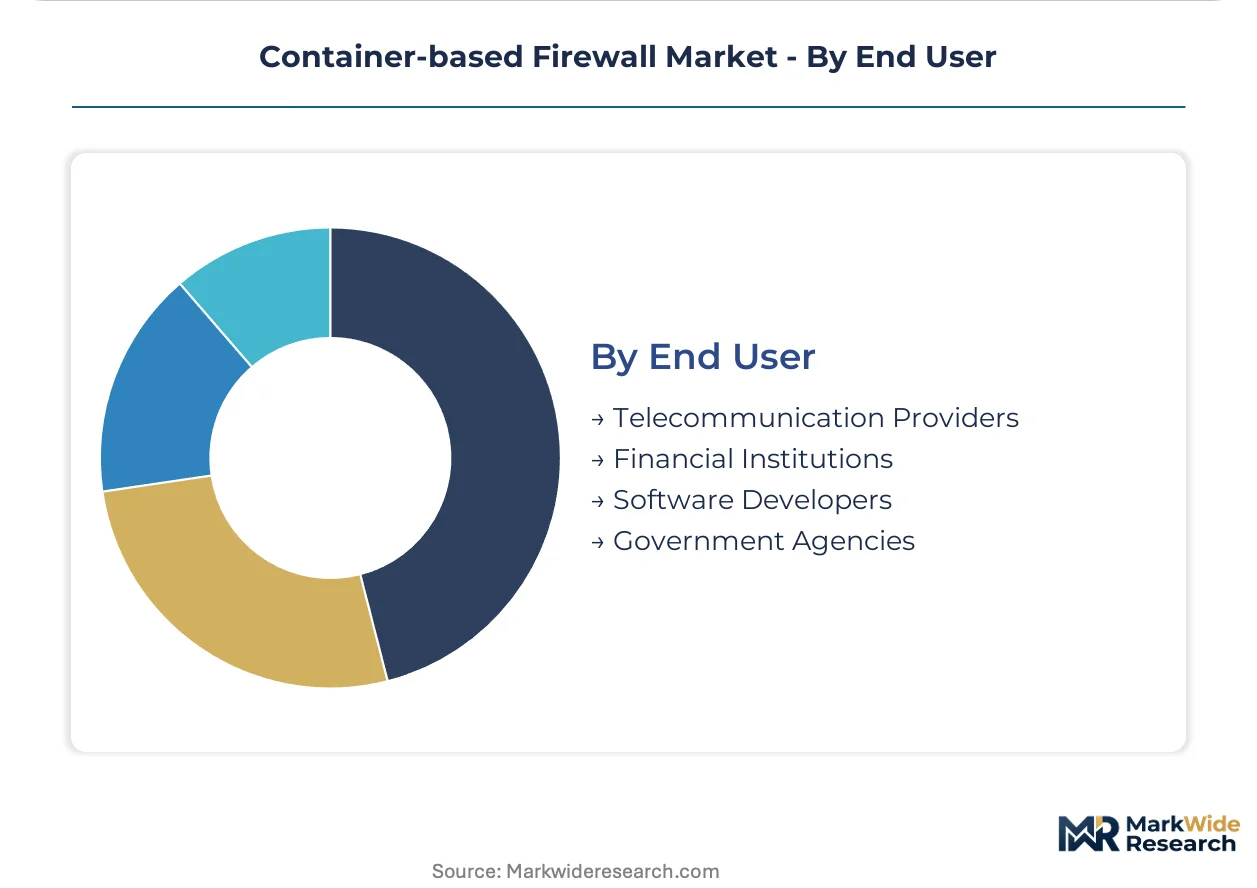
End User:
Margin concentration varies by buyer sophistication, with financial institutions and government agencies accepting premium pricing for certified configurations while software developers drive commoditization.
- Telecommunication Providers:National carriers securing 5G core network functions on Kubernetes require carrier-grade throughput guarantees. These buyers negotiate volume discounts but commit to multi-year enterprise agreements.
- Financial Institutions:Banks and payment processors face SEC disclosure rules and ECB cybersecurity expectations simultaneously. Their procurement favors pre-authorized platforms with documented AI decision pathways.
- Software Developers:DevOps teams embedding security into CI/CD pipelines prioritize API-driven policy automation. This segment exhibits the highest churn rates and price sensitivity.
- Government Agencies:Federal and defense buyers require FedRAMP or equivalent sovereign cloud certifications. Authorization timelines extend sales cycles but lock out uncertified competitors.
By contract value, Financial Institutions lead. By procurement velocity, Software Developers are ahead.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NIST SP 800-204 and FedRAMP authorization pathways anchor North American procurement frameworks, while the EU AI Act and NIS2 Directive reshape European vendor certification requirements. Demand clusters concentrate where cloud-native payment infrastructure and automotive edge deployments intersect with tightening compliance mandates.
United States
Financial institutions in New York and Chicago are deploying service mesh architectures for payment processing environments. SEC disclosure rules on material cybersecurity incidents expand enterprise accountability for runtime protection investments. Cloud-native security procurement in the San Francisco Bay Area favors vendors with pre-authorized FedRAMP platforms.
Germany
Automotive manufacturers in Stuttgart and Munich are extending Kubernetes to factory floor operational technology networks. The NIS2 Directive mandates granular network segmentation for critical infrastructure operators by October 2024. Industrial clusters in Baden-Württemberg prioritize container firewalls with pre-certified explainable AI components for regulatory audit trails.
United Kingdom
Financial services firms in the City of London face overlapping ECB cybersecurity expectations and domestic operational resilience requirements. The Financial Conduct Authority's operational resilience rules mandate maximum tolerable downtime thresholds for payment systems. DevOps teams in Manchester and Edinburgh are standardizing on API-driven policy automation for CI/CD pipeline integration.
China
State-owned banks and telecom operators in Shanghai and Shenzhen are containerizing core transaction systems under MIIT cloud security guidelines. GB standards for financial data security impose localization requirements on foreign security vendors. The Yangtze River Delta cluster drives domestic vendor development for sovereign cloud container protection.
Japan
Manufacturing conglomerates in Nagoya and Osaka are migrating legacy SCADA integrations to Kubernetes-based industrial control systems. METI's cybersecurity framework for critical infrastructure emphasizes supply chain risk management for containerized workloads. Automotive suppliers in Aichi Prefecture require low-latency enforcement for edge-deployed quality control applications.
Container-based Firewall Market Competitive Landscape
Capability concentration sits with specialized runtime protection vendors; scale advantage sits with platform-integrated network security incumbents. The vendor base organizes into three tiers: cloud-native specialists with Kubernetes-native architectures, diversified cybersecurity platforms with container modules, and hyperscale cloud providers bundling firewall functions with managed Kubernetes services. Dominant competitive moves include strategic partnerships for service mesh integration and geographic expansion through FedRAMP authorization investments.
Within the specialized tier, Aqua Security and Tigera occupy positions defined by Kubernetes-specific enforcement depth. Palo Alto Networks anchors the diversified platform segment through deep packet inspection integration for hybrid deployment architectures. Fortinet exemplifies scale-driven competitive positioning through extensive channel control and managed services penetration. These three vendors collectively represent the capability-scale tension shaping procurement decisions across financial services and automotive verticals.
| Leading Market Players |
|---|
| Palo Alto Networks |
| Fortinet |
| Juniper Networks |
| Alibaba Cloud |
| Huawei Cloud |
| Tigera |
| Aqua Security |
| Qualys |
| Microsoft |
| Others |
Pricing and Supply Chain Analysis
EU AI Act conformity assessment delays create a regulatory chokepoint that widens pricing spreads between certified and uncertified vendors while compressing supply chain flexibility for European critical infrastructure deployments. This bottleneck forces buyers to accept premium pricing for pre-certified platforms or absorb extended procurement timelines, reshaping both tier differentiation and vendor sourcing strategies.
Pricing Analysis
North American procurement runs 15-25 percent above European averages due to FedRAMP authorization premiums and managed services bundling. Pricing stratifies across certified-premium, standard-subscription, and economy-self-managed tiers, with certification level and after-sales service intensity as primary differentiation drivers. Cost compression in the economy tier is intensifying because DevOps teams prioritize API-driven automation over bundled support. Software developers exhibit highest price sensitivity, while government agencies accept premium positioning for sovereign-cloud-compliant configurations.
Supply Chain Analysis
Upstream specialized talent pools in the United States, Germany, and Israel feed kernel-level engineering and eBPF development for runtime protection modules. Component sourcing draws from Taiwan for high-performance NICs, Ireland for EU data residency infrastructure, and domestic cloud regions for managed Kubernetes control planes. Single-source vulnerability concentrates in certified Kubernetes security architects, whose scarcity extends implementation timelines. Distribution runs through hyperscaler marketplaces and specialized MSSP channel partners with outcome-aligned contracting authority.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The container-based firewall market rewards vendors who control scarce runtime protection engineering talent and pre-certified AI transparency documentation, while penalizing those dependent on perimeter-security legacy codebases.
For Market Incumbents: Entrench FedRAMP authorization moats through continuous compliance investment against emerging sovereign cloud mandates. Deepen vertical integration into eBPF-based kernel modules to eliminate sidecar latency penalties that threaten displacement by service mesh convergence. Channel control through specialized MSSPs remains critical for managed services segment retention. For New Entrants and Emerging Players: Japanese automotive edge deployments offer underpenetration opportunity for low-latency container firewalls serving quality control applications. Target German mid-market manufacturers migrating factory floor OT networks to Kubernetes, where incumbent platform complexity creates implementation friction. Lead with consumption-based licensing and pre-certified explainable AI components to bypass EU AI Act timeline disadvantages. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors runtime-specialist acquisition targets with Kubernetes-native architectures and established FedRAMP pathways. Long-term viability hinges on service mesh convergence positioning rather than standalone firewall functionality. Monitor hyperscaler bundling announcements as inflection indicator for independent vendor margin compression.| Strategic Initiative | Industry Significance |
|---|---|
| Service Mesh Integration | Collapses redundant control layers between Istio data planes and firewall policy engines. |
| FedRAMP Authorization Investment | Unlocks US federal procurement pathways with extended sales cycles but competitor exclusion. |
| eBPF Kernel Module Development | Eliminates sidecar proxy latency for high-frequency trading and automotive edge workloads. |
| Explainable AI Certification | Satisfies EU AI Act audit requirements for automated threat response in critical infrastructure. |
| Outcome-Aligned Contracting | Aligns MSSP revenue to detected breach attempts rather than protected node counts. |
Research Methodology
Cross-validation between primary interviews with CISOs, Kubernetes platform engineers, and MSSP operations directors anchors the qualitative findings against secondary validation from SEC cybersecurity disclosure filings, hyperscaler capex disclosures, and EU regulatory implementation guidance. Bottom-up triangulation across deployment type, technology tier, and end-user vertical segments integrates with top-down market sizing from vendor revenue disclosures and channel partner volume estimates.
Calibration against historical adoption curves for cloud-native security tooling informs the projection framework across the analysis window. Segmentation dimensions include deployment model, enforcement mechanism, organization size, vertical regulatory intensity, and geographic compliance cluster. CAGRs derive from slope-matching to comparable infrastructure software categories with similar compliance-driven procurement patterns, incorporating Kubernetes cluster proliferation rates and NIS2 Directive implementation timelines as industry-specific inputs.
Practitioners should monitor EU AI Act enforcement discretion and hyperscaler bundled security announcements for early signals of pricing tier compression or vendor consolidation. Forecasts reflect assumptions about regulatory timeline adherence and talent supply elasticity that may revise under sovereign cloud fragmentation or macroeconomic procurement freezes. Cross-checking against channel partner pipeline data and hyperscaler marketplace transaction volumes is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
IoT Security Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Argentina Cybersecurity Market
Cybersecurity
Global Data Exfiltration Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Benelux Cybersecurity Market
Cybersecurity
Server Security Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Artificial Intelligence-Based Cybersecurity Market
Cybersecurity
Wireless Lan Security Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Germany Cybersecurity Market