
 Endpoint Security Solutions Market | 2026-2036
Endpoint Security Solutions Market Size, Share, and Industry Trends Forecast 2026-2036
Endpoint Security Solutions Market Analysis
Managed detection and response revenue is reshaping how vendors capture value beyond perpetual licenses. CrowdStrike leverages its cloud-native architecture to dominate the endpoint detection and response segment. Palo Alto Networks anchors its position through tight integration between endpoint agents and network firewalls. Microsoft competes by bundling endpoint protection with existing enterprise productivity contracts.
Endpoint security solutions encompass software and hardware systems that protect individual computing devices from malware, unauthorized access, and data exfiltration through behavioral analysis, signature-based detection, and automated response protocols. These solutions serve the primary commercial purpose of maintaining data confidentiality and operational continuity across distributed workforces. The endpoint detection and response category leads product type segmentation as organizations prioritize threat hunting capabilities over static prevention. Cloud-based deployment models are expanding fastest among SMEs seeking reduced infrastructure overhead. The managed service segment concentrates margin pools through recurring revenue streams and specialized security expertise.
The U.S. Cybersecurity and Infrastructure Security Agency enforces binding operational directives requiring federal agencies to deploy endpoint detection and response tools across all assets. The EU NIS2 Directive mandates incident reporting and risk management measures that expand addressable demand for European critical infrastructure operators. ISO 27001 certification requirements increasingly specify endpoint control mechanisms as auditable security controls. Stakeholders must monitor how zero-trust mandates evolve from federal procurement standards into private-sector procurement criteria.
Market Dynamics
Zero-trust architecture mandates from the U.S. Cybersecurity and Infrastructure Security Agency are compressing deployment timelines across federal and civilian networks, forcing vendors to restructure licensing models around continuous monitoring rather than periodic scanning.
Growth Catalysts
- CISA Binding Operational Directive 22-01:Federal agencies must deploy endpoint detection and response tools across all assets, creating immediate procurement pull.
- Healthcare IoT expansion:Connected medical devices in delivery networks require specialized endpoint agents that isolate compromised infusion pumps and imaging systems.
- EU NIS2 Directive:Incident reporting obligations for critical infrastructure operators expand addressable demand across energy, transport, and digital service providers.
Market Restraints
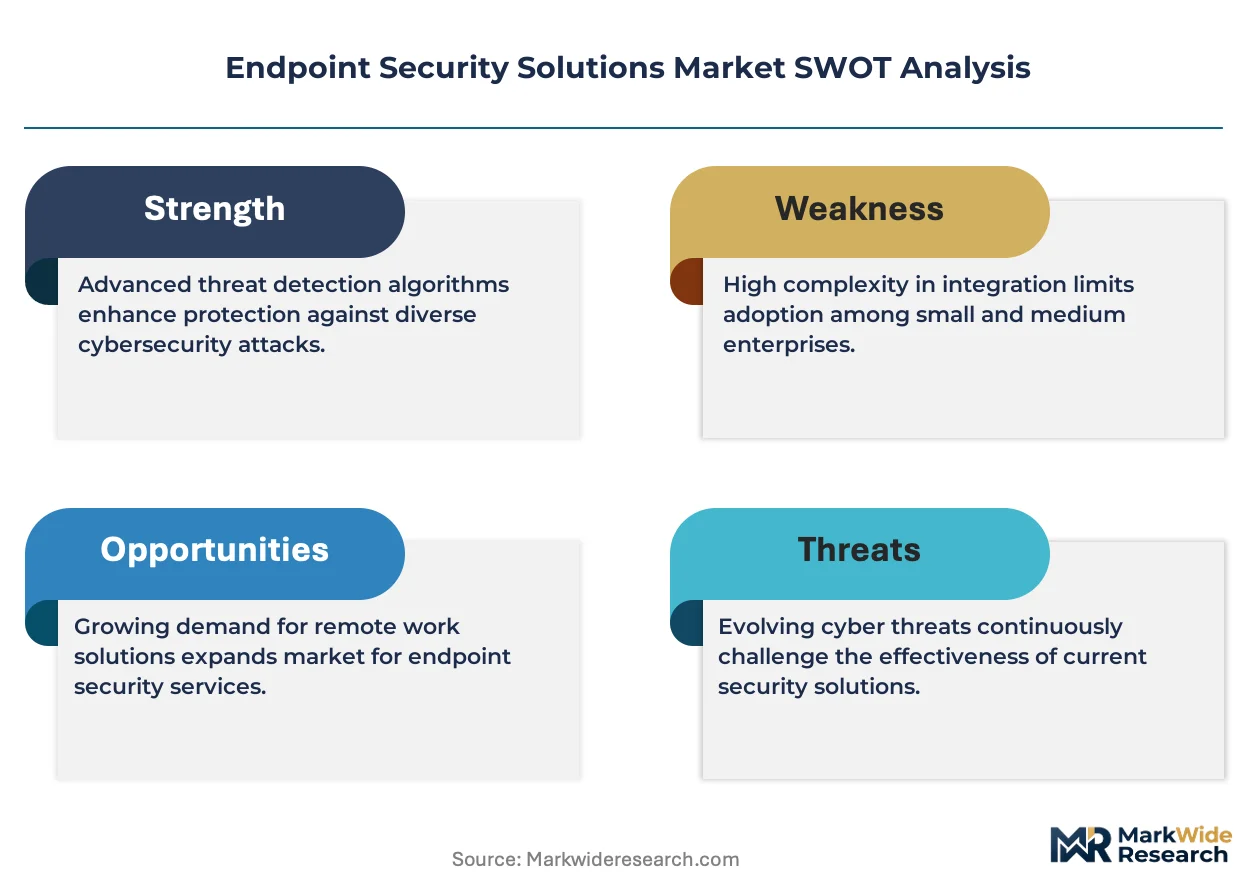
- Agent fatigue and performance drag:Endpoint protection software consumes CPU and memory resources, triggering user resistance and shadow IT workarounds.
- Threat intelligence feed costs:Real-time indicator-of-compromise subscriptions from specialized providers strain mid-market security budgets.
- Legacy Windows system persistence:Unsupported operating systems in industrial control environments block modern EDR agent deployment.
Strategic Opportunities
- Managed detection and response services:SMEs lacking security operations centers outsource threat hunting to specialized providers on recurring contracts.
- Extended detection and response convergence:Endpoint agents integrate with network, identity, and cloud workload telemetry for unified attack surface visibility.
- India's critical infrastructure digitization:Smart city deployments and national payment network expansion create greenfield endpoint protection demand.
Industry Challenges
- Security operations analyst shortage:Alert triage and incident response functions face vacancy rates exceeding thirty percent in mature markets.
- Multi-vendor tool sprawl:Enterprises operate fifteen to fifty discrete security products, fragmenting visibility and complicating orchestration.
- False positive management:Behavioral detection engines generate excessive alerts, desensitizing response teams and delaying actual threat containment.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Endpoint Security Solutions Market |
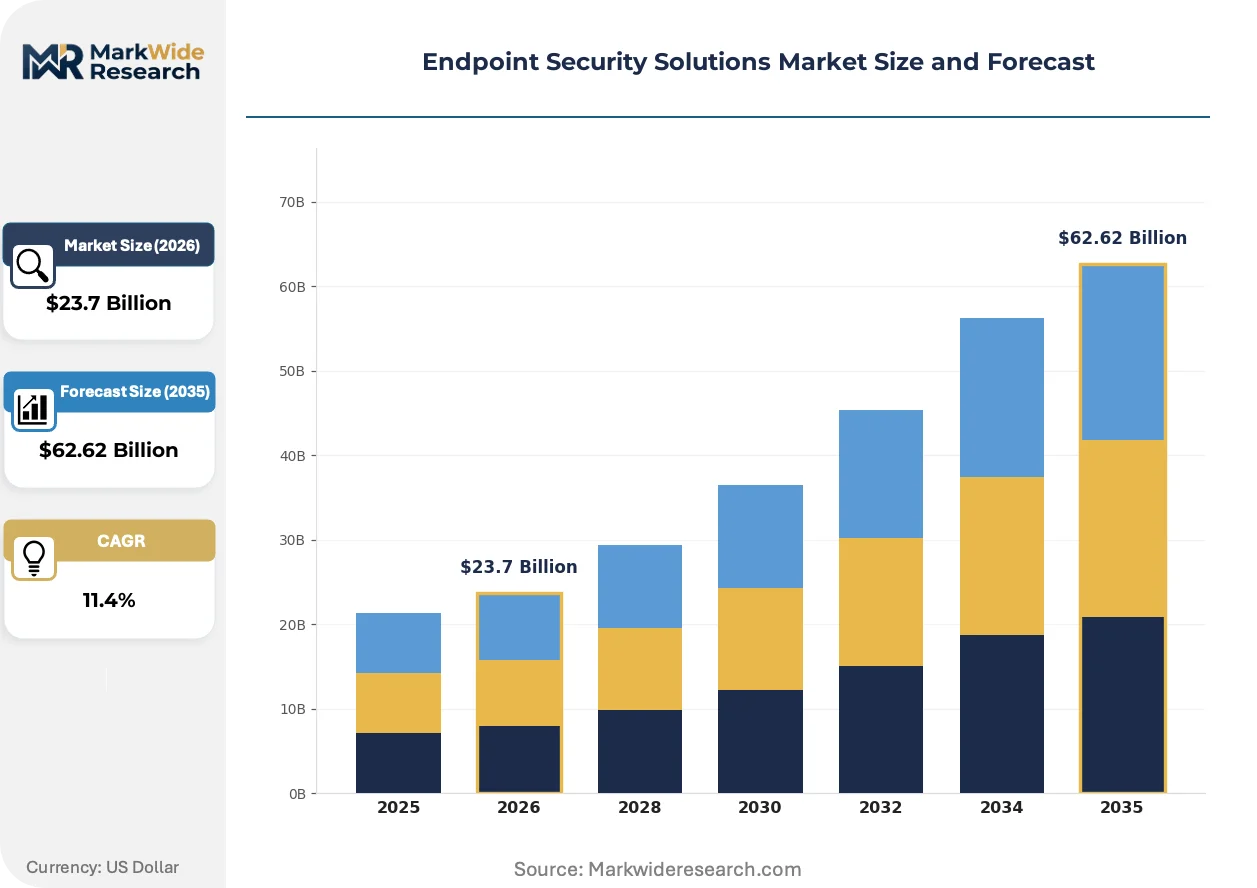
| Market Size in 2026 | $23.7 Billion |
| Market Size in 2035 | $62.62 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
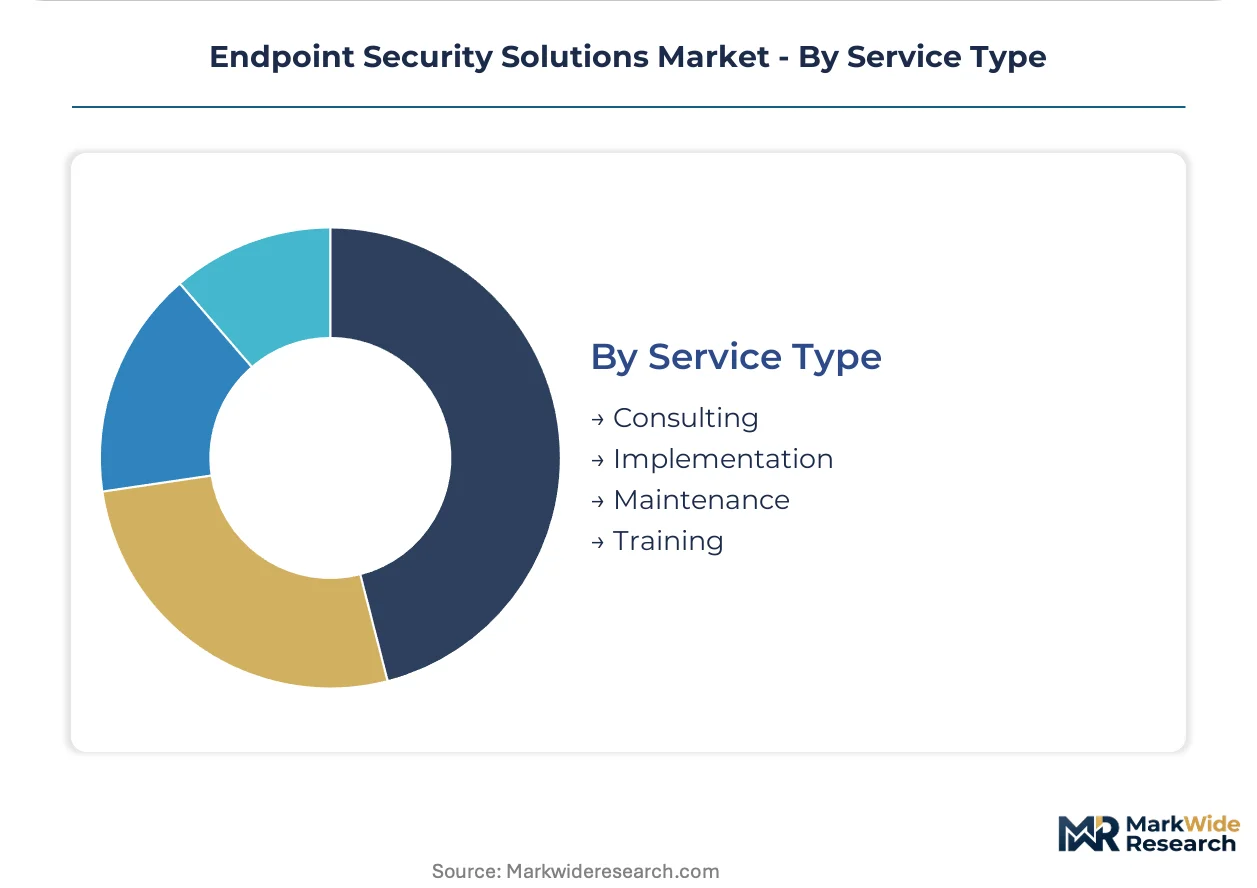
| Segmentation | Product Type: Antivirus, Firewall, Intrusion Prevention System, Endpoint Detection and Response Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: SMEs, Large Enterprises, Government, Education Service Type: Consulting, Implementation, Maintenance, Training |
| Companies Covered | Microsoft, CrowdStrike, SentinelOne, Palo Alto Networks, Broadcom, Trellix, Trend Micro, McAfee, Bitdefender, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Endpoint Security Solutions Market Emerging Trajectories
Endpoint security architecture is migrating from static prevention layers toward continuous behavioral telemetry, compressing the gap between compromise and detection from months to minutes.
Extended detection and response platforms consolidate endpoint, network, and identity signals into unified data lakes. Large enterprises with mature security operations centers deploy these stacks to correlate lateral movement across cloud and on-premises assets. The technology is migrating from standalone endpoint products into integrated security fabrics that reduce swivel-chair analysis between consoles.
The EU AI Act imposes risk classification and documentation requirements on security products employing machine learning for threat detection. Vendors must demonstrate algorithmic transparency and human oversight mechanisms for high-risk deployments. European critical infrastructure operators now demand compliance attestations before procurement, reshaping competitive qualification criteria.
Security procurement is consolidating around platform plays rather than best-of-breed point solutions. Mid-market buyers prefer bundled endpoint, email, and identity protection from single vendors to reduce integration overhead. This preference shift is most visible in North American healthcare and financial services verticals, where procurement teams prioritize vendor reduction over feature depth.
Endpoint Security Solutions Market Segmentation
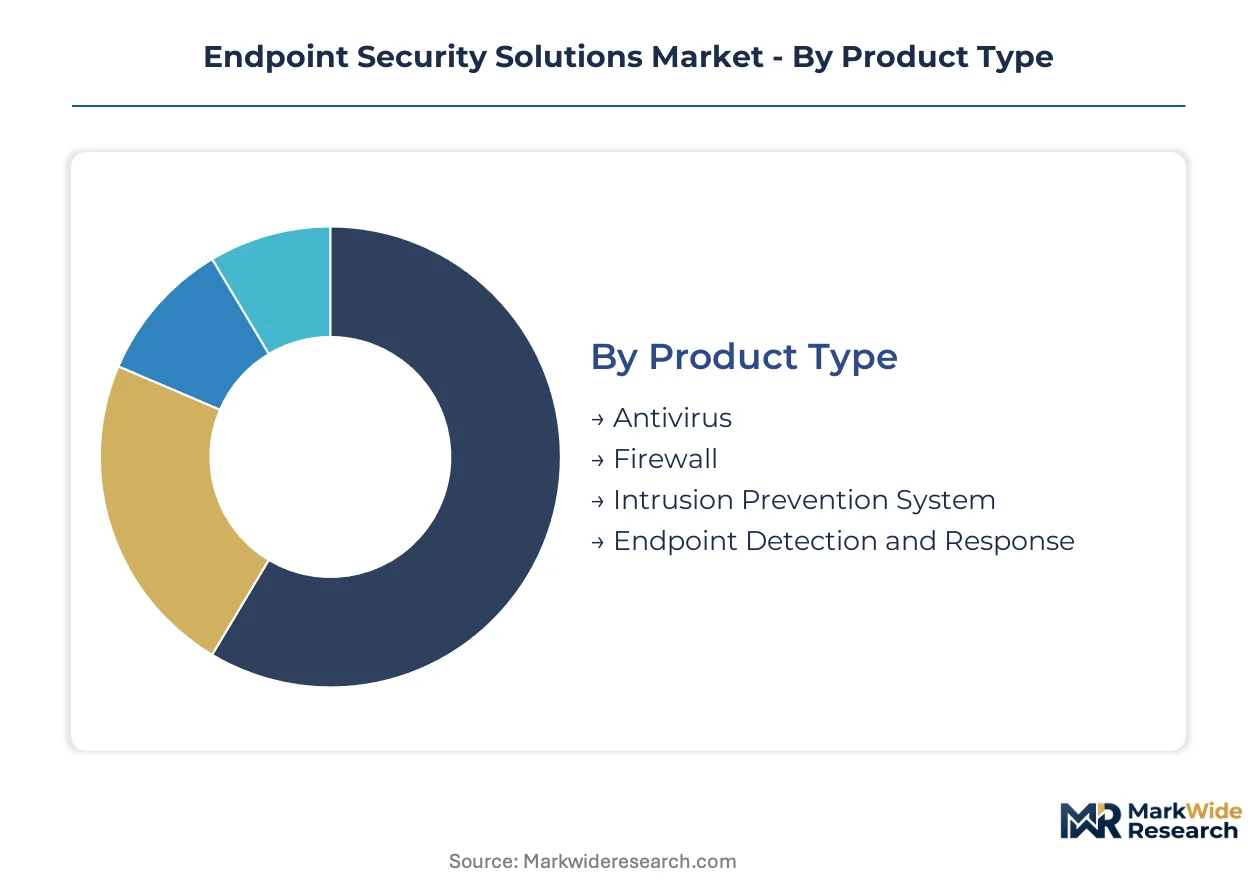
Segmentation in endpoint security reveals how procurement priorities diverge across organizational maturity and risk tolerance. Buyers select product architectures and delivery models that match their internal security operations capabilities and regulatory exposure profiles.
Product Type:
Mature prevention technologies anchor baseline protection budgets while behavioral detection platforms capture incremental investment from security-mature organizations.
- Antivirus:Signature-based malware scanning engines provide foundational threat blocking through known-pattern matching. Healthcare delivery networks in the United States deploy these agents across clinical workstations to satisfy HIPAA technical safeguard requirements.
- Endpoint Detection and Response:Continuous behavioral telemetry platforms enable threat hunting through process-level activity monitoring. Federal agencies subject to CISA Binding Operational Directive 22-01 procurement mandates prioritize these tools for asset visibility.
- Firewall:Host-based network traffic filtering controls inbound and outbound connections at the device perimeter. Manufacturing facilities with operational technology convergence deploy these for protocol-aware segmentation.
- Intrusion Prevention System:Real-time exploit blocking mechanisms inspect network packets and system calls for attack signatures. Energy sector operators in EU member states subject to NIS2 Directive risk management requirements specify these for critical infrastructure protection.
Endpoint Detection and Response handles the majority of throughput; Endpoint Detection and Response is the fastest mover on share.
Deployment Model:
Cost tier stratification separates self-managed infrastructure from fully outsourced security operations, with hybrid architectures serving transition-state buyers.
- Cloud-Based:Agent software delivered through SaaS consoles eliminates server infrastructure and accelerates deployment across distributed workforces. Mid-market professional services firms in India select these models to bypass capital expenditure approval cycles.
- Managed Service:Third-party security operations centers assume monitoring, alert triage, and incident response responsibilities under recurring contracts. European SMEs lacking certified security personnel outsource to specialized providers to satisfy EU AI Act oversight documentation requirements.
- On-Premises:Software and control infrastructure deployed within customer data centers satisfies data residency and air-gapped security requirements. Defense contractors in the United States with classified network obligations maintain these deployments.
- Hybrid:Mixed architectures combine on-premises management consoles with cloud-delivered threat intelligence and agent updates. Financial institutions in Germany balance latency-sensitive local processing with elastic cloud analytics.
Cloud-Based deployments capture the largest addressable base; Managed Service contracts are climbing the fastest as skills gaps persist.
End User:
Customer type determines feature depth requirements and procurement sophistication, with government buyers imposing certification barriers that reshape vendor qualification.
- Large Enterprises:Organizations with mature security operations centers demand integrated platforms correlating endpoint telemetry with network and identity signals. United States healthcare systems with connected medical device fleets prioritize these for infusion pump and imaging system isolation.
- Government:Civilian and defense agencies mandate FedRAMP authorization and zero-trust architecture compliance in procurement specifications. CISA operational directives create immediate demand pull across federal civilian networks.
- SMEs:Resource-constrained buyers prioritize bundled solutions reducing vendor count and integration overhead. Cloud-based endpoint protection with simplified management consoles serves these buyers in North American financial services verticals.
- Education:K-12 and higher education institutions balance open network access requirements against student data privacy obligations. State-funded universities in the United States deploy these solutions to protect research intellectual property.
Large Enterprises handle the majority of throughput; Government verticals are gaining share fastest through mandate-driven procurement acceleration.
Service Type:
Margin concentration shifts toward recurring delivery models as product commoditization pressures implementation and training revenue.
- Maintenance:Subscription renewals covering threat signature updates, software patches, and technical support generate predictable revenue streams. Vendors anchor customer lifetime value through these contracts in the United States federal sector.
- Consulting:Risk assessments, architecture design, and compliance readiness evaluations command premium day rates from specialized practitioners. EU critical infrastructure operators procure these services to document NIS2 Directive conformity.
- Implementation:Deployment planning, agent rollout, and policy configuration services accompany initial product sales. Indian smart city authorities engage these services for endpoint protection integration with national payment network infrastructure.
- Training:Security operations certification programs and end-user awareness education reduce alert fatigue and false positive generation. Healthcare delivery networks in the United States invest in these programs to optimize EDR tool utilization.
Maintenance contracts handle the majority of throughput; Consulting services are expanding most quickly as regulatory complexity deepens.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Buyers in India and Southeast Asia exhibit acute price sensitivity, squeezing vendor margins on standardized endpoint agents. German and United States procurement teams absorb premium pricing for integrated platforms with compliance documentation. This elasticity divergence shapes regional go-to-market architectures.
United States
Federal civilian agencies and defense contractors drive concentrated demand through zero-trust procurement mandates. CISA binding operational directives compress deployment timelines to ninety-day windows. The Washington-Baltimore corridor anchors vendor sales operations serving intelligence community and civilian agency accounts.
Germany
Automotive manufacturers and industrial machinery producers prioritize endpoint agents with operational technology protocol awareness. EU NIS2 Directive risk management obligations expand procurement budgets for energy and transport operators. The Munich-Stuttgart manufacturing belt concentrates deployment of specialized agents for production floor isolation.
India
Mid-market professional services firms and national payment network operators seek cloud-delivered endpoint protection without capital expenditure cycles. RBI cybersecurity guidelines for financial institutions accelerate compliance-driven procurement. Mumbai and Bengaluru technology corridors host the fastest-growing managed security service provider ecosystems.
Japan
Financial services conglomerates and precision electronics manufacturers demand endpoint solutions with localized threat intelligence feeds. METI cybersecurity framework updates mandate enhanced logging and incident response capabilities. The Tokyo-Osaka industrial corridor sustains premium pricing for solutions with domestic language support and data residency guarantees.
United Kingdom
London-based financial services firms and national health service trusts balance endpoint protection against legacy system compatibility constraints. NCSC cyber assessment framework requirements shape procurement specifications for critical national infrastructure operators. The Cambridge-Oxford-London technology triangle concentrates venture-backed endpoint security startups targeting SME segments.
Endpoint Security Solutions Market Vendor Landscape
Capability concentration sits with pure-play endpoint specialists; scale advantage sits with platform conglomerates bundling protection with productivity suites. The market structures around three tiers: cloud-native specialists with behavioral telemetry dominance, network security incumbents extending into endpoint agents, and productivity software vendors subsidizing endpoint tools through enterprise contracts. Dominant competitive moves include strategic acquisitions of threat intelligence providers and API-based integration partnerships stitching endpoint telemetry into broader security fabrics.
Within the cloud-native specialist tier, CrowdStrike and SentinelOne exemplify architecture-first positioning built on single-agent telemetry platforms. Microsoft occupies a distinct scale-driven position, leveraging existing enterprise productivity contract relationships to displace standalone endpoint vendors. Palo Alto Networks anchors the network-to-endpoint convergence archetype, representing firewall incumbents extending control plane integration into device-level protection. These three patterns—specialist telemetry depth, platform bundling leverage, and network security extension—capture the competitive geometry reshaping procurement decisions.
| Leading Market Players |
|---|
| Microsoft |
| CrowdStrike |
| SentinelOne |
| Palo Alto Networks |
| Broadcom |
| Trellix |
| Trend Micro |
| McAfee |
| Bitdefender |
| Others |
Supply Flow & Price Mechanics
The Singapore-Amsterdam data corridor carries threat intelligence feeds and agent updates between Asia-Pacific development centers and European critical infrastructure operators, with bandwidth costs and latency premiums concentrating pricing power among cloud-native vendors while compressing margins for on-premises specialists serving mid-market buyers in India and Southeast Asia.
Pricing Analysis
Recurring maintenance and managed detection response contracts generate the majority of lifetime value as perpetual licenses decline. Three-tier pricing structure across premium, standard, and economy levels segments buyers by security operations maturity, with federal agencies absorbing FedRAMP-authorized premiums while Indian SMEs select stripped-down SaaS tiers. Cost compression in the mid-market intensifies because Microsoft bundles endpoint agents with existing productivity contracts. Healthcare delivery networks in the United States exhibit the lowest price sensitivity due to HIPAA penalty exposure, whereas Indian professional services firms negotiate aggressively on per-endpoint rates.
Supply Chain Analysis
Threat intelligence feedstock draws from specialized providers concentrated in Israel, the United States, and the United Kingdom, with behavioral detection algorithms resting on curated indicator-of-compromise databases and malware sandboxing infrastructure. CPU and memory optimization for endpoint agents hinges on semiconductor fabrication in Taiwan and South Korea. Single-source vulnerability in cloud-hosted management consoles creates concentration risk for European operators subject to EU AI Act data residency requirements. Distribution runs through direct enterprise sales teams for large accounts and managed security service providers for SME penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed detection and response services expand faster than hardware agents, with recurring revenue pools deepening as skills shortages persist across security operations centers.
For Market Incumbents: Insulate platform stickiness through API-based integration partnerships that stitch endpoint telemetry into broader security fabrics, countering Microsoft's bundling leverage. Deepen vertical integration into threat intelligence acquisition to reduce feedstock cost exposure. FedRAMP authorization investments anchor federal procurement positioning against emerging cloud-native specialists. For New Entrants and Emerging Players: India's national payment network infrastructure and smart city deployments present underpenetrated greenfield demand with compressed procurement cycles. Target mid-market professional services firms lacking internal security operations centers with managed service packaging. Lead with simplified cloud-native deployment to bypass capital expenditure approval barriers. For Investors and Strategic Acquirers: The EU AI Act risk classification requirements reshape the acquisition landscape toward vendors with documented algorithmic transparency and human oversight mechanisms. Position for consolidation plays around behavioral telemetry specialists with federal certification moats. Watch CISA operational directive expansion into civilian agency procurement as the signal for mandate-driven demand inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | API-based telemetry stitching reduces swivel-chair analysis between endpoint and network consoles for federal SOC operators. |
| Acquisition of Specialist Firm | Threat intelligence provider purchases secure curated IOC feedstock against rising subscription costs. |
| Regulatory Certification Pathway | FedRAMP and EU AI Act documentation investments unlock procurement eligibility for critical infrastructure verticals. |
| Managed Service Expansion | Outsourced SOC capabilities capture recurring revenue from SME buyers facing thirty-percent analyst vacancy rates. |
| Geographic Expansion | India and Southeast Asia greenfield deployments bypass entrenched vendor relationships in mature markets. |
Methodological Framework
Operator-level perspectives from CISOs, security operations center directors, federal procurement officers, and managed security service provider executives anchored the qualitative base. Primary interviews combined with secondary validation against CISA operational directives, EU NIS2 implementation guidance, NIST zero-trust architecture publications, and vendor SEC filings. Bottom-up endpoint deployment estimates triangulated against top-down security spending benchmarks from healthcare, financial services, and federal verticals.
Scenario-bracketing framed demand trajectories across the analysis window, with segmentation modeling across deployment model, organization size, vertical risk exposure, and regulatory jurisdiction. CAGRs derived from weighted regression of historical procurement velocity against mandate implementation timelines. Forecast inputs incorporated connected medical device proliferation rates and federal zero-trust compliance deadlines.
The forecast holds incumbent behavior within observed patterns; aggressive platform bundling moves by productivity software vendors or accelerated EU AI Act enforcement would shift outcomes. Cross-checking against CISA procurement pipeline disclosures and hospital system EDR deployment announcements is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Saudi Arabia Managed Security Services Market
Security Software
Source Code Escrow Market
Security Software
Global User Provisioning Market
Security Software
Global Electronic Offender Monitoring Solutions Market
Security Software
Extended Detection and Response Market
Security Software
Facial Recognition Market
Security Software
Application Control Software Market
Security Software
Europe Encryption Software Market
Security Software
Patch and Remediation Software Market
Security Software
VPN Software Market
Security Software
Global Security Orchestration Automation and Response (SOAR) Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Global Background Screening Market
Security Software
Hardware Encryption Market
Security Software
Mobile Identity Management Market
Security Software
Managed Security Services Market