
 Global Content Disarm and Reconstruction Market | 2026-2036
Global Content Disarm and Reconstruction Market Size, Share, and Industry Trends Forecast 2026-2036
Global Content Disarm and Reconstruction Market Foresight
Enterprise-grade file sanitization is unwinding legacy antivirus dependencies across high-threat verticals. Fortinet leverages its integrated security fabric to anchor CDR modules within broader firewall deployments. OPSWAT specializes in cross-domain file transfer protection, dominating critical infrastructure segments where air-gapped environments require rigorous content reconstruction protocols.
Content Disarm and Reconstruction refers to the automated process of deconstructing inbound files to remove executable code, active content, and embedded threats, then rebuilding sanitized versions that retain original usability while eliminating attack vectors. The technology operates through deep file inspection, structural analysis, and policy-driven reconstruction to deliver threat-neutralized documents to end users. Cloud-Based deployment leads adoption among mid-market enterprises seeking rapid implementation without capital infrastructure, while Managed Services offerings capture expanding margin pools as organizations outsource specialized security operations. Email Security applications remain the largest addressable segment given persistent phishing volume, though Endpoint Protection integration is accelerating as hybrid work models extend corporate perimeters.
The European Union Agency for Cybersecurity enforces NIS2 compliance standards that mandate proactive threat neutralization for essential service operators, directly expanding CDR procurement across energy and transport sectors. The United States Cybersecurity and Infrastructure Security Agency publishes binding operational directives requiring federal civilian agencies to implement zero-trust capabilities, including content verification at network boundaries. Stakeholders must evaluate whether hybrid deployment architectures or pure SaaS delivery better align with evolving data sovereignty requirements and cross-border transfer restrictions.
Market Dynamics
Zero-trust security mandates from the United States Cybersecurity and Infrastructure Security Agency are forcing federal contractors to rebuild file-handling infrastructure around content verification at network boundaries rather than perimeter detection.
Growth Catalysts
- NIS2 Directive:The European Union Agency for Cybersecurity enforces proactive threat neutralization for essential service operators, directly expanding procurement across energy and transport sectors in member states.
- Cloud-Based deployment:Mid-market enterprises favor rapid implementation without capital infrastructure, accelerating subscription revenue models over perpetual licensing.
- Financial services:Banking and insurance firms expand file sanitization technology to neutralize malware before it reaches trading floors and customer-facing endpoints.
Market Restraints
- Deep file inspection latency:Real-time reconstruction of complex document formats introduces processing delays that conflict with high-velocity trading environments and time-sensitive workflows.
- Specialized engineering talent:Scarce expertise in file format internals and reverse engineering concentrates compensation costs in Silicon Valley and Tel Aviv clusters.
- Legacy antivirus substitution resistance:Incumbent endpoint protection vendors bundle detection-based tools at marginal cost, compressing standalone CDR pricing power in cost-conscious accounts.
Strategic Opportunities
- Managed Services:Organizations outsource specialized security operations to providers delivering 24/7 content reconstruction with guaranteed service-level agreements.
- Endpoint Protection integration:Hybrid work models extend corporate perimeters beyond traditional network boundaries, creating attach points for CDR modules in distributed agent architectures.
- India:Digital infrastructure expansion under RBI cybersecurity guidelines creates demand for file sanitization in banking, insurance, and securities trading workflows.
Industry Challenges
- Air-gapped environment deployment:Critical infrastructure operators require offline-capable reconstruction engines that operate without cloud connectivity, complicating update distribution and threat intelligence synchronization.
- File format proliferation:Proprietary document standards in design software, medical imaging, and engineering applications demand continuous parser development to maintain sanitization coverage.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Content Disarm and Reconstruction Market |
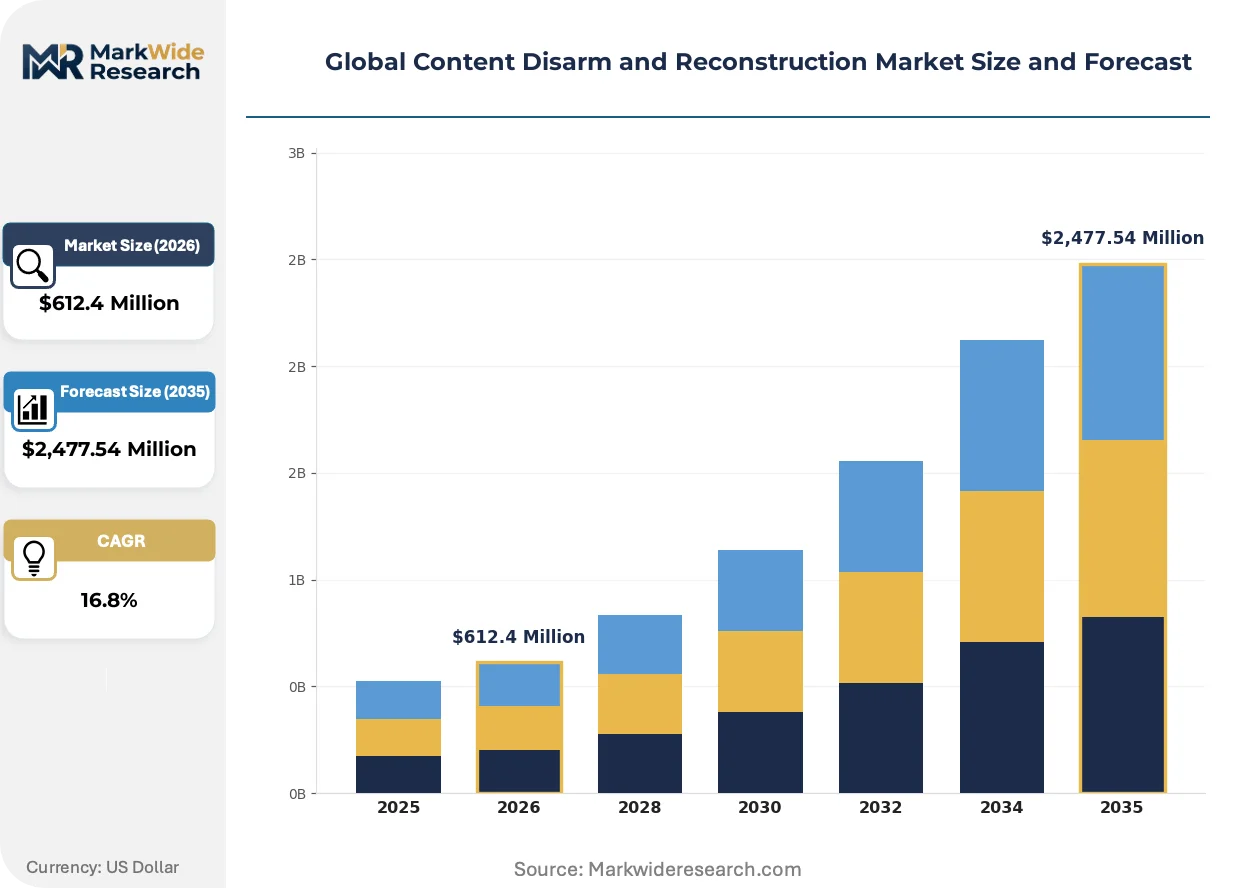
| Market Size in 2026 | $612.4 Million |
| Market Size in 2035 | $2,477.54 Million |
| CAGR (2026 – 2036) | 16.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Virtual Appliance Offering: Standalone, Integrated, Managed Services, Software as a Service Application: Email Security, Web Security, Endpoint Protection, Data Loss Prevention End User: BFSI Institutions, Government Agencies, IT & Telecom Providers, Education Institutions |
| Companies Covered | Check Point Software Technologies, Fortinet, OPSWAT, Broadcom, Glasswall Solutions, Deep Secure, Votiro, ReSec Technologies, Sasa Software, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Content Disarm and Reconstruction Market Shifts & Advancements
Automated content reconstruction is displacing detection-dependent security models as organizations recognize that signature-based tools fail against polymorphic threats and zero-day exploits.
Structural analysis engines are decomposing inbound files into constituent elements—stripping macros, embedded scripts, and active content—then rebuilding sanitized versions that retain original usability. Energy sector operators in Germany and France deploy these systems at OT-IT boundaries to protect industrial control networks. The technology is decomposing traditional antivirus market share by eliminating the detection-to-remediation gap entirely.
The EU AI Act establishes conformity assessment requirements for automated decision systems processing sensitive content, compelling vendors to document reconstruction logic and audit trails. Industrial consequence includes mandatory algorithmic transparency for critical infrastructure deployments. Energy and transport sectors most affected are restructuring procurement specifications to include explainability clauses and third-party validation.
Subscription pricing for cloud-delivered sanitization is displacing perpetual licenses as buyers prioritize operational expenditure treatment and rapid scaling. Value-added resellers and managed security service providers capture expanding margin pools by bundling CDR with broader threat detection portfolios. This shift concentrates most visibly in United States federal contracting, where agencies mandate consumption-based pricing aligned with appropriations cycles.
Global Content Disarm and Reconstruction Market Segmentation
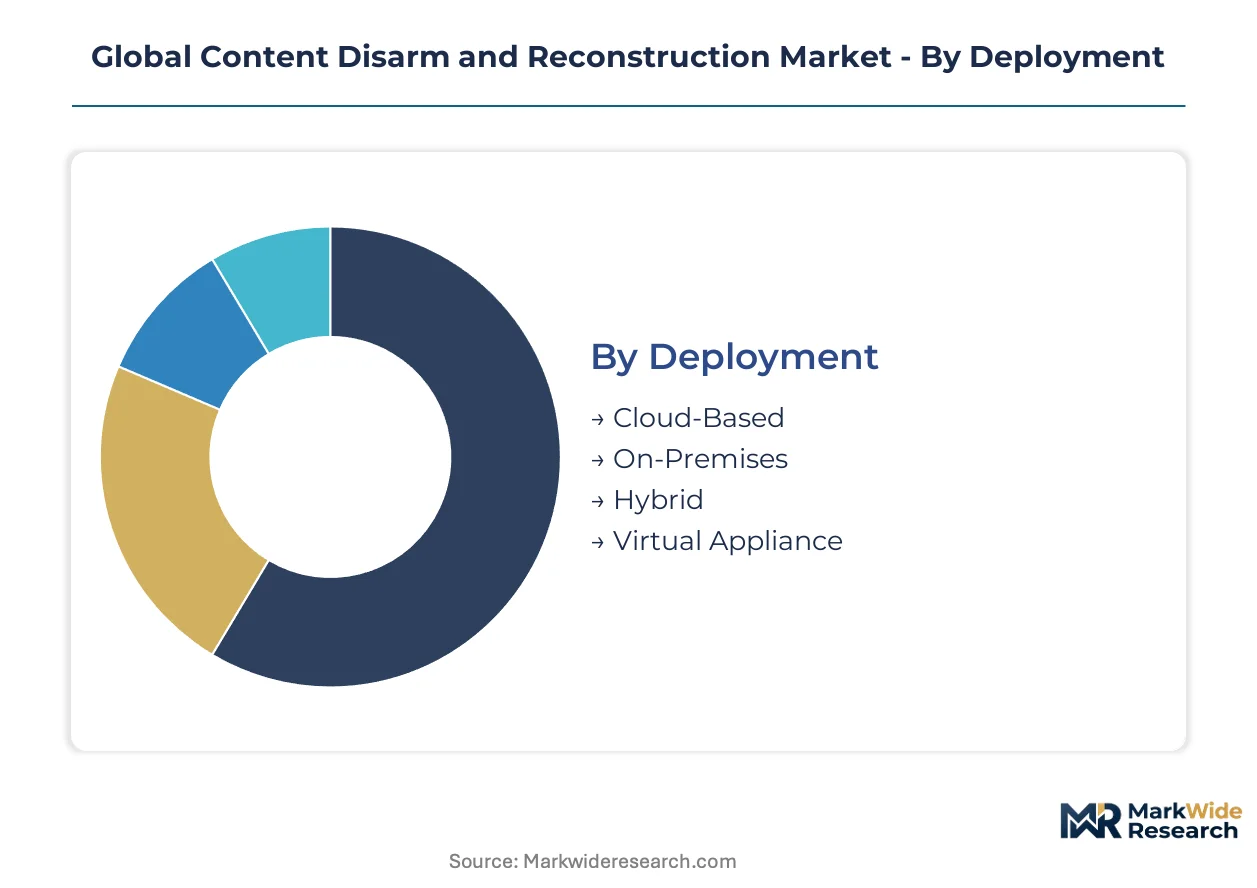
Deployment architecture determines procurement patterns across regulated and unregulated environments. Buyers select models based on data residency obligations, air-gap requirements, and operational sovereignty constraints.
Deployment:
Cloud-Based solutions dominate export-led procurement from United States and Israeli vendors into European and Asia-Pacific accounts. On-Premises deployments concentrate in domestic critical infrastructure where national security regulations mandate local processing.
- Cloud-Based:Multi-tenant architectures deliver reconstruction engines through browser-accessible consoles without customer-managed infrastructure. Demand concentrates among mid-market enterprises in Germany and the United Kingdom seeking rapid activation without capital commitment. Subscription economics align with CFO preferences for operational expenditure classification.
- On-Premises:Self-hosted appliances install within customer data centers with complete data sovereignty. Procurement runs heaviest through government agencies in France and energy operators in Saudi Arabia subject to strict data localization mandates. Capital-intensive licensing persists where cloud connectivity is prohibited or distrusted.
- Hybrid:Split architectures process routine files through cloud pipelines while reserving sensitive content for on-premises engines. Financial services firms in Singapore and Switzerland deploy this model to balance efficiency with regulatory compartmentalization.
- Virtual Appliance:Software-defined instances deploy on existing hypervisor infrastructure without dedicated hardware. Manufacturing conglomerates in Japan favor this approach to leverage sunk virtualization investments while adding sanitization capabilities.
Cloud-Based commands the established base. The steepest expansion runs through Hybrid architectures bridging sovereignty and scalability demands.
Offering:
Standalone products attract buyers with existing security stacks seeking best-of-breed reconstruction depth. Integrated modules capture customers prioritizing vendor consolidation and unified policy management.
- Standalone:Purpose-built platforms deliver specialized file sanitization with granular format support and custom policy engines. Defense contractors in the United States and intelligence agencies in Israel procure these for maximum reconstruction fidelity independent of broader security ecosystems.
- Integrated:Embedded modules within firewall, email gateway, or endpoint platforms trade depth for operational simplicity. Managed security service providers across Europe bundle these to reduce agent sprawl and console fragmentation for mid-market clients.
- Managed Services:Outsourced operations deliver 24x7 content reconstruction with guaranteed service levels and threat analyst escalation. Healthcare networks in Australia and municipal governments in Canada adopt these to address skills shortages without internal security operations center investment.
- Software as a Service:Pure subscription delivery eliminates version management and patch cycles through vendor-controlled infrastructure updates. Rapid adoption among professional services firms in India and Brazil reflects preference for consumption-aligned pricing without depreciation schedules.
Integrated offerings capture volume through platform bundling. Managed Services climbs fastest as skills scarcity deepens across all geographies.
Application:
Email Security absorbs the highest file volume given persistent phishing campaigns targeting credential theft and malware delivery. Web Security intercepts drive-by downloads and compromised legitimate sites serving weaponized documents.
- Email Security:Gateway and cloud-email integrations sanitize attachments before inbox delivery, neutralizing macro-laden Office documents and compressed executable payloads. Banking regulators in the United Kingdom and insurance supervisors in Germany mandate this protection for customer-facing correspondence channels.
- Web Security:Proxy and secure web gateway deployments reconstruct files downloaded from external sites or cloud storage services. Technology companies in Ireland and media firms in South Korea deploy these to protect creative workstations accessing external asset libraries.
- Endpoint Protection:Agent-based reconstruction operates on devices beyond traditional network perimeters. Hybrid work expansion drives procurement among professional services partnerships in the United States and consulting networks in the Netherlands.
- Data Loss Prevention:Outbound content sanitization prevents exfiltration of sensitive data through reconstructed file formats. Pharmaceutical manufacturers in Switzerland and intellectual property-intensive firms in Japan layer this capability over existing DLP policy engines.
Email Security retains the volume anchor. Endpoint Protection expands most quickly as distributed workforces multiply attack surfaces beyond centralized gateways.
End User:
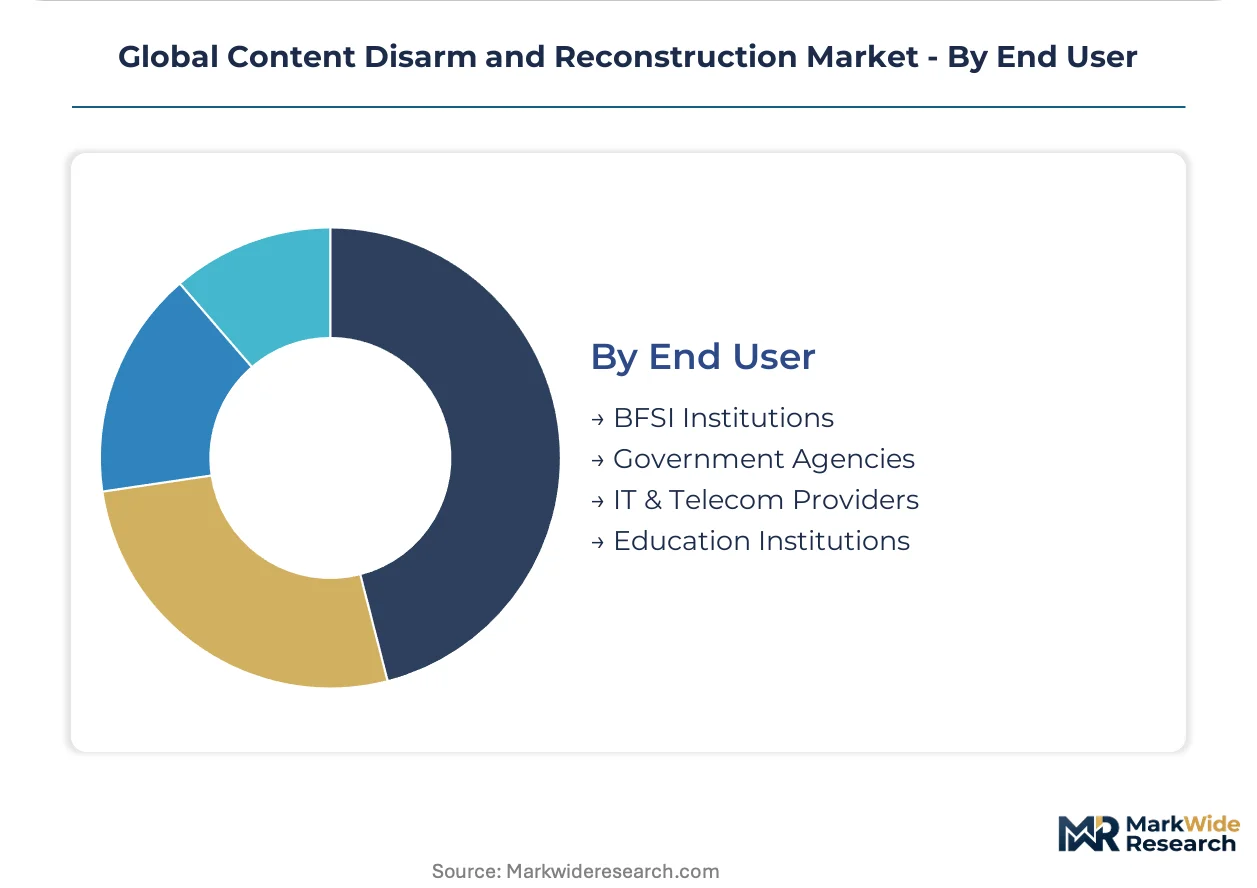
BFSI Institutions generate concentrated demand due to regulatory pressure and high-value transaction environments. Government Agencies follow with procurement driven by national security directives and supply chain protection mandates.
- BFSI Institutions:Banks, insurers, and securities firms deploy reconstruction to protect trading floors, customer portals, and interbank messaging. RBI cybersecurity guidelines in India and ECB operational resilience expectations in Frankfurt drive synchronized procurement cycles across retail and investment banking.
- Government Agencies:Civilian and defense departments mandate content verification at network boundaries under binding operational directives. CISA zero-trust mandates in the United States and NIS2 implementation across EU member states structure multi-year deployment roadmaps.
- IT & Telecom Providers:Managed service and infrastructure operators embed sanitization within customer-facing security portfolios. Cloud hyperscalers in the United States and telecommunications incumbents in Germany bundle reconstruction into multi-tenant platform offerings.
- Education Institutions:Universities and research networks protect heterogeneous user populations with limited security awareness. Federal research funding requirements in the United States and GDPR compliance obligations in European higher education accelerate adoption.
BFSI Institutions anchor current revenue concentration. Government Agencies demonstrate the steepest budget trajectory as sovereign cyber defense investments accelerate.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export flows from United States and Israeli vendors dominate cross-border procurement into European and Asia-Pacific accounts, while import substitution policies in critical infrastructure sectors reshape local sourcing patterns. Sovereign data requirements fragment deployment architectures across jurisdictions. Regulatory divergence between CISA zero-trust mandates and EU NIS2 implementation creates compliance complexity for multinational operators.
United States
Federal civilian agencies drive procurement volume under binding operational directives mandating content verification at network boundaries. CISA publishes zero-trust architecture requirements that force contractors to rebuild file-handling infrastructure around verification rather than detection. Defense contractors in Northern Virginia and cybersecurity clusters in Silicon Valley anchor domestic vendor development.
Germany
Energy operators and automotive manufacturers expand reconstruction deployments at OT-IT boundaries to protect industrial control networks. The national cybersecurity authority enforces NIS2 implementation timelines for essential service operators across energy and transport sectors. Industrial automation hubs in Bavaria and Baden-Württemberg concentrate deployment of air-gapped reconstruction engines.
United Kingdom
Banking regulators mandate file sanitization for customer-facing correspondence channels across retail and investment banking. The national cybersecurity center publishes guidelines on proactive threat neutralization for financial services infrastructure. London's financial district and Manchester's growing fintech cluster drive concentrated procurement cycles.
India
Digital infrastructure expansion under RBI cybersecurity guidelines creates demand for file sanitization in banking, insurance, and securities trading workflows. The central bank's operational resilience expectations synchronize procurement across retail and investment banking. Mumbai's financial district and Bangalore's technology corridor anchor domestic implementation.
Israel
Intelligence agencies and defense contractors procure specialized reconstruction platforms for maximum fidelity independent of broader security ecosystems. National cybersecurity directives emphasize proactive neutralization for critical infrastructure protection. Tel Aviv's cybersecurity cluster concentrates scarce expertise in file format internals and reverse engineering.
Global Content Disarm and Reconstruction Market Competitive Landscape
Listed leaders compete with private specialists across integrated platform versus standalone depth dimensions. The vendor base organizes into three tiers: network security incumbents bundling reconstruction modules, purpose-built CDR specialists delivering granular format support, and managed security service providers wrapping sanitization into outsourced operations. Dominant competitive moves include strategic partnerships with cloud email providers and geographic expansion through value-added reseller networks.
Within the network security tier, Fortinet exemplifies platform bundling strategy, while Check Point Software Technologies occupies a comparable integrated position. Among standalone specialists, OPSWAT represents purpose-built reconstruction depth for cross-domain file transfer protection. These three anchors illustrate the fundamental strategic divergence between breadth-first platform attachment and depth-first specialization that structures competitive positioning across procurement segments.
| Leading Market Players |
|---|
| Check Point Software Technologies |
| Fortinet |
| OPSWAT |
| Broadcom |
| Glasswall Solutions |
| Deep Secure |
| Votiro |
| ReSec Technologies |
| Sasa Software |
| Others |
Supply & Pricing Matrix
Consumption-based subscription contracts with guaranteed service-level agreements lock in multi-year supply access for federal agencies while providing vendors with predictable recurring revenue visibility across appropriations cycles.
Pricing Analysis
Government procurement officers anchor pricing negotiations around FedRAMP-authorized SaaS tiers with consumption-based metering. Pricing stratifies across enterprise, mid-market, and entry-level tiers based on file volume throughput and format complexity coverage. Cost compression in the mid-market segment is intensifying because bundled endpoint protection vendors add basic reconstruction at marginal cost. Financial services firms demonstrate lowest price sensitivity given regulatory mandate pressure, while municipal governments exhibit highest sensitivity due to fixed annual IT budgets.
Supply Chain Analysis
Inventory lead times for specialized reverse engineering talent extend 6-9 months for parser development teams in Tel Aviv and Silicon Valley. Software development concentrates in Israel, the United States, and India, with critical file format expertise anchored in Tel Aviv's cybersecurity cluster. Component dependencies include proprietary parsing engines, threat intelligence feeds, and cloud infrastructure from hyperscalers. Single-source vulnerability concentrates in specialized file format reverse engineering talent pools. Distribution runs through value-added resellers and managed security service providers into end-user accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
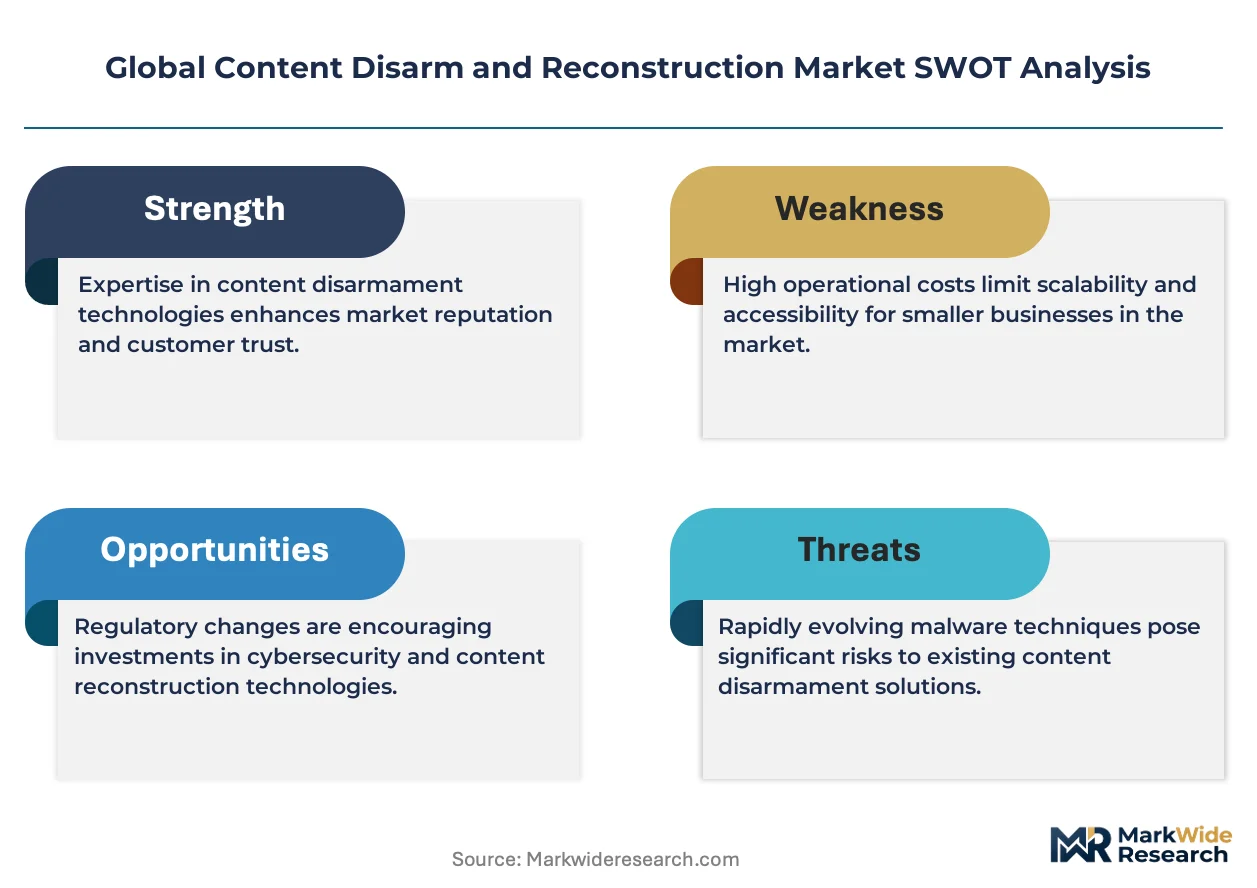
Scarcity of engineers with deep file format internals expertise constrains vendor expansion velocity and inflates compensation costs in talent clusters, creating sustainable moats for incumbent specialists.
For Market Incumbents: Compound platform stickiness by embedding reconstruction modules within broader zero-trust fabric deployments to raise switching costs. Deepen vertical integration into proprietary parsing engine development rather than licensing third-party format libraries, defending against margin erosion from detection-based endpoint bundling. For New Entrants and Emerging Players: Air-gapped deployment capabilities for critical infrastructure operators represent an underserved service layer where incumbents prioritize cloud-native architectures. Municipal governments and regional healthcare networks in Canada and Australia present the most penetrable segment given skills shortages and budget constraints. Lead with managed services wrap offering 24x7 analyst escalation rather than standalone product sales. For Investors and Strategic Acquirers: The market sits at a consolidation phase that favors specialists with proven parser libraries and federal certification pathways. Long-term viability hinges on sustained regulatory tailwinds from CISA mandates and NIS2 implementation rather than cyclical IT spending. Target acquisition archetypes include Israeli reverse engineering teams with deep format expertise and established FedRAMP authorizations. Watch for inflection signals in federal civilian agency procurement velocity under binding operational directives.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Pathway | Federal contractors must achieve FedRAMP Moderate to compete for CISA-mandated deployments. |
| Parser Library Expansion | Proprietary medical imaging and CAD format support differentiates vendors in manufacturing and healthcare verticals. |
| Managed Services Buildout | 24x7 SOC-backed reconstruction addresses skills gaps in municipal and mid-market accounts. |
| OT-IT Boundary Integration | German energy operators require air-gapped engines protecting industrial control networks. |
| Channel Partner Certification | Value-added resellers capture margin pools by bundling CDR with broader threat detection portfolios. |
Research Methodology
Cross-validation between primary executive interviews and secondary regulatory filings anchors the qualitative findings on procurement patterns. Chief information security officers, federal contracting officers, managed security service provider executives, and file format engineering leads contributed structured input. Secondary sources include CISA binding operational directives, ENISA NIS2 implementation guidance, SEC cybersecurity disclosure filings, and federal procurement databases. Bottom-up deployment modeling triangulates against top-down regulatory mandate sizing.
Sensitivity analysis tests forecast outputs against variable adoption timelines for zero-trust mandates and NIS2 enforcement intensity. The analytical framework segments by deployment architecture, offering type, application layer, and end-user vertical across the projection horizon. Modeled dimensions include cloud versus on-premises mix, standalone versus integrated attachment rates, and federal versus commercial procurement splits. CAGRs derive from regression against historical compliance-driven security spending and policy announcement impact lags. Input assumptions incorporate FedRAMP authorization backlogs and critical infrastructure operator procurement cycles.
Underlying assumptions cover sustained regulatory enforcement, cloud infrastructure availability, and talent pool expansion rates, with deviation risk concentrated in federal budget appropriation delays and air-gap deployment technical barriers. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Germany Cybersecurity Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
DNS Firewall Market
Cybersecurity
Global Cloud Security Posture Management Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
China Ransomware Protection Market
Cybersecurity
Global Database Encryption Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Global Zero-Trust Security Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
United States Cybersecurity Market