
 Norway Cybersecurity Market | 2026-2036
Norway Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Norway Cybersecurity Market Analytics
A chronic shortage of Nordic security architects is redrawing competitive dynamics across the Norwegian market. Mnemonic AS leverages its Oslo-based SOC workforce to anchor domestic incident response contracts. Telenor Cyberdefence sustains channel control through direct fiber infrastructure and sovereign data routing. IBM Corporation competes via consulting-led transformation engagements with Statoil-affiliated energy suppliers.
Norway cybersecurity encompasses defensive technologies, managed services, and risk frameworks protecting digital assets against unauthorized access, disruption, or exfiltration across enterprise and critical infrastructure environments. Solutions integrate AES-256 encryption, behavioral anomaly detection, and zero-trust network architectures to enforce confidentiality and operational continuity. Cloud-based deployment is capturing fastest expansion as Equinor-linked suppliers migrate OT monitoring to hybrid environments. Managed Security services concentrate margin pools where multi-year MDR contracts bundle threat hunting with regulatory attestation. On-Premises retains dominance in submarine cable landing stations and defense-adjacent facilities requiring air-gapped segmentation.
Norwegian Personal Data Act provisions and NIS2 transposition through the country's digitalization ministry shape mandatory incident reporting timelines and supply-chain security obligations. The Norwegian National Security Authority (NSM) enforces sector-specific ICT baseline standards for oil, gas, and electric grid operators. Stakeholders must monitor whether proposed EU Cyber Resilience Act certification requirements will force hardware and software vendors serving Norwegian critical infrastructure to absorb compliance costs or pass them downstream.
Market Dynamics
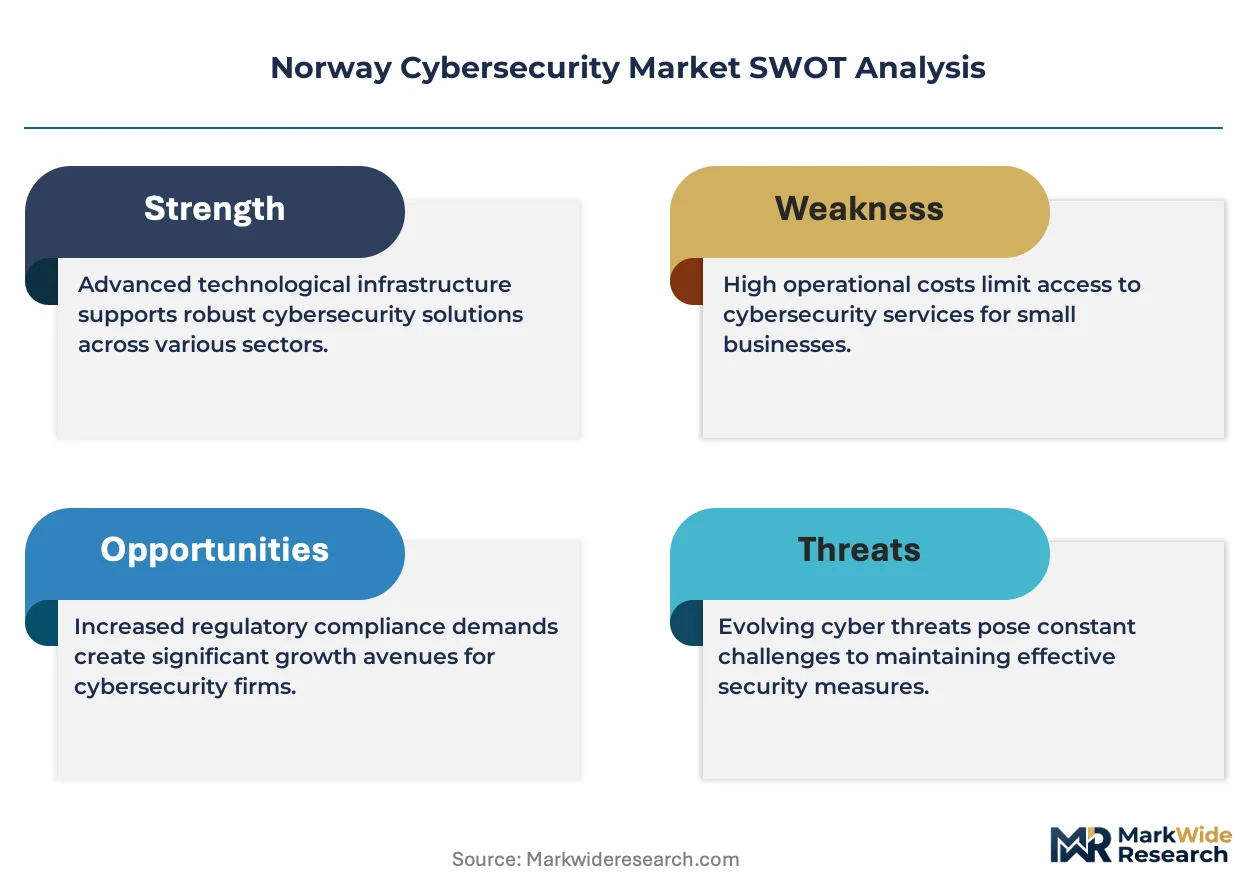
NIS2 transposition through Norway's digitalization ministry is compressing procurement cycles as energy operators accelerate security upgrades ahead of enforcement deadlines. The resulting budget reallocation is redrawing vendor selection criteria across oil, gas, and electric grid infrastructure.
Growth Catalysts
- Critical Infrastructure Mandates:NSM-enforced ICT baseline standards for oil and gas operators mandate continuous monitoring systems. Electric grid utilities must upgrade SCADA segmentation under the same framework.
- Hybrid Cloud Migration:Equinor-linked suppliers are migrating OT monitoring to hybrid environments, creating demand for cloud-native security orchestration platforms.
- Submarine Cable Protection:Landing station operators in Stavanger and Oslo require air-gapped segmentation for undersea fiber infrastructure, sustaining on-premises deployment demand.
Market Restraints
- Nordic Talent Scarcity:Security architect shortages in Oslo and Stavanger inflate implementation timelines and professional services costs.
- Compliance Cost Pass-Through:Proposed EU Cyber Resilience Act certification requirements may force hardware vendors serving Norwegian critical infrastructure to absorb compliance expenses or exit the market.
- Sovereign Data Routing Constraints:Telenor's fiber infrastructure dominance limits alternative provider market entry and compresses price competition in managed security services.
Strategic Opportunities
- Western Norway Energy Corridor:Stavanger-based offshore suppliers remain underpenetrated for managed detection and response services bundled with regulatory attestation.
- Zero-Trust Convergence:Integration of behavioral anomaly detection with AES-256 encryption protocols creates differentiated positioning for domestic SOC operators.
- Defense-Adjacent Facilities:Air-gapped segmentation requirements at classified installations present captive demand for specialized on-premises security architecture.
Industry Challenges
- Multi-Year Contract Talent Lock-In:Security analysts bound to Mnemonic AS and Telenor Cyberdefence SOC operations are unavailable for competitor hiring, constraining service expansion.
- Legacy OT Integration Complexity:Behavioral anomaly detection deployment requires retrofitting decades-old industrial control systems without operational disruption.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Norway Cybersecurity Market |
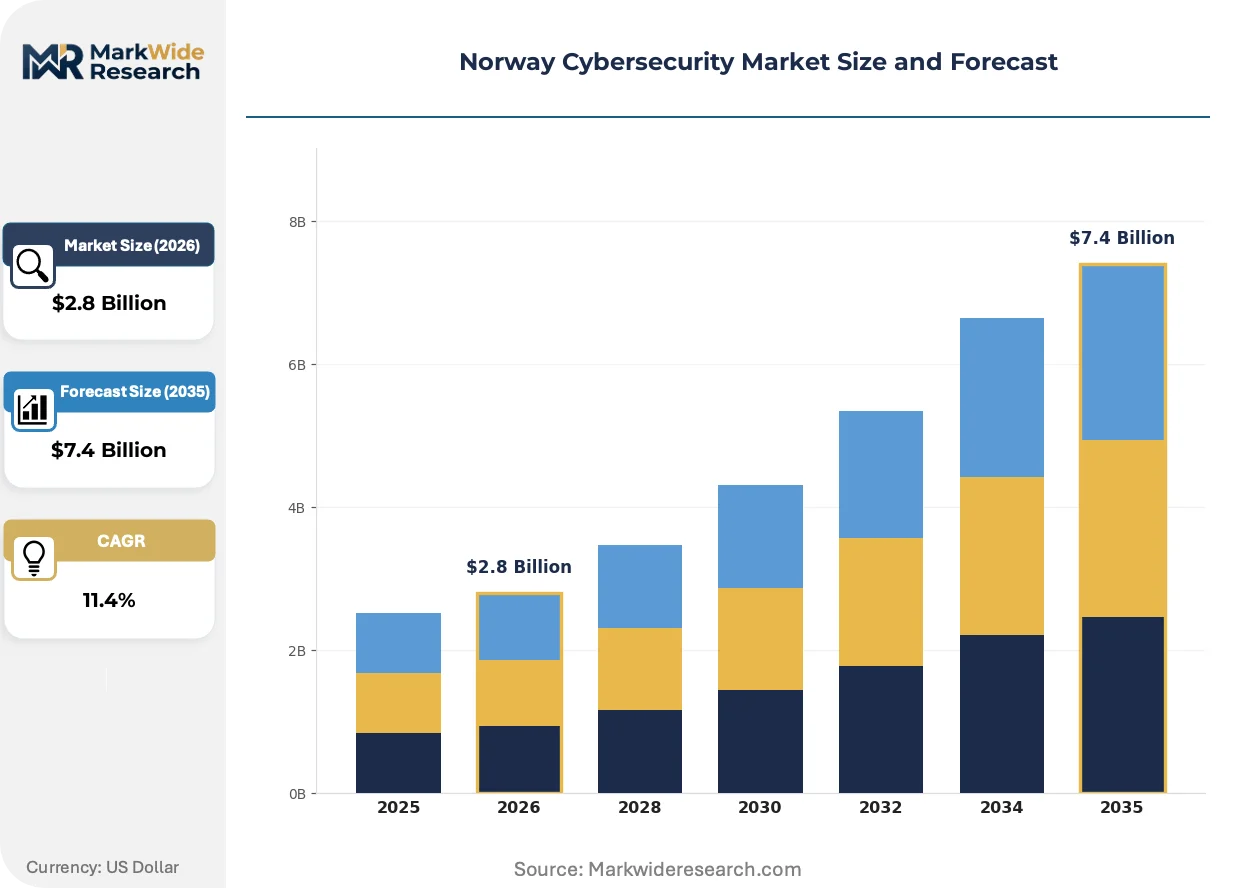
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $7.4 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Government, BFSI, Healthcare, Retail Service Type: Incident Response, Managed Security, Consulting, Risk Assessment Technology: Firewalls, Antivirus, Intrusion Detection, Encryption |
| Companies Covered | Check Point, IBM Corporation, Mnemonic AS, Dell Inc., Thales, Telenor Cyberdefence, Microsoft, Telia Company AB, Cisco Systems, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Norway Cybersecurity Market Evolving Landscape
Cloud-native security orchestration is compressing traditional managed services margins while enabling new bundling models. Norwegian buyers are prioritizing vendors with domestic data residency and sovereign routing capabilities.
Behavioral anomaly detection platforms are displacing signature-based intrusion prevention in energy sector deployments. Equinor-affiliated suppliers are adopting these systems at accelerated pace to satisfy NIS2 supply-chain security obligations. The shift is compressing incumbent endpoint protection market share and elevating vendors with native OT visibility.
Norway's digitalization ministry NIS2 transposition mandates 24-hour incident reporting for critical infrastructure operators. Oil and gas sector procurement committees are rewriting RFP evaluation criteria to prioritize vendors with pre-established NSM liaison relationships. Electric grid operators are responding by consolidating vendor panels to reduce compliance coordination overhead.
Energy sector buyers are unbundling after-sales support from initial security architecture contracts. Statoil-linked suppliers now procure threat hunting and regulatory attestation as separate line items rather than integrated multi-year agreements. This pattern is most visible in Oslo financial district procurement, where CFO oversight of security spending has intensified.
Norway Cybersecurity Market Segmentation
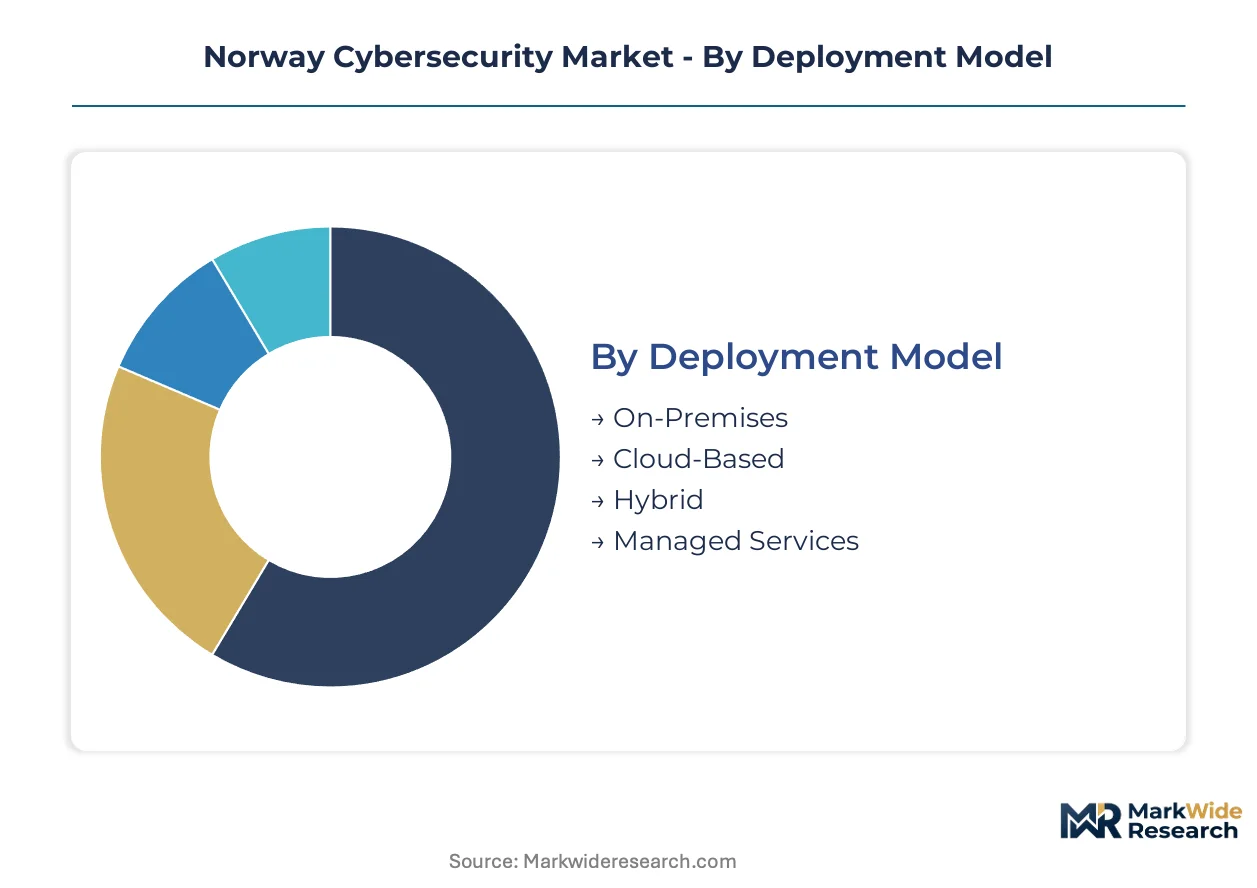
Segmentation in the Norwegian cybersecurity market reveals how NIS2 compliance deadlines and energy sector procurement patterns concentrate revenue across distinct technology and service configurations. Vendors must align offerings with submarine cable protection mandates, hybrid cloud migrations, and sovereign data routing requirements to capture margin pools.
Deployment Model:
Margin pools concentrate where multi-year contracts bundle infrastructure control with regulatory attestation, particularly in energy and defense-adjacent installations.
- On-Premises:Air-gapped architectures enforce AES-256 encryption and behavioral anomaly detection within physically segmented environments. Submarine cable landing stations in Stavanger and Oslo require these deployments to satisfy NSM baseline standards for undersea fiber protection.
- Cloud-Based:Native security orchestration platforms deliver elastic compute for threat hunting and automated response. Equinor-linked suppliers in the Western Norway Energy Corridor are migrating OT monitoring to these environments, compressing traditional managed services margins while expanding addressable contract value.
- Hybrid:Split architectures maintain sensitive workloads on-premises while routing analytics to cloud-native dashboards. Norwegian electric grid operators favor this model for SCADA segmentation that preserves operational continuity.
- Managed Services:Outsourced SOC operations bundle 24-hour incident reporting with continuous monitoring. Talent scarcity in Oslo and Stavanger inflates pricing for these contracts.
On-Premises holds installed capacity. Cloud-Based is rotating up the share rankings.
End User:
Application concentration follows critical infrastructure designation and NIS2 transposition timelines, with energy-adjacent sectors commanding premium pricing.
- Government:Classified facilities mandate zero-trust network architectures with sovereign data routing through domestic fiber infrastructure. NSM enforces ICT baseline standards that exclude non-compliant vendors from procurement shortlists.
- BFSI:Oslo financial district institutions prioritize domestic data residency and behavioral anomaly detection for transaction monitoring. CFO oversight has intensified, unbundling threat hunting from initial architecture contracts.
- Healthcare:Norwegian Personal Data Act provisions govern patient record protection with mandatory breach notification timelines. Regional health trusts are consolidating vendor panels to reduce compliance coordination overhead.
- Retail:Point-of-sale encryption and intrusion detection systems protect payment card data. E-commerce platforms in urban centers are adopting cloud-native security orchestration at accelerated pace.
Government anchors procurement volume. BFSI is climbing the fastest as unbundled service contracts expand.
Service Type:
Cost tier differentiation separates commodity alerting from premium advisory engagements where regulatory relationships command pricing power.
- Incident Response:Retained breach containment teams with pre-established NSM liaison relationships capture premium positioning. Norwegian energy sector procurement committees now require demonstrated regulatory coordination capabilities in RFP evaluations.
- Managed Security:Multi-year MDR contracts bundle threat hunting with continuous monitoring. Mnemonic AS and Telenor Cyberdefence have locked regional analyst talent, constraining competitor expansion.
- Consulting:Transformation engagements align security architecture with NIS2 supply-chain obligations. Statoil-affiliated suppliers are the primary demand concentration.
- Risk Assessment:Compliance attestation services verify adherence to NSM-enforced ICT baseline standards. Electric grid operators require these assessments for SCADA upgrade authorization.
Managed Security holds contract volume. Incident Response is gaining share fastest as procurement criteria tighten.
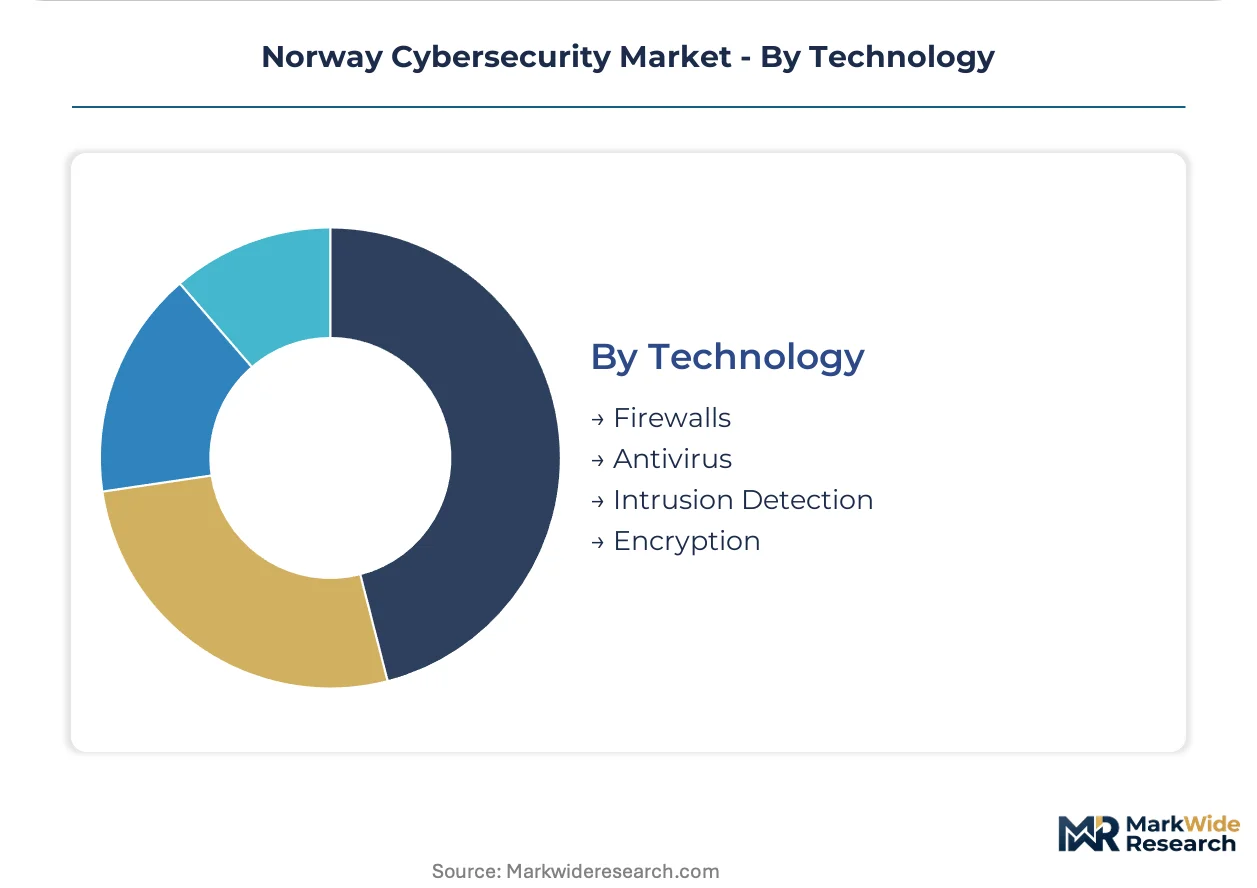
Technology:
Maturity curves separate legacy signature-based systems from behavioral platforms displacing incumbents in energy sector deployments.
- Firewalls:Next-generation platforms integrate with zero-trust architectures for granular access control. Defense-adjacent facilities require hardware-certified deployments with air-gapped management planes.
- Antivirus:Endpoint protection is ceding share to behavioral anomaly detection in Equinor-linked supplier environments. Legacy signature updates cannot match OT-native threat visibility requirements.
- Intrusion Detection:Network-based sensors monitor east-west traffic within segmented industrial control systems. Retrofitting decades-old SCADA infrastructure without operational disruption remains the primary implementation constraint.
- Encryption:AES-256 protocols protect data at rest and in transit across hybrid environments. Submarine cable operators mandate these standards for landing station interconnection points.
Firewalls maintain installed base dominance. Encryption is rotating up the share rankings as hybrid cloud migration accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
NSM enforces ICT baseline standards that concentrate procurement authority within Oslo and Stavanger corridors. Norwegian energy operators anchor regional demand through NIS2-mandated security upgrades across oil, gas, and electric grid infrastructure.
Oslo
Financial district institutions drive cloud-native security orchestration adoption for transaction monitoring. Norwegian Personal Data Act provisions mandate domestic data residency for BFSI workloads. CFO oversight has intensified procurement unbundling, separating threat hunting from initial architecture contracts.
Stavanger
Offshore suppliers in the Western Norway Energy Corridor require managed detection and response services bundled with regulatory attestation. Submarine cable landing stations mandate air-gapped segmentation for undersea fiber protection. NSM baseline standards enforce AES-256 encryption at interconnection points.
Bergen
Maritime shipping operators and seafood exporters adopt hybrid cloud architectures for supply-chain security. NIS2 transposition through the digitalization ministry compresses procurement cycles for mid-sized logistics providers. Regional health trusts consolidate vendor panels to reduce compliance coordination overhead.
Trondheim
Technology research clusters and university-affiliated startups drive zero-trust network architecture pilots. Defense-adjacent facilities require sovereign data routing through Telenor's domestic fiber infrastructure. Classified installations sustain captive demand for specialized on-premises security deployment.
Tromsø
Arctic data center operators and satellite ground stations prioritize encryption protocols for cross-border data flows. Remote critical infrastructure sites face extended implementation timelines due to Nordic security architect scarcity. NSM liaison relationships determine vendor selection for incident response retainers.
Norway Cybersecurity Market Competitive Landscape
A small set of integrated leaders sits above a broader specialist tier in the Norwegian cybersecurity market. Mnemonic AS and Telenor Cyberdefence anchor the domestic layer through SOC workforce concentration and fiber infrastructure control. International technology conglomerates compete via consulting-led transformation engagements. Two competitive moves dominate: talent lock-in through multi-year analyst contracts and pre-established regulatory liaison relationships that satisfy NIS2 procurement criteria.
Among Oslo-based defenders, Mnemonic AS exemplifies the domestic SOC operator archetype leveraging regional analyst pools for incident response positioning. Telenor Cyberdefence occupies the infrastructure-integrated tier through sovereign data routing capabilities. IBM Corporation represents the consulting-led transformation model targeting energy sector supply chains. These three anchors illustrate how vendor selection criteria now prioritize NSM coordination capabilities over standalone technology features.
| Leading Market Players |
|---|
| Check Point |
| IBM Corporation |
| Mnemonic AS |
| Dell Inc. |
| Thales |
| Telenor Cyberdefence |
| Microsoft |
| Telia Company AB |
| Cisco Systems |
| Others |
Value Network & Pricing Analysis
Ninety-day implementation timelines for behavioral anomaly detection platforms concentrate pricing power with Oslo-based SOC operators possessing pre-established NSM liaison relationships. This lead-time compression feeds directly into contract structures that bundle regulatory attestation with continuous monitoring, elevating vendors with domestic analyst pools while marginalizing technology-only providers.
Pricing Analysis
Oslo financial district procurement committees pay 15-25% premiums for managed security contracts with sovereign data routing guarantees compared to cloud-native alternatives without Telenor fiber infrastructure integration. Three-tier pricing structure across premium, standard, and economy levels separates incident response retainers with NSM coordination capabilities from commodity alerting services and unbundled threat hunting engagements. Cost compression in standard-tier MDR contracts is intensifying as Mnemonic AS and Telenor Cyberdefence lock regional analyst talent through multi-year employment agreements. Energy sector buyers in Stavanger exhibit lowest price sensitivity due to NIS2 compliance deadline pressure, while mid-sized logistics providers in Bergen face acute budget constraints.
Supply Chain Analysis
Submarine cable landing station certification bottlenecks in Stavanger and Oslo constrain hardware vendor market entry for air-gapped segmentation deployments. Supply concentration rests on Taiwan for specialized encryption chipsets, Germany for industrial firewall hardware, and the United States for cloud-native security orchestration platforms. Raw material dependencies span gallium arsenide semiconductors, rare earth magnets for hardware security modules, and specialized optical components for fiber-tap detection systems. Single-source vulnerability pervades AES-256 encryption processor supply where domestic stockpiling remains minimal. Distribution runs through Telenor's sovereign fiber infrastructure for government and defense-adjacent installations, while commercial buyers access cloud-native platforms via direct vendor relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Cloud-native security orchestration platforms threaten incumbent managed services margins through automated threat hunting that displaces analyst-intensive workflows. Incumbents must navigate this substitution by anchoring differentiation in regulatory coordination capabilities that automation cannot replicate.
For Market Incumbents: Shield multi-year contract value by embedding NSM liaison services into incident response retainers before procurement committees complete vendor panel consolidations. Deepen analyst talent pools through Oslo-based SOC workforce expansion to extend implementation timeline premiums. Prioritize certification investment in EU Cyber Resilience Act pre-compliance to capture hardware vendor exit opportunities.
For New Entrants and Emerging Players: Western Norway Energy Corridor MDR services present the most penetrable white-space where Equinor-linked suppliers remain underserved for OT-native behavioral anomaly detection. Target hybrid cloud migration projects in Bergen maritime logistics where NIS2 procurement cycle compression creates vendor selection windows. Lead with zero-trust architecture pilots at Trondheim technology research clusters to establish referenceable deployments before scaling to classified facilities.
For Investors and Strategic Acquirers: Capital-intensity ratios are inflecting upward across cloud-native security orchestration platform development as elastic compute infrastructure demands scale. Long-term viability over the next decade hinges on regulatory relationship moats rather than pure technology differentiation. Acquisition target archetypes include domestic SOC operators with locked analyst talent and pre-established NSM coordination capabilities. Watch for EU Cyber Resilience Act enforcement timeline acceleration as the critical inflection signal.
| Strategic Initiative | Industry Significance |
|---|---|
| NSM Liaison Capability Investment | Pre-established regulatory relationships satisfy NIS2 procurement criteria rewriting RFP evaluations across energy sector buyers. |
| Analyst Talent Lock-In Programs | Multi-year employment agreements in Oslo and Stavanger constrain competitor service expansion and sustain pricing premiums. |
| Hybrid Cloud Migration Partnerships | Equinor-linked supplier OT monitoring shifts create demand for split architectures preserving operational continuity. |
| Zero-Trust Architecture Pilots | Behavioral anomaly detection integration with AES-256 encryption protocols differentiates domestic SOC operators. |
| EU Cyber Resilience Act Pre-Compliance | Early certification positioning captures hardware vendor exit opportunities from Norwegian critical infrastructure procurement. |
Research Methodology
The analysis maps managed security services, cloud-native platforms, on-premises deployments, and hybrid architectures, each validated through chief information security officers, energy sector procurement committee members, NSM enforcement officials, and cloud infrastructure engineers. Primary interviews with these stakeholders combined with secondary validation against NSM ICT baseline standard publications, Norwegian digitalization ministry NIS2 transposition documents, Equinor supply-chain security RFP disclosures, and Telenor fiber infrastructure expansion filings. Bottom-up contract value aggregation and top-down market sizing triangulation anchored volume estimates.
Consistency checks against hyperscaler capex disclosures and European cybersecurity vendor revenue segmentations validated projection outputs across the modeling period. Segmentation dimensions modeled include deployment model, end-user vertical, service type tier, and technology maturity curve positioning. CAGRs derived from weighted average of historical contract renewal rates and NIS2-mandated procurement acceleration assumptions. Forecast inputs incorporated submarine cable protection mandate timelines and electric grid SCADA segmentation upgrade authorizations.
Underlying assumptions cover NIS2 enforcement deadline adherence, NSM baseline standard continuity, and EU Cyber Resilience Act transposition scope, with deviation risk concentrated in regulatory timeline delays and Nordic security architect scarcity intensification. Practitioners should keep alternative scenarios live as NIS2 procurement acceleration patterns and cloud-native platform substitution rates evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
United Kingdom Ransomware Protection Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Oman Cybersecurity Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Web Filtering Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Spain Cybersecurity Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Global Cyber Situational Awareness Market
Cybersecurity
Thailand Cybersecurity Market
Cybersecurity
Middle East Cybersecurity Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Egypt Cybersecurity Market
Cybersecurity
Global Content Disarm and Reconstruction Market