
 United Kingdom Ransomware Protection Market | 2026-2036
United Kingdom Ransomware Protection Market Size, Share, and Industry Trends Forecast 2026-2036
United Kingdom Ransomware Protection Market Insights
The UK ransomware protection market is rebalancing between premium managed detection services and commodity antivirus subscriptions. Sophos Group plc leverages its native British presence to anchor enterprise contracts across government and education sectors. Darktrace differentiates through autonomous AI-driven threat response that sustains pricing power in financial services. BAE Systems Inc. dominates public-sector procurement through security-cleared engineering capabilities.
Ransomware protection encompasses layered cybersecurity architectures combining endpoint detection, network segmentation, cryptographic backup verification, and behavioral anomaly analysis to prevent unauthorized data encryption and extortion. The primary commercial purpose centers on maintaining operational continuity and regulatory compliance against criminal encryption attacks. Cloud Security deployment models are capturing disproportionate growth as UK organizations migrate workloads to Azure and AWS regions. Endpoint Security remains the largest revenue pool though margin compression intensifies from Microsoft Defender bundling. Email Security shows resilient demand given phishing emails persist as the dominant attack vector against British enterprises.
The National Cyber Security Centre publishes mandatory minimum standards through Cyber Essentials Plus certification that shapes procurement requirements across government supply chains. The UK Information Commissioner's Office enforces GDPR-linked penalties for inadequate breach preparation, driving board-level investment in backup and recovery capabilities. Financial Conduct Authority operational resilience rules now mandate recovery time objectives for critical finance infrastructure. Stakeholders must monitor how the UK Online Safety Bill and prospective AI regulation reshape vendor liability frameworks for automated threat detection systems.
Market Dynamics
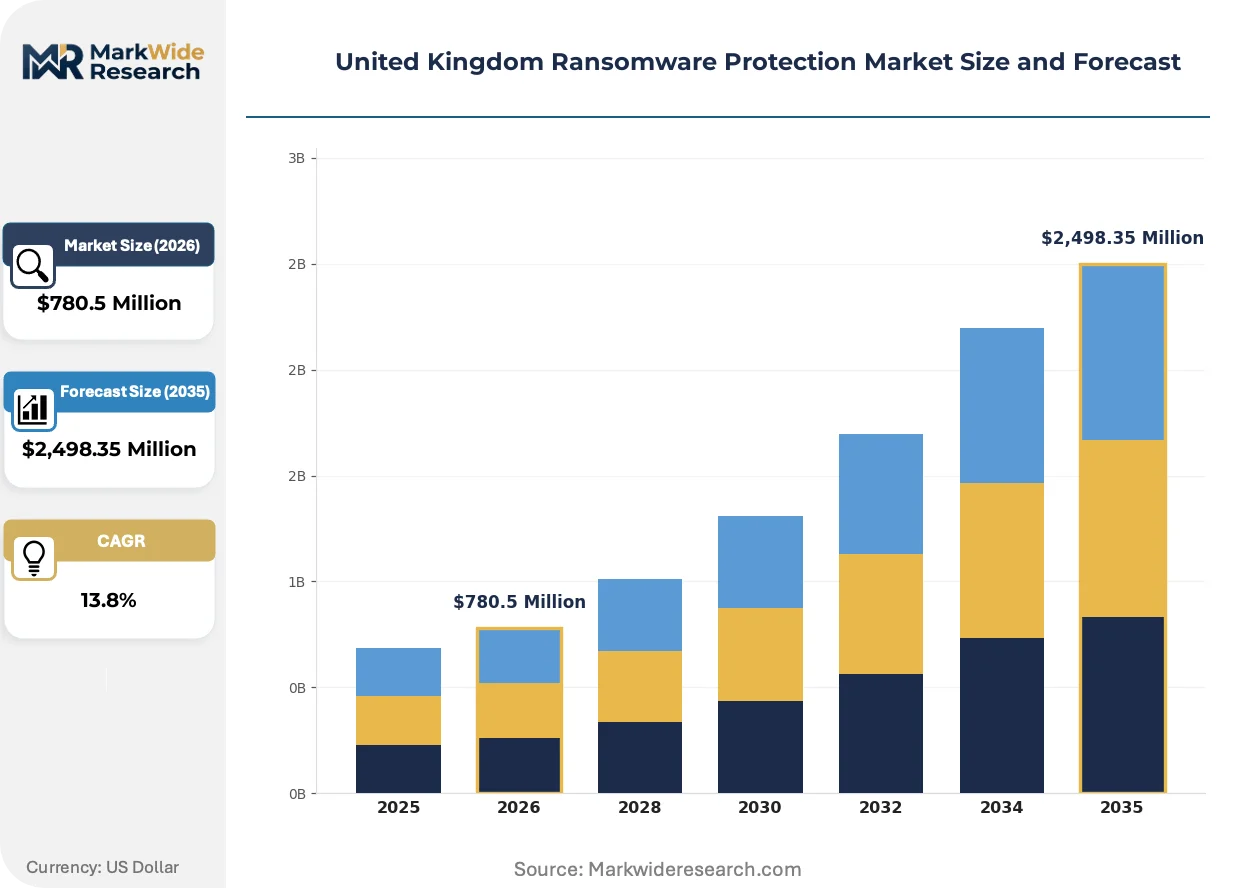
The UK ransomware protection market is rebalancing around Microsoft Defender bundling, which compresses endpoint security margins while forcing independent vendors toward differentiated managed detection services and AI-autonomous response capabilities.
Growth Catalysts
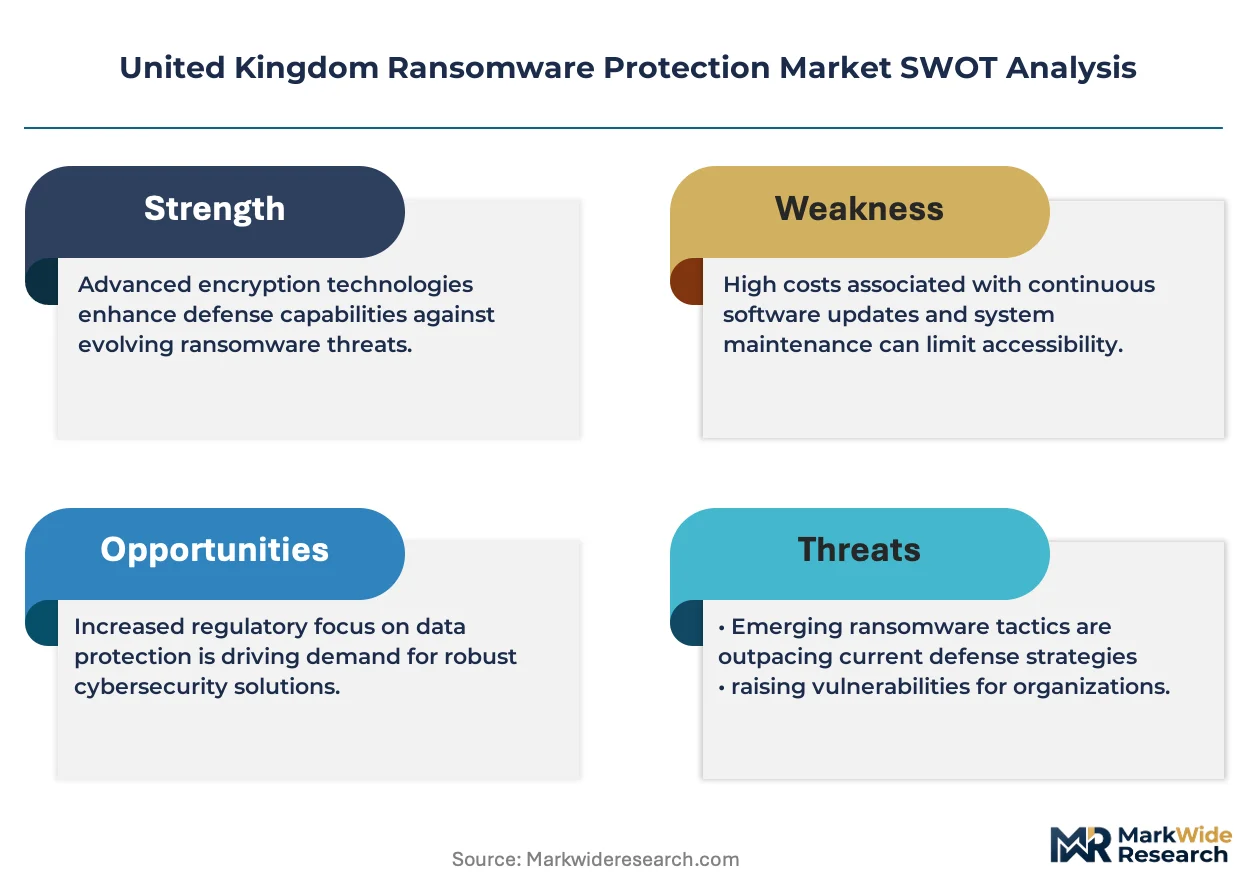
- Financial Conduct Authority operational resilience rules:Mandated recovery time objectives for critical finance infrastructure are accelerating procurement of backup verification and incident response platforms across London's banking sector.
- Endpoint detection and response (EDR) platform consolidation:Mid-market enterprises are replacing fragmented point solutions with integrated EDR-XDR suites, expanding addressable wallet share for unified vendors.
- Thames Valley technology corridor concentration:Cloud-native startups and scale-ups in Reading-Oxford-Cambridge arc are driving disproportionate demand for cloud workload protection and Kubernetes security.
Market Restraints
- Skilled cybersecurity analyst shortage:The UK's finite pool of security-cleared engineers limits vendor scaling and inflates service delivery costs for managed security providers.
- Microsoft Defender ecosystem bundling:Native integration with Microsoft 365 E5 licenses is structurally displacing standalone endpoint antivirus subscriptions in enterprise accounts.
- GDP-linked budget volatility:Public sector cyber spending remains tethered to HM Treasury fiscal cycles, creating procurement delays and payment uncertainty for government contractors.
Strategic Opportunities
- AI Act compliance preparation:The EU AI Act's risk-based classification for automated threat detection systems creates advisory and certification service revenue streams for UK cybersecurity consultancies.
- Operational technology (OT) security convergence:Manufacturing and energy infrastructure operators are extending ransomware protection from IT networks to industrial control systems, opening specialized deployment expertise.
- Channel partner program restructuring:Value-added resellers are building managed detection and response practices, creating indirect routes to mid-market accounts previously served by direct sales.
Industry Challenges
- Cyber Essentials Plus certification backlog:Limited UK-accredited assessment body capacity is extending compliance timelines for government supply chain vendors.
- Legacy SIEM integration complexity:Enterprises with entrenched Splunk or IBM QRadar deployments face architectural friction when adopting cloud-native extended detection and response platforms.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | United Kingdom Ransomware Protection Market |
| Market Size in 2026 | $780.5 Million |
| Market Size in 2035 | $2,498.35 Million |
| CAGR (2026 – 2036) | 13.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Endpoint Security, Network Security, Cloud Security, Email Security, Data Encryption, Backup & Recovery Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User Industry: Financial Services, Government Agencies, Telecommunications, Education, Manufacturing, Hospitality Attack Vector: Phishing Emails, Malicious Websites, Remote Desktop Protocol, Software Vulnerabilities, USB Drives |
| Companies Covered | Sophos Group plc, Darktrace, BAE Systems Inc., Trend Micro Incorporated, Redscan, Mimecast, SentryBay, Becrypt, Cisco Systems Inc., Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
United Kingdom Ransomware Protection Market Trends and Innovations
Generative AI is reshaping attack surface simulation and defensive automation, compressing the detection-to-response window while forcing vendors to retrain models against adversarial AI-generated phishing and polymorphic malware.
Extended detection and response platforms are automating cross-domain threat correlation across endpoint, network, and identity telemetry. Mid-market enterprises in the UK are adopting these suites at accelerated pace to offset analyst staffing gaps. This automation is compressing the competitive window for standalone endpoint detection vendors that lack native network and cloud visibility.
The UK Online Safety Bill's pending provisions on automated content scanning are creating compliance uncertainty for email security vendors operating machine-learning detection pipelines. British enterprises are delaying procurement decisions pending Ofcom guidance on liability frameworks. Financial services institutions are responding by demanding contractual indemnification clauses from vendors deploying AI-driven threat detection.
Consolidated security service edge procurement is displacing discrete point-product purchasing across distributed enterprises. British retailers and professional services firms are bundling zero-trust network access with cloud-delivered security in single-vendor arrangements. This pattern is most visible in Manchester and Birmingham regional hubs where IT teams lack specialized security engineering depth.
United Kingdom Ransomware Protection Market Segmentation
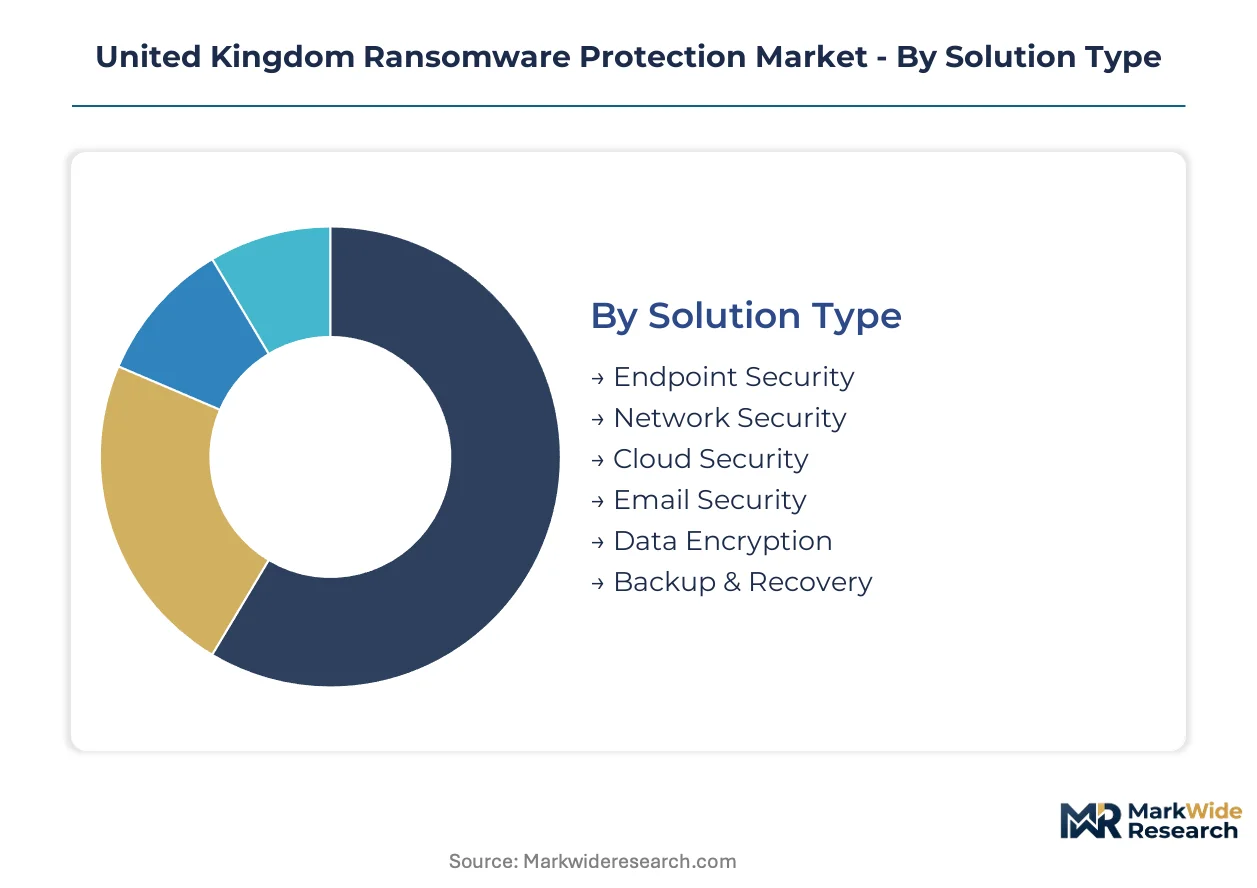
UK ransomware protection procurement diverges sharply by organizational maturity and threat exposure profile. Sophisticated financial institutions demand autonomous response capabilities while public sector bodies prioritize Cyber Essentials Plus compliance and managed service wrappers.
Solution Type:
Technical sophistication separates enterprise buyers pursuing layered defense from mid-market organizations consolidating around bundled platforms.
- Endpoint Security:EDR-XDR platforms combining behavioral analysis with automated remediation anchor enterprise architectures. London financial institutions drive premium procurement here, though Microsoft Defender bundling compresses margins for standalone vendors serving SME accounts.
- Cloud Security:Workload protection platforms for Azure and AWS deployments are capturing disproportionate growth as Thames Valley technology firms accelerate cloud migration. Native API integration with hyperscaler environments distinguishes competitive offerings.
- Network Security:Microsegmentation and zero-trust network access defend lateral movement paths.
- Email Security:Machine-learning phishing detection remains essential given email's persistence as the dominant UK attack vector.
- Data Encryption:Cryptographic key management supports GDPR-aligned data protection mandates.
- Backup & Recovery:Immutable backup verification underpins Financial Conduct Authority operational resilience compliance.
Endpoint Security leads volumes today; Cloud Security is gaining share fastest.
Deployment Model:
Staffing constraints and capital availability determine whether buyers self-operate or outsource security operations.
- Managed Services:SOC-as-a-service and MDR providers absorb analyst shortage pressures for UK organizations lacking security-cleared personnel. Government agencies and mid-market manufacturers favor this model to satisfy NCSC guidance without internal capability buildout.
- Cloud-Based:SaaS-delivered protection scales elastically for cloud-native enterprises in Reading-Oxford-Cambridge corridor, with consumption pricing aligning cost to growth trajectories.
- Hybrid:Split architectures accommodate regulated data residency requirements alongside cloud agility.
- On-Premises:Air-gapped deployments persist in defense and critical national infrastructure.
Managed Services commands the largest wallet share; Cloud-Based deployment shows the steepest expansion trajectory.
End User Industry:
Regulatory intensity and asset criticality create tiered demand profiles across UK verticals.
- Financial Services:Banks, insurers, and asset managers face layered compliance obligations from FCA operational resilience rules, GDPR, and PCI-DSS. Recovery time objectives mandate investment in backup verification, incident response retainers, and red team testing.
- Government Agencies:Central government, NHS trusts, and local authorities procure through Crown Commercial Service frameworks with Cyber Essentials Plus as mandatory baseline. Security-cleared engineering capabilities constrain vendor eligibility.
- Education:Universities and academy trusts balance open research networks against ransomware exposure.
- Telecommunications:Critical national infrastructure status drives enhanced resilience investment.
- Manufacturing:OT-IT convergence extends protection requirements to industrial control systems.
- Hospitality:Payment card data and operational continuity drive mid-market procurement.
Financial Services anchors revenue concentration; Manufacturing is expanding most quickly as OT security convergence accelerates.
Attack Vector:
Threat intelligence on UK incident patterns shapes defensive investment prioritization.
- Phishing Emails:Business email compromise and credential harvesting campaigns dominate UK ransomware entry statistics. Advanced persistent threat groups targeting British organizations favor spear-phishing over technical exploitation.
- Remote Desktop Protocol:Exposed RDP endpoints remain a high-volume attack path for opportunistic ransomware operators against under-resourced SMEs.
- Malicious Websites:Drive-by downloads and exploit kits distribute initial access payloads.
- Software Vulnerabilities:Unpatched edge devices and VPN concentrators enable zero-day exploitation.
- USB Drives:Removable media controls address insider threat and supply chain contamination vectors.
Phishing-focused defenses absorb the largest procurement budget; RDP protection is climbing the fastest as hybrid work persists.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Security-cleared engineering talent clusters anchor UK ransomware protection demand, with London's financial district and Thames Valley technology corridor commanding disproportionate procurement volumes against regional markets.
London and the Southeast
Financial services institutions dominate endpoint detection procurement, driven by FCA operational resilience mandates and recovery time objective requirements. The UK National Cyber Strategy directs Crown Commercial Service frameworks that shape government supply chain purchasing. Canary Wharf and the City of London host concentrated banking headquarters where autonomous AI-driven threat response commands premium pricing.
Thames Valley Technology Corridor
Cloud-native startups across Reading-Oxford-Cambridge arc accelerate workload protection adoption for Azure and AWS deployments. NCSC guidance on Cyber Essentials Plus certification shapes vendor selection criteria for scaling enterprises. Reading's enterprise software cluster drives disproportionate demand for Kubernetes security and API-integrated cloud platforms.
Midlands Manufacturing Belt
Operational technology security convergence extends ransomware protection from IT networks to industrial control systems across automotive and aerospace supply chains. The region's manufacturing base faces GDPR-linked enforcement from the Information Commissioner's Office for inadequate breach preparation. Birmingham's logistics and distribution hubs anchor mid-market procurement of managed detection services.
Scotland
Public sector bodies including NHS Scotland trusts and central government agencies prioritize Cyber Essentials Plus compliance through managed service wrappers. Security-cleared engineering capabilities constrain vendor eligibility for defense-adjacent contracts. Edinburgh's financial services sector and Aberdeen's energy infrastructure drive specialized resilience investment.
North England
Regional banking headquarters and professional services firms in Manchester and Leeds adopt consolidated security service edge procurement, bundling zero-trust network access with cloud-delivered protection. Limited internal security engineering depth favors single-vendor arrangements over fragmented point solutions. Manchester's emerging fintech cluster generates mid-market demand for email security and phishing defenses.
United Kingdom Ransomware Protection Market Competitive Landscape
Capital-heavy producers compete with asset-light designers across the UK ransomware protection market, where native integration capabilities and security-cleared personnel separate tier-one vendors from commodity providers. The vendor base stratifies between premium managed detection services and bundled endpoint platforms, with pricing power concentrating among autonomous response specialists and public-sector incumbents. Three archetypes dominate: AI-autonomous threat detection platforms, security-cleared systems integrators, and cloud-native workload protection specialists. Competitive moves center on channel partner program restructuring for mid-market access and operational technology security certification for industrial verticals.
Within the autonomous response tier, Darktrace exemplifies AI-driven positioning that sustains enterprise pricing in financial services. Sophos Group plc anchors the native British presence archetype across government and education procurement channels. BAE Systems Inc. occupies the security-cleared systems integrator position for defense and critical national infrastructure accounts. These three represent distinct competitive vectors rather than interchangeable substitutes, with each anchoring separate buyer segments based on compliance profile and threat sophistication requirements.
| Leading Market Players |
|---|
| Sophos Group plc |
| Darktrace |
| BAE Systems Inc. |
| Trend Micro Incorporated |
| Redscan |
| Mimecast |
| SentryBay |
| Becrypt |
| Cisco Systems Inc. |
| Others |
Pricing and Supply Chain Analysis
Managed detection premium tiers and commodity endpoint bundles diverge sharply across UK procurement channels, with NCSC Cyber Essentials Plus certification requirements anchoring public-sector pricing floors while Microsoft Defender bundling compresses margins in SME accounts and reshapes vendor sourcing toward AI-autonomous capabilities.
Pricing Analysis
Bundled Microsoft 365 E5 security suites and unbundled specialist platforms split UK ransomware protection procurement into distinct pricing strata. Subscription-based SaaS tiers dominate, with differentiation hinging on security-cleared engineering access and autonomous response certification. Pricing pressure intensifies in the mid-market as native Microsoft integration displaces standalone antivirus licenses. Financial services institutions show lowest price sensitivity, prioritizing recovery time objective guarantees over license cost.
Supply Chain Analysis
UK government procurement rules mandating domestic-content verification for critical national infrastructure contracts reshape vendor eligibility and sourcing patterns. Engineering talent concentrates in Britain, Israel, and the United States, with cloud compute infrastructure drawing from hyperscaler regions in Ireland, Germany, and the Netherlands. Single-source dependency on Microsoft Azure and AWS UK regions creates concentration risk. Distribution runs through Crown Commercial Service frameworks for public sector and value-added reseller networks for commercial accounts.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion potential concentrates in managed detection services where AI-autonomous capabilities command premium positioning, justified by analyst staffing cost inflation that shifts buyer preference toward outsourced security operations.
For Market Incumbents: Extend autonomous response capabilities into operational technology verticals to defend pricing power against Microsoft Defender ecosystem expansion. Invest in security-cleared engineering pipelines to maintain Crown Commercial Service eligibility. Channel control through managed detection reseller programs offers defensive leverage against cloud-native entrants. For New Entrants and Emerging Players: Capture mid-market manufacturing accounts in the Midlands where OT-IT convergence outpaces incumbent specialization. The Thames Valley technology corridor presents penetrable white space for Kubernetes-native workload protection. Partner with regional value-added resellers lacking managed detection practices to bypass direct sales cost barriers. For Investors and Strategic Acquirers: Consolidation pressure builds where security-cleared personnel scarcity constrains vendor scaling and inflates service delivery costs. Long-term viability favors platforms with native AI training pipelines and established NCSC certification pathways. Watch Financial Conduct Authority operational resilience enforcement intensity as inflection signal for backup verification platform valuations.| Strategic Initiative | Industry Significance |
|---|---|
| Autonomous Response Capability Investment | Darktrace-style AI automation sustains premium pricing in FCA-regulated financial institutions. |
| Operational Technology Security Certification | ICS-specific accreditation opens Midlands manufacturing and energy infrastructure procurement. |
| Channel Partner Program Restructuring | MDR practice enablement creates indirect routes to mid-market accounts lacking internal security teams. |
| Cyber Essentials Plus Assessment Body Acquisition | Vertical integration into compliance services captures government supply chain advisory revenue. |
| Cloud-Native Workload Protection Development | API-integrated Azure and AWS platforms align with Thames Valley cloud migration trajectories. |
Research Methodology
Bottom-up enterprise deployment modeling reconciled against top-down vendor revenue tracking forms the analytical core of this study. Primary interviews with CISOs, IT procurement officers, managed security service directors, and NCSC framework coordinators informed demand-side validation. Secondary sources include Crown Commercial Service procurement databases, FCA operational resilience consultation responses, and Information Commissioner's Office enforcement notices. Triangulation across these inputs grounds market sizing.
Input-output matrices map endpoint, cloud, and network security adoption rates against organization size and regulatory exposure tiers across the projection horizon. Segmentation dimensions include solution type, deployment model, end-user industry, and attack vector priority. CAGRs derive from regression analysis of historical procurement velocity and policy mandate implementation timelines. Analyst staffing shortage metrics and Cyber Essentials Plus certification throughput constrain supply-side capacity assumptions.
Regulatory enforcement intensity, hyperscaler pricing volatility, and AI-generated attack sophistication are the dominant revision risks to forecast assumptions. Model boundaries exclude consumer antivirus and non-UK headquartered vendor indirect sales. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
Europe IoT Security Market
Cybersecurity
Endpoint Protection Platforms (EPP) Market
Cybersecurity
Big Data Security Market
Cybersecurity
Global Dynamic Data Masking Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Cyber Warfare Market
Cybersecurity
Cybersecurity Mesh Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Morocco Cybersecurity Market
Cybersecurity
Application-Level Encryption Market
Cybersecurity
Banking Cyber Security Market
Cybersecurity
Data Protection Market