
 Australia Cybersecurity Market | 2026-2036
Australia Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
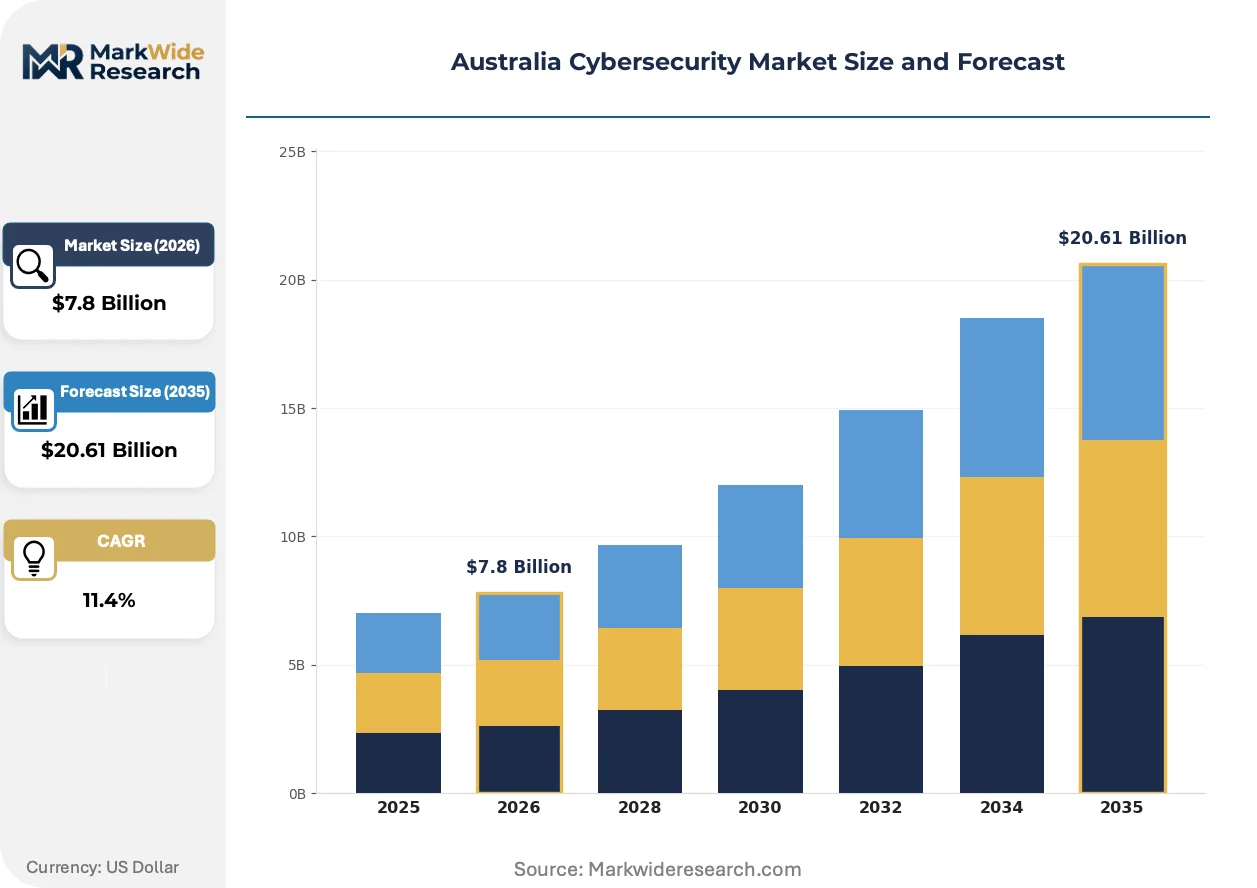
Australia Cybersecurity Market Outlook
Australia is reconfiguring its digital defense posture through sovereign capability investments and classified cloud infrastructure programs. QuintessenceLabs leverages quantum-enhanced encryption to anchor high-assurance government contracts. CyberCX sustains nationwide coverage through acquired specialist practices across state capitals. Bugcrowd competes on crowd-sourced vulnerability discovery, extending its model from Sydney into Canberra's defense ecosystem.
Australia cybersecurity encompasses technologies, services, and practices protecting networks, endpoints, applications, and cloud environments from unauthorized access, disruption, or data exfiltration, operating across on-premises, cloud-based, hybrid, and managed service architectures with encryption standards starting at AES-256 and extending to quantum-resistant algorithms. Its primary purpose is preserving confidentiality, integrity, and availability of information assets across government, financial, healthcare, and telecommunications systems. Cloud Security leads solution investment as federal agencies migrate to sovereign-hosted environments under protective policy mandates. Managed Security represents the fastest-expanding service type, driven by skills scarcity and board-level accountability for breach response. Government end users command premium pricing tiers due to classification requirements and domestic content rules.
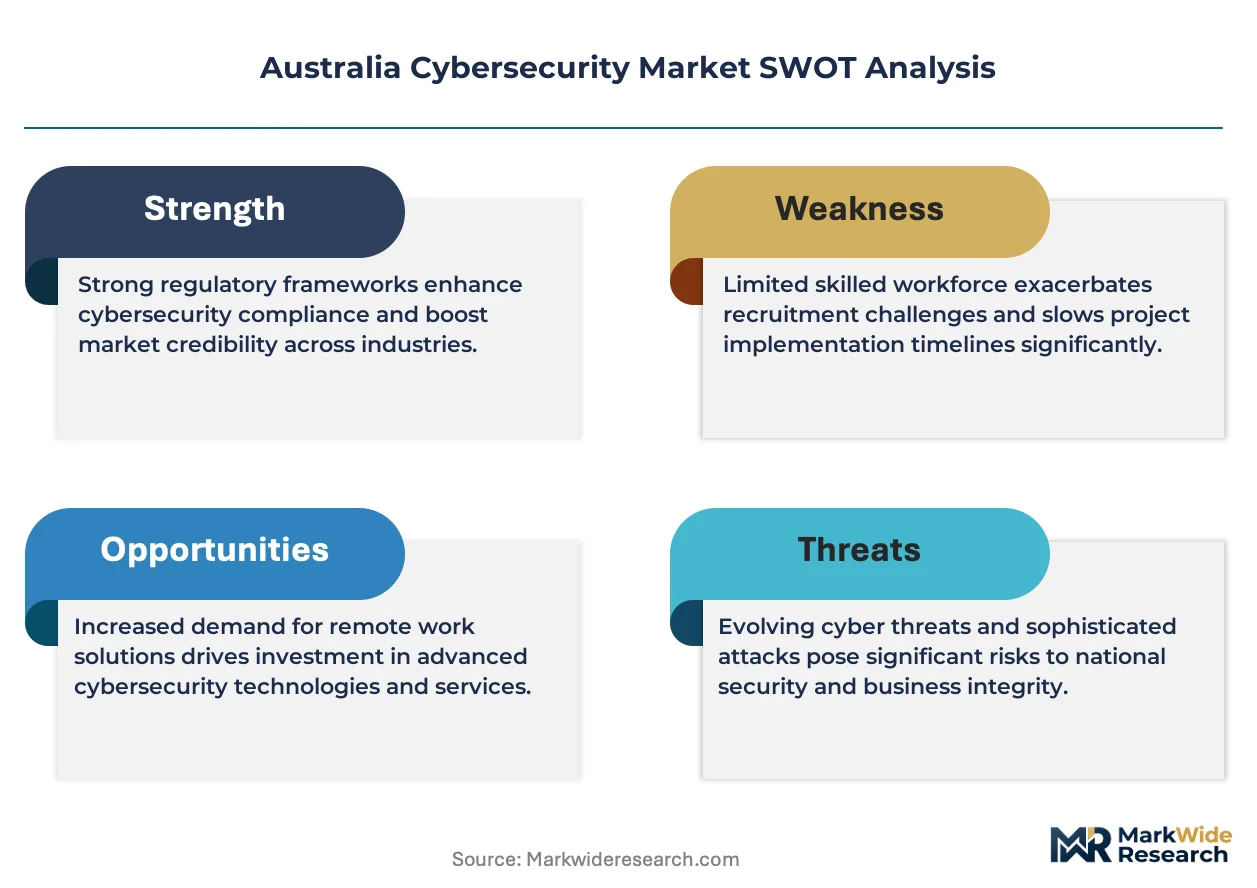
The Australian Signals Directorate issues Essential Eight maturity guidelines that shape procurement baselines for federal contractors, while the Office of the Australian Information Commissioner enforces Privacy Act penalties that elevate boardroom urgency. APRA's CPS 234 prudential standard mandates independent security assurance for banks and insurers, tightening vendor qualification thresholds. Stakeholders must monitor how the 2023-2030 Australian Cyber Security Strategy reshapes sovereign capability requirements and domestic vendor preference mechanisms.
Market Dynamics
Mandatory breach notification obligations under Australia's Privacy Act are compressing procurement cycles and elevating zero-trust architecture from aspirational to baseline requirement across financial and critical infrastructure sectors.
Growth Catalysts
- APRA CPS 234:The prudential standard mandates independent security assurance for banks and insurers, forcing institutional buyers to expand vendor panels and accelerate technology refresh cycles.
- Critical infrastructure operators:Operators of electricity, water, and transport systems face stepped-up obligations under the Security of Critical Infrastructure Act, generating sustained demand for managed detection and response services.
- Quantum-resistant encryption:Australian Signals Directorate guidance on post-quantum cryptography is pulling forward upgrade timelines for classified networks and defense contractors.
Market Restraints
- Specialized talent scarcity:Domestic supply of cleared security architects and incident responders falls short of federal and defense sector demand, inflating labor costs and extending implementation timelines.
- Sovereign cloud concentration:Certified strategic hosting providers number fewer than five nationally, creating single-point-of-failure risk for agencies requiring domestic data residency.
- Legacy system entrenchment:Core banking and government platforms running on decades-old architectures resist modular security integration without wholesale replacement.
Strategic Opportunities
- Canberra defense ecosystem:Australia's classified cloud infrastructure program and AUKUS technology-sharing arrangements are opening procurement channels for vendors with NATO-equivalent security clearances.
- Healthcare digitization:My Health Record expansion and telehealth permanence are creating first-time security procurement for regional hospital networks and primary care consortia.
- Managed security convergence:Bundling endpoint detection, identity governance, and cloud access security broker functions into unified service tiers addresses skills gaps among mid-market enterprises.
Industry Challenges
- Security clearance bottlenecks:Baseline and negative vetting backlogs at the Australian Government Security Vetting Agency delay project staffing for defense and intelligence contracts by six to eighteen months.
- Multi-cloud complexity:Federal agencies operating across sovereign, hybrid, and offshore cloud instances face inconsistent policy enforcement and fragmented visibility architectures.
- Essential Eight maturity gaps:Many contractors struggle to demonstrate implementation of all eight mitigation strategies at target maturity, risking disqualification from federal procurement panels.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Australia Cybersecurity Market |
| Market Size in 2026 | $7.8 Billion |
| Market Size in 2035 | $20.61 Billion |
| CAGR (2026 – 2036) | 11.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Network Security, Endpoint Security, Application Security, Cloud Security End User: Government, BFSI, Healthcare, Telecom Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Service Type: Consulting, Implementation, Support, Managed Security |
| Companies Covered | Qualysec, QuintessenceLabs, CyberPulse, Nuix, Bugcrowd, CyberCX, Airlock Digital, Macquarie Technology Group, Tesserent, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Australia Cybersecurity Market Strategic Shifts
Security architecture in Australia is pivoting from perimeter defense to identity-centric models, with policy mandates and supply-side innovation converging to reshape vendor competitive position.
Extended detection and response platforms are consolidating endpoint, network, and cloud telemetry into unified analyst workflows. Large financial institutions and federal agencies are adopting these stacks to reduce mean-time-to-containment. The technology is migrating from siloed point products toward integrated native-SOAR architectures that compress vendor consolidation timelines.
The Australian Cyber Security Strategy 2023-2030 introduces sovereign capability incentives and domestic content preferences for classified procurement. This industrial policy redirects federal spending toward Australian-owned or Australian-based security providers. Defense and intelligence end-use segments are restructuring supplier qualification criteria to favor vendors with domestic development and cleared support workforces.
Mid-market enterprises are abandoning capital-intensive on-premises security operations centers in favor of subscription-based co-managed detection services. Regional banks and healthcare networks outside Sydney and Melbourne are driving this transition, purchasing 24/7 coverage without building internal tier-1 analyst benches. Queensland and Western Australia present the strongest regional expansion corridors for providers establishing distributed security operations capabilities.
Australia Cybersecurity Market Segmentation
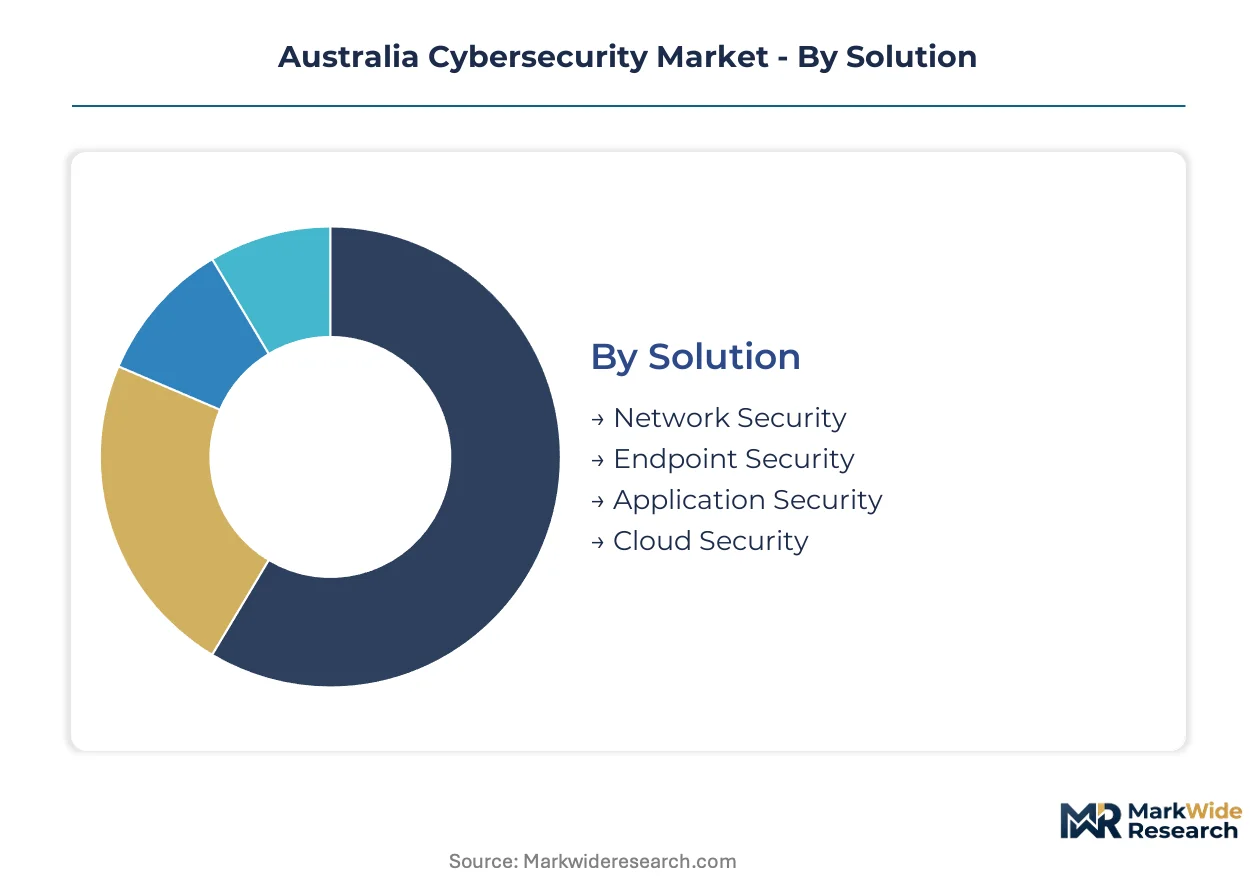
Australian procurement patterns diverge sharply across solution types and delivery models. Government buyers impose sovereign hosting mandates that reshape deployment preferences, while skills scarcity drives service-type selection in commercial sectors.
Solution:
Refresh cycles vary from eighteen months for cloud-native platforms to seven years for hardened network appliances, compressing vendor revenue recognition timelines for software while extending hardware service contracts.
- Cloud Security:Encompasses cloud access security brokers, workload protection platforms, and sovereign-hosted encryption gateways. Federal agencies migrating to ASD-certified strategic clouds under protective policy mandates anchor demand, with defense contractors following under AUKUS information-sharing protocols.
- Network Security:Includes next-generation firewalls, intrusion detection systems, and zero-trust network access controllers. Critical infrastructure operators in electricity and water face stepped-up Security of Critical Infrastructure Act obligations, forcing segmentation upgrades and OT/IT boundary hardening.
- Endpoint Security:Covers endpoint detection and response, mobile threat defense, and privileged access management agents. Regional healthcare networks digitizing under My Health Record expansion purchase first-time endpoint protection without internal security operations benches.
- Application Security:Comprises static and dynamic testing tools, software composition analysis, and runtime application self-protection. Financial institutions subject to APRA CPS 234 independent assurance mandates drive procurement for DevSecOps pipeline integration.
Network Security dominates installed base across federal and critical infrastructure estates. Cloud Security is where expansion concentrates as sovereign hosting programs mature.
End User:
Pricing power inverts across this dimension, with government commanding premium tiers for cleared personnel and domestic development requirements while healthcare operates under constrained capital budgets.
- Government:Federal agencies, state departments, and intelligence community members operating under ASD Essential Eight maturity guidelines. Classification requirements and negative vetting backlogs at the Australian Government Security Vetting Agency compress eligible vendor pools and inflate contract values.
- BFSI:Banks, insurers, and superannuation funds regulated under APRA CPS 234 prudential standards. Mandatory breach notification under the Privacy Act elevates boardroom urgency, accelerating zero-trust architecture from aspirational to baseline procurement criterion.
- Healthcare:Public hospitals, private clinic networks, and primary care consortia managing My Health Record integration. Telehealth permanence and regional digitization create first-time security procurement for organizations without legacy security operations centers.
- Telecom:Mobile network operators, fixed-line carriers, and datacenter providers designated as critical infrastructure. Security of Critical Infrastructure Act obligations mandate supply chain risk management and customer data protection enhancements.
Government commands premium pricing tiers due to classification overhead and domestic content rules. Healthcare is climbing fastest as regional networks undertake initial security modernization.
Deployment:
Capital intensity separates this category, with managed services converting fixed security operations center costs to variable subscription outlays that appeal to skills-constrained mid-market buyers.
- Managed Services:Co-managed detection and response, fully outsourced security operations centers, and subscription-based threat intelligence feeds. Skills scarcity and board-level accountability for breach response drive mid-market enterprises outside Sydney and Melbourne toward 24/7 coverage without internal tier-1 analyst benches.
- Cloud-Based:Native SaaS security controls, identity-as-a-service platforms, and sovereign-hosted encryption services. Federal agencies migrating to ASD-certified strategic clouds under the classified cloud infrastructure program pull demand toward domestic data residency guarantees.
- Hybrid:Split architectures spanning on-premises appliances and cloud-native controls with unified policy enforcement. Multi-cloud complexity across sovereign, hybrid, and offshore instances fragments visibility architectures and drives integration service demand.
- On-Premises:Hardware appliances, private cloud security stacks, and air-gapped classified networks. Defense contractors and intelligence community members maintain on-premises requirements for certain classification levels despite broader cloud migration trends.
On-Premises retains share in classified and legacy system environments. Managed Services is expanding most quickly as regional buyers abandon capital-intensive security operations center builds.
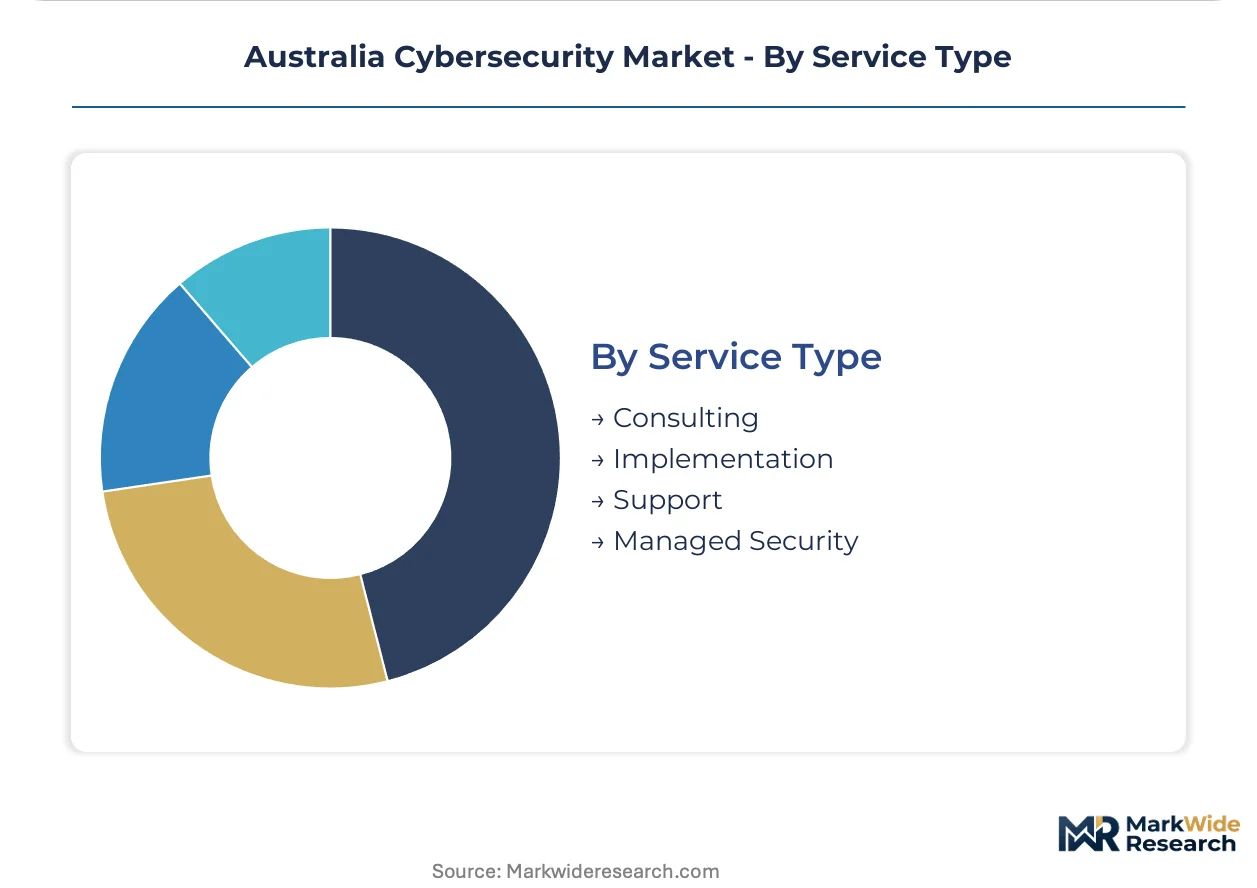
Service Type:
Margin structures diverge here, with consulting capturing value during transformation windows while managed security generates recurring revenue that stabilizes vendor cash flows.
- Managed Security:Continuous monitoring, threat hunting, incident response retainer, and vulnerability management as subscription services. The fastest-expanding service type addresses persistent skills gaps and elevates accountability to board level through defined service level agreements for containment timelines.
- Consulting:Risk assessments, zero-trust architecture design, and compliance readiness evaluations against ASD Essential Eight and APRA CPS 234 frameworks. Mandatory breach notification obligations compress procurement cycles and elevate advisory demand during technology refresh windows.
- Implementation:Deployment engineering, integration with legacy identity systems, and migration to sovereign cloud environments. Security clearance bottlenecks at the Australian Government Security Vetting Agency delay project staffing and extend implementation timelines for defense and intelligence contracts.
- Support:Technical maintenance, software updates, and cleared helpdesk services for classified environments. Domestic content preferences under the Australian Cyber Security Strategy redirect support work toward Australian-based workforces with appropriate vetting levels.
Support underpins long-term vendor relationships through maintenance renewals. Managed Security represents the steepest expansion trajectory as subscription models displace capital expenditure approaches.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Australian Signals Directorate anchors cybersecurity procurement baselines across federal and state jurisdictions, with demand clustering in capital cities where critical infrastructure operators and defense contractors concentrate procurement authority.
New South Wales
Sydney hosts the nation's largest financial services sector and defense industry presence, driving concentrated demand for zero-trust architecture and sovereign cloud migration. APRA's CPS 234 prudential standard mandates independent security assurance for banks and insurers headquartered here. Macquarie Park and the Sydney CBD anchor technology procurement for both commercial and classified government programs.
Victoria
Melbourne's critical infrastructure operators in electricity and water face stepped-up obligations under the Security of Critical Infrastructure Act, generating sustained demand for managed detection and response services. The state's Essential Eight maturity guidelines enforcement shapes vendor qualification for federal contractors. The Melbourne CBD and Docklands precincts concentrate cybersecurity service delivery capabilities.
Australian Capital Territory
Canberra's defense and intelligence ecosystem commands premium pricing tiers due to classification requirements and negative vetting backlogs at the Australian Government Security Vetting Agency. The 2023-2030 Australian Cyber Security Strategy redirects federal spending toward domestic vendors with cleared support workforces. The classified cloud infrastructure program and AUKUS technology-sharing arrangements open procurement channels for NATO-equivalent security clearance holders.
Queensland
Regional hospital networks and primary care consortia undertake first-time security procurement under My Health Record expansion and telehealth permanence. Skills scarcity drives mid-market enterprises toward subscription-based co-managed detection services rather than capital-intensive security operations center builds. Brisbane anchors demand while Gold Coast and Cairns present expansion corridors for distributed security operations capabilities.
Western Australia
Mining and resources sector digitization creates demand for operational technology security and supply chain risk management. The Security of Critical Infrastructure Act obligations extend to port operators and energy infrastructure in the Pilbara and Perth metropolitan area. Domestic content preferences under federal cybersecurity strategy redirect support work toward Australian-based workforces with appropriate vetting levels.
Australia Cybersecurity Market Competitive Environment
Specialist boutiques and integrated platforms split the market between depth and breadth propositions. The vendor base clusters around three strategic archetypes: quantum-enhanced encryption specialists, crowd-sourced vulnerability discovery platforms, and consolidated managed security service providers. Competitive moves center on geographic expansion through specialist practice acquisition and sovereign capability certification for classified procurement eligibility.
Within the quantum-encryption tier, QuintessenceLabs exemplifies high-assurance government contracting through domestic development credentials. Bugcrowd and CyberCX occupy complementary positions—Bugcrowd represents crowd-sourced security testing extending from commercial markets into defense ecosystems, while CyberCX anchors nationwide coverage through acquired specialist practices across state capitals. These three entities illustrate how Australian-owned or Australian-based status increasingly determines supplier qualification under federal procurement restructuring.
| Leading Market Players |
|---|
| Qualysec |
| QuintessenceLabs |
| CyberPulse |
| Nuix |
| Bugcrowd |
| CyberCX |
| Airlock Digital |
| Macquarie Technology Group |
| Tesserent |
| Others |
Value Chain & Pricing Dynamics
Undercapacity of cleared security architects in Canberra and Sydney compresses vendor staffing pipelines while inflating labor cost pass-throughs to government buyers, creating simultaneous pricing power for qualified suppliers and procurement bottlenecks for agencies facing Essential Eight compliance deadlines.
Pricing Analysis
Sydney and Melbourne command 30-40% premiums over Brisbane and Perth for equivalent managed security services due to concentration of federal procurement authority and defense contractor presence. Subscription-based co-managed detection dominates commercial segments while project-based consulting prevails in classified environments where negative vetting requirements inflate delivery costs. Pricing pressure stems from mid-market enterprises abandoning capital-intensive security operations center builds for variable subscription models. Healthcare networks exhibit highest price sensitivity due to constrained capital budgets, while government buyers accept premium tiers for domestic content compliance.
Supply Chain Analysis
Tariff exposure between Australia and China for semiconductor components and network hardware creates procurement vulnerability for domestic systems integrators serving federal clients. Supply chains draw from Taiwan for advanced encryption processors, the United States for threat intelligence platforms, and Israel for specialized endpoint agents. Single-source vulnerability concentrates in sovereign cloud infrastructure where fewer than five ASD-certified strategic hosting providers operate nationally. Distribution runs through systems integrators and specialist consultancies rather than direct vendor relationships, with CyberCX and Tesserent anchoring nationwide fulfillment networks.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Open-source security tools and offshore managed security service providers present viable substitution threats to incumbent Australian vendors, forcing domestic players to differentiate through cleared workforce access and sovereign hosting certification.
For Market Incumbents: Build regulatory moats through accelerated Essential Eight assessor accreditation and negative vetting pipeline investment to compress competitor staffing timelines. Expand Canberra presence via acquisition of cleared specialist practices before AUKUS procurement channels mature. Anchor against offshore substitution by bundling sovereign cloud migration with managed detection services.
For New Entrants and Emerging Players: Regional hospital networks in Queensland and Western Australia represent the most penetrable entry point for first-time security procurement without incumbent relationship entrenchment. Mid-market resources sector operators in Perth offer second-tier opportunity through operational technology security gaps. Lead with subscription-based co-managed detection to bypass capital expenditure barriers.
For Investors and Strategic Acquirers: Long-term, this sits as a consolidation play because federal procurement restructuring under the Australian Cyber Security Strategy favors scaled domestic platforms with cleared workforces over fragmented specialist boutiques. Target acquisition archetypes include Essential Eight assessor firms with existing government panel appointments and quantum-resistant encryption developers with ASD guidance alignment. Monitor negative vetting backlog clearance rates at the Australian Government Security Vetting Agency as inflection indicator for contract velocity recovery.
| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Cleared workforce access compresses six-to-eighteen month staffing delays at the Australian Government Security Vetting Agency. |
| Platform Integration | Unified native-SOAR architectures reduce mean-time-to-containment for APRA CPS 234 regulated financial institutions. |
| Geographic Expansion | Distributed security operations capabilities in Gold Coast and Cairns capture Queensland healthcare digitization demand. |
| Strategic Partnership | AUKUS technology-sharing arrangements open procurement channels for NATO-equivalent security clearance holders. |
| Product Launch | Quantum-resistant encryption modules align with Australian Signals Directorate post-quantum cryptography guidance. |
Study Parameters
A spread of perspectives from chief information security officers at federal agencies, procurement leads at critical infrastructure operators, channel partners in systems integration, and regulatory affairs specialists at financial institutions converged on the working assumptions underlying this analysis. Primary fieldwork combined structured interviews with secondary validation through Australian Signals Directorate guidance documents, APRA prudential standard filings, Privacy Act enforcement records, and Essential Eight maturity assessment reports. Bottom-up segmentation modeling triangulated against top-down macroeconomic indicators across the analysis window.
Demand-supply balance dynamics shaped the forecast framework, with skills scarcity and negative vetting backlogs constraining supply-side capacity against mandatory compliance-driven demand acceleration. Segmentation dimensions modeled encompass solution type, end-user vertical, deployment architecture, and service delivery model alongside geographic procurement authority concentration. CAGRs derived from trend extrapolation of historical contract values adjusted for policy mandate implementation timelines. Industry-specific inputs included Australian Cyber Security Strategy spending redirection patterns and AUKUS information-sharing protocol adoption curves.
Practitioners should monitor Essential Eight maturity assessment disqualification rates and sovereign cloud certification expansion for early signals of competitive positioning shifts. Forecasts reflect documented assumptions regarding policy continuity and clearance processing efficiency. Continuous validation against operating reality is the recommended discipline.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
Middle East and Africa Cybersecurity Market
Cybersecurity
Server Security Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
LAMEA Deception Technology Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
Global Mobile Application Security Market
Cybersecurity
Application Security Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Virtualization Security Tools Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Cloud Application Security Market
Cybersecurity
North America Extended Detection and Response Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Cloud Security in Banking Market