
 Global IoT Digital Forensics Market | 2026-2036
Global IoT Digital Forensics Market Size, Share, and Industry Trends Forecast 2026-2036
Global IoT Digital Forensics Market Foresight
Edge-to-cloud telemetry architecture is rewriting how forensic evidence is extracted from distributed IoT endpoints. Oxygen Forensic leverages proprietary device-level parsing engines to sustain leadership in wearable and mobile IoT evidence recovery. Magnet Forensics anchors North American market presence through deep integration with law enforcement digital evidence management workflows. Cellebrite competes aggressively across connected vehicle and smart home verticals with unified extraction platforms.
IoT digital forensics encompasses the systematic identification, preservation, analysis, and presentation of evidentiary data from internet-connected devices including sensors, actuators, gateways, and edge nodes, utilizing cryptographic chain-of-custody protocols and binary-level memory forensics to reconstruct device states and network communications. The discipline serves criminal investigations, civil litigation, regulatory compliance, and incident response by establishing tamper-proof audit trails across heterogeneous device ecosystems. Cloud-based deployment leads solution architecture as agencies seek elastic compute for large-scale IoT data correlation, while incident response and network forensics command premium investment due to the complexity of reconstructing multi-hop attack vectors across fog and edge layers. Connected vehicles and industrial automation represent the fastest-growing application segments, driven by the proliferation of CAN bus and OPC-UA telemetry requiring specialized reverse-engineering expertise.
The U.S. FBI and Department of Homeland Security shape domestic procurement standards for IoT forensic toolchains through CJIS Security Policy and FedRAMP authorization requirements. Europol and the EU Agency for Cybersecurity enforce cross-border evidence sharing protocols under the European Investigation Order, directly impacting product interoperability mandates for vendors serving multinational clients. ISO/IEC 27043 and NIST SP 800-86 provide foundational methodology frameworks that buyers reference in tender specifications. Stakeholders must monitor the divergence between U.S. CLOUD Act data access provisions and EU GDPR data localization requirements when architecting multi-jurisdictional forensic platforms.
Market Dynamics
Edge-to-cloud telemetry architecture is compressing evidence extraction timelines across distributed IoT endpoints, forcing forensic vendors to rearchitect parsing engines for real-time memory acquisition from resource-constrained sensors and gateways.
Growth Catalysts
- EU AI Act:Mandatory algorithmic audit trails for high-risk IoT systems are expanding forensic tooling budgets across European smart city deployments and connected vehicle fleets.
- Smart city infrastructure:Municipal sensor networks in the United States, Germany, and Japan are generating evidentiary data streams that require specialized chain-of-custody protocols.
- OPC-UA telemetry:Industrial automation systems are embedding forensic-ready logging standards that reduce reconstruction complexity for incident response teams.
Market Restraints
- Silicon supply concentration:Forensic hardware vendors face lead-time volatility from Taiwan-based semiconductor foundries producing specialized memory acquisition chipsets.
- GDPR-EU CLOUD Act friction:Cross-border evidence access disputes between European data localization requirements and U.S. extraterritorial jurisdiction claims are complicating multi-national deployment architectures.
- Flash memory volatility:NAND wear-leveling algorithms in consumer IoT devices are degrading recoverable evidence windows before forensic acquisition can occur.
Strategic Opportunities
- India smart manufacturing:PLI scheme incentives for industrial IoT adoption are creating first-mover advantage for forensic vendors establishing localized evidence processing centers.
- 5G-IoT convergence:Network slicing architectures are enabling carrier-grade forensic interception capabilities that were technically infeasible under 4G radio protocols.
- CSRD disclosure mandates:European corporate sustainability reporting requirements are extending forensic audit scope to environmental sensor data integrity verification.
Industry Challenges
- Binary reverse-engineering expertise:CAN bus protocol analysis and proprietary RTOS forensics require specialized skill sets that command premium compensation and retention difficulty.
- FedRAMP authorization timelines:U.S. federal procurement eligibility requires 12-18 month compliance cycles that delay revenue recognition for cloud-native forensic platforms.
- ISO/IEC 27043 harmonization:Divergent national implementations of digital evidence methodology standards are forcing vendors to maintain multiple certification pathways.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global IoT Digital Forensics Market |
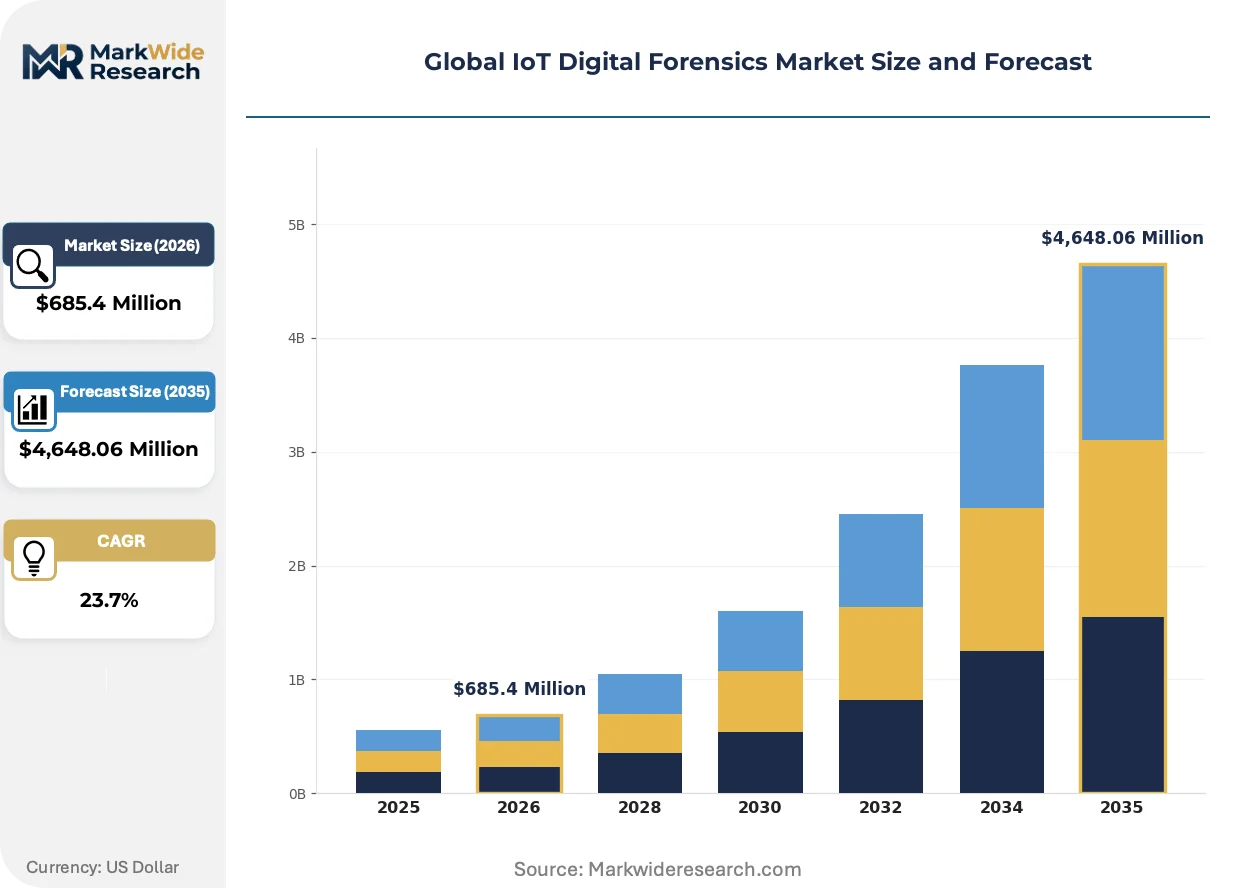
| Market Size in 2026 | $685.4 Million |
| Market Size in 2035 | $4,648.06 Million |
| CAGR (2026 – 2036) | 23.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: Cloud-Based, On-Premises, Hybrid, Edge, Fog Solution: Data Collection, Incident Response, Malware Analysis, Network Forensics, Device Authentication Application: Smart Homes, Industrial Automation, Smart Grids, Connected Vehicles, Wearable Devices End User: Law Enforcement, Cybersecurity Firms, Forensic Laboratories, Government Agencies, Network Operators |
| Companies Covered | Paraben Corporation, Coalfire, Oxygen Forensic, LogRhythm, Envista Forensic, Cellebrite, OpenText, MSAB, Magnet Forensics, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global IoT Digital Forensics Market Shifts & Advancements
Forensic evidence processing is migrating from post-incident batch analysis toward continuous telemetry monitoring, compressing detection-to-response intervals and expanding addressable use cases beyond criminal investigation into proactive threat hunting.
Homomorphic encryption is hybridizing with edge-based evidence collection, enabling law enforcement agencies to perform computational analysis on encrypted IoT telemetry without exposing plaintext data to cloud infrastructure operators. Police digital evidence units in the Netherlands and Singapore are piloting these architectures for smart home device investigations. The structural consequence is fragmenting vendor competitive advantage away from raw extraction speed toward cryptographic protocol implementation depth.
The EU AI Act's high-risk system classification is mandating built-in logging capabilities for biometric IoT deployments, directly expanding forensic audit trail requirements for facial recognition access control and voice authentication endpoints. Industrial buyers in Germany and France are now specifying ISO/IEC 27043-compliant evidence preservation as a procurement gate. Smart building integrators are responding by embedding write-once memory modules that satisfy both operational logging and legal admissibility standards.
Consolidated procurement through national digital evidence management frameworks is displacing point-solution purchasing across European law enforcement agencies. The United Kingdom's National Police Chiefs' Council and France's Gendarmerie Nationale are centralizing vendor selection through framework agreements that bundle IoT forensics with mobile and computer forensics tooling. This concentration is most visible in connected vehicle investigations, where standardized CAN bus extraction protocols are becoming a non-negotiable tender requirement.
Global IoT Digital Forensics Market Segmentation
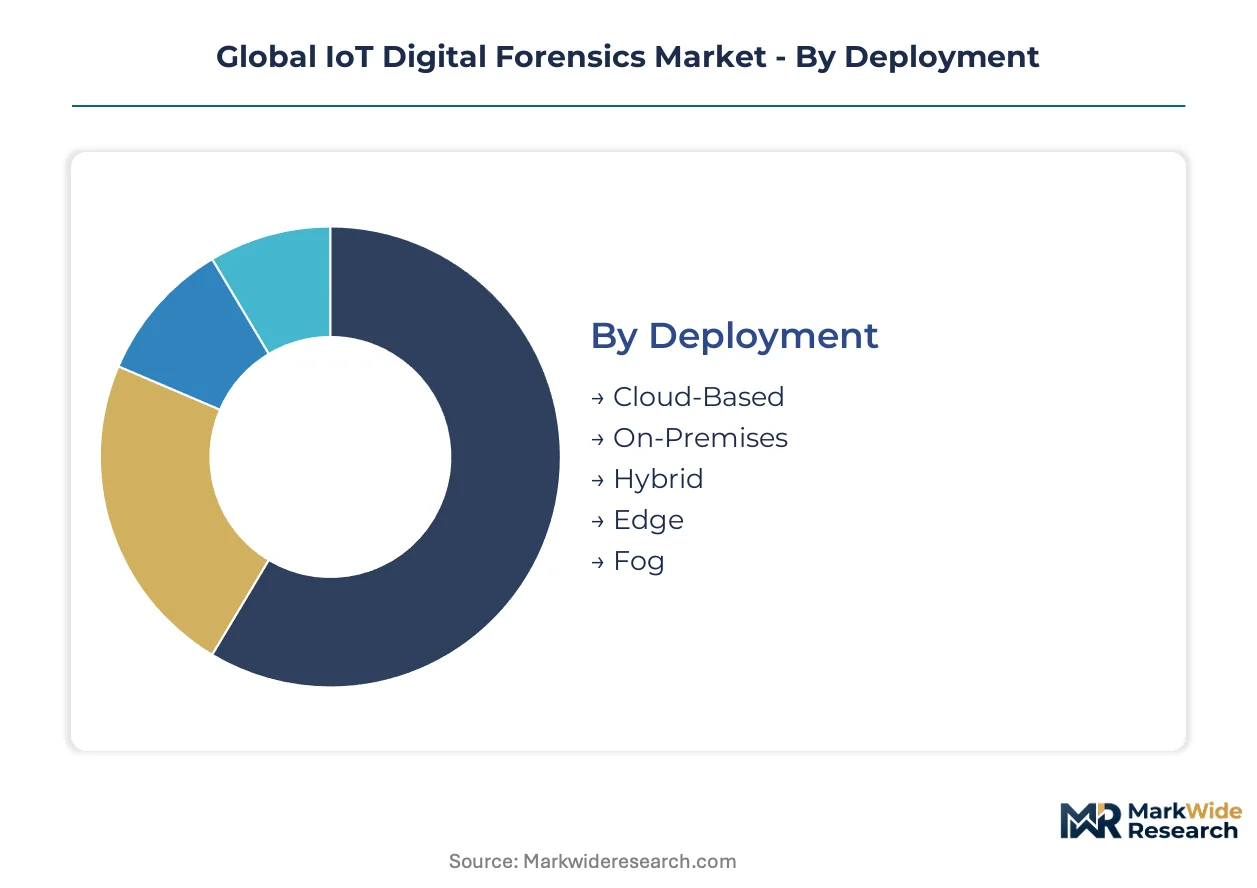
IoT digital forensics segmentation reflects the architectural complexity of distributed evidence ecosystems spanning cloud, edge, and device layers. Procurement patterns diverge sharply between criminal justice workflows requiring chain-of-custody rigor and enterprise incident response prioritizing speed over admissibility standards.
Deployment:
Use-case spectrum spans elastic correlation of petabyte-scale sensor telemetry to air-gapped acquisition in classified environments.
- Cloud-Based:Elastic compute architectures enable real-time correlation across millions of distributed IoT endpoints. Law enforcement agencies in the United States and Germany are consolidating procurement through FedRAMP-authorized platforms to satisfy CJIS Security Policy requirements for criminal evidence handling.
- On-Premises:Air-gapped infrastructure serves classified government facilities and critical infrastructure operators with data sovereignty mandates. Defense contractors and nuclear facility operators in France and Japan specify on-premises deployment to satisfy national security regulations prohibiting cross-border data transit.
- Hybrid:Tiered architectures partition sensitive acquisition locally while pushing analytics to cloud substrates.
- Edge:Resource-constrained parsing engines deploy directly on IoT gateways for latency-sensitive incident response.
- Fog:Intermediate compute layers aggregate evidence from sensor clusters before upstream transmission.
The dominant share belongs to Cloud-Based deployment, while Edge is closing the gap fastest as 5G network slicing enables carrier-grade forensic interception.
Solution:
Customer type determines solution prioritization — criminal investigators demand admissibility-grade documentation while enterprise security teams optimize for mean-time-to-containment.
- Data Collection:Proprietary parsing engines extract binary artifacts from NAND flash, eMMC, and NOR memory architectures across heterogeneous IoT device populations. Municipal smart city operators in Singapore and Dubai are mandating standardized collection protocols for sensor network evidence preservation.
- Incident Response:Automated playbook orchestration compresses detection-to-containment intervals for multi-hop attacks traversing fog and edge layers. Managed security service providers in the United Kingdom and Australia are bundling IoT-specific response retainers for industrial automation clients.
- Malware Analysis:Sandbox environments execute IoT firmware in emulated hardware configurations to identify persistence mechanisms.
- Network Forensics:Protocol reconstruction engines parse OPC-UA, MQTT, and CoAP telemetry to reconstruct attack vectors.
- Device Authentication:Cryptographic attestation verifies device integrity prior to evidence acquisition.
Data Collection commands the largest procurement allocation, though Incident Response is expanding most quickly as proactive threat hunting displaces post-breach investigation.
Application:
Volume concentration tracks smart infrastructure deployment density across municipal, industrial, and consumer domains.
- Smart Homes:Voice assistants, security cameras, and environmental sensors generate evidentiary data streams for domestic violence and burglary investigations. Police digital evidence units in the Netherlands and Canada are establishing dedicated smart home device laboratories to handle extraction backlogs.
- Industrial Automation:OPC-UA telemetry from programmable logic controllers and SCADA systems requires specialized reverse-engineering expertise for incident reconstruction. German automotive manufacturers are specifying forensic-ready logging as a procurement requirement for Industry 4.0 equipment purchases.
- Smart Grids:Phasor measurement units and smart meter networks create audit trail requirements for utility cybersecurity compliance.
- Connected Vehicles:CAN bus and Ethernet-based automotive networks preserve collision reconstruction and insurance fraud evidence.
- Wearable Devices:Biometric and location telemetry supports health data integrity verification and alibi establishment.
Industrial Automation holds the dominant position, while Connected Vehicles is climbing the fastest as automotive cybersecurity regulations mandate standardized evidence preservation.
End User:
Margin structure varies across procurement frameworks — national police tenders emphasize total cost of ownership while enterprise buyers prioritize integration speed.
- Law Enforcement:Criminal justice agencies require ISO/IEC 27043-compliant toolchains with courtroom-admissible chain-of-custody documentation. The FBI and Europol shape interoperability standards through framework agreements that bundle IoT forensics with mobile and computer forensics capabilities.
- Cybersecurity Firms:Managed detection and response providers integrate IoT forensics into broader threat hunting service offerings. CrowdStrike and Mandiant competitors in Israel and the United States are building specialized IoT practices to differentiate in saturated enterprise security markets.
- Forensic Laboratories:Independent testing facilities provide third-party validation for device extraction methodologies.
- Government Agencies:National security and intelligence organizations operate classified programs for targeted IoT device exploitation.
- Network Operators:Telecommunications carriers leverage 5G network slicing for lawful intercept and evidence preservation.
Law Enforcement captures the dominant procurement volume, though Cybersecurity Firms are gaining share fastest as enterprise IoT attack surface expansion outpaces public sector budget cycles.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Export-import dynamics in IoT digital forensics tooling favor technology-exporting economies. The United States, Germany, and Japan maintain net export positions in specialized forensic software and hardware, while emerging smart city markets in India and Singapore drive import demand for evidence-processing infrastructure.
United States
FBI CJIS Security Policy mandates shape procurement standards for cloud-based forensic platforms. FedRAMP authorization requirements create 12-18 month compliance barriers for foreign vendors entering federal contracts. The Washington-Boston corridor concentrates cybersecurity vendors serving law enforcement digital evidence units.
Germany
Automotive OEMs in Bavaria and Baden-Württemberg specify forensic-ready OPC-UA logging for Industry 4.0 equipment purchases. The EU AI Act drives algorithmic audit trail mandates for biometric IoT systems deployed in smart city infrastructure. Berlin hosts Europol coordination centers establishing cross-border evidence-sharing protocols.
Japan
METI industrial cybersecurity guidelines accelerate forensic tooling adoption in connected vehicle manufacturing clusters. The Nagoya-Toyota corridor generates specialized demand for CAN bus protocol analysis capabilities. Japanese semiconductor foundries supply memory acquisition chipsets to global forensic hardware vendors.
India
PLI scheme incentives for industrial IoT adoption create first-mover opportunities for evidence-processing center localization. State-level smart city missions in Maharashtra and Gujarat generate municipal procurement for sensor network forensic protocols. Bangalore cybersecurity firms build specialized IoT forensics practices for export service delivery.
Singapore
National cybersecurity agency directives mandate forensic telemetry standards for critical infrastructure IoT deployments. The city-state's 5G network slicing infrastructure enables carrier-grade lawful intercept capabilities for regional law enforcement partners. Government digital evidence laboratories pilot homomorphic encryption architectures for smart home device investigations.
Global IoT Digital Forensics Market Competitive Landscape
On the supply side, the industry is consolidating around platform vendors with integrated extraction-to-analysis workflows. Tiered competitive structure separates full-stack forensic suite providers from specialized device-parsing specialists. Three archetypes dominate: law enforcement workflow integrators, automotive and industrial vertical specialists, and cloud-native telemetry correlation platforms. M&A activity concentrates on acquiring proprietary parsing engine technology, while strategic partnerships with telecommunications carriers unlock 5G network slicing forensic capabilities.
Within the law enforcement workflow integrator tier, Cellebrite and Magnet Forensics occupy positions shaped by deep CJIS Security Policy compliance and North American procurement frameworks. Oxygen Forensic represents the specialized device-parsing archetype, with proprietary engines targeting wearable and mobile IoT endpoints. These three anchors demonstrate how competitive positioning fragments across extraction methodology depth rather than geographic coverage alone.
| Leading Market Players |
|---|
| Paraben Corporation |
| Coalfire |
| Oxygen Forensic |
| LogRhythm |
| Envista Forensic |
| Cellebrite |
| OpenText |
| MSAB |
| Magnet Forensics |
| Others |
Supply & Pricing Matrix
Taiwan-based semiconductor foundry concentration for specialized memory acquisition chipsets exposes forensic hardware vendors to dual pricing tier compression and supply chain reconfiguration pressures. This single-source dependency forces cloud-native platform providers toward extended FedRAMP authorization timelines that inflate customer acquisition costs while compressing margin structures for on-premises deployment specialists.
Pricing Analysis
Industrial OEM buyers anchor a three-tier pricing structure across premium, standard, and economy levels in IoT digital forensics procurement. Premium tiers command certification-grade documentation aligned with ISO/IEC 27043 and CJIS Security Policy mandates, while economy tiers serve incident-response teams prioritizing speed over courtroom admissibility. Price differentiation hinges on chain-of-custody rigor and vertical integration depth of parsing engine technology. Cost compression in standard tiers is intensifying because municipal smart city operators are consolidating procurement through national framework agreements. Law enforcement agencies exhibit lowest price sensitivity due to federal grant funding, whereas managed security service providers face acute margin pressure from bundled service expectations.
Supply Chain Analysis
Taiwan Semiconductor Manufacturing Company and United Microelectronics Corporation hold dominant capacity for forensic-grade NAND flash and eMMC memory acquisition chipsets. Hardware assembly draws from China, Mexico, and Vietnam for cost-optimized component integration. Raw material dependencies span silicon wafers, specialized FPGA modules, and cryptographic security elements. Single-source vulnerability concentrates in Taiwanese foundry output for high-reliability memory parsing engines. Distribution runs through authorized reseller networks serving law enforcement digital evidence units and direct enterprise sales for cybersecurity firm integration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Buyer power is concentrating through consolidated national procurement frameworks that displace point-solution purchasing across European and North American law enforcement agencies. This framework-agreement dominance shifts vendor selection criteria toward bundled workflow integration and away from specialized extraction speed.
For Market Incumbents: Pre-empt cloud-native entrant displacement by deepening proprietary parsing engine moats in wearable and connected vehicle verticals. Acquire specialized CAN bus and OPC-UA protocol analysis capabilities before automotive cybersecurity regulations mandate standardized evidence preservation. Invest in FedRAMP authorization acceleration to compress 12-18 month compliance cycles that currently delay federal revenue recognition. For New Entrants and Emerging Players: Build out localized evidence processing centers in India to capture PLI scheme-driven industrial IoT adoption before incumbent forensic laboratories establish regional presence. Target smart manufacturing corridors in Maharashtra and Gujarat with OPC-UA telemetry expertise that incumbent vendors have underdeveloped. Pursue carrier-grade 5G network slicing partnerships as the primary go-to-market angle for lawful intercept capabilities. For Investors and Strategic Acquirers: EU AI Act high-risk system classification reshapes the acquisition landscape by mandating built-in logging capabilities that expand forensic audit trail addressable spend. Long-term viability favors vendors with cryptographic protocol implementation depth over raw extraction speed competitors. Target acquisition archetypes include specialized RTOS forensics boutiques and homomorphic encryption pilot operators. Watch for Netherlands and Singapore government laboratory homomorphic encryption deployment scale-up as the signal indicating mainstream adoption inflection.| Strategic Initiative | Industry Significance |
|---|---|
| Proprietary Parsing Engine Acquisition | Secures device-level extraction moats in wearable and mobile IoT endpoints against cloud-native competitors. |
| FedRAMP Authorization Acceleration | Unlocks FBI and Department of Homeland Security procurement eligibility for federal law enforcement contracts. |
| 5G Network Slicing Partnership | Enables carrier-grade forensic interception capabilities technically infeasible under legacy 4G radio protocols. |
| OPC-UA Telemetry Certification | Aligns with German automotive OEM forensic-ready logging mandates for Industry 4.0 equipment procurement. |
| Homomorphic Encryption Pilot Scale-Up | Positions vendors for EU AI Act biometric IoT audit trail requirements without plaintext data exposure. |
Research Methodology
A standing panel of digital evidence unit commanders, forensic laboratory directors, cybersecurity firm CTOs, and smart city infrastructure procurement officers provided ongoing calibration throughout the study. Primary fieldwork combined structured interviews with law enforcement agency technology leads and industrial automation security architects. Secondary validation drew from Europol threat assessment publications, NIST SP 800-86 documentation, FBI CJIS Security Policy updates, and ISO/IEC 27043 implementation guidelines. Bottom-up device shipment and procurement tender analysis triangulated against top-down spending estimates from national digital evidence management framework disclosures.
Scenario bracketing anchored volume projections across conservative, baseline, and expansion cases reflecting divergent regulatory enforcement intensity. The analytical framework modeled deployment mode, solution type, application vertical, and end-user segment dimensions throughout the projection horizon. CAGRs derived from segment-level growth rate synthesis weighted by procurement pattern momentum. Forecast inputs incorporated EU AI Act implementation timelines, 5G network slicing infrastructure deployment curves, and industrial IoT PLI scheme incentive uptake trajectories.
The forecast holds incumbent behavior within observed patterns; aggressive vertical integration moves by cloud-native platform providers or specialized RTOS forensics boutiques would shift outcomes. Regulatory friction between GDPR data localization and U.S. CLOUD Act extraterritorial claims, Taiwanese foundry capacity constraints, and NAND flash wear-leveling algorithm evolution represent primary revision risks. Quarterly review of national framework agreement award volumes and homomorphic encryption pilot expansion indicators is advised to detect inflection.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Network Traffic Analysis Solutions Market
Cybersecurity
Asia Pacific IoT Security Market
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Global Cloud Encryption Market
Cybersecurity
Global Sandboxing Market
Cybersecurity
Canada Ransomware Protection Market
Cybersecurity
Asia-Pacific Software Defined Perimeter Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Threat Hunting Market
Cybersecurity
Saas-Based IT Security Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Data Diode Solution Market