
 Hungary Cybersecurity Market | 2026-2036
Hungary Cybersecurity Market Size, Share, and Industry Trends Forecast 2026-2036
Hungary Cybersecurity Market Foresight
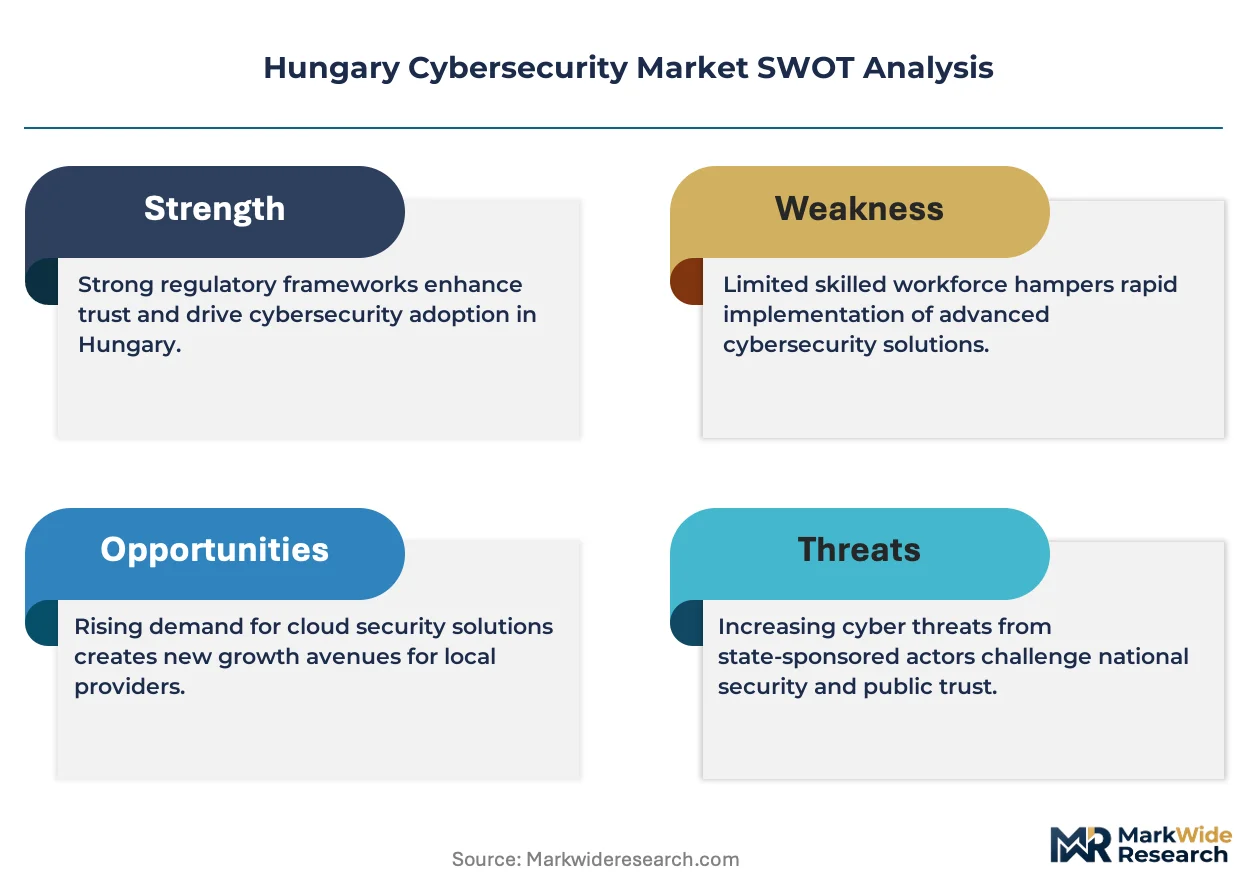
Cybersecurity talent scarcity in Hungary is rotating enterprise procurement toward managed security services and automated threat detection platforms. IBM Corporation leverages its Budapest delivery center to sustain regional consulting capacity for banking and telecom clients. Balasys IT Ltd. anchors domestic firewall and encryption deployments with localized compliance expertise. Magyar Telekom competes through integrated network-security bundles across its enterprise subscriber base.
Cybersecurity encompasses hardware, software, and service layers designed to protect digital assets from unauthorized access, data exfiltration, and operational disruption through mechanisms including AES-256 encryption, behavioral anomaly detection, and zero-trust network segmentation. Its primary purpose is ensuring confidentiality, integrity, and availability of information systems across commercial and governmental operations. Cloud-based deployment models are capturing accelerated enterprise migration as Hungarian firms retire legacy on-premises infrastructure. Managed Security Services represent the fastest-expanding service category, driven by skills shortages and NIS2-driven 24/7 monitoring mandates. The BFSI end-user segment dominates current spending, though healthcare providers are expanding procurement to address patient data protection requirements.
Hungary's cybersecurity governance integrates the National Cybersecurity Strategy, NIS2 transposition requirements enforced by the National Cybersecurity Center, and GDPR-aligned data protection standards administered by the National Authority for Data Protection and Freedom of Information. These frameworks mandate incident reporting timelines, supply-chain security assessments, and critical infrastructure operator certification, directly shaping vendor qualification criteria and procurement specifications. Stakeholders must monitor forthcoming sector-specific NIS2 implementation decrees that will define mandatory technical and organizational measures for energy, transport, and digital service providers.
Market Dynamics
NIS2 transposition deadlines are compressing procurement cycles across Hungarian critical infrastructure, forcing operators to accelerate security architecture overhauls ahead of enforcement milestones.
Growth Catalysts
- NIS2 Compliance Mandates:The National Cybersecurity Center's incident reporting requirements are compelling energy and transport operators to deploy 24/7 security operations centers ahead of statutory deadlines.
- Zero-Trust Architecture:Budapest's banking sector is replacing perimeter-based defenses with microsegmentation frameworks to satisfy internal risk committees and external auditors simultaneously.
- Healthcare Digitalization:Hospital information systems modernization is creating demand for patient data encryption and access logging systems aligned with GDPR technical standards.
Market Restraints
- Specialized Talent Scarcity:Domestic universities produce insufficient certified ethical hackers and SOC analysts, forcing wage inflation above regional averages.
- Legacy Infrastructure Debt:State agencies and manufacturing SMEs operate decades-old SCADA and ERP systems that resist API-based security integration without complete replacement.
- Import Dependency:Hardware security modules and advanced firewall appliances rely on German and US supply chains vulnerable to extended lead times.
Strategic Opportunities
- Managed Detection and Response:Mid-market manufacturers in the Budapest enterprise corridor are outsourcing threat hunting to avoid building in-house SOC capabilities.
- Cloud-Native Security:Convergence of containerization and Kubernetes security tooling is opening deployment pathways for Hungarian software vendors.
- Critical Infrastructure Certification:NIS2 sector-specific decrees will create mandatory procurement specifications for energy distributors and wastewater utilities.
Industry Challenges
- Skills Pipeline Gaps:Universities lack curricula synchronized with CISSP and CEH certification requirements, forcing employers into expensive retraining cycles.
- Interoperability Friction:Heterogeneous legacy stacks across Hungarian enterprises complicate single-vendor security platform rollouts and increase integration costs.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Hungary Cybersecurity Market |
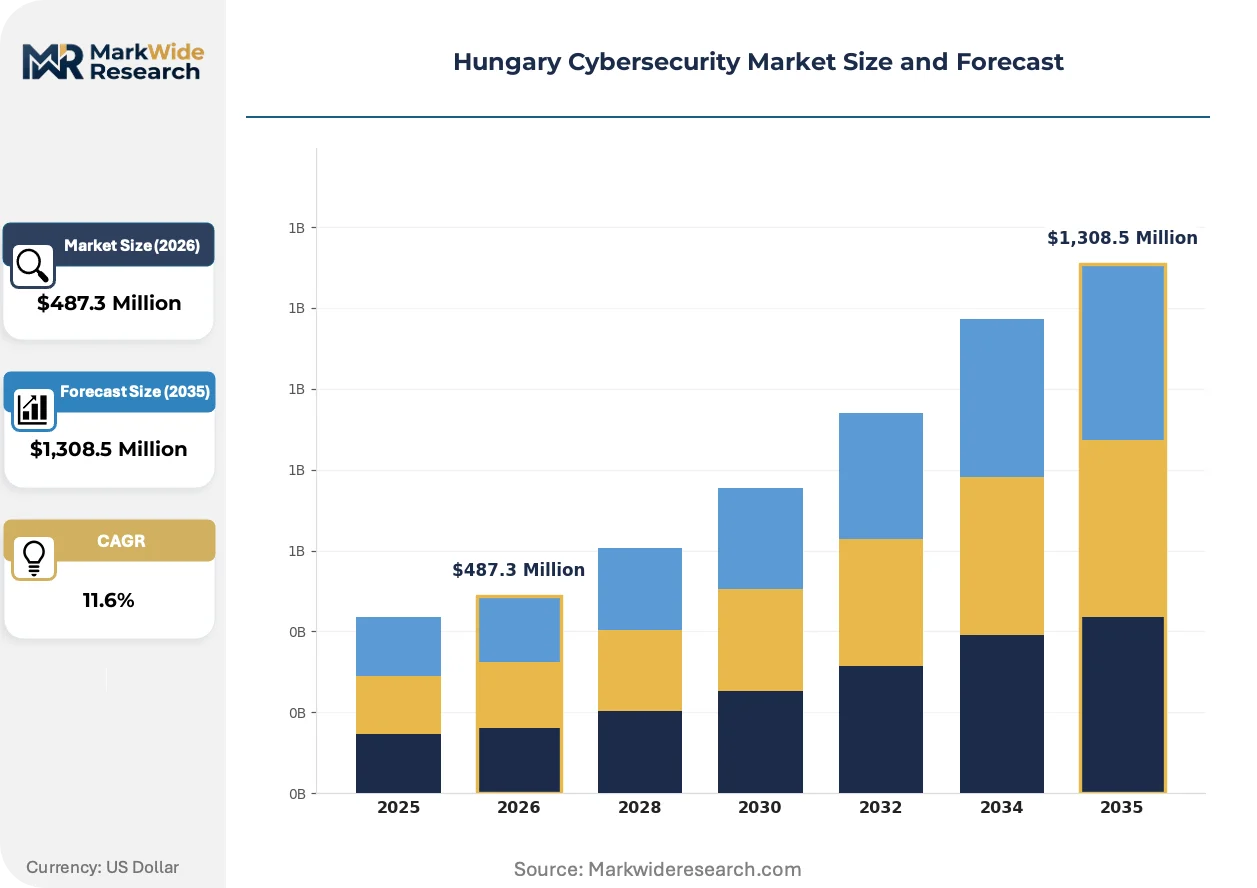
| Market Size in 2026 | $487.3 Million |
| Market Size in 2035 | $1,308.5 Million |
| CAGR (2026 – 2036) | 11.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewall, Antivirus, Intrusion Detection System, Encryption Software Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Service End User: Government, BFSI, Healthcare, Retail Service Type: Consulting, Implementation, Managed Security Services, Training |
| Companies Covered | IBM Corporation, Magyar Telekom / T-Systems Hungary, Seon Fraud Fighters, Cisco Systems, Inc., Microsoft Corporation, Balasys IT Ltd., Tresorit, Avatao, Hackrate, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Hungary Cybersecurity Market Shifts & Advancements
Security architecture decisions in Hungary are separating into two distinct tracks: cloud-native transformation for digital-first enterprises and defensive hardening for operational technology environments.
Extended detection and response platforms are consolidating endpoint, network, and cloud telemetry into unified analyst workflows. Hungarian financial institutions are deploying these systems within eighteen-month refresh cycles. The vendor landscape is bifurcating between integrated suites and best-of-breed specialists, compressing mid-tier security software margins.
NIS2 implementation decrees issued by the National Cybersecurity Center are mandating supply-chain security assessments for critical infrastructure operators. Energy distributors must now certify third-party vendor access controls before contract execution. Healthcare providers face the tightest compliance timelines, with patient data processing agreements requiring technical security annexes.
Enterprise buyers are unbundling managed security services from telecommunications contracts. Magyar Telekom's enterprise base is negotiating standalone SOC agreements with specialized cybersecurity providers. Manufacturing firms in western Hungary are driving this disintermediation, seeking vendor-agnostic threat intelligence rather than carrier-captive offerings.
Hungary Cybersecurity Market Segmentation
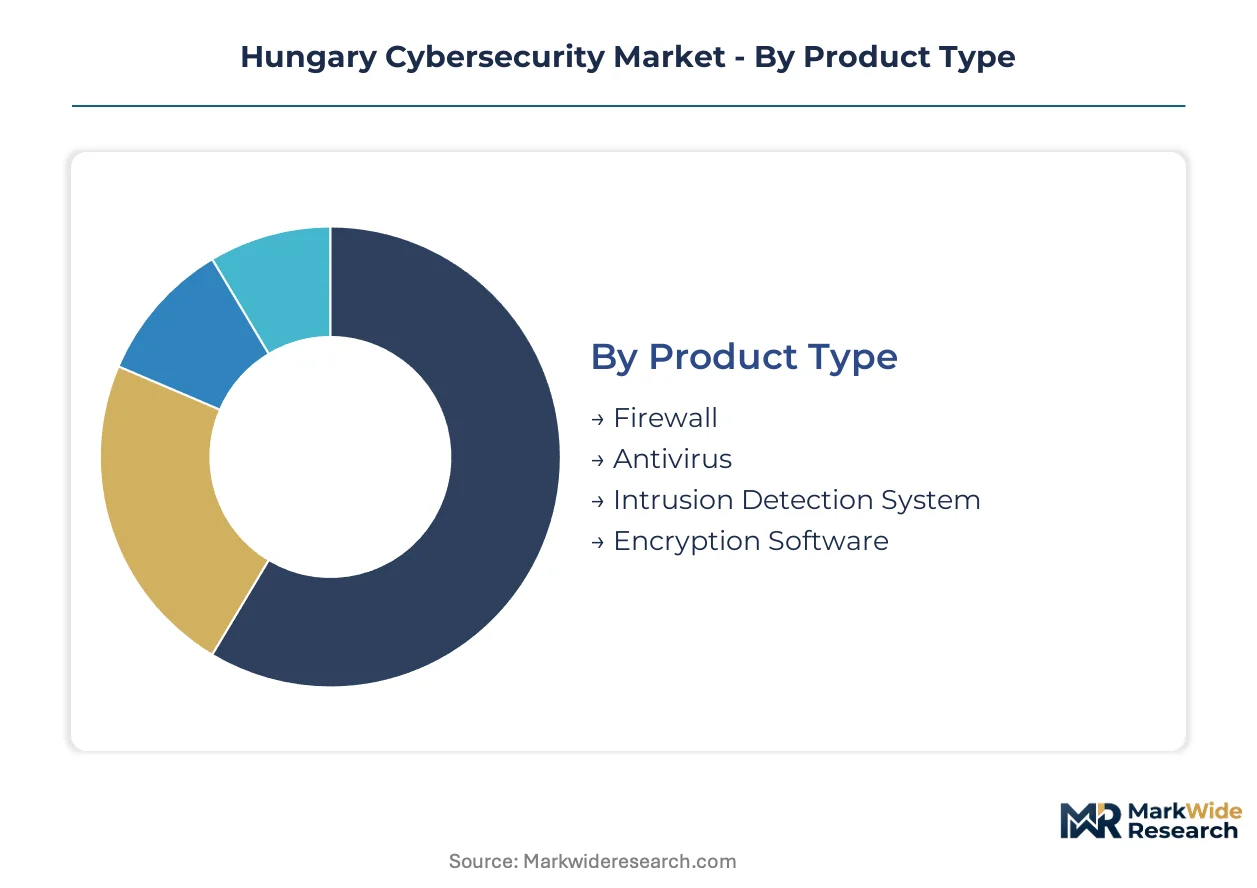
Hungary's cybersecurity market segments reflect divergent procurement priorities across legacy infrastructure defenders and cloud-native adopters. NIS2 compliance deadlines are reshaping budget allocation across product categories and service models.
Product Type:
Margin pools concentrate in encryption software and next-generation firewall appliances where NIS2 mandates drive premium pricing for certified deployments.
- Firewall:Next-generation firewalls integrate deep packet inspection with application-layer controls for Budapest banking networks. Magyar Telekom's enterprise corridor demands hardware appliances with localized threat intelligence feeds and sub-millisecond latency specifications.
- Encryption Software:AES-256 and post-quantum cryptographic modules protect patient records and financial transactions under GDPR technical standards. Healthcare providers in Debrecen and Szeged are procuring field-level encryption for legacy hospital information systems.
- Antivirus:Endpoint protection platforms with behavioral heuristics defend manufacturing SMEs in western Hungary against ransomware payloads.
- Intrusion Detection System:Network-based and host-based sensors monitor SCADA environments for energy distributors facing mandatory 24/7 surveillance requirements.
The dominant share belongs to Firewall, while Encryption Software is closing the gap fastest as healthcare digitalization accelerates.
Deployment Model:
Volume concentration tilts toward hybrid architectures as state agencies straddle legacy on-premises systems and cloud migration timelines.
- Managed Service:Outsourced security operations centers deliver 24/7 threat monitoring without domestic SOC analyst recruitment. Mid-market manufacturers across the Budapest enterprise corridor favor subscription models to bypass skills shortages.
- Cloud-Based:Container-native security platforms protect Kubernetes workloads for software vendors and fintech startups. The Hungarian National Cloud strategy accelerates sovereign cloud procurement with data residency guarantees.
- On-Premises:Air-gapped deployments persist in defense and critical infrastructure where network segmentation mandates prohibit external connectivity.
- Hybrid:Split workloads combine private cloud encryption gateways with on-premises identity management for banks transitioning core systems incrementally.
Managed Service commands the largest revenue pool, though Cloud-Based deployment is expanding most quickly among digital-native enterprises.
End User:
Application intensity varies sharply across sectors with divergent regulatory pressure and asset sensitivity profiles.
- BFSI:Budapest's banking sector deploys zero-trust microsegmentation and privileged access management to satisfy internal risk committees and ECB supervisory expectations. OTP Bank and K&H lead procurement of behavioral biometrics and transaction monitoring systems.
- Government:National Cybersecurity Center directives mandate supply-chain security assessments and incident response playbooks for state agencies. The National Tax and Customs Administration is modernizing endpoint detection across regional offices.
- Healthcare:Hospital information systems require patient data encryption and access logging aligned with GDPR technical annexes. Semmelweis University and regional hospitals face the tightest NIS2 implementation timelines.
- Retail:E-commerce platforms and payment processors deploy web application firewalls and tokenization for card-not-present transactions.
BFSI retains the dominant expenditure position, while Healthcare is gaining share fastest as patient data protection requirements tighten.
Service Type:
Customer type differentiation separates enterprises seeking strategic advisory from operators requiring operational execution.
- Managed Security Services:Continuous monitoring, threat hunting, and incident response delivered through Budapest-based SOCs. Energy distributors and transport operators outsource 24/7 coverage to meet NIS2 surveillance mandates without building captive capabilities.
- Consulting:Risk assessments, architecture design, and compliance gap analyses for boards and CISOs. IBM's Budapest delivery center sustains regional capacity for banking and telecom transformation programs.
- Implementation:Deployment and integration services for firewall appliances, encryption infrastructure, and identity platforms. System integrators bridge skills gaps in legacy SCADA security retrofitting.
- Training:Certification preparation for CISSP, CEH, and vendor-specific credentials addressing domestic talent pipeline deficiencies.
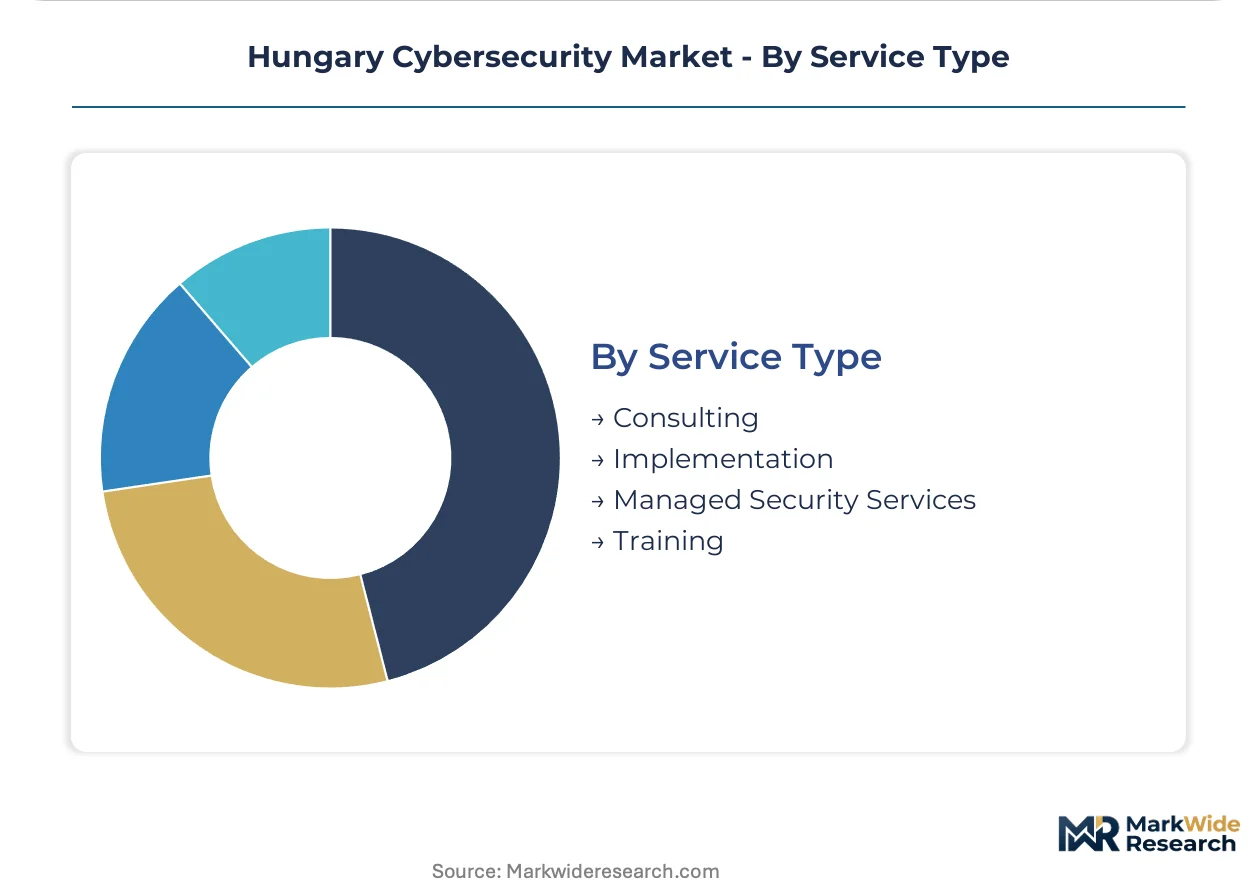
Managed Security Services holds the leading revenue position, with Consulting climbing fastest as NIS2 readiness assessments compress procurement cycles.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Hungary's cybersecurity consumption patterns diverge from neighboring states through tighter NIS2 transposition timelines and heavier state-agency procurement concentration. Budapest anchors enterprise demand while regional cities address healthcare and manufacturing gaps.
Central Hungary
Budapest's financial district drives zero-trust architecture deployments across OTP Bank and K&H. The National Cybersecurity Center enforces incident reporting mandates compressing procurement cycles. The Budapest enterprise corridor concentrates managed security services demand from mid-market manufacturers.
Western Transdanubia
Manufacturing SMEs in Győr and Sopron outsource threat detection to bypass domestic skills shortages. GDPR technical standards govern patient data processing agreements for regional healthcare networks. Automotive suppliers near the Austrian border deploy air-gapped SCADA monitoring for production line integrity.
Southern Great Plain
Hospitals in Szeged and Békéscsaba accelerate encryption procurement ahead of NIS2 healthcare implementation decrees. The National Authority for Data Protection audits access logging systems for legacy hospital information platforms. University medical centers anchor cybersecurity training partnerships with Budapest-based consultancies.
Northern Hungary
Energy distributors in Miskolc deploy 24/7 security operations centers to satisfy surveillance mandates. Critical infrastructure operators face mandatory supply-chain security assessments before vendor contracting. Mining and metallurgical firms retrofit decades-old ERP systems with API-based monitoring gateways.
Hungary Cybersecurity Market Competitive Landscape
A small set of integrated leaders sits above a broader specialist tier, with multinational technology conglomerates competing against domestic compliance-focused providers. The upper tier combines global threat intelligence feeds with localized delivery capacity. Three archetypes dominate: integrated technology platforms, telecommunications-captive security bundles, and pure-play compliance specialists. Competitive moves center on managed service outsourcing contracts and zero-trust architecture certification programs.
Within the integrated platform tier, IBM Corporation anchors regional consulting capacity through its Budapest delivery center, while Microsoft Corporation exemplifies cloud-native security convergence. Among domestic specialists, Balasys IT Ltd. occupies a position representing localized firewall and encryption expertise aligned with National Cybersecurity Center requirements. These three entities collectively illustrate the market's bifurcation between global scale and regulatory proximity.
| Leading Market Players |
|---|
| IBM Corporation |
| Magyar Telekom / T-Systems Hungary |
| Seon Fraud Fighters |
| Cisco Systems, Inc. |
| Microsoft Corporation |
| Balasys IT Ltd. |
| Tresorit |
| Avatao |
| Hackrate |
| Others |
Supply & Pricing Matrix
Sixty-to-ninety-day lead times for hardware security modules from German suppliers compress procurement cycles and amplify pricing power for certified encryption vendors serving Budapest's banking sector. Inventory buffers at domestic distributors remain thin, forcing mid-market manufacturers into premium pricing tiers for expedited firewall appliance delivery.
Pricing Analysis
Long-term managed security service contracts dominate enterprise procurement, with three-year subscriptions locking in SOC coverage rates before NIS2 enforcement tightens vendor qualification criteria. Price differentiation hinges on certification tier (Common Criteria EAL4+ versus baseline CE marking) and bundled after-sales response time (four-hour versus next-business-day). Cost compression in standard-tier endpoint protection intensifies as Cisco and Microsoft bundle security modules into existing enterprise agreements. State agencies exhibit highest price sensitivity due to fixed annual IT budgets, while OTP Bank and K&H absorb premium pricing for zero-trust architecture consulting.
Supply Chain Analysis
Hardware security modules and next-generation firewall appliances draw from concentrated manufacturing in Germany, the United States, and Taiwan, with Budapest-based distributors holding thirty-to-forty-five days of forward cover. Semiconductor components for encryption accelerators and network processors rest on silicon wafer supply from South Korean foundries. Single-source vulnerability persists for FIPS 140-2 certified modules where only three global vendors qualify for Hungarian critical infrastructure procurement. Distribution runs through Budapest-based system integrators with direct relationships to the National Cybersecurity Center for compliance pre-certification.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Hungary cybersecurity market functions as a defensive-moat opportunity where regulatory entrenchment creates durable competitive positioning. NIS2 certification requirements erect switching costs that protect incumbent vendor relationships across energy and healthcare verticals.
For Market Incumbents: Consolidate managed security service contracts through multi-year SOC agreements that embed incident response playbooks ahead of sector-specific NIS2 decrees. Acquire Budapest-based training providers to address domestic CISSP certification gaps and capture retraining revenue from skills-shortage-driven procurement. Vertical integration into cloud-native security tooling protects margin pools as containerization displaces legacy firewall appliances.
For New Entrants and Emerging Players: Lead with specialized healthcare encryption solutions targeting Semmelweis University and regional hospitals facing the tightest GDPR technical compliance timelines. Penetrate western Hungary's manufacturing corridor with air-gapped SCADA monitoring for automotive suppliers resisting carrier-captive security bundles. Deploy vendor-agnostic threat intelligence platforms to exploit Magyar Telekom's enterprise base disintermediation.
For Investors and Strategic Acquirers: Carve-out targets emerge from telecommunications parent companies spinning non-core cybersecurity divisions. Long-term viability rests on NIS2 implementation decree enforcement sustaining mandatory procurement specifications. Monitor National Cybersecurity Center sector-specific announcements as the inflection signal for energy and transport operator security architecture overhaul timelines.
| Strategic Initiative | Industry Significance |
|---|---|
| Managed Security Service Expansion | Budapest-based SOCs capture NIS2-mandated 24/7 surveillance contracts from energy distributors. |
| Zero-Trust Architecture Certification | Microsegmentation frameworks satisfy OTP Bank risk committees and ECB supervisory expectations simultaneously. |
| Healthcare Encryption Specialization | Field-level encryption for legacy hospital information systems addresses GDPR technical annex requirements. |
| Cloud-Native Security Platform Launch | Kubernetes security tooling opens deployment pathways for Hungarian software vendors in sovereign cloud environments. |
| Critical Infrastructure Vendor Qualification | Supply-chain security assessment capabilities position providers for mandatory energy distributor procurement specifications. |
Research Methodology
Two parallel data streams informed the analysis: structured primary interviews with CISOs at OTP Bank and K&H, National Cybersecurity Center policy officers, procurement leads at energy distributors in Miskolc, and healthcare IT directors at Semmelweis University; alongside secondary validation through National Authority for Data Protection enforcement notices, NIS2 transposition decrees, and enterprise security expenditure disclosures. Bottom-up segmentation modeling triangulated against top-down macroeconomic indicators produced volume and value estimates.
Across the analysis window, forecasts incorporated deployment model migration patterns, end-user vertical regulatory pressure differentials, and service type outsourcing intensity. CAGRs derived from segment-level growth trajectory analysis weighted by NIS2 implementation timeline proximity. Industry-specific inputs included certified ethical hacker pipeline data from domestic universities and hardware security module import volume patterns from customs records.
The analysis sits within stated boundaries; outcomes outside sustained NIS2 enforcement or accelerated cloud migration timelines would require recalibration. Forecasts reflect documented assumptions regarding regulatory implementation pace and skills shortage persistence. Outputs are directional rather than point-estimates.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
IT and Telecom Cyber Security Market
Cybersecurity
Europe Data Protection-As-A-Service Market
Cybersecurity
Global Mobile Data Protection Market
Cybersecurity
Latin America Ransomware Protection Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Micro-Segmentation Solutions Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Dark Web Intelligence Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
Global Mobile Application Security Market
Cybersecurity
Latin America IoT Security Market
Cybersecurity
Mainframe Security Market
Cybersecurity
Middle East & Africa AI Cybersecurity Market
Cybersecurity
Network Sandboxing Market
Cybersecurity
Micro Segmentation Technology Market
Cybersecurity
Enterprise Network Firewall Market