
 Micro Segmentation Technology Market | 2026-2036
Micro Segmentation Technology Market Size, Share, and Industry Trends Forecast 2026-2036
Micro Segmentation Technology Market Analysis
The EU NIS2 Directive is realigning enterprise security procurement across critical infrastructure sectors by mandating granular network controls. Cisco Secure Workload leverages its extensive hardware ecosystem to embed micro segmentation directly into switching fabric. Illumio specializes in host-based enforcement that operates independently of underlying network topology. Akamai Guardicore Segmentation anchors its position through agentless visibility capabilities for unmanaged devices and IoT endpoints.
Micro segmentation technology partitions network environments into discrete, policy-governed zones to restrict lateral threat movement and contain breach propagation. The architecture typically enforces identity-based policies at the workload level using software-defined perimeters rather than traditional VLAN boundaries or subnet segmentation. Cloud-based deployment models are capturing the fastest expansion as organizations migrate security controls to align with distributed infrastructure. Services and platform offerings command superior margin pools compared to standalone hardware, reflecting the shift toward subscription consumption and managed policy orchestration.
The U.S. federal zero-trust architecture mandate from NIST and OMB shapes procurement specifications across government contractors and regulated industries. HIPAA security rule enforcement by HHS intensifies segmentation requirements for healthcare entities protecting electronic protected health information. Stakeholders must evaluate whether their current architectures can satisfy converging demands from cybersecurity insurers, sector regulators, and cloud-native application patterns without proliferating operational complexity.
Market Dynamics
Federal zero-trust mandates are compressing enterprise procurement cycles as security teams re-architect perimeter-less networks around workload identity rather than network location.
Growth Catalysts
- HIPAA Security Rule Enforcement:HHS audits of healthcare entities protecting electronic protected health information are mandating granular segmentation controls across hybrid cloud environments.
- EU NIS2 Directive:Critical infrastructure operators in energy, transport, and digital services must deploy granular network controls by October 2024, accelerating replacement of legacy VLAN architectures.
- Cloud-Native Application Patterns:Kubernetes and containerized workloads are forcing security policies to follow ephemeral infrastructure rather than static network boundaries.
Market Restraints
- Skill Scarcity in Policy Orchestration:Enterprise security teams lack practitioners capable of authoring and maintaining thousands of workload-level identity policies without operational error.
- Integration Tax with Legacy Infrastructure:Brownfield environments running decades-old mainframe and SCADA systems resist agent-based enforcement without costly parallel overlay networks.
- Input Cost Volatility in Cybersecurity Talent:Compensation inflation for zero-trust architects and cloud security engineers is compressing vendor margin structures and elongating deployment timelines.
Strategic Opportunities
- Agentless Visibility for IoT and OT:Unmanaged medical devices, manufacturing sensors, and building automation systems represent addressable endpoints beyond current host-based coverage.
- Convergence of Micro Segmentation and SASE:Unified policy planes spanning on-premises workloads and cloud edge are displacing separate procurement of network security and identity controls.
- India's Digital Personal Data Protection Act:Data localization requirements for critical personal data are creating first-mover advantages for segmentation vendors establishing in-country policy enforcement nodes.
Industry Challenges
- Policy Sprawl and Technical Debt:Thousands of manually authored rules accumulate stale permissions and shadow access paths that breach simulations repeatedly exploit.
- Certification Timeline Compression:FedRAMP and StateRAMP authorization cycles stretch 12-18 months, delaying revenue recognition for vendors targeting U.S. public sector buyers.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Micro Segmentation Technology Market |
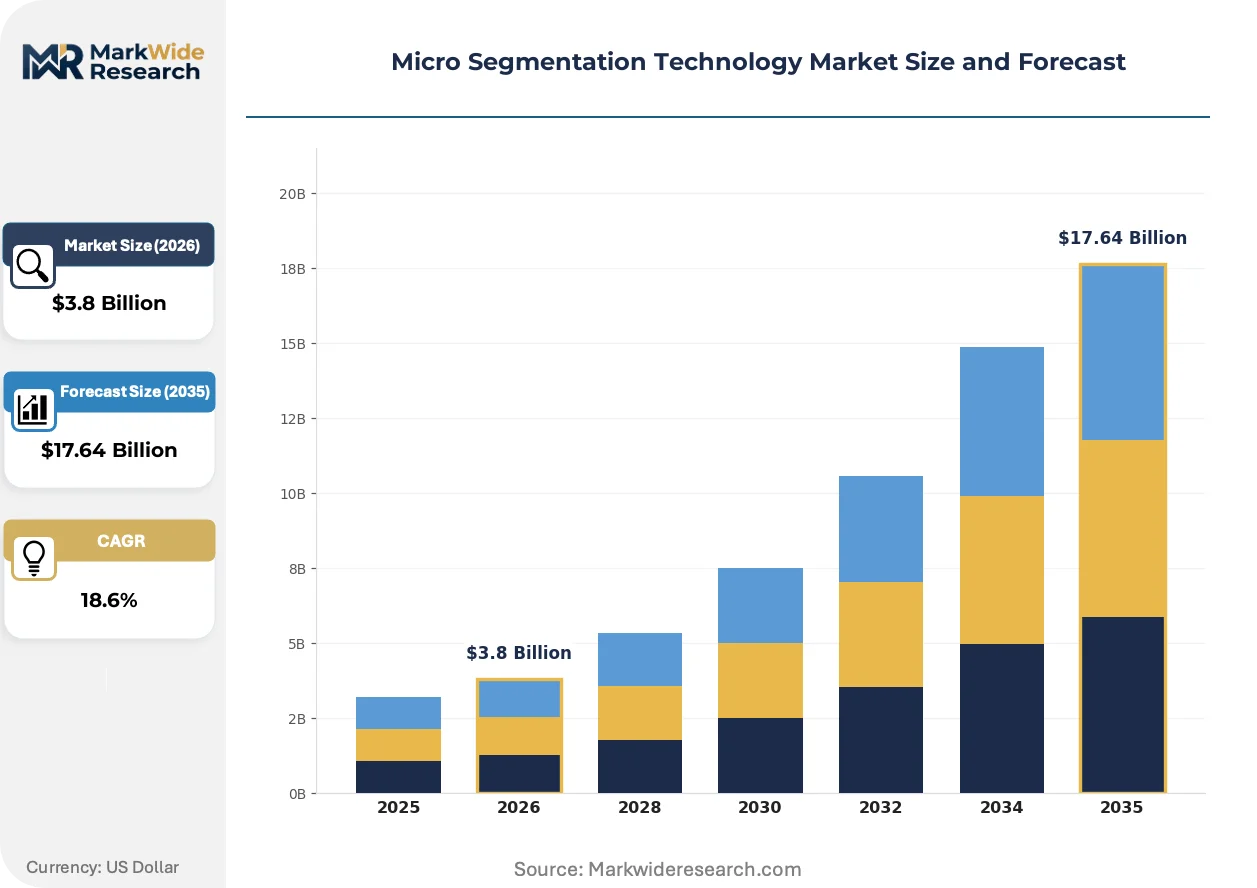
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $17.64 Billion |
| CAGR (2026 – 2036) | 18.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware, Software, Services, Platform Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Industry Vertical: Healthcare, Banking, Retail, Government End User: SMBs, Enterprises, Service Providers, Telecommunication |
| Companies Covered | Cisco Secure Workload, AlgoSec Horizon, Illumio, Nutanix Flow, ColorTokens Xshield, Akamai Guardicore Segmentation, Tufin, Check Point CloudGuard Network Security, VMware NSX, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Micro Segmentation Technology Market Emerging Trajectories
Workload identity is displacing network location as the primary segmentation attribute, forcing architectural bets between host-based agents, network-embedded enforcement, and agentless flow analysis.
Software-defined perimeters built on cryptographic workload identity are electrifying the market by enabling policy enforcement that migrates with containers across multi-cloud footprints. DevSecOps teams at financial services and SaaS providers are deploying these controls during CI/CD pipelines rather than post-production. The shift is compressing sales cycles for vendors offering Kubernetes-native policy APIs and Terraform provider ecosystems.
The EU AI Act's risk-based classification system is mandating granular access controls for high-risk AI systems processing biometric or critical infrastructure data. Providers of AI model training infrastructure must demonstrate technical documentation of segmentation controls to national market surveillance authorities. German and French healthcare AI deployments are prioritizing vendors with pre-certified compliance mappings to reduce regulatory uncertainty.
Buyers are consolidating vendor relationships around platforms integrating micro segmentation with cloud workload protection and identity threat detection. CISOs at U.S. healthcare systems and federal contractors are issuing single procurement vehicles replacing separate point solutions. This concentration favors vendors with broad control plane coverage over specialists requiring integration partnerships for adjacent functions.
Micro Segmentation Technology Market Segmentation
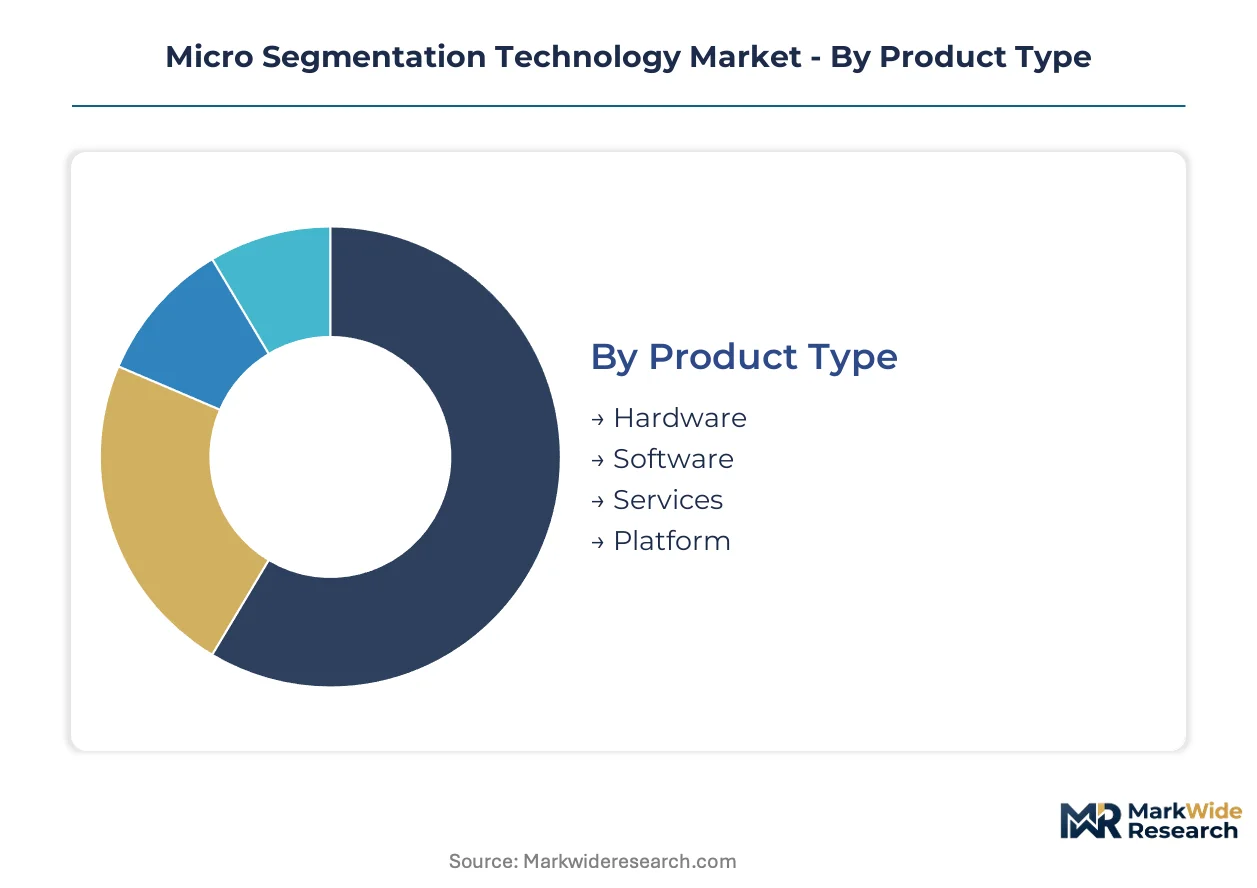
Segmentation granularity determines how vendors align enforcement mechanisms with buyer infrastructure maturity. Product architecture, deployment topology, sector compliance requirements, and organizational scale each create distinct procurement patterns and margin structures.
Product Type:
Supply concentration clusters around software-defined control planes rather than commodity switching hardware.
- Hardware:Dedicated appliances and network-embedded enforcement modules process traffic at line rate without host agent dependencies. Demand concentrates among federal contractors and critical infrastructure operators in the United States facing NIST zero-trust mandates requiring physical segmentation boundaries.
- Software:Host-based agents and hypervisor-integrated modules enforce identity policies at the workload level independent of network topology. Healthcare systems in Germany and France prioritize these deployments for HIPAA and EU AI Act compliance mapping across hybrid cloud environments.
- Services:Managed policy authoring, rule lifecycle governance, and breach simulation testing.
- Platform:Unified control planes integrating segmentation with cloud workload protection and identity threat detection.
Software absorbs the bulk of installed capacity; platform offerings are expanding most quickly.
Deployment Model:
Cost tier stratification separates capital-intensive perpetual licenses from consumption-based subscriptions.
- Cloud-Based:SaaS-delivered policy orchestration with API-native Kubernetes integration follows ephemeral infrastructure across AWS, Azure, and GCP footprints. Financial services firms in Singapore and SaaS providers in Ireland deploy these controls during CI/CD pipelines rather than post-production.
- Hybrid:Synchronized policy enforcement spanning on-premises data centers and multi-cloud edge nodes. Telecommunication operators in Japan and energy utilities in Australia require this architecture for OT-IT convergence without forklift infrastructure replacement.
- On-Premises:Air-gapped control planes for classified and sovereign cloud requirements.
- Managed:Third-party policy administration and continuous rule optimization.
Cloud-based deployments command the steepest expansion trajectory; hybrid configurations retain the largest revenue share.
Industry Vertical:
Application-specific compliance deadlines compress procurement cycles unevenly across sectors.
- Healthcare:Electronic protected health information segmentation across medical devices, EHR systems, and research computing clusters. HHS audit enforcement in the United States and NHS Digital requirements in the United Kingdom mandate granular controls for patient data in hybrid environments.
- Government:FedRAMP-authorized platforms for civilian agencies and defense contractors. The U.S. OMB zero-trust mandate and EU NIS2 Directive for critical infrastructure operators create synchronized procurement waves across NATO-aligned procurement frameworks.
- Banking:PCI-DSS segmentation for cardholder data environments and SWIFT CSP compliance.
- Retail:Point-of-sale isolation and supply chain partner access governance.
Healthcare generates the densest policy rule counts per endpoint; government verticals show the most concentrated vendor consolidation.
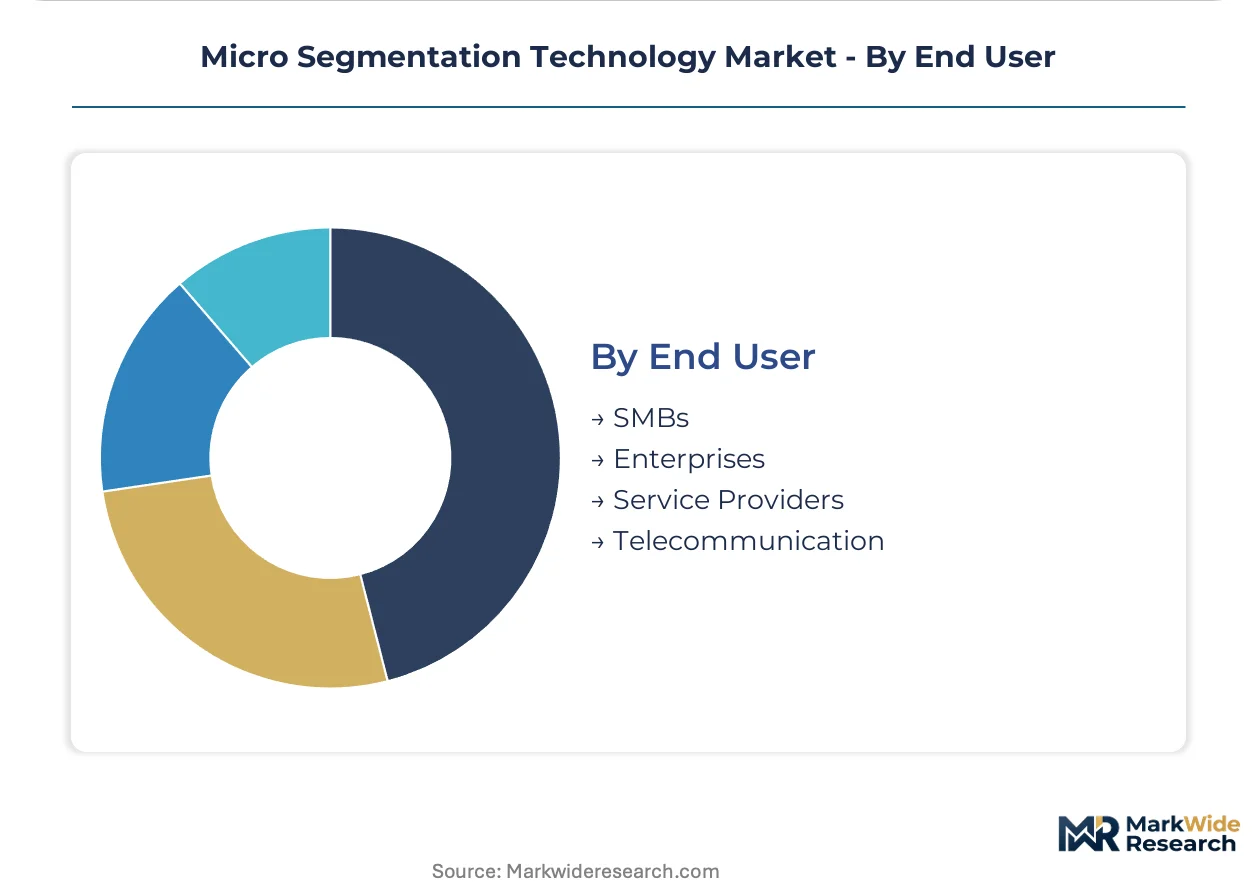
End User:
Customer type determines sales motion complexity and implementation support intensity.
- Enterprises:Global 2000 organizations with multi-site, multi-cloud footprints requiring centralized policy governance. Manufacturing conglomerates in Germany and pharmaceutical multinationals in Switzerland deploy these at scale across thousands of workloads.
- Service Providers:MSSPs and cloud service providers delivering segmentation-as-a-service to downstream clients. Providers in India and Brazil build multi-tenant policy planes supporting India's Digital Personal Data Protection Act localization requirements.
- SMBs:Simplified agentless solutions with pre-built compliance templates.
- Telecommunication:5G network slicing and edge computing security for subscriber isolation.
Enterprises anchor current revenue; service providers are climbing the fastest as consumption models displace direct licensing.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Production of micro segmentation platforms concentrates in the United States and Israel, while consumption spreads across healthcare systems in Germany, financial services in Singapore, and critical infrastructure operators in Australia seeking NIS2-aligned controls.
United States
Federal contractors and civilian agencies drive procurement volume under NIST zero-trust mandates and OMB memoranda. HIPAA enforcement by HHS intensifies segmentation requirements for healthcare entities protecting electronic protected health information. The Washington D.C. corridor and Northern Virginia data center clusters host dense concentrations of FedRAMP-authorized platform development.
Germany
Energy utilities and automotive manufacturers deploy granular controls for OT-IT convergence and industrial AI systems. The EU NIS2 Directive and EU AI Act impose technical documentation requirements for high-risk AI infrastructure segmentation. Munich and Stuttgart engineering clusters prioritize vendors with pre-certified compliance mappings to reduce regulatory uncertainty.
Singapore
Financial services firms and sovereign wealth fund technology units adopt cloud-native segmentation during CI/CD pipelines. The Monetary Authority of Singapore's technology risk management guidelines mandate granular access controls for critical systems. Marina Bay financial district and one-north technology precinct anchor regional platform engineering talent pools.
Australia
Telecommunication operators and energy utilities require hybrid architectures for 5G network slicing and distributed energy resource management. The Security of Critical Infrastructure Act and subsequent amendments impose mandatory segmentation for systems of national significance. Sydney and Melbourne enterprise corridors concentrate procurement decision-making for Asia-Pacific headquarters operations.
India
IT service providers and cloud operators build multi-tenant policy planes for data localization under the Digital Personal Data Protection Act. The Reserve Bank of India's cybersecurity guidelines for payment systems mandate granular network controls. Bengaluru and Hyderabad technology clusters drive domestic platform development and managed security service delivery.
Micro Segmentation Technology Market Vendor Landscape
The competitive structure tilts toward platform-integrated specialists with cloud-native orchestration capabilities. Consolidation pressure intensifies as CISOs issue single procurement vehicles replacing separate point solutions. Three archetypes dominate: network-embedded enforcement vendors, host-based identity policy specialists, and unified control plane platforms. M&A activity targets Kubernetes-native policy APIs, while strategic partnerships focus on managed policy orchestration for mid-market penetration.
Among network-centric platforms, Cisco Secure Workload leverages switching fabric integration, while VMware NSX anchors virtualization-layer enforcement. Illumio and Akamai Guardicore Segmentation exemplify the host-based and agentless visibility archetypes respectively, occupying positions that bypass underlying topology dependencies. These three represent divergent architectural bets on workload identity enforcement.
| Leading Market Players |
|---|
| Cisco Secure Workload |
| AlgoSec Horizon |
| Illumio |
| Nutanix Flow |
| ColorTokens Xshield |
| Akamai Guardicore Segmentation |
| Tufin |
| Check Point CloudGuard Network Security |
| VMware NSX |
| Others |
Supply Flow & Price Mechanics
U.S. federal contractors and healthcare systems concentrate procurement volume under zero-trust mandates, anchoring vendor pricing power to FedRAMP authorization timelines and HIPAA audit enforcement cycles rather than commodity hardware costs.
Pricing Analysis
Margin tightening in cloud-native deployments reflects compensation inflation for zero-trust architects and cloud security engineers compressing vendor structures. Three-tier pricing structure across enterprise, mid-market, and managed service tiers separates workload-scale commitments from per-agent consumption models. Pricing pressure stems from cybersecurity talent scarcity elongating deployment timelines and forcing professional services bundling. Mid-market buyers exhibit highest price sensitivity due to limited internal policy orchestration capabilities.
Supply Chain Analysis
Dual-sourcing requirements for policy orchestration engines mandate qualification of both U.S.-based FedRAMP-authorized platforms and Israeli host-based enforcement specialists. Platform engineering concentrates in the United States, Israel, and India, with Bengaluru and Hyderabad clusters feeding managed security service delivery. Component dependencies span cryptographic workload identity libraries, Kubernetes-native APIs, and Terraform provider ecosystems. Single-source vulnerability in FedRAMP authorization cycles stretches 12-18 months, delaying revenue recognition. Distribution runs through direct enterprise sales, MSSP channel partners, and hyperscaler marketplace integrations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Policy orchestration talent scarcity props vendor pricing power, as enterprise security teams lack practitioners capable of authoring thousands of workload-level identity policies without operational error.
For Market Incumbents: Anchor platform positioning through Kubernetes-native policy APIs and pre-certified compliance mappings to EU AI Act and NIS2 Directive requirements. Deepen backward integration into cloud workload protection and identity threat detection to displace separate point solutions. Defend against specialist vendors requiring integration partnerships by consolidating control plane coverage. For New Entrants and Emerging Players: Launch via agentless visibility capabilities targeting unmanaged medical devices, manufacturing sensors, and building automation systems beyond current host-based coverage. India's Digital Personal Data Protection Act creates first-mover advantages for segmentation vendors establishing in-country policy enforcement nodes. Target MSSP channel partnerships for mid-market penetration with simplified compliance templates. For Investors and Strategic Acquirers: The window for entry favors Kubernetes-native policy API specialists with pre-built Terraform provider ecosystems and CI/CD pipeline integration capabilities. Long-term viability hinges on convergence with SASE architectures and unified policy planes spanning on-premises workloads and cloud edge. Watch for FedRAMP authorization timeline compression as inflection indicator for public sector revenue acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| FedRAMP Authorization Acceleration | Unlocks procurement from U.S. civilian agencies and defense contractors under OMB zero-trust mandates. |
| Kubernetes-Native Policy API Development | Enables DevSecOps teams at financial services and SaaS providers to deploy controls during CI/CD pipelines. |
| Agentless IoT/OT Visibility Expansion | Addresses unmanaged medical devices and manufacturing sensors beyond current host-based enforcement coverage. |
| SASE Convergence Partnership | Displaces separate procurement of network security and identity controls through unified policy planes. |
| India Data Localization Node Establishment | Captures first-mover advantages under Digital Personal Data Protection Act requirements for critical personal data. |
Methodological Framework
SEC filings, hyperscaler capex disclosures, and FedRAMP authorization databases formed the secondary backbone for vendor revenue and deployment trajectory validation. Primary interviews with CISOs at U.S. healthcare systems, federal procurement officers, zero-trust architects, and MSSP operations directors combined with secondary sources through bottom-up and top-down triangulation. Conversations spanned policy orchestration complexity, compliance deadline pressures, and integration cost structures across hybrid cloud environments.
Bottom-up modeling aggregated workload-level deployment volumes by organization size, deployment model, and vertical compliance requirements. Top-down validation cross-referenced aggregate cybersecurity spending shifts and regulatory enforcement budget allocations. Segmentation dimensions spanned product architecture, deployment topology, sector compliance deadlines, and organizational scale. CAGRs were derived from policy rule density trajectories and cloud-native workload expansion patterns across the analysis window.
Regulatory timeline delays, FedRAMP authorization cycle extensions, and cybersecurity talent availability shocks are the dominant revision risks to deployment assumptions. Deviation in U.S. federal zero-trust mandate enforcement intensity would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Germany Endpoint Detection and Response Market
Cybersecurity
Global Distributed Denial of Service (Ddos) Protection Market
Cybersecurity
ASEAN Cyber Security Market
Cybersecurity
Global SSH Terminal Market
Cybersecurity
Japan Cybersecurity Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
Greece Cybersecurity Market
Cybersecurity
Africa Cybersecurity Market
Cybersecurity
Global Managed Detection and Response (MDR) Market
Cybersecurity
Network Detection and Response Market
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
Nordics Cybersecurity Market
Cybersecurity
Deception Technology Market
Cybersecurity
Cognitive Security Market
Cybersecurity
North America Software Defined Perimeter Market
Cybersecurity
Data-Centric Security Market