
 Mainframe Security Market | 2026-2036
Mainframe Security Market Size, Share, and Industry Trends Forecast 2026-2036
Mainframe Security Market Outlook
North American mainframe security vendors is realigning around hybrid cloud integration demands as enterprises modernize without abandoning core systems. IBM Corporation leverages its zSystems platform dominance to anchor enterprise-grade encryption capabilities across financial and government installations. Broadcom sustains competitive pressure through specialized mainframe software licensing and security module consolidation. BMC Software differentiates via automated compliance workflows that reduce manual audit burdens for regulated industries.
Mainframe security encompasses hardware, software, and procedural controls protecting IBM zSystems and compatible enterprise servers from unauthorized access, data exfiltration, and operational disruption. Solutions typically employ RACF or equivalent access control matrices, hardware security module-backed encryption at 256-bit AES standards, and real-time SMF log monitoring to enforce least-privilege principles across multi-tenant workloads. Encryption technology commands the deepest margin pools as quantum-resistant algorithm migration drives replacement cycles. Cloud-based deployment represents the fastest-expanding configuration as banks adopt hybrid architectures linking on-premises z/OS instances with AWS and Azure key management services. Managed services within the solution category is maturing rapidly as skills scarcity pushes institutions toward outsourced security operations centers.
FDA data integrity guidelines, NIST zero-trust architecture mandates, and the EU Digital Operational Resilience Act collectively reshape procurement specifications for regulated mainframe operators. NIST SP 800-207 compliance requirements are forcing institutions to replace legacy perimeter-based access models with continuous verification frameworks. Stakeholders must monitor quantum computing timelines to time cryptographic refresh investments before harvest-now-decrypt-later threats materialize against long-duration financial records.
Market Dynamics
Quantum-resistant cryptography migration is forcing accelerated replacement cycles across financial and government mainframe estates, compressing decade-long refresh timelines into three-to-five-year windows as harvest-now-decrypt-later threats intensify.
Growth Catalysts
- NIST SP 800-207 zero-trust mandates:US federal agencies must replace perimeter-based access models with continuous verification frameworks, driving hardware and software procurement across civilian and defense installations.
- EU Digital Operational Resilience Act:European financial institutions face binding operational resilience testing requirements, expanding spending on real-time monitoring and automated compliance tooling.
- Hybrid cloud workload expansion:Banks are linking on-premises z/OS instances with AWS and Azure key management services, creating demand for cross-platform encryption orchestration.
Market Restraints
- Specialized skills scarcity:Deep expertise in RACF, ACF2, and Top Secret administration concentrates among aging practitioner cohorts, inflating labor costs and constraining implementation velocity.
- IBM zSystems hardware dependency:Proprietary processor architectures and licensed internal code create vendor lock-in, limiting price competition and architectural flexibility for security module procurement.
- Regulatory fragmentation:Divergent national cryptographic approval regimes, including France's ANSSI and Germany's BSI certification requirements, complicate product standardization across European deployments.
Strategic Opportunities
- Managed security services white space:Skills scarcity pushes institutions toward outsourced security operations centers, creating recurring revenue pools for specialized mainframe security providers.
- Post-quantum algorithm standardization:NIST's finalization of quantum-resistant encryption standards enables vendors to certify next-generation hardware security modules ahead of compliance deadlines.
- India's financial modernization:RBI-mandated digital payment infrastructure expansion and core banking system upgrades generate demand for mainframe-grade access control and audit capabilities.
Industry Challenges
- SMF log analysis expertise gap:Real-time security event correlation from System Management Facility records requires scarce z/OS systems programming skills that universities no longer produce.
- Multi-tenant isolation complexity:Containerized workloads on z/OS require re-engineered access control matrices that preserve least-privilege principles across shared logical partitions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Mainframe Security Market |
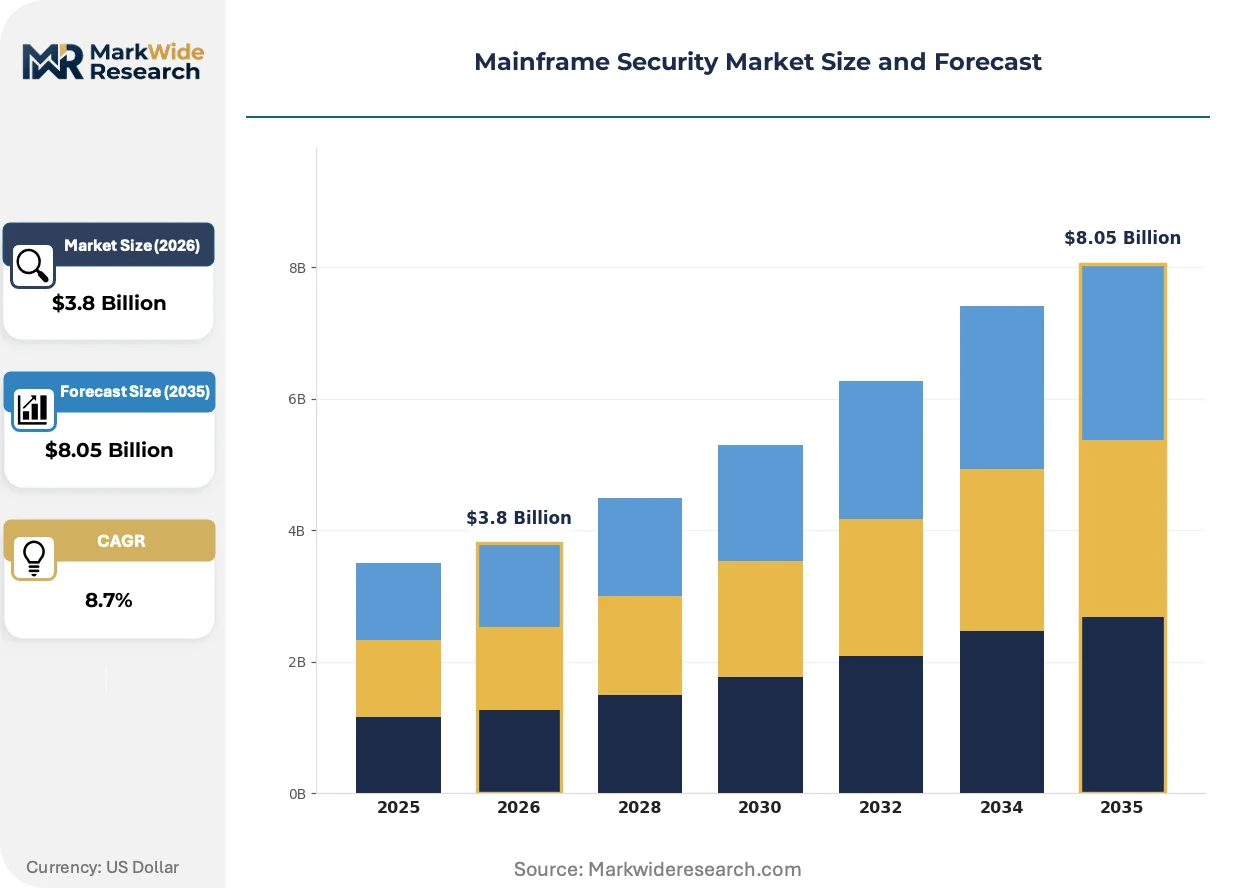
| Market Size in 2026 | $3.8 Billion |
| Market Size in 2035 | $8.05 Billion |
| CAGR (2026 – 2036) | 8.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technology: Encryption, Access Control, Intrusion Detection, Data Masking End User: Banking Sector, Government, Telecommunications, Healthcare Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution: Compliance Management, Threat Intelligence, Security Information, Risk Assessments |
| Companies Covered | IBM Corporation, BMC Software, DXC Technology Company, CA Technologies, McAfee, NEC Corporation, HCL Technologies, Broadcom, Compuware Corporation, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Mainframe Security Market Strategic Shifts
Homomorphic encryption capabilities are advancing from experimental to production-grade, enabling computation on encrypted data without decryption and eliminating exposure windows that traditional models require.
Lattice-based cryptographic algorithms are rewriting the competitive landscape for hardware security module vendors. NIST's selected post-quantum standards are accelerating bank procurement of crypto-agile mainframe adapters. IBM and Thales are certifying quantum-resistant firmware before regulatory mandates harden.
The EU Digital Operational Resilience Act imposes mandatory threat-led penetration testing on critical financial infrastructure. Institutions must demonstrate recovery capabilities within strict timeframes. German and French banks are prioritizing automated failover and immutable backup validation to satisfy national supervisors.
Subscription-based security software licensing is displacing perpetual entitlement models across North American banking procurement. CIOs prefer operational expenditure treatment for encryption and monitoring tools. Canadian and US regional banks are consolidating vendor relationships to simplify license management and audit preparation.
Mainframe Security Market Segmentation
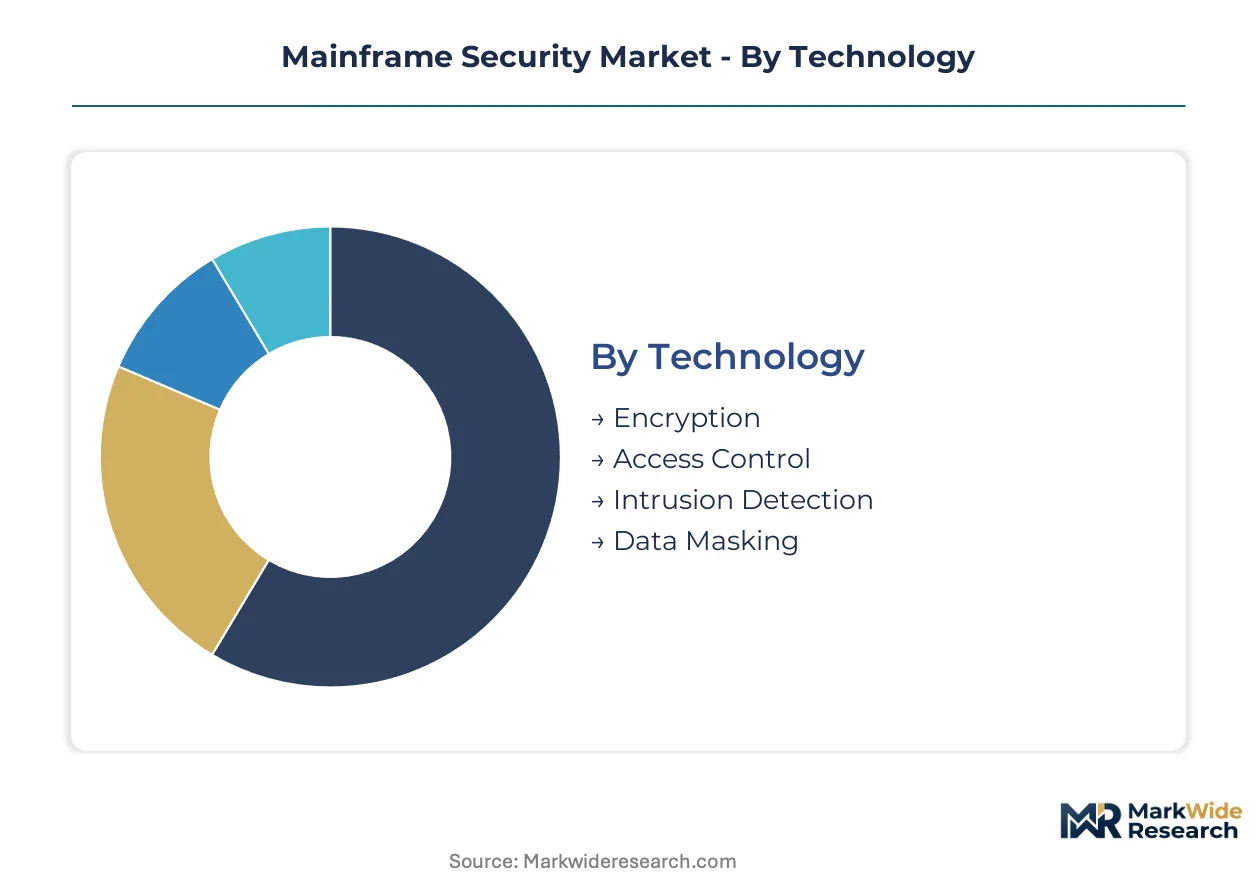
Mainframe security procurement patterns diverge sharply across technology maturity, operational models, and regulatory exposure. Each segmentation axis reveals distinct margin structures and implementation timelines that vendors must navigate.
Technology:
Standardization dominates encryption and access control, while intrusion detection and data masking retain customization flexibility for specialized workloads.
- Encryption:Hardware security module-backed implementations at 256-bit AES standards anchor financial and government installations. Demand concentrates in the United States as federal agencies modernize legacy systems under zero-trust architecture directives, with quantum-resistant algorithm migration compressing refresh timelines.
- Access Control:RACF, ACF2, and Top Secret matrices enforce least-privilege principles across multi-tenant z/OS workloads. Banking institutions across North America are expanding procurement amid stricter data protection mandates, though specialized skills scarcity inflates implementation costs.
- Intrusion Detection:Real-time SMF log monitoring correlates security events from System Management Facility records. The European Banking Authority's digital operational resilience framework is accelerating compliance spending among financial institutions for automated threat detection.
- Data Masking:Dynamic obfuscation protects sensitive fields in non-production environments. Homomorphic encryption capabilities are advancing from experimental to production-grade, enabling computation on encrypted data without decryption.
Most installed capacity flows through Encryption. Expansion is steepest in Intrusion Detection as real-time monitoring mandates proliferate.
End User:
Regulatory intensity creates four distinct demand profiles, with banking and government commanding premium pricing for certified solutions.
- Banking Sector:Core banking systems and payment infrastructure require immutable audit trails and cross-border transaction encryption. RBI-mandated digital payment expansion in India generates demand for mainframe-grade access control capabilities.
- Government:Civilian and defense installations face NIST SP 800-207 compliance deadlines for continuous verification frameworks. Procurement specifications prioritize hardware security modules with post-quantum cryptographic agility.
- Telecommunications:Subscriber databases and billing systems demand high-throughput encryption with minimal latency overhead. Containerized workloads on z/OS require re-engineered access control matrices for shared logical partitions.
- Healthcare:FDA data integrity guidelines reshape procurement for regulated mainframe operators handling longitudinal patient records. HIPAA compliance drives investment in automated compliance workflows that reduce manual audit burdens.
Banking Sector absorbs the deepest investment pools. Government procurement is climbing the fastest as zero-trust mandates harden.
Deployment:
Cost tier stratification separates capital-intensive on-premises installations from operational expenditure-favored cloud and managed alternatives.
- On-Premises:Traditional z/OS security stacks with dedicated hardware security modules and licensed internal code. IBM zSystems hardware dependency creates vendor lock-in, limiting architectural flexibility for security module procurement.
- Cloud-Based:AWS and Azure key management services linked to on-premises z/OS instances enable hybrid encryption orchestration. Skills scarcity pushes institutions toward outsourced key lifecycle management.
- Hybrid:Split workloads across mainframe logical partitions and cloud-native security services. Canadian and US regional banks are consolidating vendor relationships to simplify license management and audit preparation.
- Managed Services:Outsourced security operations centers address RACF, ACF2, and Top Secret administration expertise gaps. Subscription-based licensing is displacing perpetual entitlement models across North American banking procurement.
On-Premises retains the largest installed base. Managed Services is gaining share fastest as practitioner cohorts age out of the workforce.
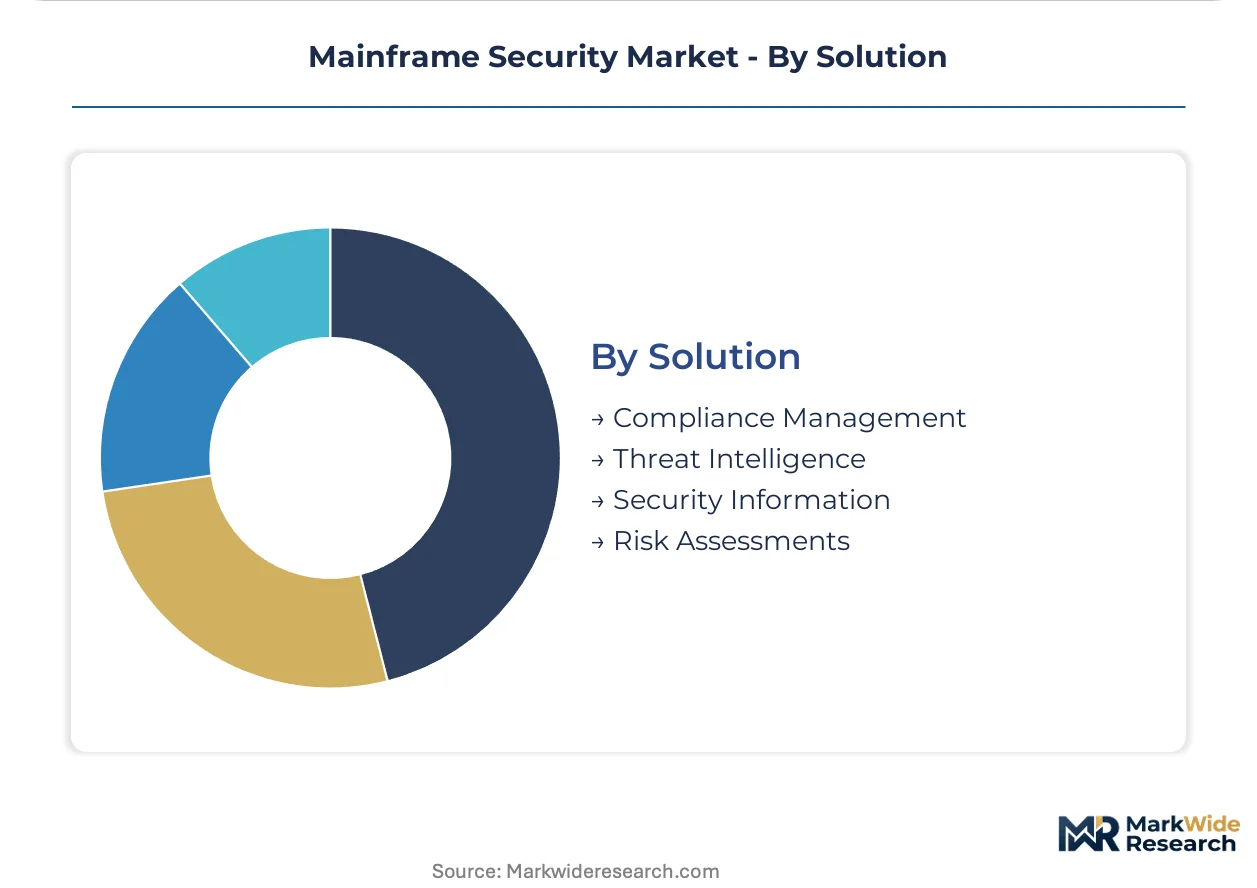
Solution:
Maturity levels vary from commoditized risk assessments to emerging threat intelligence platforms with predictive capabilities.
- Compliance Management:Automated audit preparation and regulatory reporting for GDPR, HIPAA, and sector-specific mandates. German and French banks are prioritizing automated failover and immutable backup validation to satisfy national supervisors.
- Threat Intelligence:Predictive analytics and adversary pattern recognition integrated with SIEM workflows. EU Digital Operational Resilience Act mandates threat-led penetration testing on critical financial infrastructure.
- Security Information:Centralized logging and event correlation from distributed mainframe estates. Real-time SMF log analysis expertise gaps constrain implementation velocity for complex multi-system environments.
- Risk Assessments:Periodic vulnerability scanning and control effectiveness measurement. Divergent national cryptographic approval regimes complicate product standardization across European deployments.
Compliance Management processes the highest transaction volumes. Threat Intelligence shows the steepest expansion trajectory as predictive capabilities mature.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory arbitrage is reshaping procurement patterns as financial institutions migrate security operations toward jurisdictions with harmonized compliance frameworks and lower certification costs. The United States and Germany currently anchor premium-tier spending, while India and Singapore emerge as alternative delivery hubs for managed security services.
United States
Federal agencies are modernizing legacy systems under NIST SP 800-207 zero-trust mandates, compressing refresh timelines for continuous verification frameworks. The FDA data integrity guidelines impose additional procurement specifications on healthcare mainframe operators. New York and Chicago financial centers dominate demand concentration, with regional banks consolidating vendor relationships to simplify audit preparation.
Germany
The BSI national cryptographic approval regime and EU Digital Operational Resilience Act drive compliance spending among financial institutions. Automated failover and immutable backup validation are prioritized to satisfy BaFin supervisory requirements. Frankfurt's banking cluster leads procurement volume, while Munich technology centers specialize in hardware security module integration.
India
RBI-mandated digital payment infrastructure expansion generates demand for mainframe-grade access control capabilities across core banking upgrades. The country's national financial regulator has tightened operational resilience testing standards for systemically important institutions. Mumbai and Bangalore technology corridors concentrate implementation activity, with Hyderabad emerging as a managed security services delivery hub.
United Kingdom
FCA operational resilience requirements and post-Brexit regulatory divergence are forcing institutions to reassess cross-border data protection architectures. The Bank of England's stress testing mandates accelerate spending on real-time monitoring tooling. London's financial district absorbs the deepest investment pools, while Edinburgh and Manchester regional banking centers expand procurement for compliance automation.
Japan
METI cybersecurity framework updates and Financial Services Agency guidelines are tightening mainframe security specifications for banking and insurance sectors. The country's aging practitioner cohort is accelerating managed services adoption. Tokyo's financial district dominates enterprise procurement, with Osaka regional banks piloting hybrid cloud encryption orchestration linking z/OS instances with domestic cloud providers.
Mainframe Security Market Competitive Environment
United States producers anchor the premium software tier; European specialists hold certification-intensive hardware security module segments. The vendor base concentrates around three structural positions: platform-anchored incumbents with proprietary processor architectures, independent software vendors with automated compliance workflows, and managed services providers addressing skills scarcity. Consolidation pressure intensifies through strategic partnerships for hybrid cloud integration and technology licensing for post-quantum cryptographic agility.
Within the platform-dominant tier, IBM Corporation exemplifies the vertically integrated archetype through zSystems hardware and software bundling. BMC Software and Broadcom occupy positions as independent software specialists with consolidated security module portfolios. DXC Technology Company represents the managed services vector, addressing RACF and ACF2 administration expertise gaps through outsourced security operations centers.
| Leading Market Players |
|---|
| IBM Corporation |
| BMC Software |
| DXC Technology Company |
| CA Technologies |
| McAfee |
| NEC Corporation |
| HCL Technologies |
| Broadcom |
| Compuware Corporation |
| Others |
Value Chain & Pricing Dynamics
Post-quantum cryptographic algorithm standardization is compressing refresh timelines and simultaneously concentrating procurement power among certified hardware security module vendors while fragmenting software licensing economics across subscription and perpetual models.
Pricing Analysis
Direct-to-OEM discount structures dominate encryption hardware procurement, with three-tier pricing stratification across FIPS 140-2 Level 4 certified modules, standard enterprise-grade implementations, and economy-tier software-only solutions. Price differentiation rests on certification grade and after-sales service bundling, with government buyers absorbing premium tiers and regional banks exhibiting acute price sensitivity. Cost compression in software licensing is intensifying because subscription models displace perpetual entitlements, eroding upfront revenue recognition for independent software vendors.
Supply Chain Analysis
Reverse-logistics flows for hardware security module refurbishment and firmware upgrade cycles create secondary supply channels extending product lifecycles. Manufacturing concentrates in the United States, Germany, and Taiwan, with specialized semiconductor fabrication for cryptographic processors drawing from silicon wafers, tamper-resistant packaging substrates, and quantum-resistant algorithm IP. Single-source vulnerability around IBM zSystems proprietary architectures constrains vendor diversification. Distribution runs through direct enterprise sales teams and specialized systems integrators serving financial and government verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion opportunities concentrate in managed security services and post-quantum certification tiers, justified by skills scarcity inflating labor arbitrage premiums and compliance mandates forcing cryptographic refresh investments.
For Market Incumbents: Anticipate quantum-resistant algorithm migration compressing replacement cycles and defend installed base positions through backward integration into firmware certification pipelines. Prioritize automated compliance workflow investments to reduce customer audit burdens and anchor recurring revenue streams against emerging cloud-native competitors. For New Entrants and Emerging Players: Begin with managed security services white space in India and Southeast Asia, where RBI-mandated digital payment expansion outpaces local RACF and ACF2 expertise availability. Target mid-tier regional banks with hybrid cloud encryption orchestration offerings that bridge on-premises z/OS instances with AWS and Azure key management services. For Investors and Strategic Acquirers: Valuations sit cheapest among independent software vendors with automated compliance workflows and concentrated government contracting relationships. Long-term viability over the coming decade hinges on cryptographic agility and cross-platform integration capabilities. Monitor NIST post-quantum standard finalization timelines as inflection indicators for hardware security module replacement demand acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptographic Certification | NIST standard finalization enables vendors to certify quantum-resistant firmware ahead of compliance deadlines. |
| Managed Security Services Expansion | Skills scarcity pushes institutions toward outsourced security operations centers for RACF and ACF2 administration. |
| Hybrid Cloud Integration Partnerships | AWS and Azure key management service linkages create demand for cross-platform encryption orchestration capabilities. |
| Automated Compliance Workflow Development | EU Digital Operational Resilience Act mandates expand spending on real-time monitoring and audit automation tooling. |
| India Market Entry and Localization | RBI-mandated digital payment infrastructure generates demand for mainframe-grade access control and audit capabilities. |
Study Parameters
Bottom-up financial institution procurement modeling reconciled against top-down vendor shipment tracking forms the analytical core of this study. Primary interviews with z/OS systems programmers, CISOs at Tier 1 banks, government cybersecurity procurement officers, and managed security services operators combined with secondary validation from NIST publications, FDA data integrity guidelines, EU Digital Operational Resilience Act regulatory texts, and SEC 10-K filings from disclosed mainframe security vendors. Triangulation across these sources ensures demand-side and supply-side estimates converge.
Input-output matrices map encryption technology adoption rates, access control deployment patterns, and managed services penetration across banking, government, telecommunications, and healthcare verticals throughout the forecast period. Segmentation dimensions include technology type, end-user industry, deployment model, and solution category. CAGRs derive from regression analysis against regulatory mandate timelines and cryptographic refresh cycle compression indicators, with quantum computing threat assessments and zero-trust architecture adoption curves serving as industry-specific forecast inputs.
Several conditions sit outside the modeled scope, including hypothetical breakthroughs in cryptanalysis accelerating harvest-now-decrypt-later threats, abrupt shifts in IBM zSystems licensing economics, and geopolitical disruptions to semiconductor supply chains. Practitioners should monitor NIST post-quantum algorithm standardization announcements, EU supervisory enforcement patterns under DORA, and Indian banking regulator technology mandates for early signals warranting forecast revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Europe Digital Forensics Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Indonesia Cybersecurity Market
Cybersecurity
Data Center Security Market
Cybersecurity
Digital Security Market
Cybersecurity
Europe SOC As a Service Market
Cybersecurity
Global Breach and Attack Simulation Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Application Programming Interface Security Market
Cybersecurity
Australia Cybersecurity Market
Cybersecurity
Homomorphic Encryption Market
Cybersecurity
Japan Ransomware Protection Market
Cybersecurity
Global Virtualization Security Market