
 Global Security and Vulnerability Management Market | 2026-2036
Global Security and Vulnerability Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Security and Vulnerability Management Market Foresight
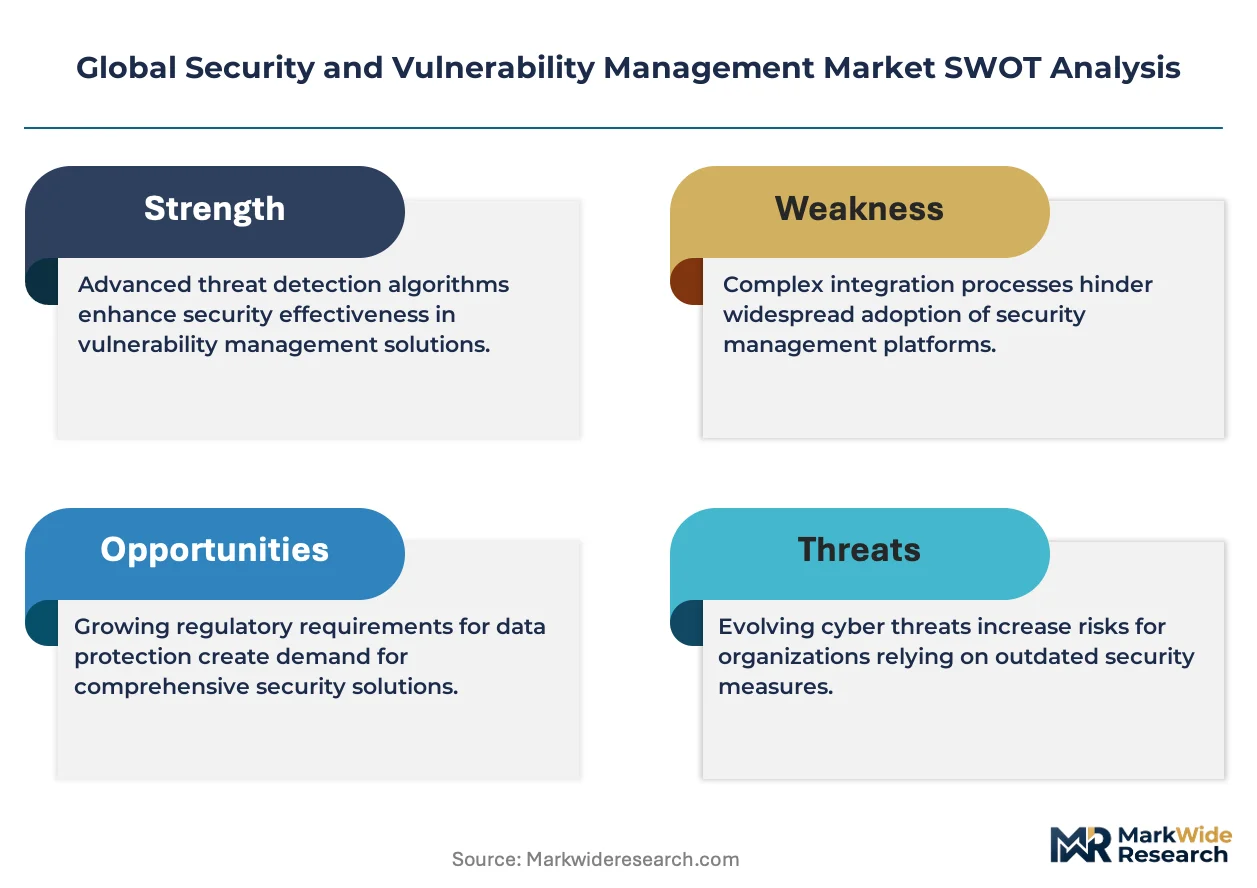
Enterprise-grade vulnerability assessment is unwinding legacy security postures across Fortune 500 environments. Tenable, Inc. leverages continuous exposure management to anchor high-assurance contracts with federal buyers. Qualys, Inc. dominates cloud-based vulnerability scanning through its integrated platform architecture. IBM Corporation sustains mainframe-adjacent security services that extend deep into regulated verticals.
Security and vulnerability management encompasses systematic identification, classification, remediation, and reporting of security weaknesses across IT infrastructure, typically operating through automated scanning engines that detect misconfigurations, missing patches, and exploitable code paths at network throughput rates exceeding 10 Gbps. The discipline serves primary commercial purpose by quantifying attack surface exposure and prioritizing remediation workflows based on exploitability scoring. Cloud-based deployment models are capturing the fastest expansion as organizations abandon capital-intensive on-premises scanner farms. Threat intelligence segments command premium pricing due to real-time indicator feed integration and adversary-tracking capabilities. Endpoint security applications within the broader application category concentrate vendor R&D spending because remote work architectures have fragmented traditional network perimeters.
The U.S. Securities and Exchange Commission mandates timely disclosure of material cybersecurity incidents, compelling publicly traded firms to maintain continuous vulnerability monitoring capabilities. The European Union Agency for Cybersecurity enforces NIS2 harmonized requirements that expand regulated entity coverage to critical supply chain intermediaries. Japan's Ministry of Economy, Trade and Industry publishes baseline guidelines that shape procurement specifications for domestic critical infrastructure operators. Stakeholders must evaluate whether their current scanning cadences satisfy emerging cross-border data residency requirements before regulator deadlines harden.
Market Dynamics
Continuous exposure management platforms are compressing vulnerability remediation cycles from weeks to hours, forcing security vendors to abandon point-in-time scanning architectures in favor of real-time telemetry feeds that correlate asset inventory with active threat intelligence.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Publicly traded firms in the United States must now report material breaches within four business days, mandating automated vulnerability detection pipelines that feed directly into incident response workflows.
- Cloud Migration Velocity:Enterprise IT estates are shifting from on-premises data centers to multi-cloud configurations, creating attack surfaces that traditional perimeter scanners cannot map without API-native discovery tools.
- Critical Infrastructure Designation Expansion:Japan's METI guidelines now classify semiconductor supply chains and satellite operators as critical infrastructure, extending vulnerability management procurement mandates to previously unregulated sectors.
Market Restraints
- Specialized Talent Scarcity:Organizations face acute shortages of security engineers capable of interpreting CVSS 4.0 scoring outputs and configuring exposure management platforms, inflating implementation timelines.
- Scanner Proliferation Costs:Large enterprises operate overlapping vulnerability tools from distinct procurement silos, generating redundant license expenditures and conflicting remediation priorities that stall security programs.
- Encryption Blind Spots:East-west traffic inspection remains technically constrained in TLS 1.3 environments, leaving lateral movement paths undetected by network-based scanning engines.
Strategic Opportunities
- OT/ICS Convergence:Manufacturing and energy operators are bridging information technology and operational technology networks, opening demand for passive scanning solutions that discover industrial controllers without disrupting production processes.
- Attack Surface Management Adjacencies:External attack surface monitoring services that map internet-exposed assets are attracting venture investment, creating acquisition targets for vulnerability platform vendors seeking to expand beyond internal scanning.
- EU NIS2 Implementation Lag:Member states are still transposing the directive into national law, creating a temporary window for vendors to establish compliant service templates before enforcement deadlines crystallize.
Industry Challenges
- Alert Fatigue and Prioritization Failure:Security teams receive thousands of vulnerability notifications monthly, overwhelming ticketing systems and causing high-severity findings to languish unpatched for months.
- Legacy Asset Integration:Mainframe and AS/400 systems in financial services lack modern APIs, requiring custom connector development that extends deployment timelines and fragments platform coverage.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Security and Vulnerability Management Market |
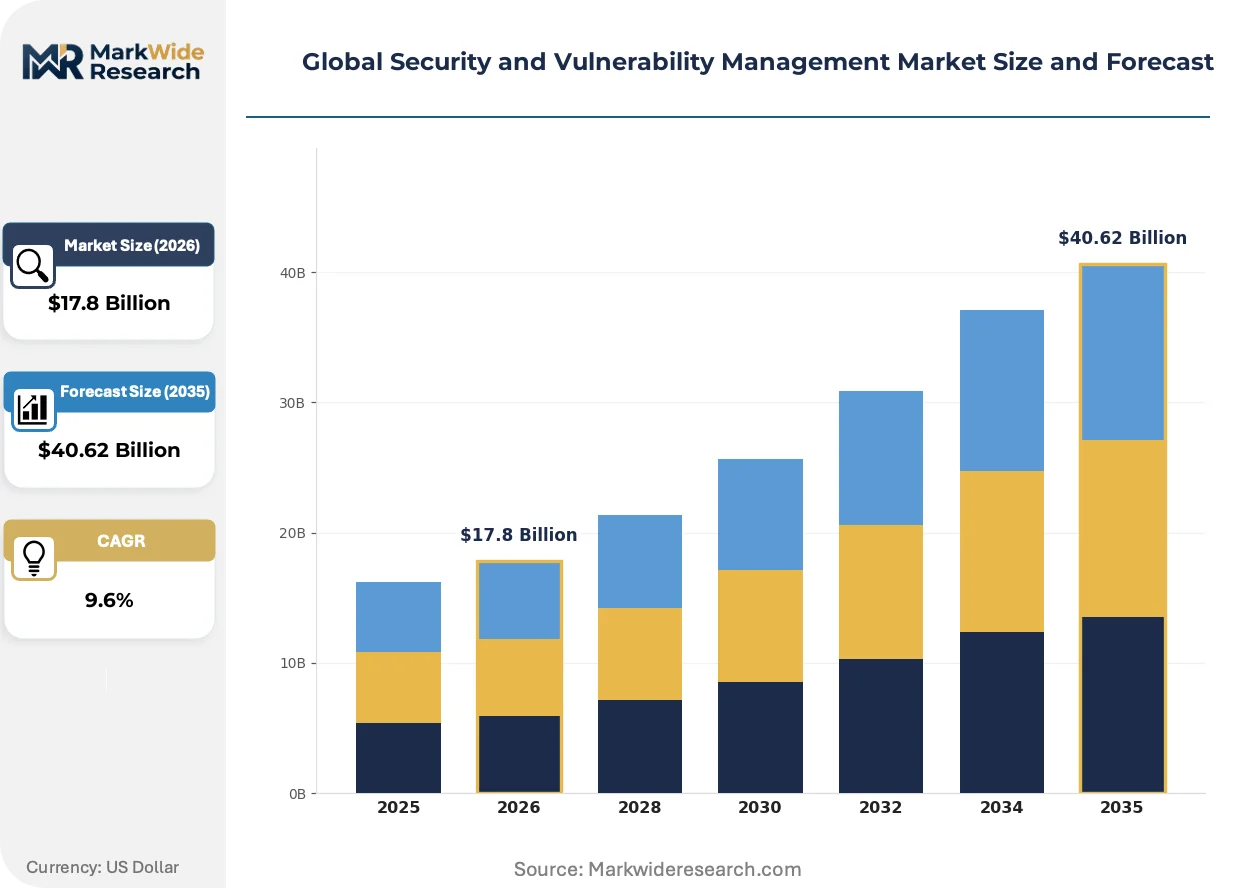
| Market Size in 2026 | $17.8 Billion |
| Market Size in 2035 | $40.62 Billion |
| CAGR (2026 – 2036) | 9.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Vulnerability Assessment, Threat Intelligence, Risk Management, Compliance Management, Incident Response Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Services Application: Endpoint Security, Network Security, Application Security, Data Protection, Identity & Access Management End User: Financial Institutions, IT & Telecom Firms, Government Agencies, Manufacturing Corporations |
| Companies Covered | Tenable, Inc., Qualys, Inc., IBM Corporation, Microsoft, Rapid7, Cisco Systems, Inc., CrowdStrike, Broadcom Inc., Fortra, LLC, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Security and Vulnerability Management Market Shifts & Advancements
Agentless scanning architectures are gaining traction as organizations seek to reduce endpoint performance overhead, while adversary simulation capabilities are merging with vulnerability data to produce risk scores weighted by actual exploitability rather than theoretical severity.
Exposure management platforms that aggregate vulnerability findings with cloud security posture management and identity risk data are supplanting standalone scanning tools in enterprise procurement cycles. Fortune 500 CISOs are consolidating vendor relationships around these unified control planes, compressing procurement decisions from twelve-month evaluation periods to ninety-day pilots. The structural consequence is margin pressure on point-solution vendors lacking adjacent capability integration.
The EU AI Act's risk classification framework for high-stakes AI systems is mandating security-by-design documentation that includes vulnerability assessment protocols throughout the machine learning lifecycle. AI service providers must now demonstrate continuous monitoring of training pipelines and model serving infrastructure, extending vulnerability management scope into data science operations. German automotive manufacturers and French healthcare AI developers are deploying specialized scanning tools for ML model repositories and containerized inference endpoints.
Consolidated security procurement is displacing best-of-breed tool selection as CFOs impose vendor rationalization mandates. Mid-market enterprises are abandoning dedicated vulnerability scanners in favor of bundled endpoint detection and response suites that include basic assessment functionality. This compression is most visible in the United Kingdom and Australia, where private equity-owned portfolio companies are standardizing on Microsoft Defender Vulnerability Management to reduce software spend.
Global Security and Vulnerability Management Market Segmentation
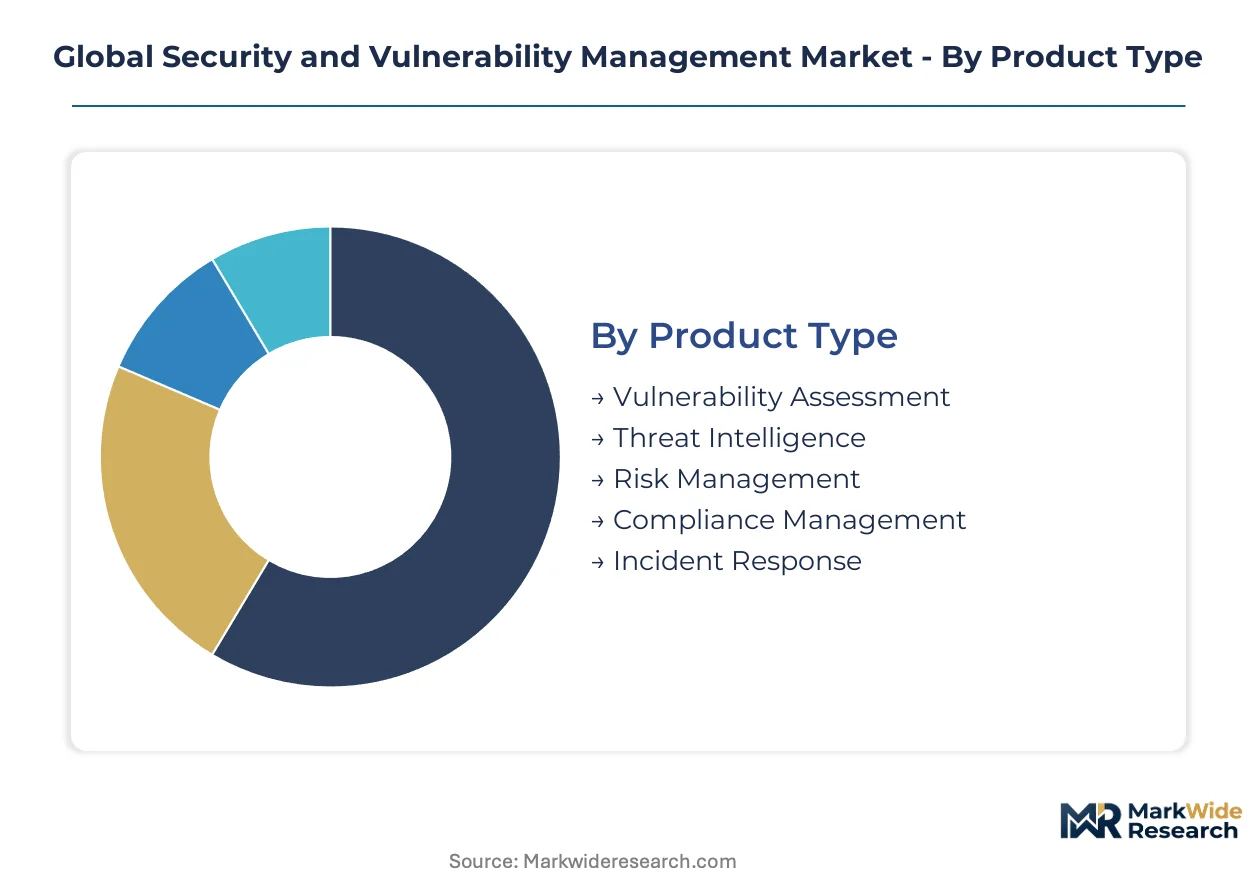
Segmentation reveals how vulnerability management vendors must architect platform capabilities around distinct operational contexts. Procurement patterns diverge sharply between cloud-native enterprises maintaining ephemeral infrastructure and regulated entities preserving legacy control frameworks.
Product Type:
Substitution pressure concentrates in compliance management tools as integrated governance-risk-compliance platforms absorb standalone vulnerability reporting functions.
- Vulnerability Assessment:Automated scanning engines detect misconfigurations, missing patches, and exploitable code paths at network throughput rates exceeding 10 Gbps. Financial institutions in the United States anchor demand as SEC disclosure rules mandate continuous monitoring pipelines feeding directly into incident response workflows.
- Threat Intelligence:Real-time indicator feed integration and adversary-tracking capabilities command premium pricing due to exploit prediction accuracy. Germany's automotive sector drives adoption as EU NIS2 implementation expands regulated entity coverage to critical supply chain intermediaries.
- Risk Management:Quantifies attack surface exposure through business-impact scoring models.
- Compliance Management:Generates audit-ready documentation mapping vulnerabilities to regulatory control frameworks.
- Incident Response:Orchestrates remediation workflows with automated ticketing and patch deployment.
Vulnerability assessment retains volume leadership; threat intelligence holds the steepest expansion curve.
Deployment Model:
Cost tier stratification separates capital-intensive on-premises scanner farms from operational-expense cloud subscriptions favored by mid-market enterprises.
- Cloud-Based:API-native discovery tools map multi-cloud attack surfaces without perimeter scanner deployment. Japan's semiconductor manufacturers accelerate migration as METI guidelines classify supply chains as critical infrastructure requiring scalable monitoring.
- On-Premises:Air-gapped scanning architectures serve classified government networks and financial core banking systems. German federal agencies sustain demand despite cloud migration trends elsewhere in Europe.
- Hybrid:Correlates cloud asset inventory with on-premises legacy system coverage.
- Managed Services:Outsourced vulnerability operations address specialized talent scarcity in mid-market enterprises.
Cloud-based deployment captures the fastest volume gains; managed services climb fastest among regulated verticals unable to hire security engineers.
Application:
Volume concentration tracks endpoint fragmentation as remote work architectures dissolve traditional network perimeters.
- Endpoint Security:Agentless scanning architectures reduce performance overhead on distributed devices. IT and telecom firms across the United States dominate procurement as bring-your-own-device policies proliferate.
- Network Security:East-west traffic inspection faces technical constraints in TLS 1.3 environments. Japanese critical infrastructure operators invest heavily despite encryption blind spots limiting lateral movement detection.
- Application Security:Scans containerized inference endpoints and ML model repositories for the EU AI Act's security-by-design documentation.
- Data Protection:Maps vulnerabilities in data residency configurations for cross-border compliance.
- Identity & Access Management:Correlates credential exposure with vulnerability findings in unified risk scoring.
Endpoint security retains volume leadership; application security gains share fastest from AI system risk classification mandates.
End User:
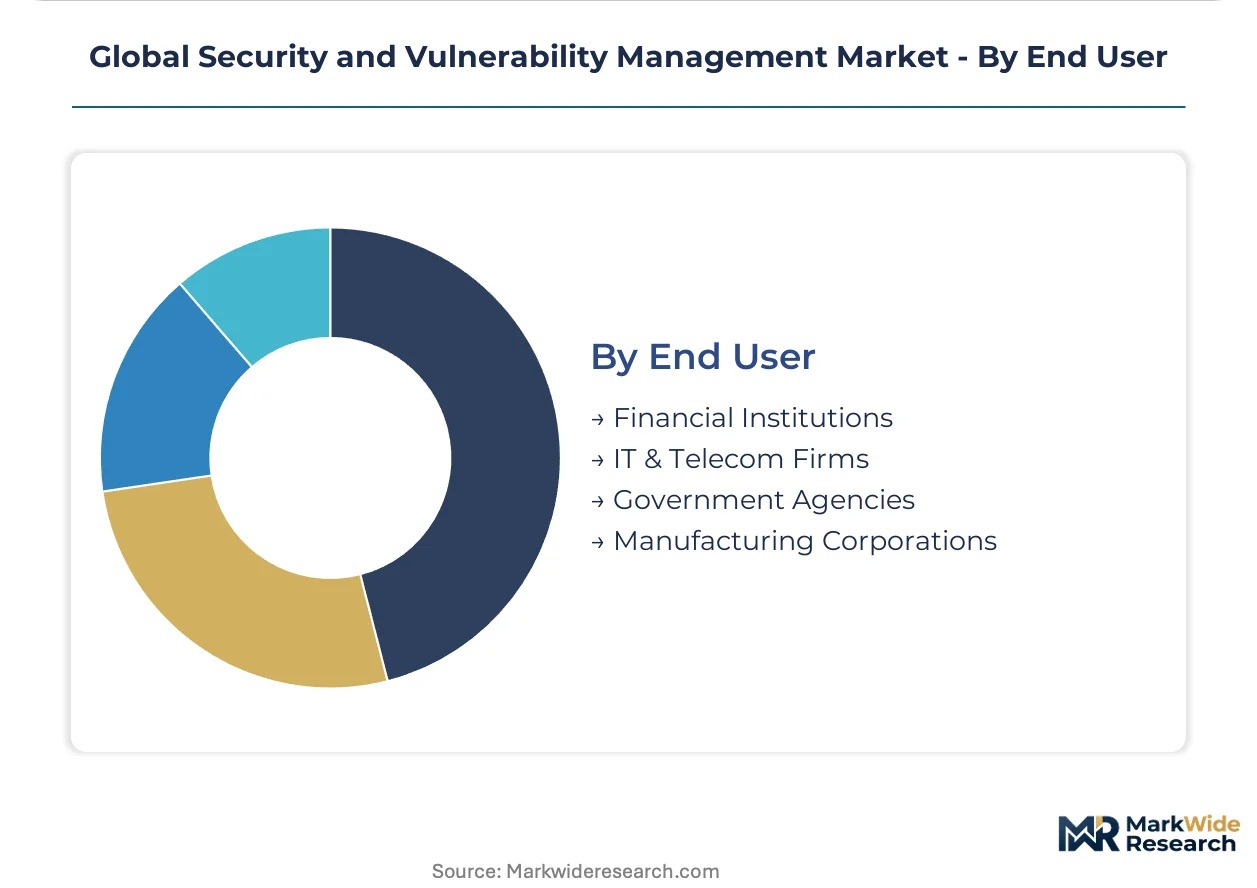
Customer type determines procurement sophistication, with financial institutions demanding real-time telemetry while manufacturing prioritizes passive scanning for operational technology convergence.
- Financial Institutions:Maintain continuous vulnerability monitoring capabilities to satisfy SEC four-day breach disclosure requirements. United States banking regulators enforce strict scanning cadences that compress remediation cycles from weeks to hours.
- IT & Telecom Firms:Operate the most fragmented tool estates, generating redundant license expenditures across overlapping procurement silos.
- Government Agencies:German and Japanese federal buyers anchor high-assurance contract awards through continuous exposure management platforms.
- Manufacturing Corporations:Bridge information technology and operational technology networks, opening demand for passive scanning solutions that discover industrial controllers without production disruption.
Financial institutions retain volume leadership; manufacturing corporations follow the steepest trajectory as OT/ICS convergence accelerates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Specialized security engineering talent clusters disproportionately in jurisdictions with dense federal contracting ecosystems and stringent disclosure mandates. Regulatory divergence across major economies is fragmenting compliance architectures and forcing multinational enterprises to maintain jurisdiction-specific vulnerability management stacks.
United States
SEC cybersecurity disclosure rules compress breach reporting windows to four business days, compelling Fortune 500 firms to deploy continuous monitoring pipelines. Federal buyers anchor high-assurance contract awards through exposure management platforms that feed directly into incident response workflows. Silicon Valley and Washington D.C. metro areas concentrate vendor engineering operations serving defense and intelligence community procurement.
Germany
EU NIS2 Directive transposition expands regulated entity coverage to critical supply chain intermediaries, extending procurement mandates to previously exempt manufacturing tiers. The country's automotive sector drives threat intelligence adoption as OEMs impose security requirements on tiered component suppliers. Munich and Stuttgart industrial clusters deploy passive scanning solutions for operational technology convergence without production disruption.
Japan
METI guidelines now classify semiconductor supply chains and satellite operators as critical infrastructure, mandating vulnerability management for previously unregulated sectors. Cloud-based deployment accelerates among manufacturers seeking scalable monitoring for distributed production networks. Tokyo and Osaka financial centers maintain mainframe-adjacent security services extending into core banking systems.
United Kingdom
Private equity-owned portfolio companies standardize on bundled endpoint detection suites to reduce software spend, compressing dedicated vulnerability scanner procurement. The National Cyber Security Centre shapes baseline guidelines that influence domestic critical infrastructure operator specifications. London's fintech cluster drives demand for API-native discovery tools mapping multi-cloud attack surfaces.
France
EU AI Act risk classification mandates security-by-design documentation throughout machine learning lifecycles, extending vulnerability scope into data science operations. Healthcare AI developers deploy specialized scanning tools for containerized inference endpoints and model repositories. Paris-Saclay research cluster anchors academic-industry partnerships developing adversary simulation capabilities.
Global Security and Vulnerability Management Market Competitive Landscape
Concentration sits with integrated platform vendors possessing adjacent cloud security and identity risk capabilities. The vendor landscape stratifies across three tiers: unified exposure management suites commanding enterprise procurement, point-solution specialists defending niche segments, and bundled security suites absorbing mid-market share. Dominant competitive moves include portfolio consolidation through acquisition and technology licensing arrangements that extend platform coverage into operational technology environments.
Within the integrated platform tier, Tenable, Inc. and Qualys, Inc. exemplify contrasting architectural approaches to continuous exposure management, while IBM Corporation occupies a position serving regulated verticals with mainframe-adjacent security services. Microsoft represents the bundled suite trajectory, absorbing mid-market vulnerability assessment functionality into broader endpoint protection offerings. These four anchors illustrate how vendor strategy diverges between best-of-breed depth and consolidated procurement convenience.
| Leading Market Players |
|---|
| Tenable, Inc. |
| Qualys, Inc. |
| IBM Corporation |
| Microsoft |
| Rapid7 |
| Cisco Systems, Inc. |
| CrowdStrike |
| Broadcom Inc. |
| Fortra, LLC |
| Others |
Supply & Pricing Matrix
Platform-scale economies in cloud-native vulnerability scanning compress marginal delivery costs below on-premises alternatives, concentrating supply-side power among hyperscaler-integrated vendors while establishing subscription pricing floors that mid-market entrants struggle to undercut without sacrificing threat intelligence feed quality.
Pricing Analysis
SEC cybersecurity disclosure rules dictate the pricing tier structure across the United States market, segmenting procurement into continuous monitoring premiums versus basic scanning commoditization. Three-tier pricing structure across enterprise, mid-market, and managed service levels separates federal-grade exposure management from bundled endpoint suites and self-service cloud subscriptions. Cost compression in mid-market tiers intensifies because Microsoft Defender Vulnerability Management absorbs price-sensitive demand previously served by standalone scanners. Financial institutions exhibit least price sensitivity due to four-day breach disclosure penalties, while private equity-owned portfolio companies in the United Kingdom demonstrate highest elasticity as CFOs impose vendor rationalization mandates.
Supply Chain Analysis
Just-in-time delivery preferences dominate threat intelligence feed distribution, with real-time indicator pipelines replacing batch-updated signature databases that introduced exploitable latency windows. Software development concentrates in the United States, Israel, and Ireland, drawing from specialized security engineering talent pools clustered around federal contracting ecosystems. Raw material dependencies center on cloud compute capacity, proprietary vulnerability research teams, and licensed exploit databases. Single-source vulnerability emerges from concentration in Israeli military-alumni-founded research units that anchor multiple vendor threat intelligence offerings. Distribution runs through direct enterprise sales teams for Fortune 500 accounts and hyperscaler marketplaces for mid-market cloud-native procurement.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Consolidated security procurement represents an existential substitution threat to standalone vulnerability vendors, as bundled endpoint detection suites absorb mid-market demand previously served by best-of-breed scanning tools.
For Market Incumbents: Shield platform stickiness through API-native integration depth that embeds vulnerability telemetry into customer security orchestration workflows, neutralizing displacement risk from Microsoft Defender's bundled economics. Prioritize acquisition of attack surface management specialists to extend coverage beyond internal scanning before private equity roll-ups capture this adjacency. Vertical integration into proprietary threat intelligence research reduces dependency on Israeli military-alumni talent pipelines that constrain competitor differentiation. For New Entrants and Emerging Players: Passive scanning solutions for operational technology environments represent the most penetrable white-space where incumbent platforms lack non-disruptive discovery capabilities for industrial controllers. Target German automotive tier suppliers facing EU NIS2 supply chain mandates as the fastest-regulated expansion segment without entrenched vendor relationships. Go-to-market leverage rests on managed service packaging that addresses acute security engineer scarcity without requiring customer headcount expansion. For Investors and Strategic Acquirers: Recurring-revenue conversion is highest among cloud-native vulnerability platforms with API-integrated customer deployments that generate usage-based expansion rather than license renewal negotiations. Long-term viability favors vendors possessing adjacent identity risk and cloud security posture capabilities that satisfy CFO consolidation mandates. Acquisition target archetype: mid-market exposure management platforms with 70%+ net revenue retention and OT/ICS scanning modules. Signal to watch: EU member state NIS2 transposition deadlines crystallizing enforcement timelines that trigger procurement acceleration.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies vulnerability findings with cloud security posture and identity risk data to satisfy CFO consolidation mandates. |
| Acquisition of Specialist Firm | Extends coverage into attack surface management and OT/ICS passive scanning where incumbents lack capability depth. |
| Strategic Partnership | Embeds vulnerability telemetry into hyperscaler marketplaces and security orchestration platforms to reduce customer switching. |
| Geographic Expansion | Establishes compliant service templates in EU member states before NIS2 enforcement deadlines crystallize procurement. |
| Product Launch | Deploys agentless scanning architectures and adversary simulation capabilities that reduce endpoint performance overhead. |
Research Methodology
Operator-level perspectives from CISOs, security operations center directors, federal procurement officers, and cloud platform engineers anchored the qualitative base for this analysis. Primary fieldwork combined structured interviews with secondary validation across SEC cybersecurity disclosure filings, EU NIS2 implementation progress reports, Japanese METI guideline publications, and hyperscaler security service expansion announcements. Bottom-up deployment model sizing triangulated against top-down regulatory mandate coverage estimates to produce segment-level projections.
Sensitivity analysis tested forecast robustness across alternative regulatory enforcement timelines and cloud migration velocity scenarios throughout the projection horizon. Segmentation dimensions modeled include deployment architecture, organization scale tier, vertical regulatory exposure, integration complexity level, and geographic adoption pattern. CAGRs derived from installed base expansion rates and annual contract value growth trajectories, with inputs from threat intelligence feed pricing trends and security engineer wage inflation indices.
Forecasts assume regulatory continuity in United States SEC enforcement, EU NIS2 transposition, and Japanese METI critical infrastructure designation regimes; material policy shifts would require re-modeling demand acceleration or compliance delay scenarios. Revision becomes warranted when cloud-native vulnerability scanning penetration in mid-market enterprises crosses thresholds that trigger accelerated bundled suite displacement.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Explosive Detection Kit Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
Global Security As a Service Market
Security and Surveillance
North America Security Testing Market
Security and Surveillance
Europe Anti-Piracy Protection Market
Security and Surveillance
Alarm Monitoring Software Market
Security and Surveillance
Full Body Scanner Market
Security and Surveillance
TSCM Equipment Market
Security and Surveillance
Signal Jamming Systems Market
Security and Surveillance
Signal Jammer Market
Security and Surveillance
Stadium Security Market
Security and Surveillance
Speed Limit Radar Signs Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Residential Security Market
Security and Surveillance
Maritime Security Market
Security and Surveillance
5G-Enhanced Surveillance Market