
 Global Container Security Market | 2026-2036
Global Container Security Market Size, Share, and Industry Trends Forecast 2026-2036
Global Container Security Market Foresight
The gap between premium container security stacks and commodity tooling is broadening as runtime protection with behavioral analytics commands enterprise budgets while basic vulnerability scanning faces price compression. Palo Alto Networks leverages deep integration between its Prisma Cloud platform and Kubernetes-native enforcement to sustain premium positioning. Aqua Security anchors its competitive stance through specialized supply chain security capabilities for software development firms. Trend Micro competes aggressively in the Asia-Pacific channel with consolidated workload protection bundles that span virtual machines and containers.
Container security encompasses runtime vulnerability scanning, image integrity verification, and policy-driven access control designed to protect ephemeral workloads orchestrated through Docker, Kubernetes, and CRI-O environments. The discipline centers on maintaining cryptographic provenance across container images while enforcing least-privilege network segmentation between microservices. Runtime protection solutions lead current revenue generation as organizations prioritize live threat detection over static pre-deployment scanning. Hybrid cloud deployments represent the fastest-expanding segment as regulated industries demand data sovereignty controls that pure public cloud configurations cannot satisfy. DevSecOps application workflows command disproportionate margin pools by embedding security gates directly into CI/CD pipelines.
The US Federal Risk and Authorization Management Program and the EU Cybersecurity Act impose baseline container hardening requirements on government-facing and critical infrastructure deployments. HIPAA and PCI-DSS audit frameworks in the US extend container security obligations to healthcare and financial services data environments. Stakeholders must monitor whether emerging sovereign cloud mandates fragment compliance standards across national boundaries.
Market Dynamics
Runtime threat detection is concentrating procurement budgets as ephemeral workload protection overtakes static vulnerability scanning in enterprise security stacks. Financial services and healthcare organizations now mandate behavioral analytics for containerized payment processing and patient data environments.
Growth Catalysts
- Kubernetes-native enforcement architectures:Cloud-native application platforms require policy-driven admission controllers that intercept orchestration requests before container deployment.
- EU AI Act compliance mandates:European enterprises must maintain cryptographic provenance and audit trails for AI/ML training pipelines running in containerized infrastructure.
- Financial services containerization:PCI-DSS audit frameworks now explicitly require runtime segmentation for cardholder data environments orchestrated through Docker and CRI-O.
Market Restraints
- Specialized talent scarcity:DevSecOps engineers with Kubernetes security expertise command premium compensation that constrains mid-market adoption velocity.
- Tooling fragmentation:The absence of unified standards across image registries, runtime scanners, and policy engines forces costly integration overhead.
- Open-source substitution pressure:Falco and OPA (Open Policy Agent) provide baseline runtime detection that compresses pricing for commercial alternatives.
Strategic Opportunities
- Sovereign cloud mandates:Germany's federal data protection standards and France's ANSSI cloud security certifications create demand for on-premises container security stacks.
- Edge container convergence:5G network slicing and industrial IoT gateways require lightweight security agents that protect distributed microservices outside centralized data centers.
- Software supply chain attestation:SLSA (Supply Chain Levels for Software Artifacts) frameworks are embedding cryptographic signing requirements into CI/CD pipelines.
Industry Challenges
- Ephemeral forensics gaps:Container lifecycles measured in minutes complicate incident response and evidence preservation for security operations centers.
- Legacy monolith integration:Hybrid environments combining VM-based workloads with Kubernetes clusters require dual-stack security policies that increase operational complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Container Security Market |
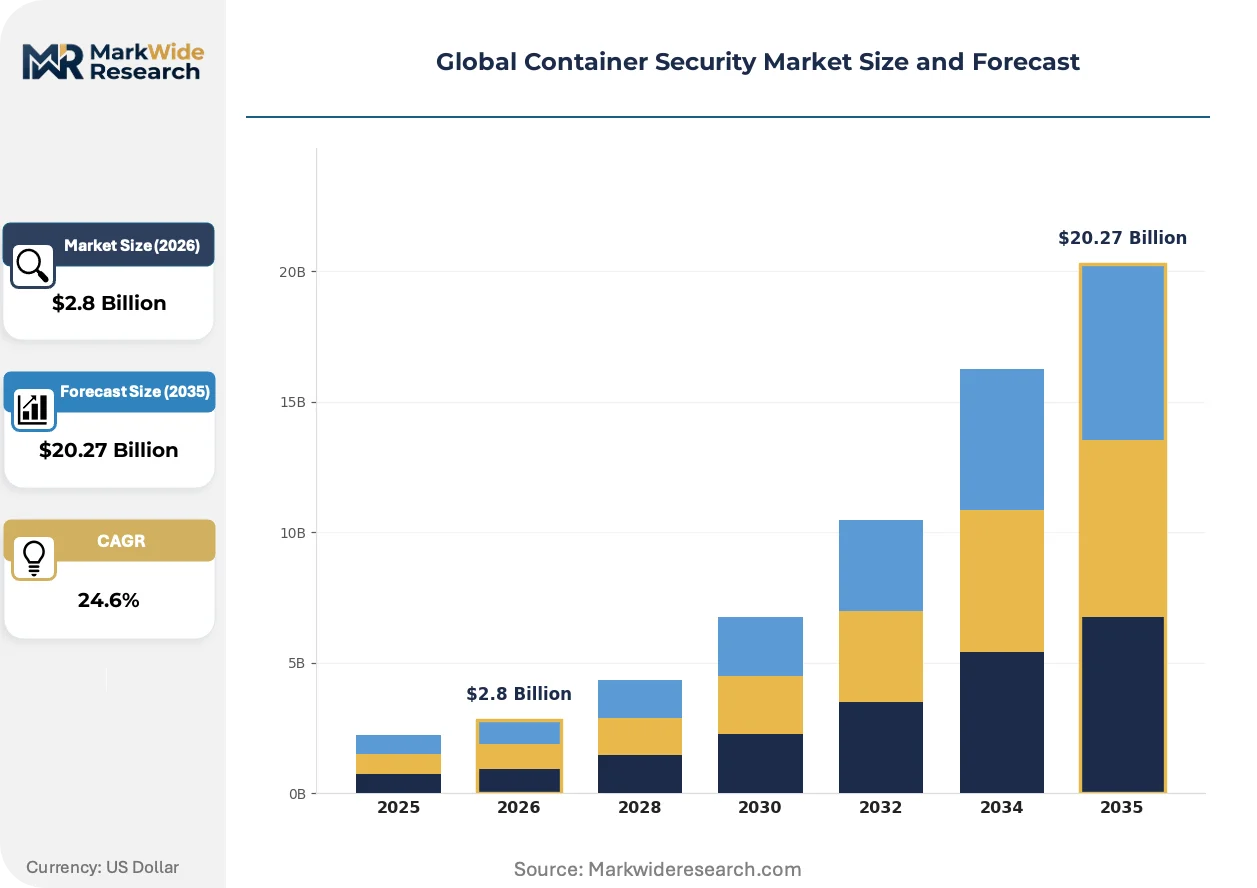
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $20.27 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Vulnerability Scanning, Runtime Protection, Compliance Monitoring, Encryption, Identity & Access Management, Behavior Analytics Deployment: On-Premises, Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud Application: DevSecOps, Microservices Security, Network Security, Endpoint Security, API Security, Data Protection End User: Cloud Service Providers, Software Development Firms, Telecommunications, Financial Services, Government Agencies |
| Companies Covered | Qualys, Trend Micro, Palo Alto Networks, IBM, Fortinet, Check Point Software Technologies, Cisco Systems, Microsoft Corporation, Aqua Security, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Container Security Market Shifts & Advancements
Security control planes are migrating closer to workload instantiation points as zero-trust architectures eliminate implicit trust boundaries between microservices. This architectural shift demands real-time policy enforcement without proxy latency.
eBPF (Extended Berkeley Packet Filter) instrumentation is decentralizing runtime visibility by enabling kernel-level observability without container-sidecar overhead. Telcos and high-frequency trading firms are deploying eBPF-based security agents to capture system calls with sub-millisecond latency. This kernel-native approach is decentralizing the market away from traditional agent-based scanning toward embedded telemetry pipelines.
GDPR Article 32 and the EU Cybersecurity Act are mandating encryption-at-rest and access logging for container orchestration control planes. European critical infrastructure operators must now document container image provenance through immutable registries. German industrial cloud providers are responding by hardening Kubernetes API servers with mutual TLS and audit-forwarding to sovereign data lakes.
Security purchasing is consolidating through platform bundles as CISOs reduce vendor sprawl. Mid-market enterprises are displacing point solutions with consolidated workload protection spanning VMs, containers, and serverless functions. This preference shift is most visible in US healthcare systems seeking unified HIPAA compliance across heterogeneous infrastructure.
Global Container Security Market Segmentation
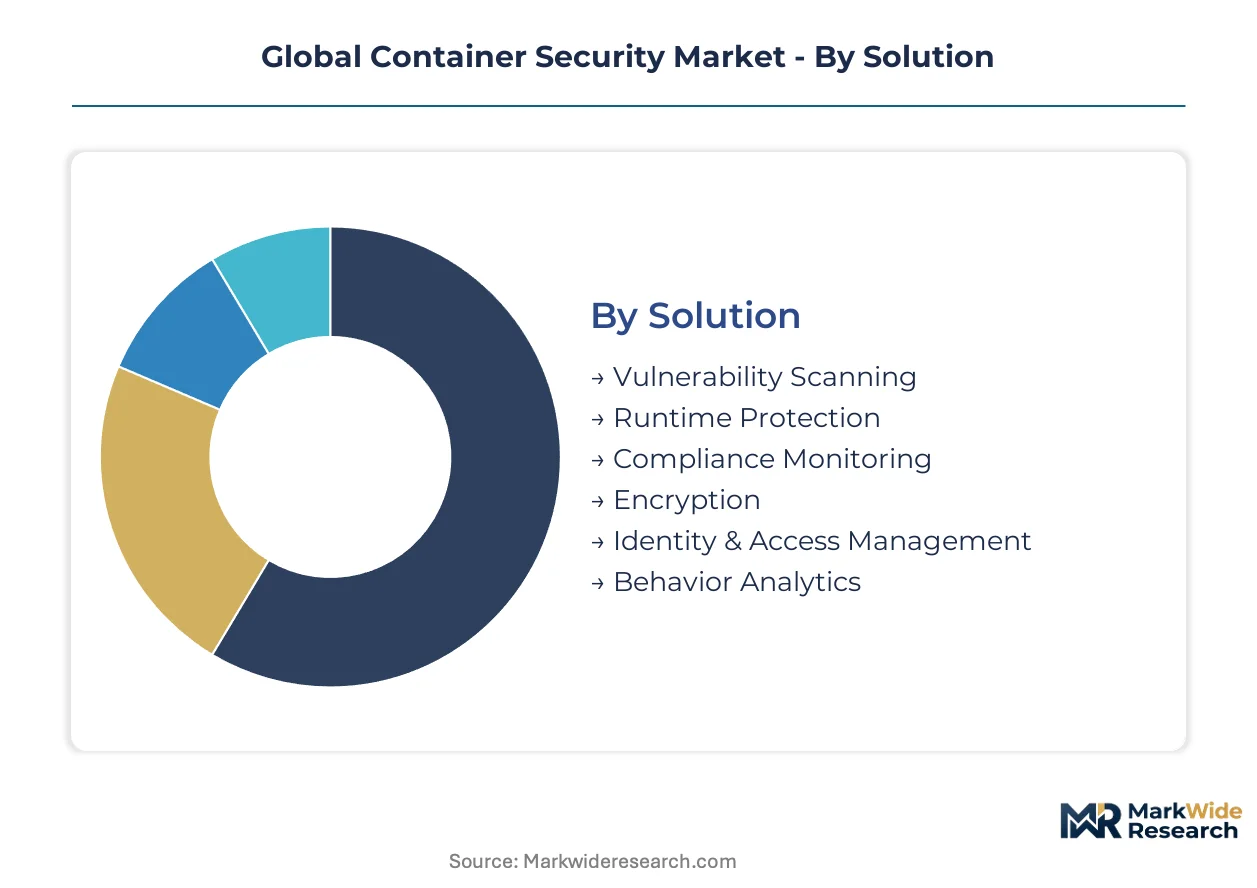
Container security procurement patterns diverge sharply across solution types, with runtime protection commanding enterprise budgets while vulnerability scanning commoditizes. Deployment models reflect sovereignty pressures, as regulated industries reject pure public cloud configurations for hybrid architectures that preserve data residency controls.
Solution:
Runtime Protection and Vulnerability Scanning carry distinct certification burdens under PCI-DSS and HIPAA frameworks, with behavioral analytics solutions now requiring explicit audit trail documentation for financial services deployments.
- Runtime Protection:Kernel-level threat detection intercepts system calls and network flows from ephemeral workloads without sidecar overhead. Financial services institutions in Germany and the United States mandate behavioral analytics for containerized payment processing environments, with eBPF instrumentation displacing traditional agent-based approaches in high-frequency trading stacks.
- Vulnerability Scanning:Static image analysis identifies CVEs in container registries before orchestration deployment. Mid-market enterprises compress pricing here through open-source substitution with Trivy and Clair, while regulated healthcare providers maintain commercial subscriptions for HIPAA-compliant audit documentation.
- Compliance Monitoring:Automated policy enforcement maps container configurations against GDPR Article 32 and EU Cybersecurity Act baselines.
- Encryption:Cryptographic provenance for container images and runtime secrets management.
- Identity & Access Management:Kubernetes-native RBAC and service mesh authentication for microservice-to-microservice trust.
- Behavior Analytics:Machine learning models detect anomalous container behavior without signature-based rules.
Runtime Protection sits at the top of the volume ranking, with Behavior Analytics climbing the fastest as AI/ML training pipelines harden under EU AI Act mandates.
Deployment:
Cost tiering separates sovereign-compliant on-premises stacks from consumption-priced public cloud offerings, with hybrid configurations capturing premium margins through data residency orchestration.
- Hybrid Cloud:Workload portability across on-premises Kubernetes and hyperscaler environments enables data sovereignty without sacrificing elasticity. German industrial cloud providers and French ANSSI-certified operators concentrate procurement here, responding to federal mandates that prohibit pure public cloud for critical infrastructure.
- Multi-Cloud:Unified security control planes span AWS, Azure, and GCP container services through centralized policy management. Large financial services institutions in the United States deploy multi-cloud strategies to avoid vendor lock-in while maintaining consistent PCI-DSS segmentation across environments.
- On-Premises:Air-gapped container security for classified government and defense workloads.
- Public Cloud:Native CSP tooling and third-party marketplace solutions for cloud-native startups.
- Private Cloud:Dedicated tenant isolation with single-organization infrastructure control.
Hybrid Cloud leads commercial margin capture, with Multi-Cloud expanding most quickly among Fortune 500 enterprises pursuing vendor diversification.
Application:
Maturity differentiation separates embedded DevSecOps pipelines from retrofitted network security controls, with earlier integration points commanding implementation premiums.
- DevSecOps:Security gates embedded directly into CI/CD pipelines enforce SLSA attestation and cryptographic signing before container registry publication. Software development firms in India and Israel concentrate demand here, integrating Aqua Security and Prisma Cloud scanners into GitOps workflows.
- Microservices Security:East-west traffic segmentation and service mesh policy enforcement protect inter-pod communication. Telecommunications operators deploying 5G network functions virtualization prioritize this segment for subscriber data isolation.
- Network Security:Container-aware firewalls and ingress controllers for perimeter protection.
- Endpoint Security:Host-level protection for container runtime daemons and worker nodes.
- API Security:Gateway-level authentication and rate limiting for exposed microservice interfaces.
- Data Protection:Encryption-at-rest and access logging for persistent container volumes.
DevSecOps dominates current implementation spend, with Microservices Security gaining share fastest as service mesh adoption accelerates in telecommunications infrastructure.
End User:
Customer type determines procurement sophistication, with cloud service providers internalizing security tooling while financial services outsource to specialized vendors for audit separation.
- Financial Services:PCI-DSS and SOX compliance mandates drive runtime segmentation for cardholder data environments. JPMorgan Chase and Deutsche Bank deploy dedicated container security operations centers with 24/7 behavioral monitoring, representing the highest per-seat spending in the market.
- Cloud Service Providers:Hyperscalers internalize container security through proprietary control planes and shared responsibility models. AWS, Microsoft Azure, and Google Cloud Platform invest in native Kubernetes security offerings that compress third-party vendor addressable market in downstream segments.
- Software Development Firms:Agile shops embedding security into release pipelines.
- Telecommunications:5G core network containerization requiring telco-specific NFV security.
- Government Agencies:FedRAMP and NIST-compliant deployments for federal container workloads.
Financial Services anchors revenue concentration, with Government Agencies showing steepest expansion trajectory as NIST SP 800-190 hardening requirements extend across federal departments.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
DevSecOps engineers cluster in the United States, Germany, and India, anchoring regional capability formation as enterprises compete for Kubernetes-native security talent.
United States
JPMorgan Chase and Capital One drive procurement for runtime behavioral analytics in containerized payment environments. The FedRAMP authorization program mandates baseline hardening for federal Kubernetes workloads. Silicon Valley security vendors concentrate development operations in San Francisco and Seattle metro areas.
Germany
Siemens and Deutsche Bank require sovereign-compliant container stacks for industrial cloud and financial services workloads. The BSI (Federal Office for Information Security) enforces technical guidelines for critical infrastructure Kubernetes deployments. Bavarian industrial cloud providers in Munich anchor procurement for air-gapped container security solutions.
United Kingdom
HSBC and Barclays embed container security gates into CI/CD pipelines for trading platform modernization. The National Cyber Security Centre publishes Kubernetes hardening guidance under the UK Cyber Security Strategy. London's fintech cluster in Shoreditch drives demand for microservices security expertise.
Japan
NTT and SoftBank prioritize container security for 5G network function virtualization deployments. METI's Cyber/Physical Security Framework extends to cloud-native infrastructure protection standards. Tokyo's Marunouchi financial district concentrates procurement for runtime segmentation solutions.
India
Infosys and TCS integrate container scanners into GitOps workflows for North American and European clients. The Ministry of Electronics and Information Technology's Data Protection Bill drives compliance monitoring investments. Bangalore's Whitefield tech corridor anchors DevSecOps talent formation for container security implementation.
Global Container Security Market Competitive Landscape
Capital-heavy platform vendors compete with asset-light specialists for enterprise security budgets. The market structure concentrates around three to five integrated cybersecurity conglomerates with broad workload protection portfolios. Strategic archetypes include full-stack platform vendors, Kubernetes-native specialists, and channel-optimized regional players. Dominant competitive moves encompass API-level integration partnerships with cloud service providers and acquisition of eBPF telemetry startups.
Within the platform vendor tier, Palo Alto Networks and Microsoft Corporation exemplify consolidation strategies spanning virtual machines, containers, and serverless functions. Trend Micro occupies a position among Asia-Pacific-optimized providers with bundled workload protection offerings. Aqua Security represents the Kubernetes-native specialist archetype with concentrated supply chain security capabilities.
| Leading Market Players |
|---|
| Qualys |
| Trend Micro |
| Palo Alto Networks |
| IBM |
| Fortinet |
| Check Point Software Technologies |
| Cisco Systems |
| Microsoft Corporation |
| Aqua Security |
| Others |
Supply & Pricing Matrix
Backward integration into eBPF telemetry development anchors supply positioning for container security vendors while sustaining premium pricing power against open-source substitution. The report traces how captive control over kernel-level instrumentation capabilities separates platform vendors from channel-dependent specialists across Germany, the United States, and India.
Pricing Analysis
The bundled-vs-unbundled service split separates consolidated workload protection platforms from point-solution vendors. Three-tier pricing structure across premium, standard, and economy levels tracks runtime behavioral analytics depth, with PCI-DSS certification tiers commanding substantial premiums over baseline vulnerability scanning. Cost compression in the scanning tier is intensifying because Trivy and Clair provide substitutable static analysis, while margins are tightening due to hyperscaler marketplace commissions. Mid-market enterprises exhibit highest price sensitivity, whereas JPMorgan Chase and Deutsche Bank demonstrate minimal elasticity for sovereign-compliant runtime stacks.
Supply Chain Analysis
Returns and refurbishment flows remain minimal in software delivery, though subscription renewal mechanics and customer success touchpoints function as reverse-logistics equivalents that anchor lifetime value calculations. Supply concentrates in the United States, Israel, and India for security engineering talent, with kernel-level expertise clustering in San Francisco, Tel Aviv, and Bangalore. Component dependencies include eBPF toolchain development, cloud-native policy engines, and Kubernetes admission controller frameworks. Single-source vulnerability around hyperscaler API dependencies creates concentration risk. Distribution runs through direct enterprise sales, cloud marketplace integrations, and channel partners serving regulated verticals.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Global Container Security Market functions as a stable compounder. Kubernetes deployment expansion across financial services and healthcare institutions generates recurring procurement that sustains vendor revenue predictability.
For Market Incumbents: Deepen integration between runtime protection and CI/CD pipeline orchestration to defend against Kubernetes-native specialists. Acquire eBPF telemetry startups to secure kernel-level instrumentation capabilities before open-source tooling commoditizes this layer. The threat of Falco and OPA substitution demands vertical control over policy engine development.
For New Entrants and Emerging Players: Mid-market healthcare providers in the United States represent an underserved buyer archetype with unmet demand for HIPAA-compliant container security at accessible price points. Target sovereign cloud operators in France and Germany seeking ANSSI-certified and BSI-compliant on-premises stacks. A channel-first go-to-market through regional system integrators accelerates credibility formation.
For Investors and Strategic Acquirers: Roll-up economics work for Kubernetes-native security specialists because platform consolidation eliminates redundant engineering overhead while preserving specialized customer relationships. The five-to-ten-year viability window favors vendors with demonstrated FedRAMP or EU Cybersecurity Act compliance pathways. Acquisition target archetypes include eBPF instrumentation startups and supply chain attestation toolmakers. Monitor hyperscaler native security tooling releases as the inflection indicator for third-party vendor displacement risk.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified workload protection spanning VMs and containers reduces CISO vendor sprawl at US healthcare systems. |
| Acquisition of Specialist Firm | eBPF telemetry startups provide kernel-level observability without sidecar overhead for high-frequency trading stacks. |
| Strategic Partnership | Cloud marketplace integrations with AWS and Azure compress customer acquisition costs for runtime protection vendors. |
| Geographic Expansion | German industrial cloud providers in Munich anchor demand for air-gapped sovereign-compliant container security solutions. |
| Product Launch | SLSA attestation frameworks embed cryptographic signing requirements into CI/CD pipelines for software development firms. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window. Primary fieldwork engaged CISOs, DevSecOps engineers, Kubernetes platform architects, and channel sales heads at container security vendors across the United States, Germany, and India. Secondary validation drew from SEC 10-K filings, hyperscaler capex disclosures, FedRAMP authorization databases, and EU Cybersecurity Act implementation guidance. Bottom-up segment sizing triangulated against top-down market estimates derived from IT security spending benchmarks.
Comparable historical periods anchored the projection framework, with growth trajectories calibrated against prior infrastructure security adoption cycles. The analytical framework modeled deployment architecture, solution type, end-user vertical, and regional regulatory cluster dimensions throughout the forecast period. CAGRs were derived from segment-level growth rate convergence analysis. Forecast inputs included Kubernetes adoption curves, PCI-DSS audit framework updates, and sovereign cloud mandate implementation timelines.
Underlying measurement precision varies by segment; runtime protection and hybrid cloud deployments carry tighter precision than vulnerability scanning and public cloud configurations. Forecasts reflect documented assumptions regarding regulatory enforcement intensity and open-source tooling substitution rates. Practitioners should monitor hyperscaler native security feature releases, EU AI Act implementation guidance, and eBPF kernel mainline adoption for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Global Threat Intelligence Management Market
Security and Surveillance
Explosive Detection Technology Market
Security and Surveillance
Baggage Scanner Market
Security and Surveillance
Global Contraband Detector Market
Security and Surveillance
Global Acoustic Hailing Devices Market
Security and Surveillance
Maritime Security Market
Security and Surveillance
Intelligent Fencing Market
Security and Surveillance
Explosive Detection Kit Market
Security and Surveillance
Global Corporate Travel Security Market
Security and Surveillance
Prison Management Systems Market
Security and Surveillance
Surveillance Radars Market
Security and Surveillance
Global Firearm Sight Market
Security and Surveillance
North America Security Screening Market
Security and Surveillance
Europe Urban Security Screening Market
Security and Surveillance
5G-Enhanced Surveillance Market
Security and Surveillance
Security Analytics Market