
 Multi-Layer Security Market | 2026-2036
Multi-Layer Security Market Size, Share, and Industry Trends Forecast 2026-2036
Multi-Layer Security Market Outlook
ISO/IEC 27001 certification is rotating as the primary gating credential for enterprise security procurement, filtering vendor eligibility across Fortune 500 contracts. Palo Alto Networks leverages cloud-native architecture to sustain platform consolidation across hybrid environments. Fortinet anchors hardware-dominant accounts with integrated SD-WAN and firewall bundles. Check Point Software Technologies differentiates through quantum-resistant encryption previews aimed at government buyers.
Multi-layer security denotes a defense-in-depth architecture combining firewalls, intrusion detection systems, antivirus software, and encryption tools operating across network, endpoint, and application strata with sub-100-millisecond threat correlation latency. The architecture's primary purpose is to eliminate single points of failure by forcing adversaries to breach multiple independent controls. Cloud-based deployment models capture the fastest expansion as enterprises abandon capital-intensive on-premises refresh cycles. Managed security services concentrate margin pools through recurring revenue and vendor lock-in, while hybrid deployments dominate heavily regulated healthcare and government agencies unable to fully externalize control.
NIST, ISO/IEC 27001, and the EU AI Act collectively reshape product standards by mandating explainable threat detection, audit-ready logging, and cross-border data residency. These frameworks force vendors to engineer compliance-native features rather than retrofit controls. Stakeholders must monitor how zero-trust architecture mandates proliferate from federal agencies into commercial procurement templates.

Market Dynamics
Federal zero-trust mandates are compressing procurement cycles across enterprise security stacks, forcing vendors to pre-integrate identity verification and micro-segmentation capabilities or exit competitive bids. This structural pressure is eliminating point-product vendors that cannot demonstrate cross-layer orchestration.
Growth Catalysts
- Ransomware proliferation in financial services:Banking and insurance firms are accelerating multi-layer deployments to satisfy cyber insurance underwriters and regulatory examiners.
- NIST SP 800-207 adoption:Federal agencies in the United States are mandating zero-trust architecture assessments, creating immediate replacement demand for perimeter-centric legacy systems.
- Sub-100-millisecond correlation requirements:Real-time threat detection specifications in enterprise RFPs are pulling cloud-native security service edge platforms ahead of hardware-bound alternatives.
Market Restraints
- Specialized cybersecurity talent scarcity:Shortages of cloud security architects and threat intelligence analysts are extending implementation timelines and inflating professional services costs.
- Legacy infrastructure entrenchment:Manufacturing and utilities sectors face capital constraints and operational continuity requirements that delay full-stack security modernization.
- Cross-border data residency friction:Divergent national data localization laws are fragmenting cloud security architectures and raising compliance engineering overhead.
Strategic Opportunities
- Managed detection and response expansion:Mid-market enterprises lacking internal security operations centers represent an underpenetrated buyer segment for outsourced multi-layer monitoring.
- Quantum-resistant encryption previews:Government buyers are piloting post-quantum cryptographic modules ahead of NIST standardization, creating early-mover positioning for compliant vendors.
- Healthcare hybrid deployment models:HIPAA-covered entities require on-premises control for protected health information while extending cloud-based analytics, demanding purpose-built architectural flexibility.
Industry Challenges
- ISO/IEC 27001 certification timeline compression:Vendor eligibility for Fortune 500 contracts now hinges on current certification cycles that require 12-18 month preparation windows.
- Multi-vendor integration complexity:Enterprises stitching together firewalls, endpoint detection, and identity platforms face interoperability gaps that degrade threat correlation accuracy.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Multi-Layer Security Market |
| Market Size in 2026 | $18.7 Billion |
| Market Size in 2035 | $61.78 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewalls, Intrusion Detection Systems, Antivirus Software, Encryption Tools Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Security Services End User: Enterprises, Government Agencies, Healthcare, Educational Institutions Threat Type: Malware, Phishing Attacks, Ransomware, Insider Threats |
| Companies Covered | Cisco Systems, Palo Alto Networks, Fortinet, Check Point Software Technologies, CrowdStrike Holdings, Zscaler, McAfee, Symantec, Trend Micro, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Multi-Layer Security Market Strategic Shifts
Security architecture is fragmenting into two competing design philosophies: consolidated cloud-native platforms versus best-of-breed layered stacks. This divergence is reshaping vendor R&D priorities and buyer evaluation criteria simultaneously.
Extended detection and response platforms are bifurcating the endpoint security market. These systems aggregate telemetry across endpoints, networks, and cloud workloads into unified investigation workflows. Large enterprises with mature security operations centers are adopting native XDR suites from platform vendors, while mid-market buyers prefer managed XDR services that outsource detection engineering. The technology is compressing standalone endpoint detection and response vendor margins by absorbing their core functionality into broader platforms.
The EU AI Act's risk-based classification system is mandating human oversight and audit trails for automated threat detection systems deployed in critical infrastructure. Security vendors must now engineer explainability features that document decision pathways for anomaly alerts. European energy and transportation operators are most affected, with procurement teams rewriting technical specifications to require algorithmic transparency documentation.
Enterprise buyers are unbundling security professional services from product licenses, demanding à la carte implementation and managed detection contracts. This purchasing pattern is disrupting traditional vendor attach-rate models that relied on mandatory deployment services. The shift is most visible in United States federal contracting, where agencies now separately evaluate product technical merit and implementation vendor qualifications.
Multi-Layer Security Market Segmentation
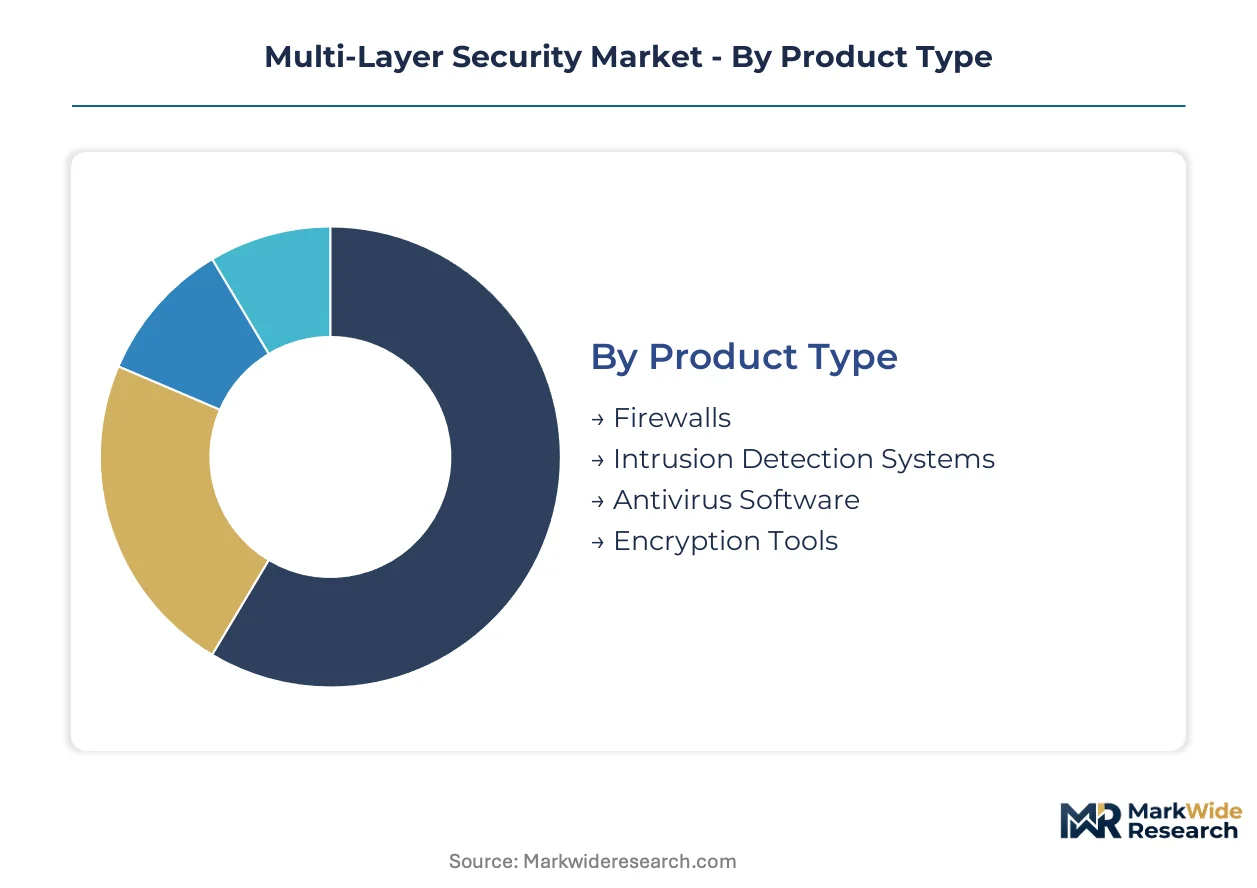
Multi-layer security procurement patterns diverge sharply across product architectures, operational models, and threat vectors. Buyers segment investments by compliance mandates, latency requirements, and internal security operations maturity rather than uniform technology refresh cycles.
Product Type:
Firewalls dominate domestic procurement in regulated financial services, while encryption tools drive export-led demand from defense contractors serving allied government markets.
- Firewalls:Next-generation firewall platforms integrate application awareness, intrusion prevention, and SSL inspection at network perimeters. United States federal agencies mandate these for zero-trust segmentation, compressing vendor qualification timelines.
- Intrusion Detection Systems:Network-based and host-based variants monitor traffic anomalies and system call patterns for signature and behavioral threats. Healthcare delivery organizations in Germany and France deploy these for GDPR-aligned breach detection, balancing automated response with human oversight requirements.
- Antivirus Software:Endpoint protection platforms with machine-learning classification engines.
- Encryption Tools:Quantum-resistant algorithm previews for classified communications.
Firewalls hold the largest share; momentum sits with encryption tools.
Deployment Model:
Cost tier differentiation separates capital-intensive on-premises builds from operational-expense cloud subscriptions, with hybrid architectures commanding premium professional services margins.
- On-Premises:Hardware appliances and perpetual software licenses deployed within customer data centers demand 3-5 year amortization cycles. Japanese manufacturing conglomerates and South Korean semiconductor fabs favor this model for intellectual property protection, accepting higher total cost of ownership for air-gapped control.
- Cloud-Based:Security service edge platforms deliver firewall-as-a-service, zero-trust network access, and cloud access security broker functions through distributed points of presence. Mid-market enterprises across Australia and Singapore adopt these to bypass security operations center buildouts, trading customization for speed-to-deployment.
- Hybrid:Split architectures maintaining on-premises policy enforcement with cloud analytics.
- Managed Security Services:Outsourced monitoring, detection engineering, and incident response.
Managed security services capture recurring revenue concentration; cloud-based deployments are expanding most quickly.
End User:
Application intensity varies by sector-specific regulatory exposure and adversary targeting profiles.
- Enterprises:Fortune 500 corporations across banking, technology, and energy verticals deploy integrated platforms spanning network, endpoint, and identity layers. ISO/IEC 27001 certification requirements filter vendor pools, with procurement teams prioritizing cross-layer orchestration over point-product depth.
- Government Agencies:Civilian and defense departments mandate FedRAMP authorization and NIST SP 800-207 compliance. United States federal zero-trust directives are displacing perimeter-centric legacy investments, creating replacement demand for micro-segmentation and continuous authentication capabilities.
- Healthcare:HIPAA-covered entities requiring audit-ready logging for protected health information access.
- Educational Institutions:Universities and K-12 districts with constrained security staffing.
Enterprises hold the largest share; government agencies are gaining share fastest.
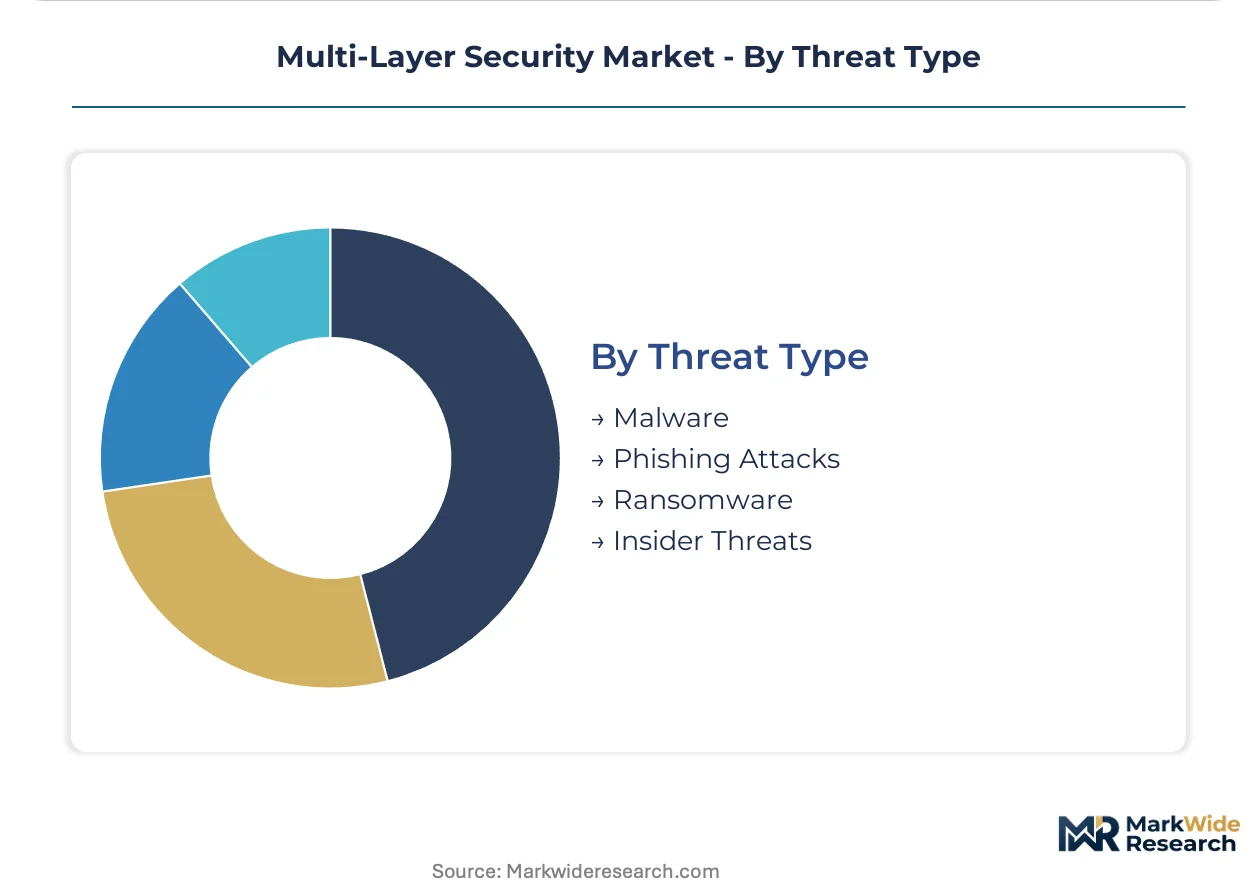
Threat Type:
Customer type stratification separates organizations with advanced persistent threat exposure from commodity malware targets.
- Ransomware:Encryption-based extortion campaigns against operational technology and business-critical systems drive cyber insurance underwriting requirements. United Kingdom financial services firms and German automotive suppliers accelerate multi-layer investments to satisfy policy renewal conditions and BaFin regulatory examinations.
- Phishing Attacks:Social engineering vectors compromising credentials and enabling business email fraud. Email security gateways with link sandboxing and behavioral anomaly detection concentrate demand among professional services firms in Switzerland and the Netherlands.
- Malware:File-based and fileless execution techniques requiring endpoint detection and response.
- Insider Threats:Privileged access monitoring and data loss prevention for malicious and negligent insiders.
Ransomware defense holds the largest share; phishing attack mitigation shows the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Enterprise security procurement concentrates in jurisdictions with stringent regulatory mandates and deep financial services penetration. Federal zero-trust directives and cyber insurance underwriting requirements are reshaping buyer archetypes across developed economies.
United States
Financial services firms in New York and Chicago drive demand as ransomware attacks intensify and cyber insurers mandate multi-layer controls. NIST SP 800-207 zero-trust assessments compress procurement cycles for federal agencies. Silicon Valley cloud-native vendors capture mid-market enterprises abandoning capital-intensive hardware refresh cycles.
Germany
Automotive suppliers and industrial machinery manufacturers in Bavaria and Baden-Württemberg accelerate investments to satisfy BaFin regulatory examinations and operational technology security requirements. The EU AI Act mandates explainable threat detection for critical infrastructure operators. Frankfurt's financial services cluster demands audit-ready logging aligned with GDPR breach notification timelines.
United Kingdom
London-based banking and insurance sectors prioritize ransomware defense to meet policy renewal conditions from Lloyd's of London underwriters. The National Cyber Security Centre publishes procurement guidance favoring cloud-native security service edge platforms. Manchester and Birmingham mid-market enterprises adopt managed detection and response services to bypass security operations center buildouts.
Japan
Manufacturing conglomerates in Tokyo and Osaka favor on-premises deployments for intellectual property protection despite higher total cost of ownership. METI cybersecurity frameworks guide critical infrastructure operator investments. Semiconductor fabs in Kyushu maintain air-gapped controls while extending cloud-based analytics for threat intelligence.
Australia
Sydney and Melbourne financial services firms adopt cloud-based security service edge platforms to satisfy APRA CPS 234 information security requirements. Mid-market enterprises across Queensland and Victoria trade customization for speed-to-deployment through outsourced monitoring. The Australian Cyber Security Centre's Essential Eight maturity model filters vendor eligibility in government procurement.
Multi-Layer Security Market Competitive Environment
Player mix skews toward platform consolidators with cross-layer orchestration capabilities. The vendor base separates into hardware-anchored incumbents, cloud-native challengers, and managed security service specialists. Strategic archetypes include integrated platform vendors bundling firewall, endpoint, and identity functions; best-of-breed stack assemblers stitching point products through API connectors; and pure-play managed detection providers outsourcing security operations center functions. Dominant competitive moves center on pre-integrated zero-trust certification bundles and quantum-resistant encryption module previews targeting government buyers.
Within the platform consolidator tier, Palo Alto Networks and Fortinet exemplify divergent architectural philosophies. Palo Alto Networks represents cloud-native consolidation across hybrid environments with sub-100-millisecond threat correlation latency. Fortinet anchors hardware-dominant accounts with integrated SD-WAN and firewall bundles serving manufacturing and utilities sectors with capital constraints. Check Point Software Technologies occupies a position targeting government buyers through quantum-resistant encryption previews ahead of NIST standardization.
| Leading Market Players |
|---|
| Cisco Systems |
| Palo Alto Networks |
| Fortinet |
| Check Point Software Technologies |
| CrowdStrike Holdings |
| Zscaler |
| McAfee |
| Symantec |
| Trend Micro |
| Others |
Value Chain & Pricing Dynamics
Capacity reservation contracts with NIST compliance indexation lock in multi-year supply access for federal zero-trust deployments while fixing professional services margins. United States government buyers trade pricing predictability for vendor certification commitments, compressing procurement cycles for Palo Alto Networks and Fortinet.
Pricing Analysis
Cost-plus contracts with FedRAMP authorization indexation dominate federal procurement, anchoring price visibility across deployment timelines. Three-tier pricing structure across premium, standard, and economy levels separates managed detection and response bundles from standalone firewall licenses, with ISO/IEC 27001 certification tiering access to Fortune 500 RFPs. Pricing pressure stems from cloud-native challengers undercutting hardware-anchored incumbents on total cost of ownership. Mid-market enterprises exhibit highest price sensitivity, while defense contractors absorbing quantum-resistant encryption modules show least.
Supply Chain Analysis
Semiconductor fabrication chokepoints in Taiwan and South Korea constrain next-generation firewall ASIC availability, extending lead times for Fortinet's hardware-dominant accounts. Critical component dependencies span specialized encryption processors from United States foundries, threat intelligence feeds from Israeli cybersecurity labs, and cloud infrastructure from hyperscalers. Single-source vulnerability concentrates in quantum-resistant cryptographic module suppliers awaiting NIST standardization. Distribution runs through value-added resellers holding federal contracting clearances, with direct-to-government channels bypassing traditional VAR margins.

Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Managed detection and response services expand faster than hardware appliances, converting capital expenditure into recurring revenue streams. This service-attach dynamic rewards vendors bundling monitoring, detection engineering, and incident response over standalone product licenses.
For Market Incumbents: Secure FedRAMP authorization renewals ahead of zero-trust mandate acceleration, locking out unqualified challengers from federal replacement cycles. Deepen backward integration into threat intelligence ingestion pipelines, reducing dependency on third-party data feeds. Fortify channel control through exclusive value-added reseller agreements holding cleared personnel certifications. For New Entrants and Emerging Players: Lead with cloud-native security service edge platforms targeting Australian and Singaporean mid-market enterprises bypassing security operations center buildouts. Healthcare hybrid deployment models present white-space opportunity, combining on-premises HIPAA controls with cloud analytics. Position through APRA CPS 234 compliance bundling to shortcut procurement qualification. For Investors and Strategic Acquirers: Capital is best deployed toward managed detection and response specialists with recurring revenue concentration above product-centric vendors facing margin compression. Long-term viability hinges on zero-trust architecture certification breadth rather than point-product depth. Watch NIST post-quantum cryptographic standardization timing as inflection indicator for quantum-resistant encryption module demand.| Strategic Initiative | Industry Significance |
|---|---|
| Zero-Trust Architecture Certification | FedRAMP authorization unlocks United States federal replacement demand displacing perimeter-centric legacy systems. |
| Managed Detection and Response Expansion | Recurring revenue concentration captures mid-market enterprises lacking internal security operations center capabilities. |
| Quantum-Resistant Encryption Preview | Early-mover positioning ahead of NIST standardization secures government pilot contracts and procurement preference. |
| Cloud-Native Platform Integration | Sub-100-millisecond threat correlation latency satisfies enterprise RFP specifications compressing hardware-bound alternatives. |
| Healthcare Hybrid Deployment Development | HIPAA-aligned architectural flexibility addresses protected health information control requirements extending cloud analytics. |
Study Parameters
Operator-level perspectives from chief information security officers, federal procurement officers, managed security service provider executives, and healthcare IT directors anchored the qualitative base. Primary interviews combined with secondary validation against SEC 10-K filings, FedRAMP authorization databases, NIST publication repositories, and cyber insurance underwriting guidelines. Bottom-up deployment model sizing triangulated against top-down regulatory mandate tracking.
Sensitivity analysis tested forecast outputs against alternative zero-trust mandate adoption timelines and quantum-resistant encryption standardization delays. Segmentation dimensions spanned product architecture, deployment model, end-user vertical, and threat vector intensity across the modeling period. CAGRs derived from historical procurement cycle analysis projected against regulatory compliance deadline clustering. Forecast inputs incorporated federal budget authorization patterns and cyber insurance policy renewal conditions.
The analysis sits within stated boundaries; outcomes outside sustained federal zero-trust funding or accelerated NIST post-quantum standardization would require recalibration. Forecasts reflect assumptions regarding cloud migration velocity and managed security service penetration rates. Geopolitical fragmentation of cross-border data residency regimes poses revision risk to cloud-based deployment projections. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Speed Limit Radar Signs Market
Security and Surveillance
Destructible Security Labels Market
Security and Surveillance
Global Physical Security Software Market
Security and Surveillance
Cargo Container X-Ray Inspection Systems Market
Security and Surveillance
Security Services Market
Security and Surveillance
Smart Security in Healthcare Market
Security and Surveillance
Latin America Security Services Market
Security and Surveillance
Europe Border Security Market
Security and Surveillance
Global Law Enforcement Software Market
Security and Surveillance
Prescriptive Security Market
Security and Surveillance
Explosive Trace Detection Market
Security and Surveillance
Security System Integrators Market
Security and Surveillance
Global Security Advisory Services Market
Security and Surveillance
Resale Authentication Services Market
Security and Surveillance
Airport Baggage Screening Systems Market
Security and Surveillance
Proactive Security Market