
 North America Security Testing Market | 2026-2036
North America Security Testing Market Size, Share, and Industry Trends Forecast 2026-2036
North America Security Testing Market Foresight
Managed detection and response revenue is fragmenting across specialized security testing providers as enterprises unbundle comprehensive cybersecurity contracts. Bishop Fox leverages its offensive security expertise to anchor premium penetration testing engagements for Fortune 500 clients. Coalfire competes aggressively in compliance-driven assessment work, particularly for organizations navigating FedRAMP and CMMC requirements. NetSPI sustains technology leadership through its continuous attack surface management platform, differentiating from episodic testing models.
North America Security Testing encompasses systematic evaluation of information systems, networks, and applications to identify exploitable vulnerabilities before malicious actors discover them. The discipline employs methodologies including automated vulnerability scanning, manual penetration testing, and adversary simulation against frameworks such as MITRE ATT&CK to validate defensive controls. Cloud-Based deployment models are capturing disproportionate growth as distributed workforces eliminate traditional network perimeters and accelerate SaaS adoption. AI-Driven technology segments attract concentrated R&D investment as machine learning enables dynamic threat modeling and reduces false-positive rates in vulnerability assessment workflows.
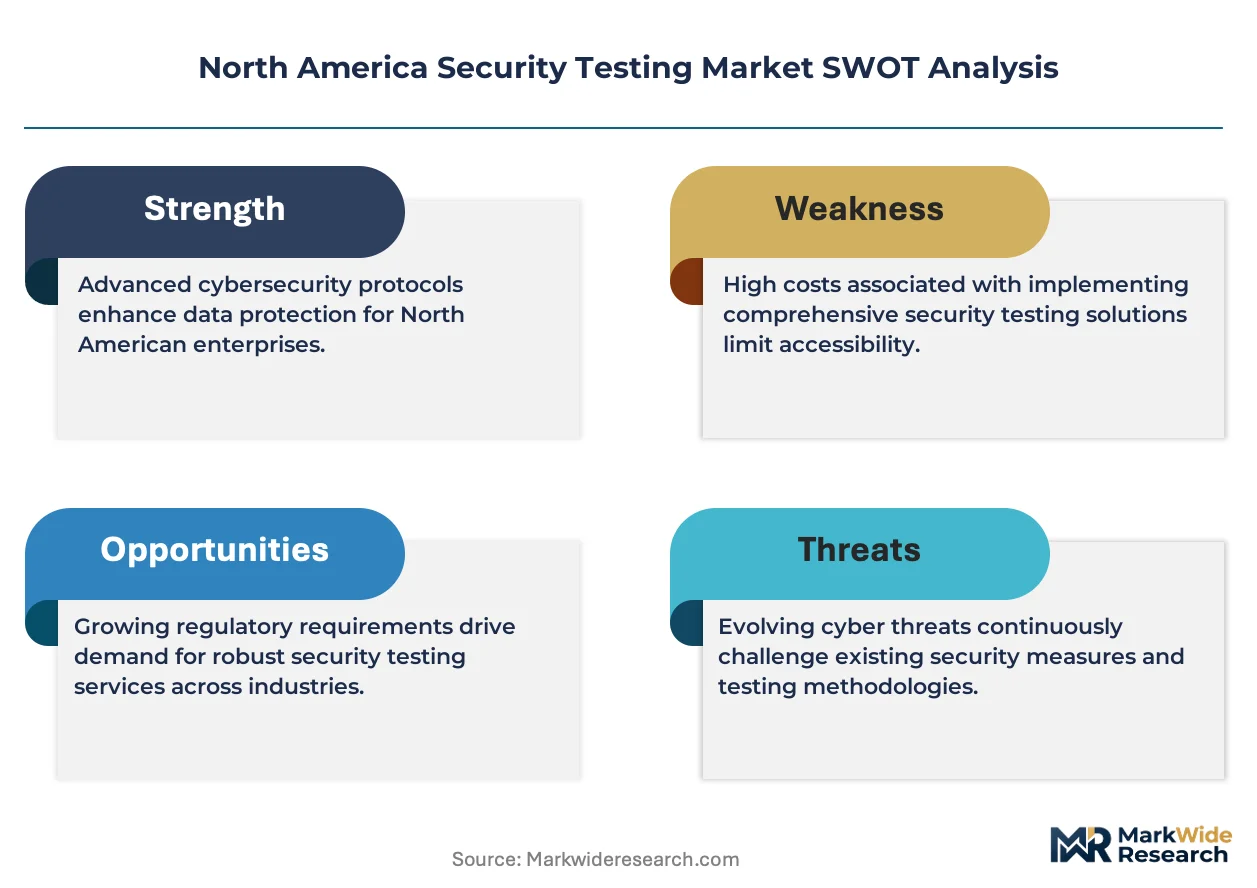
The US SEC, NIST, and Canada's OSFI mandate structured security validation through disclosure requirements, risk management frameworks, and supervisory guidance that directly expand addressable testing budgets. HIPAA security rule enforcement and state-level privacy statutes in California and New York further institutionalize recurring assessment obligations across healthcare and consumer-facing industries. Stakeholders must monitor how evolving AI governance standards reshape testing scope and whether automated tooling commoditizes baseline vulnerability assessment faster than specialized providers can elevate advisory margins.
Market Dynamics
The US SEC's cybersecurity disclosure rules are compressing procurement cycles for independent security validation as publicly traded firms race to demonstrate compliance before audit deadlines.
Growth Catalysts
- SEC Mandate Enforcement:The US Securities and Exchange Commission's disclosure requirements compel Fortune 500 firms to commission third-party penetration testing and vulnerability assessments, directly expanding addressable service budgets across the BFSI sector.
- Cloud Migration Acceleration:Distributed workforces and SaaS adoption are eliminating traditional network perimeters, forcing organizations to validate cloud-native architectures through continuous attack surface monitoring rather than episodic testing.
- CMMC and FedRAMP Compliance:Defense contractors and federal suppliers face mandatory third-party assessment requirements, creating recurring revenue streams for authorized testing providers serving the government contracting ecosystem.
Market Restraints
- Certified Talent Scarcity:The shallow pool of OSCP-certified penetration testers and CISSP-qualified assessors constrains service provider capacity, inflating bill rates and extending project backlogs across the industry.
- Tooling Commoditization:Automated vulnerability scanners from open-source projects and low-cost vendors are compressing margins on baseline assessment work, forcing providers to differentiate through manual expertise.
- California Privacy Statutes:The California Consumer Privacy Act and subsequent amendments impose complex data handling requirements on testing providers, increasing compliance overhead and limiting cross-border service delivery.
Strategic Opportunities
- AI Governance Standards:Emerging frameworks for artificial intelligence risk management are creating demand for specialized testing protocols that validate model security, bias controls, and adversarial robustness in machine learning pipelines.
- Healthcare Vertical Expansion:HIPAA security rule enforcement and ransomware targeting of hospital networks are institutionalizing recurring assessment obligations across regional health systems and medical device manufacturers.
- Adversary Simulation Convergence:The integration of breach and attack simulation platforms with continuous validation workflows is enabling subscription-based revenue models that displace traditional project-based penetration testing.
Industry Challenges
- Legacy System Integration:Mainframe and on-premise infrastructure at established financial institutions resist automated testing tooling, requiring costly manual workarounds that erode project profitability.
- False Positive Management:Alert fatigue from automated scanning tools burdens security operations teams, demanding human analyst triage that scales linearly with client environment complexity.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | North America Security Testing Market |
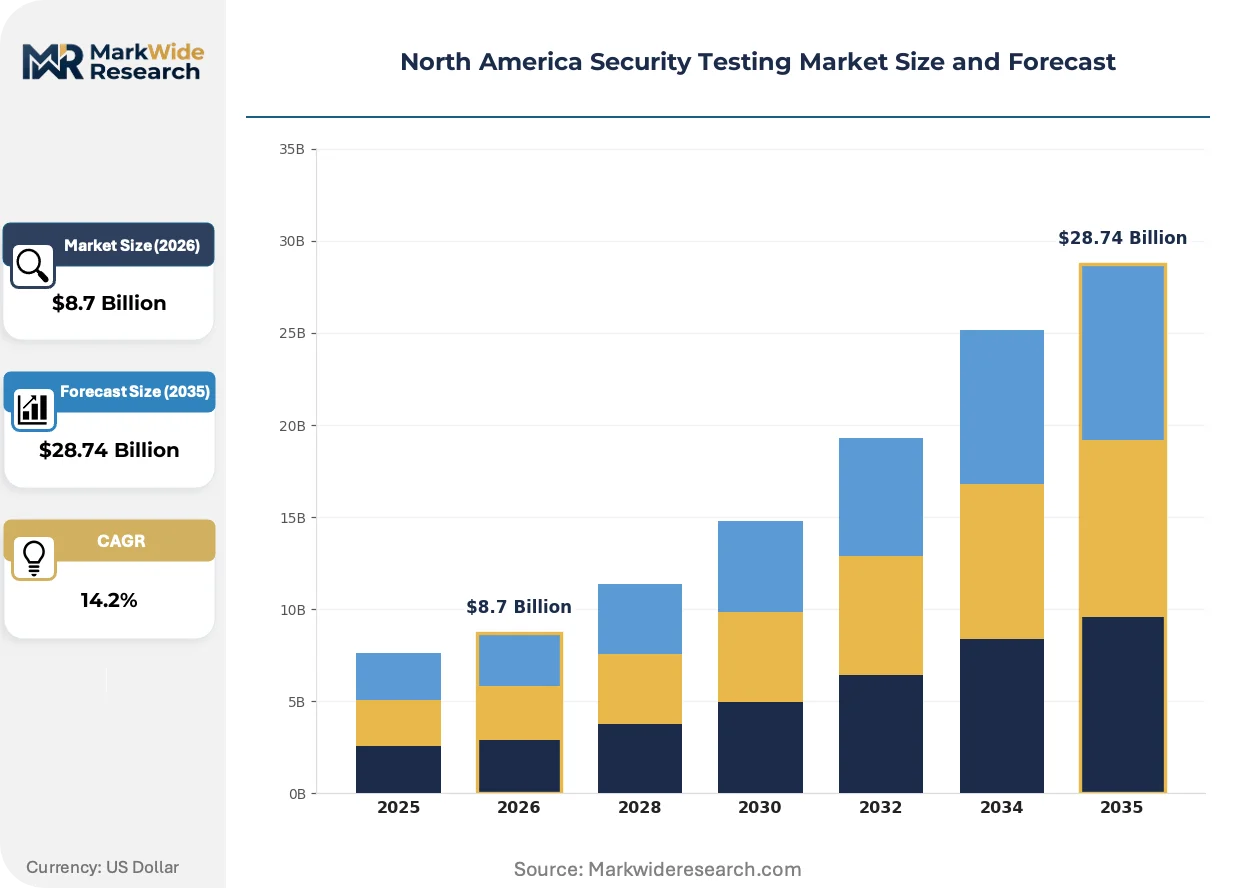
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $28.74 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Pentest, Vulnerability Assessment, Compliance Testing, Mobile Security Deployment Model: On-Premises, Cloud-Based, Hybrid, Managed Services End User: Healthcare, BFSI, Retail, Telecommunications Technology: AI-Driven, Automation Tools, Continuous Monitoring, IoT Security |
| Companies Covered | IOActive, DeepStrike, Bishop Fox, Genetec Inc, SpecterOps, Coalfire, Black Hills Information Security, Kastle Systems, NetSPI, Others |
| Regions Covered | North America: US, Canada, Mexico |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
North America Security Testing Market Shifts & Advancements
Security testing delivery models are fragmenting as buyers unbundle comprehensive managed security contracts in favor of specialized, outcome-defined engagements with independent validation firms.
Cloud-native penetration testing platforms are virtualizing the traditional consultant-client engagement model. These environments enable remote, scalable access to target systems without on-site presence. Mid-market enterprises and technology startups are adopting these platforms fastest, drawn by reduced scheduling friction and faster report turnaround. The virtualization of testing infrastructure is compressing geographic barriers that previously concentrated engagements in major metropolitan corridors.
The US SEC's cybersecurity disclosure rules are mandating independent validation of material incident response capabilities and board-level risk oversight. Public companies must now document third-party testing of their security controls in annual filings. This regulatory pressure is most acute among financial services firms in New York and technology companies in California, which are expanding recurring assessment contracts to satisfy audit trail requirements.
Enterprise buyers are fragmenting their security testing spend across multiple specialized providers rather than consolidating with single-vendor managed detection and response contracts. Chief information security officers are unbundling penetration testing, red team exercises, and compliance assessments to access deeper expertise in each discipline. This pattern is most visible among Fortune 500 firms in the BFSI sector, where procurement teams now maintain rosters of pre-qualified testing specialists rather than sole-source relationships.
North America Security Testing Market Segmentation
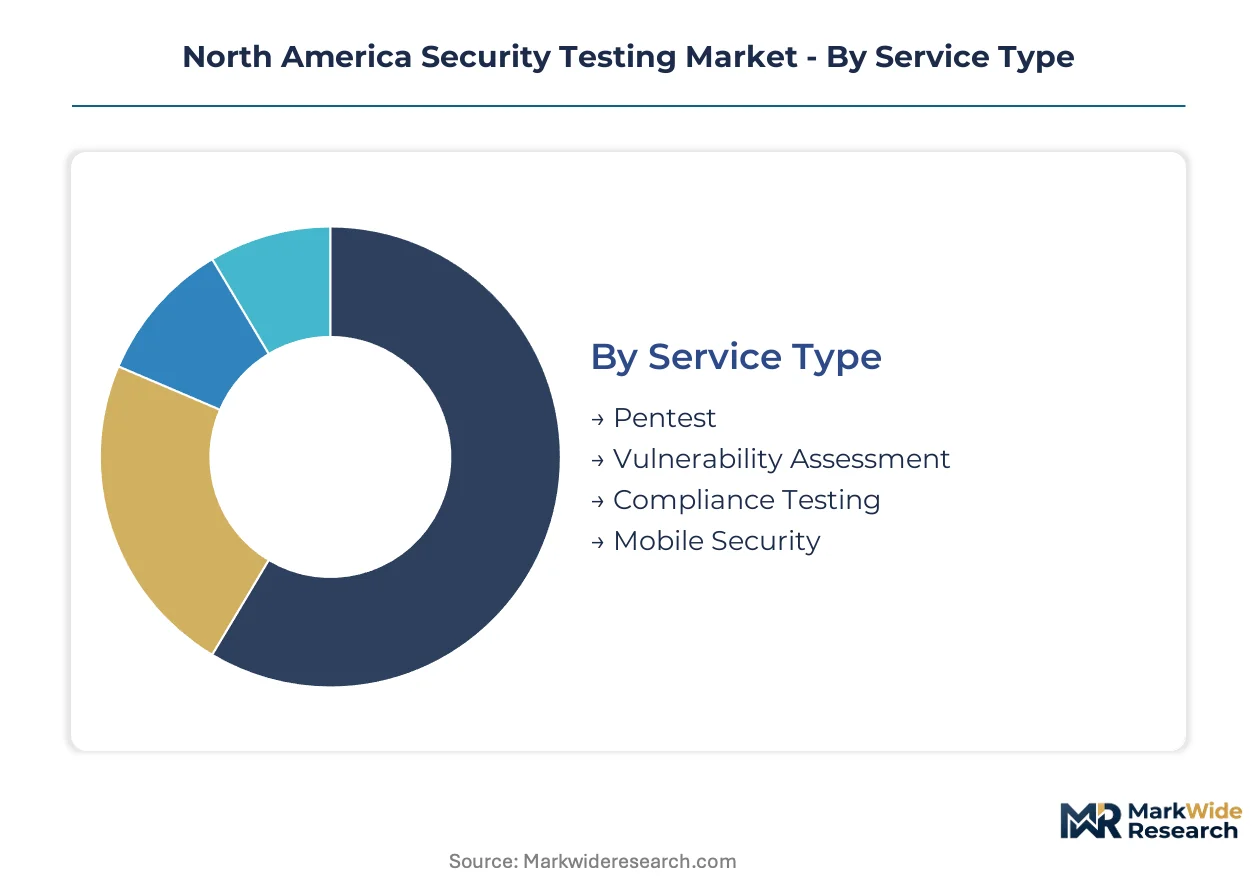
Security testing buyers in North America fragment their procurement across multiple specialized service categories rather than consolidating with single-vendor solutions. Segmentation reveals how regulatory mandates, cloud migration patterns, and talent scarcity reshape demand concentration across service types and deployment models.
Service Type:
Cost tier differentiation separates commoditized vulnerability scanning from premium manual penetration testing engagements.
- Pentest:Manual exploitation exercises conducted by certified ethical testers simulate real-world adversary tactics against production systems. Financial services firms in New York and defense contractors across Virginia commission recurring red team engagements to satisfy SEC disclosure and CMMC audit requirements.
- Vulnerability Assessment:Automated scanning protocols identify known CVEs and misconfigurations across network perimeters and cloud assets. Mid-market enterprises in Texas and Illinois adopt these services fastest as baseline compliance documentation for cyber insurance underwriting.
- Compliance Testing:Structured control validation against HIPAA, PCI-DSS, and FedRAMP frameworks produces audit-ready evidence packages.
- Mobile Security:Specialized iOS and Android application testing addresses BYOD policies and mobile banking proliferation.
Pentest commands the established base. The steepest expansion runs through Vulnerability Assessment.
Deployment Model:
Application architecture preferences divide buyers between legacy on-premise validation and cloud-native continuous monitoring platforms.
- Cloud-Based:SaaS-delivered testing platforms eliminate hardware provisioning delays and enable elastic scaling across distributed development teams. Technology companies in California's Silicon Valley and Seattle corridor deploy these solutions to validate microservices architectures without traditional network access constraints.
- On-Premises:Air-gapped testing appliances satisfy classified environment requirements and data sovereignty mandates. Federal agencies and critical infrastructure operators in Washington DC and Colorado Springs mandate these deployments for systems handling controlled unclassified information.
- Hybrid:Mixed architectures accommodate phased cloud migrations and mainframe coexistence scenarios.
- Managed Services:Outsourced security operations centers deliver continuous validation through subscription consumption models.
On-Premises retains the regulated institutional base. Cloud-Based platforms are climbing the fastest as SaaS-native enterprises displace episodic testing cycles.
End User:
Customer type concentration reflects sector-specific regulatory pressure and threat actor targeting patterns.
- BFSI:Banks, insurers, and payment processors face layered compliance obligations from SEC disclosure rules, PCI-DSS mandates, and state-level privacy statutes. Institutions in Manhattan and Charlotte maintain the largest recurring assessment budgets as ransomware groups prioritize financial data exfiltration.
- Healthcare:Hospital networks and medical device manufacturers navigate HIPAA security rule enforcement and FDA cybersecurity guidance. Regional health systems in Florida and Ohio expand testing spend following high-profile ransomware disruptions to patient care operations.
- Retail:E-commerce platforms and brick-and-mortar chains validate payment card environments against skimming and Magecart attacks.
- Telecommunications:5G infrastructure operators and broadband providers assess supply chain vulnerabilities and subscriber data protection controls.
BFSI commands the established base. Healthcare is gaining share fastest as ransomware targeting accelerates assessment obligations across regional hospital networks.
Technology:
Maturity gradients separate experimental AI-driven tooling from proven automation platforms in buyer procurement decisions.
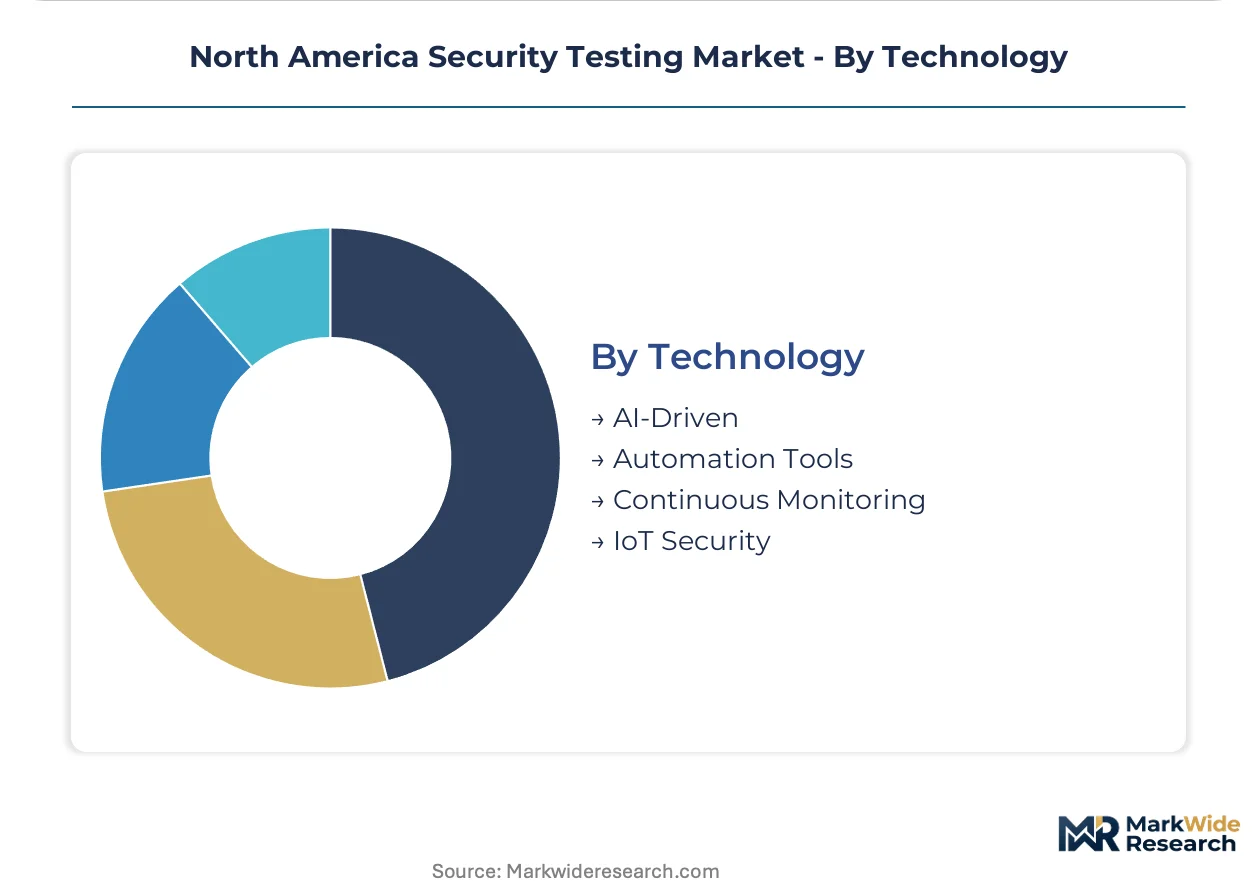
- AI-Driven:Machine learning models prioritize vulnerability exploitation paths and reduce false-positive rates through pattern recognition across historical breach data. Venture-backed cybersecurity vendors in San Francisco and Boston deploy these capabilities to differentiate from legacy scanner vendors.
- Continuous Monitoring:Attack surface management platforms discover shadow IT assets and validate remediations through persistent agent deployment. Fortune 500 technology firms adopt these solutions to replace quarterly penetration testing with always-on visibility.
- Automation Tools:Script-based scanning and orchestration frameworks accelerate baseline assessment throughput.
- IoT Security:Specialized protocols address embedded device firmware, wireless communication stacks, and industrial control system interfaces.
Automation Tools command the established base. Continuous Monitoring is expanding most quickly as CISOs unbundle project-based testing for subscription validation models.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Mid-market buyers in the Great Lakes and Southwest regions demonstrate the highest price elasticity, squeezing margins on standardized vulnerability assessments. Enterprise purchasers in Manhattan and Silicon Valley show minimal price sensitivity for premium penetration testing and adversary simulation services.
United States
Defense contractors across Virginia and Maryland drive demand for CMMC-mandated third-party assessments ahead of contract eligibility deadlines. The SEC's cybersecurity disclosure rules compel Fortune 500 firms to commission independent validation of material security controls. Technology clusters in California's Silicon Valley and Seattle anchor the steepest adoption of continuous attack surface management platforms.
Canada
Financial institutions in Toronto and Vancouver expand security testing budgets to satisfy OSFI supervisory guidance on technology risk management. The Office of the Superintendent of Financial Institutions mandates structured validation of cyber resilience frameworks for federally regulated banks. Montreal's aerospace and defense suppliers pursue FedRAMP-aligned assessments to access US federal procurement opportunities.
Mexico
Maquiladora operations in Baja California and Chihuahua commission compliance testing to satisfy US customer supply chain security requirements. The country's national data protection authority enforces breach notification obligations that elevate assessment priorities for consumer-facing enterprises. Guadalajara's technology corridor attracts vulnerability assessment providers serving nearshore software development clients.
North America Security Testing Market Competitive Landscape
Capability concentration sits with boutique offensive security specialists; scale advantage sits with compliance-focused assessment platforms with federal authorization credentials. The vendor base stratifies across three tiers: premium penetration testing boutiques commanding premium bill rates, mid-market compliance automation platforms, and commodity vulnerability scanning tools. Two strategic archetypes dominate: adversary simulation specialists differentiating through manual expertise, and authorized assessors capturing recurring FedRAMP and CMMC revenue streams. Consolidation pressure is accelerating through strategic acquisitions of specialized boutiques by platform players, while technology licensing agreements proliferate between scanning engine vendors and managed security service providers.
Within the adversary simulation tier, Bishop Fox and SpecterOps occupy positions exemplifying premium manual penetration testing expertise. Coalfire anchors the compliance-driven assessment segment, representing the archetype of federal-authorized testing providers capturing recurring regulatory-mandated revenue. These three firms illustrate how market positioning fragments across offensive security depth versus audit-ready documentation capabilities.
| Leading Market Players |
|---|
| IOActive |
| DeepStrike |
| Bishop Fox |
| Genetec Inc |
| SpecterOps |
| Coalfire |
| Black Hills Information Security |
| Kastle Systems |
| NetSPI |
| Others |
Supply & Pricing Matrix
Virginia's defense contracting corridor concentrates CMMC-authorized assessment capacity, translating certification scarcity into premium pricing power for compliance-driven engagements. The shallow pool of OSCP-certified penetration testers and FedRAMP-accredited assessors constrains service delivery across the continent, forcing buyers into extended procurement cycles and elevating bill rates for qualified providers.
Pricing Analysis
Subscription-based continuous monitoring contracts now drive lifetime value, displacing episodic project fees. Three-tier pricing structure across premium manual penetration testing, standard compliance automation, and economy vulnerability scanning reflects certification grade and manual expertise depth. Cost compression in baseline automated assessment intensifies because open-source tooling erodes scanner margins. Mid-market enterprises in Texas and Illinois exhibit highest price elasticity, while Manhattan financial institutions show minimal sensitivity for adversary simulation services.
Supply Chain Analysis
Extended payment terms from enterprise buyers strain boutique testing providers, accelerating consolidation toward platform players with stronger balance sheets. Talent supply concentrates in the United States, Canada, and the United Kingdom as immigration restrictions limit cross-border service delivery. The supply chain rests on certified human capital, cloud infrastructure subscriptions, and proprietary scanning engines. Single-source vulnerability in OSCP certification pipelines threatens capacity expansion. Distribution runs through direct enterprise sales teams and hyperscaler marketplace integrations.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The shallow bench of certified offensive security practitioners creates persistent bottlenecks, elevating acquisition premiums for boutiques with credentialed teams. Organizations that control talent pipelines or certification pathways capture disproportionate margin.
For Market Incumbents: Insulate premium positioning by acquiring specialized boutiques in adversary simulation and red team disciplines before platform competitors consolidate remaining targets. Invest in captive OSCP training pipelines to reduce bill-rate inflation from external talent competition. CMMC authorization moats and FedRAMP credentials represent defensible assets against automation-driven commoditization. For New Entrants and Emerging Players: Build out continuous attack surface management platforms targeting mid-market SaaS enterprises in Seattle and Austin that have outgrown quarterly penetration testing but lack Fortune 500 security budgets. Healthcare verticals in Florida and Ohio present penetrable white space as ransomware targeting accelerates HIPAA-mandated assessment obligations. Partner with cyber insurance carriers to embed validation services into policy underwriting workflows. For Investors and Strategic Acquirers: Long-term, this sits as a regulatory-complexity play because SEC disclosure rules, CMMC deadlines, and HIPAA enforcement institutionalize recurring third-party validation demand regardless of economic cycles. Target acquisition archetypes include FedRAMP-authorized assessors with defense contractor relationships and boutiques with demonstrated adversary simulation expertise. Monitor AI governance standard emergence as inflection indicator for specialized testing protocol expansion.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Consolidates scarce OSCP-certified talent pools into platform delivery models. |
| Platform Integration | Embeds continuous monitoring into hyperscaler marketplaces for frictionless procurement. |
| Geographic Expansion | Establishes CMMC-authorized presence in Colorado Springs and Huntsville defense clusters. |
| Strategic Partnership | Aligns boutique penetration testing with cyber insurance carrier validation requirements. |
| Product Launch | Introduces AI model security testing protocols ahead of NIST AI risk management framework finalization. |
Research Methodology
Demand-side practitioners and supply-side operators were both consulted through structured primary interviews with CISOs at Fortune 500 BFSI institutions, penetration testing firm principals, FedRAMP authorization leads, healthcare compliance officers, and cyber insurance underwriters. Secondary validation drew from SEC cybersecurity disclosure filings, NIST framework documentation, CMMC assessment methodology publications, and healthcare breach notification databases. Bottom-up service provider revenue estimates triangulated against top-down regulatory-mandated spending requirements.
Calibration against historical contract values and disclosed procurement volumes anchored the analytical framework across the projection horizon. Segmentation dimensions modeled include service type, deployment architecture, end-user vertical, technology maturity tier, and geographic regulatory cluster. CAGRs were derived from regression analysis of compliance deadline impacts and cloud migration velocity. Forecast inputs incorporated OSCP certification pipeline constraints and FedRAMP authorization queue backlogs.
Sensitivities concentrate around CMMC implementation timeline shifts, AI governance standard emergence, and automated tooling commoditization rates. Forecasts reflect documented assumptions regarding regulatory enforcement continuity and talent supply elasticity. Macroeconomic contraction affecting cyber insurance underwriting, regulatory rollback of disclosure requirements, or breakthrough autonomous vulnerability remediation would prompt revision.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Resale Authentication Services Market
Security and Surveillance
North America Urban Security Screening Market
Security and Surveillance
Europe Baggage and Parcel Screening Market
Security and Surveillance
Europe Cargo and Vehicle Screening Market
Security and Surveillance
Forensic Technologies Market
Security and Surveillance
Air Cargo Security Equipment Market
Security and Surveillance
Alarm Monitoring Software Market
Security and Surveillance
Situational Awareness System Market
Security and Surveillance
Global Bot Security Market
Security and Surveillance
Alarm Monitoring [Central Stations] Software Market
Security and Surveillance
Global Cargo Inspection Market
Security and Surveillance
Explosive Trace Detection Market
Security and Surveillance
Security Analytics Market
Security and Surveillance
Home Security Solution Market
Security and Surveillance
Home Security Market
Security and Surveillance
Global Security Advisory Services Market