
 Open RAN Security Market | 2026-2036
Open RAN Security Market Size, Share, and Industry Trends Forecast 2026-2036
Open RAN Security Market Analytics
The capital-intensity divergence between hardware-centric incumbents and software-native challengers is unwinding traditional competitive moats in Open RAN security. NEC Corporation leverages its long-standing relationships with NTT and other Japanese operators to sustain integration advantages across multi-vendor environments. Mavenir competes through cloud-native software stacks that reduce dependency on proprietary silicon, while Samsung Electronics anchors its position through end-to-end portfolio breadth spanning radios to core security orchestration.
Open RAN security encompasses the cryptographic, access-control, and threat-detection mechanisms that protect disaggregated radio access networks built on open interfaces such as O-RAN Alliance specifications. These systems enforce confidentiality and integrity across the fronthaul, midhaul, and RAN intelligent controller layers that separate baseband processing from radio units. Cloud-based deployment models now attract the fastest-growing investment as operators seek elastic scalability for security functions that must adapt to dynamic network slicing workloads. Threat intelligence solutions command disproportionate margin pools because real-time adversary tracking requires continuous data feeds and specialized analyst labor that resists commoditization. Consulting services retain structural importance during early deployment phases as enterprises and government agencies lack internal expertise to architect zero-trust perimeters across heterogeneous vendor environments.
The O-RAN Alliance's security specifications, the FCC's supply chain rulemakings for communications equipment, and the EU's Cybersecurity Act collectively reshape product requirements and vendor eligibility across major addressable markets. National regulators in Germany through the BSI and in Japan through MIC now mandate source-code audits and hardware provenance documentation for critical network components. Stakeholders must monitor how fragmentation between regional certification regimes affects interoperability timelines and procurement costs for multi-country deployments.
Market Dynamics
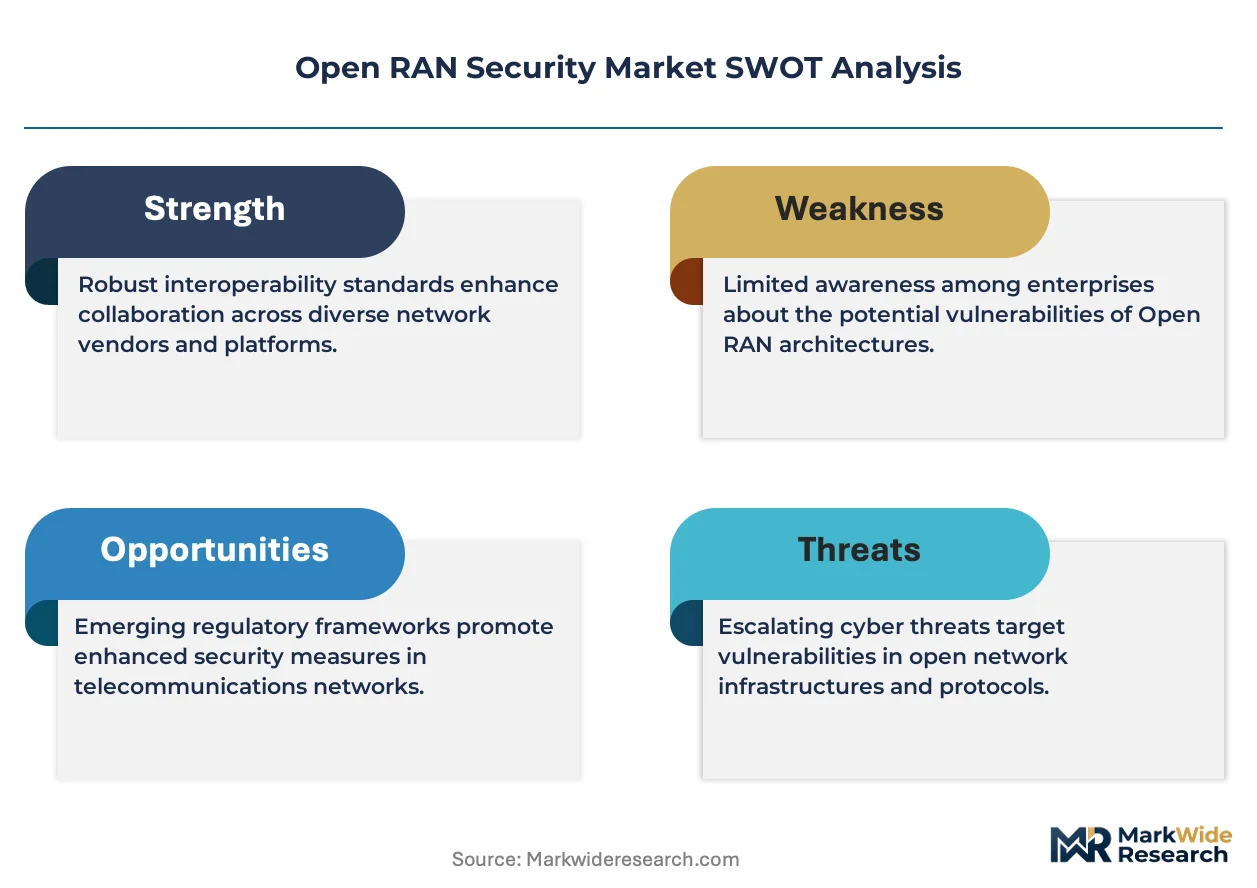
Regulatory fragmentation across the United States, Germany, and Japan is forcing vendors to maintain parallel certification tracks for Open RAN security components, elevating compliance costs while compressing time-to-market windows for multi-country deployments.
Growth Catalysts
- Supply chain integrity mandates:The FCC's equipment authorization rules and BSI's hardware provenance requirements in Germany compel operators to source security-audited components, expanding addressable demand for certified solutions.
- Cloud-native architecture migration:Tier-one mobile operators are containerizing security functions to achieve elastic scaling across network slices, creating pull for software-defined protection layers.
- Japan:MIC's source-code audit requirements for critical infrastructure accelerate procurement of transparent, disaggregated security stacks by NTT and regional carriers.
Market Restraints
- Silicon supply concentration:Dependency on Taiwan-based semiconductor fabrication creates vulnerability for hardware-dependent security appliances, constraining vendor margin flexibility.
- Interoperability certification costs:O-RAN Alliance security specifications require extensive multi-vendor testing, imposing fixed overhead that disadvantages smaller systems integrators.
- Technical debt in legacy RAN:Brownfield operators face sunk-cost barriers when migrating proprietary encryption schemes to open-interface architectures, slowing replacement cycles.
Strategic Opportunities
- Managed security services:German operators lacking internal zero-trust expertise present white space for outsourced RAN security operations centers serving multi-vendor environments.
- AI-driven threat detection:Convergence of machine learning inference at the edge with O-RAN RIC architectures enables real-time anomaly detection without core network dependency.
- United States:Rural broadband infrastructure programs create procurement channels for cost-optimized Open RAN security stacks outside tier-one urban deployments.
Industry Challenges
- Multi-vendor integration complexity:Disaggregated fronthaul encryption requires orchestration across radio unit, distributed unit, and centralized unit suppliers with incompatible key management protocols.
- Specialized talent scarcity:Shortage of engineers proficient in both 3GPP security specifications and cloud-native deployment patterns constrains deployment velocity for systems integrators.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Open RAN Security Market |
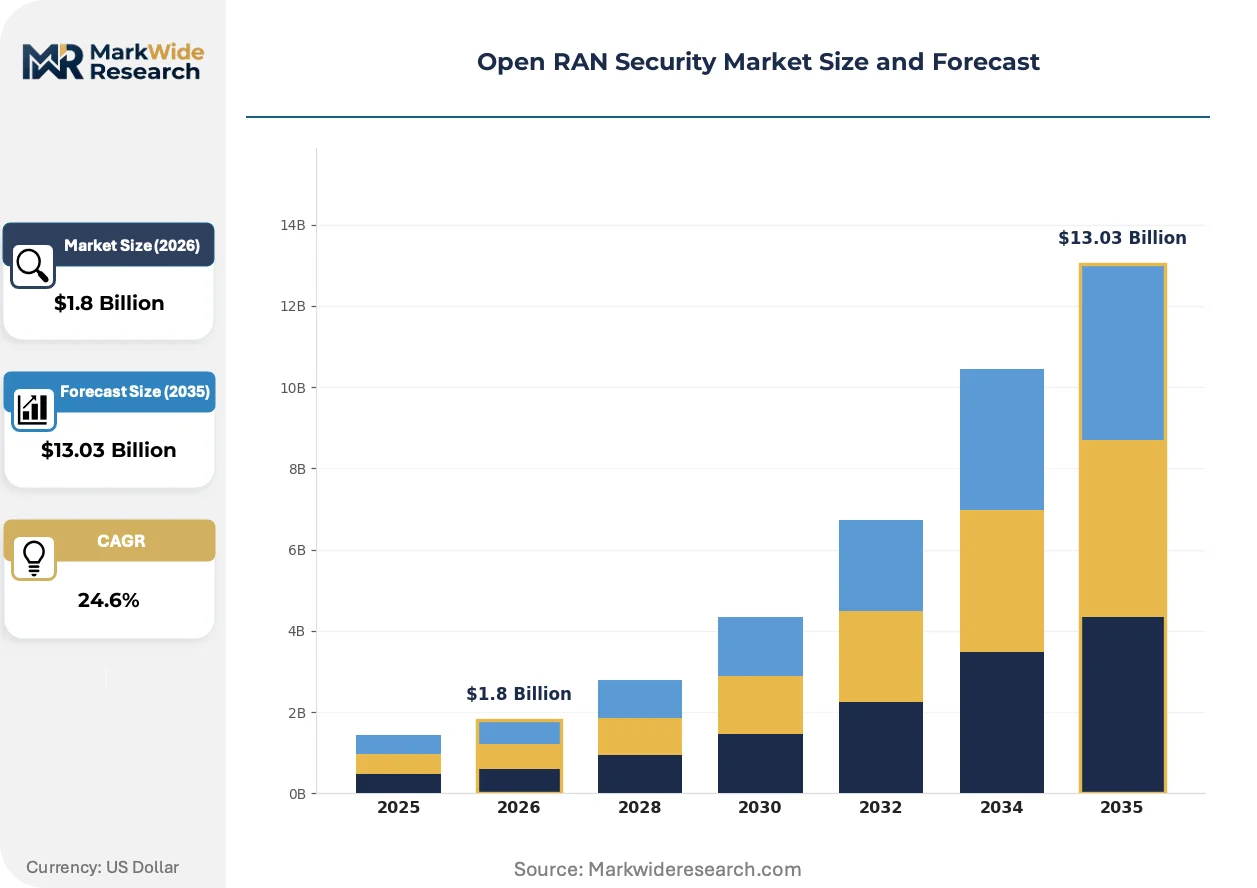
| Market Size in 2026 | $1.8 Billion |
| Market Size in 2035 | $13.03 Billion |
| CAGR (2026 – 2036) | 24.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment Model: On-Premise, Cloud-Based, Hybrid, Edge Computing Service Type: Consulting, Integration, Maintenance, Security Management End User: Telecom Operators, Enterprises, Government Agencies, Managed Service Providers Solution: Firewalls, Intrusion Detection Systems, Encryption, Threat Intelligence |
| Companies Covered | NEC Corporation, Ericsson, Nokia Corporation, Juniper Networks, Inc., ZTE Corporation, Mavenir, Fujitsu Limited, Broadcom, Inc., Samsung Electronics Co., Ltd., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Open RAN Security Market Evolving Landscape
Zero-trust architecture principles are penetrating radio access networks, compressing traditional perimeter-based security models and demanding continuous authentication across disaggregated infrastructure layers.
Confidential computing using hardware-based trusted execution environments is displacing software-only encryption for sensitive RAN functions. Tier-one operators in Germany and Japan are piloting these enclaves for key management and subscriber authentication. This technology is displacing conventional hypervisor-based isolation, reducing attack surface for multi-tenant edge deployments.
The EU Cybersecurity Act's Common Criteria certification scheme is mandating standardized security evaluations for network equipment across member states. Vendors must now maintain parallel certification tracks against both European and national German BSI requirements. Component suppliers serving pan-European operators face compressed development timelines to satisfy overlapping compliance regimes.
Security function disaggregation is altering procurement patterns as operators unbundle hardware appliances from software licenses. Japanese carriers now source encryption accelerators separately from policy engines, disrupting traditional bundled pricing. This unbundling is most pronounced in cloud-native deployments where Kubernetes-based security microservices replace monolithic platforms.
Open RAN Security Market Segmentation
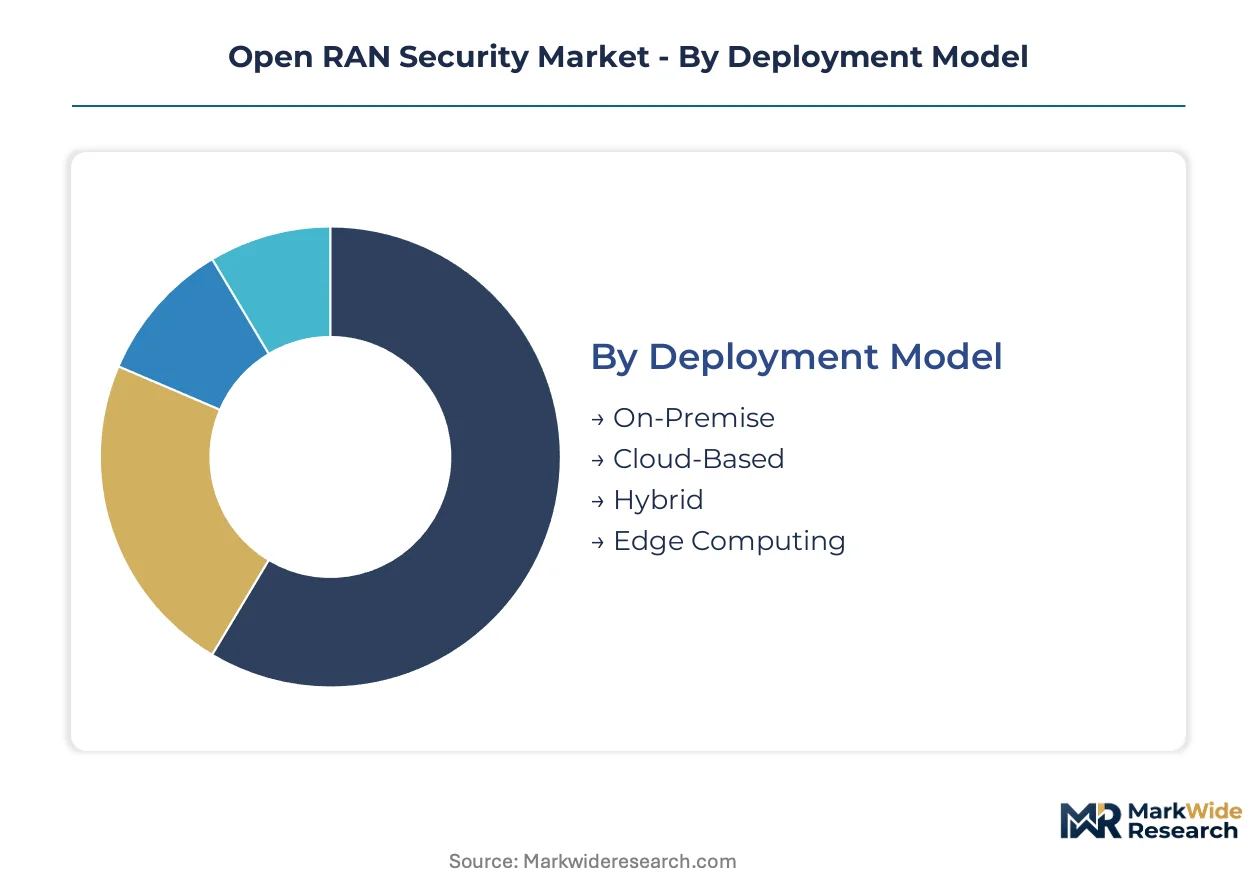
Open RAN security procurement patterns diverge sharply across deployment architectures and buyer sophistication, with regulatory mandates in Germany, Japan, and the United States reshaping how vendors prioritize feature roadmaps and certification investments.
Deployment Model:
Regulatory differentiation across jurisdictions favors cloud elasticity in some markets while mandating on-premise sovereignty in others.
- Cloud-Based:Containerized security functions deploy across network slices with Kubernetes orchestration, enabling elastic scaling for dynamic traffic loads. German operators under BSI cloud sovereignty guidelines and Japanese carriers responding to MIC data localization rules drive concentrated demand for sovereign cloud configurations.
- On-Premise:Dedicated hardware appliances enforce encryption and access control within operator-controlled facilities, satisfying FCC supply chain integrity requirements for critical infrastructure. United States rural broadband programs specify on-premise stacks to minimize external dependency.
- Hybrid:Split workloads between private facilities and managed cloud instances balance control with operational flexibility.
- Edge Computing:Distributed security functions at radio sites reduce latency for real-time threat response.
Established volume favors On-Premise; emerging adoption favors Cloud-Based.
Service Type:
Cost tier stratification separates high-touch advisory engagements from automated operational layers.
- Security Management:Continuous monitoring and incident response across multi-vendor RAN environments requires specialized analyst labor and proprietary threat intelligence feeds. Tier-one operators in Germany outsource these functions to compensate for internal zero-trust expertise gaps.
- Consulting:Architecture design and compliance roadmap development command premium pricing during initial deployment phases. Japanese government agencies engage consultants to navigate MIC source-code audit preparation.
- Integration:Multi-vendor orchestration across disaggregated fronthaul layers demands rare cross-functional engineering capability.
- Maintenance:Patch management and certificate lifecycle operations stabilize long-term vendor relationships.
Revenue concentration sits with Security Management; margin expansion favors Consulting.
End User:
Customer type determines procurement sophistication and contract structure complexity.
- Telecom Operators:Mobile network carriers with nationwide infrastructure deploy end-to-end security stacks across thousands of cell sites, driving standardization requirements. NTT and regional Japanese carriers accelerate procurement following Release 18 specification maturation.
- Government Agencies:Defense and critical infrastructure authorities mandate hardware provenance documentation and source-code audits. United States federal programs specify Open RAN security for secure communications backbone replacement.
- Enterprises:Private 5G deployments for manufacturing and logistics facilities require scaled-down security architectures.
- Managed Service Providers:Aggregated demand from mid-market clients creates volume channels for standardized offerings.
Contract value concentrates with Telecom Operators; growth velocity favors Government Agencies.
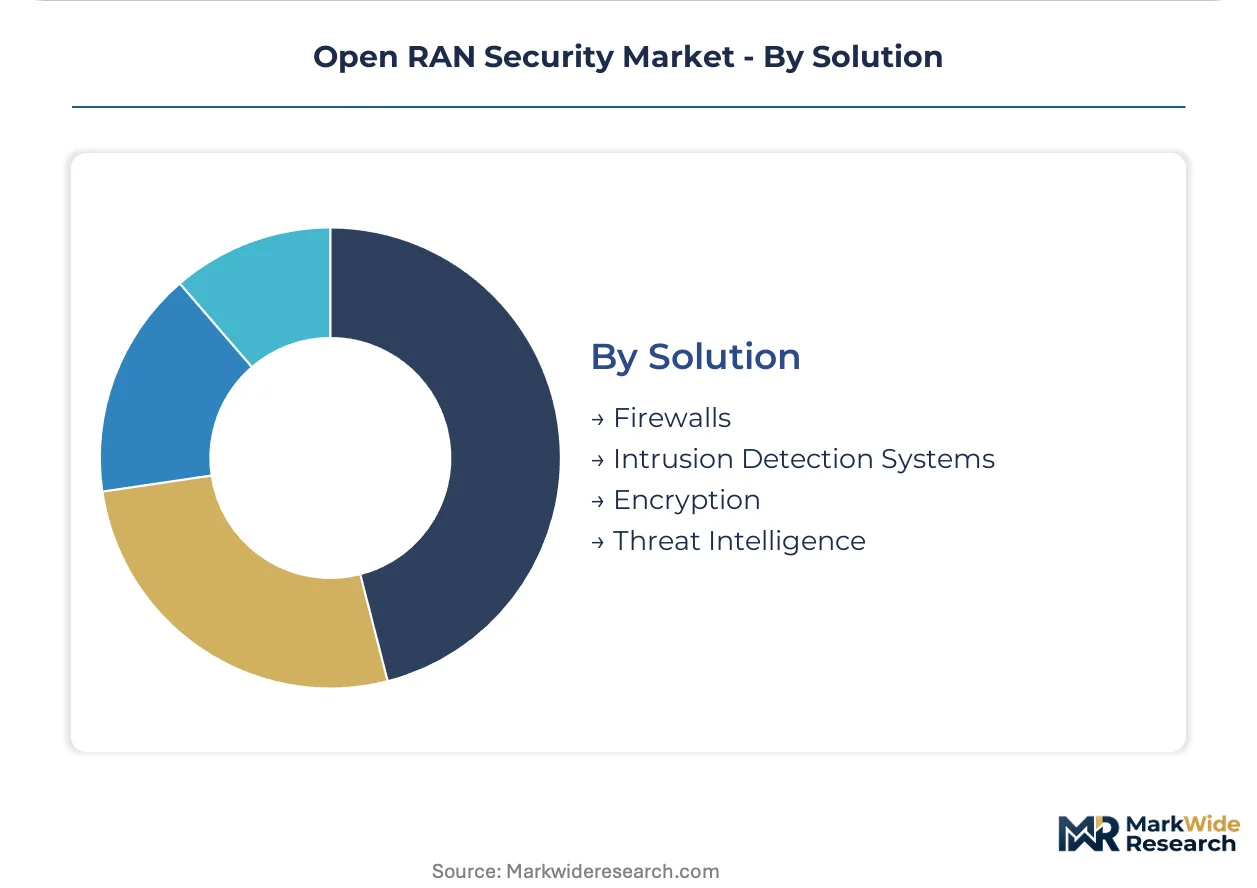
Solution:
Technology maturity separates commodity protection layers from differentiated intelligence capabilities.
- Threat Intelligence:Real-time adversary tracking and indicator-of-compromise feeds resist commoditization through continuous data acquisition costs and specialized analyst interpretation. German BSI mandates for critical infrastructure monitoring expand addressable demand.
- Encryption:Hardware-accelerated cryptographic processing for fronthaul, midhaul, and RIC interfaces ensures confidentiality across disaggregated layers. Confidential computing pilots in Japan displace software-only implementations.
- Firewalls:Perimeter enforcement between RAN functional splits follows standardized O-RAN Alliance specifications.
- Intrusion Detection Systems:Signature and behavioral analysis engines monitor anomalous traffic patterns across open interfaces.
Margin pools concentrate in Threat Intelligence; deployment scale favors Encryption.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Trade flows in Open RAN security equipment favor net-importing markets with mature telecom infrastructure and stringent certification regimes. Germany, Japan, and the United States absorb the majority of cross-border solution procurement while maintaining domestic integration capabilities.
United States
FCC supply chain integrity mandates and rural broadband infrastructure programs drive procurement of on-premise security stacks. Tier-one carriers deploy disaggregated encryption layers across nationwide 5G rollouts. Silicon Valley and Austin clusters host cloud-native security development for containerized RAN protection.
Germany
BSI hardware provenance requirements and cloud sovereignty guidelines compel operators toward sovereign cloud configurations. Deutsche Telekom and regional carriers source audited components under critical infrastructure monitoring mandates. Berlin and Munich engineering centers concentrate multi-vendor integration expertise for zero-trust RAN architectures.
Japan
MIC source-code audit requirements for critical infrastructure accelerate transparent security stack procurement by NTT and regional carriers. Release 18 specification maturation supports domestic vendor qualification timelines. Tokyo and Osaka metro areas anchor confidential computing pilots for hardware-based trusted execution environments.
South Korea
MFDS-aligned cybersecurity frameworks for network equipment shape procurement specifications for domestic operators. Samsung Electronics anchors end-to-end portfolio development spanning radios to core security orchestration. Seoul Capital Area clusters drive 5G-Advanced security function disaggregation for network slicing workloads.
United Kingdom
Telecom Security Act obligations mandate supply chain diversification away from high-risk vendors in RAN procurement. BT and Vodafone pilot multi-vendor security orchestration under national resilience guidelines. London and Cambridge technology corridors concentrate threat intelligence development for real-time adversary tracking.
Open RAN Security Market Competitive Landscape
Concentration sits with diversified telecom infrastructure incumbents possessing end-to-end portfolio breadth. Hardware-centric vendors maintain integration advantages through long-standing operator relationships, while software-native challengers compete on cloud-native deployment flexibility. Three archetypes dominate: integrated infrastructure conglomerates, cloud-native software specialists, and semiconductor platform providers. Competitive dynamics center on multi-vendor certification partnerships and managed security service outsourcing agreements.
Within the integrated infrastructure tier, NEC Corporation and Samsung Electronics exemplify archetypes combining radio hardware with security orchestration layers. Mavenir occupies a position representing cloud-native software stacks that reduce proprietary silicon dependency. These three anchors illustrate how vendor strategies diverge across hardware-software boundaries while converging on O-RAN Alliance specification compliance.
| Leading Market Players |
|---|
| NEC Corporation |
| Ericsson |
| Nokia Corporation |
| Juniper Networks, Inc. |
| ZTE Corporation |
| Mavenir |
| Fujitsu Limited |
| Broadcom, Inc. |
| Samsung Electronics Co., Ltd. |
| Others |
Value Network & Pricing Analysis
Containerized security function deployment at scale compresses per-unit licensing costs while elevating fixed certification overhead, concentrating margin leverage with vendors capable of amortizing O-RAN Alliance compliance investments across multi-country operator portfolios.
Pricing Analysis
Industrial OEM buyers anchor subscription-tiered pricing for cloud-native security stacks, with three-tier pricing structure across premium, standard, and economy levels differentiating by certification grade and managed service bundling. Price differentiation stems from BSI audit documentation and MIC source-code transparency requirements. Pricing pressure stems from silicon supply constraints constraining hardware appliance margins. Government agencies exhibit lowest price sensitivity due to mandate-driven procurement.
Supply Chain Analysis
Taiwan-based semiconductor fabrication chokepoints tether hardware security appliance production to concentrated foundry capacity, with South Korea and Japan providing alternative sourcing for specialized encryption accelerators. Raw material dependencies include advanced node semiconductors, trusted execution environment hardware, and cryptographic key management modules. Single-source vulnerability in Taiwan-based fabrication elevates supply risk. Distribution runs through direct operator procurement channels and systems integrator partnerships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Open RAN security incumbents face substitution pressure from cloud-native software stacks that displace proprietary hardware dependencies, requiring defensive repositioning across integration depth and managed service breadth.
For Market Incumbents: Compound integration advantages through captive supply of confidential computing hardware and exclusive certification partnerships with BSI and MIC. Deepen managed security service capabilities to offset margin compression from disaggregated software licensing. Prioritize zero-trust architecture investments as cloud-native challengers erode hardware-centric moats.
For New Entrants and Emerging Players: Managed security service gaps in German operator environments present immediate white-space capture opportunities. Target rural broadband infrastructure programs in the United States for cost-optimized stack deployment. Pursue AI-driven threat detection specialization as the primary go-to-market angle.
For Investors and Strategic Acquirers: Cloud-native security specialists with O-RAN Alliance certification traction represent the most defensible acquisition archetype. Long-term viability hinges on regulatory compliance automation capabilities. Monitor FCC supply chain rulemaking enforcement intensity as the critical inflection signal.
| Strategic Initiative | Industry Significance |
|---|---|
| Confidential Computing Integration | Hardware-based trusted execution environments displace software-only encryption in Japanese operator pilots. |
| Managed Security Service Expansion | German operators outsource zero-trust operations to compensate for internal expertise scarcity. |
| O-RAN Alliance Certification Investment | Multi-vendor interoperability testing creates fixed overhead barriers for smaller competitors. |
| AI-Driven Threat Detection Development | Machine learning inference at the edge enables real-time anomaly detection without core dependency. |
| Sovereign Cloud Configuration Deployment | BSI cloud sovereignty guidelines and MIC data localization rules drive elastic security function demand. |
Research Methodology
The analysis maps cloud-native security stacks, hardware appliances, threat intelligence solutions, and managed services, each validated through network security architects, telecom procurement officers, O-RAN Alliance working group participants, and regulatory compliance consultants. Primary intelligence combines structured interviews with secondary validation against FCC rulemakings, BSI technical guidelines, MIC audit protocols, O-RAN Alliance specification documents, and operator RFP disclosures. Bottom-up deployment modeling triangulates against top-down addressable market sizing.
Consistency checks validated volume and value outputs against hyperscaler security capex disclosures, tier-one operator procurement patterns, and national broadband program funding allocations across the projection horizon. Segmentation dimensions modeled include deployment architecture, service type layering, end-user sophistication, and solution technology maturity. CAGRs derive from installed base replacement cycles and network slicing workload elasticity assumptions.
Forecasts assume regulatory continuity in FCC equipment authorization regimes, BSI hardware provenance mandates, and MIC source-code audit requirements; material policy shifts would require re-modeling compliance cost structures and vendor eligibility pools. Practitioners should keep alternative scenarios live as 3GPP Release 18 specification maturation and confidential computing pilot outcomes evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Network Detection and Response Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Asia Pacific Cybersecurity Market
Cybersecurity
UK Cybersecurity Market
Cybersecurity
Mobile Encryption Market
Cybersecurity
Poland Cybersecurity Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Education Data Security Market
Cybersecurity
United States Virtualization Security Market
Cybersecurity
Digital Forensics Market
Cybersecurity
South Africa Cybersecurity Market
Cybersecurity
North America Digital Forensics Market
Cybersecurity
Firewall-As-A-Service (Fwaas) Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Philippines Cybersecurity Market
Cybersecurity
Indonesia Cybersecurity Market