
 Data Exfiltration Techniques Market | 2026-2036
Data Exfiltration Techniques Market Size, Share, and Industry Trends Forecast 2026-2036
Data Exfiltration Techniques Market Outlook
Healthcare sector procurement is restructuring the competitive landscape for data exfiltration defenses as hospital networks confront ransomware-to-extortion kill chains. Palo Alto Networks leverages cloud-native architecture to dominate North American enterprise accounts. CrowdStrike Holdings, Inc. sustains endpoint detection leadership through AI-driven threat graph analytics. Fortinet Inc. anchors mid-market expansion with integrated firewall and sandboxing bundles.
Data exfiltration techniques encompass the technical methods and toolchains adversaries employ to extract sensitive information from compromised environments, spanning covert channel protocols, steganographic payload embedding, and living-off-the-land binary abuse with file sizes often compressed below detection thresholds. These techniques serve the primary purpose of enabling intellectual property theft, espionage, or secondary monetization through darknet brokerage. Malware and phishing vectors command the largest detection spend, though network protocol manipulation is growing fastest as state-sponsored actors refine DNS tunneling and HTTPS domain fronting. Endpoint security and user behavior analytics capture expanding margin pools as organizations shift from perimeter blocking to insider-threat monitoring.
The SEC, CISA, and EU GDPR enforcement apparatuses collectively reshape product roadmaps by mandating disclosure timelines, audit logging standards, and cross-border data governance protocols that vendors must embed natively. HIPAA security rule audits and PCI DSS compliance deadlines further tighten procurement specifications for healthcare and retail buyers. Stakeholders must weigh whether behavioral analytics platforms or zero-trust network architectures offer superior resilience against AI-generated social engineering campaigns that bypass conventional detection heuristics.
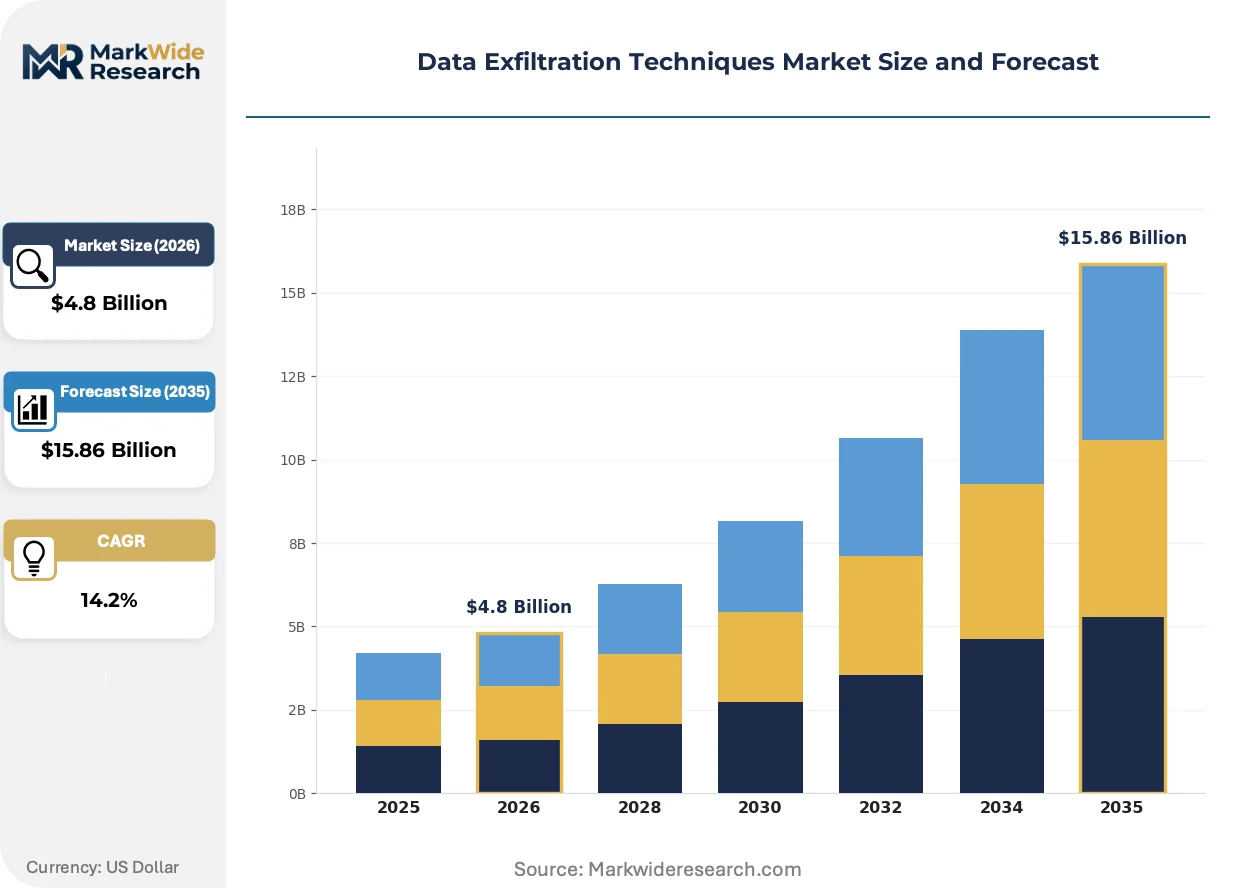
Market Dynamics
The SEC's breach disclosure mandates and CISA's incident reporting directives are compressing vendor sales cycles while forcing native compliance embedding into detection platforms.
Growth Catalysts
- SEC Cybersecurity Disclosure Rules:Public companies must report material breaches within four business days, accelerating procurement of automated exfiltration detection systems.
- Healthcare ransomware-to-extortion chains:Hospital networks facing HIPAA security rule audits are restructuring cybersecurity budgets toward behavioral anomaly platforms.
- DNS tunneling refinement:State-sponsored actors advancing protocol manipulation techniques is expanding demand for network traffic inspection tools.
Market Restraints
- Skilled analyst shortage:The talent gap in threat hunting and SOC operations limits deployment velocity for behavioral analytics platforms.
- False positive fatigue:Alert overload from legacy endpoint detection systems erodes buyer confidence in expanding tool licenses.
- Cross-border data governance friction:GDPR's data localization requirements complicate cloud-native architecture deployment for multinational enterprises.
Strategic Opportunities
- Critical infrastructure operators:CISA mandatory reporting requirements for energy and water utilities create a compliance-driven procurement wave.
- AI-generated social engineering:Deepfake-enabled phishing campaigns bypassing conventional heuristics open white space for voice and video authentication convergence.
- Managed detection and response channel:Mid-market buyers lacking in-house SOC capabilities are consolidating vendor relationships through MDR service bundles.
Industry Challenges
- Legacy SIEM integration complexity:Enterprises with decade-old log management infrastructure face protracted migration timelines for cloud-native detection platforms.
- Threat intelligence standardization delays:Fragmented STIX/TAXII implementation across vendor ecosystems hinders automated indicator sharing.
- Certification timeline compression:FedRAMP and StateRAMP authorization requirements extend sales cycles for public sector deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Data Exfiltration Techniques Market |
| Market Size in 2026 | $4.8 Billion |
| Market Size in 2035 | $15.86 Billion |
| CAGR (2026 – 2036) | 14.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Technique Type: Malware, Phishing, USB Transfer, Network Protocol Manipulation Target Sector: Government, Healthcare, Finance, Retail Detection Method: Data Loss Prevention, Intrusion Detection, User Behavior Analytics, Endpoint Security Impact Level: High, Medium, Low, Critical |
| Companies Covered | Broadcom Inc., CrowdStrike Holdings, Inc., Palo Alto Networks, Fortinet Inc., Check Point Software Technologies, McAfee, LLC, Cisco Systems Inc., Forcepoint, Trend Micro Inc., Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Data Exfiltration Techniques Market Strategic Shifts
Adversarial AI capabilities and regulatory enforcement timelines are compressing the window between breach occurrence and detection, reshaping platform architecture priorities.
Extended detection and response platforms are modularizing security telemetry ingestion across endpoint, network, and identity sources. Financial services institutions with expanded cybersecurity procurement budgets are deploying these architectures fastest. This modularization is compressing standalone point solution markets while elevating vendors with native data lake consolidation.
The EU AI Act's risk classification framework for biometric and behavioral analytics is mandating algorithmic audit trails and human oversight requirements. Vendors must now embed explainability features natively into anomaly detection engines. Healthcare and critical infrastructure buyers in EU member states are prioritizing platforms with pre-certified conformity assessment documentation.
Enterprise buying committees are consolidating vendor relationships through platform consolidation plays that displace standalone endpoint or network tools. Mid-market organizations lacking dedicated CISO functions are gravitating toward integrated firewall-sandbox-SIEM bundles. This pattern is most visible in United States healthcare networks confronting ransomware-to-extortion kill chains and HIPAA audit pressures.
Data Exfiltration Techniques Market Segmentation
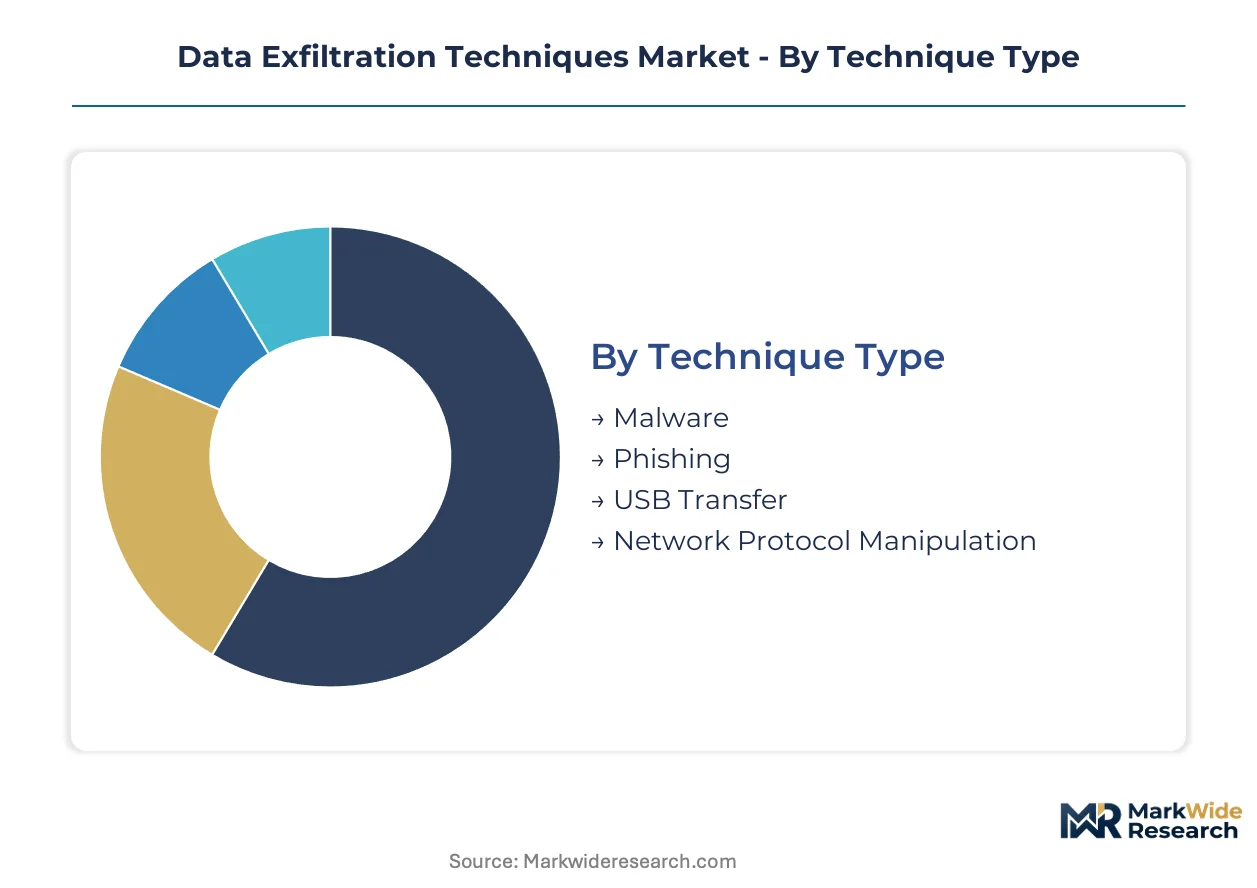
Segmentation clarity enables procurement teams to match defensive architectures against specific adversary tradecraft. Buyers in regulated sectors face divergent certification burdens depending on which technique vectors dominate their threat models.
Technique Type:
FedRAMP authorization and StateRAMP compliance timelines vary sharply across these segments, with cloud-native detection platforms facing extended review cycles for protocol manipulation capabilities.
- Malware:File-based payloads employ polymorphic encryption and code injection to evade signature-based detection. Financial services institutions in the United States allocate the largest procurement budgets here, driven by SEC disclosure mandates compressing incident response windows.
- Phishing:Social engineering vectors leverage credential harvesting and malicious attachments to establish initial access. Healthcare networks confronting HIPAA security rule audits are restructuring defenses toward email authentication convergence and behavioral anomaly detection.
- USB Transfer:Physical media exfiltration exploits air-gapped environments through autorun manipulation and hidden partition embedding. Critical infrastructure operators under CISA directives deploy hardware control policies and data diode architectures.
- Network Protocol Manipulation:DNS tunneling and HTTPS domain fronting compress payload transmission through trusted channels. State-sponsored actor refinement of these methods is expanding demand for deep packet inspection and encrypted traffic analysis platforms.
Malware sits at the top of the volume ranking, with network protocol manipulation climbing the fastest.
Target Sector:
Cost tier stratification separates enterprise-grade platforms from mid-market bundles, with government buyers commanding premium pricing for classified environment deployments.
- Government:National security agencies and civilian departments require cross-domain solutions with native audit logging and supply chain attestation. FedRAMP High authorization extends sales cycles but locks in multi-year enterprise agreements.
- Healthcare:Hospital networks and payers face ransomware-to-extortion kill chains targeting patient data monetization. HIPAA security rule audits and state breach notification laws are accelerating behavioral analytics procurement.
- Finance:Banks, insurers, and asset managers confront intellectual property theft and SWIFT network compromise. SEC cybersecurity disclosure rules mandate four-day material breach reporting, forcing automated detection system adoption.
- Retail:E-commerce platforms and brick-and-mortar chains prioritize PCI DSS compliance for payment card data protection. Mid-market buyers lacking dedicated CISO functions gravitate toward managed detection and response service bundles.
Finance sits at the top of the volume ranking, with healthcare climbing the fastest.
Detection Method:
Application-specific deployment patterns separate perimeter-blocking architectures from insider-threat monitoring platforms, with identity-centric approaches gaining share in zero-trust migrations.
- Data Loss Prevention:Content inspection engines classify and block sensitive data movement across endpoint, network, and cloud channels. United States critical infrastructure operators under CISA mandatory reporting requirements are prioritizing DLP with native encryption and rights management.
- Intrusion Detection:Signature and anomaly-based systems monitor network traffic for known attack indicators and behavioral deviations. Energy and water utilities facing compliance-driven procurement waves are deploying network traffic inspection tools with ICS protocol awareness.
- User Behavior Analytics:Machine learning models baseline employee activity patterns to flag insider threats and compromised credentials. EU AI Act algorithmic audit trail requirements are mandating explainability features in platforms sold to European healthcare and critical infrastructure buyers.
- Endpoint Security:Agents on workstations and servers prevent execution of malicious code and monitor for data staging. Mid-market organizations are consolidating vendor relationships through integrated firewall-sandbox-SIEM bundles displacing standalone tools.
Endpoint security sits at the top of the volume ranking, with user behavior analytics expanding most quickly.
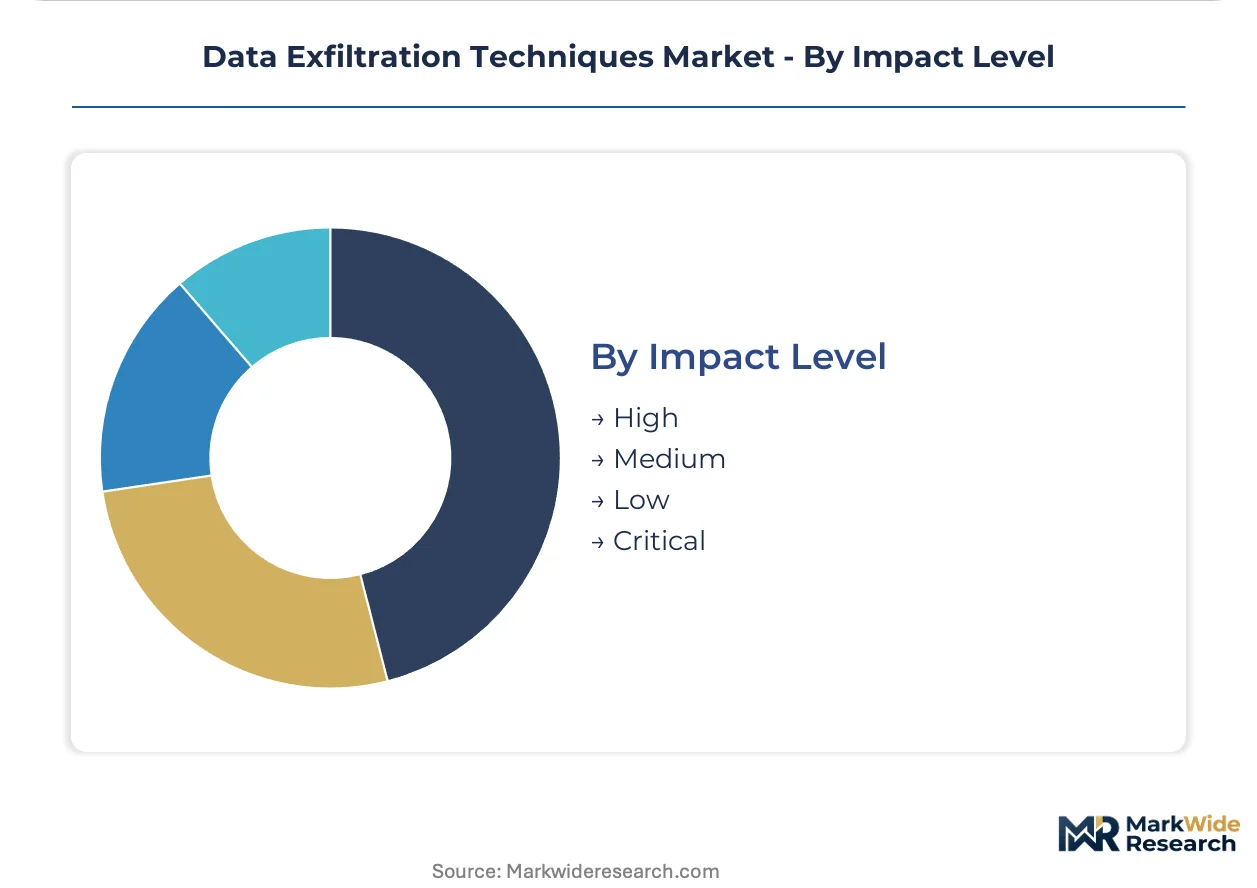
Impact Level:
Maturity differentiation separates legacy compliance-checking approaches from predictive risk quantification, with critical-impact segments commanding the highest platform licensing premiums.
- High:Breaches exposing regulated data trigger mandatory disclosure and regulatory investigation. Financial services and healthcare buyers prioritize high-impact detection with automated incident response playbooks.
- Medium:Incidents affecting operational technology or business continuity demand containment without full breach declaration. Manufacturing and logistics sectors allocate defensive spend here.
- Low:Policy violations and inadvertent data exposure require remediation without external reporting. Education and nonprofit organizations with constrained budgets focus limited resources on low-impact prevention.
- Critical:National security events and infrastructure sabotage activate government coordination protocols. Defense industrial base contractors and energy sector operators deploy critical-impact architectures with air-gapped forensics.
High impact sits at the top of the volume ranking, with critical impact gaining share fastest.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Regulatory-arbitrage dynamics are reshaping procurement patterns as compliance cost differentials between jurisdictions drive vendor localization strategies and data sovereignty investments.
United States
Critical infrastructure operators and financial institutions anchor North American demand for data exfiltration defenses. CISA's mandatory incident reporting directives for energy and water utilities compress procurement timelines. Texas and California data center clusters host the densest concentrations of cloud-native detection platform deployments.
Germany
Industrial manufacturers and automotive suppliers prioritize air-gapped forensics for intellectual property protection. The EU AI Act's algorithmic audit requirements mandate explainability features in behavioral analytics platforms sold to German buyers. Bavaria's defense industrial base contractors deploy critical-impact architectures with native GDPR compliance embedding.
United Kingdom
Financial services firms and government agencies drive demand for automated exfiltration detection systems. The National Cyber Security Centre's guidance on ransomware response shapes procurement specifications. London's fintech corridor concentrates the highest density of extended detection and response platform deployments.
Japan
Manufacturing conglomerates and semiconductor fabricators invest in insider-threat monitoring for trade secret protection. METI's cybersecurity framework for critical infrastructure operators mandates supply chain attestation. The Kanto region's Tokyo-Osaka technology corridor hosts specialized vendors refining steganographic payload detection.
Australia
Healthcare networks and mining operators confront ransomware-to-extortion kill chains targeting operational technology. The country's national cybersecurity regulator mandates incident reporting for critical infrastructure sectors. New South Wales and Victoria host the primary concentrations of managed detection and response service providers.
Data Exfiltration Techniques Market Competitive Environment
Platform consolidation dominates the current landscape as enterprise buyers displace standalone point solutions with integrated architectures. The vendor base stratifies across three tiers: cloud-native specialists with native SIEM consolidation, legacy perimeter-security incumbents bundling firewall-sandbox capabilities, and managed detection and response service providers addressing mid-market SOC gaps. M&A activity and technology licensing agreements represent the dominant competitive moves, with acquirers targeting behavioral analytics engines and encrypted traffic inspection capabilities.
Within the cloud-native specialist tier, Palo Alto Networks and CrowdStrike Holdings, Inc. exemplify platform-first strategies that compress standalone endpoint markets through modular telemetry ingestion. Fortinet Inc. occupies a position bridging mid-market bundles with enterprise-grade network protocol manipulation detection. These three anchors illustrate how vendor selection increasingly hinges on native compliance embedding for SEC, GDPR, and CISA mandates rather than detection efficacy alone.
| Leading Market Players |
|---|
| Broadcom Inc. |
| CrowdStrike Holdings, Inc. |
| Palo Alto Networks |
| Fortinet Inc. |
| Check Point Software Technologies |
| McAfee, LLC |
| Cisco Systems Inc. |
| Forcepoint |
| Trend Micro Inc. |
| Others |
Value Chain & Pricing Dynamics
Private-equity-rolled-up cybersecurity specialists have consolidated fragmented detection-tool vendors across the United States and Israel, compressing channel margins while enforcing disciplined SaaS pricing tiers that reflect FedRAMP certification costs rather than raw feature differentiation.
Pricing Analysis
Distributor margins in the data exfiltration defense market typically absorb 15-25 points before enterprise end-users, though direct-to-OEM arrangements for embedded detection agents bypass this layer entirely. Subscription-based SaaS tiers dominate, with pricing stratifying across premium (FedRAMP High-authorized platforms), standard (commercial cloud-native bundles), and economy (on-premise legacy SIEM add-ons) levels. Cost compression in the standard tier intensifies as Palo Alto Networks and CrowdStrike force bundle pricing on mid-market buyers. Healthcare networks with constrained CISO staffing prove most price-sensitive, while defense industrial base contractors accept premium licensing for air-gapped forensics capabilities.
Supply Chain Analysis
Workforce availability constraints in cybersecurity engineering concentrate platform development across the United States, Israel, and United Kingdom, with Bangalore and Tallinn emerging as specialized hubs for threat intelligence analytics. Cloud infrastructure draws from hyperscaler capacity in Northern Virginia, Frankfurt, and Singapore, while specialized hardware for deep packet inspection sources from Taiwan and South Korea. Single-source vulnerability in AI training data pipelines poses structural risk as behavioral analytics vendors depend on common threat intelligence feeds. Distribution runs through value-added resellers with security specialization, though managed detection and response providers increasingly displace this channel with direct service relationships.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The data exfiltration techniques market functions as a stable compounder, with regulatory disclosure mandates from SEC and EU GDPR creating irreversible procurement commitments that renew through multi-year enterprise agreements.
For Market Incumbents: Deepen native compliance embedding for CISA incident reporting timelines and EU AI Act algorithmic audit requirements to lock out point-solution competitors. Acquire behavioral analytics engines from emerging Israeli or Estonian specialists before they achieve FedRAMP authorization independently. Vertical integration into managed detection and response service delivery protects margin pools as mid-market buyers consolidate vendor relationships.
For New Entrants and Emerging Players: CISA mandatory reporting requirements for energy and water utilities open a window for specialized network protocol manipulation detection targeting operational technology environments. Target Australian healthcare networks and mining operators confronting ransomware-to-extortion kill chains with managed service bundles that displace in-house SOC investments. Pursue channel partnerships with established firewall distributors to bypass direct enterprise sales cycle compression.
For Investors and Strategic Acquirers: Valuations sit cheapest among mid-market SIEM vendors with healthcare customer concentrations but lagging cloud-native architecture transitions. Five-to-ten year viability hinges on successful platform consolidation plays that displace standalone endpoint tools. Watch for inflection in StateRAMP authorization timelines as signal for public sector procurement acceleration.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Native SIEM consolidation compresses standalone endpoint markets through modular telemetry ingestion. |
| Acquisition of Specialist Firm | Behavioral analytics engines from Israeli vendors address AI-generated social engineering detection gaps. |
| Regulatory Certification Pathway | FedRAMP High authorization extends sales cycles but locks multi-year agreements with defense buyers. |
| Strategic Partnership | Managed detection and response bundles address mid-market SOC capability gaps through channel consolidation. |
| Geographic Expansion | EU AI Act pre-certified platforms capture German automotive and healthcare procurement mandates. |
Study Parameters
Direct dialogue with CISOs at financial services institutions, threat intelligence directors at energy utilities, healthcare network security architects, and managed detection and response service heads grounded qualitative findings in operational procurement realities. Secondary validation drew from SEC cybersecurity disclosure filings, CISA incident reporting databases, EU AI Act conformity assessment documentation, and healthcare breach notification logs. Bottom-up segment sizing triangulated against top-down regulatory mandate impact modeling.
Market size and growth projections emerged from integrated demand-side and supply-side calibration across the projection horizon. Segmentation dimensions modeled include technique type (malware, phishing, network protocol manipulation), target sector (finance, healthcare, government, retail), detection method (endpoint security, user behavior analytics, data loss prevention), and impact level (high, critical). CAGRs derived from regression analysis against regulatory enforcement timeline acceleration and enterprise security budget elasticity estimates.
Revisions become necessary when CISA expands mandatory reporting sector coverage, EU AI Act enforcement timelines accelerate, or adversarial AI capabilities compress detection-to-breach windows beyond current platform architectures. Material deviation in these triggers warrants pause and re-evaluation.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Global Cyber Security in Healthcare Market
Cybersecurity
Spear Phishing Solution Market
Cybersecurity
Singapore Cybersecurity Market
Cybersecurity
Malaysia Cybersecurity Market
Cybersecurity
Big Data Security Market
Cybersecurity
Cloud DLP Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Cryptojacking Solution Market
Cybersecurity
Quantum Cryptography Market
Cybersecurity
Cloud Network Security Market
Cybersecurity
Hong Kong Cybersecurity Market
Cybersecurity
Cloud Security in Banking Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Global Content Disarm and Reconstruction Market
Cybersecurity
United States Virtualization Security Market