
 Multi-Cloud Data Protection Market | 2026-2036
Multi-Cloud Data Protection Market Size, Share, and Industry Trends Forecast 2026-2036
Multi-Cloud Data Protection Market Analysis
GDPR enforcement is repositioning the cost-of-entry calculus for multi-cloud data protection vendors serving European enterprises. Commvault leverages its unified platform architecture to sustain backup consistency across heterogenous cloud estates. Dell Technologies anchors its competitive stance through integrated hardware-software recovery stacks that dominate on-premises-to-cloud failover scenarios. Palo Alto Networks differentiates by embedding zero-trust security controls directly into data protection workflows, reducing lateral breach risks during recovery operations.
Multi-cloud data protection encompasses policy-driven backup, disaster recovery, archiving, and security orchestration across two or more independent cloud service providers, typically leveraging agentless snapshotting, immutable object storage, and encryption key segregation to ensure recoverability without vendor lock-in. Its primary commercial purpose is to eliminate single points of failure while satisfying data sovereignty mandates that prohibit exclusive reliance on one hyperscaler's infrastructure. The Backup segment leads current revenue contribution as ransomware frequency forces shorter recovery point objectives across enterprise workloads. Disaster Recovery is expanding fastest as financial services firms demand sub-hour failover between geographically separated cloud regions. The Security segment commands premium pricing due to converged data loss prevention and access governance requirements.
The EU AI Act, HIPAA, and ISO 27001 collectively shape product roadmaps by mandating audit trails, encryption standards, and breach notification protocols that vary by data classification tier. HIPAA constrains how US healthcare entities replicate protected health information across public cloud boundaries, while ISO 27001 certification has become a procurement prerequisite for enterprise buyers evaluating vendor shortlists. Stakeholders must monitor regulatory divergence between the European Union's data localization requirements and emerging sector-specific frameworks in Asia-Pacific jurisdictions to avoid architectural redesign costs.
Market Dynamics
Ransomware frequency is compressing recovery point objectives across enterprise workloads, forcing infrastructure teams to abandon single-cloud backup architectures in favor of distributed resilience models that satisfy data sovereignty mandates.
Growth Catalysts
- GDPR cross-border enforcement:The European Union's data localization requirements compel enterprises to maintain redundant protection stacks across independent cloud service providers. German automotive suppliers now mandate geographic separation of backup copies.
- Healthcare data volume surge:Patient imaging and genomic datasets are overwhelming hospital storage capacities. HIPAA constraints on protected health information replication are accelerating sovereign cloud partnerships for US providers.
- Immutable object storage maturation:Write-once-read-many architectures now deliver ransomware-resistant backup targets at commodity pricing, displacing tape-based archival strategies in financial services vaults.
Market Restraints
- Encryption key management complexity:Enterprises maintaining separate key hierarchies across AWS KMS, Azure Key Vault, and sovereign cloud instances face operational overhead that erodes multi-cloud economic justifications.
- API fragmentation:Hyperscalers expose incompatible snapshot and recovery interfaces, forcing vendors to maintain parallel integration codebases that slow feature parity.
- Skilled architect scarcity:The labor pool capable of designing consistent policy frameworks across heterogeneous cloud estates remains concentrated in technology hubs, inflating professional services costs.
Strategic Opportunities
- EU AI Act audit trail mandates:The regulation's documentation requirements for training data lineage create demand for immutable backup systems that preserve model development artifacts across cloud boundaries.
- Edge-to-cloud orchestration:Manufacturing facilities generating terabyte-scale sensor streams require localized protection before cloud ingress, opening appliance-based backup markets for industrial IoT deployments.
- Channel partner certification programs:Managed service providers lacking ISO 27001 credentials face procurement exclusion, creating whitespace for compliance-focused distributor enablement initiatives.
Industry Challenges
- Legacy workload containerization friction:Mainframe and AS/400 systems resist agentless snapshotting, forcing hybrid architectures that complicate recovery orchestration and extend RTO commitments.
- Cross-cloud consistency verification:Enterprises struggle to validate that backup policies execute identically across AWS, Azure, and sovereign instances, creating audit vulnerabilities during regulatory examinations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Multi-Cloud Data Protection Market |
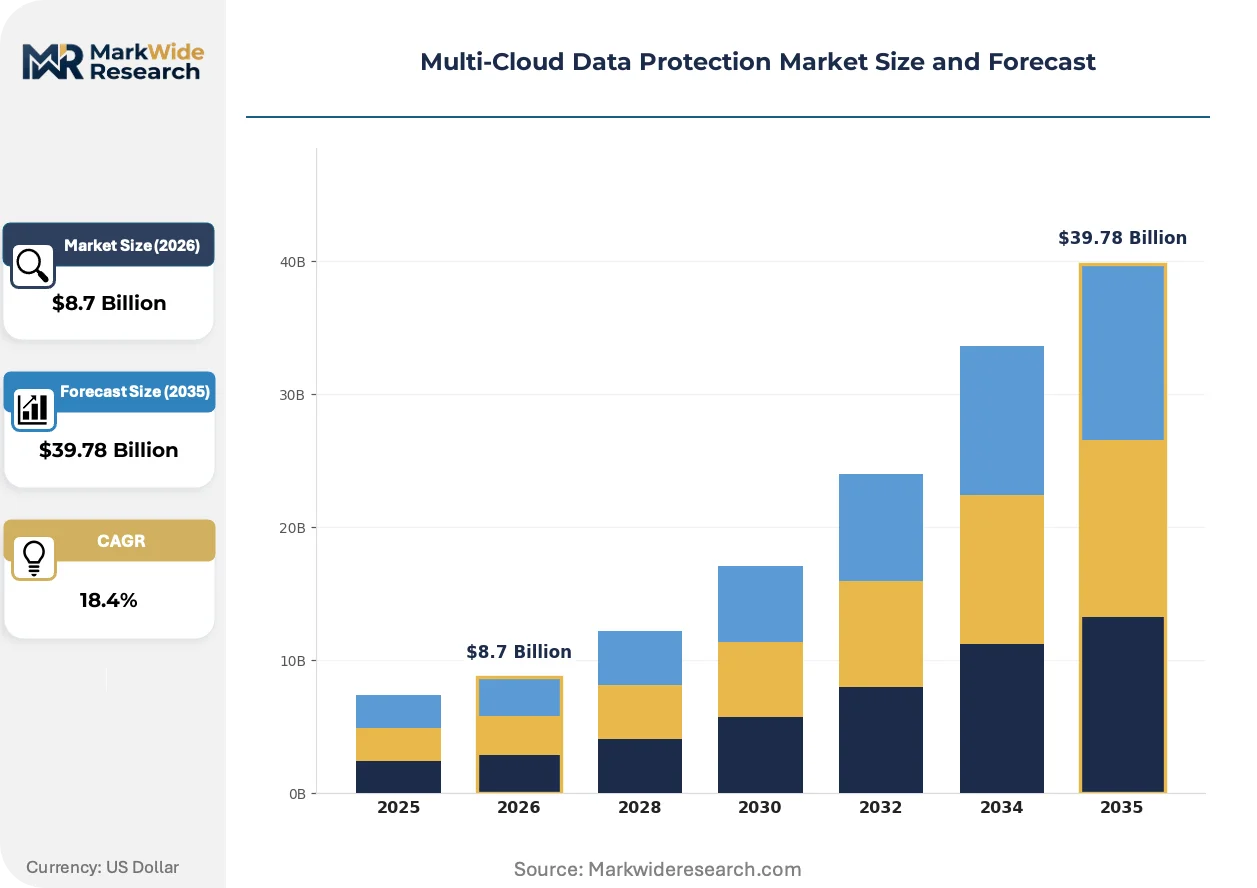
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $39.78 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Backup, Disaster Recovery, Archiving, Security Deployment Model: Public Cloud, Private Cloud, Hybrid Cloud, Multi-Cloud End User: Healthcare, BFSI, Retail, Government Compliance Standard: GDPR, HIPAA, ISO 27001, PCI DSS |
| Companies Covered | Commvault, Veritas Technologies, Dell Technologies, HYCU, IBM Corporation, Microsoft Corporation, Palo Alto Networks, Check Point Software Technologies, Immuta, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Multi-Cloud Data Protection Market Emerging Trajectories
Agentless snapshotting technology is compressing deployment timelines while zero-trust security integration is redefining recovery workflow architectures. These shifts are converging with policy-driven automation to reshape vendor competitive positioning.
Immutable object storage is expanding into primary backup workloads from its archival origins. Financial services firms now demand air-gapped protection for operational databases, not just compliance archives. This capability compression is forcing traditional backup vendors to acquire or build object-native engines rather than retrofit tape-centric codebases.
The EU AI Act's training data documentation requirements are mandating immutable preservation of model development artifacts. Machine learning teams must demonstrate lineage across distributed cloud environments where data scientists provision their own storage. Healthcare and automotive AI developers face the steepest compliance burdens as regulators scrutinize algorithmic decision trails.
Enterprise buying committees are consolidating vendor relationships to reduce operational complexity. Procurement teams now evaluate backup, disaster recovery, and security orchestration as a unified capability rather than discrete purchases. This pattern concentrates most visibly in German industrial conglomerates building redundant protection stacks across AWS, Azure, and sovereign cloud instances.
Multi-Cloud Data Protection Market Segmentation
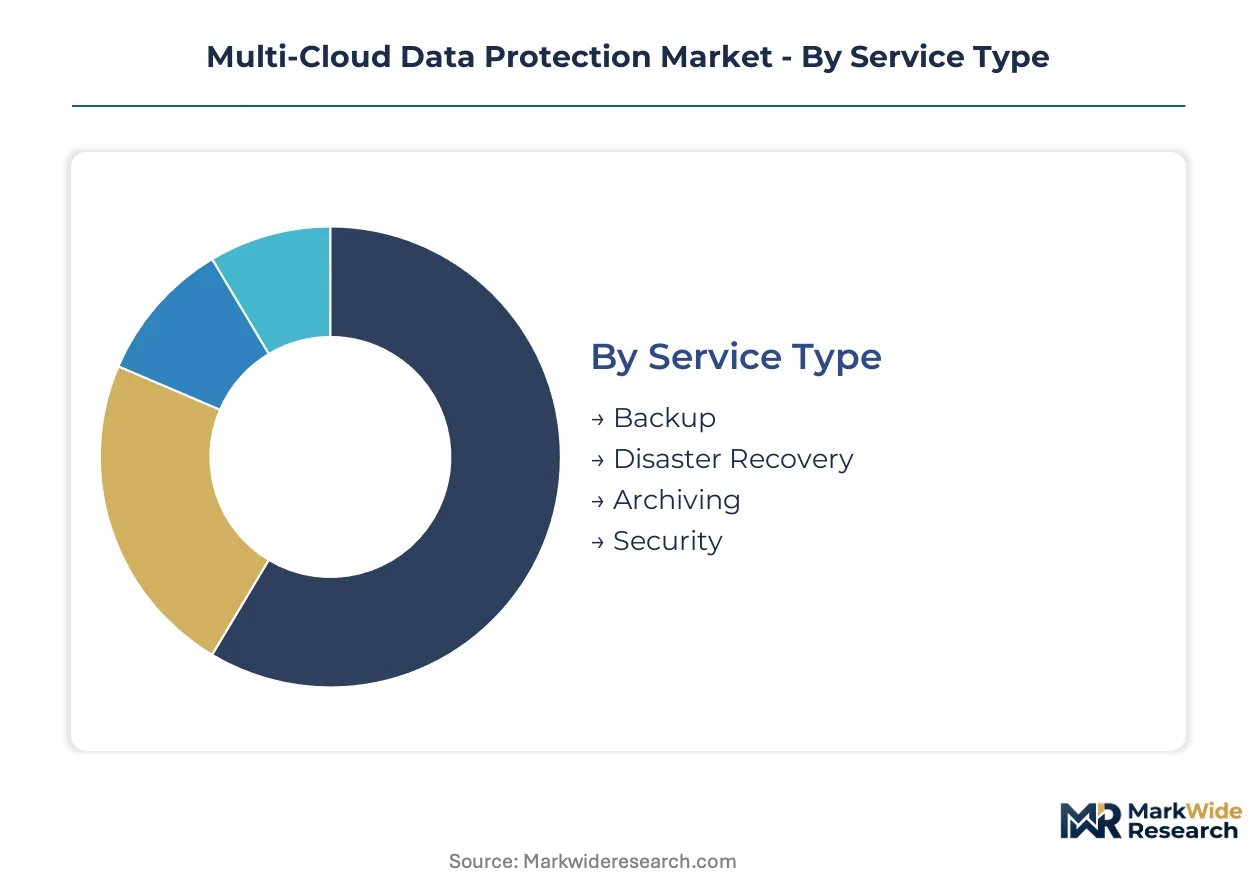
Multi-cloud data protection vendors face divergent technical requirements across service tiers, deployment architectures, and regulatory jurisdictions. Segmentation reveals where premium pricing concentrates versus where volume deployments scale.
Service Type:
Backup commands the largest revenue share while Disaster Recovery captures the steepest expansion trajectory as financial services compress recovery time objectives.
- Backup:Policy-driven snapshot orchestration across heterogeneous cloud estates with immutable object storage anchoring ransomware-resistant retention. German automotive suppliers now mandate geographic separation of backup copies across AWS, Azure, and sovereign cloud instances to satisfy GDPR cross-border enforcement.
- Disaster Recovery:Automated failover orchestration between geographically separated cloud regions with sub-hour recovery point objectives. Financial services firms in Frankfurt and Singapore are driving demand as regulatory pressure intensifies on operational resilience.
- Archiving:Long-term retention for compliance and litigation hold with tape displacement accelerating.
- Security:Converged data loss prevention and access governance commanding premium pricing due to zero-trust integration requirements.
Today's leader: Backup. Tomorrow's challenger: Disaster Recovery.
Deployment Model:
Deployment choice tracks data sovereignty mandates and latency sensitivity rather than pure cost optimization.
- Public Cloud:Hyperscaler-native protection leveraging AWS, Azure, and Google Cloud APIs with consumption-based pricing. Healthcare providers in the United States face HIPAA constraints on protected health information replication that limit pure public cloud strategies.
- Private Cloud:Dedicated infrastructure for classified workloads and regulated industries requiring physical control. Defense contractors and government agencies in France and Germany favor sovereign private instances under CNIL and BSI oversight.
- Hybrid Cloud:Orchestrated protection spanning on-premises and cloud targets with unified policy management.
- Multi-Cloud:Deliberate distribution across independent providers to eliminate single points of failure and vendor lock-in.
Volume concentrates in Public Cloud. Premium attaches to Multi-Cloud.
End User:
End-user segmentation aligns with data gravity centers and regulatory exposure severity.
- Healthcare:Patient imaging and genomic datasets overwhelming storage capacities with HIPAA and EU AI Act dual compliance burdens. US hospital systems are accelerating sovereign cloud partnerships to isolate protected health information while enabling research collaboration.
- BFSI:Sub-hour failover mandates and immutable vaulting for operational databases. Frankfurt-based insurers under BaFin supervision are pioneering cross-cloud consistency verification frameworks.
- Retail:Seasonal elasticity demands and payment card data protection driving hybrid architectures.
- Government:Classified workload isolation and supply chain security requirements favoring certified sovereign clouds.
Healthcare leads current procurement velocity. BFSI defines technical specifications.
Compliance Standard:
Certification requirements function as procurement gatekeepers with divergent architectural implications.
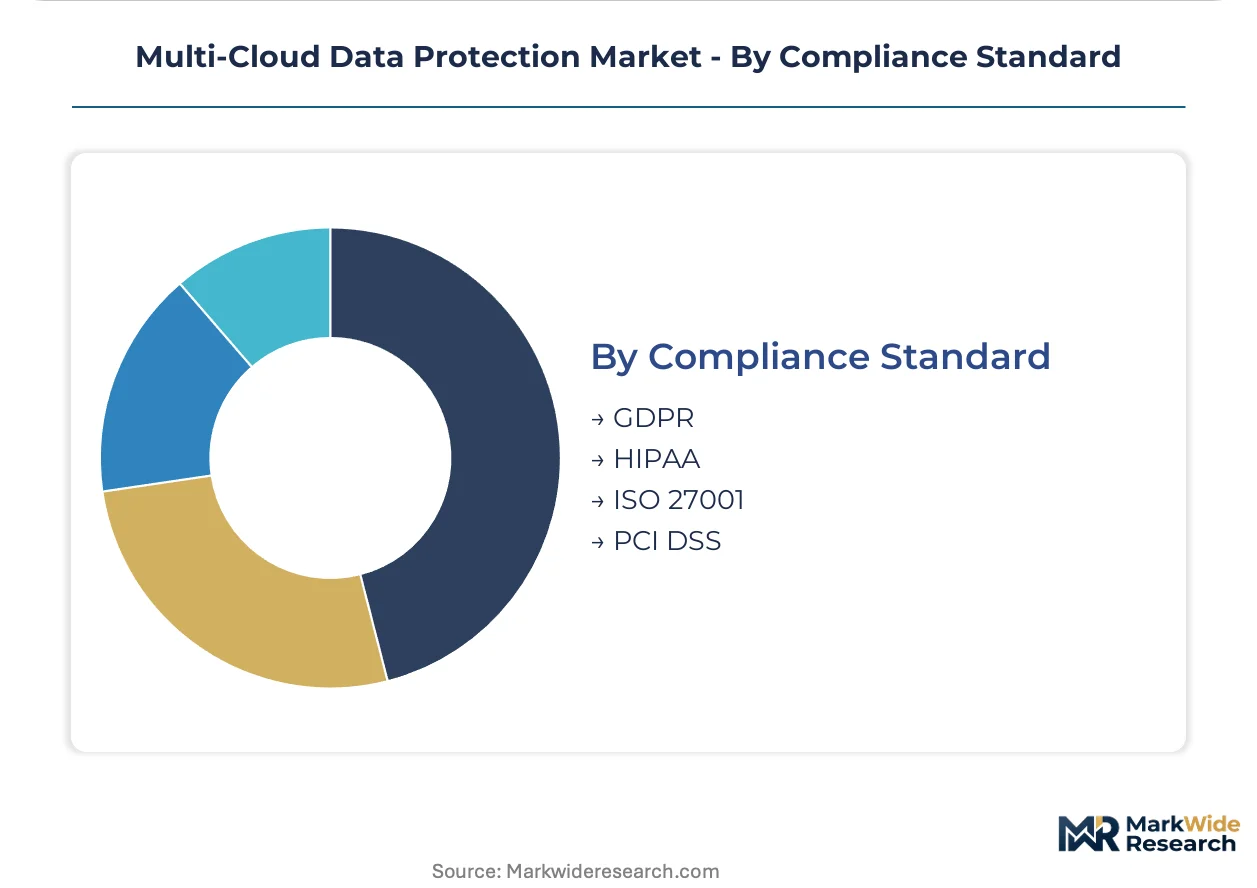
- GDPR:EU data localization with cross-border transfer mechanisms and breach notification protocols. The regulation compels redundant protection stacks across independent cloud service providers with German industrial conglomerates setting implementation benchmarks.
- HIPAA:US healthcare privacy constraints on protected health information access, audit trails, and business associate agreements. Covered entities must demonstrate administrative, physical, and technical safeguards across cloud boundaries.
- ISO 27001:Information security management certification prerequisite for enterprise vendor shortlists globally.
- PCI DSS:Payment card data protection with network segmentation and encryption key management requirements.
GDPR shapes European architecture. HIPAA governs US healthcare purchasing.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The multi-cloud data protection industry traces its commercial origins to early 2010s enterprise SaaS expansion in the United States, where hyperscaler-native backup architectures first achieved scale before spreading to regulated European markets.
United States
Healthcare systems in Massachusetts and California are consolidating petabyte-scale imaging archives across AWS and Azure instances to satisfy HIPAA constraints on protected health information. The Department of Health and Human Services enforces breach notification protocols that compress recovery point objectives. Hospital networks in the Research Triangle are pioneering sovereign cloud partnerships to isolate genomic datasets while enabling cross-institutional research collaboration.
Germany
Industrial conglomerates in Bavaria and Baden-Württemberg mandate geographic separation of backup copies across AWS, Azure, and T-Systems sovereign cloud instances. BSI oversight and GDPR cross-border enforcement compel redundant protection stacks with audit-grade consistency verification. Automotive suppliers in Stuttgart are building sub-hour failover architectures between Frankfurt and Munich cloud regions to satisfy operational resilience mandates.
United Kingdom
Financial services firms in the City of London and Canary Wharf demand immutable vaulting for operational databases under Prudential Regulation Authority supervision. The UK GDPR retention framework shapes multi-cloud residency decisions for cross-border data flows. InsurTech clusters in Manchester are deploying edge-to-cloud orchestration for localized protection of IoT sensor streams before cloud ingress.
Japan
Manufacturing headquarters in Tokyo and Osaka are distributing backup workloads across AWS Tokyo, Azure Japan East, and Fujitsu FJcloud to eliminate single points of failure. METI guidelines on critical infrastructure protection influence procurement specifications for industrial control system data. Automotive electronics suppliers in Nagoya are implementing agentless snapshotting for terabyte-scale design simulation archives.
India
IT services exporters in Bengaluru and Hyderabad are building multi-tenant protection stacks across AWS Mumbai, Azure Central India, and domestic cloud providers to satisfy data localization expectations. The Digital Personal Data Protection Act shapes cross-border transfer architectures for multinational captive centers. Fintech clusters in Mumbai are demanding ISO 27001-certified disaster recovery with sub-hour RTO commitments for payment processing workloads.
Multi-Cloud Data Protection Market Vendor Landscape
The competitive structure tilts toward diversified technology conglomerates with established enterprise relationships. Platform breadth and regulatory certification density determine vendor positioning more than point-product innovation. Three archetypes dominate: unified data management platforms, security-integrated protection stacks, and hardware-anchored recovery systems. Strategic moves concentrate on ISO 27001 certification acquisition and sovereign cloud partnership expansion to satisfy European procurement requirements.
Within the unified platform tier, Commvault and Veritas Technologies occupy positions defined by heterogeneous cloud estate coverage. Dell Technologies exemplifies the hardware-integrated archetype through on-premises-to-cloud failover specialization. Palo Alto Networks sits within the security-converged segment, embedding zero-trust controls into recovery workflows. These three anchors illustrate how competitive differentiation now hinges on policy consistency across independent cloud service providers rather than single-platform performance optimization.
| Leading Market Players |
|---|
| Commvault |
| Veritas Technologies |
| Dell Technologies |
| HYCU |
| IBM Corporation |
| Microsoft Corporation |
| Palo Alto Networks |
| Check Point Software Technologies |
| Immuta |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up backup specialists have consolidated fragmented regional vendors across Germany and the United States, creating pricing discipline through portfolio standardization while compressing professional services margins. This ownership concentration feeds directly into supply chain decisions, as these platforms negotiate unified appliance procurement from Dell Technologies and HYCU rather than maintaining fragmented vendor relationships.
Pricing Analysis
Consumption-based SaaS tiers with committed-use discounts dominate enterprise procurement, separating premium multi-cloud orchestration from standard single-cloud protection and economy archival-only tiers. Price differentiation rests on ISO 27001 certification density and geographic redundancy levels. Cost compression in the standard tier is intensifying because hyperscalers are bundling native backup tools at marginal cost. Healthcare providers exhibit the highest price sensitivity due to constrained capital budgets, while financial services firms accept premium pricing for sub-hour recovery guarantees.
Supply Chain Analysis
Domestic-content mandates in France and Germany under CNIL and BSI oversight are reshaping sourcing, compelling vendors to qualify sovereign cloud hardware partners. Supply concentrates in the United States, Germany, and Japan for appliance manufacturing, with software development anchored in India and Israel. Component dependencies include encryption processors from Taiwan, flash storage from South Korea, and specialized networking gear from the United States. Single-source vulnerability around TPM chip supply creates bottleneck risk. Distribution runs through certified managed service providers and hyperscaler marketplaces.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The multi-cloud data protection market functions as a regulatory compounder, with the EU AI Act's training data lineage mandates forcing architectural redesigns across healthcare and automotive AI development pipelines.
For Market Incumbents: Deepen sovereign cloud partnerships in Germany and France to preempt CNIL and BSI procurement exclusions. Consolidate channel certification programs to capture managed service provider relationships before emerging platform-native entrants achieve ISO 27001 credentials. The threat of hyperscaler-native backup tools bundling at marginal cost demands defensive integration of zero-trust security controls as a differentiation lever. For New Entrants and Emerging Players: Launch via appliance-based edge-to-cloud orchestration targeting manufacturing IoT deployments in Japan and Germany. The most penetrable segment sits in mid-market industrial facilities generating terabyte-scale sensor streams without existing protection infrastructure. A compliance-first go-to-market emphasizing EU AI Act audit trail capabilities opens procurement doors closed to uncertified incumbents. For Investors and Strategic Acquirers: Valuations sit cheapest among hardware-anchored recovery specialists lacking cloud-native orchestration layers. Long-term viability over the next decade hinges on platform breadth across heterogeneous estates rather than point-product performance. The signal to watch is sovereign cloud partnership density, as European procurement rules harden around domestic-content requirements.| Strategic Initiative | Industry Significance |
|---|---|
| Sovereign Cloud Partnership Expansion | CNIL and BSI oversight in France and Germany now mandate domestic-content verification for public sector procurement. |
| Zero-Trust Security Integration | Palo Alto Networks and Check Point Software Technologies embed access governance directly into recovery workflows. |
| Edge-to-Cloud Appliance Development | Manufacturing facilities in Stuttgart and Nagoya require localized protection before terabyte-scale sensor ingress. |
| ISO 27001 Certification Acquisition | Managed service providers lacking credentials face exclusion from enterprise vendor shortlists globally. |
| Immutable Object Storage Migration | Financial services firms in Frankfurt and London now demand air-gapped protection for operational databases. |
Methodological Framework
Multiple input streams — primary interviews with cloud architects and compliance officers, hyperscaler capex disclosures, and regulatory filing analysis — were reconciled to construct market estimates. Conversations with data protection vendors, healthcare IT directors, and financial services infrastructure leads provided operational context. Secondary validation drew from SEC filings, GDPR enforcement actions, EU AI Act implementation guidance, and ISO certification databases. Bottom-up deployment counts and top-down vendor revenue triangulation anchored segment splits.
Historical spending patterns were cross-referenced against expert panel inputs to project trajectory across the analysis window. Segmentation dimensions modeled include service type, deployment architecture, end-user vertical, and regional regulatory cluster. CAGRs were derived from curve-fitting observed adoption rates against compliance deadline schedules. Industry-specific inputs encompassed ransomware incident frequency data and sovereign cloud partnership announcements.
Several conditions sit outside the modeled scope, including unannounced hyperscaler acquisitions, sudden regulatory enforcement shifts, and breakthrough encryption technologies. Forecasts reflect documented assumptions about compliance timeline adherence and cloud migration continuity. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Netherlands Cybersecurity Market
Cybersecurity
Mainframe Security Market
Cybersecurity
Data-Centric Security Market
Cybersecurity
V2X Cybersecurity Market
Cybersecurity
Big Data Security Market
Cybersecurity
Europe Zero Trust Security Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Global Automated Breach and Attack Simulation (BAS) Market
Cybersecurity
Digital Security Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
India Ransomware Protection Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Global Ransomware Protection Market
Cybersecurity
Web Filtering Market
Cybersecurity
Global Internet Security Market
Cybersecurity
Global Network Security Firewall Market