
 Application Programming Interface Security Market | 2026-2036
Application Programming Interface Security Market Size, Share, and Industry Trends Forecast 2026-2036
Application Programming Interface Security Market Analytics
Behavioral AI is restructuring API threat detection economics by displacing signature-based rule engines that require constant manual tuning. Salt Security leverages machine learning models trained on billions of API calls to sustain detection accuracy across shadow endpoints. Traceable AI anchors its platform architecture around distributed tracing, competing directly with legacy web application firewall vendors that lack native API context awareness.
Application programming interface security encompasses the policies, technologies, and practices that protect APIs from unauthorized access, data exfiltration, and service disruption across REST, GraphQL, and gRPC protocols. These systems operate through runtime analysis, schema validation, and continuous traffic inspection to enforce authentication, rate limiting, and encryption for machine-to-machine communications. Gateway security solutions dominate current procurement cycles among large enterprises managing thousands of public-facing endpoints. Cloud-based deployment models are capturing accelerated interest as organizations migrate API traffic away from on-premises data centers. Financial services end users command the deepest investment pools, driven by PSD2 open banking compliance and real-time payment network expansion.
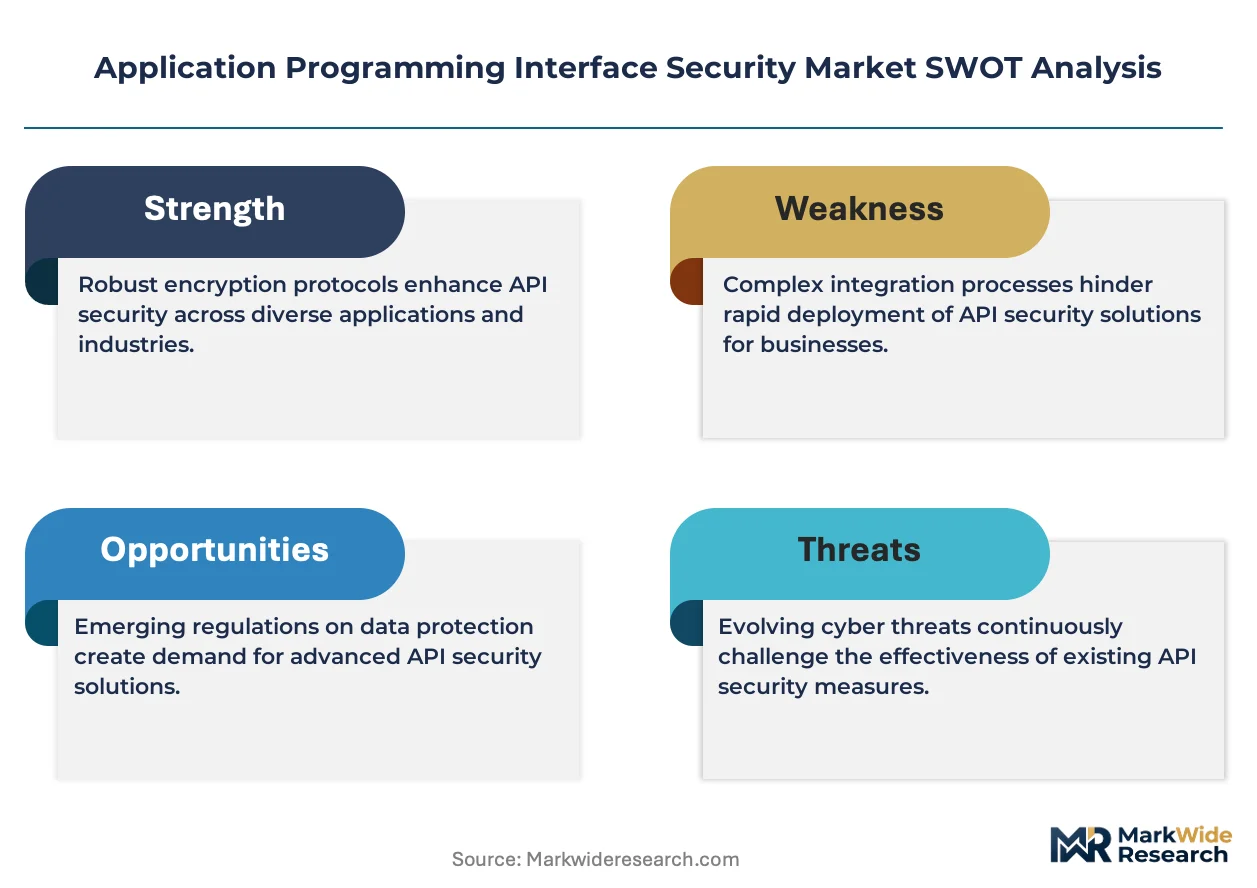
The EU AI Act, GDPR, and NIS2 Directive collectively mandate algorithmic transparency and incident reporting for automated systems processing sensitive data through APIs. The Federal Reserve's operational resilience guidelines and SEC cybersecurity disclosure rules in the United States impose comparable accountability standards on financial API infrastructure. Stakeholders must monitor how fragmented regulatory timelines across jurisdictions will reshape compliance tooling requirements and vendor certification priorities.
Market Dynamics
Behavioral AI architectures are restructuring competitive economics by displacing signature-based detection systems that demand constant manual rule tuning across expanding API endpoint inventories.
Growth Catalysts
- Open banking mandates:PSD2 in Europe and similar frameworks in Brazil and Australia compel financial institutions to expose payment APIs, mandating runtime security layers that validate traffic patterns against behavioral baselines.
- Cloud-native fintech proliferation:Digital banks and embedded finance platforms deploy thousands of microservices, each requiring automated schema validation and continuous traffic inspection to prevent data exfiltration.
- Real-time payment networks:FedNow in the United States and equivalent instant settlement systems in India and Singapore process high-velocity transactions through APIs, elevating the cost of service disruption and authentication failures.
Market Restraints
- Specialized talent scarcity:Shortage of engineers proficient in both API gateway architecture and machine learning model tuning constrains enterprise deployment velocity and drives compensation inflation above general cybersecurity roles.
- Legacy infrastructure entrenchment:Large enterprises maintain decades-old SOAP-based integrations that resist retrofitting with modern REST and GraphQL security controls without service interruption.
- Input cost concentration:Cloud compute and specialized GPU clusters for training behavioral models concentrate pricing power with hyperscale providers, compressing vendor margins.
Strategic Opportunities
- Healthcare API expansion:HIPAA-mandated interoperability rules in the United States accelerate electronic health record exchange, creating demand for PHI-compliant traffic inspection and audit logging.
- IoT device authentication:Connected manufacturing and automotive platforms deploy machine-to-machine APIs at scale, opening segments where lightweight edge security modules replace heavyweight gateway deployments.
- EU AI Act compliance tooling:Algorithmic transparency requirements for automated decision systems processing personal data through APIs create certification-driven procurement criteria favoring vendors with built-in explainability features.
Industry Challenges
- Shadow endpoint discovery:Development teams deploy unauthorized APIs outside security governance, leaving organizations unable to inventory attack surfaces or enforce consistent policy.
- Cross-protocol complexity:Security teams must simultaneously protect REST, GraphQL, gRPC, and asynchronous event streams, each with distinct schema validation requirements and authentication mechanisms.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Application Programming Interface Security Market |
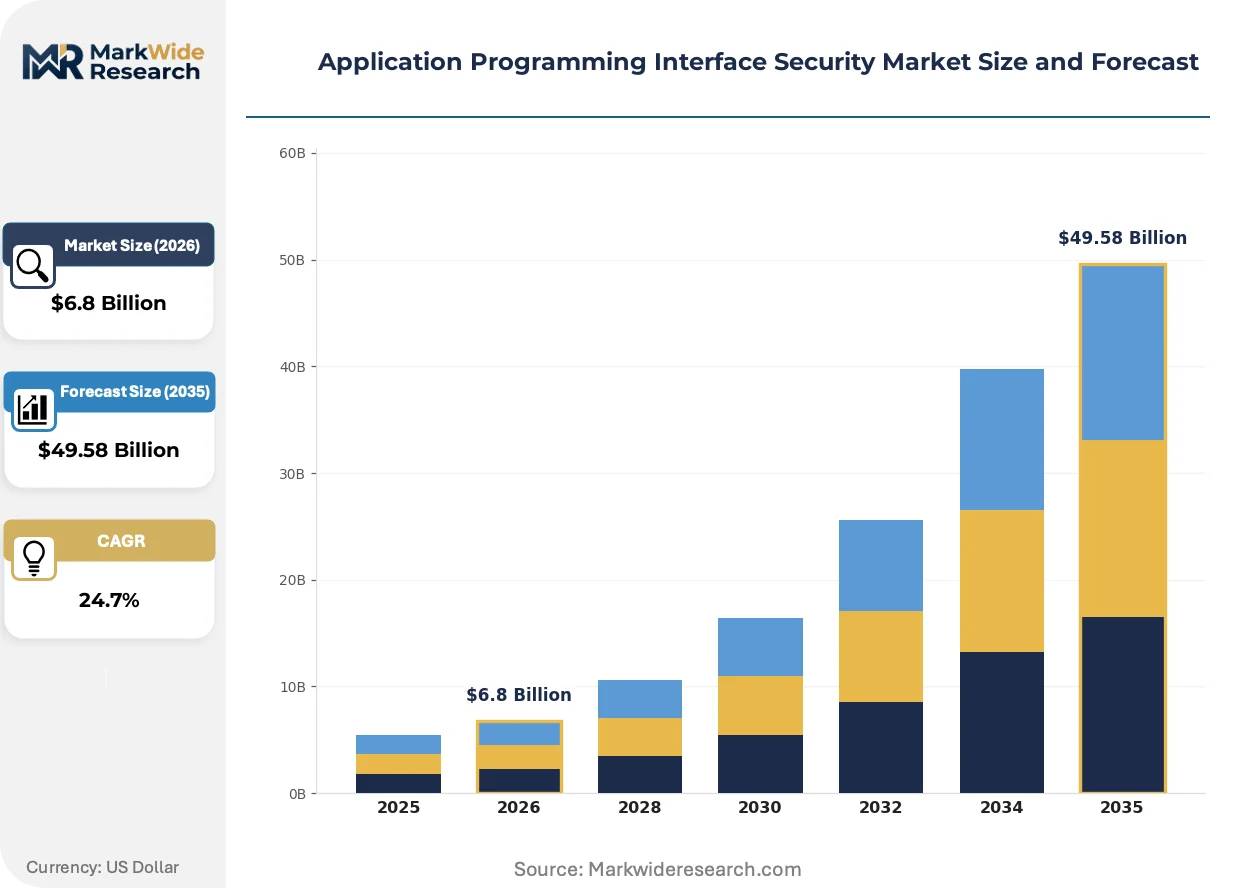
| Market Size in 2026 | $6.8 Billion |
| Market Size in 2035 | $49.58 Billion |
| CAGR (2026 – 2036) | 24.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution: Gateway Security, Threat Protection, Access Control, Testing Tools Deployment: On-Premises, Cloud-Based, Hybrid, Public Cloud End User: Enterprises, SMEs, Government, Financial Services Application: E-Commerce, Mobile Apps, Cloud Services, IoT Solutions |
| Companies Covered | Salt Security, Traceable AI, Noname Security, 42Crunch, Imperva, Akamai Technologies, Wallarm, Cequence Security, Data Theorem, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Application Programming Interface Security Market Evolving Landscape
Machine learning inference at the edge is compressing detection latency while distributed tracing architectures expose previously invisible attack paths across microservice meshes.
Speculative execution detection is electrifying runtime protection by identifying anomalous API call sequences that precede data exfiltration attempts. Financial services institutions in Singapore and the United Kingdom deploy these models to protect open banking endpoints. The technology is electrifying competitive positioning by reducing mean-time-to-detect from hours to milliseconds without constant signature updates.
The EU AI Act mandates algorithmic transparency and incident reporting for automated systems processing sensitive personal data through APIs. Financial institutions must now maintain audit trails of machine learning model decisions affecting customer outcomes. European banks and payment processors are restructuring procurement criteria to prioritize vendors with built-in explainability dashboards and automated compliance documentation.
Security procurement is consolidating around platform vendors that bundle API discovery, runtime protection, and compliance reporting under unified subscription terms. Mid-market enterprises previously buying point solutions now favor integrated suites that reduce vendor management overhead. This pattern is most visible in the United States, where CISOs face board-level pressure to demonstrate measurable risk reduction with leaner security operations teams.
Application Programming Interface Security Market Segmentation
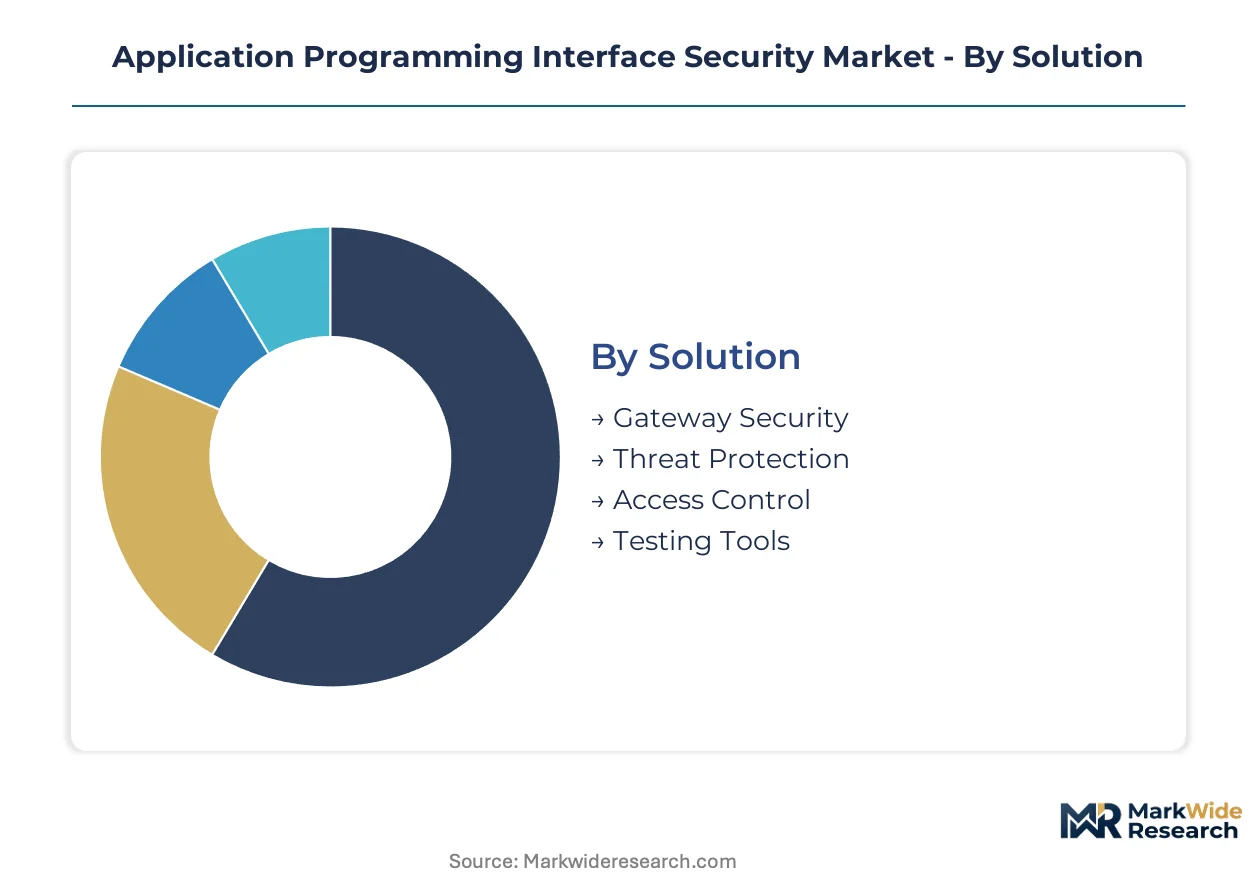
API security procurement patterns diverge sharply across organizational maturity, infrastructure legacy, and regulatory exposure. Solution architecture, deployment topology, and end-user risk profiles create distinct purchasing workflows that vendors must navigate.
Solution:
Buyers in this category separate by whether they prioritize perimeter defense or runtime behavioral analysis.
- Gateway Security:Centralized enforcement points inspect traffic at network boundaries, applying rate limiting, authentication, and encryption policies. Financial services institutions in Singapore and the United Kingdom deploy these to protect open banking endpoints against credential stuffing and DDoS attacks.
- Threat Protection:Behavioral models trained on API call sequences detect anomalous patterns preceding data exfiltration. Cloud-native fintech platforms favor this approach for shadow endpoint discovery without manual rule tuning.
- Access Control:Identity-centric authorization frameworks enforce least-privilege principles across microservice meshes.
- Testing Tools:Automated vulnerability scanners validate schema compliance and injection resistance before production deployment.
Volume sits with Gateway Security; growth tilts toward Threat Protection.
Deployment:
Infrastructure decisions track data residency requirements and cloud migration velocity.
- Cloud-Based:Fully managed services eliminate hardware procurement cycles and scale elastically with traffic spikes. Digital banks and embedded finance platforms in the United States favor this model for rapid microservice deployment.
- Hybrid:Split architectures keep sensitive authentication logic on-premises while pushing traffic inspection to cloud edge nodes. European banks navigating GDPR data localization mandates select this topology.
- On-Premises:Air-gapped installations serve defense contractors and critical infrastructure operators with strict network segmentation requirements.
- Public Cloud:Native integrations with hyperscale provider marketplaces accelerate procurement for mid-market enterprises lacking dedicated security engineering teams.
Deployment gravity centers on Cloud-Based; Hybrid configurations are climbing the fastest.
End User:
Risk tolerance and compliance burden shape procurement sophistication in this category.
- Financial Services:PSD2 open banking mandates and real-time payment network expansion drive the deepest investment pools. Institutions must validate traffic patterns against behavioral baselines while maintaining audit trails for regulatory examination.
- Enterprises:Fortune 500 organizations managing thousands of public-facing endpoints consolidate around platform vendors bundling discovery, runtime protection, and compliance reporting.
- Government:Federal agencies and defense departments prioritize FedRAMP-authorized solutions with mandatory supply chain attestation.
- SMEs:Resource-constrained organizations favor managed security service providers delivering API protection as a subscription without internal engineering overhead.
Financial Services commands procurement volume; SMEs are expanding most quickly.
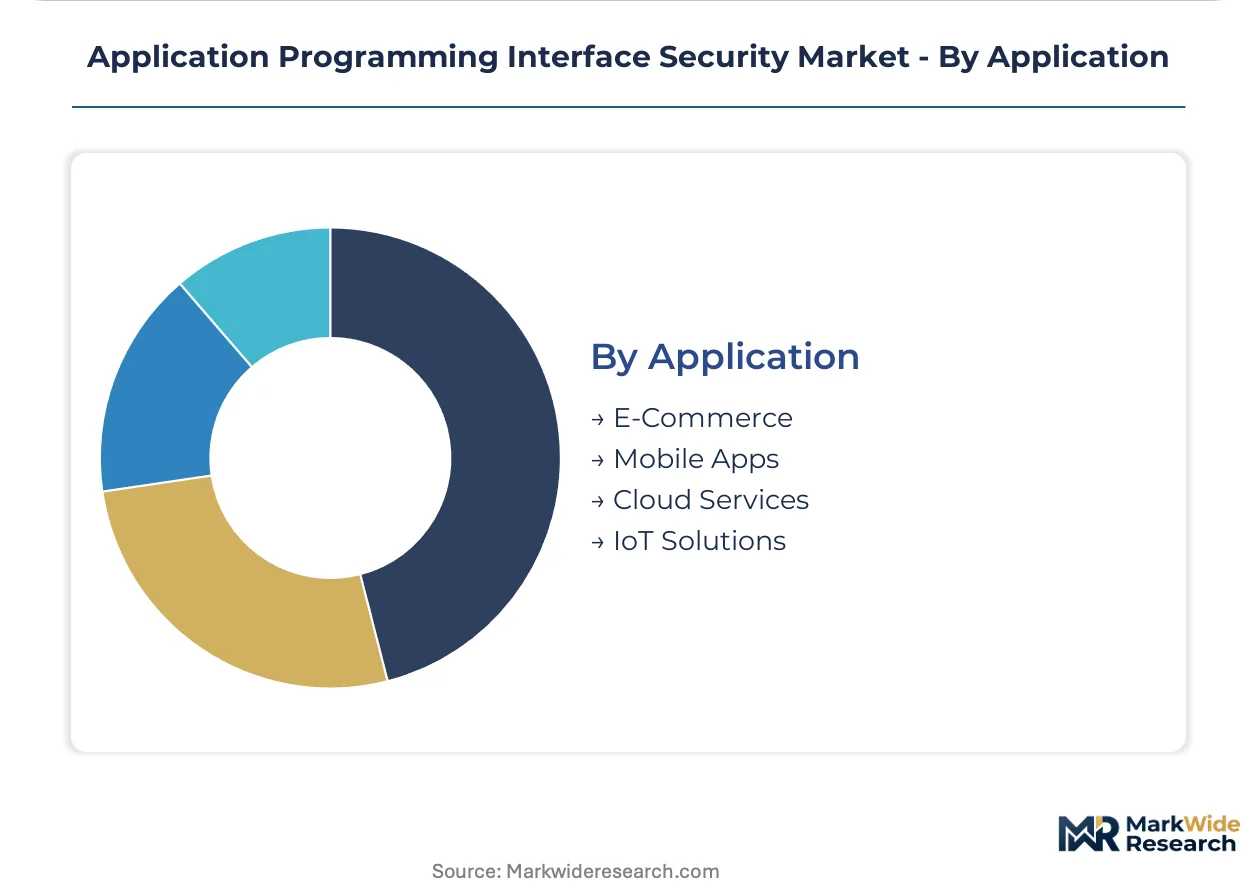
Application:
Use case complexity determines whether buyers need lightweight edge modules or comprehensive gateway deployments.
- Cloud Services:Microservice architectures generate inter-service traffic volumes requiring distributed tracing and continuous schema validation. SaaS providers in the United States anchor demand here.
- IoT Solutions:Connected manufacturing and automotive platforms deploy machine-to-machine APIs at massive scale, creating demand for lightweight authentication modules that operate at network edge.
- E-Commerce:Payment API protection against card-not-present fraud drives seasonal procurement spikes aligned with retail calendar cycles.
- Mobile Apps:Consumer-facing applications require certificate pinning and payload encryption to prevent reverse engineering and man-in-the-middle attacks.
Cloud Services dominates current procurement; IoT Solutions shows the steepest expansion trajectory.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Special economic zones in Singapore and Dubai are concentrating API security procurement as financial institutions establish regional headquarters for open banking operations. Tax incentives for fintech licensing in these jurisdictions accelerate vendor selection cycles and compliance tooling investments.
United States
FedNow real-time payment networks and cloud-native fintech proliferation drive gateway security procurement among digital banks. SEC cybersecurity disclosure rules and Federal Reserve operational resilience guidelines mandate audit trails for automated API systems. New York and San Francisco financial clusters host the deepest vendor engagement for behavioral AI threat detection platforms.
United Kingdom
PSD2 open banking mandates compel traditional institutions to expose payment APIs with runtime behavioral validation. The Financial Conduct Authority enforces operational resilience standards requiring incident reporting for automated decision systems. London's fintech corridor concentrates procurement for integrated discovery and compliance reporting suites.
Germany
Industrial IoT platforms in automotive and manufacturing deploy machine-to-machine API authentication at massive scale. BaFin banking supervision guidelines align with NIS2 Directive requirements for critical infrastructure protection. Stuttgart and Munich industrial clusters favor hybrid deployment models balancing GDPR data localization with cloud scalability.
Singapore
Monetary Authority of Singapore open banking frameworks and digital banking licenses accelerate API security spending among neobanks. The Personal Data Protection Act mandates breach notification timelines compressing vendor selection cycles. The Marina Bay financial district anchors regional procurement for real-time payment protection and speculative execution detection.
Australia
Consumer Data Right open banking mandates force major banks to expose customer data APIs with continuous traffic inspection. Australian Prudential Regulation Authority information security standards impose accountability for third-party API integrations. Sydney and Melbourne fintech hubs drive demand for cloud-native threat protection with embedded compliance documentation.
Application Programming Interface Security Market Competitive Landscape
Branded specialists and contract manufacturers split share differently across segments, with behavioral AI vendors capturing growth while legacy gateway providers defend installed base positions. The vendor base organizes into three tiers: machine learning-native platforms, web application firewall incumbents with API modules, and managed security service providers. Strategic moves center on platform consolidation bundling discovery, runtime protection, and compliance reporting, plus partnerships with hyperscale cloud providers for native marketplace distribution.
Within the machine learning-native tier, Salt Security and Traceable AI exemplify architectures displacing signature-based detection with trained behavioral models. Noname Security occupies a position emphasizing shadow endpoint discovery without manual rule tuning. These vendors anchor competitive dynamics around detection latency reduction and automated schema validation across microservice meshes.
| Leading Market Players |
|---|
| Salt Security |
| Traceable AI |
| Noname Security |
| 42Crunch |
| Imperva |
| Akamai Technologies |
| Wallarm |
| Cequence Security |
| Data Theorem |
| Others |
Value Network & Pricing Analysis
EU AI Act algorithmic transparency mandates gate qualified supply access and premium-tier pricing for API security vendors serving European financial institutions. Compliance certification costs compress margins for mid-tier providers while concentrating pricing power with vendors offering built-in explainability dashboards and automated audit documentation.
Pricing Analysis
Short lead-time premiums dominate procurement for FedNow and real-time payment network protection, with spot inventory discounts available for standardized gateway modules. The market runs on subscription-based SaaS tiers differentiated by API call volume scale and FedRAMP certification level. Pricing pressure stems from hyperscale cloud provider marketplace commissions compressing vendor margins. SMEs exhibit highest price sensitivity, while Fortune 500 financial institutions prioritize detection latency performance over unit cost.
Supply Chain Analysis
Dual-sourcing requirements from US federal agencies and European banks mandate multi-vendor qualification for runtime behavioral analysis engines. Supply concentrates in the United States, Israel, and the United Kingdom for machine learning-native platforms. GPU clusters for model training and specialized API gateway hardware constitute critical input dependencies. Single-source vulnerability in NVIDIA chip supply creates concentration risk. Distribution runs through hyperscale cloud marketplaces and direct enterprise sales teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
API security vendors are racing to deepen backward integration into behavioral model training infrastructure and downstream compliance documentation tooling. Control over GPU cluster allocation and automated audit trail generation separates margin leaders from commodity gateway providers.
For Market Incumbents: Anticipate displacement pressure from machine learning-native entrants by accelerating schema validation R&D and acquiring specialized testing tool vendors. Salt Security and Traceable AI architectures threaten legacy web application firewall installed bases. Certification investment in EU AI Act explainability features defends premium pricing in European financial services procurement cycles.
For New Entrants and Emerging Players: Capture white-space in healthcare API expansion driven by HIPAA interoperability mandates and lightweight IoT edge authentication modules for connected manufacturing. The SME segment offers lowest competitive density with managed security service provider channel partnerships as the optimal go-to-market angle.
For Investors and Strategic Acquirers: FedRAMP authorization timelines stretching beyond eighteen months is the leading indicator that vendor consolidation will accelerate among cloud-native platforms seeking government credentialing. Long-term viability hinges on platform breadth bundling discovery, runtime protection, and compliance reporting. Acquisition targets should demonstrate distributed tracing architecture and explainable AI feature sets. Deviation in NIS2 Directive enforcement intensity would shift the outlook materially.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unified discovery-runtime-compliance bundles reduce vendor management overhead for CISOs. |
| Acquisition of Specialist Firm | Testing tool vendors add automated vulnerability scanning to runtime protection portfolios. |
| Strategic Partnership | Hyperscale marketplace distribution accelerates procurement for resource-constrained mid-market buyers. |
| Geographic Expansion | Singapore and Dubai special economic zones concentrate open banking security procurement. |
| Product Launch | Speculative execution detection modules reduce mean-time-to-detect for high-velocity payment APIs. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs for this API security market analysis. Primary interviews with CISOs, API platform engineers, financial services compliance officers, and cloud procurement specialists combined with secondary sources including SEC cybersecurity disclosures, FedRAMP authorization databases, and EU AI Act implementation guidance. Bottom-up vendor revenue triangulation against top-down IT security spending estimates validated market sizing.
Data-stream reconciliation across deployment model, organization size, vertical risk profile, integration complexity, and regional regulatory framework produced volume and value outputs. CAGRs derived from trend extrapolation of open banking mandate proliferation and cloud-native fintech adoption rates. Behavioral AI inference latency benchmarks and FedNow transaction volume projections informed segment-specific trajectory modeling throughout the forecast period.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to NIS2 Directive enforcement timelines and hyperscale cloud provider pricing power. Forecasts reflect documented assumptions regarding PSD2 compliance tooling refresh cycles and real-time payment network expansion rates. Deviation in EU AI Act algorithmic transparency audit intensity would shift the outlook materially.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
E-Mail Security Market
Cybersecurity
Norway Cybersecurity Market
Cybersecurity
Cloud Encryption Gateways Market
Cybersecurity
Cyber Deception Market
Cybersecurity
Open RAN Security Market
Cybersecurity
Cloud-Based IDS IPS Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Global Bug Bounty Platforms Market
Cybersecurity
Artificial Intelligence-Based Cybersecurity Market
Cybersecurity
Peru Cybersecurity Market
Cybersecurity
Chile Cybersecurity Market
Cybersecurity
Denmark Cybersecurity Market
Cybersecurity
Cyber Security and Big Data Analytics Market
Cybersecurity
Germany Ransomware Protection Market
Cybersecurity
Colombia Cybersecurity Market
Cybersecurity
Global Managed Detection and Response (MDR) Market