
 Global Incident Response Market | 2026-2036
Global Incident Response Market Size, Share, and Industry Trends Forecast 2026-2036
Global Incident Response Market Foresight
Artificial intelligence is rebalancing how security teams detect and contain breaches, shifting analyst hours from triage to strategic response. CrowdStrike leverages native AI threat graphs to compress detection-to-response intervals. Palo Alto Networks anchors its platform strategy on integrated SOAR and XDR modules. Mandiant specializes in high-severity breach response retainers for Fortune 500 enterprises.
Incident response encompasses the structured methodology for detecting, containing, eradicating, and recovering from cybersecurity breaches, typically governed by service-level agreements measured in minutes for containment and hours for full eradication. Cloud-based deployment is outpacing on-premises installations as distributed workforces expand the attack surface beyond traditional perimeter controls. Threat intelligence and endpoint detection represent the deepest margin pools, while behavioral analytics is gaining traction among organizations seeking preemptive insider threat identification.
FCC guidelines for telecommunications breach reporting, SEC cybersecurity disclosure mandates, and EU NIS2 requirements for critical infrastructure operators are converging to mandate shorter notification windows and documented response playbooks. ISO 27035 standards further shape how enterprises structure their incident management frameworks. Stakeholders must evaluate whether their current response architectures can satisfy tightening regulatory clocks without fragmenting operational continuity.
Market Dynamics
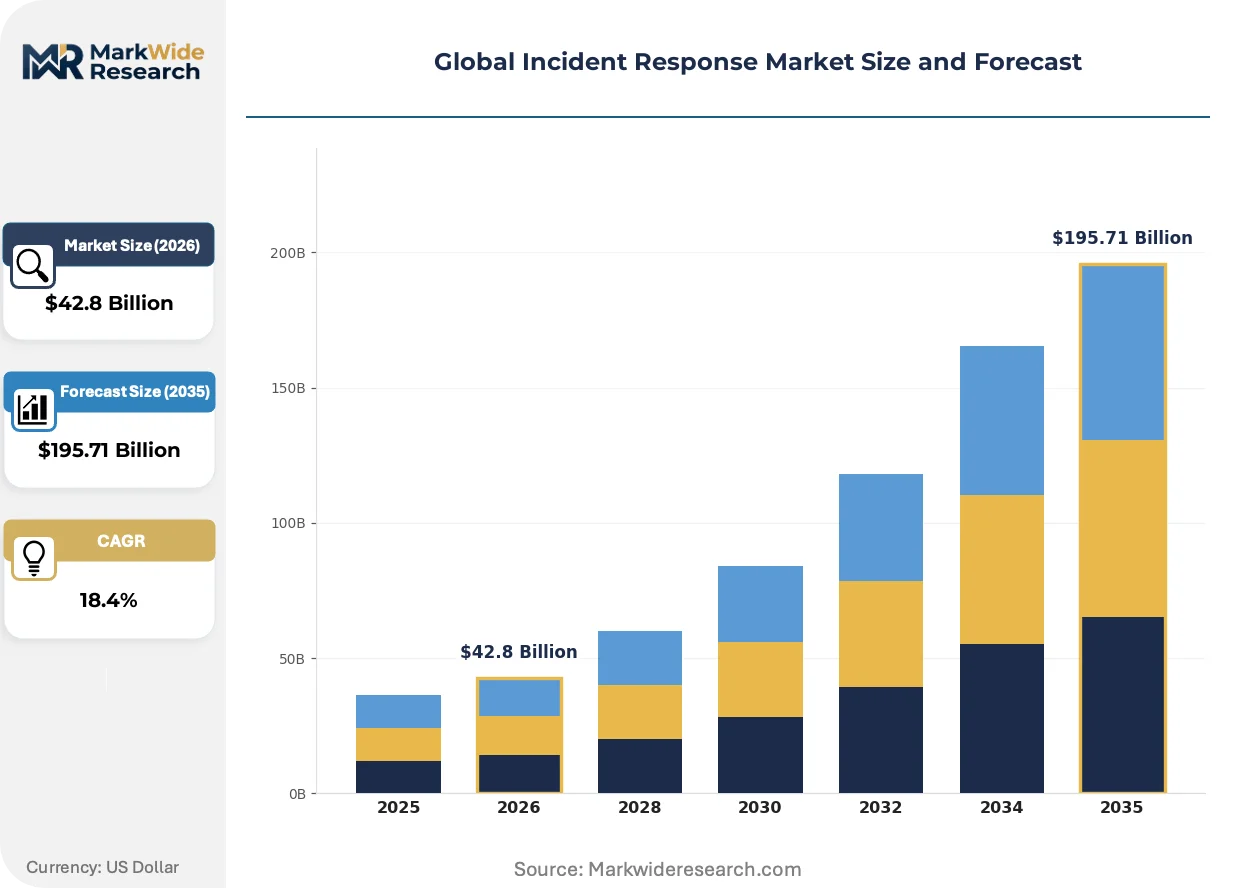
The Global Incident Response Market faces a structural compression of response timelines as ransomware dwell times shrink and regulatory disclosure windows tighten. Financial services and critical infrastructure operators now demand containment measured in minutes rather than hours.
Growth Catalysts
- EU NIS2 Directive:Critical infrastructure operators across Europe must deploy documented response playbooks with 24-hour notification mandates, forcing systematic IR retainer purchases.
- Telecommunications sector:FCC breach reporting guidelines for US carriers mandate immediate disclosure protocols, accelerating dedicated IR team buildouts at major operators.
- Cloud-native forensics:Distributed workforce architectures expand attack surfaces beyond perimeter controls, requiring cloud-based IR tooling that scales elastically during active breaches.
Market Restraints
- Specialized talent scarcity:Experienced incident responders command premium compensation, inflating service delivery costs and constraining boutique firm expansion.
- Tool fragmentation:Enterprises operate dozens of disconnected security products, creating data silos that slow correlation and extend investigation timelines.
- False positive fatigue:Alert overload from poorly tuned detection systems erodes analyst effectiveness and delays genuine threat recognition.
Strategic Opportunities
- Behavioral analytics convergence:Insider threat detection platforms combining user behavior analytics with endpoint telemetry represent underpenetrated whitespace in regulated industries.
- India's digital infrastructure:CERT-In mandates and RBI cybersecurity guidelines for financial institutions create compliance-driven demand for localized IR capabilities.
- Managed detection and response:Mid-market enterprises lacking internal SOAR expertise present channel opportunities for bundled IR subscription services.
Industry Challenges
- ISO 27035 implementation complexity:Enterprises struggle to align incident management frameworks with existing ITIL processes, creating documentation gaps during audits.
- Legacy system integration:Air-gapped industrial control environments resist modern EDR deployment, leaving critical infrastructure with blind spots during targeted intrusions.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Incident Response Market |
| Market Size in 2026 | $42.8 Billion |
| Market Size in 2035 | $195.71 Billion |
| CAGR (2026 – 2036) | 18.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Edge Computing Solution Type: Threat Intelligence, Endpoint Detection, Network Monitoring, Incident Forensics, Behavioral Analytics Use Case: Data Breach Response, Malware Removal, Insider Threat Management, Distributed Denial of Service Mitigation, Vulnerability Assessment End User Type: Financial Institutions, Telecommunications Providers, Government Agencies, Energy Operators, Educational Institutions |
| Companies Covered | Mandiant, Cisco, CrowdStrike, SentinelOne, Secureworks, Palo Alto Networks, IBM, FortiGuard, Microsoft, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Incident Response Market Shifts & Advancements
Artificial intelligence is restructuring how security operations centers triage and escalate threats, compressing the interval between initial detection and coordinated response. Three developments are redefining competitive positioning in incident response services.
XDR platforms are integrating native threat intelligence feeds with automated containment playbooks, enabling tier-one analysts to execute previously specialist-grade response actions. Mid-market enterprises lacking dedicated SOAR engineering resources adopt these bundled capabilities fastest. The technology is integrating forensic data lakes with real-time endpoint telemetry, collapsing investigation timelines from days to hours.
SEC cybersecurity disclosure mandates now require US-listed firms to report material breaches within four business days, eliminating historical disclosure delays. This regulatory pressure forces board-level accountability for IR preparedness and documented response procedures. Fortune 500 legal and risk functions are most affected, driving retainer contract renewals with guaranteed response time clauses.
Retainer pricing models are displacing pure hourly billing as CISOs seek predictable cost structures during high-severity events. Breach response services now bundle predetermined analyst hours with forensic tooling access. This shift is most visible among US healthcare systems navigating HIPAA breach notification complexities alongside ransomware recovery costs.
Global Incident Response Market Segmentation
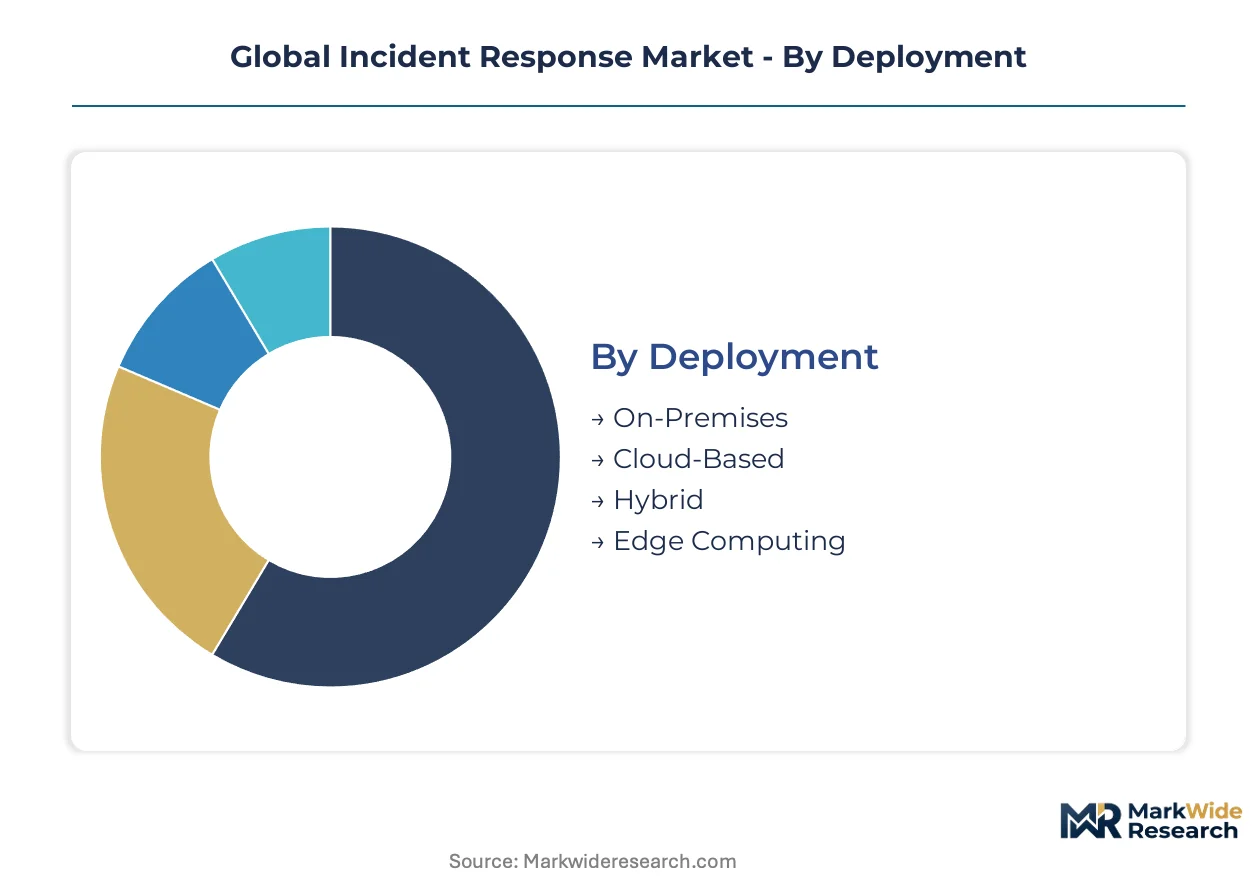
Incident response architectures fragment across deployment models, solution capabilities, and organizational risk profiles. Procurement patterns diverge sharply between enterprises seeking integrated platforms and those prioritizing specialized point solutions for targeted threat vectors.
Deployment:
Standalone deployments dominate where data sovereignty requirements block external infrastructure, while embedded cloud modules gain traction among distributed workforces.
- On-Premises:Hardware and software installations within organizational data centers, requiring dedicated security operations infrastructure. Air-gapped environments at German automotive manufacturers and US defense contractors sustain demand despite elastic cloud alternatives.
- Cloud-Based:Scalable architectures hosted by third-party providers with consumption-based pricing. Japanese financial institutions and Australian healthcare networks prioritize these deployments for rapid elastic scaling during active breach events.
- Hybrid:Orchestrated workloads spanning on-premises and cloud environments with unified management planes. Energy operators in Saudi Arabia and Canada favor this model for balancing legacy SCADA integration with modern analytics.
- Edge Computing:Distributed processing nodes deployed at network peripheries for low-latency threat containment. Manufacturing clusters across South Korea and Mexico adopt these for real-time industrial control protection.
Volume placements concentrate in Cloud-Based; the faster expansion belongs to Edge Computing.
Solution Type:
Margin structures favor intelligence-layer offerings over commodity detection tools, with behavioral platforms commanding premium pricing in regulated verticals.
- Threat Intelligence:Curated feeds of adversary tactics, infrastructure, and indicators of compromise with attribution context. US critical infrastructure operators and UK financial services firms consume these feeds to preempt ransomware campaigns.
- Endpoint Detection:Agent-based monitoring of laptops, servers, and mobile devices for anomalous process execution. Mid-market enterprises across France and Singapore standardize on these solutions as primary IR tooling.
- Network Monitoring:Deep packet inspection and flow analysis for lateral movement detection. Telecommunications providers in Brazil and India embed these capabilities within core infrastructure.
- Incident Forensics:Post-breach evidence preservation and timeline reconstruction with chain-of-custody documentation. Legal retainers from German and Swiss enterprises drive specialized provider consolidation.
- Behavioral Analytics:Machine learning models profiling user and entity behavior for insider threat identification. Healthcare systems in the United States and Netherlands adopt these for HIPAA and GDPR compliance alignment.
Revenue concentration sits with Endpoint Detection; Behavioral Analytics gains share fastest among compliance-driven buyers.
Use Case:
Response complexity and pricing correlate directly with dwell time reduction requirements, with ransomware scenarios commanding highest service premiums.
- Data Breach Response:Structured containment and notification workflows for regulated data exfiltration events. Retail and hospitality chains across the United Kingdom and Japan activate these playbooks most frequently.
- Malware Removal:Automated and manual eradication of malicious code with persistence mechanism elimination. Manufacturing facilities in Germany and Italy rely on specialized industrial control expertise for these engagements.
- Insider Threat Management:Investigation and remediation of credential misuse or data theft by authorized personnel. Financial institutions in Singapore and the United States deploy dedicated internal teams for this use case.
- Distributed Denial of Service Mitigation:Traffic scrubbing and upstream filtering to maintain service availability. Gaming platforms and media companies across South Korea and Brazil consume these services during competitive events.
- Vulnerability Assessment:Proactive identification and prioritization of exploitable security weaknesses. Government agencies in Australia and Canada mandate these assessments for vendor certification.
Service volume clusters around Data Breach Response; Insider Threat Management climbs fastest as remote work expands attack surfaces.
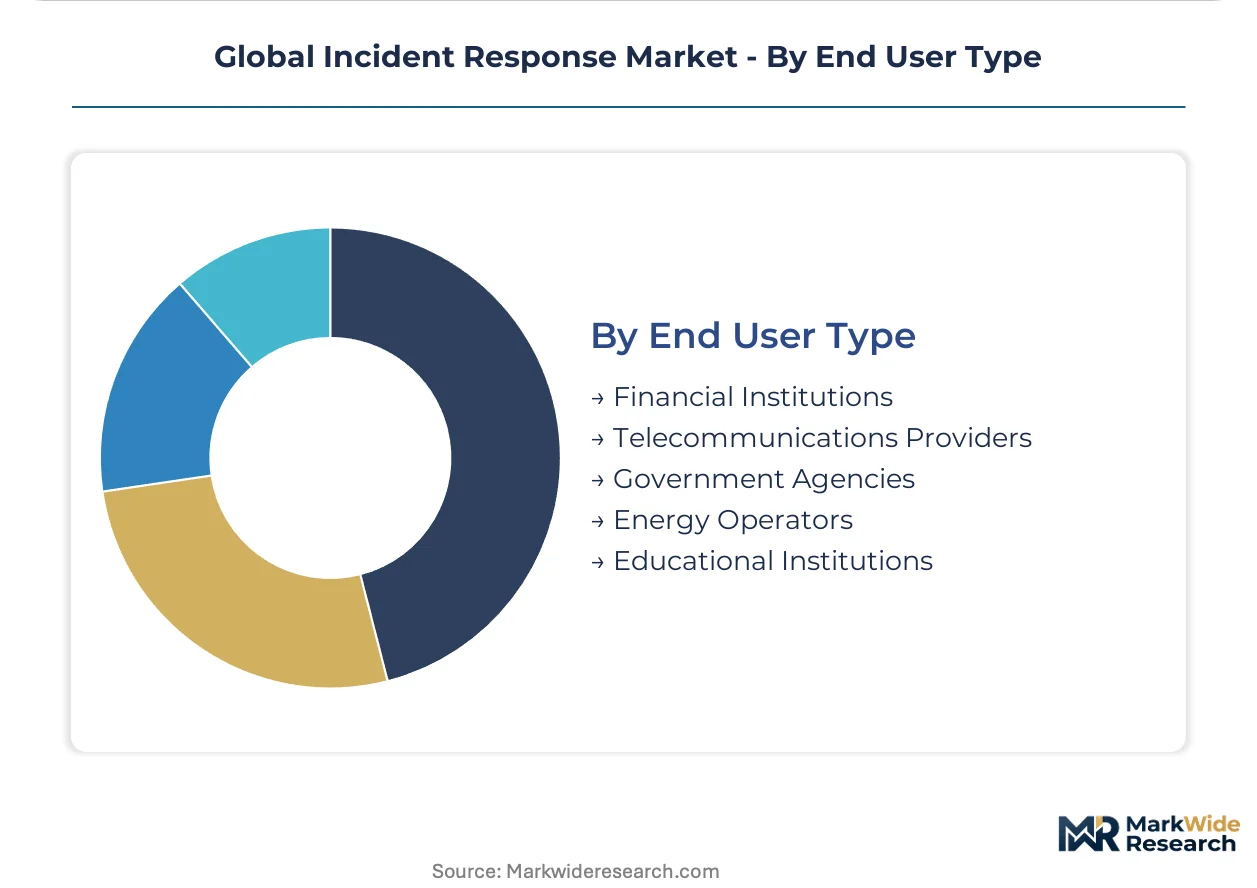
End User Type:
Procurement sophistication varies dramatically, with financial services demanding guaranteed response time clauses and educational institutions prioritizing cost containment.
- Financial Institutions:Banks, insurers, and payment processors with regulatory mandates for sub-hour containment. The SEC and RBI drive retainer contract standardization across US and Indian markets.
- Telecommunications Providers:Carriers and ISPs with FCC-mandated breach disclosure timelines. Major operators in the United States and Germany maintain 24/7 dedicated response teams.
- Government Agencies:Civilian and defense entities with classified data handling requirements. National CERT structures in France, Japan, and Australia coordinate sector-wide response capabilities.
- Energy Operators:Electric utilities and oil & gas producers with NIS2 and NERC CIP compliance obligations. European and North American operators invest heavily in OT-specific IR tooling.
- Educational Institutions:Universities and K-12 districts with limited security budgets and open network architectures. State university systems across the United States and Canada consolidate purchasing through shared services.
Contract value concentrates with Financial Institutions; Energy Operators represent the steepest expansion trajectory as critical infrastructure designations expand.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Demand for incident response services concentrates in the United States, where critical infrastructure operators face intensifying ransomware campaigns and regulatory disclosure mandates compress response timelines to hours.
United States
Financial institutions and telecommunications carriers drive procurement volume, with SEC cybersecurity disclosure rules forcing four-day breach reporting windows. FCC guidelines mandate immediate disclosure protocols for carriers, accelerating dedicated IR team buildouts at Verizon and AT&T. Healthcare systems across Texas and California navigate HIPAA breach notification alongside ransomware recovery costs.
Germany
Automotive manufacturers and industrial control operators sustain demand for air-gapped forensic capabilities. EU NIS2 Directive implementation requires documented response playbooks with 24-hour notification mandates for critical infrastructure. Manufacturing clusters in Bavaria and Baden-Württemberg invest in OT-specific IR tooling for production line protection.
United Kingdom
Financial services firms and retail chains activate data breach response playbooks most frequently under GDPR enforcement pressure. National Cyber Security Centre guidance shapes enterprise IR framework adoption across regulated sectors. London-based insurance underwriters and professional services firms drive retainer contract standardization with guaranteed response clauses.
Japan
Financial institutions and telecommunications providers standardize on cloud-based deployments for rapid elastic scaling during active events. METI cybersecurity guidelines and national CERT coordination structures shape sector-wide capability investments. Manufacturing clusters in the Chubu region around Nagoya deploy edge computing nodes for real-time industrial control protection.
India
Banks and payment processors expand IR budgets following RBI cybersecurity guidelines and CERT-In mandates for financial institutions. Mid-market enterprises lacking internal SOAR expertise present channel opportunities for bundled subscription services. Technology corridors in Karnataka and Telangana develop localized IR capabilities for compliance-driven demand.
Global Incident Response Market Competitive Landscape
Platform consolidation dominates the current landscape as endpoint detection vendors acquire SOAR and threat intelligence capabilities to compress detection-to-response intervals. The vendor base separates into three tiers: integrated platform providers, specialized breach response boutiques, and managed detection and response services. Two strategic archetypes define competitive positioning: vendors bundling XDR with native AI threat graphs, and retainer-based consultancies guaranteeing analyst response times. M&A activity and cloud-native forensic tooling development represent the dominant competitive moves reshaping market structure.
Within the integrated platform tier, CrowdStrike, Palo Alto Networks, and Mandiant exemplify divergent strategic positions. CrowdStrike occupies a position anchored on native AI threat graphs and endpoint-centric architectures. Palo Alto Networks sits within the network-security-origin expansion archetype, leveraging integrated SOAR and XDR modules. Mandiant represents the specialized breach response consultancy model, focusing on high-severity retainers for enterprise clients. These three companies illustrate how vendor origin—endpoint, network, or professional services—shapes platform development priorities and customer segmentation approaches.
| Leading Market Players |
|---|
| Mandiant |
| Cisco |
| CrowdStrike |
| SentinelOne |
| Secureworks |
| Palo Alto Networks |
| IBM |
| FortiGuard |
| Microsoft |
| Others |
Supply & Pricing Matrix
Private-equity-rolled-up specialist boutiques across the United States and United Kingdom have consolidated fragmented incident response capabilities, concentrating forensic tooling ownership among fewer holding companies and enabling coordinated pricing discipline across retainer contracts. This ownership compression tightens supply-side control while CISOs at Fortune 500 enterprises face inelastic demand for guaranteed response time clauses under SEC disclosure mandates.
Pricing Analysis
Volume concentrates in standardized endpoint detection subscriptions while margin pools in high-severity breach response retainers with guaranteed analyst deployment. Three-tier pricing structure across premium, standard, and economy levels separates Fortune 500 enterprises with 24/7 retainers from mid-market SaaS bundles and project-based forensic engagements. Cost compression in mid-market subscriptions is intensifying because Microsoft and Cisco bundle IR capabilities into broader security suites. Educational institutions exhibit highest price sensitivity due to constrained security budgets, while financial institutions under RBI and SEC mandates show lowest sensitivity to retainer premiums.
Supply Chain Analysis
Direct-to-OEM channels handle hyperscale buyer demand from telecommunications carriers and cloud providers, while value-added resellers serve mid-market enterprises lacking internal SOAR expertise. Supply concentrates in the United States, Israel, and Ireland where threat intelligence research clusters and forensic tooling development centers feed global distribution. Raw material dependencies include specialized semiconductor components for hardware forensic imagers, proprietary machine learning training datasets, and certified incident responder labor pools. Single-source vulnerability runs through Israeli threat intelligence feed providers subject to geopolitical export restrictions. Distribution runs through managed security service providers who bundle IR retainers with broader SOC offerings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
This market functions as a cost-of-compliance story where EU NIS2 Directive 24-hour notification mandates and SEC four-day disclosure rules erect substantial documentation and capability barriers that favor incumbent players with established retainer relationships and certified playbooks.
For Market Incumbents: Acquire specialized OT-security forensic boutiques to close critical infrastructure coverage gaps as energy operators face NERC CIP and NIS2 compliance deadlines. Consolidate cloud-native forensic tooling development in India and Singapore to capture CERT-In and MAS regulatory-driven demand while defending against Microsoft and Palo Alto Networks platform bundling. Vertical integration into behavioral analytics training data pipelines reduces reliance on third-party user behavior feeds. For New Entrants and Emerging Players: Enter via managed detection and response subscription bundles targeting mid-market healthcare systems in Texas and California navigating HIPAA breach notification complexity alongside ransomware recovery. India's technology corridors present the most penetrable geography where RBI guidelines and CERT-In mandates create compliance-driven demand exceeding localized IR capacity. Position around ISO 27035 implementation services to capture documentation gap remediation during enterprise audits. For Investors and Strategic Acquirers: Retainer contract renewal rates above 85% across Fortune 500 legal and risk functions is the leading indicator that platform consolidation will accelerate toward integrated XDR-SOAR providers with native AI threat graphs. Acquisition targets should display vertical-specific certification depth in financial services or healthcare alongside elastic cloud forensic infrastructure. Watch for FCC enforcement actions against telecommunications carriers as signals of regulatory clock compression driving dedicated IR team buildouts.| Strategic Initiative | Industry Significance |
|---|---|
| Acquisition of Specialist Firm | Consolidates OT-forensic capabilities for NERC CIP and NIS2 compliance at European energy operators. |
| Platform Integration | Embeds SOAR automation into XDR consoles, compressing detection-to-response intervals for tier-one analysts. |
| Geographic Expansion | Establishes localized IR capabilities in Karnataka and Telangana to serve RBI-mandated financial institutions. |
| Strategic Partnership | Aligns behavioral analytics vendors with HIPAA-covered entities for preemptive insider threat identification. |
| Product Launch | Introduces edge computing forensic nodes for real-time industrial control protection in South Korean manufacturing. |
Research Methodology
SEC cybersecurity disclosure filings, EU NIS2 implementation guidance documents, and RBI circulars on information security formed the secondary backbone, cross-referenced against primary interviews with CISOs at financial institutions, incident response retainer managers at specialized boutiques, SOC directors at telecommunications carriers, and compliance officers at critical infrastructure operators. Bottom-up triangulation across deployment model adoption rates and top-down validation against regulatory mandate timelines anchored market sizing.
Historical trendline analysis of retainer contract pricing and cloud-native forensic tooling deployment informed the projection framework across the analysis window. Segmentation dimensions modeled include deployment architecture, solution capability layer, organizational risk profile, and regulatory jurisdiction cluster. CAGRs were derived from elasticity-adjusted adoption curves incorporating SEC disclosure timeline compression and EU critical infrastructure designation expansion. Forecast inputs encompass ransomware dwell time reduction targets and ISO 27035 certification penetration rates.
Forecast precision tightens around the base case; tail outcomes carry wider variance under sustained sovereign-backed cyberattack campaigns or abrupt regulatory clock acceleration beyond current NIS2 and SEC mandates. Periodic stress-testing of base assumptions is recommended, particularly regarding specialist talent scarcity constraints and cloud provider platform bundling intensity.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Disaster Recovery Solutions
Global Data Protection and Recovery Solutions Market
Disaster Recovery Solutions
Rope Rescue Harness Market
Disaster Recovery Solutions
Business Continuity Management Planning Solution Market
Disaster Recovery Solutions
Incident and Deviation Management Solution Market
Disaster Recovery Solutions
Flood Protection Sandbags Market
Disaster Recovery Solutions
Global Security Solutions Market
Disaster Recovery Solutions
France Ransomware Protection Market
Disaster Recovery Solutions
Business Continuity Management Solutions Market
Disaster Recovery Solutions
Incident Response Services Market
Disaster Recovery Solutions
Global Data Resiliency Market
Disaster Recovery Solutions
Global Disaster Recovery Software Market
Disaster Recovery Solutions
Rescue Pole Market
Disaster Recovery Solutions
Spain Ransomware Protection Market
Disaster Recovery Solutions
Latin America Incident Response Services Market
Disaster Recovery Solutions
Italy Ransomware Protection Market
Disaster Recovery Solutions
Disaster Preparedness Systems Market