
 Global File Integrity Monitoring Market | 2026-2036
Global File Integrity Monitoring Market Size, Share, and Industry Trends Forecast 2026-2036
Global File Integrity Monitoring Market Foresight
The gap between premium enterprise-grade file integrity monitoring and commodity open-source alternatives is shifting as regulated industries demand agentless cloud-native architectures with sub-second change detection. CrowdStrike leverages its endpoint security footprint to extend file integrity capabilities across distributed Kubernetes clusters. Tripwire anchors its position through deep configuration management integration that sustains long-term contracts with energy sector operators. McAfee competes on brand recognition and channel density in mid-market financial services accounts.
File integrity monitoring comprises automated systems that track unauthorized or unexpected modifications to files, directories, and configuration states through cryptographic hashing, real-time event streaming, and policy-driven alerting. The technology serves critical infrastructure protection by detecting tampering that precedes data breaches or compliance violations. Cloud-based deployment leads solution type growth as organizations abandon capital-intensive on-premises server farms, while real-time monitoring captures the fastest expansion trajectory among solution categories due to zero-trust architecture mandates. Policy compliance applications concentrate margin pools because auditors require immutable logs that satisfy SOX, HIPAA, and PCI-DSS evidentiary standards.
The US Federal Energy Regulatory Commission enforces mandatory file integrity controls for electric utility cyber assets under CIP-010 configuration management requirements. European GDPR supervisory authorities and the EU AI Act impose algorithmic transparency obligations that amplify demand for tamper-evident model repositories. Japan's METI cybersecurity framework and South Korea's K-ISMS certification extend similar file monitoring expectations across Asia-Pacific critical infrastructure. Stakeholders must evaluate whether their current tooling can map file-level changes to identity provider audit trails without degrading system performance.
Market Dynamics
Zero-trust security mandates are compressing detection latency requirements from minutes to milliseconds, forcing vendors to rebuild agent architectures for ephemeral container workloads rather than static servers.
Growth Catalysts
- PCI-DSS audit mandates:Financial services firms in the United States face quarterly file integrity attestation requirements that sustain procurement cycles for automated monitoring platforms.
- Japan METI cybersecurity framework:Critical infrastructure operators must deploy tamper-evident logging systems that integrate with national incident response protocols.
- Containerized workload expansion:Kubernetes orchestration across hybrid cloud environments creates attack surfaces that legacy agent-based tools cannot instrument without performance degradation.
Market Restraints
- Specialized engineering talent scarcity:Cryptographic hashing optimization and kernel-level event streaming require skills concentrated among contributors to eBPF and Windows ETW frameworks.
- On-premises data gravity:Healthcare and energy sector buyers in Germany and France maintain air-gapped systems that resist cloud-native deployment models.
- Agent footprint overhead:Real-time file system hooks consume CPU and memory resources that conflict with latency-sensitive trading applications in capital markets.
Strategic Opportunities
- India BIS critical infrastructure standards:Upcoming mandatory cybersecurity certifications for power grid and telecommunications operators will open procurement windows for foreign solution providers.
- Algorithmic model provenance:EU AI Act requirements for tamper-evident machine learning artifact repositories create adjacent demand beyond traditional file integrity use cases.
- Managed detection service bundling:MSSP channel partners in Brazil and Mexico seek white-label file integrity modules to differentiate commodity endpoint offerings.
Industry Challenges
- Legacy SIEM integration complexity:Decades-old security information platforms at Fortune 500 enterprises lack native APIs for structured file change telemetry, forcing expensive connector development.
- Cross-border data residency conflicts:Brazilian LGPD and Chinese PIPL requirements fragment telemetry storage architectures, complicating single-pane-of-glass deployments for multinational corporations.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global File Integrity Monitoring Market |
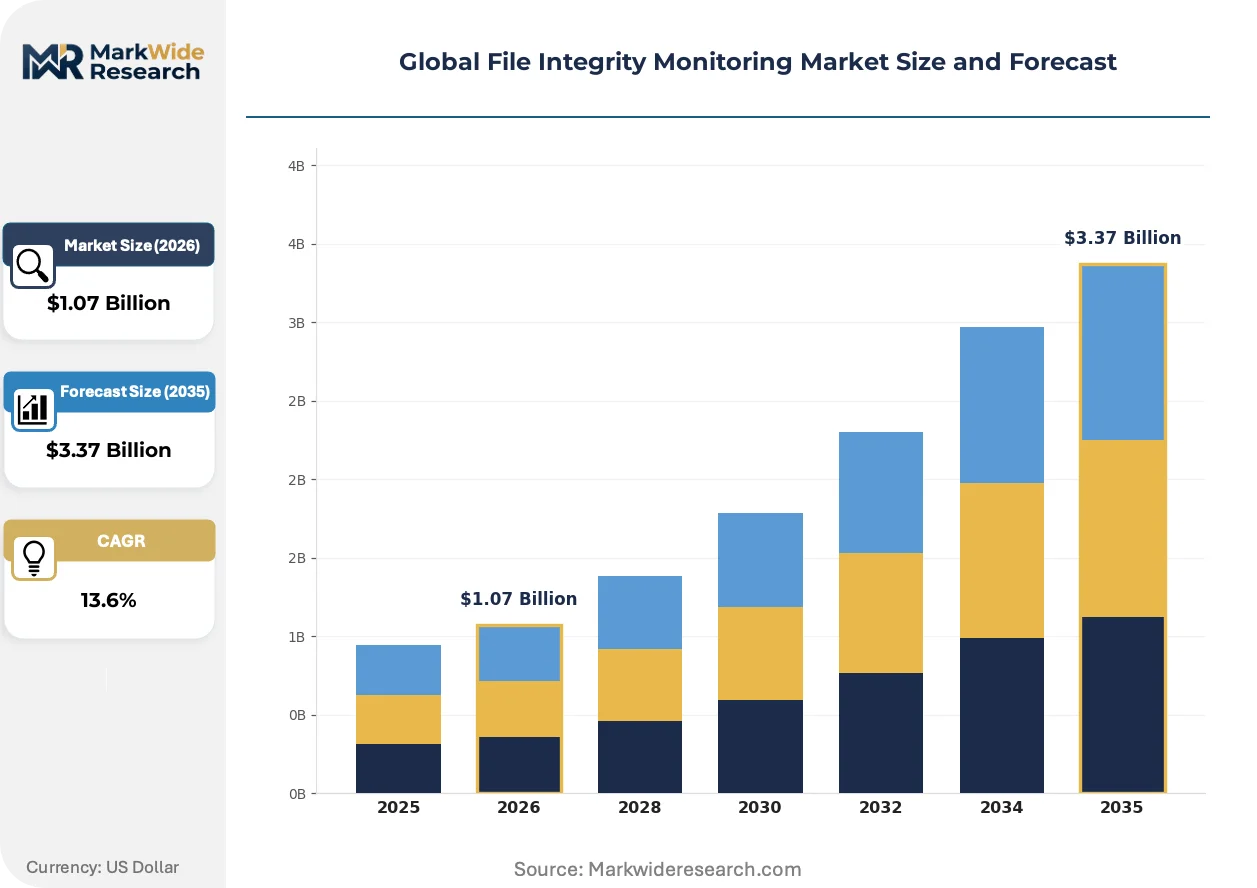
| Market Size in 2026 | $1.07 Billion |
| Market Size in 2035 | $3.37 Billion |
| CAGR (2026 – 2036) | 13.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Solution Type: Real-Time Monitoring, Log Analysis, Configuration Management, Policy Compliance, Change Detection Application: Cybersecurity, Compliance Auditing, Data Protection, Insider Threat Detection, Malware Prevention End User: Financial Services, Government Agencies, IT & Telecom, Manufacturing, Energy & Utilities |
| Companies Covered | SolarWinds, Wazuh, McAfee, CrowdStrike, ManageEngine, Tripwire, IBM Security, Cisco Systems, Qualys, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global File Integrity Monitoring Market Shifts & Advancements
Extended Berkeley Packet Filter instrumentation is displacing kernel module approaches for file system event capture, enabling monitoring without traditional agent installation overhead.
eBPF-based telemetry collection is integrating cryptographic hashing directly into Linux kernel tracepoints, eliminating context switches between user-space agents and file system drivers. Large SaaS providers in the United States are deploying this architecture across multi-tenant Kubernetes clusters to achieve sub-100-millisecond change detection without guest OS modifications. The approach is compressing total cost of ownership for cloud-native workloads by removing per-instance licensing overhead.
EU AI Act algorithmic transparency obligations are mandating immutable audit trails for training data sets and model weights before systems deploy in high-risk categories. Financial services firms in Frankfurt and Amsterdam are constructing tamper-evident model registries that satisfy both GDPR supervisory authority expectations and internal risk committee requirements. This regulatory vector is expanding addressable market scope beyond traditional IT security buyers into data science governance functions.
Consumption-based licensing is displacing perpetual seat-count contracts as the dominant procurement model for mid-market buyers. Healthcare systems in the United Kingdom and Australia prefer monthly billing tied to monitored endpoint volume rather than upfront capital commitments. This shift is forcing incumbent vendors to rebuild revenue recognition systems and partner compensation structures.
Global File Integrity Monitoring Market Segmentation
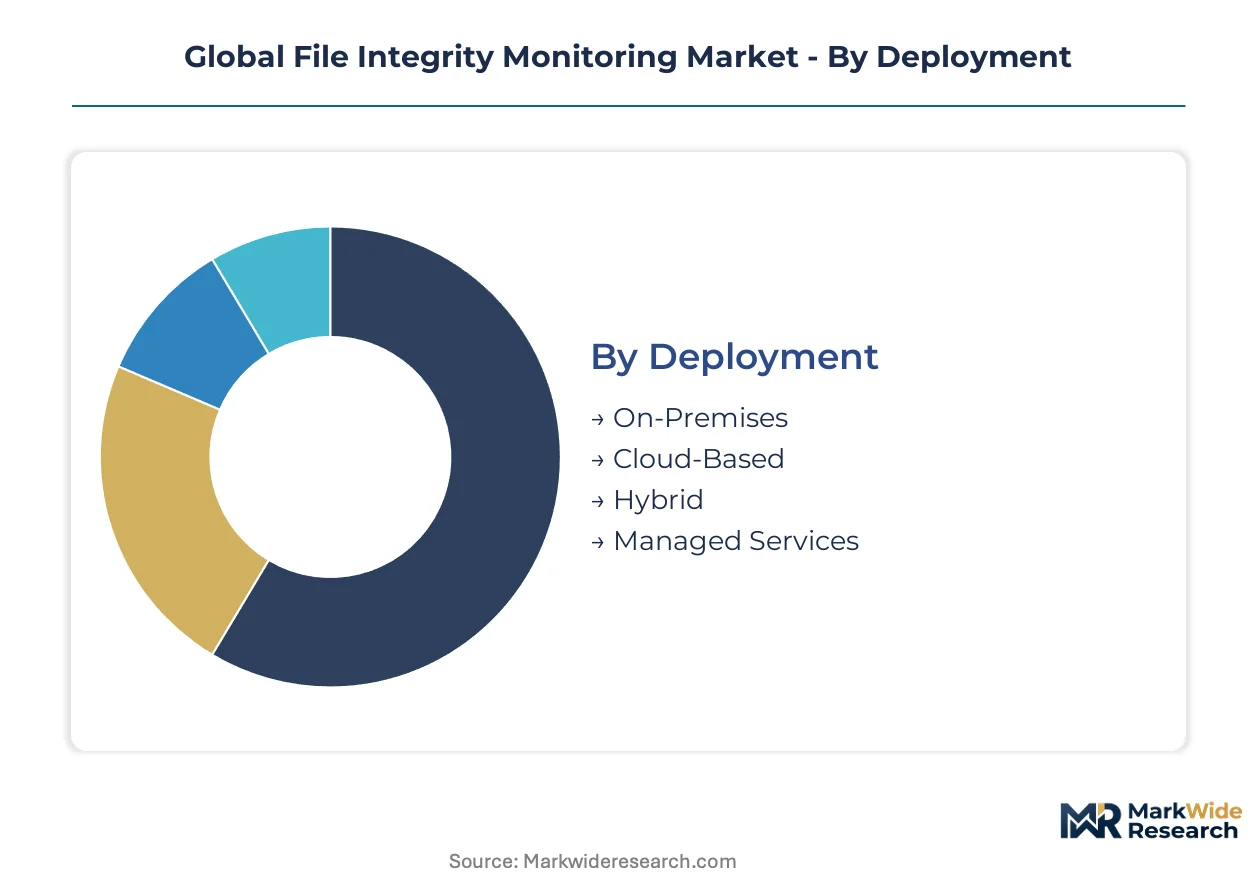
File integrity monitoring procurement varies sharply by infrastructure maturity and regulatory exposure. Buyers prioritize deployment flexibility, solution granularity, and audit-readiness depending on their cloud migration stage and compliance burden.
Deployment:
Capital commitment thresholds and data residency requirements determine deployment choice more than technical preference.
- Cloud-Based:Multi-tenant architectures with API-driven policy management eliminate server maintenance overhead. Healthcare systems in the United Kingdom and Australia favor monthly consumption billing tied to monitored endpoint volume rather than perpetual licenses.
- Hybrid:Unified control planes span on-premises legacy systems and containerized cloud workloads without telemetry fragmentation. European banking sectors accelerating cloud migration sustain procurement cycles for these architectures.
- On-Premises:Air-gapped installations serve German and French healthcare operators with strict data gravity requirements.
- Managed Services:MSSP channel partners in Brazil and Mexico white-label file integrity modules to differentiate commodity endpoint offerings.
Volume sits with On-Premises; growth tilts toward Cloud-Based.
Solution Type:
Detection latency specifications separate enterprise-grade procurement from mid-market adoption.
- Real-Time Monitoring:Kernel-level event streaming through eBPF instrumentation achieves sub-100-millisecond change detection without guest OS modifications. Zero-trust architecture mandates across United States federal agencies compress detection requirements from minutes to milliseconds.
- Policy Compliance:Immutable log architectures satisfy SOX, HIPAA, and PCI-DSS evidentiary standards for auditor attestation. Financial services firms in the United States face quarterly file integrity requirements that sustain premium pricing.
- Log Analysis:Structured telemetry ingestion for legacy SIEM platforms at Fortune 500 enterprises demands expensive connector development.
- Configuration Management:Deep integration with infrastructure-as-code pipelines supports energy sector operators under FERC CIP-010 mandates.
- Change Detection:Cryptographic hashing at Linux kernel tracepoints eliminates context switches between user-space agents and file system drivers.
Revenue concentrates in Policy Compliance; steepest expansion trajectory belongs to Real-Time Monitoring.
Application:
Risk ownership structures—CISO versus compliance officer—drive feature prioritization and budget source.
- Cybersecurity:File integrity serves as an early warning layer for tampering that precedes data exfiltration or ransomware deployment.
- Compliance Auditing:Automated attestation workflows reduce manual evidence collection for PCI-DSS, GDPR, and Japan METI framework assessments.
- Data Protection:Integrity verification for backup repositories prevents restoration of compromised golden images.
- Insider Threat Detection:Privileged user activity correlation with file-level changes identifies credential misuse patterns.
- Malware Prevention:Unauthorized binary modifications trigger isolation workflows before payload execution.
Spend clusters in Compliance Auditing; Cybersecurity applications gain share fastest.
End User:
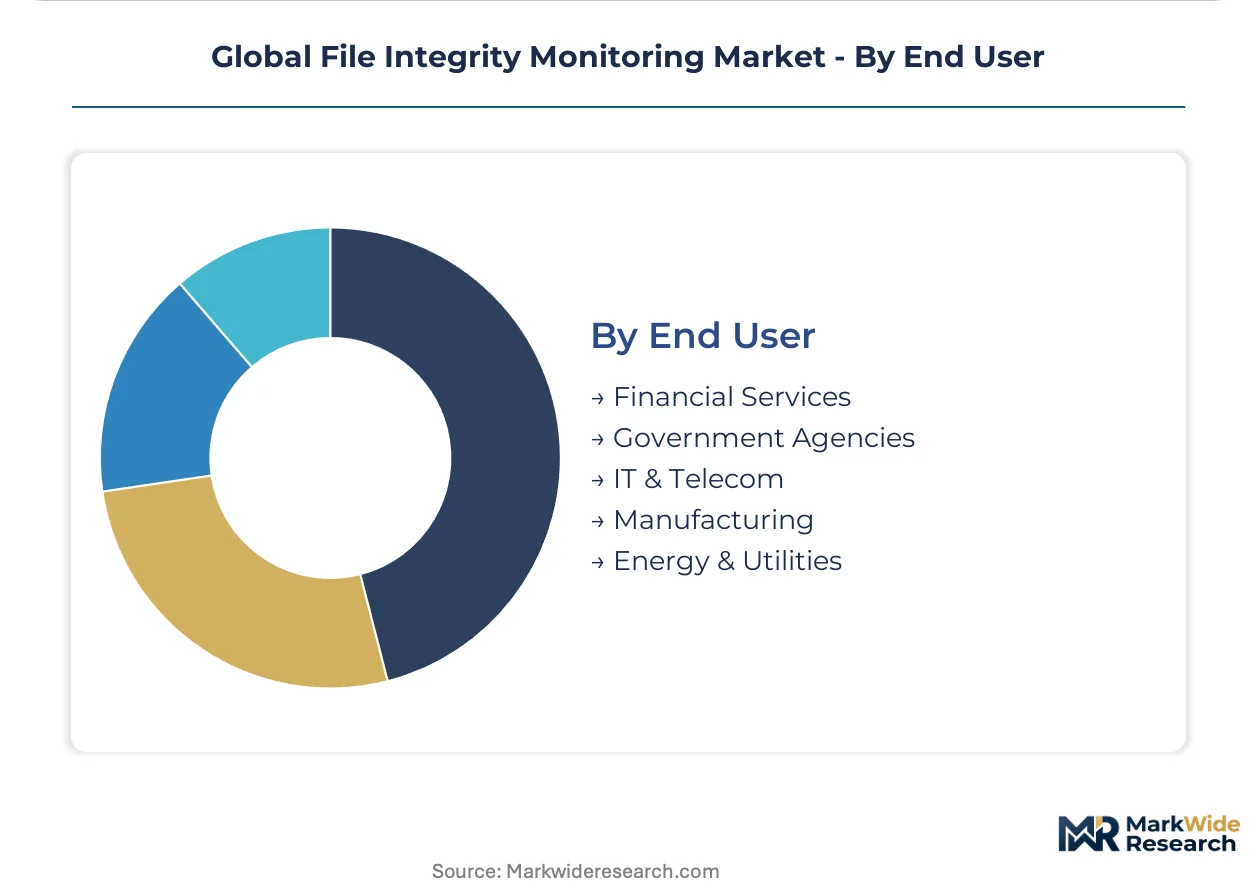
Regulatory enforcement intensity and critical infrastructure designation determine solution sophistication and contract duration.
- Financial Services:Capital markets firms demand agentless architectures that avoid CPU overhead conflicts with latency-sensitive trading applications. PCI-DSS audit mandates sustain recurring procurement for automated monitoring platforms.
- Government Agencies:United States federal deployments follow zero-trust mandates with sub-second detection requirements for classified networks.
- IT & Telecom:Multi-tenant Kubernetes clusters at large SaaS providers drive eBPF-based instrumentation adoption.
- Energy & Utilities:FERC CIP-010 configuration management requirements enforce mandatory file integrity controls for electric utility cyber assets.
- Manufacturing:Operational technology networks with legacy Windows systems resist cloud-native deployment models.
Contract value peaks in Financial Services; Energy & Utilities shows strongest renewal rates.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
San Francisco Bay Area technology corridors anchor global procurement for cloud-native file integrity platforms, with federal compliance mandates and financial sector zero-trust architectures driving concentrated demand across three continents.
United States
FERC CIP-010 requirements enforce mandatory file integrity controls for electric utility cyber assets, while PCI-DSS quarterly attestation sustains procurement cycles among capital markets firms. New York and Chicago trading floors demand agentless architectures that avoid CPU overhead conflicts with latency-sensitive applications.
Germany
Air-gapped healthcare systems in Bavaria and Baden-Württemberg resist cloud-native deployment models due to strict data gravity requirements. The national cybersecurity authority BSI mandates tamper-evident logging for critical infrastructure operators, sustaining on-premises installation preferences among energy sector buyers.
United Kingdom
NHS trusts across England prefer monthly consumption billing tied to monitored endpoint volume rather than perpetual licenses. London financial services clusters deploy hybrid architectures spanning legacy mainframes and containerized cloud workloads to satisfy FCA operational resilience requirements.
Japan
METI cybersecurity framework obligations require critical infrastructure operators to deploy tamper-evident logging systems integrated with national incident response protocols. Tokyo and Osaka metropolitan manufacturing hubs resist Kubernetes-native tooling due to legacy Windows-based operational technology networks.
India
Upcoming BIS mandatory cybersecurity certifications for power grid and telecommunications operators will open procurement windows for foreign solution providers. Mumbai financial district and Bangalore technology corridors demonstrate early adoption of eBPF-based instrumentation for multi-tenant cloud environments.
Global File Integrity Monitoring Market Competitive Landscape
Capital-heavy endpoint security platforms compete with asset-light open-source monitoring tools for enterprise procurement budgets. The vendor base separates into three tiers: integrated cybersecurity suites with bundled file integrity modules, standalone configuration management specialists, and cloud-native telemetry platforms. Consolidation pressures favor vendors with existing SIEM relationships and federal certification pathways. Dominant competitive moves include strategic partnerships with managed security service providers and technology licensing for kernel-level instrumentation frameworks.
Within the integrated security suite tier, CrowdStrike and McAfee exemplify vendors leveraging endpoint protection footprints to extend file integrity capabilities across distributed workloads. Tripwire occupies a position among configuration management specialists anchoring long-term contracts with energy sector operators under FERC mandates. SolarWinds represents the network management heritage segment seeking to reposition monitoring toolchains for zero-trust compliance requirements.
| Leading Market Players |
|---|
| SolarWinds |
| Wazuh |
| McAfee |
| CrowdStrike |
| ManageEngine |
| Tripwire |
| IBM Security |
| Cisco Systems |
| Qualys |
| Others |
Supply & Pricing Matrix
Enterprise-grade agentless architectures with sub-second detection capabilities command premium positioning against open-source alternatives, bifurcating procurement budgets between capital-intensive federal deployments and consumption-billed mid-market healthcare systems. This performance-certification divergence manifests in tiered SaaS structures for cloud-native buyers and perpetual licensing for air-gapped German energy operators.
Pricing Analysis
Outcome-based pricing tied to audit-pass rates and compliance attestation sustains premium tiers among United States financial services firms facing quarterly PCI-DSS mandates. Three-tier pricing structure across premium, standard, and economy levels separates FERC-certified energy deployments from consumption-billed NHS trusts and open-source Wazuh implementations. Cost compression in the mid-market intensifies because hyperscaler Kubernetes tooling commoditizes kernel-level instrumentation. Capital markets firms exhibit lowest price sensitivity due to trading-floor latency requirements, while Brazilian MSSP partners face acute margin pressure in white-label bundling negotiations.
Supply Chain Analysis
Refurbishment flows for legacy SIEM connectors and kernel-module agent architectures sustain secondary markets among Fortune 500 enterprises with decades-old telemetry platforms. Supply concentrates in the United States for eBPF instrumentation talent, India for offshore MSSP delivery, and Germany for air-gapped configuration management hardware. Component dependencies include cryptographic hashing libraries, kernel tracepoint frameworks, and immutable log storage substrates. Single-source vulnerability in eBPF contributor pools creates bottleneck risk for real-time detection capabilities. Distribution runs through direct enterprise sales for federal certifications and hyperscaler marketplaces for cloud-native consumption billing.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Consolidation pressure from zero-trust mandate compliance costs will eliminate vendors lacking kernel-level instrumentation capabilities or federal certification pathways.
For Market Incumbents: To counter hyperscaler commoditization of container-native monitoring, CrowdStrike and Tripwire must deepen SIEM partnership ecosystems and acquire eBPF specialist teams. Certification investment in FERC CIP-010 and EU AI Act algorithmic provenance standards anchors long-term contract renewal rates with energy and financial services accounts. For New Entrants and Emerging Players: Indian power grid operators facing upcoming BIS mandatory certifications represent the most penetrable buyer archetype for foreign solution providers lacking established federal footprints. White-label MSSP partnerships in Mexico and Brazil offer channel leverage without direct enterprise sales infrastructure. Consumption-based pricing with monthly endpoint billing aligns procurement patterns with NHS trust and Australian healthcare preferences. For Investors and Strategic Acquirers: Re-rating potential sits with configuration management specialists possessing FERC-certified energy sector contracts given renewable grid modernization catalysts. Acquisition targets should demonstrate kernel-level instrumentation IP and established incident response protocol integrations. Practitioners should monitor EU AI Act implementation timelines for tamper-evident model registry demand inflections.| Strategic Initiative | Industry Significance |
|---|---|
| Kernel-Level Instrumentation Acquisition | eBPF specialist teams eliminate context-switch overhead for sub-100-millisecond detection in Kubernetes clusters. |
| Federal Certification Pathway Investment | FERC CIP-010 and zero-trust mandates sustain premium pricing among United States electric utilities. |
| Managed Detection Service Partnership | White-label modules differentiate Brazilian and Mexican MSSP offerings from commodity endpoint security. |
| Algorithmic Provenance Registry Launch | EU AI Act compliance expands addressable market into data science governance functions beyond traditional security buyers. |
| Consumption Billing Infrastructure Buildout | Monthly endpoint-based pricing aligns with United Kingdom and Australian healthcare procurement preferences. |
Research Methodology
Trade association data, regulatory filings, and customs records anchored secondary inputs, supplemented by primary interviews with CISOs at financial services firms, compliance officers at German energy utilities, platform engineers at United States hyperscalers, and MSSP channel partners in Latin America. SEC 10-K disclosures, FERC CIP-010 audit documentation, METI framework implementation guidelines, and NHS procurement databases provided validation. Bottom-up endpoint deployment estimates and top-down cybersecurity spending allocations were triangulated for market sizing.
Deployment model, organization size, vertical regulatory exposure, integration complexity, and regional cloud adoption maturity were modeled at segment-level granularity across the analysis window. CAGRs derived from historical procurement cycle analysis and projected compliance mandate phase-in schedules. Forecast inputs included PCI-DSS audit frequency data, Kubernetes cluster growth trajectories at SaaS providers, and BIS certification timeline announcements for Indian critical infrastructure.
Revisions become necessary when eBPF instrumentation talent scarcity accelerates, hyperscalers bundle file integrity capabilities into base platform offerings, or data residency conflicts fragment single-pane-of-glass architectures. Forecasts reflect assumptions about regulatory enforcement consistency and cloud migration pace among European banking sectors. Practitioners should monitor EU AI Act delegated act publications and Indian BIS certification finalization dates for early signals.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Deception Technology Market
Cybersecurity
Turkey Cybersecurity Market
Cybersecurity
Multi-Cloud Data Protection Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Asia-Pacific Cloud DLP Market
Cybersecurity
Network Edge Security Solutions Market
Cybersecurity
Next-Generation Firewall Market
Cybersecurity
Cloud Siem Market
Cybersecurity
Ddos Protection and Mitigation Security Market
Cybersecurity
Global Cyber Data Security Market
Cybersecurity
Advanced Malware Detection (AMD) Market
Cybersecurity
Global Patch Management Market
Cybersecurity
Global Serverless Security Market
Cybersecurity
CDN Security Market
Cybersecurity
India Cybersecurity Market
Cybersecurity
Latin America Ransomware Protection Market