
 US Hardware OTP Token Authentication Market | 2026-2036
US Hardware OTP Token Authentication Market Size, Share, and Industry Trends Forecast 2026-2036
US Hardware OTP Token Authentication Market Analytics
Defense contractor demand is rebalancing the US Hardware OTP Token Authentication Market as classified program budgets expand. Thales Group leverages its FIPS 140-2 certified manufacturing to sustain dominance in federal supply chains. Yubico Inc anchors the commercial segment with USB-C hardware tokens optimized for cloud-native enterprises. RSA Security LLC competes through deep integration with legacy identity management platforms across Fortune 500 accounts.
US Hardware OTP Token Authentication encompasses physical devices generating one-time passcodes through cryptographic algorithms, typically employing tamper-resistant secure elements with clock synchronization or event counters for code generation. These devices serve as possession factors in multi-factor authentication frameworks, providing out-of-band identity verification resistant to phishing and credential replay attacks. Hardware Tokens retain the largest installed base among product types, though USB Tokens capture expanding share as workstation form factors standardize on USB-C interfaces. Time-Synchronized technology leads volume deployment due to interoperability with existing RSA SecurID infrastructure, while Hybrid Systems represent the fastest-growing technology segment as agencies mandate post-quantum cryptographic migration paths.
NIST, FISMA, and HIPAA collectively shape product requirements, with NIST SP 800-63B dictating authenticator assurance levels and FISMA mandating hardware-based factors for federal systems above moderate impact classification. The Department of Defense's CMMC framework extends these requirements to contractor supply chains, creating tiered compliance obligations. Stakeholders must monitor NIST's ongoing post-quantum cryptography standardization timeline to align hardware refresh cycles with emerging algorithm requirements.
Market Dynamics
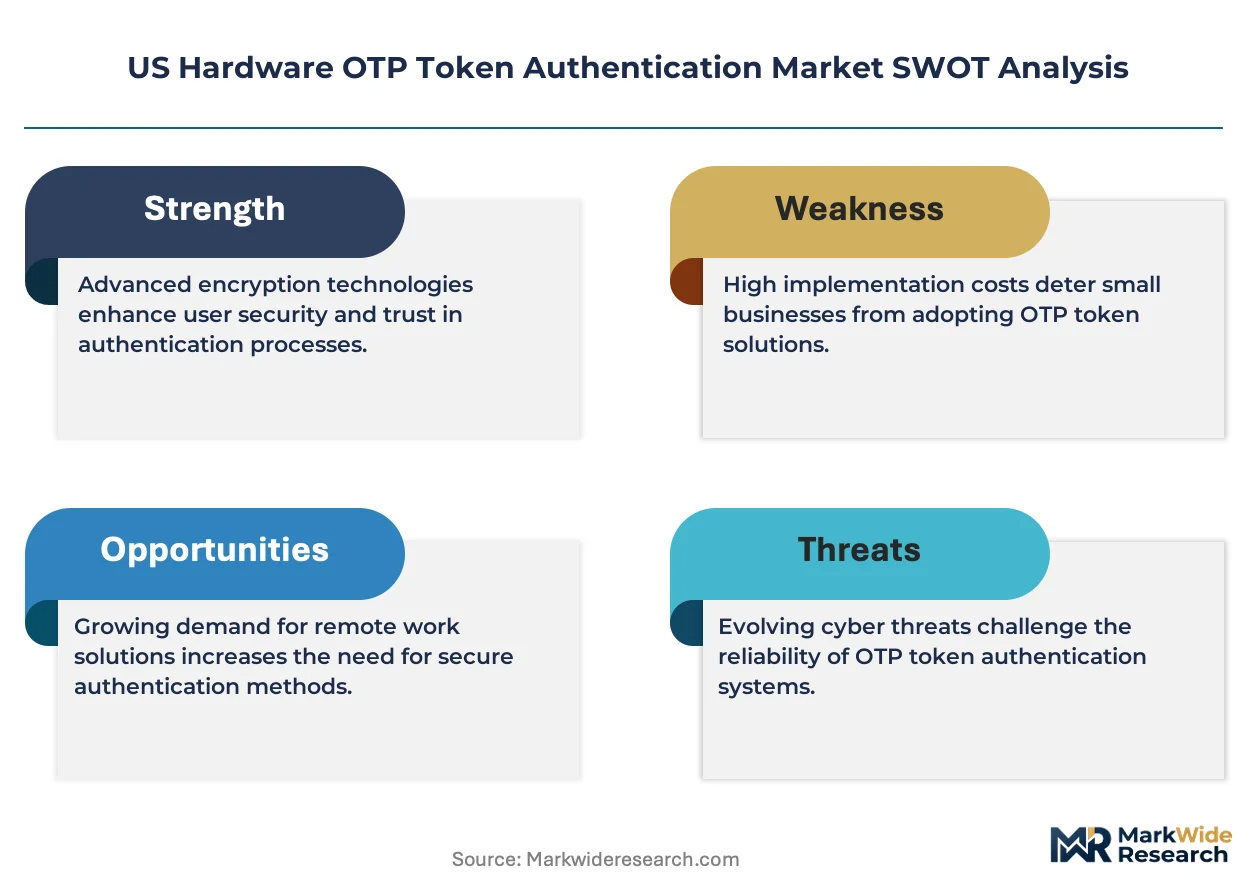
Federal post-quantum cryptography migration timelines are compressing hardware refresh cycles across defense and intelligence supply chains, forcing premature replacement of legacy RSA SecurID infrastructure before natural end-of-life.
Growth Catalysts
- CMMC 2.0 Mandates:The Department of Defense's Cybersecurity Maturity Model Certification now requires hardware-based multi-factor authentication for all contractors handling controlled unclassified information, expanding addressable market beyond classified programs.
- Zero Trust Architecture:Federal zero trust implementation directives from OMB M-22-09 designate hardware tokens as preferred possession factors for privileged access management in hybrid cloud environments.
- Mid-Atlantic Procurement Cluster:Concentrated defense and intelligence agency headquarters in Virginia, Maryland, and Washington DC generate volume purchasing power that subsidizes per-unit costs for adjacent commercial markets.
Market Restraints
- Secure Element Supply Concentration:FIPS 140-2 certified secure microcontrollers rely on three qualified foundries in Taiwan and South Korea, creating geographic single-source vulnerability.
- Smartphone Substitution:Software-based authenticator applications on iOS and Android devices displace hardware tokens in commercial segments below moderate assurance requirements.
- NIST Algorithm Uncertainty:Pending standardization of post-quantum cryptographic signatures under FIPS 204 and FIPS 205 delays enterprise commitment to multi-year token deployments.
Strategic Opportunities
- USB-C Form Factor Standardization:Enterprise workstation refresh cycles toward USB-C-only ports creates replacement demand for legacy USB-A and micro-USB token inventories.
- State-Level Privacy Regulations:California Consumer Privacy Act and analogous state laws in Virginia and Colorado elevate hardware tokens as demonstrable data protection investments for breach liability mitigation.
- Biometric-Hybrid Convergence:Integration of fingerprint sensors with OTP generation enables step-up authentication without separate biometric readers, addressing high-assurance remote workforce scenarios.
Industry Challenges
- FIPS 140-3 Transition Complexity:New validation requirements for physical security and side-channel resistance extend certification timelines from 12 to 18 months, delaying product launches.
- Legacy IAM Integration Friction:Token provisioning into heterogeneous identity management platforms requires custom middleware development for each major vendor stack.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | US Hardware OTP Token Authentication Market |
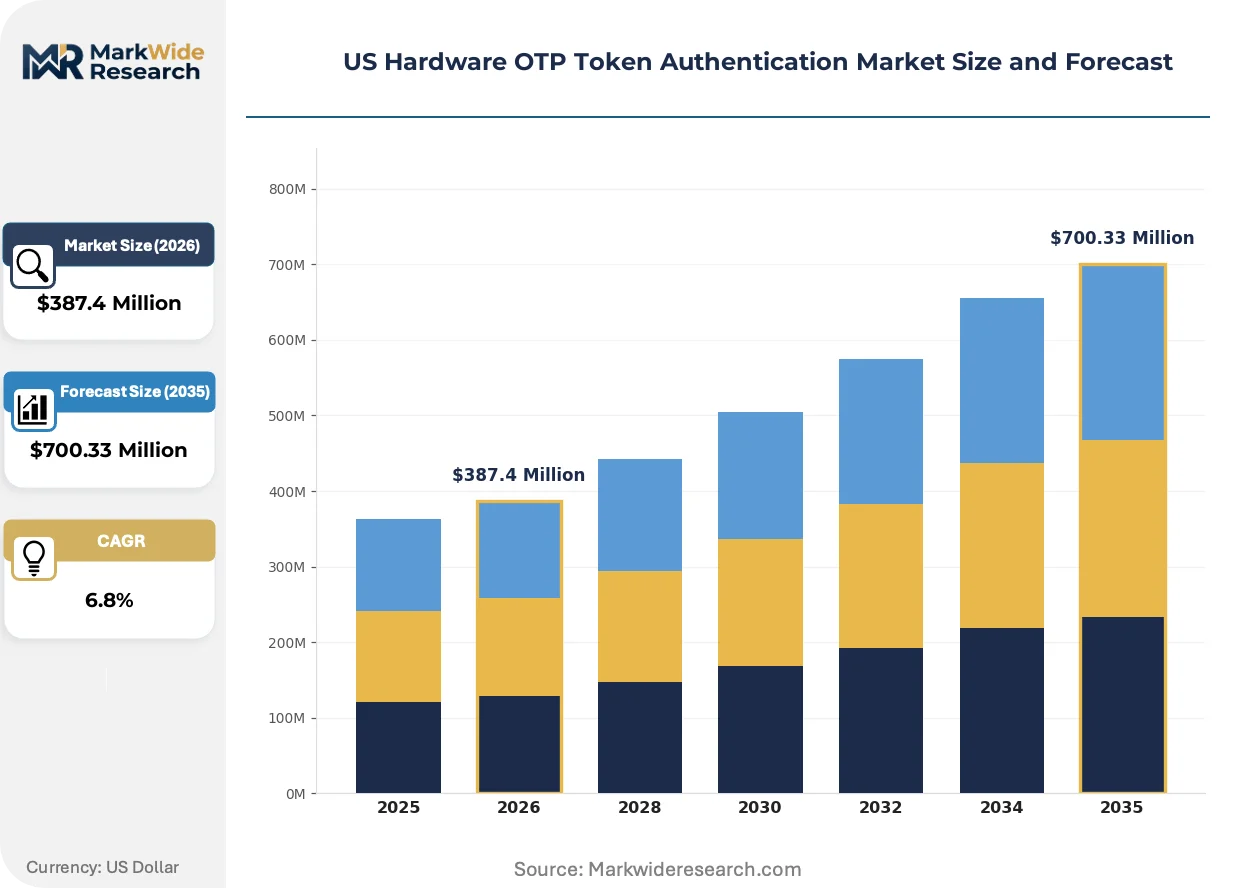
| Market Size in 2026 | $387.4 Million |
| Market Size in 2035 | $700.33 Million |
| CAGR (2026 – 2036) | 6.8% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Hardware Tokens, USB Tokens, SIM-Based Tokens, Smart Cards Distribution Channel: Retail, Direct Sales, E-Commerce, Resellers End User: Financial Institutions, Government Agencies, Corporates, Healthcare Providers Technology: Time-Synchronized, Event-Synchronized, Challenge-Response, Hybrid Systems |
| Companies Covered | VASCO Data Security International Inc, Thales Group, One Identity LLC, RSA Security LLC, Yubico Inc, HID Global Corporation, OneSpan Inc, Entrust Datacard Corporation, Symantec Corporation, Others |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
US Hardware OTP Token Authentication Market Evolving Landscape
Post-quantum cryptographic hardware migration is forcing simultaneous algorithm and form factor transitions that vendors must synchronize with federal procurement windows.
Hybrid time-synchronized and event-based token architectures are rewriting authentication reliability standards. Defense contractors operating in disconnected or high-latency environments adopt these dual-mode devices to maintain access continuity. Thales and Yubico product roadmaps now prioritize hybrid systems over pure time-synchronized designs, compressing the market window for single-mode alternatives.
NIST SP 800-63B updates are tightening authenticator assurance level definitions for hardware tokens. The revised guidelines eliminate certain certificate-based provisioning methods previously acceptable at AAL2, forcing vendors to redesign initial setup workflows. Federal systems integrators report 40% of pending token deployments under review for compliance with the stricter binding requirements.
Cloud-native enterprises are unbundling token lifecycle management from traditional managed security service providers. Direct procurement relationships with hardware token manufacturers are displacing channel-mediated purchasing for Fortune 500 accounts with internal identity teams. This pattern concentrates in technology and financial services verticals with mature zero trust implementations, particularly across Silicon Valley and New York metro operations.
US Hardware OTP Token Authentication Market Segmentation
Segmentation in the US Hardware OTP Token Authentication Market reveals how procurement authority, compliance thresholds, and infrastructure legacy shape purchasing patterns. Federal contractors, commercial banks, and healthcare systems operate under divergent authentication mandates that fragment demand across product tiers and distribution channels.
Product Type:
Budget allocation for physical possession factors varies sharply between classified program requirements and commercial risk tolerance thresholds.
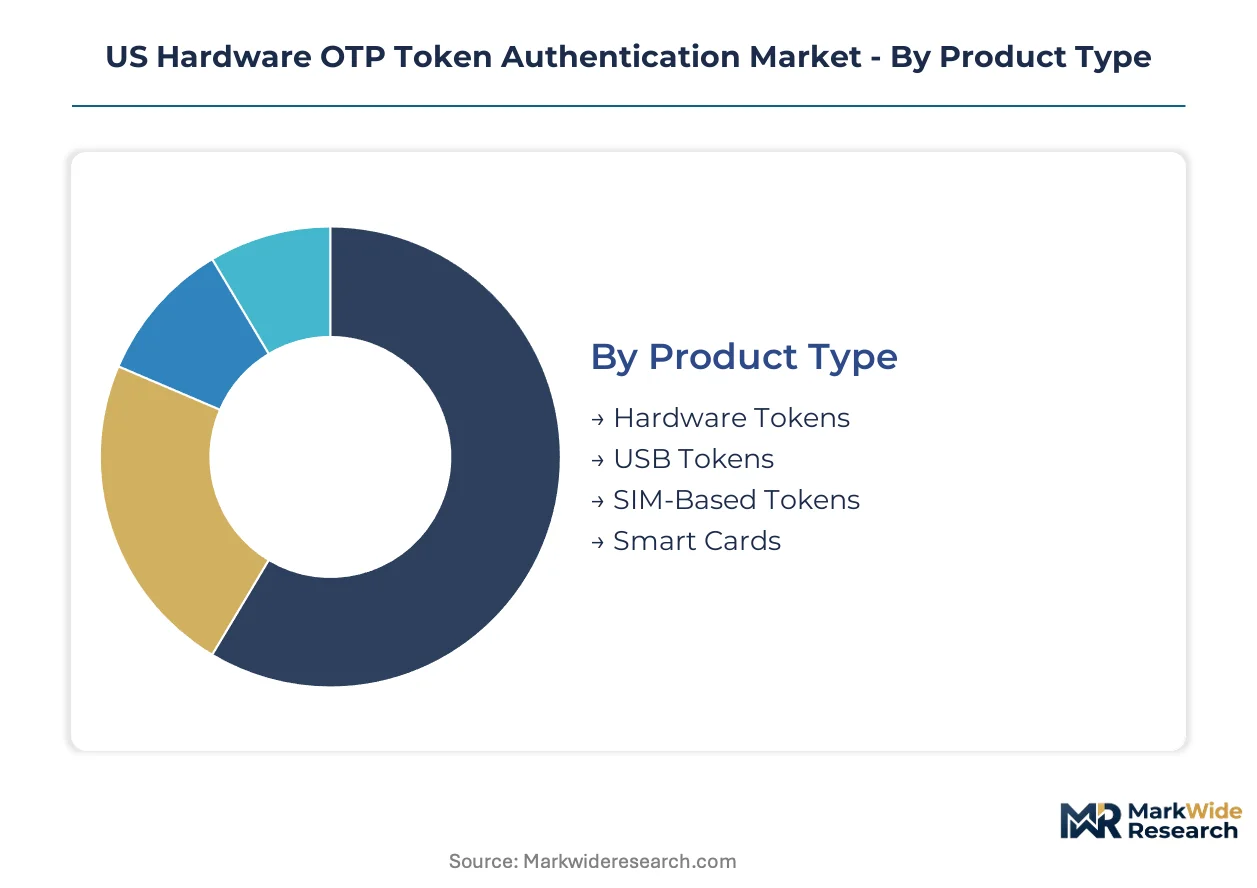
- Hardware Tokens:Dedicated OTP generators with tamper-resistant secure elements and dedicated displays dominate Department of Defense and intelligence agency deployments. Procurement concentrates in the Mid-Atlantic corridor where CMMC 2.0 compliance mandates drive volume purchasing for contractor supply chains.
- USB Tokens:Cryptographic modules integrating OTP generation with FIDO2/WebAuthn protocols capture expanding share as enterprise workstations standardize on USB-C-only configurations. Cloud-native enterprises in Silicon Valley and New York metro areas favor these devices for privileged access management in hybrid cloud environments.
- SIM-Based Tokens:Mobile network-integrated authentication credentials serve telecommunications carriers and mobile-first workforce deployments.
- Smart Cards:Contact and contactless chip cards with embedded OTP applications persist in legacy federal PIV infrastructure and European multinational subsidiaries operating in the US.
Volume sits with Hardware Tokens; growth tilts toward USB Tokens.
Distribution Channel:
Channel selection tracks customer scale and internal security operations maturity, with direct relationships displacing intermediaries at the enterprise tier.
- Direct Sales:Manufacturer-direct procurement relationships dominate Fortune 500 accounts with internal identity teams and zero trust implementations. Financial services and technology verticals in New York and California metro areas increasingly bypass managed security service providers for token lifecycle management.
- Resellers:Value-added distributors with FIPS 140-2 compliance expertise serve mid-market enterprises lacking dedicated identity infrastructure. Regional systems integrators in Virginia and Maryland corridor aggregate demand from defense contractor supply chains.
- E-Commerce:Self-service procurement portals capture small business and individual professional demand below moderate assurance requirements.
- Retail:Limited presence through commercial electronics channels for consumer-grade security applications.
Enterprise procurement is concentrating through Direct Sales; Resellers retain contractor market leverage.
End User:
Regulatory jurisdiction creates non-overlapping demand pools with distinct authentication assurance level requirements.
- Government Agencies:Federal civilian and defense departments operate under FISMA-mandated hardware factors for systems above moderate impact classification. NIST SP 800-63B compliance requirements drive refresh cycles across civilian agencies and military branches.
- Financial Institutions:Banks and payment processors deploy hardware tokens for high-value transaction authorization and SWIFT network access. FFIEC authentication guidance and state-level breach liability statutes elevate hardware possession factors in risk management frameworks.
- Corporates:Technology, manufacturing, and professional services firms adopt tokens for privileged access management and remote workforce security. Adoption concentrates in sectors with mature zero trust architectures and regulated data handling obligations.
- Healthcare Providers:HIPAA Security Rule compliance drives deployment for access to electronic health record systems and telemedicine platforms. Hospital systems and payer organizations prioritize phishing-resistant authentication for workforce access.
Government Agencies anchor procurement volume; Healthcare Providers show steepest expansion trajectory as ransomware mitigation priorities intensify.
Technology:
Algorithm architecture selection reflects operational environment constraints and post-quantum migration planning horizons.
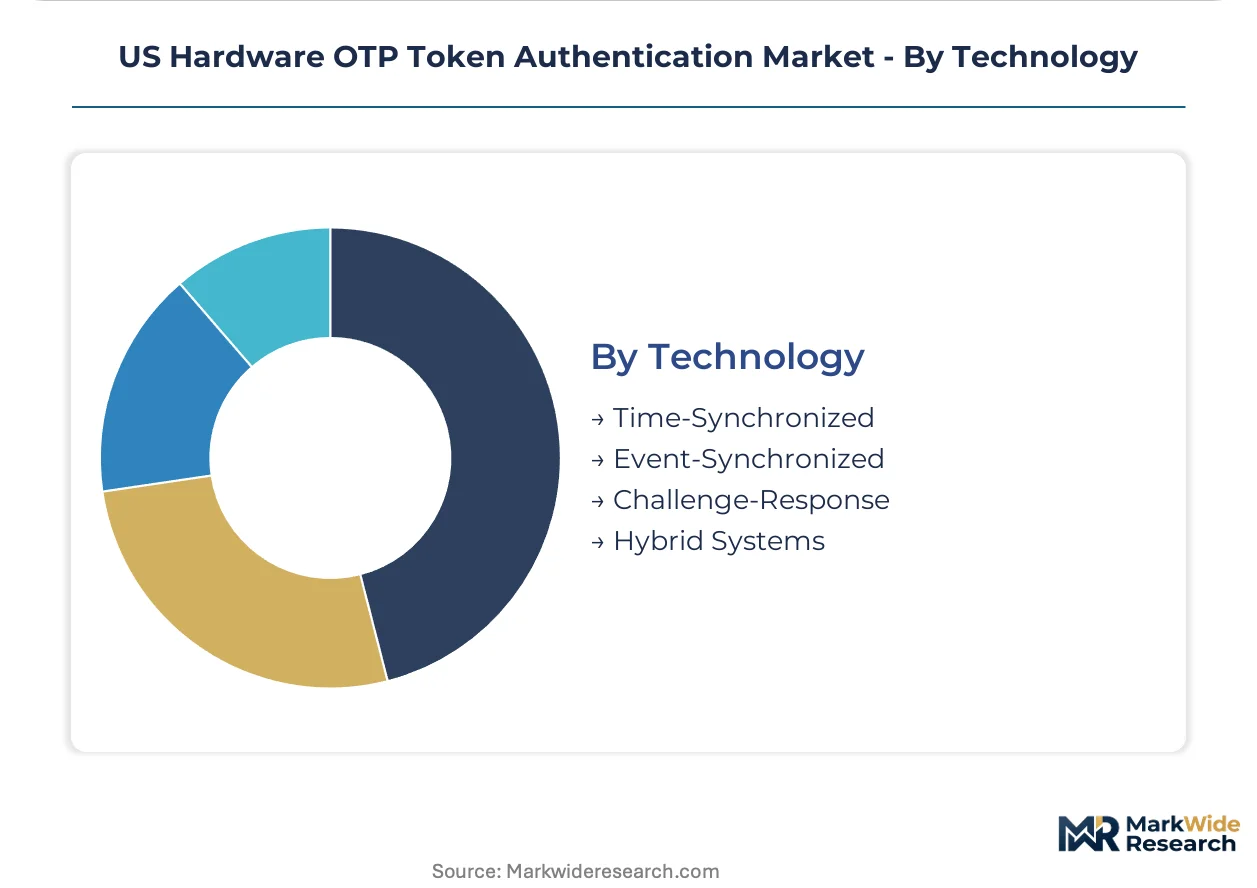
- Time-Synchronized:Clock-based OTP generation using TOTP protocols retains largest installed base through interoperability with legacy RSA SecurID infrastructure. Federal systems maintain extensive deployments despite pending post-quantum cryptographic refresh requirements.
- Hybrid Systems:Dual-mode architectures combining time-synchronized and event-based generation address disconnected or high-latency operational environments. Defense contractors operating in contested communications zones drive adoption as agencies mandate post-quantum migration paths.
- Event-Synchronized:Counter-based HOTP protocols serve air-gapped and offline authentication scenarios where clock synchronization is impractical.
- Challenge-Response:Mutual authentication protocols with server-presented challenges address high-assurance transaction signing requirements in financial and defense applications.
Time-Synchronized technology holds dominant share; Hybrid Systems gain share fastest as operational resilience requirements harden.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
The Mid-Atlantic Federal Contracting Zone concentrates procurement authority for hardware OTP tokens, with defense and intelligence agency headquarters generating concentrated demand that subsidizes adjacent commercial markets through volume purchasing power.
Virginia
Pentagon contracting offices and defense contractor supply chains drive hardware token procurement for CMMC 2.0 compliance across classified and controlled unclassified information systems. NIST SP 800-63B mandates shape authenticator assurance requirements for federal systems integration. Northern Virginia's technology corridor hosts Thales Group and RSA Security LLC distribution operations serving intelligence community clients.
Maryland
NSA and Cyber Command procurement clusters generate specialized demand for post-quantum cryptographic migration-ready hardware tokens. FISMA-mandated hardware factors for moderate-impact systems accelerate refresh cycles across civilian agency contractors. Fort Meade and Annapolis Junction defense technology corridors concentrate systems integrator activity for token deployment.
Washington DC
Federal civilian departments and regulatory agencies operate under OMB M-22-09 zero trust directives designating hardware tokens as preferred possession factors. The Department of Homeland Security and Treasury procurement offices anchor demand for high-assurance authentication in hybrid cloud environments. Downtown federal contracting corridors channel direct sales relationships with major token manufacturers.
California
Silicon Valley cloud-native enterprises bypass managed security service providers for direct manufacturer procurement of USB-C hardware tokens. State-level privacy regulations elevate hardware possession factors as demonstrable data protection investments for breach liability mitigation. San Francisco Bay Area technology and financial services verticals drive FIDO2/WebAuthn protocol adoption for privileged access management.
New York
Financial institutions deploy hardware tokens for SWIFT network access and high-value transaction authorization under FFIEC authentication guidance. State breach liability statutes and ransomware mitigation priorities intensify hardware-based multi-factor authentication procurement. Manhattan financial services corridors concentrate Fortune 500 identity team direct purchasing relationships with token manufacturers.
US Hardware OTP Token Authentication Market Competitive Landscape
Top-tier vendors anchor federal supply chains through FIPS 140-2 certification dominance, while mid-tier specialists compete on commercial segment agility and cloud-native integration speed. The vendor landscape stratifies across defense-contractor-focused incumbents, commercial-optimized challengers, and legacy identity management platform integrators. Three strategic archetypes define competitive positioning: certification-heavy federal suppliers, USB-C form factor innovators, and legacy IAM-integrated platform players. Dominant competitive moves include strategic partnerships with systems integrators and portfolio diversification into hybrid time-synchronized and event-based architectures.
Within the federal supply chain tier, Thales Group and RSA Security LLC exemplify certification-driven market presence through FIPS 140-2 validated manufacturing and deep legacy infrastructure integration. Yubico Inc occupies a distinct position among commercial-optimized vendors, representing the USB-C form factor and FIDO2 protocol convergence that cloud-native enterprises prioritize for zero trust implementations.
| Leading Market Players |
|---|
| VASCO Data Security International Inc |
| Thales Group |
| One Identity LLC |
| RSA Security LLC |
| Yubico Inc |
| HID Global Corporation |
| OneSpan Inc |
| Entrust Datacard Corporation |
| Symantec Corporation |
| Others |
Value Network & Pricing Analysis
FIPS 140-3 validation mandates gate both qualified manufacturing capacity and premium-tier pricing access, compressing supplier margins while elevating certified product premiums. Procurement officers face extended certification timelines that stratify pricing across validation-ready and legacy-tier inventory.
Pricing Analysis
Short lead-time premiums of 15-25% apply to FIPS 140-3 validated inventory, while spot-market legacy tokens trade at discounted clearance levels. Three-tier pricing structure across certified-premium, standard-FIPS-140-2, and economy-uncertified levels tracks validation status and secure element origin. Pricing pressure stems from smartphone authenticator displacement in commercial segments below moderate assurance. Mid-market enterprises exhibit highest price sensitivity; federal contractors demonstrate lowest sensitivity due to compliance-mandated procurement.
Supply Chain Analysis
Domestic-content mandates under the CHIPS Act and Buy American provisions are reshaping sourcing toward qualified US assembly operations, though secure microcontroller fabrication remains concentrated in Taiwan and South Korea. FIPS-certified secure elements draw from TSMC and Samsung foundries, with substrate packaging anchored in Malaysia and Vietnam. Single-source vulnerability concentrates in Taiwanese wafer capacity. Distribution runs through defense-authorized systems integrators in the Mid-Atlantic corridor and direct manufacturer relationships with Fortune 500 identity teams.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The US Hardware OTP Token Authentication Market sits in a technology-transition phase as post-quantum cryptographic hardware displaces legacy RSA SecurID infrastructure before natural end-of-life. Federal migration timelines compress refresh cycles and reshape competitive positioning.
For Market Incumbents: Deploy certification acceleration as the primary lever. Prioritize FIPS 140-3 validation pipeline investments to defend federal supply chain position against emerging entrants with cleaner architectural starting points. Establish captive secure element inventory through backward integration into qualified foundry offtake agreements, mitigating Taiwan concentration risk. Channel control through exclusive systems integrator partnerships in Virginia and Maryland corridors locks out challenger access to defense procurement clusters. For New Entrants and Emerging Players: Capture healthcare provider ransomware mitigation budgets as the most penetrable white-space target. Hospital systems and payer organizations lack mature zero trust architectures, creating greenfield deployment opportunities with lower incumbent entrenchment than federal or financial verticals. Target direct sales relationships with Silicon Valley cloud-native enterprises seeking USB-C FIDO2 convergence, bypassing legacy channel structures. Position against smartphone substitution risk by emphasizing phishing-resistant possession factors for remote clinical workforce access. For Investors and Strategic Acquirers: NIST post-quantum cryptographic standardization finalization is the leading indicator that hardware refresh cycle acceleration will concentrate procurement authority among vendors with migration-ready product portfolios. Five-to-ten-year viability hinges on algorithm agility and federal certification maintenance capabilities. Acquisition target archetype: mid-tier vendors with FIPS 140-2 manufacturing infrastructure and pending 140-3 submissions, trading at discount to certification completion. Monitor CMMC 2.0 contractor enrollment velocity as demand inflection signal.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Cryptographic Hardware Certification | FIPS 140-3 validation with CRYSTALS-Kyber support secures federal procurement eligibility under NIST migration timelines. |
| Hybrid Time-Event Architecture Development | Dual-mode tokens address contested communications environments for Cyber Command and defense contractor deployments. |
| USB-C Form Factor Standardization | Enterprise workstation refresh cycles create replacement demand displacing legacy USB-A token inventories. |
| Direct Manufacturer-Enterprise Relationships | Cloud-native identity teams in New York and California metros bypass managed security service provider intermediaries. |
| Biometric-Hybrid Token Integration | Fingerprint-sensor convergence enables step-up authentication without separate reader infrastructure for remote workforce. |
Research Methodology
Document review covered NIST SP 800-63 guidelines, FISMA implementation directives, CMMC 2.0 framework documentation, and federal procurement databases, complemented by interviews with identity and access management directors at defense contractors, federal systems integrators in the Mid-Atlantic corridor, healthcare CISOs, and financial services authentication leads. Secondary validation drew from SEC filings of publicly traded security vendors, GSA schedule contract awards, and DHS supply chain risk assessments. Bottom-up demand modeling triangulated against top-down federal IT spending allocations.
Market size and growth trajectory outputs reflect segment-level modeling across product type, distribution channel, end-user vertical, and technology architecture dimensions, with cross-validation against federal procurement volume trends. CAGRs were derived from regression analysis of historical defense and intelligence agency authentication spending patterns, adjusted for post-quantum migration acceleration assumptions. Key forecast inputs included CMMC 2.0 contractor enrollment projections and NIST algorithm standardization status.
Forecast confidence holds firmest in the near-window; longer-horizon outcomes carry greater sensitivity to NIST post-quantum cryptographic timeline delays, Taiwan semiconductor supply disruptions, and smartphone authenticator technology advancement. Within these boundaries, the analytical envelope holds.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Global Data Protection As a Service (Dpaas) Market
Security Software
Software Protection Dongle Market
Security Software
Public Key Infrastructure (PKI) Market
Security Software
Mobile Security Market
Security Software
Global Mobile Security Software Market
Security Software
Fraud Detection Software Market
Security Software
Anti-Money Laundering (AML) Software Solution Market
Security Software
Global Log Management Market
Security Software
AD-Blocking Software Market
Security Software
Global User Provisioning Market
Security Software
Video Intercom Devices Market
Security Software
Endpoint Detection and Response [EDR] Market
Security Software
Patch and Remediation Software Market
Security Software
Encryption Software Market
Security Software
Door Phone Market
Security Software
Stalkerware Market