
 Managed SIEM Service Market | 2026-2036
Managed SIEM Service Market Size, Share, and Industry Trends Forecast 2026-2036
Managed SIEM Service Market Insights
GDPR enforcement is realigning the cost-of-entry calculus for European enterprises seeking 24/7 security monitoring without building internal SOCs. IBM leverages its Watson-powered analytics platform to sustain differentiation in threat detection accuracy across hybrid environments. ReliaQuest anchors its competitive position through Open XDR architecture that unifies telemetry across cloud and on-premises estates. Cyderes competes by extending Google Cloud-native SIEM capabilities to mid-market enterprises lacking specialized security engineering teams.
Managed SIEM services deliver continuous security information and event management through cloud-based, on-premises, or hybrid deployment models, ingesting log data at terabyte scale to correlate threats across distributed IT environments. These services functionally replace or augment internal security operations centers by applying machine-driven correlation rules and human analyst oversight to identify anomalous behavior indicating breach activity. Cloud-based deployment dominates current uptake as organizations exit data center ownership, while hybrid configurations retain stronghold status in financial services and healthcare where regulated data residency requirements fragment workload placement. Managed security service type captures expanding margin pools as clients shift from software licensing toward outcome-based operational expenditure models.
FDA oversight of connected medical devices, HIPAA security rule enforcement by the Office for Civil Rights, and PCI DSS mandate adherence by the Payment Card Industry Security Standards Council collectively elevate baseline logging and monitoring requirements across healthcare and financial verticals. ISO 27001 certification has become a de facto procurement filter for enterprise buyers evaluating vendor risk profiles. Stakeholders must weigh cloud-native platform bets against hybrid flexibility as regulatory fragmentation across federal and state jurisdictions complicates single-architecture standardization.
Market Dynamics
Cloud-native security operations are compressing the traditional managed security services model as enterprises abandon data center ownership for elastic consumption models. The shift from capital-intensive SIEM infrastructure toward operational expenditure frameworks is redrawing competitive boundaries between pure-play MSSPs and hyperscale platform providers.
Growth Catalysts
- GDPR Article 33 breach notification mandates:European enterprises face 72-hour disclosure windows that internal security teams cannot meet without continuous monitoring partnerships.
- PCI DSS 4.0 logging requirements:Payment processors must demonstrate 12 months of accessible log history, driving mid-market retailers toward outsourced retention architectures.
- Healthcare IoT device proliferation:FDA-cleared connected medical instruments generate telemetry volumes that overwhelm hospital IT departments, necessitating external SIEM capacity.
Market Restraints
- Skilled analyst scarcity:The global shortage of SOC engineers with cloud-native platform expertise limits service provider scaling velocity and inflates labor costs.
- Data residency fragmentation:Divergent national data localization laws in Germany, France, and Switzerland prevent standardized cross-border security operations architectures.
- API rate limiting:Cloud platform ingestion throttles constrain real-time correlation performance for high-velocity telemetry sources including OT networks.
Strategic Opportunities
- Operational technology convergence:Manufacturing facilities combining IT and OT security monitoring under unified SIEM contracts represent an underpenetrated expansion vector.
- AI-augmented threat hunting:Machine learning correlation layered atop traditional rule-based detection creates differentiation in managed detection and response bundles.
- India's data protection bill implementation:Domestic data localization requirements will force multinational enterprises to establish in-country security operations partnerships.
Industry Challenges
- Multi-cloud telemetry normalization:Security teams struggle to correlate events across disparate cloud provider logging formats without custom parser development.
- Mean-time-to-containment targets:Contractual SLAs demanding sub-one-hour breach response strain analyst availability during off-peak hours across time zones.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Managed SIEM Service Market |
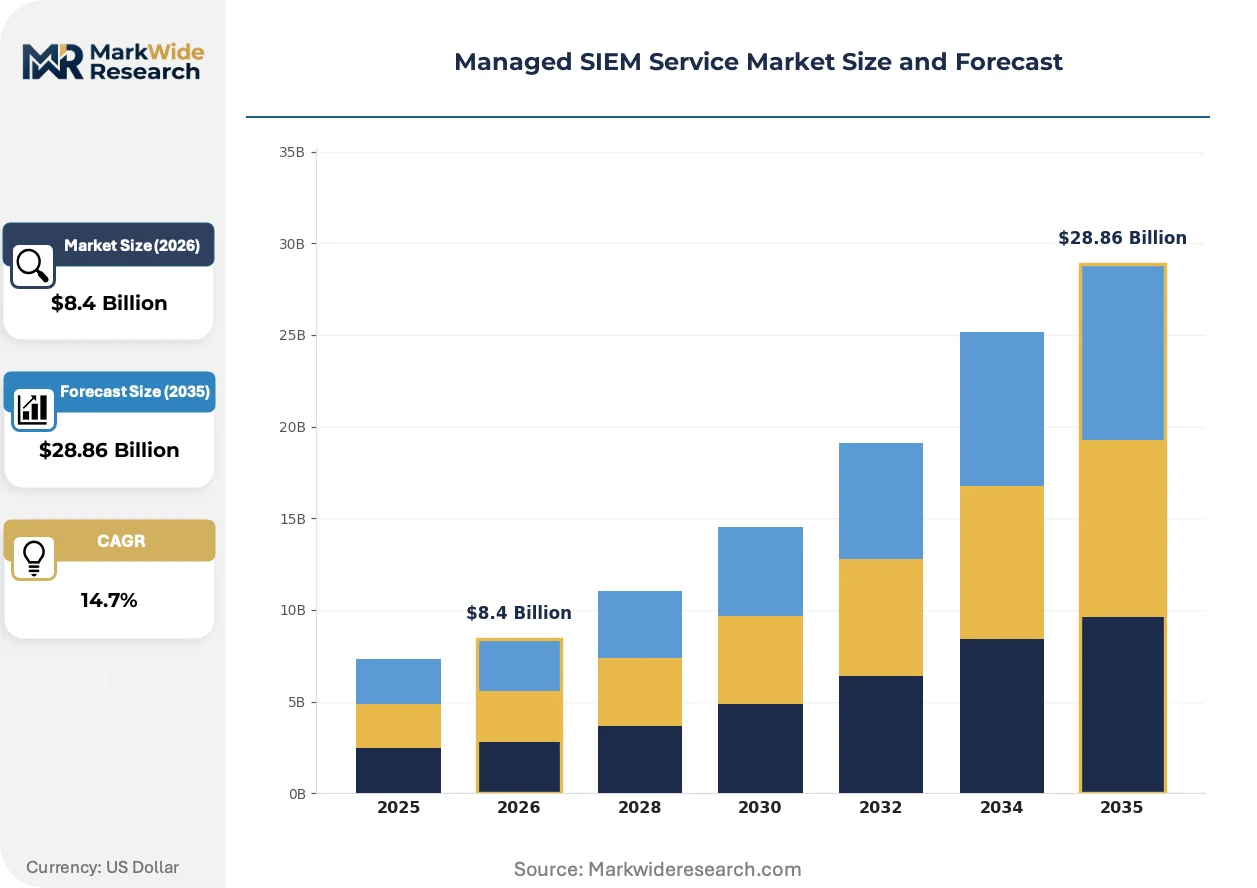
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $28.86 Billion |
| CAGR (2026 – 2036) | 14.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Service Type: Cloud-Based, On-Premises, Hybrid, Managed Security End User: Healthcare, Financial Services, Retail, Government Deployment Model: Public Cloud, Private Cloud, Community Cloud, Multi-Tenant Compliance Standard: GDPR, HIPAA, PCI DSS, ISO 27001 |
| Companies Covered | AT&T, Unisys, Verizon, NTT, GoSecure, IBM, ReliaQuest, Cyderes, Redscan, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Managed SIEM Service Market Trends and Innovations
Open XDR architectures are dissolving the traditional SIEM-SOAR boundary as vendors unify detection, investigation, and response workflows under single-pane management. This architectural consolidation is compressing procurement cycles and elevating platform breadth over point-solution depth in enterprise evaluations.
Extended detection and response platforms are modularizing security operations by decoupling data ingestion, analytics processing, and response automation into interchangeable components. Large financial institutions in London and Singapore are adopting this architecture to avoid vendor lock-in while maintaining hybrid cloud flexibility. The approach is modularizing competitive differentiation away from proprietary correlation engines toward integration depth and third-party ecosystem breadth.
EU AI Act risk classification requirements are mandating algorithmic transparency for automated security decision systems deployed in critical infrastructure sectors. Managed service providers must now document machine learning model training data and decision boundaries for client audit trails. German energy utilities and French transportation operators are demanding these disclosures as procurement prerequisites, forcing architectural investments in explainable AI pipelines.
Consumption-based pricing models are displacing seat-license arrangements as CISOs demand cost alignment with actual log volume and analyst touch frequency. Mid-market enterprises in the United States are negotiating contracts tied to events-per-second rather than fixed monthly fees, transferring operational risk to service providers. This shift is most pronounced among SaaS-native companies lacking historical capital investments in on-premises security infrastructure.
Managed SIEM Service Market Segmentation
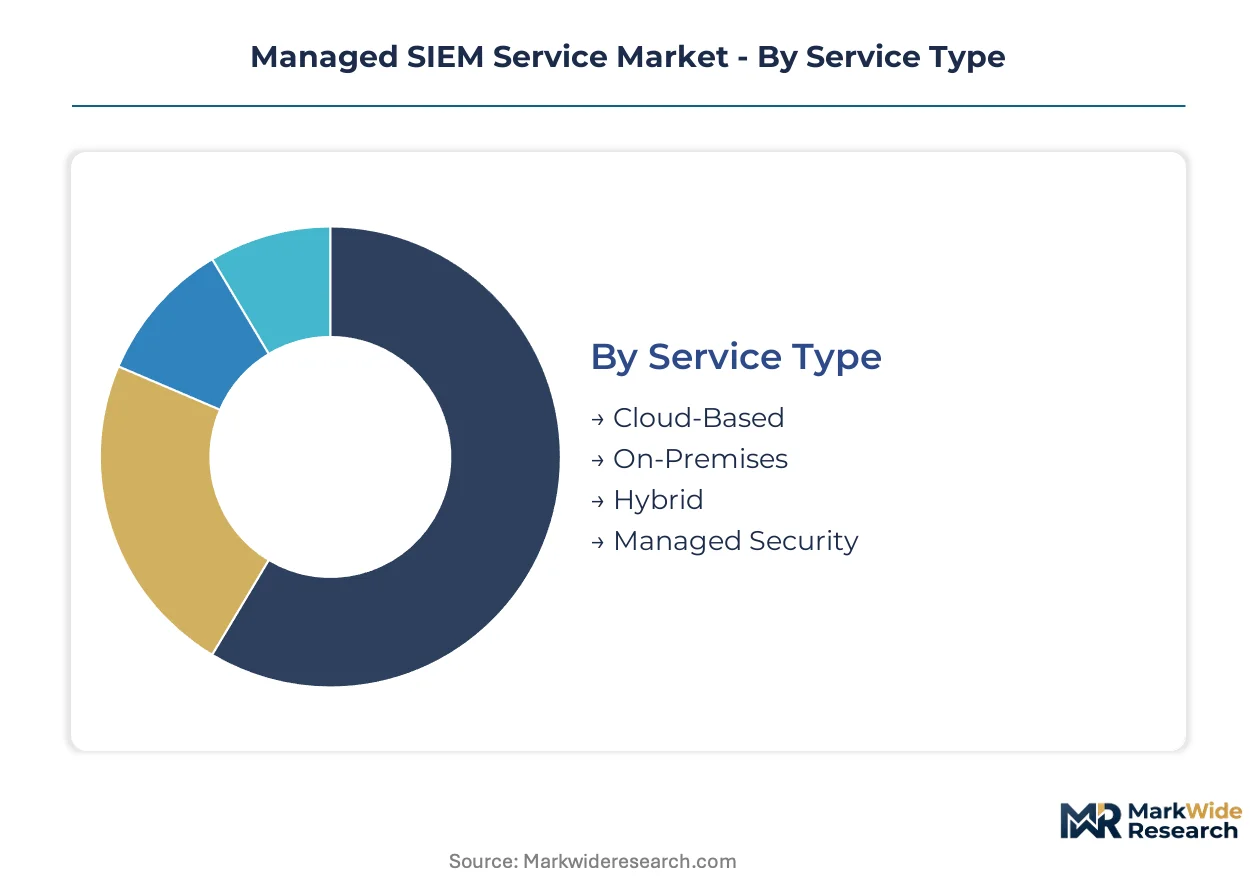
Segmentation in managed SIEM services reveals how compliance mandates, infrastructure legacies, and risk appetites fragment procurement patterns across buyer categories. Understanding these fault lines enables vendors to calibrate platform investments and pricing architectures against addressable demand pools.
Service Type:
Certification burdens vary sharply across deployment modalities, with HIPAA and PCI DSS imposing distinct logging retention rules on cloud versus on-premises configurations. GDPR Article 33 drives European buyers toward externally managed options that guarantee 72-hour breach notification compliance.
- Cloud-Based:Elastic compute architectures ingest terabyte-scale telemetry without capital expenditure, with SaaS-native enterprises in the United States migrating aggressively from owned data centers. Demand concentrates among mid-market retailers and healthcare clinics lacking internal security engineering capacity.
- On-Premises:Dedicated hardware deployments satisfy data residency requirements in German financial institutions and Swiss pharmaceutical manufacturers where national regulators restrict cross-border data flows. Capital-intensive procurement limits adoption to large enterprises with existing data center investments.
- Hybrid:Split architectures segment regulated workloads on-premises while pushing non-sensitive analytics to public cloud, serving multinational banks navigating fragmented supervisory requirements across jurisdictions.
- Managed Security:Outcome-based contracts transfer operational risk to service providers, with payment processors and hospital networks purchasing 24/7 analyst coverage rather than software licenses.
Cloud-based deployments sit at the top of the volume ranking, with managed security climbing the fastest as buyers shift from capital to operational expenditure frameworks.
End User:
Vertical-specific regulatory enforcement creates divergent logging complexity and analyst touch frequency across buyer segments. FDA oversight of connected devices and PCI DSS 4.0 mandates reshape procurement specifications in healthcare and retail respectively.
- Healthcare:HIPAA Security Rule enforcement by the Office for Civil Rights mandates audit trails for electronic protected health information access, with connected medical device telemetry overwhelming hospital IT departments.
- Financial Services:PCI DSS 4.0 requires 12 months of accessible log history for payment processors, while GDPR Article 33 imposes 72-hour breach disclosure windows that internal SOCs cannot meet without external partnerships. London and Singapore banking clusters drive premium demand for hybrid deployment flexibility.
- Retail:Mid-market payment processors outsource retention architectures to avoid capital investment in compliance infrastructure, with seasonal transaction spikes favoring elastic consumption models.
- Government:Federal and state agencies in the United States maintain classified workloads on air-gapped systems, requiring cleared personnel and specialized facility certifications that limit vendor participation.
Financial services commands the largest revenue pool, with healthcare expanding most rapidly under FDA device oversight and IoT telemetry proliferation.
Deployment Model:
Infrastructure choices reflect risk tolerance for multi-tenancy, with regulated sectors paying premiums for isolation while cost-sensitive buyers accept shared resources. Data localization laws in Germany, France, and Switzerland fragment standardized architecture deployment.
- Public Cloud:Shared infrastructure delivers lowest unit economics, with SaaS companies and mid-market retailers accepting commingled environments for non-sensitive workloads.
- Private Cloud:Single-tenant isolation satisfies German banking regulators and French energy utilities demanding dedicated compute under EU AI Act risk classification requirements.
- Community Cloud:Sector-specific instances serve healthcare consortiums and defense industrial bases requiring mutualized compliance investments without full public exposure.
- Multi-Tenant:Logical separation architectures balance cost and isolation for managed service providers serving heterogeneous client portfolios across compliance regimes.
Public cloud captures the widest deployment base, with private cloud gaining share fastest among critical infrastructure operators facing algorithmic transparency mandates.
Compliance Standard:
Regulatory scope determines correlation rule complexity, retention architecture, and audit documentation burden. ISO 27001 functions as a procurement filter while sector-specific mandates create non-negotiable technical requirements.
- GDPR:European breach notification windows and data subject access request logging drive continuous monitoring partnerships, with Article 33 enforcement realigning cost-of-entry calculus for 24/7 coverage.
- HIPAA:Access logging for electronic protected health information and business associate agreement obligations shape healthcare procurement specifications, with OCR audit activity elevating baseline requirements.
- PCI DSS:Payment card data environment segmentation and log integrity verification dominate retail and financial services implementations, with version 4.0 expanding compensating control documentation.
- ISO 27001:Certification serves as de facto vendor risk assessment prerequisite across enterprise buyers, with surveillance audit requirements embedding ongoing compliance into contract structures.
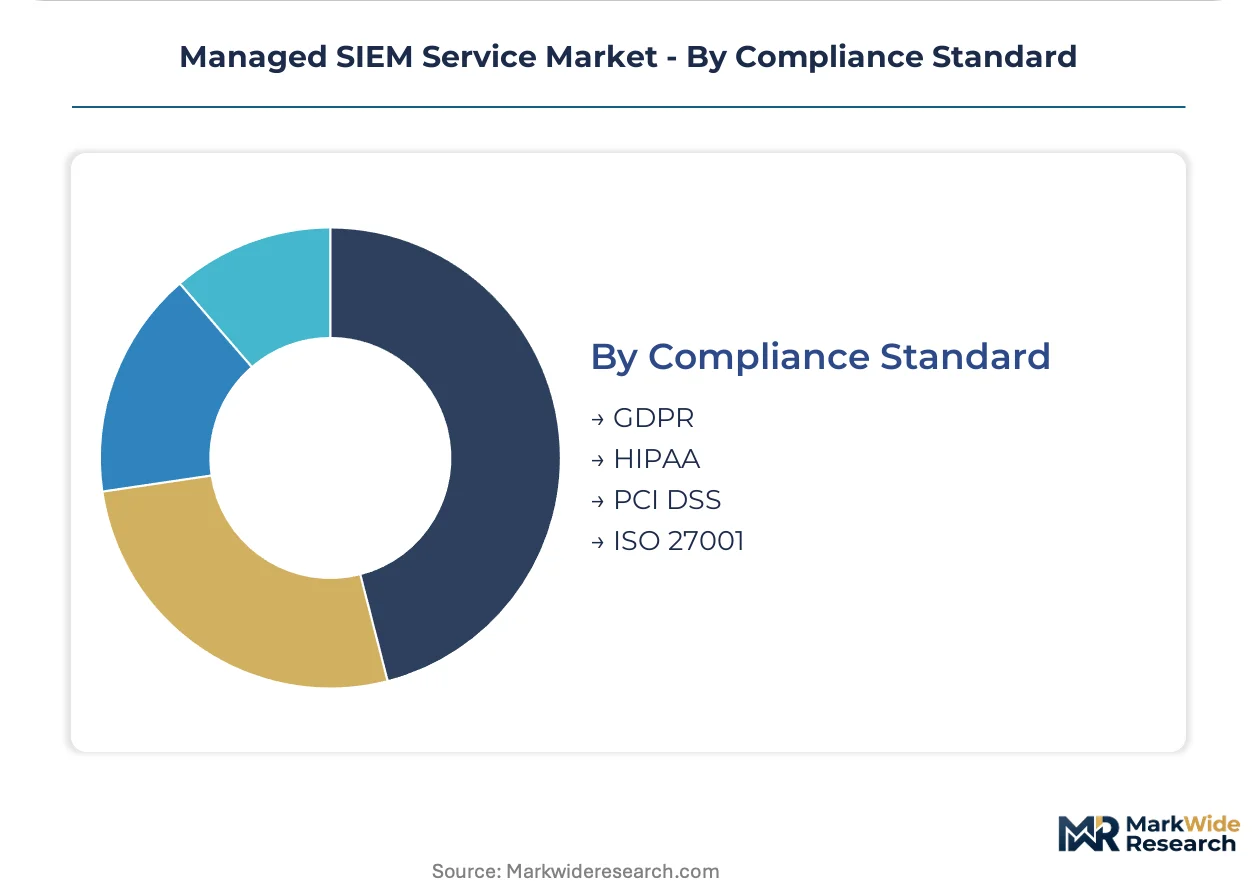
PCI DSS underpins the broadest addressable demand, with GDPR driving the steepest expansion trajectory as enforcement tightens across European member states.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Managed SIEM services trace their commercial scaling to United States technology corridors where early cloud infrastructure investments created the operational template for outsourced security operations. The industry's geographic footprint now reflects regulatory enforcement patterns across major economies.
United States
HIPAA enforcement by the Office for Civil Rights and PCI DSS mandates from the Payment Card Industry Security Standards Council drive healthcare systems and payment processors toward continuous monitoring partnerships. The SEC's cybersecurity disclosure rules for public companies elevate baseline logging requirements. Financial services clusters in New York and Chicago purchase hybrid deployment flexibility to navigate fragmented state-level data privacy laws.
Germany
German banking regulators restrict cross-border data flows, compelling financial institutions in Frankfurt and Munich to maintain on-premises or private cloud SIEM architectures. The EU AI Act's risk classification requirements mandate algorithmic transparency for automated security systems in critical infrastructure. Energy utilities in the Ruhr region demand explainable AI documentation as procurement prerequisites.
United Kingdom
London's banking concentration generates premium demand for 24/7 analyst coverage meeting GDPR Article 33's 72-hour breach notification windows. The Financial Conduct Authority's operational resilience requirements push payment processors toward outsourced retention architectures. Fintech clusters in Manchester and Edinburgh adopt consumption-based pricing models tied to events-per-second rather than fixed fees.
India
The country's data protection bill implementation forces multinational enterprises to establish in-country security operations partnerships for domestic data localization compliance. RBI guidelines for financial institutions mandate comprehensive audit trails for digital payment systems. Technology corridors in Bangalore and Hyderabad attract managed security service providers building delivery centers for Asia-Pacific clients.
Japan
METI's cybersecurity framework for critical infrastructure elevates logging and monitoring requirements across energy and transportation sectors. Pharmaceutical manufacturers in Osaka and Tokyo navigate FDA-equivalent domestic regulations for connected medical devices generating telemetry volumes beyond internal IT capacity. Financial institutions in Tokyo's Marunouchi district purchase hybrid SIEM configurations balancing cloud elasticity with data residency controls.
Managed SIEM Service Market Competitive Landscape
The competitive structure tilts toward platform-integrated specialists with cloud-native delivery capabilities. Pure-play managed security service providers compete against telecommunications carriers and hyperscale technology platforms offering bundled security operations. Three archetypes dominate: telecommunications-anchored providers leveraging network infrastructure, independent specialists emphasizing Open XDR architecture, and cloud-platform-native vendors extending infrastructure services. Consolidation through strategic partnerships and geographic expansion represent the primary competitive vectors as vendors seek compliance expertise across fragmented regulatory jurisdictions.
Among telecommunications-based providers, AT&T, Verizon, and NTT occupy positions anchored by network infrastructure ownership that enables integrated threat detection across client connectivity layers. These carriers exemplify the infrastructure-integrated archetype, using existing enterprise relationships to cross-sell security operations without requiring separate procurement cycles. IBM and Unisys represent established technology platforms that have extended into managed services, sitting within the hybrid cloud flexibility tier where decades of enterprise relationships translate into complex environment expertise. ReliaQuest and Cyderes exemplify the independent specialist model, with ReliaQuest's Open XDR positioning and Cyderes's Google Cloud-native architecture representing divergent platform bets for mid-market penetration.
| Leading Market Players |
|---|
| AT&T |
| Unisys |
| Verizon |
| NTT |
| GoSecure |
| IBM |
| ReliaQuest |
| Cyderes |
| Redscan |
| Others |
Pricing and Supply Chain Analysis
Analyst labor costs cascade through managed SIEM pricing tiers as cloud-native platform expertise concentrates in Bangalore, Hyderabad, and Warsaw delivery centers. European data localization mandates force redundant infrastructure investments that inflate premium-tier quotations for Frankfurt and Zurich financial institutions.
Pricing Analysis
Consumption-based contracts tied to events-per-second dominate mid-market procurement, displacing fixed monthly fees as SaaS-native enterprises demand cost alignment with actual telemetry volumes. Price differentiation hinges on ISO 27001 certification tier and analyst touch frequency, with uncertified providers competing on unit economics while accredited vendors capture HIPAA and PCI DSS-mandated premiums. Cost compression in standard-tier offerings intensifies as hyperscale platforms bundle security operations with infrastructure services. Retail payment processors exhibit highest price sensitivity, while London banking clusters prioritize response-time SLAs over per-unit costs.
Supply Chain Analysis
Cloud-native SIEM platforms rest on infrastructure-as-a-service provisioning from United States, Ireland, and Singapore hyperscale regions, with telemetry ingestion capacity tethered to AWS, Azure, and Google Cloud availability zone expansion. Specialized security engineering talent draws from Indian technology corridors and Polish delivery centers, while correlation rule development feeds from Israeli and United States threat intelligence vendors. Single-source vulnerability concentrates in Google Cloud-native architectures where mid-market providers lack portability options. Distribution runs through direct enterprise sales teams and telecommunications carrier relationships for bundled network-security offerings.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Margin expansion in managed SIEM services stems from automation-driven analyst productivity gains and premium-tier pricing for EU AI Act-compliant explainable AI pipelines.
For Market Incumbents: Anchor competitive position through Open XDR architecture investments that unify telemetry across hybrid estates, countering hyperscale platform bundling threats. Pursue backward integration into proprietary threat intelligence feeds to reduce dependency on Israeli and United States security vendors. Expand cleared personnel capacity for United States federal and defense industrial base contracts where facility certifications limit competitor participation. For New Entrants and Emerging Players: Cloud-native SIEM marketplaces and hyperscaler partner programs offer lowest-friction customer acquisition routes for mid-market penetration. Target healthcare clinics in United States secondary cities where HIPAA Security Rule enforcement has overwhelmed internal IT departments but enterprise-grade solutions remain unaffordable. Differentiate through FDA-connected medical device telemetry specialization rather than generic log management. For Investors and Strategic Acquirers: Consolidation pressure builds where compliance expertise fragments across GDPR, HIPAA, and PCI DSS jurisdictions, favoring platforms with multi-certification audit automation. Long-term viability centers on AI-augmented threat hunting capabilities that reduce per-customer analyst headcount. Watch India's data protection bill enforcement timeline as the signal indicating forced in-country security operations partnership demand.| Strategic Initiative | Industry Significance |
|---|---|
| Open XDR Architecture Deployment | Unifies detection workflows across cloud and on-premises estates for hybrid flexibility. |
| EU AI Act Compliance Investment | Mandates explainable AI documentation for German energy and French transportation procurement. |
| India Delivery Center Expansion | Positions providers for domestic data localization requirements under pending data protection legislation. |
| OT Security Convergence Offering | Captures manufacturing facility demand for unified IT and operational technology monitoring. |
| Consumption-Based Pricing Rollout | Aligns revenue with events-per-second for SaaS-native enterprises avoiding capital expenditure. |
Research Methodology
Quantitative tracking and qualitative interviews ran in parallel throughout the study window, combining primary discussions with CISOs, SOC directors, managed security service procurement officers, and cloud platform engineers with secondary validation against SEC filings, hyperscaler capex disclosures, and healthcare GPO contract databases. Bottom-up telemetry volume estimates triangulated against top-down security operations spending surveys.
Segment-weighting approaches modeled deployment modality, compliance standard, and end-user vertical dimensions across the projection horizon. CAGRs derived from elasticity-adjusted adoption curves incorporating GDPR enforcement intensity, PCI DSS version migration timelines, and cloud infrastructure migration rates. Forecast inputs included analyst labor cost indices and data center construction permitting velocity in Frankfurt, Singapore, and Mumbai corridors.
The model assumes a particular technology adoption path; alternative pathways for on-premises SIEM retention would alter the outlook if German banking regulators tighten cross-border data flow restrictions beyond current baselines. Forecasts reflect documented assumptions about breach notification enforcement consistency and hyperscale platform pricing stability. A small set of triggers—EU AI Act implementation rigor, India's data protection bill passage, and OT network telemetry standardization—warrants ongoing watch.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Cybersecurity
Artificial Intelligence in Cybersecurity Market
Cybersecurity
Cloud-Based Email Security Market
Cybersecurity
Secure Socket Layer (SSL) Certification Market
Cybersecurity
Thailand IT and Security Market
Cybersecurity
Cloud Endpoint Protection Market
Cybersecurity
DNS Firewall Market
Cybersecurity
North America Cyber Security Market
Cybersecurity
Data-Centric Security Market
Cybersecurity
Asia Pacific Data Exfiltration Market
Cybersecurity
Digital Forensics Market
Cybersecurity
Global Container and Kubernetes Security Market
Cybersecurity
Global Cyber Threat Intelligence Market
Cybersecurity
Data Protection Market
Cybersecurity
Cloud Workload Protection Market
Cybersecurity
AI in Cybersecurity Market
Cybersecurity
Cloud DLP Market