
 Security Analytics Market | 2026-2036
Security Analytics Market Size, Share, and Industry Trends Forecast 2026-2036
Security Analytics Market Analysis
Multi-source procurement of threat detection capabilities is consolidating as enterprises abandon single-vendor security stacks for interoperable analytics layers. Cisco Systems leverages its network hardware installed base to embed telemetry collection at the edge. Palo Alto Networks competes through platform consolidation that unifies firewall, endpoint, and cloud workload data. CrowdStrike anchors its growth on endpoint-centric behavioral models that feed downstream SIEM correlation engines.
Security analytics denotes the systematic application of statistical analysis, machine learning, and rule-based correlation to security event data in order to identify anomalous patterns indicative of compromise, policy violation, or operational risk. The discipline processes log files, network flow records, and identity telemetry through normalized schemas such as the Common Event Format to enable cross-source querying and automated response orchestration. SIEM platforms occupy the largest revenue share as legacy compliance mandates sustain on-premises deployments among regulated institutions. Cloud-based delivery represents the fastest-expanding deployment mode as managed detection vendors abstract infrastructure overhead for mid-market buyers. Threat intelligence feeds constitute a concentrated margin pool where proprietary indicator enrichment commands subscription premiums.
FCC guidelines on communications infrastructure resilience, SEC disclosure rules for material cybersecurity incidents, and GDPR breach notification timelines collectively elevate the operational cost of undetected intrusions. HIPAA security rule enforcement drives healthcare systems toward continuous monitoring architectures that generate auditable detection trails. Buyers must evaluate vendor support for emerging quantum-resistant logging standards and cross-border data sovereignty requirements before committing to long-term analytics contracts.
Market Dynamics
Multi-source threat detection procurement is consolidating as enterprises abandon fragmented security stacks for interoperable analytics layers that unify telemetry across network, endpoint, and cloud workloads. This structural shift toward platform consolidation is compressing vendor margins while elevating the strategic value of normalized data schemas and automated response orchestration.
Growth Catalysts
- EU AI Act compliance mandates:BFSI institutions across Germany, France, and Italy are accelerating deployment of explainable detection algorithms to satisfy algorithmic transparency requirements for automated threat scoring.
- Behavioral analytics platforms:Industrial critical infrastructure operators are expanding real-time user and entity behavior analytics to detect insider threats and compromised credentials before lateral movement occurs.
- Federal auditing requirements:German operators of energy and transportation systems face intensified Bundesamt für Sicherheit in der Informationstechnik inspections, driving continuous monitoring architecture investments.
Market Restraints
- Specialized talent scarcity:The shortage of data scientists with domain expertise in adversarial machine learning limits enterprise ability to tune detection models and reduce false-positive rates.
- Cross-border data sovereignty:GDPR breach notification timelines and divergent national cloud localization laws fragment centralized analytics architectures, forcing redundant regional deployments.
- Legacy SIEM sunk costs:Regulated institutions with substantial on-premises compliance infrastructure face high migration friction when evaluating cloud-native detection alternatives.
Strategic Opportunities
- Managed detection services:Mid-market buyers lacking security operations center capabilities represent an underpenetrated segment for vendors abstracting infrastructure overhead through cloud delivery.
- Quantum-resistant logging standards:Early alignment with NIST post-quantum cryptographic guidelines for log integrity will differentiate vendors serving defense and financial sectors with long data retention requirements.
- Threat intelligence feed convergence:Proprietary indicator enrichment combining open-source, commercial, and sector-specific sources commands subscription premiums in a concentrated margin pool.
Industry Challenges
- Detection engineering skill gaps:Organizations struggle to hire analysts capable of translating threat intelligence into actionable detection rules across diverse telemetry sources.
- Multi-cloud correlation complexity:Security teams face integration friction when normalizing event formats across AWS, Azure, and Google Cloud native logging schemas into unified analytics pipelines.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Security Analytics Market |
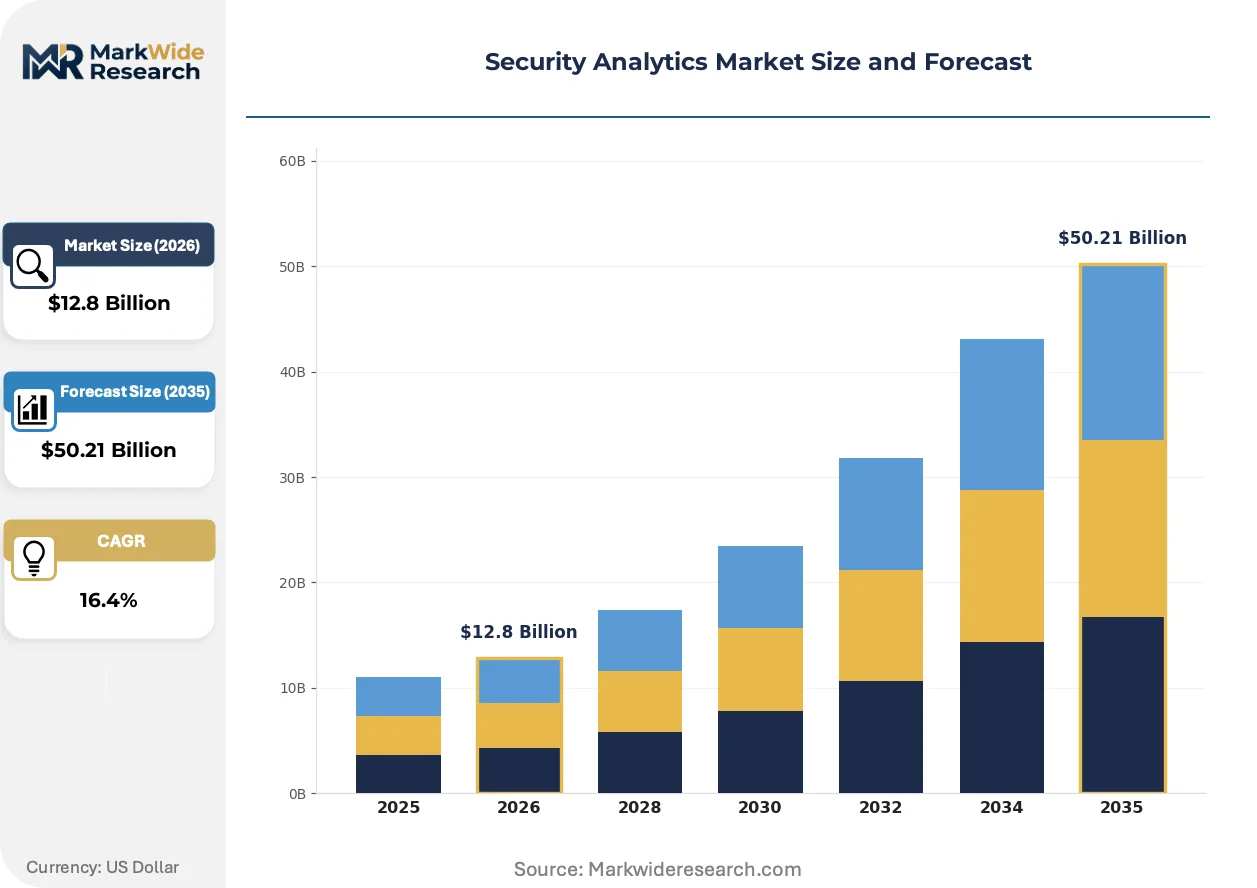
| Market Size in 2026 | $12.8 Billion |
| Market Size in 2035 | $50.21 Billion |
| CAGR (2026 – 2036) | 16.4% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: SIEM, User Behavior Analytics, Threat Intelligence, Network Traffic Analysis Deployment: Cloud-Based, On-Premises, Hybrid, Managed Service End User: Government, Healthcare, BFSI, Retail Application: Incident Response, Compliance Management, Risk Management, Fraud Detection |
| Companies Covered | Cisco Systems, Fortinet, Microsoft, Splunk, Check Point Software Technologies, Palo Alto Networks, CrowdStrike, RSA Security, IBM, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Security Analytics Market Emerging Trajectories
Extended detection and response architectures are actively reshaping competitive positioning by collapsing the traditional boundary between endpoint agents and centralized security information management. Vendors that control telemetry collection at the network edge are leveraging that position to displace standalone analytics providers.
Extended detection and response platforms are consolidating security telemetry from endpoints, networks, cloud workloads, and identity systems into unified detection pipelines. Large enterprises with mature security operations centers are adopting these architectures at the fastest pace, replacing point-product deployments. This consolidation is compressing the addressable market for standalone network traffic analysis and user behavior analytics vendors that lack native telemetry sources.
The EU AI Act and NIS2 Directive are mandating algorithmic explainability and supply-chain security attestations for automated threat detection systems. Industrial consequences include mandatory documentation of model training data provenance and human-in-the-loop requirements for high-risk automated blocking decisions. German critical infrastructure operators are most affected, responding by procuring only vendors with EU-established data processing and model governance capabilities.
Security procurement patterns are rotating from perpetual license purchases toward consumption-based pricing tied to event volume or analyst seat requirements. The channel being disrupted is traditional value-added reseller arrangements based on upfront enterprise license agreements, replaced by direct vendor relationships with usage-based billing. This shift is most visible in North American mid-market technology and professional services verticals where CFOs demand operational expenditure treatment for security tooling.
Security Analytics Market Segmentation
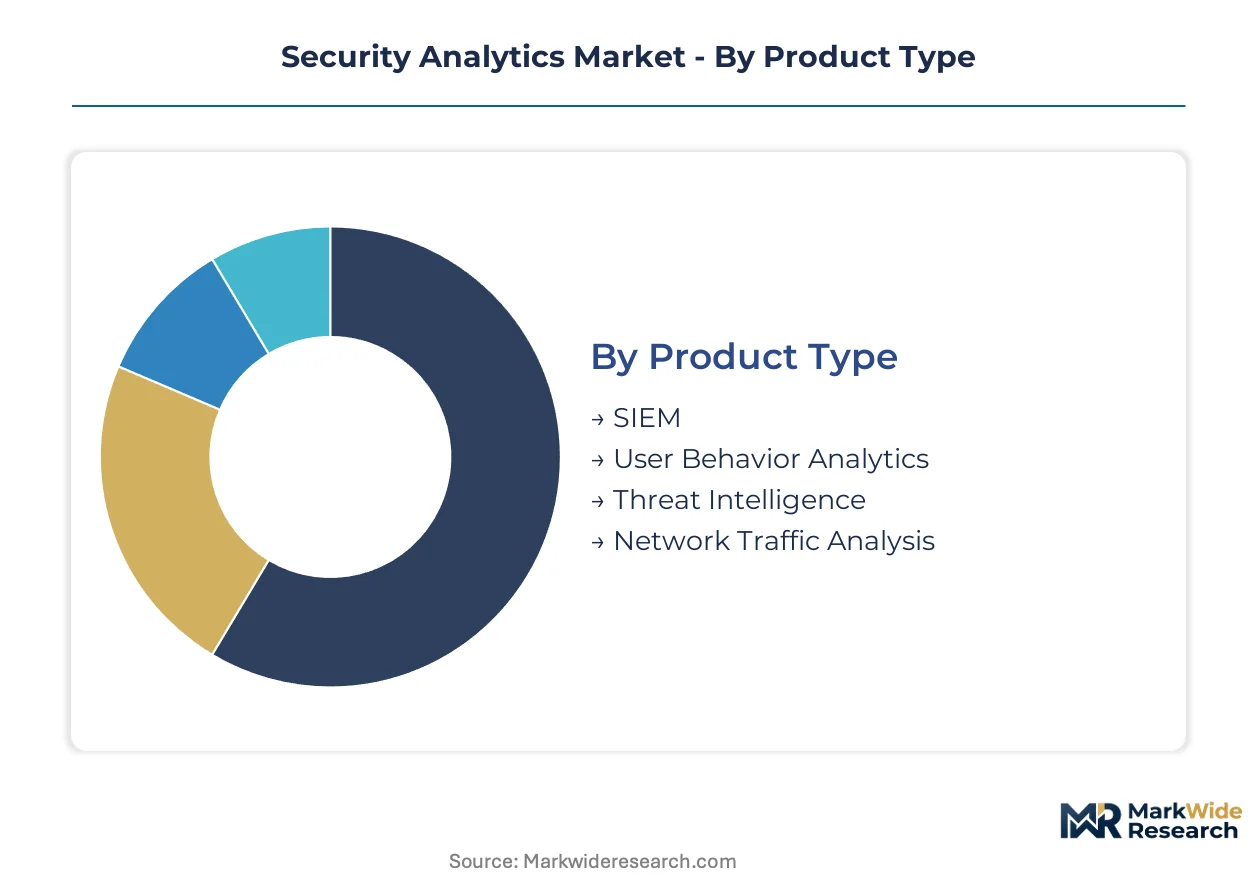
Security analytics procurement patterns diverge sharply across deployment architectures and end-user maturity. Buyers prioritize different capability bundles based on regulatory exposure, telemetry complexity, and security operations center sophistication.
Product Type:
Technology differentiation centers on data normalization depth and correlation engine architecture across four core platform categories.
- SIEM:Centralized platforms aggregate log streams through Common Event Format schemas, enabling cross-source querying and automated response orchestration. Demand concentrates among regulated BFSI institutions in Germany facing intensified federal auditing requirements for continuous monitoring.
- User Behavior Analytics:Statistical models profile entity activity baselines to flag anomalous access patterns indicative of compromised credentials or insider threats. Healthcare systems subject to HIPAA security rule enforcement are expanding real-time deployment to generate auditable detection trails.
- Threat Intelligence:Proprietary indicator enrichment combining open-source, commercial, and sector-specific sources commands subscription premiums in a concentrated margin pool.
- Network Traffic Analysis:Deep packet inspection and flow record correlation identify lateral movement and command-and-control communications.
Mature deployment sits with SIEM platforms. Newer deployment is concentrated in User Behavior Analytics.
Deployment:
Delivery mode selection reflects infrastructure ownership preferences and security operations center staffing constraints.
- Cloud-Based:Vendor-managed infrastructure abstracts compute and storage overhead, enabling consumption-based pricing tied to event volume. Mid-market technology and professional services verticals in North America are adopting this mode fastest as CFOs demand operational expenditure treatment.
- Managed Service:Third-party security operations centers assume detection engineering and incident response responsibilities. Buyers lacking internal analyst capabilities represent an underpenetrated segment for vendors offering 24/7 coverage.
- On-Premises:Dedicated hardware deployments satisfy data sovereignty requirements and legacy compliance mandates sustaining regulated institution preference.
- Hybrid:Split architectures retain sensitive log processing on-premises while offloading lower-sensitivity telemetry to cloud correlation engines.
Cloud-Based deployment is climbing the fastest. On-Premises retains the largest installed base.
End User:
Sector-specific regulatory frameworks dictate detection architecture priorities and vendor selection criteria.
- BFSI:Institutions across Germany, France, and Italy are accelerating explainable detection algorithm procurement to satisfy EU AI Act algorithmic transparency requirements for automated threat scoring.
- Government:Defense and intelligence agencies require quantum-resistant logging standards alignment with NIST post-quantum cryptographic guidelines for long data retention.
- Healthcare:HIPAA security rule enforcement drives continuous monitoring investments with mandatory breach notification timeline compliance.
- Retail:Payment card industry data security standard mandates sustain demand for transaction anomaly detection and point-of-sale telemetry correlation.
BFSI commands the highest per-seat analytics spending. Retail represents the most price-sensitive procurement segment.
Application:
Use case prioritization varies by organizational risk posture and regulatory enforcement exposure.
- Compliance Management:Automated audit trail generation and control mapping satisfy GDPR breach notification timelines, SEC disclosure rules, and FCC communications infrastructure resilience guidelines.
- Incident Response:Orchestrated containment workflows reduce mean time to remediation through pre-configured playbooks integrated with endpoint and network enforcement points.
- Risk Management:Quantitative exposure scoring correlates threat intelligence with asset criticality to prioritize vulnerability remediation.
- Fraud Detection:Real-time transaction scoring identifies synthetic identity and account takeover attempts before financial loss crystallization.
Compliance Management anchors procurement among regulated institutions. Incident Response is gaining share fastest in technology and professional services verticals.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Silicon Valley's concentration of cloud infrastructure anchors North American security analytics demand, while Frankfurt's data center density drives European procurement patterns.
United States
Financial services firms in New York and technology companies in California are consolidating threat detection stacks into unified platforms. SEC disclosure rules for material cybersecurity incidents mandate continuous monitoring investments. The Washington DC metro area hosts defense contractors requiring quantum-resistant logging standards alignment with NIST post-quantum cryptographic guidelines.
Germany
Industrial critical infrastructure operators across energy and transportation sectors are expanding behavioral analytics deployments. The EU AI Act and NIS2 Directive accelerate explainable detection algorithm procurement for automated threat scoring. Munich and Frankfurt clusters concentrate vendor activity as Bundesamt für Sicherheit in der Informationstechnik inspections intensify federal auditing requirements.
United Kingdom
London-based financial institutions are migrating from legacy SIEM toward cloud-native detection architectures. GDPR breach notification timelines and Financial Conduct Authority operational resilience rules elevate compliance automation priorities. The Cambridge-Oxford technology corridor generates demand for managed detection services among mid-market enterprises lacking security operations center capabilities.
Japan
Tokyo-headquartered manufacturers and Osaka-based financial groups are adopting extended detection and response platforms. METI cybersecurity framework updates emphasize supply-chain security attestations for automated systems. The Nagoya industrial cluster drives network traffic analysis investments to protect operational technology environments.
India
Bangalore's technology services sector and Mumbai's banking institutions are procuring cloud-based security analytics at accelerating rates. RBI guidelines on information security and SEBI cyber resilience directives mandate continuous monitoring. The Hyderabad cyber security cluster hosts domestic vendors competing on cost-optimized managed detection offerings.
Security Analytics Market Vendor Landscape
Global majors compete with regional champions across platform consolidation and telemetry source control. The vendor landscape segments into three tiers: network hardware incumbents embedding edge collection, cloud-native specialists unifying multi-source correlation, and endpoint-centric behavioral model providers. Consolidation pressure favors players with native telemetry generation capabilities over standalone analytics software vendors. Dominant competitive moves include strategic partnerships for data normalization schema alignment and geographic expansion through managed service delivery.
Within the network-embedded telemetry tier, Cisco Systems exemplifies hardware-anchored platform strategies, while Palo Alto Networks occupies a position bridging firewall consolidation with cloud workload visibility. CrowdStrike represents the endpoint-centric archetype feeding behavioral models into downstream correlation engines. These three companies illustrate how control over data collection infrastructure increasingly determines competitive positioning in unified security analytics architectures.
| Leading Market Players |
|---|
| Cisco Systems |
| Fortinet |
| Microsoft |
| Splunk |
| Check Point Software Technologies |
| Palo Alto Networks |
| CrowdStrike |
| RSA Security |
| IBM |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up managed detection vendors have compressed pricing discipline across the security analytics value chain, bundling 24/7 analyst coverage with cloud infrastructure to offset customer procurement fatigue while squeezing standalone SIEM providers into defensive discounting.
Pricing Analysis
Warranty and service bundling separates premium-tier offerings from unbundled alternatives. Three-tier pricing structure across premium, standard, and economy levels dominates, with premium tiers bundling dedicated detection engineering and sub-15-minute response SLAs. Price differentiation rests on analyst seat volume and data retention duration. Pricing pressure stems from hyperscaler-native entrants offering consumption-based telemetry ingestion at marginal cost. Retail verticals exhibit highest price sensitivity; defense contractors show lowest due to mandated audit trail requirements.
Supply Chain Analysis
Logistics and freight costs for on-premises SIEM hardware deployments concentrate supply chain friction in Germany, Japan, and the United States where data sovereignty mandates sustain localized appliance manufacturing. Component dependencies span specialized ASICs for deep packet inspection, high-density storage arrays, and EU-fabricated trusted platform modules. Single-source vulnerability in quantum-resistant cryptographic chip supply threatens long-term log integrity commitments. Distribution runs through direct vendor relationships and hyperscaler marketplaces, displacing traditional value-added reseller channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Platform consolidation is accelerating elimination of standalone analytics vendors, with EU AI Act compliance costs and telemetry source control advantages forcing weaker players toward acquisition or exit.
For Market Incumbents: Hedge against hyperscaler encroachment by deepening native telemetry generation through network edge appliance refresh cycles and endpoint agent ubiquity. Acquire specialized UEBA vendors in Germany and France to satisfy BSI and CNIL audit requirements. Prioritize explainable AI documentation capabilities before NIS2 enforcement deadlines tighten.
For New Entrants and Emerging Players: Enter via managed detection service delivery to mid-market healthcare systems in the United Kingdom and India lacking SOC staffing. Target cloud-native SIEM displacement in North American technology verticals where CFOs mandate OpEx treatment. Pursue channel partnerships with regional system integrators possessing existing federal security clearances.
For Investors and Strategic Acquirers: Distressed-cycle entries favor endpoint-centric behavioral model specialists with EU-established data processing capabilities in Germany and the Netherlands. Five-to-ten-year viability hinges on quantum-resistant logging certification alignment with NIST guidelines. Monitor Bundesamt für Sicherheit in der Informationstechnik inspection frequency as inflection indicator for German critical infrastructure procurement velocity.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, network, and cloud telemetry into single correlation pipeline for BFSI compliance. |
| Acquisition of Specialist Firm | Captures UEBA capabilities and EU AI Act documentation expertise concentrated in German vendors. |
| Strategic Partnership | Aligns data normalization schemas with hyperscaler logging formats to reduce multi-cloud friction. |
| Geographic Expansion | Establishes sovereign data processing presence in Frankfurt and Munich for BSI audit readiness. |
| Product Launch | Introduces quantum-resistant log integrity modules targeting defense sector retention requirements. |
Methodological Framework
Document review covered vendor technical documentation, EU regulatory filings, and NIST cryptographic guidelines, complemented by interviews with CISOs at BFSI institutions, detection engineering leads at managed security providers, federal audit specialists at BSI, and procurement officers at critical infrastructure operators. Secondary validation drew from SEC cybersecurity disclosure filings, EBA threat intelligence reports, and cloud infrastructure capex disclosures. Bottom-up deployment estimates triangulated against top-down market sizing across the analysis window.
Segmented outputs by deployment architecture, end-user vertical, and application use case informed analytical framework construction throughout the projection horizon. CAGRs derived from telemetry volume growth curves, compliance mandate enforcement timelines, and substitution elasticity between on-premises and cloud-native delivery. Industry-specific inputs included SIEM replacement cycle data, SOC staffing cost inflation, and EU AI Act implementation phase schedules.
Revisions become necessary when quantum-resistant standard finalization delays, BSI inspection scope expansions, or hyperscaler pricing aggression materialize beyond modeled assumptions. Stakeholders should weight assumptions against their own operating context.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
Forensic Technologies Market
Security and Surveillance
Home Security Sensors Market
Security and Surveillance
Integrated Security Solutions Market
Security and Surveillance
Crowdsourced Security Market
Security and Surveillance
Global Security Policy Management Market
Security and Surveillance
Electronic Alarms Market
Security and Surveillance
Global Wireless Doorbells Market
Security and Surveillance
Global Integration Security Services Market
Security and Surveillance
Air Cargo Security and Screening Systems Market
Security and Surveillance
Threat Detection Systems Market
Security and Surveillance
Asia-Pacific Security Services Market
Security and Surveillance
Underwater Security (Systems and Services) Market
Security and Surveillance
Signal Jammer Market
Security and Surveillance
Maritime Security Market
Security and Surveillance
Latin America Electronics Security Market
Security and Surveillance
Global Police and Law Enforcement Equipment Market