
 Global Threat Intelligence Management Market | 2026-2036
Global Threat Intelligence Management Market Size, Share, and Industry Trends Forecast 2026-2036
Global Threat Intelligence Management Market Foresight
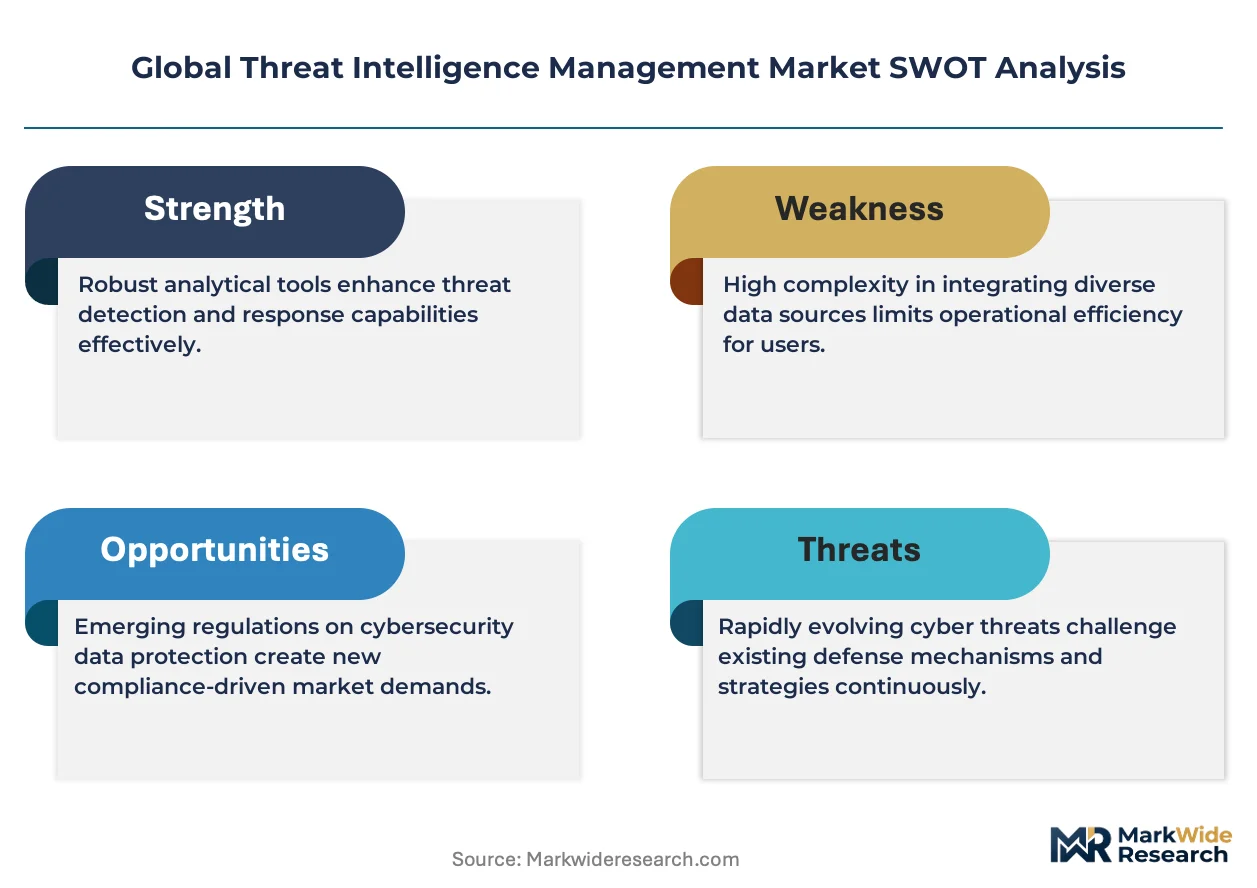
The capability gap between cloud-native platforms and legacy on-premises architectures is rotating competitive capital allocation across the sector. IBM Corporation leverages its hybrid cloud infrastructure to sustain enterprise deployments at scale. CrowdStrike Inc. anchors its position through endpoint-native intelligence collection that extends real-time threat correlation. Palo Alto Networks, Inc. competes via integrated network-security-to-intelligence pipelines that dominate large telecom and energy accounts.
Threat intelligence management encompasses the collection, normalization, analysis, and operationalization of adversary indicators, attack patterns, and vulnerability data to preempt or shorten security incidents. Platforms ingest structured feeds such as STIX/TAXII protocols alongside unstructured dark-web monitoring to automate indicator-to-action workflows at machine speed. Cloud-based deployment models are capturing the fastest expansion as Security Operations Centers demand elastic compute for behavioral analytics and automated orchestration. Threat Intelligence Platform solutions occupy the deepest margin pools where proprietary scoring algorithms and exclusive source partnerships create switching costs. On-premises deployments retain material share among government agencies and regulated financial institutions with data-sovereignty requirements.
The U.S. Securities and Exchange Commission's cyber disclosure rules, the EU NIS2 Directive, and Japan's METI cybersecurity framework collectively mandate systematic threat intelligence integration into governance and incident response. These regulations shape demand by penalizing delayed detection and imposing supply-chain security attestations on critical service providers. Stakeholders must monitor divergence between regional certification standards and cloud-provider compliance architectures as fragmentation risk escalates procurement complexity.
Market Dynamics
The migration from signature-based detection to behavioral analytics and AI-driven threat hunting is compressing refresh cycles for security infrastructure and reallocating vendor procurement budgets toward platforms with native machine-learning inference.
Growth Catalysts
- EU NIS2 Directive:The directive mandates systematic threat intelligence integration for critical service providers across energy, transport, and digital infrastructure sectors, creating compliance-driven procurement pipelines.
- Behavioral analytics engines:Financial services firms deploy these systems to detect anomalous payment patterns and insider threats at machine speed, shortening mean-time-to-detection metrics.
- Japan METI cybersecurity framework:Japan's industrial policy requires supply-chain security attestations from critical manufacturers, expanding platform deployments among automotive and semiconductor suppliers.
Market Restraints
- Data sovereignty requirements:Government agencies in Germany and France restrict cross-border telemetry flows, fragmenting cloud-native platform architectures and inflating compliance engineering costs.
- Skilled analyst scarcity:The shortage of professionals trained in STIX/TAXII protocol implementation and indicator-of-compromise validation limits operationalization of raw intelligence feeds.
- Legacy SIEM sunk costs:Enterprises with entrenched on-premises security information and event management systems face high switching costs that delay platform consolidation decisions.
Strategic Opportunities
- Operational technology convergence:The integration of IT and OT security stacks in manufacturing and energy creates demand for industrial control system-aware threat intelligence platforms.
- India's digital public infrastructure:The country's expanding critical digital services require indigenous threat intelligence capabilities, opening procurement channels for localized platform deployments.
- Automated orchestration standards:The OASIS OpenC2 protocol enables standardized machine-to-machine response actions, allowing vendors to differentiate through response-playbook sophistication.
Industry Challenges
- Alert fatigue remediation:Security operations centers struggle to prioritize high-fidelity indicators amid noise from commoditized threat feeds, degrading operational effectiveness.
- Attribution confidence calibration:Analysts face pressure to assign threat actor provenance with insufficient telemetry, risking false-positive escalations and resource misallocation.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Global Threat Intelligence Management Market |
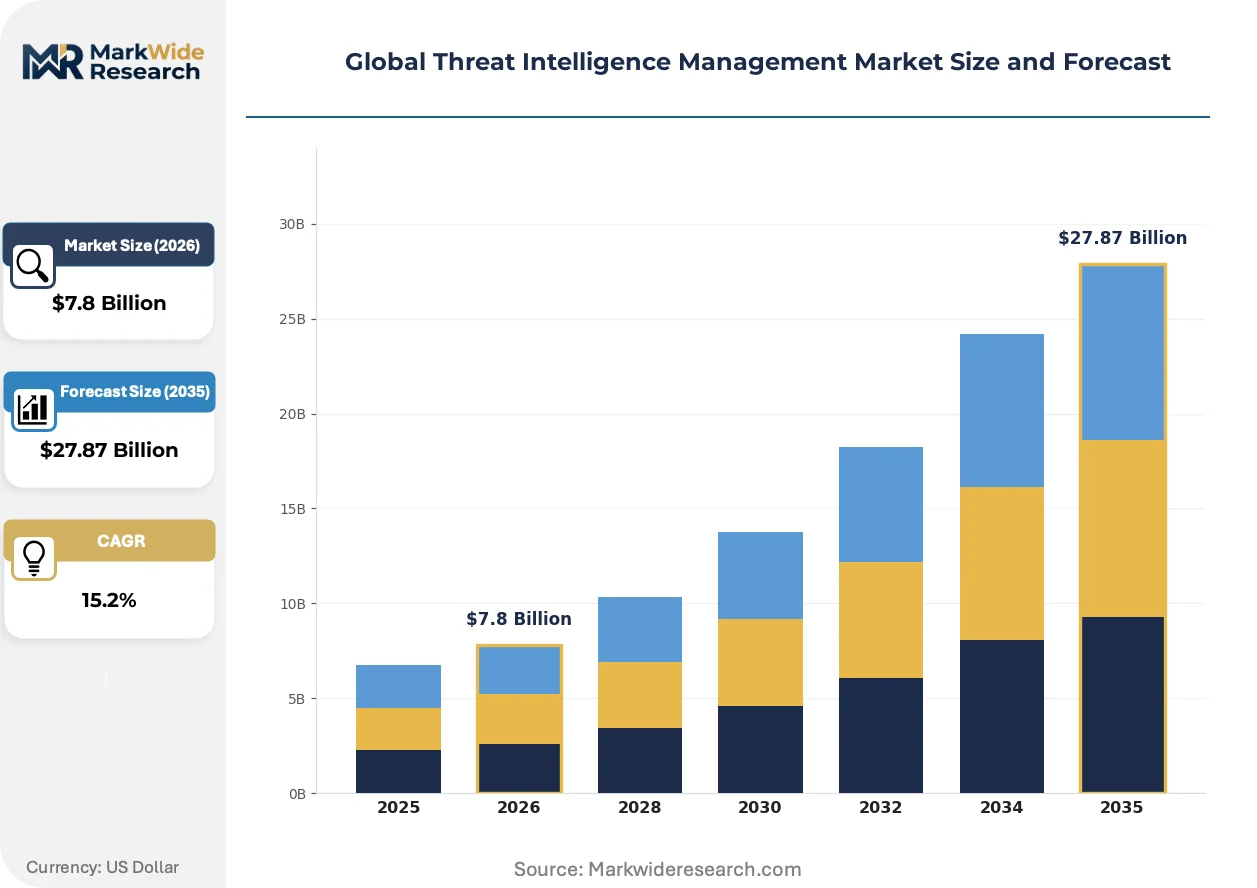
| Market Size in 2026 | $7.8 Billion |
| Market Size in 2035 | $27.87 Billion |
| CAGR (2026 – 2036) | 15.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Threat Intelligence Platform, Threat Data Feeds, Vulnerability Intelligence, Endpoint Detection, Incident Response, Security Analytics Deployment Model: Cloud-Based, On-Premises, Hybrid, Managed Security Service, Virtual Appliance Application Sector: Financial Services, Telecommunications, Government Agencies, Energy & Utilities, Manufacturing, Education End User Category: Security Operations Centers, Managed Security Providers, Enterprises, IT Service Providers, Consulting Firms |
| Companies Covered | IBM Corporation, Cisco Systems, Inc., CrowdStrike Inc., Palo Alto Networks, Inc., Fortinet, Inc., McAfee, LLC, Check Point Software Technology Ltd., Trend Micro Incorporated, Recorded Future, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Global Threat Intelligence Management Market Shifts & Advancements
Threat intelligence platforms are absorbing adjacent security functions while fragmenting into specialized layers, creating new competitive battlegrounds around data provenance and inference speed.
Extended detection and response architectures are bifurcating the vendor landscape. These systems consolidate endpoint telemetry, network traffic analysis, and third-party intelligence into unified correlation engines. Large enterprises with mature security operations centers adopt these platforms rapidly, compressing standalone threat intelligence point solutions into feature sets within broader suites.
The EU AI Act imposes risk-classification requirements on automated threat detection systems used in critical infrastructure. High-risk applications must maintain human oversight mechanisms and algorithmic transparency documentation. European energy and telecom operators are restructuring procurement specifications to mandate compliance attestations from platform vendors.
Security buyers are consolidating vendor relationships to reduce integration complexity. Large enterprises now prefer single-platform contracts covering intelligence ingestion, analysis, and response orchestration rather than stitching together specialized tools. This preference shift is most pronounced in United States financial services, where procurement teams prioritize operational simplicity over best-of-breed feature depth.
Global Threat Intelligence Management Market Segmentation
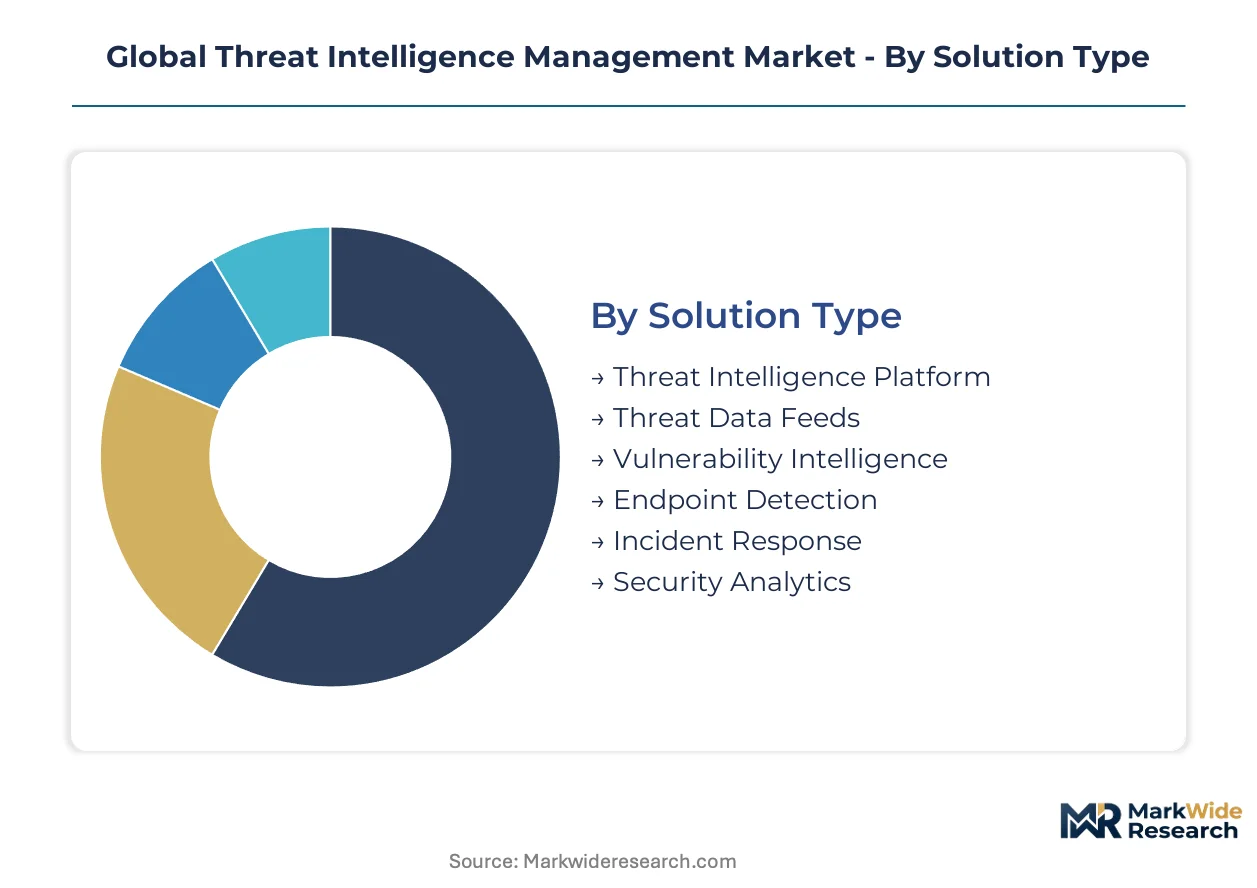
Segmentation in threat intelligence management reveals how procurement priorities diverge between compliance-driven government buyers and velocity-focused financial services. Deployment choices and solution architectures cluster around data sovereignty requirements, while application sectors show distinct tolerance for cloud-native versus on-premises delivery models.
Solution Type:
Substitution pressure concentrates in commoditized threat data feeds, where open-source alternatives erode pricing power, while integrated platforms build durable switching costs through proprietary scoring algorithms.
- Threat Intelligence Platform:Unified systems ingest STIX/TAXII feeds alongside dark-web telemetry to automate indicator-to-action workflows. United States financial services firms prioritize these platforms for real-time ransomware correlation, driven by SEC cyber disclosure mandates requiring systematic threat integration.
- Threat Data Feeds:Structured streams of indicators of compromise delivered via API or file exchange, facing margin compression from open-source alternatives like MISP. Demand persists among German manufacturers with OT security requirements, constrained by skilled analyst scarcity for feed operationalization.
- Vulnerability Intelligence:Curated databases of exploitability assessments and patch prioritization scoring.
- Endpoint Detection:Telemetry collection agents that feed behavioral analytics engines for device-level threat hunting.
- Incident Response:Orchestration modules that automate containment playbooks and forensic evidence preservation.
- Security Analytics:Behavioral correlation engines processing multi-source telemetry for anomaly detection.
Threat Intelligence Platform retains volume leadership; Threat Data Feeds holds the steepest expansion curve as managed service wrappers restore differentiation.
Deployment Model:
Cost tiering separates elastic cloud consumption from capital-intensive on-premises builds, with hybrid architectures capturing mid-market buyers seeking staged migration paths.
- Cloud-Based:Elastic compute resources supporting behavioral analytics and automated orchestration without infrastructure ownership. United States Security Operations Centers dominate procurement, propelled by demand for machine-speed threat hunting without capacity constraints.
- On-Premises:Dedicated hardware deployments maintaining complete data sovereignty and air-gapped operations. Japanese government agencies and German critical infrastructure operators require these configurations, limited by cross-border telemetry restrictions fragmenting architectures.
- Hybrid:Split workloads with sensitive analytics on-premises and scalable processing in cloud environments.
- Managed Security Service:Outsourced platform operation delivered as subscription by specialized providers.
- Virtual Appliance:Pre-configured software images deployable on customer-owned virtualization infrastructure.
Cloud-Based deployments command the largest revenue pool; Hybrid models are climbing the fastest as regulated industries pursue staged cloud adoption.
Application Sector:
Customer maturity stratifies around incident response velocity requirements, with financial services demanding real-time correlation while education sectors tolerate batch-processed intelligence.
- Financial Services:Banks, payment processors, and insurance carriers deploying behavioral analytics for fraud and ransomware defense. Germany's BaFin supervisory requirements and Japan's FSA guidelines mandate systematic threat intelligence integration, accelerating platform procurement.
- Telecommunications:Network operators correlating traffic anomalies with adversary infrastructure indicators. United States carriers face FCC supply-chain security attestations, driving integrated network-security-to-intelligence pipeline investments.
- Government Agencies:National security and civilian departments with data sovereignty and classification requirements.
- Energy & Utilities:Critical infrastructure operators subject to NIS2 Directive systematic threat intelligence mandates.
- Manufacturing:Industrial firms converging IT and OT security stacks for control system protection.
- Education:Universities and research institutions with limited security operations center staffing.
Financial Services maintains the deepest procurement budgets; Energy & Utilities gains share fastest under EU NIS2 compliance deadlines.
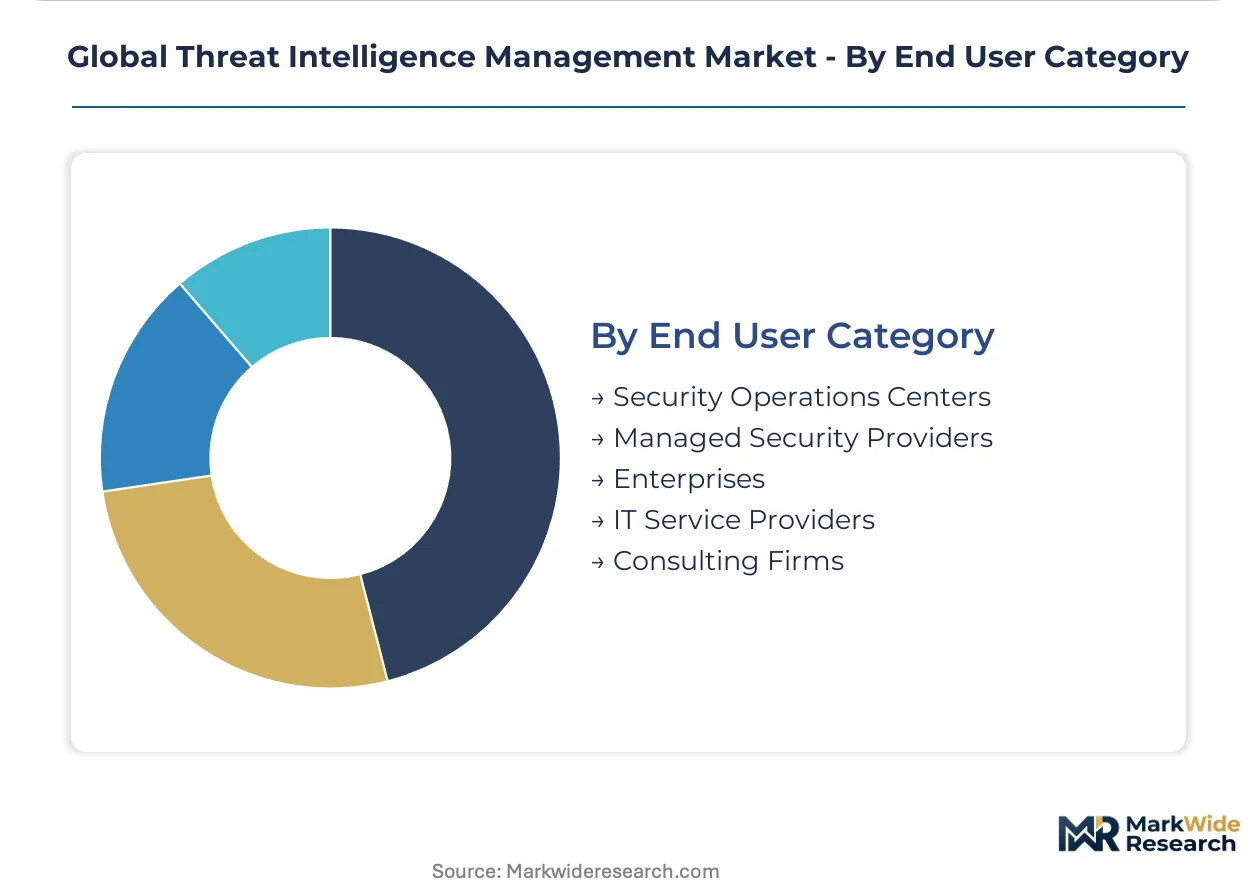
End User Category:
Supply concentration among large enterprises creates tiered service models, with Managed Security Providers capturing mid-market buyers lacking internal analyst capacity.
- Security Operations Centers:Internal threat hunting teams demanding high-fidelity indicators and automated orchestration. United States enterprises with mature SOCs consolidate vendor relationships, preferring single-platform contracts covering ingestion through response.
- Managed Security Providers:Outsourced security operations delivering threat intelligence as service to client portfolios. These providers scale across German Mittelstand manufacturers and Japanese automotive suppliers, capitalizing on skilled analyst scarcity limiting internal hiring.
- Enterprises:Large organizations with dedicated security staff and multi-year platform commitments.
- IT Service Providers:Technology integrators embedding threat intelligence into broader managed service offerings.
- Consulting Firms:Advisory practices delivering strategic threat assessments and program design.
Security Operations Centers represent the largest addressable base; Managed Security Providers expand most quickly through mid-market penetration.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Pricing power concentrates in the United States while compliance engineering costs inflate deployments across Germany, creating a transatlantic asymmetry in platform profitability. German operators absorb 15-25% cost premiums for data-sovereignty architectures. Japanese buyers command specialized OT-aware configurations unavailable in standardized offerings.
United States
Financial services SOCs drive elastic cloud procurement for machine-speed ransomware correlation. SEC cyber disclosure rules mandate systematic threat intelligence integration into governance frameworks. New York and Chicago banking clusters consolidate vendor relationships toward single-platform contracts covering ingestion through response orchestration.
Germany
Critical infrastructure operators under NIS2 Directive deadlines expand systematic threat intelligence procurement across energy and transport sectors. BaFin supervisory requirements impose supply-chain security attestations on financial institutions. Munich and Frankfurt technology hubs concentrate hybrid deployment expertise for Mittelstand manufacturers navigating data-sovereignty constraints.
Japan
Automotive and semiconductor suppliers deploy industrial control system-aware platforms under METI cybersecurity framework mandates. FSA guidelines accelerate behavioral analytics adoption for payment fraud detection. Nagoya and Osaka manufacturing belts converge IT-OT security stacks for production line protection.
India
Digital public infrastructure expansion creates procurement channels for localized threat intelligence capabilities. RBI cybersecurity guidelines push banks toward automated indicator-to-action workflows. Bangalore and Hyderabad technology corridors attract MSSP investments serving mid-market enterprises lacking internal analyst capacity.
United Kingdom
Telecom operators face supply-chain security attestations driving integrated network-security-to-intelligence pipeline investments. NCSC guidance shapes procurement specifications for critical national infrastructure protection. London financial services clusters prioritize operational simplicity over best-of-breed feature depth in platform selection.
Global Threat Intelligence Management Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes, with endpoint-native specialists commanding premium pricing while network-security incumbents leverage installed base scale. The vendor landscape consolidates around three strategic tiers: cloud-native platforms with proprietary scoring algorithms, legacy on-premises providers with government relationships, and managed security service wrappers restoring differentiation to commoditized threat feeds. Dominant competitive moves include portfolio diversification into adjacent security functions and strategic partnerships for exclusive source access.
Within the cloud-native platform tier, CrowdStrike Inc. and Palo Alto Networks, Inc. exemplify divergent architectural bets on endpoint telemetry versus network-security integration. IBM Corporation anchors the hybrid infrastructure segment through enterprise deployment scale. These three entities occupy positions reflecting the sector's central tension between velocity-focused financial services buyers and compliance-constrained government agencies.
| Leading Market Players |
|---|
| IBM Corporation |
| Cisco Systems, Inc. |
| CrowdStrike Inc. |
| Palo Alto Networks, Inc. |
| Fortinet, Inc. |
| McAfee, LLC |
| Check Point Software Technology Ltd. |
| Trend Micro Incorporated |
| Recorded Future |
| Others |
Supply & Pricing Matrix
Long-term subscription contracts with capacity reservation clauses lock in supply access for cloud-native threat intelligence platforms while anchoring price visibility across multi-year procurement cycles. These arrangements concentrate buyer power among United States financial services SOCs and German critical infrastructure operators facing NIS2 Directive compliance deadlines.
Pricing Analysis
The customization-premium spread separates configured-to-order deployments for German government agencies with data-sovereignty requirements from standardized SaaS tiers serving United States mid-market enterprises. Subscription-based pricing dominates, with differentiation anchored in certification level (ISO 27001, SOC 2 Type II) and integration complexity. Cost compression in commoditized threat data feeds is intensifying because open-source alternatives like MISP erode feed pricing power. Mid-market buyers lacking internal STIX/TAXII expertise exhibit highest price sensitivity, while regulated financial institutions absorb premium pricing for compliance-attested configurations.
Supply Chain Analysis
Proprietary dark-web source networks in Israel, exclusive government partnerships in the United States, and specialized OT telemetry providers in Japan constitute critical chokepoints for high-fidelity intelligence ingestion. Platform architectures draw from commercial threat feeds, open-source indicator repositories, and human-curated adversary research. Single-source vulnerability in exclusive source partnerships fragments competitive positioning when contracts expire. Distribution runs through direct enterprise sales for large accounts and managed security service provider channels for mid-market penetration.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The threat intelligence management market sits in early-cycle expansion as behavioral analytics adoption accelerates refresh cycles for signature-based detection infrastructure. EU NIS2 Directive mandates across energy and transport sectors create compliance-driven procurement pipelines that extend through mid-decade.
For Market Incumbents: Secure exclusive source partnerships with dark-web monitoring specialists and government CERT teams to differentiate feed quality. Invest in algorithmic transparency documentation required by EU AI Act high-risk system classifications. Vertical integration into OT-aware telemetry collection addresses manufacturing convergence demand while raising switching costs for industrial clients.
For New Entrants and Emerging Players: Managed service wrappers for threat feed operationalization address skilled analyst scarcity limiting German Mittelstand manufacturers and Japanese automotive suppliers. India's digital public infrastructure expansion offers the most penetrable geography for localized platform deployment. A channel-first go-to-market through regional MSSPs bypasses direct competition with entrenched enterprise sales teams.
For Investors and Strategic Acquirers: Cloud-native platforms with proprietary scoring algorithms and established STIX/TAXII integration layers represent the priority acquisition archetype. Long-term viability hinges on differentiation durability as EDR suites absorb standalone intelligence functions. Monitor OpenC2 protocol adoption rates as an inflection indicator for automated orchestration standardization enabling vendor consolidation.
| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Consolidates endpoint, network, and intelligence telemetry into unified correlation engines for SOC efficiency. |
| Acquisition of Specialist Firm | Captures exclusive dark-web source networks or OT-aware telemetry capabilities that create switching costs. |
| Geographic Expansion | Establishes localized deployments in India and Southeast Asia serving digital infrastructure protection mandates. |
| Strategic Partnership | Secures government CERT relationships or critical infrastructure operator co-development for compliance-attested configurations. |
| Product Launch | Introduces AI Act-compliant transparency documentation and human oversight mechanisms for European energy operators. |
Research Methodology
Operator-level perspectives from CISOs at financial services institutions, SOC directors at telecommunications operators, procurement leads at German energy utilities, and compliance officers at Japanese automotive suppliers anchored the qualitative base. These primary insights combined with secondary validation from SEC cyber disclosure filings, EU NIS2 implementation guidance documents, Japan METI framework updates, and hyperscaler security capex disclosures. Bottom-up deployment estimates triangulated against top-down market sizing across cloud-native platform, hybrid architecture, and on-premises configuration categories.
Sensitivity analysis tested forecast outputs against alternative adoption curves for behavioral analytics engines and regulatory enforcement intensity variations. Segmentation dimensions modeled include solution type, deployment model, application sector, and end user maturity tier across the projection horizon. CAGRs derived from elasticity-adjusted demand curves incorporating compliance deadline clustering and infrastructure refresh cycle timing. Industry-specific inputs encompassed STIX/TAXII protocol adoption rates and skilled analyst availability indices by geography.
Forecasts assume regulatory continuity in EU NIS2 Directive implementation, SEC cyber disclosure enforcement, and Japan METI framework evolution; material policy shifts would require re-modeling demand timing and procurement specification changes. Specific risk factors include data sovereignty restriction tightening fragmenting cloud architectures and alert fatigue degradation reducing operationalization effectiveness. Practitioners should keep alternative scenarios live as EDR suite absorption rates and OpenC2 standardization progress evolve.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security and Surveillance
North America Security Services Market
Security and Surveillance
Urban Security Screening Market
Security and Surveillance
Global Adaptive Security Market
Security and Surveillance
Global Firearm Sight Market
Security and Surveillance
Door and Window Alarm Market
Security and Surveillance
TSCM Equipment Market
Security and Surveillance
Russian Intelligent Eavesdropping Detection System Market
Security and Surveillance
Europe Border Security Market
Security and Surveillance
Security Analytics Market
Security and Surveillance
Underwater Security (Systems and Services) Market
Security and Surveillance
Latin America Security Services Market
Security and Surveillance
Smart Security Market
Security and Surveillance
Multi-Layer Security Market
Security and Surveillance
Night Vision Binoculars Market
Security and Surveillance
Smart Security in Healthcare Market
Security and Surveillance
Europe Urban Security Screening Market