
 Digital Security Control Market | 2026-2036
Digital Security Control Market Size, Share, and Industry Trends Forecast 2026-2036
Digital Security Control Market Outlook
Cloud-native security architectures is reshaping how enterprises deploy and manage digital protection layers, shifting capital from hardware appliances to subscription-based platforms. Palo Alto Networks leverages its Prisma portfolio to anchor cloud-delivered security across multi-tenant environments. CrowdStrike differentiates through endpoint detection and response telemetry that feeds a unified threat graph. Fortinet sustains competitive pressure with integrated networking-security convergence at scale.
Digital security control encompasses hardware, software, and service-based mechanisms engineered to authenticate users, encrypt data transmissions, detect anomalous network behavior, and enforce access policies across distributed IT environments. These systems typically process traffic at line rates exceeding 100 Gbps while maintaining sub-millisecond inspection latency for real-time threat mitigation. Firewalls and intrusion detection systems occupy the mature core of product spending, while encryption tools command premium pricing in regulated verticals. Cloud security deployments are expanding fastest as organizations retire on-premise data centers, though hybrid configurations retain dominant share among enterprises with legacy mainframe dependencies.
The National Institute of Standards and Technology, the Securities and Exchange Commission, and the Cybersecurity and Infrastructure Security Agency collectively shape vendor product roadmaps through mandatory disclosure rules, zero-trust architecture mandates, and critical infrastructure protection standards. FDA cybersecurity guidance for connected medical devices further extends compliance obligations into healthcare sub-markets. Stakeholders must weigh sovereign data localization requirements against cloud economics when configuring multi-region deployment strategies.
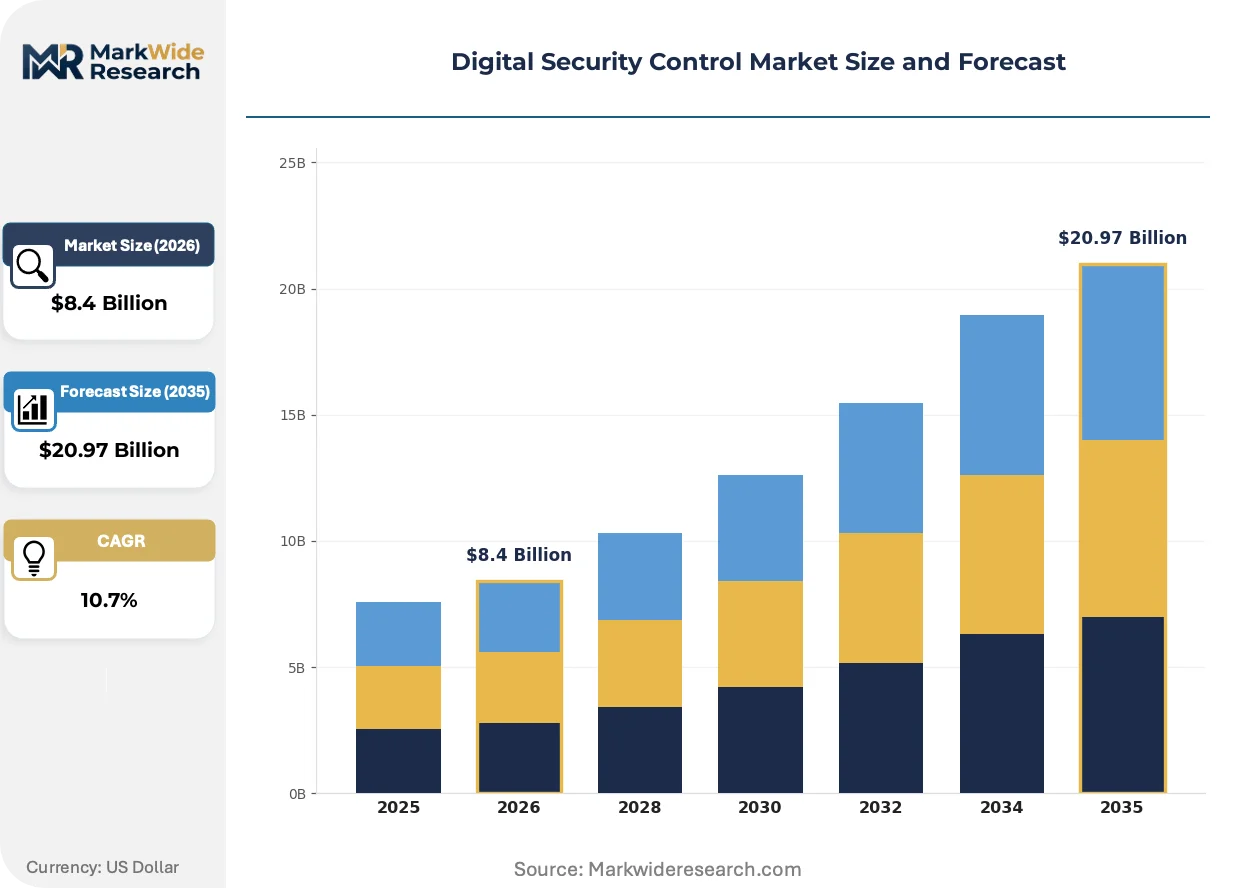
Market Dynamics
Cloud-native security architectures are collapsing traditional hardware procurement cycles as federal agencies and defense contractors accelerate zero-trust mandates, forcing vendors to reengineer delivery models around subscription telemetry rather than perpetual licensing.
Growth Catalysts
- Zero-Trust Architecture Mandates:CISA directives require federal contractors to eliminate implicit trust from network perimeters. Defense industrial base suppliers are retrofitting legacy access controls to meet these binding operational requirements.
- EU AI Act Compliance Deadlines:European enterprises face tiered conformity obligations for automated threat detection systems. Vendors serving this market are accelerating product certification timelines to capture procurement windows.
- Medical Device Connectivity Expansion:FDA cybersecurity guidance for connected diagnostics and surgical robotics is extending digital security control requirements into hospital capital expenditure cycles.
Market Restraints
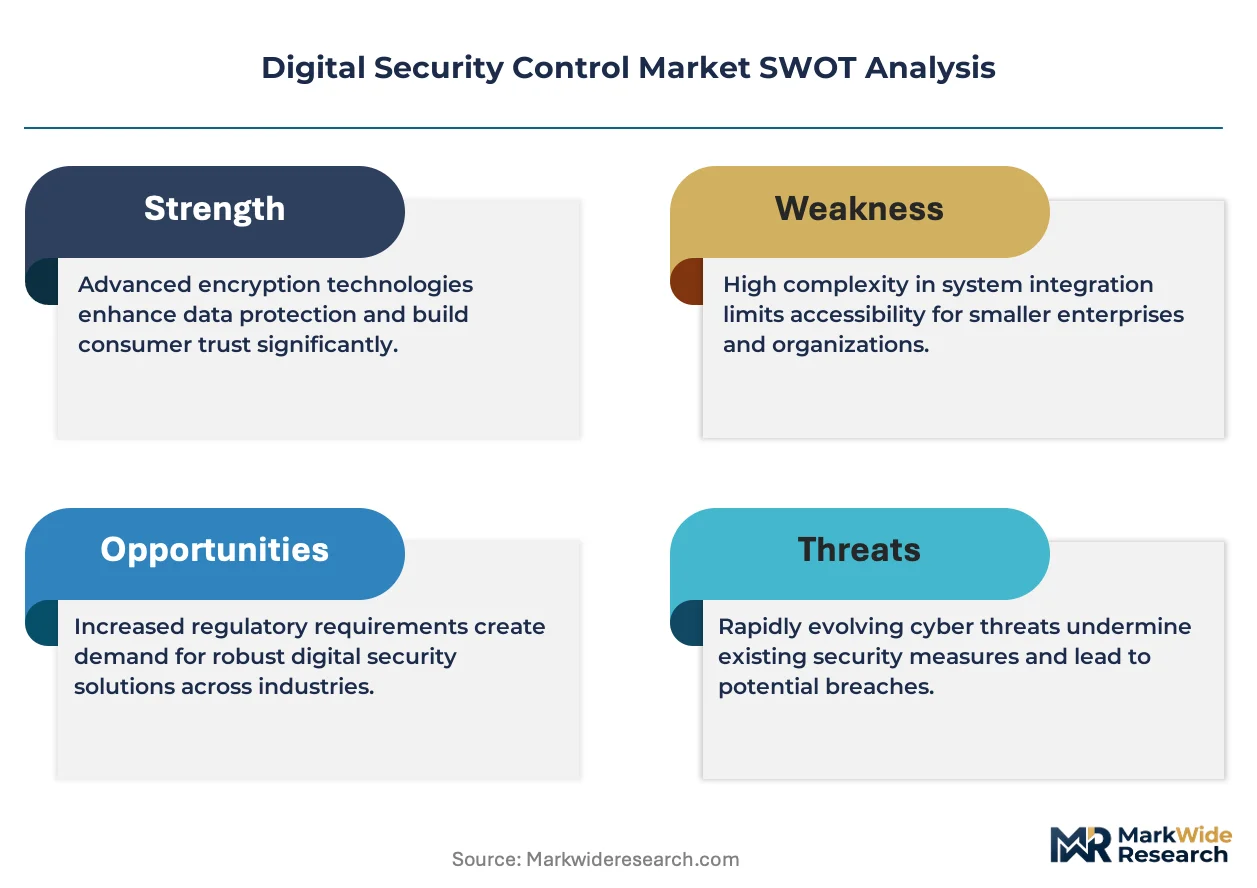
- Semiconductor Supply Concentration:Advanced packet inspection ASICs depend on TSMC fabrication capacity in Taiwan. Geopolitical friction creates inventory vulnerability for firewall appliance manufacturers.
- Specialized Cybersecurity Labor Scarcity:Zero-trust architecture deployment requires certified security architects. Talent pools in cloud security engineering remain insufficient relative to implementation demand.
- Encryption Export Control Friction:US Commerce Department restrictions on cryptographic technology transfers limit vendor addressable markets in certain sovereign jurisdictions.
Strategic Opportunities
- Operational Technology Convergence:Industrial control systems in energy and manufacturing are merging IT and OT security stacks. Vendors with cross-domain visibility platforms can capture greenfield deployment budgets.
- India Digital Infrastructure Expansion:CERT-In directives and data localization requirements are creating procurement velocity for indigenous security operations centers and sovereign cloud deployments.
- Post-Quantum Cryptography Transition:NIST standardization of quantum-resistant algorithms will force certificate authority and encryption tool refreshes across financial services and government sectors.
Industry Challenges
- Mainframe Integration Complexity:Enterprises with legacy IBM zSystems environments struggle to extend zero-trust policies to transaction processing workloads. Hybrid security orchestration remains technically immature.
- Cross-Border Data Sovereignty Conflicts:Conflicting localization mandates between EU GDPR, China PIPL, and US CLOUD Act create architectural paralysis for multinational security deployments.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Digital Security Control Market |
| Market Size in 2026 | $8.4 Billion |
| Market Size in 2035 | $20.97 Billion |
| CAGR (2026 – 2036) | 10.7% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Product Type: Firewalls, Antivirus Software, Encryption Tools, Intrusion Detection Systems Technology: Blockchain, Artificial Intelligence, Cloud Security, Biometrics End User: Government, Financial Services, Healthcare, Education Deployment: On-Premise, Cloud-Based, Hybrid, Managed Services |
| Companies Covered | Cisco Systems, Inc., Fortinet, Inc., Palo Alto Networks, Microsoft, McAfee, LLC, Check Point Software Technologies Ltd., IBM Corporation, Trend Micro, Inc., CrowdStrike, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Digital Security Control Market Strategic Shifts
Security delivery models are fragmenting across edge, cloud, and sovereign infrastructure layers, creating pressure on vendors to unify telemetry without consolidating physical control planes.
Confidential computing hardware enclaves are collapsing the traditional boundary between encryption-at-rest and encryption-in-use. Financial services institutions are piloting AMD SEV-SNP and Intel TDX implementations for high-frequency trading analytics. This architectural shift is collapsing the separate procurement tracks for data protection and compute infrastructure.
EU AI Act risk classification tiers are reshaping vendor product development roadmaps. High-risk automated threat detection systems now require conformity assessments before market placement. European critical infrastructure operators are prioritizing vendors with pre-certified AI governance documentation.
Consumption-based licensing is displacing perpetual entitlement models in enterprise procurement. Security operations teams prefer metered billing aligned to actual event volume and user count. This pattern is most pronounced among mid-market SaaS providers replacing three-year firewall refresh cycles with month-to-month cloud security subscriptions.
Digital Security Control Market Segmentation
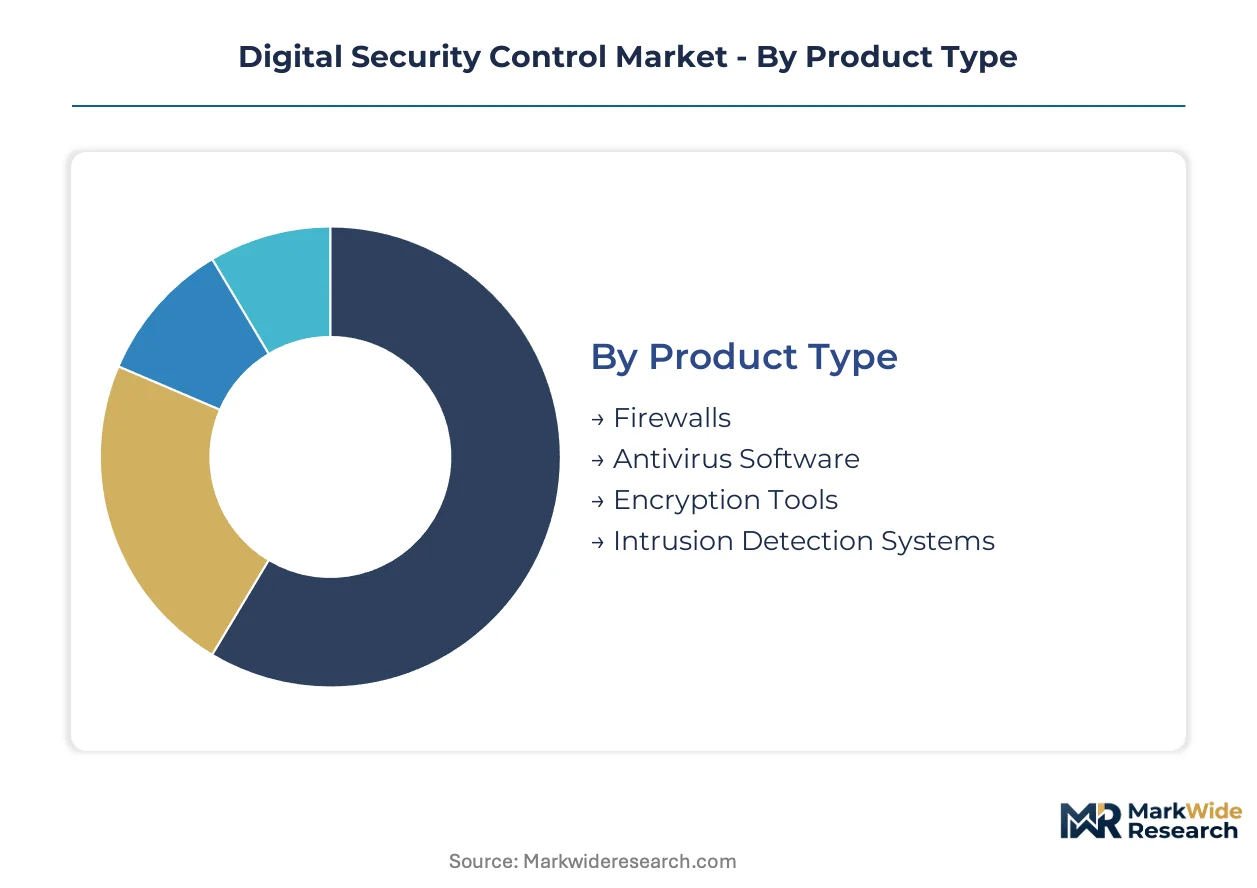
Digital security control procurement patterns diverge sharply across product architectures, deployment models, and compliance regimes. Vendors must align certification roadmaps with sector-specific threat profiles rather than pursuing horizontal platform strategies.
Product Type:
After-sales service intensity varies dramatically across product categories, with hardware-dependent segments requiring field engineering support while software segments rely on remote telemetry and subscription renewals.
- Firewalls:Packet inspection appliances process traffic at line rates exceeding 100 Gbps with sub-millisecond latency. Federal contractors in the United States are retrofitting legacy perimeter controls to meet CISA zero-trust mandates, driving replacement cycles despite semiconductor supply constraints from TSMC fabrication bottlenecks.
- Encryption Tools:Cryptographic key management and certificate authority systems command premium pricing in regulated verticals. Financial institutions across Germany, France, and Switzerland are accelerating procurement ahead of post-quantum cryptography standardization by NIST, creating inventory pre-positioning demand.
- Antivirus Software:Signature-based endpoint protection is consolidating into broader extended detection and response platforms with automated remediation.
- Intrusion Detection Systems:Network behavior analytics platforms are migrating from appliance form factors to cloud-native traffic mirroring architectures.
Firewalls hold the largest share; momentum sits with encryption tools.
Technology:
Technology selection correlates directly with customer IT modernization maturity, with cloud-native stacks displacing legacy on-premise implementations fastest among mid-market SaaS providers.
- Cloud Security:Multi-tenant access brokers and security service edge platforms deliver policy enforcement as metered subscriptions. Organizations retiring on-premise data centers in the United Kingdom, Netherlands, and Sweden are prioritizing cloud-native deployments over hybrid configurations despite mainframe integration complexity.
- Artificial Intelligence:Automated threat detection systems process endpoint telemetry through unified threat graphs. EU AI Act risk classification tiers are forcing vendors serving European enterprises to accelerate conformity assessments for high-risk deployments before procurement windows close.
- Biometrics:Behavioral and physiological authentication systems are expanding beyond consumer devices into workforce access management.
- Blockchain:Distributed ledger approaches to identity verification remain experimental outside cryptocurrency custody applications.
Cloud Security commands dominant procurement volume; Artificial Intelligence is climbing the fastest.
End User:
End-user verticals exhibit divergent compliance obligations and capital cycle timing, with government and healthcare procurement governed by mandatory disclosure rules while financial services operate under continuous examination frameworks.
- Government:Federal agencies and defense contractors are modernizing zero-trust architectures under binding CISA directives. Procurement is concentrating in the United States, with the Department of Defense and civilian agencies eliminating implicit trust from network perimeters through multi-year modernization programs.
- Healthcare:Connected medical devices and surgical robotics are extending digital security control requirements into hospital capital expenditure cycles. FDA cybersecurity guidance is forcing device manufacturers and health systems in the United States to integrate security controls into diagnostic equipment procurement.
- Financial Services:Banks and insurers are deploying AI-driven threat detection platforms with real-time transaction monitoring capabilities.
- Education:University and K-12 networks are adopting cloud-delivered security to protect distributed learning environments with limited on-site IT staffing.
Government represents the deepest procurement base; Healthcare is gaining share fastest.
Deployment:
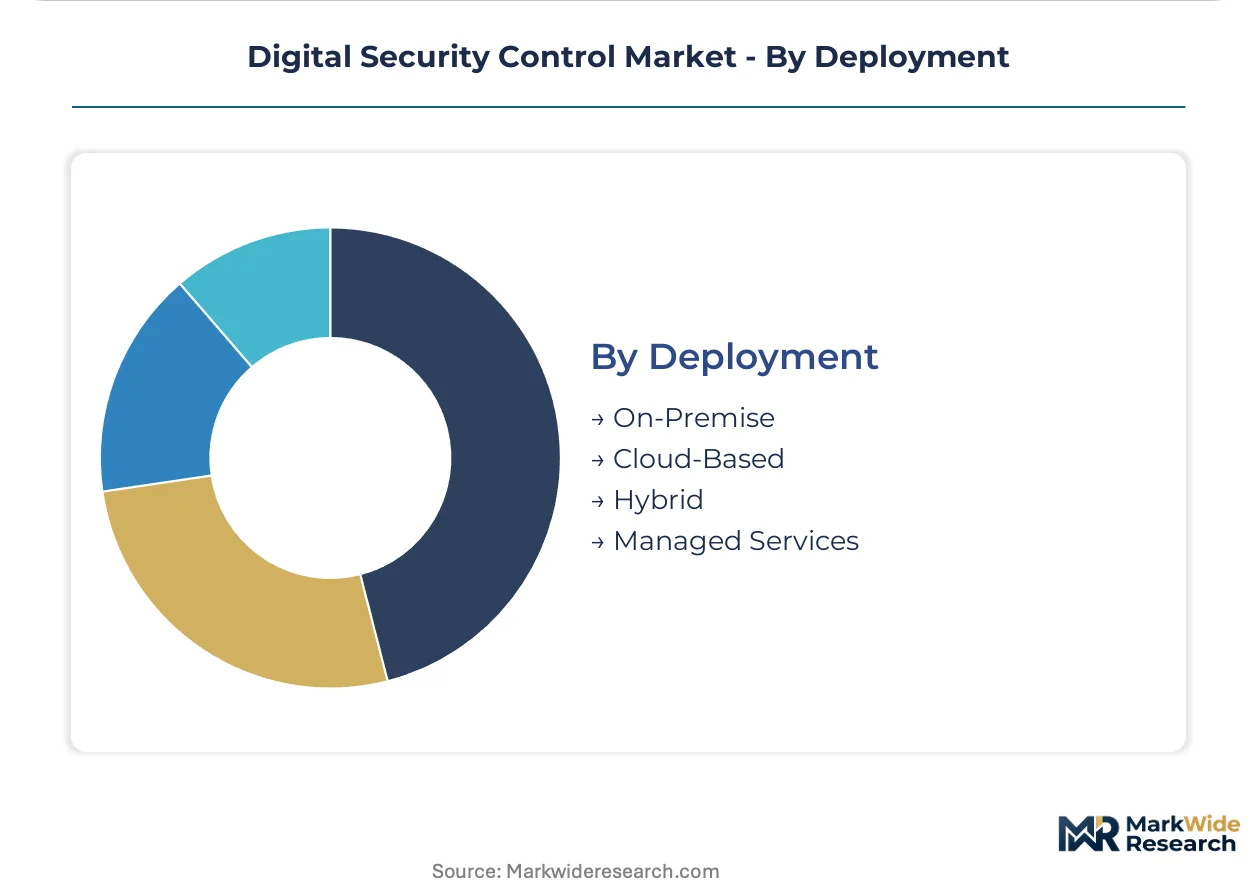
Deployment model selection reflects data sovereignty requirements and legacy infrastructure dependencies, with hybrid configurations retaining dominant share among enterprises with mainframe workloads.
- Hybrid:Split-control architectures route sensitive workloads through on-premise inspection while leveraging cloud scale for commodity traffic. Enterprises in Japan, Australia, and Canada with legacy IBM zSystems environments are maintaining hybrid deployments despite orchestration complexity, as zero-trust policy extension to transaction processing remains technically immature.
- Cloud-Based:Fully cloud-delivered security stacks eliminate hardware refresh cycles through consumption-based licensing. Mid-market SaaS providers across Singapore, Ireland, and the United Arab Emirates are replacing three-year firewall entitlements with month-to-month subscriptions aligned to actual event volume.
- On-Premise:Air-gapped and sovereign cloud deployments persist in classified and critical infrastructure environments with data localization mandates.
- Managed Services:Security operations center outsourcing is expanding among organizations facing certified security architect scarcity.
Hybrid retains the largest installed base; Cloud-Based is expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Israel exports cybersecurity platforms to defense contractors in the United States and financial institutions across Germany and Switzerland. This trade corridor channels specialized threat intelligence capabilities into Western procurement pipelines.
United States
Federal agencies and defense contractors drive demand through CISA zero-trust mandates and multi-year modernization programs. The SEC enforces mandatory disclosure rules for material cybersecurity incidents. Procurement concentrates in Northern Virginia's defense corridor and California's Silicon Valley, where cloud-native security stacks displace hardware refresh cycles.
Germany
Industrial manufacturers and automotive suppliers anchor demand for operational technology security convergence. The EU AI Act imposes conformity assessments on automated threat detection systems. Frankfurt's financial district and Munich's industrial cluster host the densest vendor deployment activity for encryption tools and certificate authority systems.
India
CERT-In directives and data localization requirements accelerate indigenous security operations center procurement. The RBI mandates cybersecurity frameworks for payment systems and digital banking infrastructure. Bengaluru's technology corridor and Mumbai's financial district dominate cloud security adoption among mid-market SaaS providers.
United Kingdom
Organizations retiring on-premise data centers prioritize cloud-native deployments over hybrid configurations. The National Cyber Security Centre publishes binding operational guidance for critical infrastructure protection. London's financial services cluster and Cambridge's technology hub lead metered-billing subscription adoption.
Japan
Enterprises with legacy IBM zSystems environments maintain hybrid deployments despite orchestration complexity. METI promotes secure digital infrastructure standards for Industry 4.0 transformation. Tokyo's corporate headquarters district and Osaka's manufacturing belt sustain firewall appliance procurement despite semiconductor supply constraints.
Digital Security Control Market Competitive Environment
Channel-controlling players compete with product-specialist players for enterprise procurement budgets. The vendor base clusters around three tiers: integrated platform providers, best-of-breed specialists, and regional system integrators. Platform providers leverage subscription telemetry to displace perpetual licensing. Specialists capture premium pricing in regulated verticals through certification depth. Consolidation pressures intensify as cloud-native delivery collapses traditional hardware refresh cycles.
Among platform-integrated providers, Palo Alto Networks, CrowdStrike, and Fortinet exemplify divergent architectural bets. Palo Alto Networks anchors multi-tenant cloud security through its Prisma portfolio. CrowdStrike occupies a position defined by endpoint telemetry feeding unified threat graphs. Fortinet represents integrated networking-security convergence at manufacturing scale. These three entities collectively illustrate how subscription economics and zero-trust mandates reshape competitive positioning across federal, financial, and industrial customer bases.
| Leading Market Players |
|---|
| Cisco Systems, Inc. |
| Fortinet, Inc. |
| Palo Alto Networks |
| Microsoft |
| McAfee, LLC |
| Check Point Software Technologies Ltd. |
| IBM Corporation |
| Trend Micro, Inc. |
| CrowdStrike |
| Others |
Value Chain & Pricing Dynamics
Trans-Pacific freight corridors from Taiwan and South Korea to Long Beach and Rotterdam anchor cost dynamics for firewall appliance manufacturers, where container rate volatility amplifies pricing power for semiconductor-dependent hardware tiers while subscription-based cloud security platforms decouple from physical logistics entirely.
Pricing Analysis
Next-generation confidential computing enclaves command substantial premiums over legacy encryption-at-rest solutions, while prior-generation packet inspection appliances face accelerating price erosion. Three-tier pricing structure across premium, standard, and economy levels separates FedRAMP-authorized federal deployments from mid-market SaaS subscriptions and basic perimeter controls. Pricing pressure stems from consumption-based licensing displacing perpetual entitlements, with certified security architects scarce and implementation costs rising. Federal contractors exhibit lowest price sensitivity due to binding CISA mandates; mid-market SaaS providers show highest elasticity, preferring metered billing aligned to actual event volume.
Supply Chain Analysis
TSMC in Taiwan and Samsung Foundry in South Korea hold dominant fabrication capacity for advanced packet inspection ASICs and cryptographic processors. Raw material dependencies center on silicon wafers, rare earth elements for magnetics, and specialized substrates for high-frequency signal processing. Single-source vulnerability concentrates in Taiwan Strait geopolitical friction, where inventory pre-positioning cannot fully offset fabrication bottlenecks. Distribution runs through authorized value-added resellers serving defense contractors, direct enterprise sales for cloud-native platforms, and systems integrators managing hybrid deployments.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Zero-trust architecture mandates across federal agencies and defense contractors signal early-cycle expansion, with penetration rates for cloud-native security stacks still below saturation among enterprises with legacy mainframe dependencies.
For Market Incumbents: Build switching-cost moats through unified threat graph telemetry that deepens customer data gravity. Fortify certification depth for EU AI Act high-risk system conformity assessments before procurement windows narrow. Extend orchestration capabilities into operational technology environments where IT-OT convergence creates defensive bundling opportunities against pure-play cloud entrants. For New Entrants and Emerging Players: Establish a beachhead in India's indigenous security operations center market where CERT-In directives and data localization requirements outpace incumbent response capacity. Target healthcare sub-markets where FDA cybersecurity guidance for connected medical devices extends procurement cycles beyond traditional IT refresh timelines. Lead with managed detection and response services that bypass capital-intensive hardware manufacturing entirely. For Investors and Strategic Acquirers: Specialist AI governance documentation vendors serving EU critical infrastructure operators represent priority acquisition archetypes as conformity assessment bottlenecks intensify. Long-term viability hinges on post-quantum cryptography transition readiness across financial services and government certificate authority refreshes. Watch NIST algorithm standardization announcements as inflection indicators for encryption tool replacement velocity.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies endpoint, cloud, and OT telemetry through Prisma and Falcon architectures for federal contractors. |
| Certification Investment | Accelerates EU AI Act conformity assessments for high-risk automated threat detection systems before deadlines. |
| Strategic Partnership | Aligns systems integrators with hybrid deployment complexity for IBM zSystems mainframe environments. |
| Geographic Expansion | Captures India CERT-In directive procurement for sovereign cloud and indigenous SOC deployments. |
| Acquisition of Specialist Firm | Consolidates OT security visibility platforms for energy and manufacturing IT-OT convergence budgets. |
Study Parameters
Initial hypotheses were tested against primary input from CISOs at federal agencies and defense contractors, cloud security architects at financial institutions, and procurement officers at health systems, then refined through secondary validation against SEC cybersecurity disclosure filings, CISA zero-trust implementation guidance, FDA medical device cybersecurity premarket submissions, and EU AI Act conformity assessment documentation. Bottom-up deployment volume estimates across product types, technologies, and end-user verticals were triangulated with top-down addressable market sizing.
Demand-supply-balance framing anchored the analytical framework across the analysis window, modeling procurement velocity from government modernization programs against semiconductor fabrication capacity constraints and certified security architect labor pools. Segmentation dimensions included deployment model, organization size, compliance regime complexity, and legacy infrastructure dependency. CAGRs were derived from deployment curve penetration rates and replacement cycle compression, incorporating post-quantum cryptography transition timelines and confidential computing hardware refresh patterns as industry-specific inputs.
Stress conditions across Taiwan Strait geopolitical friction, EU AI Act enforcement variance, and zero-trust mandate implementation pace were modeled; outcomes outside those bands fall beyond the analytical envelope. Forecasts reflect documented assumptions regarding subscription displacement rates and hybrid deployment persistence. Cross-checking against CISA binding operational directive release schedules and NIST post-quantum algorithm standardization milestones is advised before commitment-grade decisions.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Access Control Systems
Australia Industrial Barrier Systems Market
Access Control Systems
North America Safety Systems Market
Access Control Systems
China Access Control Market
Access Control Systems
Germany Access Control Market
Access Control Systems
Mechanical Locks Market
Access Control Systems
Latin America Proximity Access Control Market
Access Control Systems
Global Industrial Safety Gates Market
Access Control Systems
India Access Control Hardware Market
Access Control Systems
Network Access Control Market
Access Control Systems
Global Keyless Vehicle Access Control Systems Market
Access Control Systems
North America Proximity Access Control Market
Access Control Systems
Global Fingerprint Access Control Systems Market
Access Control Systems
Border Security System Market
Access Control Systems
Mode Locking Device Market
Access Control Systems
Europe Pin-Based Access Control Market
Access Control Systems
Bluetooth Smart Lock Market