
 Public Key Infrastructure (PKI) Market | 2026-2036
Public Key Infrastructure (PKI) Market Size, Share, and Industry Trends Forecast 2026-2036
Public Key Infrastructure (PKI) Market Analysis
The EU AI Act is recalibrating compliance costs for automated identity systems across European enterprises. DigiCert leverages its certificate authority network to anchor high-assurance provisioning for regulated industries. Thales Group specializes in hardware security module integration, sustaining competitive differentiation through physical root-of-trust architectures. Entrust controls government credentialing pipelines, dominating federal and defense-grade PKI deployments in North America.
Public Key Infrastructure constitutes a trust framework built on asymmetric cryptography, where certificate authorities bind public keys to identities through X.509 digital certificates and maintain revocation status via OCSP responders or CRL distributions. Its primary purpose is to enable confidential communication, authenticated access, and non-repudiable transactions across networked systems without pre-shared secrets. Cloud-based deployment is capturing the fastest expansion as organizations abandon capital-intensive on-premises certificate management for elastic, API-driven services. Hardware security modules retain the deepest margin pools due to tamper-resistant silicon requirements and FIPS 140-2 Level 3 certification barriers that limit supplier entry.
NIST post-quantum cryptography standards and the EU Cybersecurity Act reshape product roadmaps, forcing vendors to retrofit algorithms and re-certify trust anchors. FDA 21 CFR Part 11 in healthcare and ETSI eIDAS frameworks in Europe mandate qualified electronic signatures, directly stimulating certificate volume demand. Stakeholders must decide whether to absorb quantum-safe migration costs incrementally or defer and risk forced infrastructure replacement under accelerated compliance deadlines.
Market Dynamics
NIST post-quantum cryptography mandates and the EU Cybersecurity Act are forcing infrastructure vendors to re-architect certificate authorities around algorithmic resilience, compressing traditional five-year product cycles into accelerated retrofit timelines.
Growth Catalysts
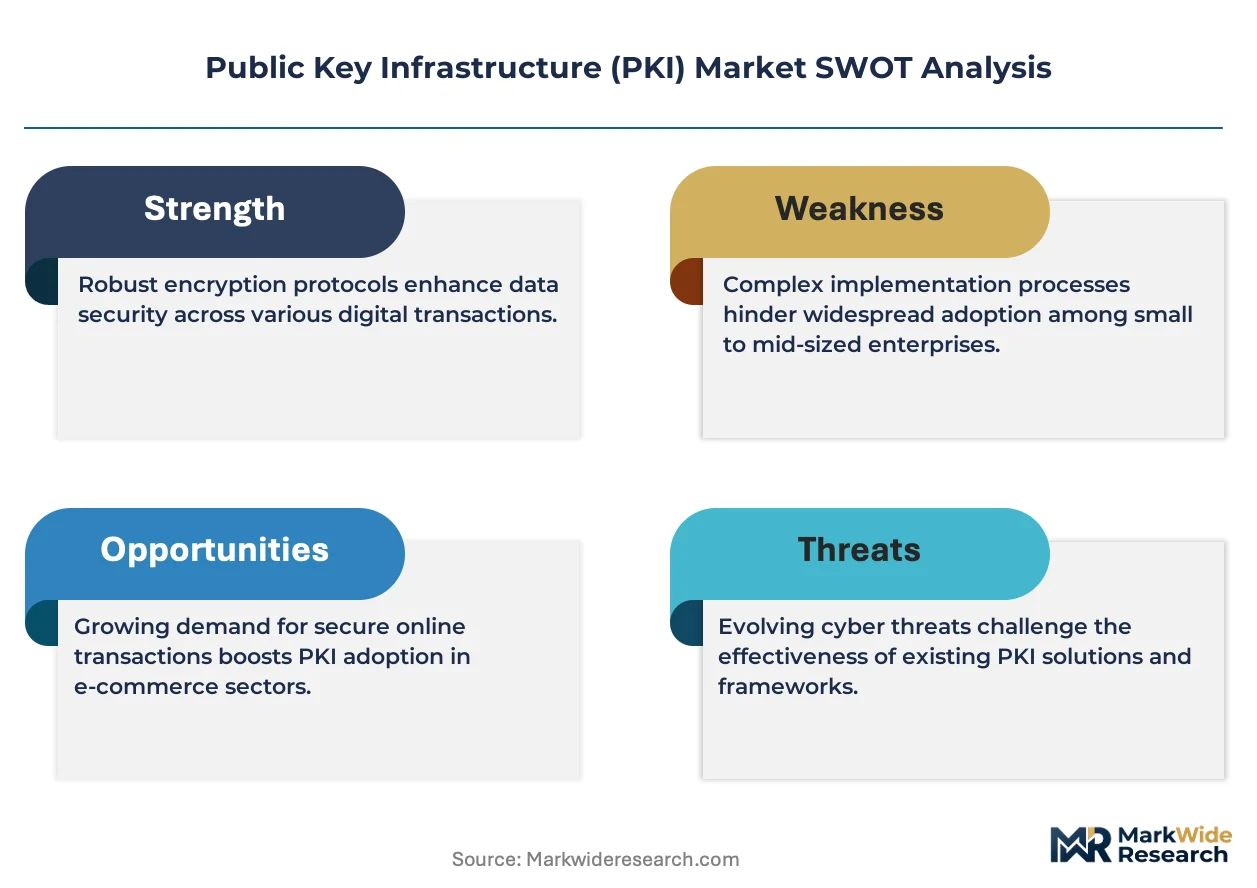
- ETSI eIDAS Framework:Qualified electronic signature mandates across European member states are expanding certificate volume demand for cross-border digital identity verification.
- Financial Services Digitization:Real-time payment networks and open banking APIs require automated certificate lifecycle management to secure high-velocity transaction flows.
- Cloud Migration:Elastic, API-driven PKI services are displacing capital-intensive on-premises hardware deployments in Germany, Japan, and the United States.
Market Restraints
- FIPS 140-2 Level 3 Certification Barriers:Tamper-resistant hardware security module requirements limit supplier entry and sustain premium pricing for qualified vendors.
- Quantum-Safe Migration Costs:Algorithm retrofitting and trust anchor re-certification impose substantial capital burdens without immediate revenue offset.
- Legacy System Interoperability:Decades-old certificate management infrastructure resists API-driven automation, constraining cloud adoption velocity.
Strategic Opportunities
- Healthcare Digital Identity:FDA 21 CFR Part 11 compliance requirements for electronic records create qualified signature demand in clinical trial and pharmaceutical manufacturing workflows.
- IoT Device Authentication:Machine-to-machine certificate provisioning at manufacturing scale opens high-volume, low-margin service models for industrial automation vendors.
- Post-Quantum Readiness Services:Cryptographic inventory assessment and hybrid certificate deployment offer consultative revenue streams ahead of NIST enforcement deadlines.
Industry Challenges
- Specialized Cryptographic Engineering Talent:Shortage of practitioners versed in both classical PKI operations and lattice-based post-quantum algorithms constrains vendor roadmap execution.
- Multi-Jurisdiction Compliance Complexity:Simultaneous adherence to eIDAS, NIST SP 800-63, and sector-specific frameworks fragments product architecture and documentation overhead.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Public Key Infrastructure (PKI) Market |
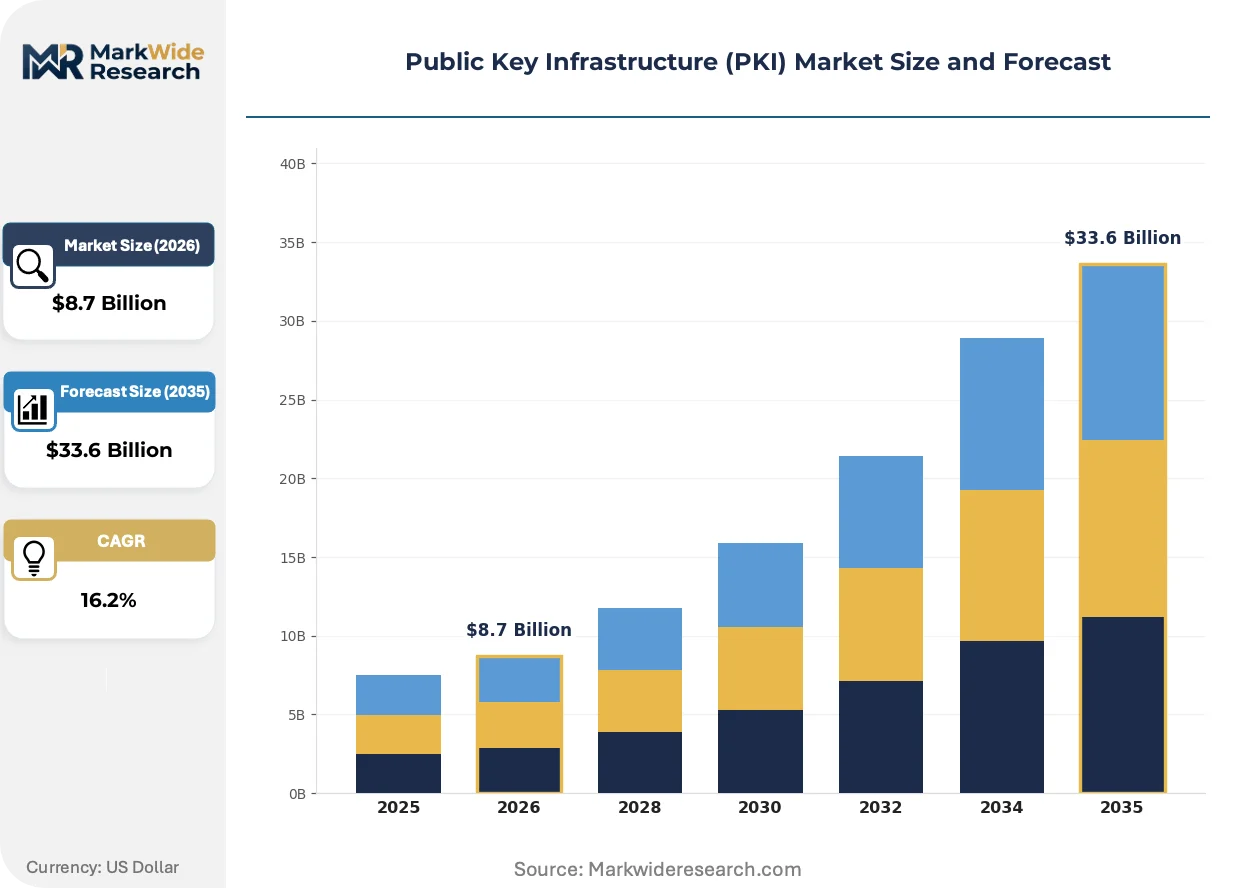
| Market Size in 2026 | $8.7 Billion |
| Market Size in 2035 | $33.6 Billion |
| CAGR (2026 – 2036) | 16.2% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Deployment: On-Premises, Cloud-Based, Hybrid, Managed Services Industry Vertical: Government, Healthcare, Finance, Telecommunications Offering: Certificates, Key Management, Hardware Security Modules, Digital Signature Solutions End User: Enterprises, SMEs, Service Providers, Individual Consumers |
| Companies Covered | DigiCert, Entrust, Thales Group, Keyfactor, Sectigo, IBM, Microsoft, HID Global, Futurex, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Public Key Infrastructure (PKI) Market Emerging Trajectories
Automated certificate lifecycle management is compressing operational overhead while post-quantum algorithm standardization reshapes trust anchor architectures. Vendor roadmaps now prioritize cryptographic agility over static algorithm commitments.
Hardware security modules with hybrid classical-quantum support are consolidating high-assurance key protection for financial clearing systems and government credentialing pipelines. Tier-one banks in the United States and EU member state tax authorities are deploying these systems ahead of NIST's 2035 deprecation timeline for RSA and elliptic curve algorithms. This consolidation is compressing the addressable market for software-only key management vendors.
The EU AI Act imposes transparency and auditability requirements on automated identity verification systems, forcing PKI vendors to embed certificate-based provenance logging into AI training data pipelines. Healthcare and financial services deployments face the steepest compliance recalibration. German automotive manufacturers are responding by mandating qualified timestamping for all training set metadata.
Certificate consumption is fragmenting from enterprise-wide annual procurement toward DevOps-integrated, API-driven micro-purchases. Platform engineering teams now provision short-lived certificates through infrastructure-as-code workflows, displacing centralized IT security gatekeeping. This pattern is most visible in United States technology sector deployments and spreading to Japanese industrial conglomerates modernizing operational technology networks.
Public Key Infrastructure (PKI) Market Segmentation
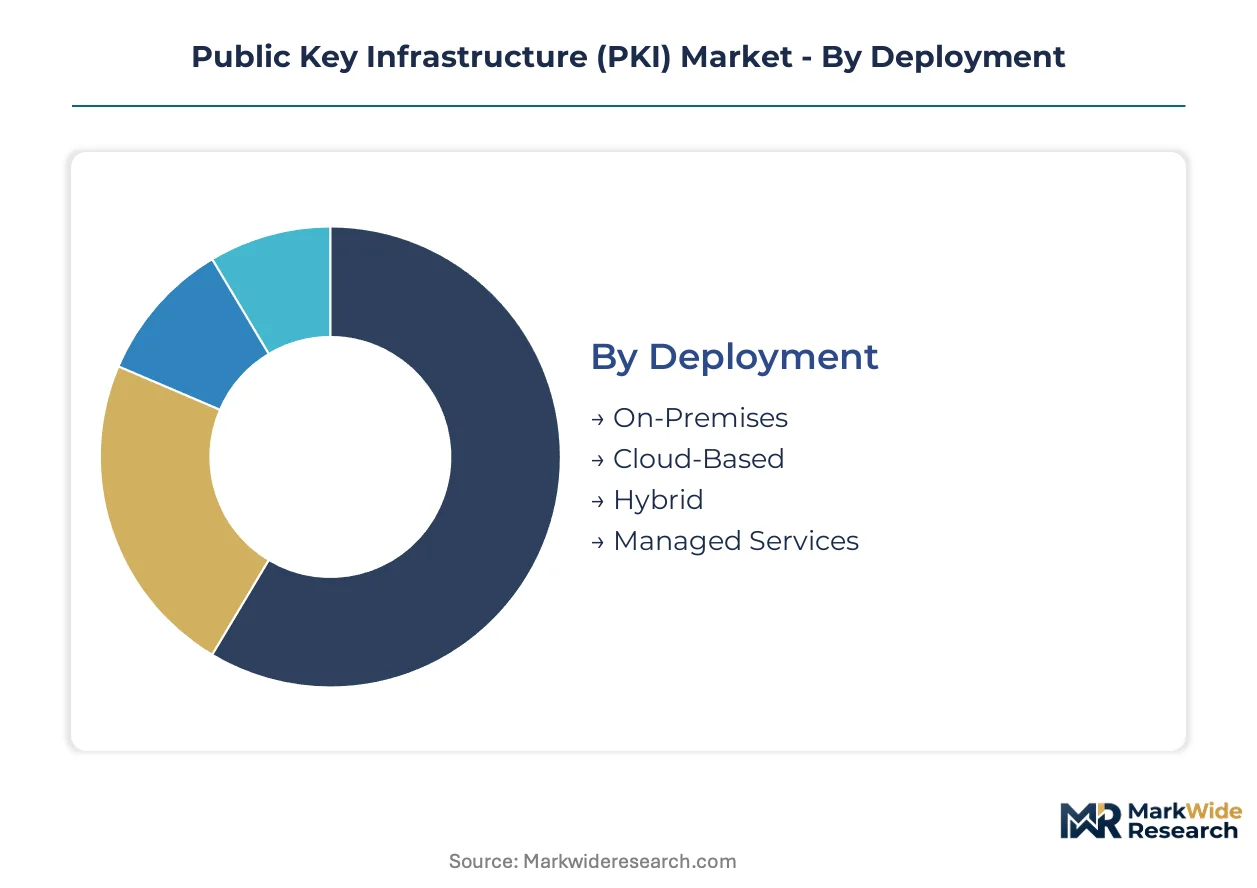
PKI procurement patterns diverge sharply across deployment architectures and customer scale, with cloud migration cycles and post-quantum retrofit timelines driving segment-specific upgrade decisions. Certificate lifecycle automation and hardware root-of-trust requirements create distinct margin pools that reshape vendor prioritization.
Deployment:
Upgrade cycles compress from five-year hardware refresh schedules to elastic cloud provisioning as NIST post-quantum mandates force algorithmic re-architecture across all architectures.
- On-Premises:Self-managed certificate authorities operating within enterprise data centers retain dominance in defense and classified government networks where air-gapped operation is mandatory. Demand concentrates in United States federal agencies and German automotive manufacturers facing ETSI eIDAS qualified signature mandates; FIPS 140-2 Level 3 hardware requirements sustain premium pricing despite cloud migration pressure.
- Cloud-Based:API-driven certificate provisioning through multi-tenant SaaS platforms eliminates capital expenditure for certificate lifecycle management. Japanese industrial conglomerates and United States technology sector firms are displacing on-premises hardware fastest here; elastic scaling aligns with DevOps-integrated micro-purchase patterns.
- Hybrid:Split architectures anchor root certificate authorities on-premises while distributing issuance workloads to cloud infrastructure. Financial services firms in Germany and Japan deploy hybrid models to satisfy data residency requirements while gaining operational flexibility.
- Managed Services:Outsourced PKI operations where third-party providers assume full certificate authority administration and compliance documentation. SMEs without cryptographic engineering talent favor this model to absorb quantum-safe migration costs.
Volume placements concentrate in On-Premises; the faster expansion belongs to Cloud-Based.
Industry Vertical:
Regulatory mandate density determines vertical penetration rates, with qualified electronic signature requirements and post-quantum deadlines creating divergent cost absorption timelines.
- Government:Federal credentialing pipelines and citizen identity systems require FIPS 140-2 Level 3 hardware security modules and ETSI eIDAS qualified trust service compliance. United States federal deployments and EU member state tax authorities are accelerating hybrid classical-quantum HSM procurement ahead of algorithm deprecation deadlines.
- Finance:Real-time payment networks and open banking APIs demand automated certificate lifecycle management for high-velocity transaction security. German banks and United States clearing systems face the steepest compliance recalibration under simultaneous NIST and EU Cybersecurity Act pressures.
- Healthcare:FDA 21 CFR Part 11 mandates qualified electronic signatures for clinical trial documentation and pharmaceutical manufacturing workflows. Certificate volume demand is climbing fastest here as digital identity requirements spread from research to operational systems.
- Telecommunications:Subscriber identity protection and network equipment authentication at manufacturing scale drive machine-to-machine certificate provisioning. 5G network rollouts in Japan and Germany are expanding device certificate volumes.
Government captures the deepest margin pools; Healthcare is climbing the fastest.
Offering:
Product architecture separates commodity certificate issuance from high-assurance hardware where tamper-resistant silicon creates certification barriers limiting supplier entry.
- Certificates:X.509 digital credentials binding public keys to identities, issued in durations from short-lived DevOps certificates to multi-year qualified signatures. Volume demand is fragmenting toward API-driven micro-purchases as platform engineering teams displace centralized IT security gatekeeping.
- Hardware Security Modules:Tamper-resistant silicon appliances protecting cryptographic key material with FIPS 140-2 Level 3 certification. Tier-one United States banks and EU tax authorities are consolidating procurement ahead of post-quantum retrofit requirements.
- Key Management:Software and appliance-based systems for cryptographic key generation, distribution, and lifecycle control. Cloud migration is displacing on-premises key management fastest in German and Japanese enterprise deployments.
- Digital Signature Solutions:End-user applications and middleware enabling qualified electronic signature creation and verification. ETSI eIDAS framework expansion across European member states is stimulating cross-border demand.
Hardware Security Modules command premium pricing; Certificates are gaining share fastest.
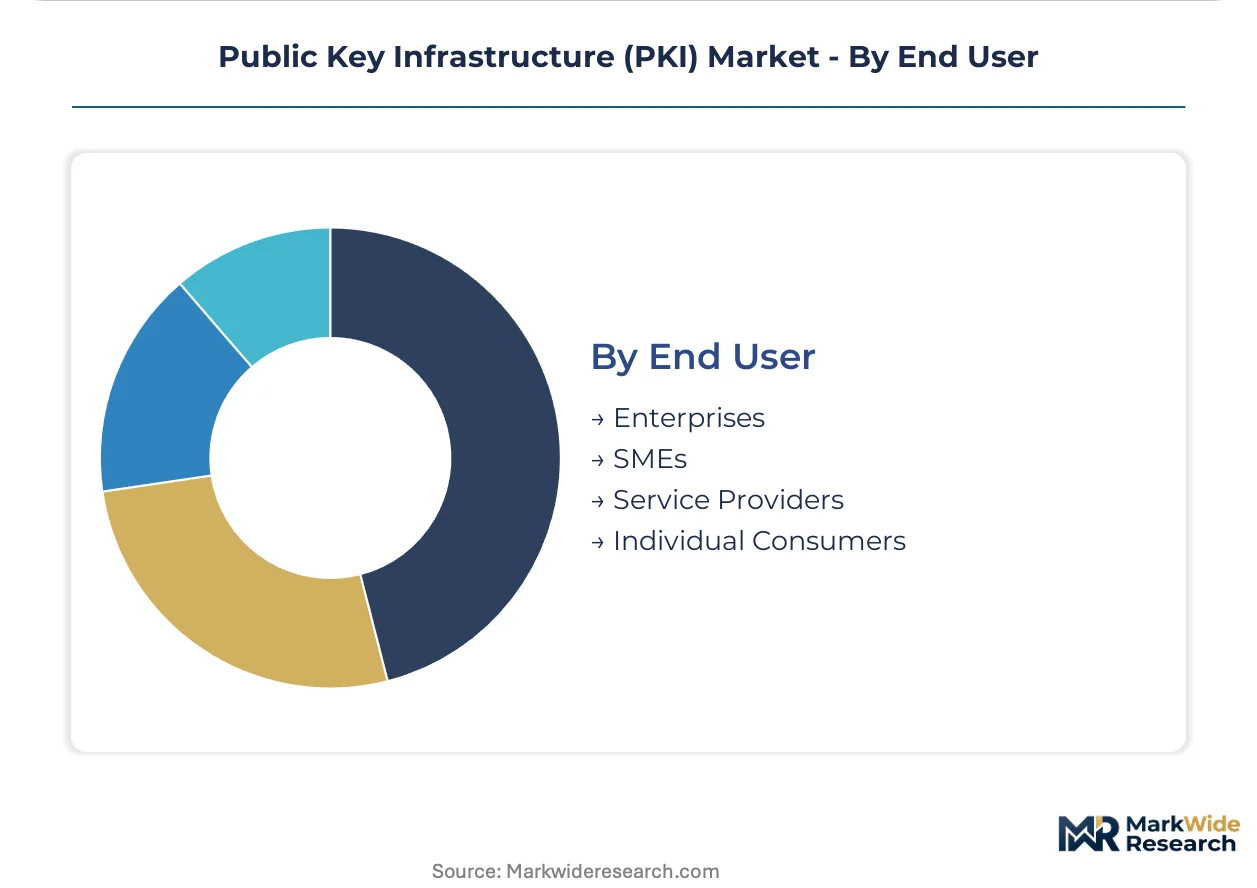
End User:
Customer scale determines procurement sophistication, with enterprises absorbing quantum-safe migration costs incrementally while SMEs defer and risk forced replacement.
- Enterprises:Large organizations with dedicated cryptographic engineering teams and compliance documentation infrastructure. United States technology sector firms and German automotive manufacturers are deploying automated certificate lifecycle management across operational technology networks.
- SMEs:Mid-sized organizations lacking in-house PKI expertise, increasingly outsourcing to managed services. Japanese industrial suppliers are adopting cloud-based certificate provisioning to avoid capital-intensive hardware procurement.
- Service Providers:Telecommunications carriers, cloud platforms, and trust service providers issuing certificates to downstream customers. These intermediaries face multi-jurisdiction compliance complexity across eIDAS, NIST SP 800-63, and sector-specific frameworks.
- Individual Consumers:End-users obtaining qualified electronic signatures for tax filing, contract execution, and identity verification. EU member state digital identity programs are expanding this segment through qualified signature mandates.
Enterprises dominate current spending; Service Providers are expanding most quickly.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
Germany's Industrie 4.0 tax incentives and Japan's J-Startup visa programs are concentrating PKI infrastructure investment in specialized economic zones. These zones attract cryptographic engineering talent and hardware security module manufacturing. Certificate authority operations cluster near regulatory hubs to accelerate compliance certification.
United States
Federal credentialing pipelines and real-time payment networks drive hardware security module procurement. NIST post-quantum cryptography mandates compress product refresh cycles for defense contractors. Tier-one banks in New York and federal agencies in Washington D.C. deploy hybrid classical-quantum systems ahead of algorithm deprecation deadlines.
Germany
ETSI eIDAS qualified signature mandates expand certificate volume for automotive and industrial automation. The EU Cybersecurity Act forces trust service providers to re-certify cryptographic modules. Bavarian automotive manufacturers and Frankfurt financial clearinghouses anchor European demand for high-assurance provisioning.
Japan
5G network rollouts and operational technology modernization stimulate machine-to-machine certificate provisioning. METI industrial cybersecurity guidelines mandate cryptographic inventory assessment for critical infrastructure. Tokyo-based telecommunications carriers and Nagoya industrial conglomerates lead cloud-based PKI migration.
United Kingdom
Open banking API security requirements and digital identity program expansion drive automated certificate lifecycle management. Post-Brexit regulatory divergence from eIDAS creates dual compliance burden for trust service providers. London financial services firms and Cambridge cybersecurity clusters absorb quantum-safe migration costs incrementally.
India
Digital India initiative and UIDAI Aadhaar ecosystem expansion create qualified electronic signature demand for government services. RBI guidelines for payment system operators mandate hardware security module deployment. Bangalore technology parks and Mumbai financial districts concentrate certificate authority outsourcing contracts.
Public Key Infrastructure (PKI) Market Vendor Landscape
United States producers anchor the certificate authority tier; European specialists hold hardware security module integration. The market exhibits consolidated leadership in high-assurance provisioning alongside fragmented competition in cloud-based lifecycle management. Three archetypes dominate: full-stack trust service providers, hardware-rooted security vendors, and API-native certificate automation platforms. Competitive moves center on post-quantum algorithm licensing partnerships and managed services portfolio expansion.
Within the full-stack tier, DigiCert and Entrust exemplify integrated certificate authority and identity provisioning capabilities. Thales Group anchors the hardware-rooted segment through physical root-of-trust architectures. These three occupy positions spanning government credentialing, financial services clearing, and regulated industry compliance pipelines.
| Leading Market Players |
|---|
| DigiCert |
| Entrust |
| Thales Group |
| Keyfactor |
| Sectigo |
| IBM |
| Microsoft |
| HID Global |
| Futurex |
| Others |
Supply Flow & Price Mechanics
Private-equity-rolled-up certificate automation specialists have consolidated procurement leverage across cloud-based PKI services, compressing margins for standalone software vendors while sustaining premium pricing for FIPS 140-2 Level 3 hardware security modules anchored in sovereign-backed production facilities.
Pricing Analysis
Short lead-time premiums for post-quantum-ready hardware security modules command substantial markups over standard inventory, with three-tier pricing structure across premium, standard, and economy levels differentiating by FIPS certification grade and algorithm agility. Subscription-based SaaS tiers for certificate lifecycle management face downward pressure from API-native entrants, while defense-grade HSM procurement shows minimal price sensitivity due to NIST-mandated compliance deadlines.
Supply Chain Analysis
FIPS 140-2 Level 3 certification gates concentrate qualified hardware security module production in the United States, Germany, and Japan, with tamper-resistant silicon fabrication drawing from specialized foundry capacity in Taiwan and South Korea. Single-source vulnerability in cryptographic processor supply creates exposure to export control restrictions, while distribution runs through authorized security equipment resellers and direct government contracting channels.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
The Public Key Infrastructure market sits in a technology-transition phase as lattice-based post-quantum algorithms displace RSA and elliptic curve cryptography across trust anchor architectures.
For Market Incumbents: Anticipate accelerated product obsolescence by pre-integrating hybrid classical-quantum certificate issuance into existing certificate authority infrastructure. Consolidate cryptographic engineering talent through targeted acquisition in Germany and Japan, where ETSI eIDAS and METI guidelines concentrate qualified expertise. Defend margin pools in hardware security modules by securing early NIST post-quantum algorithm certifications ahead of 2035 deprecation timelines. For New Entrants and Emerging Players: The premium-to-economy pricing gap in managed PKI services for SMEs offers white-space entry through API-native certificate automation without legacy on-premises baggage. Target Japanese industrial suppliers and mid-tier German automotive component manufacturers seeking to avoid capital-intensive HSM procurement. Pursue consultative post-quantum readiness assessments as a beachhead into enterprise accounts facing NIST compliance uncertainty. For Investors and Strategic Acquirers: Distressed-cycle entries favor cloud-native certificate automation platforms with recurring revenue bases in the United States and Germany, where quantum-safe migration costs strain SME budgets. Long-term viability hinges on cryptographic agility rather than static algorithm commitments. Watch NIST post-quantum standard finalization as the inflection trigger for accelerated infrastructure replacement spending.| Strategic Initiative | Industry Significance |
|---|---|
| Post-Quantum Algorithm Licensing Partnership | Secures NIST-compliant cryptographic modules for federal and financial clearing pipelines. |
| Managed Services Portfolio Expansion | Captures SME demand for outsourced certificate lifecycle management amid talent scarcity. |
| Hybrid HSM-Cloud Architecture Deployment | Balances data residency requirements with operational flexibility for German and Japanese enterprises. |
| Certificate Lifecycle Automation Platform Launch | Displaces centralized IT gatekeeping through DevOps-integrated API provisioning. |
| Healthcare Digital Identity Vertical Integration | Addresses FDA 21 CFR Part 11 qualified signature demand in clinical trial workflows. |
Methodological Framework
Document review covered NIST post-quantum cryptography standards, ETSI eIDAS implementation guidelines, and FDA 21 CFR Part 11 compliance documentation, complemented by interviews with chief information security officers at tier-one banks, cryptographic engineering leads at certificate authorities, federal procurement officers, and trust service provider executives. Secondary validation drew from SEC filings of publicly traded security vendors, FIPS 140-2 certification databases, and EU Cybersecurity Act regulatory notices. Bottom-up certificate volume estimates triangulated against top-down infrastructure spending projections.
Market sizing outputs reflect deployment model penetration curves, vertical regulatory mandate density, and hardware security module refresh cycles across the analysis window. Segmentation modeling incorporated certificate duration tiers, FIPS certification levels, organization scale, and geographic compliance framework clusters. CAGRs derived from algorithmic retrofit timelines and cloud migration velocity assumptions, with post-quantum readiness service revenue treated as a discrete emerging category.
Underlying measurement precision varies by segment; hardware security module unit placements carry tighter precision than emerging post-quantum consulting revenue. Forecasts reflect assumptions regarding NIST enforcement timing and EU Cybersecurity Act implementation pace. A model refresh is warranted upon material change in post-quantum algorithm standardization or accelerated deprecation timelines for classical cryptography.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Security Software
Certificate Authority Market
Security Software
Italy Endpoint Detection and Response Market
Security Software
Broadcast Censorship Solutions Market
Security Software
Asia-Pacific Fraud Detection & Prevention Market
Security Software
Employee Computer Monitoring Software Market
Security Software
US Evidence Management Market
Security Software
Latin America Fraud Detection and Prevention Market
Security Software
Application Control Market
Security Software
Software Assurance Market
Security Software
Europe IP Video Intercom Device and Equipment Market
Security Software
Secaas Market
Security Software
Global Cloud IAM Market
Security Software
North America Secure Access Service Edge Market
Security Software
Global Consumer Identity and Access Management Market
Security Software
AI in Security Market
Security Software
Banking Encryption Software Market