
 Continuous Threat Exposure Management Market | 2026-2036
Continuous Threat Exposure Management Market Size, Share, and Industry Trends Forecast 2026-2036
Continuous Threat Exposure Management Market Insights
Market Context
The capability gap between cloud-native specialists and legacy platform vendors is rotating competitive capital allocation toward automated validation architectures. Palo Alto Networks leverages its platform consolidation strategy to extend control over enterprise security budgets. Tenable sustains technology leadership in vulnerability intelligence through deep instrumentation of hybrid infrastructure. Rapid7 specializes in managed detection and response services that anchor recurring revenue relationships with mid-market buyers.
Technical Definition and Segment Structure
Continuous Threat Exposure Management comprises programmatic processes that discover, prioritize, and validate security control effectiveness against simulated adversary techniques across cloud, on-premises, and hybrid environments, typically operating through agentless network scanning, breach and attack simulation, and real-time posture scoring against frameworks such as MITRE ATT&CK. Cloud-based deployment modes are capturing the fastest expansion as enterprises abandon capital-intensive on-premises security stacks for elastic consumption models. Banking institutions represent the most concentrated end-user margin pool due to stringent operational resilience mandates and dedicated cybersecurity budgets, while public sector agencies are emerging as a structurally important demand segment through dedicated procurement frameworks for critical infrastructure protection.
Regulatory Framework and Outlook
The EU AI Act, NIS2 Directive, and GDPR collectively reshape product requirements by mandating automated security testing for high-risk digital infrastructure and imposing substantial penalties for inadequate exposure management. The US SEC cyber disclosure rules and HIPAA security evaluation standards similarly compel regulated entities to adopt continuous validation rather than point-in-time assessment methodologies. Stakeholders must monitor how converging compliance timelines across multiple jurisdictions will compress vendor selection cycles and favor integrated platforms over point solutions.
Market Dynamics
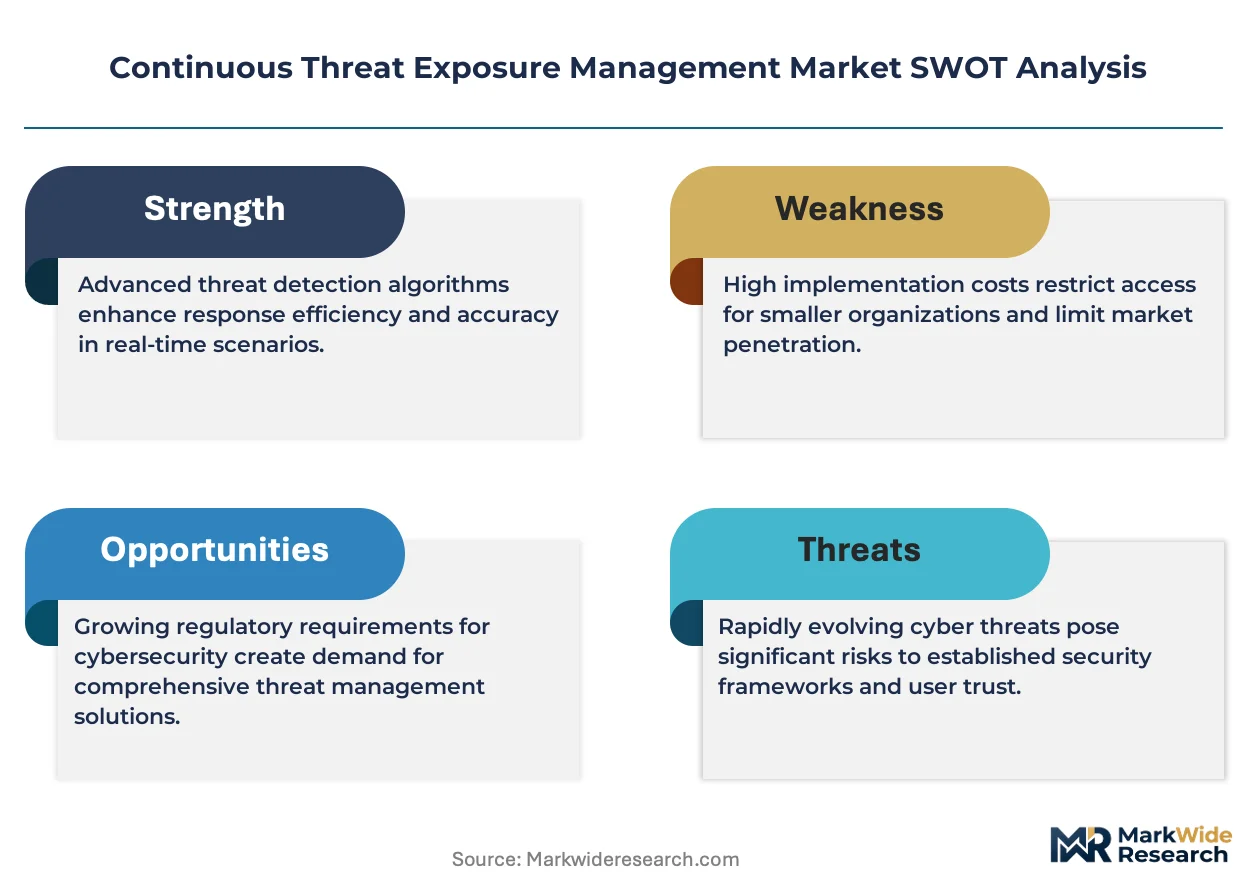
Automated adversary simulation is compressing enterprise security assessment cycles from quarterly point-in-time audits to continuous validation loops, forcing vendors to rearchitect delivery models around real-time telemetry rather than scheduled scanning windows.
Growth Catalysts
- EU NIS2 Directive:The directive mandates continuous security monitoring for essential and important entities, compelling regulated operators to replace periodic penetration testing with persistent exposure validation.
- Cloud-native workload expansion:Containerized and serverless architectures generate ephemeral attack surfaces that static vulnerability management cannot track, driving demand for agentless discovery and dynamic prioritization.
- Financial services operational resilience mandates:Banking regulators in Germany, the United Kingdom, and Singapore now require demonstrable control effectiveness testing, concentrating procurement authority among institutions with dedicated cyber budgets.
Market Restraints
- Skills scarcity in purple team functions:The shortage of practitioners capable of interpreting adversary simulation output and translating findings into remediation workflows limits deployment velocity at mid-market buyers.
- On-premises sunk cost entrenchment:Enterprises with heavy investments in legacy vulnerability scanners face integration friction and budget allocation conflicts when evaluating cloud-native CTEM platforms.
- Alert fatigue from overlapping tools:Security operations centers already managing fragmented detection stacks resist adding exposure management layers without guaranteed reduction in mean-time-to-remediate metrics.
Strategic Opportunities
- Operational technology convergence:Industrial control systems and critical infrastructure operators represent an underpenetrated segment where IT/OT network unification creates demand for unified exposure visibility.
- MITRE ATT&CK framework commercialization:Vendors embedding automated mapping to adversary tactics and techniques can differentiate through measurable risk reduction tied to recognized security architecture standards.
- Managed validation services for mid-market:Fractional access to continuous threat exposure expertise through subscription delivery models addresses capability gaps without requiring full-time specialist hiring.
Industry Challenges
- Legacy SIEM integration complexity:Correlating exposure intelligence with existing security information and event management workflows demands custom connector development and sustained engineering partnership.
- False positive management at scale:Automated validation tools generate voluminous findings that require contextual business risk scoring to prevent operational teams from ignoring critical alerts amid noise.
Report Scope
MarkWide Research| Attributes | Details |
|---|---|
| Report Title | Continuous Threat Exposure Management Market |
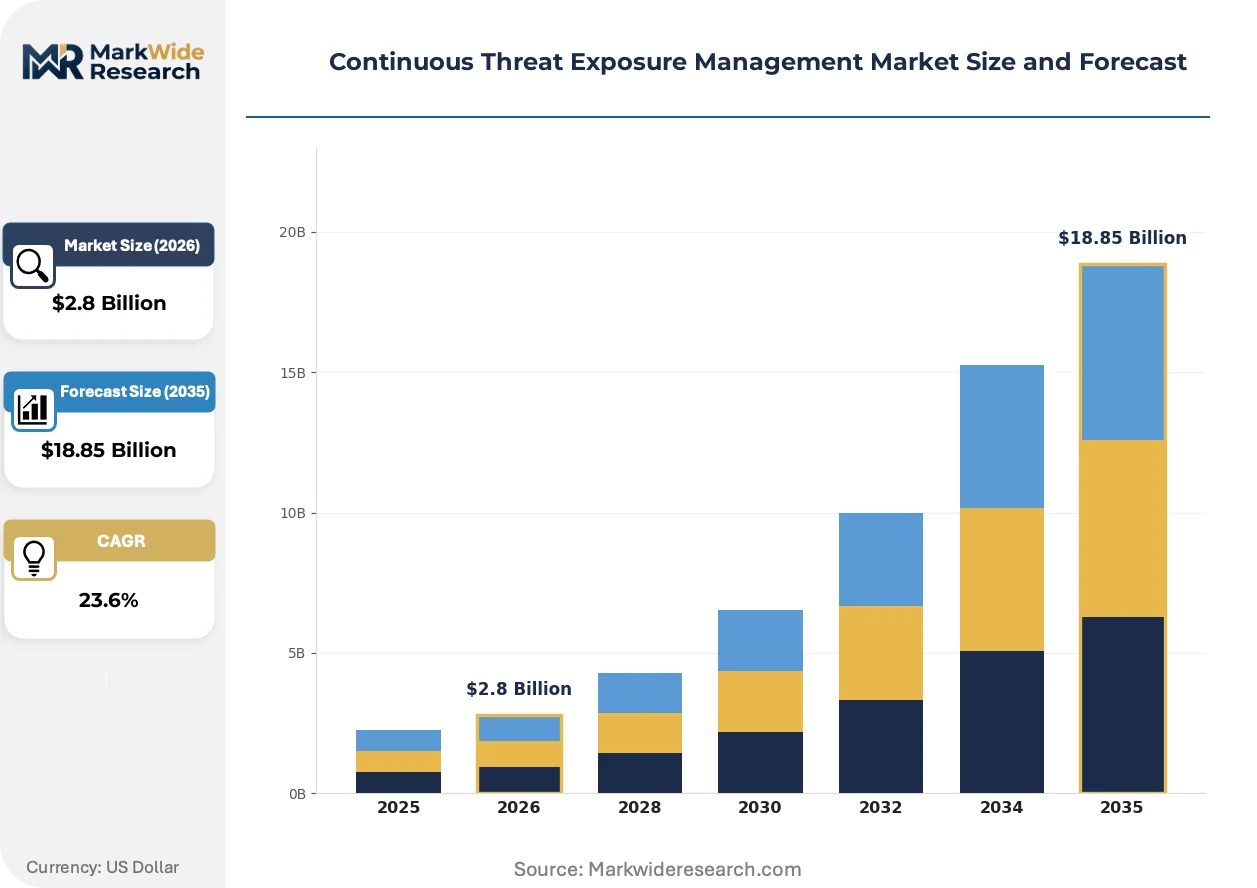
| Market Size in 2026 | $2.8 Billion |
| Market Size in 2035 | $18.85 Billion |
| CAGR (2026 – 2036) | 23.6% |
| Historical Year | 2020-2024 |
| Base Year | 2025 |
| Forecast Period | 2026-2036 |
| Segmentation | Solution Type: Risk Assessment, Vulnerability Management, Attack Surface Analysis, Security Posture Monitoring Deployment Mode: Cloud-Based, On-Premises, Hybrid, Managed Services Application: Enterprise Security, Government Security, Financial Monitoring, Technology Infrastructure Protection End User: Banking Institutions, Telecommunication Providers, Energy Corporations, Public Sector Agencies |
| Companies Covered | IBM, Microsoft, Palo Alto Networks, Rapid7, Tenable, Qualys, Cymulate, AttackIQ, BitSight, Others |
| Regions Covered | North America: US, Canada, Mexico Europe: Germany, Italy, France, UK, Spain, Denmark, Sweden, Austria, Belgium, Finland, Turkey, Poland, Russia, Greece, Switzerland, Netherlands, Norway, Portugal, Rest of Europe Asia Pacific: China, Japan, India, South Korea, Indonesia, Malaysia, Kazakhstan, Taiwan, Vietnam, Thailand, Philippines, Singapore, Australia, New Zealand, Rest of Asia Pacific South America: Brazil, Argentina, Colombia, Chile, Peru, Rest of South America Middle East & Africa: Saudi Arabia, UAE, Qatar, South Africa, Israel, Kuwait, Oman, North Africa, West Africa, Rest of MEA |
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Continuous Threat Exposure Management Market Trends and Innovations
Agentless attack surface discovery is replacing persistent endpoint instrumentation as the preferred discovery modality, reducing deployment friction while expanding coverage to unmanaged and shadow IT assets.
Breach and attack simulation platforms are displacing traditional vulnerability assessment tools in enterprise security budgets by delivering empirical evidence of control failure rather than theoretical risk scores. Large financial institutions in Frankfurt and London have accelerated adoption to satisfy regulatory demands for demonstrable resilience testing. The technology is displacing quarterly penetration testing contracts with continuous validation subscriptions that compress mean-time-to-detect metrics from weeks to hours.
The EU AI Act imposes automated security testing requirements for high-risk AI systems, including critical infrastructure components that rely on machine learning for operational decisions. Providers must now demonstrate continuous validation of AI supply chain integrity and model inference security. Banking and healthcare sectors across Germany, France, and the Netherlands are restructuring procurement specifications to mandate CTEM coverage for AI-enabled applications.
Consolidated platform procurement is displacing best-of-breed point solution acquisition as CISOs prioritize vendor reduction and unified telemetry over specialized capabilities. Enterprise buyers in the United Kingdom and Switzerland now favor integrated exposure management suites that feed directly into existing security orchestration workflows. This concentration pattern favors vendors with broad control plane coverage rather than narrow simulation specialists.
Continuous Threat Exposure Management Market Segmentation
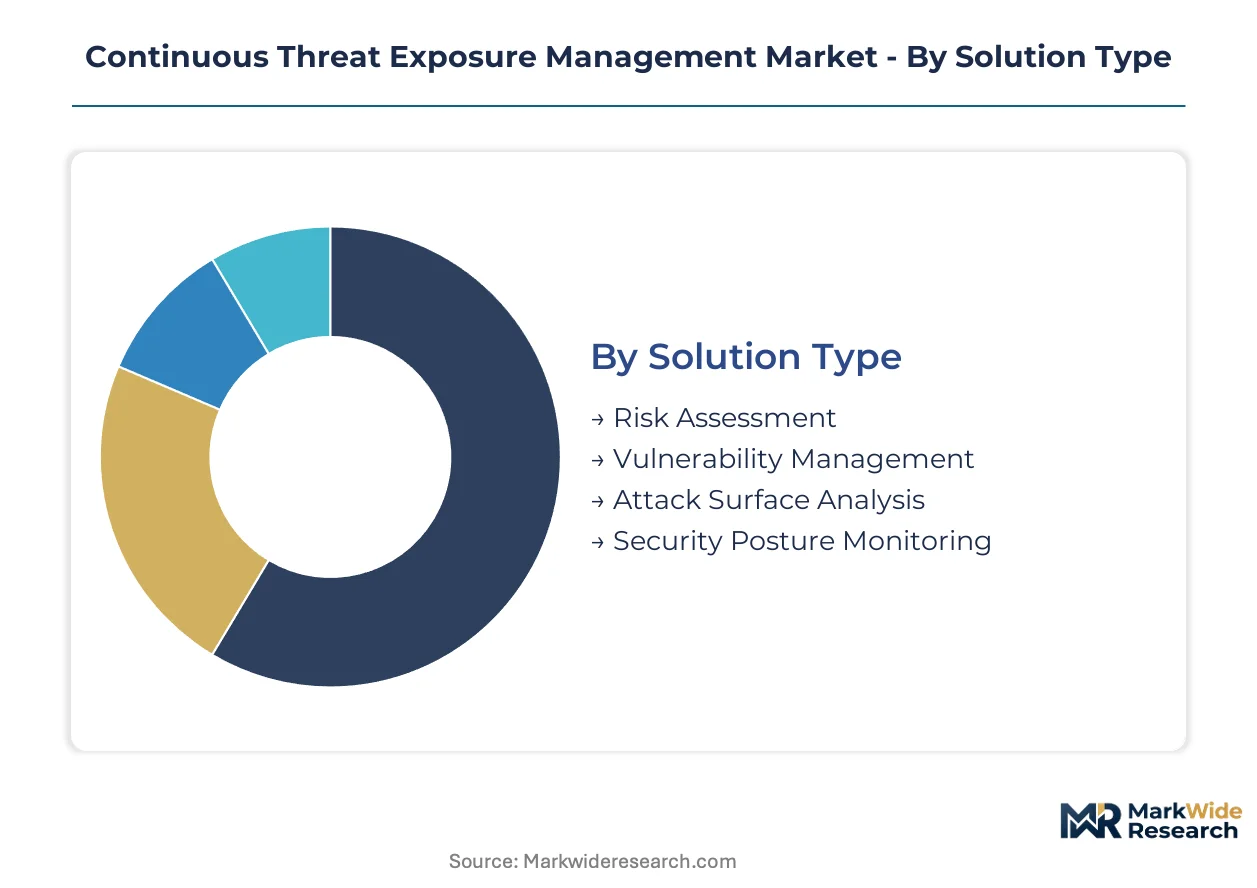
CTEM procurement patterns diverge sharply across solution architectures and operational contexts. Regulatory mandates in Germany, the United Kingdom, and Singapore reshape how buyers prioritize deployment modes and end-user applications.
Solution Type:
The EU AI Act and NIS2 Directive impose distinct validation requirements that favor certain solution architectures over others.
- Risk Assessment:Quantitative scoring engines evaluate exposure severity against business-critical asset inventories. German banking regulators now mandate dynamic risk quantification for operational resilience certifications, concentrating procurement among institutions with dedicated cyber budgets.
- Vulnerability Management:Continuous discovery and prioritization platforms track patch status across ephemeral cloud workloads. Demand is accelerating in Frankfurt and London where financial institutions replace quarterly scanning with persistent validation loops.
- Attack Surface Analysis:Agentless discovery maps shadow IT and unmanaged assets without endpoint instrumentation.
- Security Posture Monitoring:Real-time control effectiveness scoring against MITRE ATT&CK frameworks.
Established volume favors Risk Assessment; emerging adoption favors Vulnerability Management.
Deployment Mode:
Cost tier differentiation separates capital-intensive infrastructure from elastic consumption models.
- Cloud-Based:Elastic compute resources enable continuous validation without hardware procurement cycles. Singaporean technology infrastructure providers are expanding fastest here, driven by containerized workload protection requirements.
- Hybrid:Unified visibility across on-premises legacy systems and cloud-native environments. United Kingdom enterprises with SIEM investments favor this architecture for telemetry correlation.
- On-Premises:Air-gapped installations for classified government networks.
- Managed Services:Fractional expertise delivery addressing purple team skill scarcity.
Hybrid deployments capture the steepest expansion trajectory; On-Premises retains defensive revenue in regulated sectors.
Application:
Customer maturity and security operations sophistication determine solution complexity requirements.
- Enterprise Security:Integrated platforms serving diversified business units with unified control planes. Large German manufacturers are consolidating vendor relationships here, seeking reduction in alert fatigue from fragmented tools.
- Financial Monitoring:Specialized validation for payment systems and trading infrastructure. Singapore and Frankfurt banking regulators mandate demonstrable control effectiveness, concentrating procurement authority.
- Government Security:Classified network protection with sovereign data requirements.
- Technology Infrastructure Protection:Cloud service provider and hyperscaler security validation.
Financial Monitoring leads margin capture; Technology Infrastructure Protection is climbing the fastest.
End User:
Supply concentration in regulated sectors creates distinct procurement authority patterns.
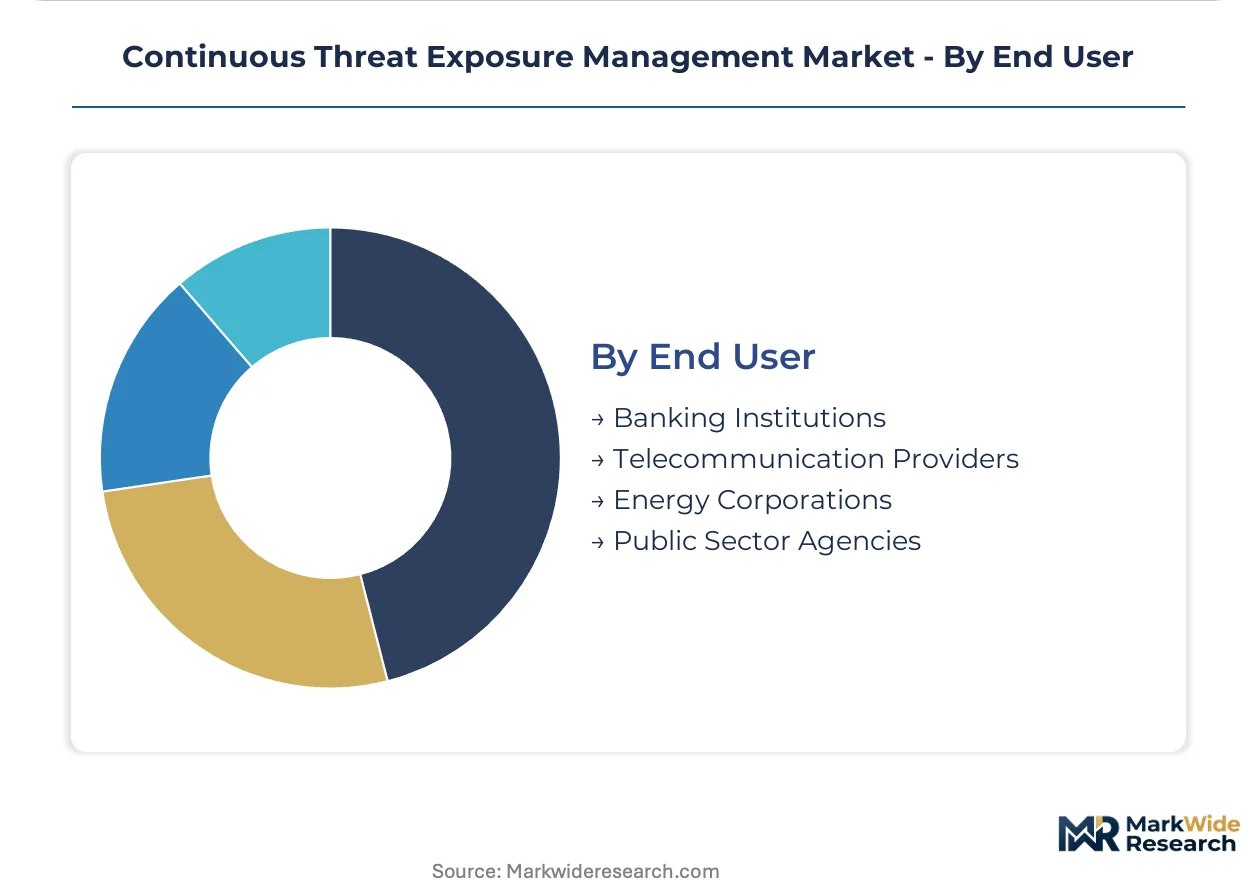
- Banking Institutions:Dedicated cybersecurity budgets and operational resilience mandates drive premium platform adoption. German and UK regulators now require continuous validation evidence, compressing vendor selection cycles.
- Public Sector Agencies:Critical infrastructure protection frameworks channel procurement through centralized frameworks. NIS2 Directive implementation is expanding addressable demand across essential and important entity designations.
- Telecommunication Providers:Network edge protection for 5G and fiber infrastructure.
- Energy Corporations:IT/OT convergence creating unified exposure visibility requirements.
Banking Institutions anchor current revenue; Public Sector Agencies represent the fastest-growing demand pool.
Need this report tailored to your region?
Request specific countries, segments, or companies — tailored to your requirements.
Regional Outlook
German enterprises command pricing premiums for integrated CTEM platforms while Indian mid-market buyers concentrate procurement around managed service tiers. This asymmetry reflects divergent regulatory enforcement intensity and security operations maturity across procurement geographies.
Germany
BaFin operational resilience mandates and NIS2 Directive implementation are compressing vendor selection cycles for banking institutions. The national cybersecurity authority requires continuous validation evidence for critical infrastructure operators. Frankfurt's financial cluster is consolidating procurement around unified exposure management suites that feed directly into existing security orchestration workflows.
United Kingdom
FCA and PRA operational resilience deadlines are driving replacement of quarterly penetration testing with persistent validation subscriptions. The National Cyber Security Centre procurement frameworks channel demand through centralized security validation specifications. London's banking and insurance concentration is accelerating adoption of breach and attack simulation platforms for demonstrable control effectiveness testing.
Singapore
MAS Technology Risk Management Guidelines mandate continuous security monitoring for financial institutions and payment service providers. The Cyber Security Agency operates dedicated procurement frameworks for critical information infrastructure protection. The technology infrastructure provider cluster is expanding fastest in cloud-based deployment modes driven by containerized workload protection requirements.
United States
SEC cyber disclosure rules and HIPAA security evaluation standards compel regulated entities to adopt continuous validation methodologies. CISA guidance on vulnerability management prioritization shapes federal procurement specifications. The New York financial services cluster is restructuring vendor relationships around platform consolidation strategies that reduce alert fatigue from fragmented tools.
France
ANSSI certification requirements and EU AI Act implementation are restructuring procurement specifications for AI-enabled applications in banking and healthcare. The national cybersecurity agency mandates automated security testing for high-risk digital infrastructure operators. Paris-based financial institutions are embedding MITRE ATT&CK framework mapping into vendor evaluation criteria for measurable risk reduction.
Continuous Threat Exposure Management Market Competitive Landscape
Technology leadership and cost leadership are held by different player archetypes across the CTEM market structure. Consolidated platform vendors with broad control plane coverage capture enterprise procurement authority while specialized simulation providers occupy niche validation segments. Three strategic archetypes dominate: integrated cybersecurity platforms extending exposure management modules, pure-play breach and attack simulation specialists, and managed security service providers delivering fractional validation expertise. Competitive dynamics center on vendor consolidation partnerships and cloud-native architecture migrations that displace on-premises security stacks.
Within the integrated platform tier, Palo Alto Networks and Microsoft exemplify archetypes leveraging existing security budget relationships to extend control over exposure management procurement. Tenable occupies a position representing vulnerability intelligence leadership through deep instrumentation capabilities. These three anchors demonstrate how technology breadth and telemetry depth determine competitive positioning against point solution specialists.
| Leading Market Players |
|---|
| IBM |
| Microsoft |
| Palo Alto Networks |
| Rapid7 |
| Tenable |
| Qualys |
| Cymulate |
| AttackIQ |
| BitSight |
| Others |
Pricing and Supply Chain Analysis
Ninety-day implementation cycles for enterprise CTEM platforms compress vendor cash conversion and concentrate pricing power among suppliers with pre-built connector libraries. German banking procurement teams now demand configured-to-order deployments with MITRE ATT&CK framework mapping, widening spreads between standard SaaS tiers and premium integration packages.
Pricing Analysis
Configured-to-order pricing for custom MITRE ATT&CK framework mapping and SIEM connector development commands premiums exceeding standard SaaS subscriptions by substantial margins. Subscription tiers stratify across agentless discovery modules, breach and attack simulation engines, and managed validation services, with price differentiation driven by telemetry depth and regulatory certification scope. Pricing pressure stems from hyperscaler security bundles absorbing mid-market budgets, compressing standalone vendor margins. Financial institutions in Frankfurt and Singapore exhibit lowest price sensitivity due to operational resilience mandates, while Indian mid-market buyers concentrate procurement around managed service tiers with fractional expertise delivery.
Supply Chain Analysis
Container availability constraints on Asia-Europe trade lanes elevate inbound logistics costs for hardware-dependent on-premises deployments, though cloud-native delivery mitigates physical supply exposure. Engineering talent concentrates in Israel, the United States, and the United Kingdom, with adversary simulation research anchored in Tel Aviv and Boston clusters. Cloud compute resources draw from hyperscaler infrastructure in Ireland, Singapore, and Virginia, creating single-source vulnerability to regional outage events. Distribution runs through direct enterprise sales organizations supplemented by channel partners serving mid-market segments, with managed service providers capturing growing downstream share.
Get the full picture before you read further.
Download a free sample with table of contents, companies, segments, and methodology.
Analyst Recommendations
Regulatory entrenchment creates defensive moats for established CTEM vendors as EU NIS2 Directive and AI Act compliance requirements elevate switching costs beyond point-solution replacement thresholds.
For Market Incumbents: Compound platform consolidation advantages by embedding breach and attack simulation modules into existing security orchestration workflows, neutralizing point-solution specialists. Extend control plane coverage into operational technology networks before industrial control system vendors develop native exposure management capabilities. Prioritize certification investment for EU AI Act automated testing requirements to entrench procurement relationships with Frankfurt and Paris banking clusters. For New Entrants and Emerging Players: Differentiate on agentless discovery speed for ephemeral cloud workloads, targeting technology infrastructure providers in Singapore and Bangalore with container-native architectures. The most penetrable segment lies in mid-market managed validation services where purple team skill scarcity creates fractional expertise demand. Pursue channel partnerships with regional system integrators possessing existing security operations center relationships rather than direct enterprise sales buildout. For Investors and Strategic Acquirers: Carve-out targets emerge from diversified cybersecurity conglomerates seeking to monetize non-core exposure management divisions amid portfolio rationalization. Long-term viability favors vendors with demonstrated MITRE ATT&CK framework integration and recurring revenue concentration above project-based consulting. Monitor CISA vulnerability management prioritization guidance revisions as signal for federal procurement specification shifts.| Strategic Initiative | Industry Significance |
|---|---|
| Platform Integration | Unifies telemetry from Palo Alto Networks and Microsoft security stacks into continuous validation workflows. |
| Regulatory Certification Investment | Secures ANSSI and BaFin accreditation for EU AI Act and NIS2 Directive compliance mandates. |
| Managed Service Tier Launch | Addresses purple team skill scarcity through fractional expertise subscriptions for mid-market buyers. |
| OT Network Expansion | Captures IT/OT convergence demand from German energy and manufacturing critical infrastructure operators. |
| Strategic Partnership | Accelerates SIEM connector development through engineering alliances with Splunk and IBM QRadar channels. |
Research Methodology
Cross-validation between primary interviews with CISOs, security operations center directors, and channel partners anchors the qualitative findings against secondary sources including SEC cyber disclosure filings, EU NIS2 Directive implementation guidelines, and CISA vulnerability management advisories. Bottom-up demand estimation triangulates against top-down market sizing derived from hyperscaler security revenue disclosures and banking regulatory procurement frameworks.
Sensitivity analysis across deployment mode adoption curves, regulatory compliance timeline acceleration, and cloud-native workload expansion rates shapes the forecast framework. Segmentation dimensions include solution architecture, deployment mode, end-user industry, and geographic regulatory cluster. CAGRs derive from logistic diffusion modeling of enterprise security budget reallocation patterns, with inputs incorporating BaFin operational resilience mandate enforcement intensity and containerized infrastructure penetration trajectories.
The analysis sits within stated boundaries; outcomes outside sustained regulatory enforcement pressure and hyperscaler platform bundling aggression would require recalibration. Forecasts reflect assumptions regarding EU AI Act implementation consistency and banking sector cybersecurity budget maintenance. Outcomes outside this envelope would require model recalibration.
Need Custom Data?
Can't find what you're looking for? Our analysts can build a custom report tailored to your exact requirements.
1,000+
Global Clients
150+
Countries Covered
65,000+
Reports Available
Frequently Asked Questions
Why Work With MWR
Trusted by 1,000+ businesses across 150+ countries for high-stakes market decisions.
Ready to access intelligence that moves business?
Browse Reports →Trusted by Global Leaders
From Fortune-level organizations to global SMEs, we provide intelligence for high-stakes decisions.
Multi-Language Support
Research available in French, German, Spanish, Chinese, and more.
ISO & IAF Certified
Globally aligned quality standards ensuring methodological discipline and data integrity.
Competitive Relevance
Free inclusion of 3–4 additional companies of your choice in every report.
Customized Insights
Tailored intelligence for market entry, niche expansion, or competitive benchmarking.
Post-Sale Assistance
Dedicated coordination to help interpret findings and address queries post-delivery.
Cutting-Edge Methods
Structured data collection, advanced analytics, and expert validation for reliable forecasts.
Value for Investment
Credible, structured intelligence at a cost that makes strategic sense.
What Our Clients Say
My team needed the real numbers on AI spending for our Reinvention Services work. MarkWide delivered. No fluff, just a clear look at where the money is actually going. It saved us about three weeks of guesswork.
Accenture
We recently leaned on MarkWide Research for a deep dive into the evolving snacking habits within Southeast Asia. Their report on the premium biscuit segment was exceptionally detailed, providing us with the specific consumer sentiment data we needed to refine our regional flavor strategy. It wasn't just a data dump; the cultural nuances they captured helped us avoid several localization pitfalls.
Mondelez
Director of Global Consumer Insights
For a recent engagement in the automotive sector, we needed rigorous, independent verification of EV battery recycling capacities. MWR delivered a report that made our work easier. Their ability to segment the competitive landscape by chemical composition and regional throughput was exactly the kind of 'hard-to-find' intel that our team was looking for.
BCG
We were looking for a report on Xcelerator ecosystem's potential and got in touch with MarkWide's team through one of my old colleagues who worked with them in the past. Their research team was incredibly polite and were always available for us which was important for my team as this was a custom project. Their methodology for tracking industrial IoT adoption gave our R&D heads the clarity needed to prioritize our next-gen sensor development.
Siemens
Head of Industrial Digitalization
During a recent M&A project, we needed a fast, reliable breakdown of the Fintech landscape in Southeast Asia. MarkWide came through with a report that was actually readable and focused on the metrics that matter. It saved my team a good week of primary research, which, given our timelines, was a massive win.
KPMG
Advisory Partner
We tapped MarkWide Research for a deep dive into the ESG reporting software market. At Deloitte, our clients expect us to have the most current insights, and this report didn't disappoint. It provided a breakdown of the competitive field that was far more detailed than what we were expecting.
Deloitte
Lead Consultant, Sustainability Services
For our semiconductor division at Samsung, the supply chain forecast from MarkWide was incredibly useful. It provided a realistic outlook on raw material availability that helped us refine our production timelines. No fluff, just the data we needed to make a tough call.
Samsung
The value for our organization comes from three things: depth of research, specificity of segments and being easy to work with. As important as the first two are, the third can't be underestimated. MarkWide Research, maybe more than any other research vendor, wants to know what is top of mind for our team and what big questions we are grappling to answer. Their customer first approach and high value engagement model have given us great analysis and excellent value for money.
3M
I can share that it was a positive experience wherein MarkWide Research demonstrated flexibility to adapt to our needs and delivered an excellent report that fits all our requirements. Personally, I liked the timely follow up by the team and we will definitively reach out in case more research support is required.
VITO
Related Reports
Critical Infrastructure Protection
Global High Integrity Pressure Protection System (HIPPS) Market
Critical Infrastructure Protection
North America Public Infrastructure Safety Market
Critical Infrastructure Protection
Global Perimeter Protection Market
Critical Infrastructure Protection
Threat Lifecycle Services Market
Critical Infrastructure Protection
Global Airport and Marine Port Security Market
Critical Infrastructure Protection
Tele Protection Market
Critical Infrastructure Protection
Guardrail Protection System Market
Critical Infrastructure Protection
Europe Tank Protection Market
Critical Infrastructure Protection
Middle East and Africa Explosion-Proof Equipment Market
Critical Infrastructure Protection
Global Advanced Persistent Threat (APT) Protection Market
Critical Infrastructure Protection
Global Hazardous Area Equipment Market
Critical Infrastructure Protection
Asia-Pacific Public Infrastructure Safety Market
Critical Infrastructure Protection
Critical Infrastructure Monitoring Market
Critical Infrastructure Protection
Asia Pacific Tank Protection Market
Critical Infrastructure Protection
Perimeter Defense System Market
Critical Infrastructure Protection
Global Railway Platform Security Market